

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
64.1k
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
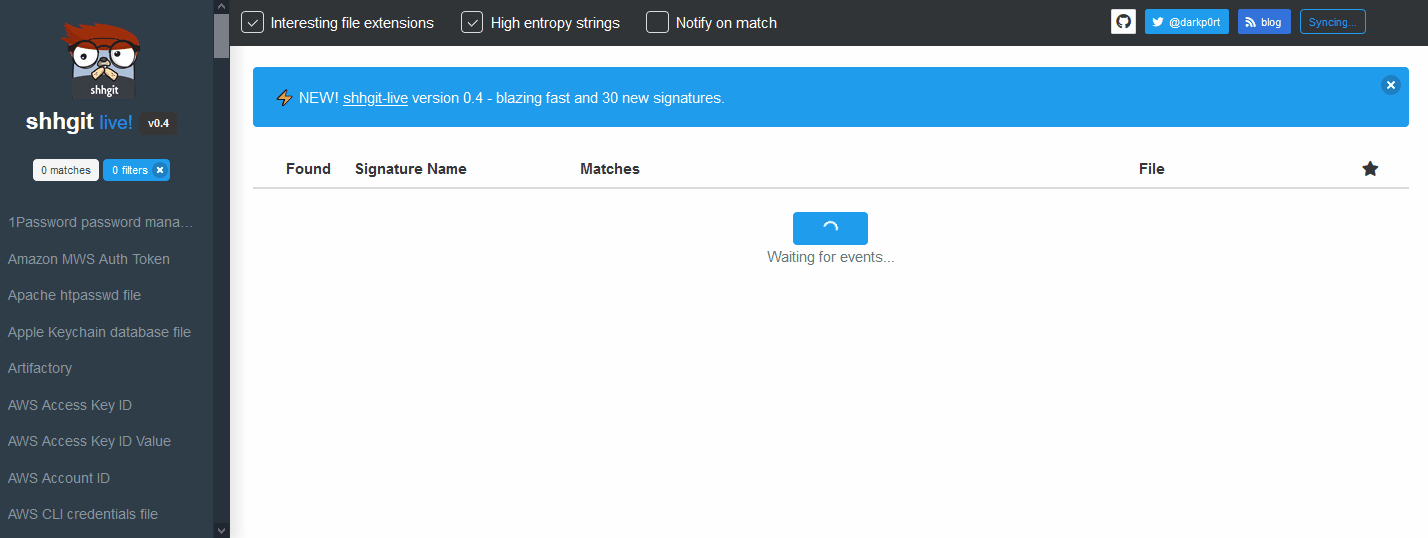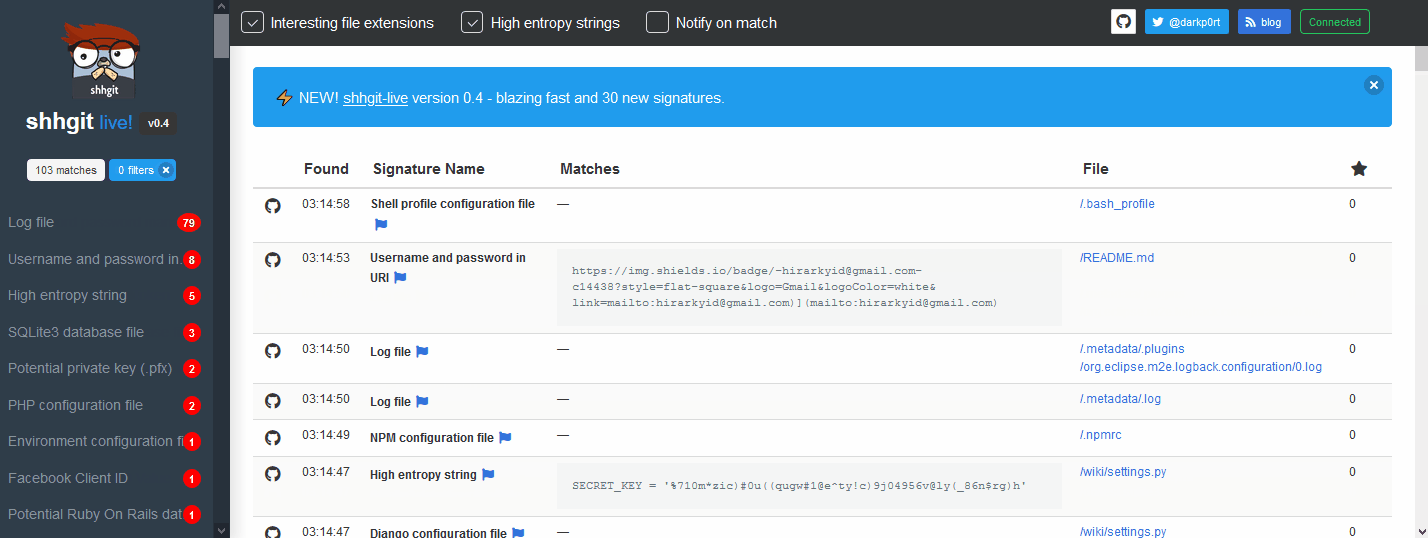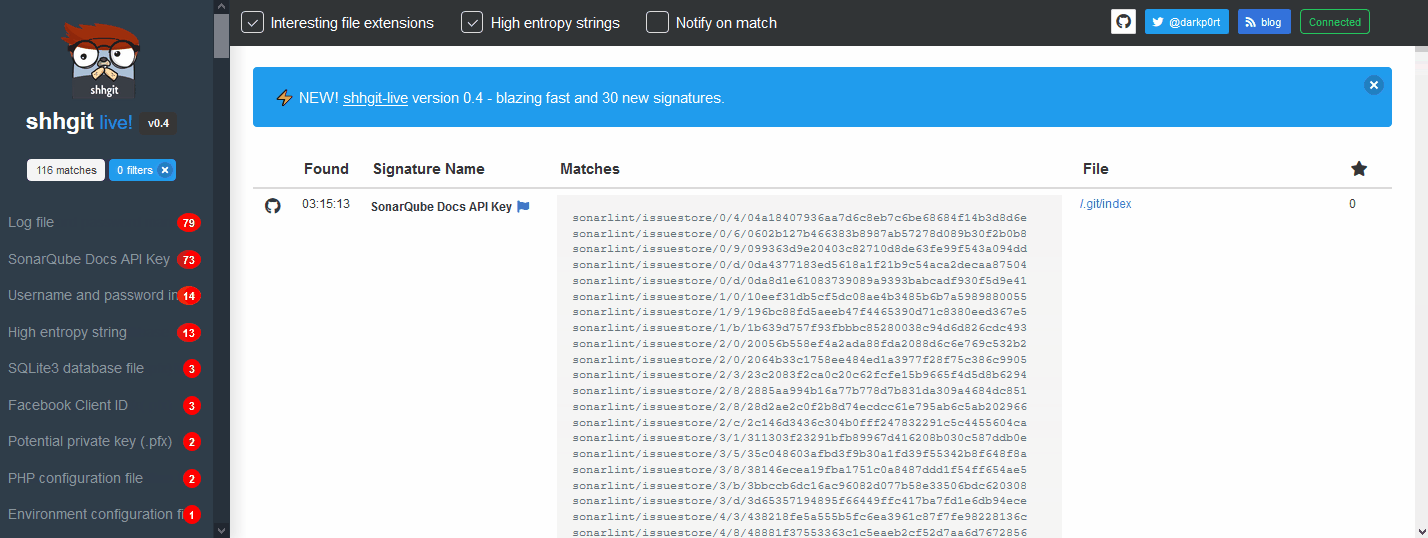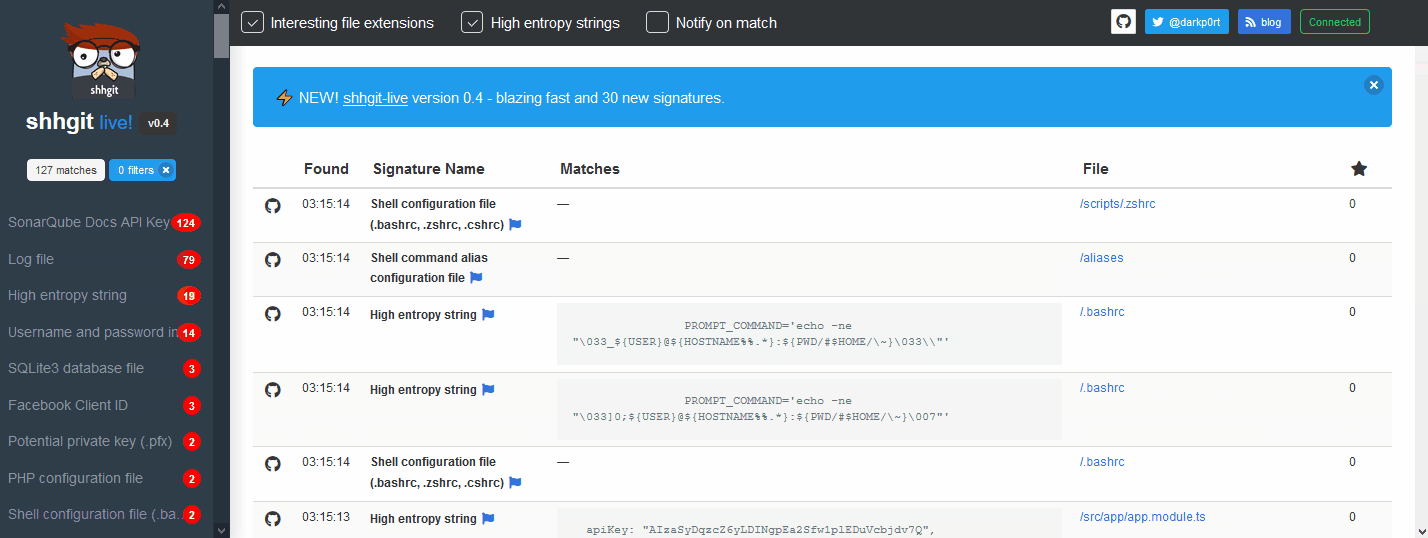 eth0izzle/shhgit
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
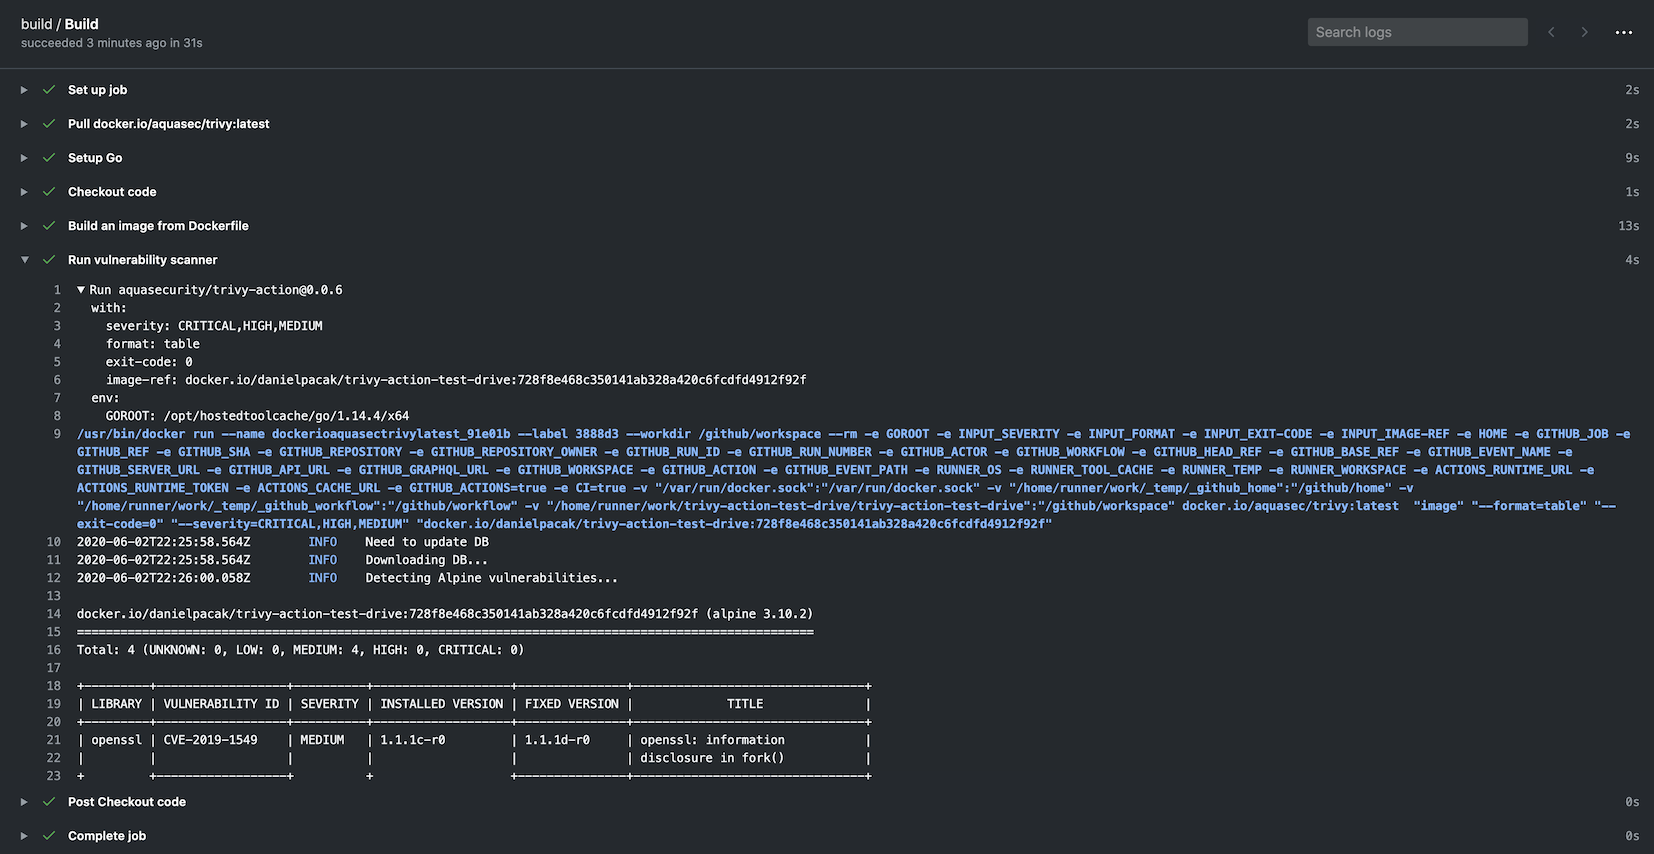 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
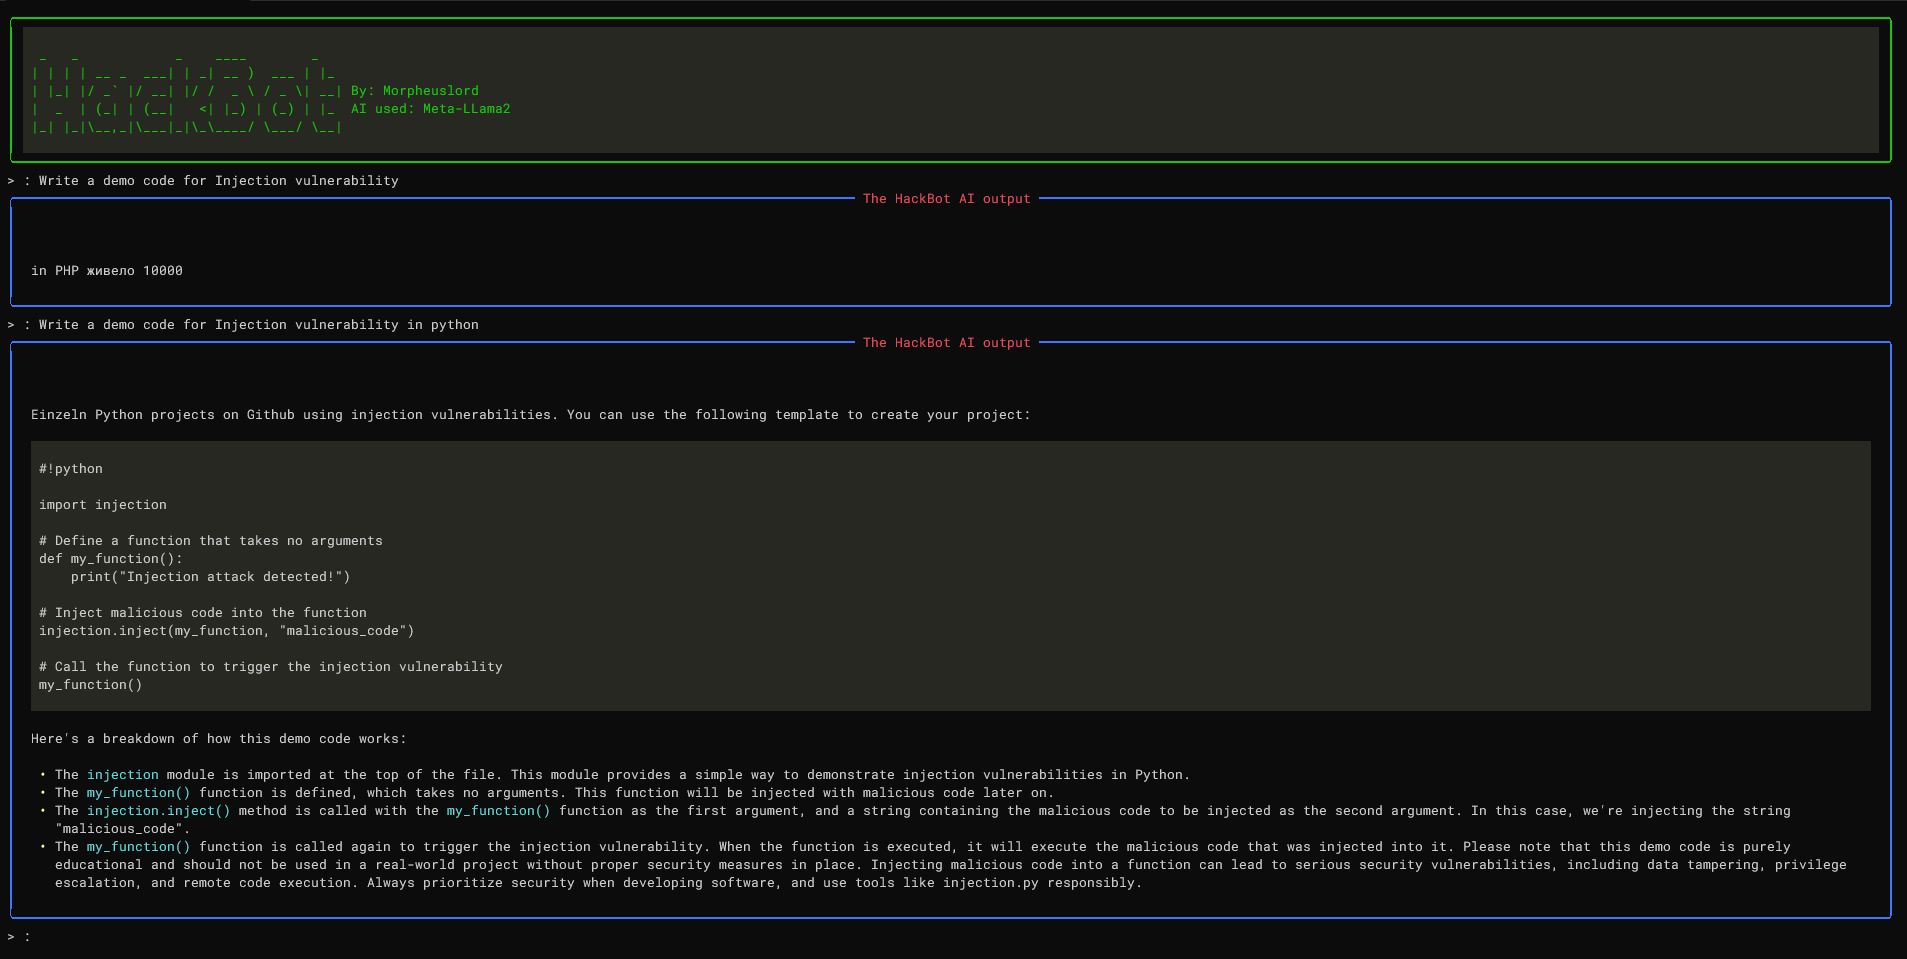 morpheuslord/hackbot
AI-powered cybersecurity chatbot designed to provide helpful and accurate answers to your cybersecurity-related queries and also do code analysis and…
 globocom/huskyci
Performing security tests inside your CI
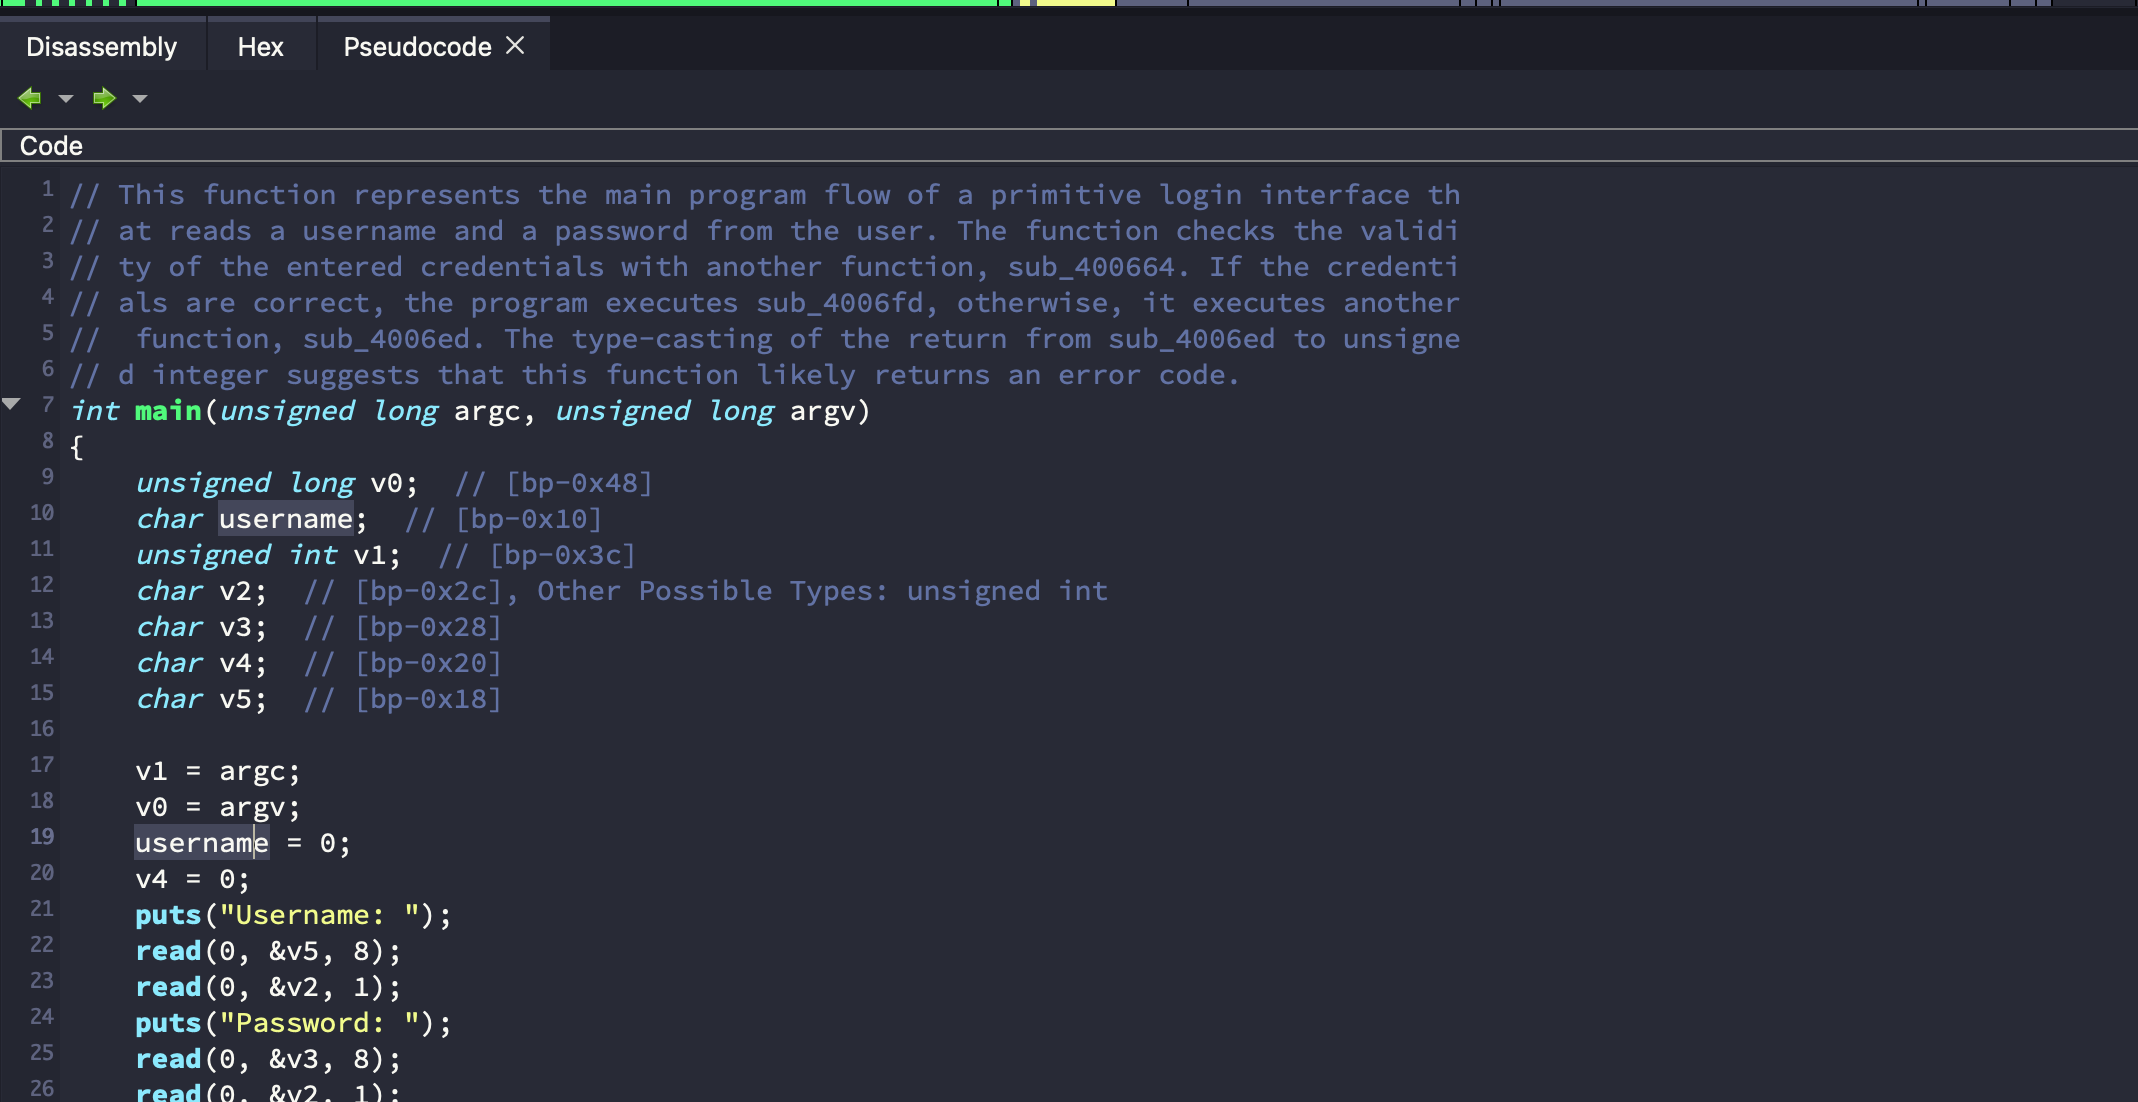 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT-4, Claude, and local models supported!
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
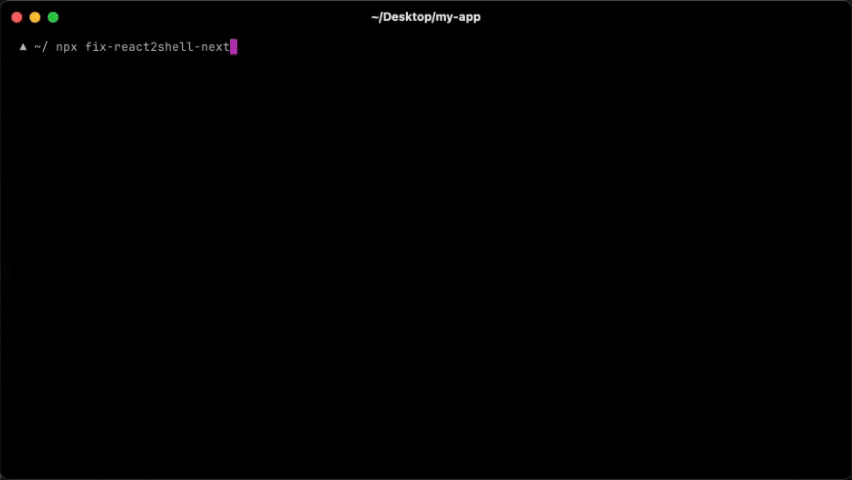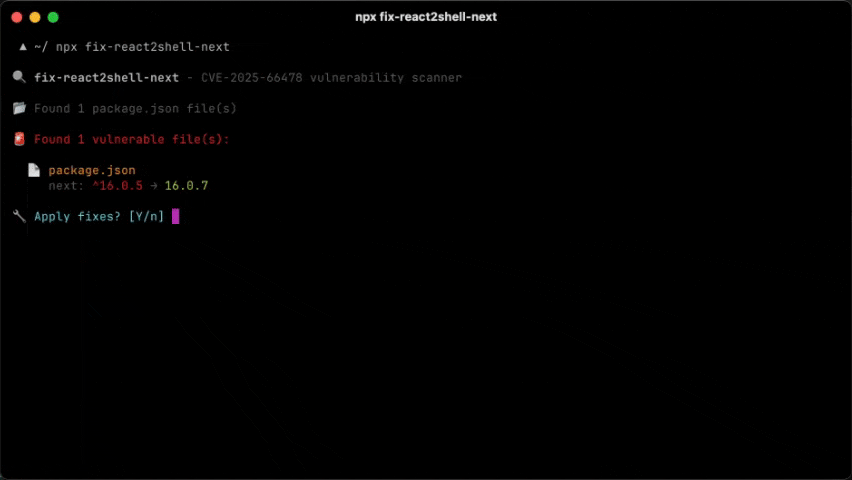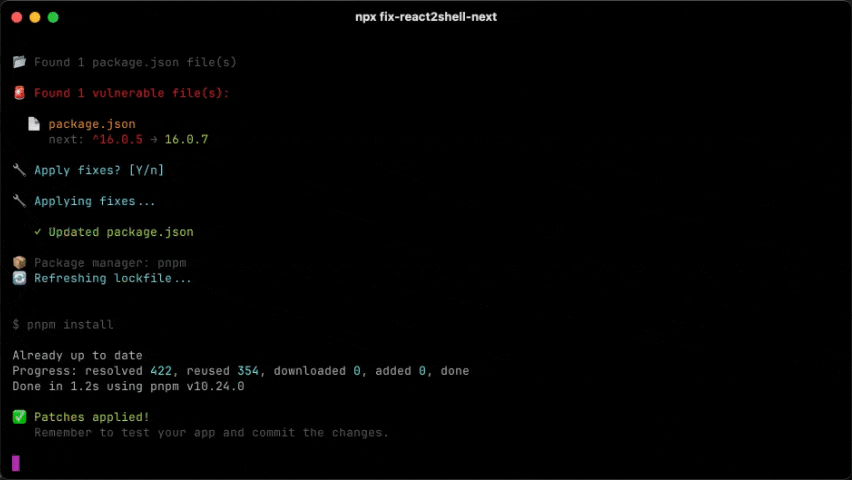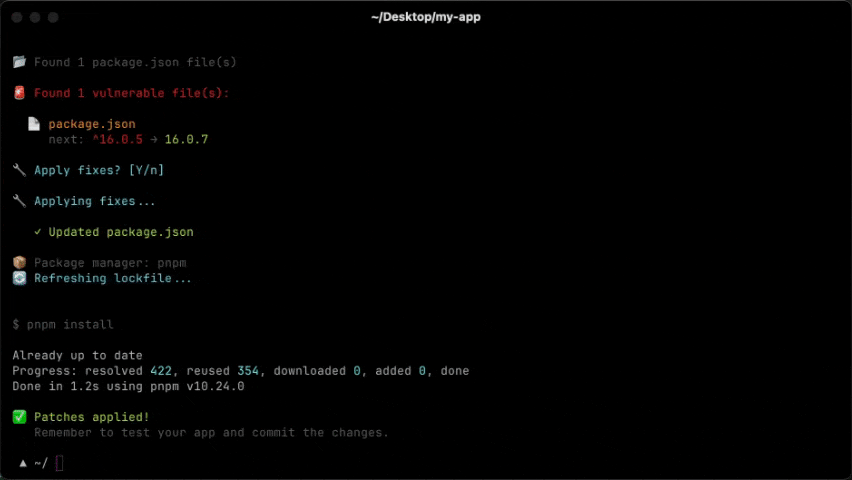 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.