
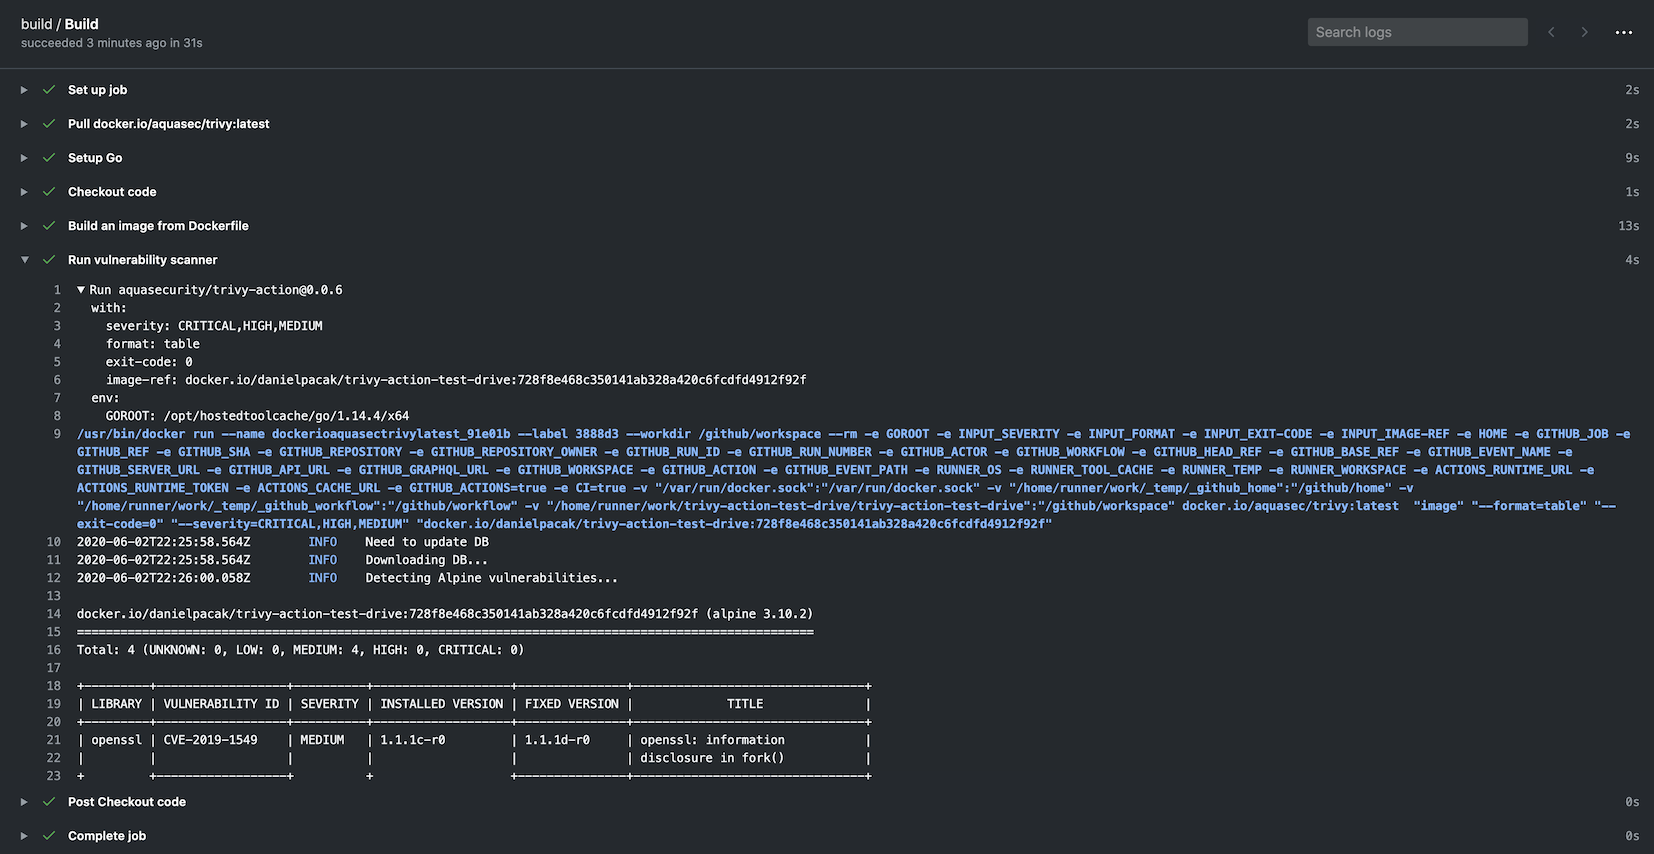
trivy-action
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.4k
aquasecurity/trivy-actionRuns Trivy as GitHub action to scan your Docker container image for vulnerabilities
 falconkei/snakeyaml_cve_poc
SnakeYAML-CVE-2022-1471-POC
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
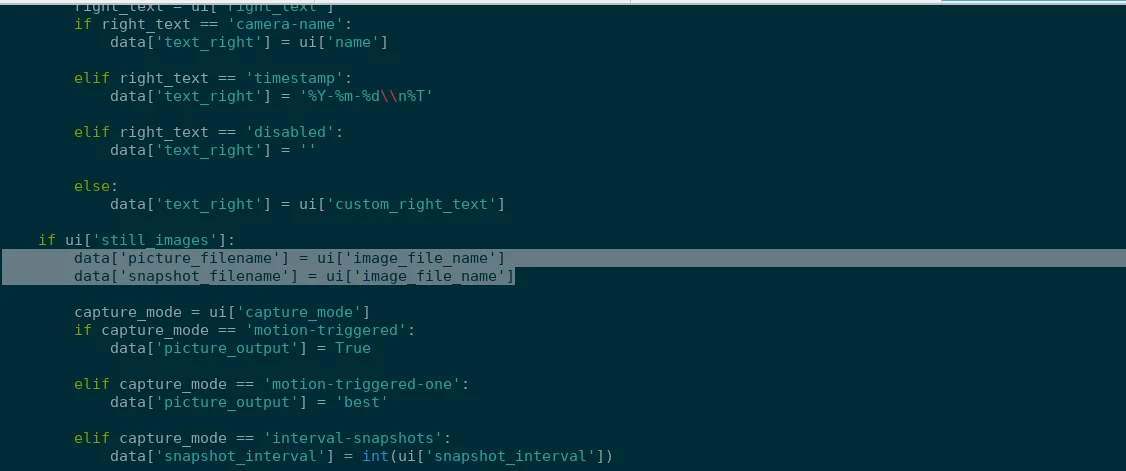 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
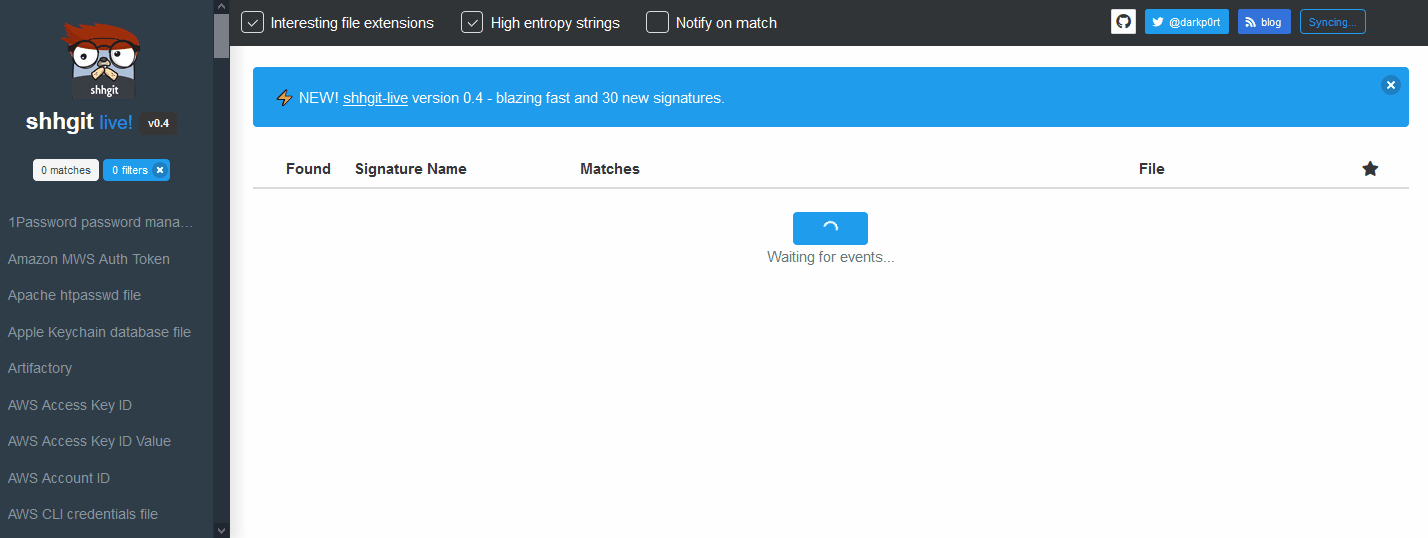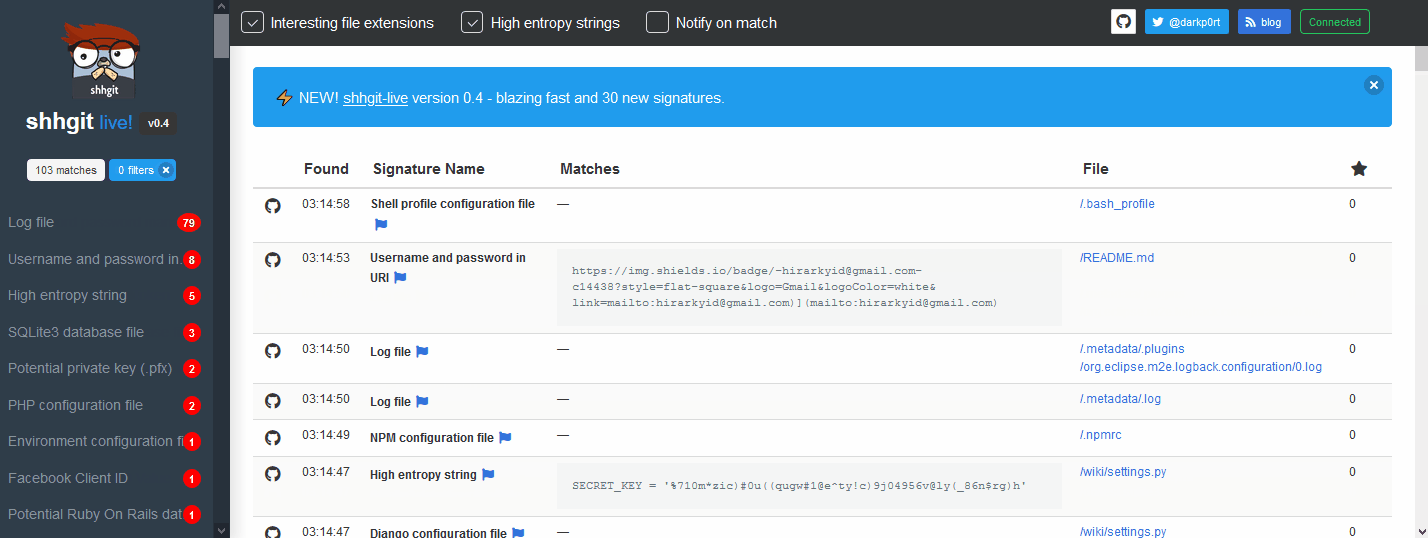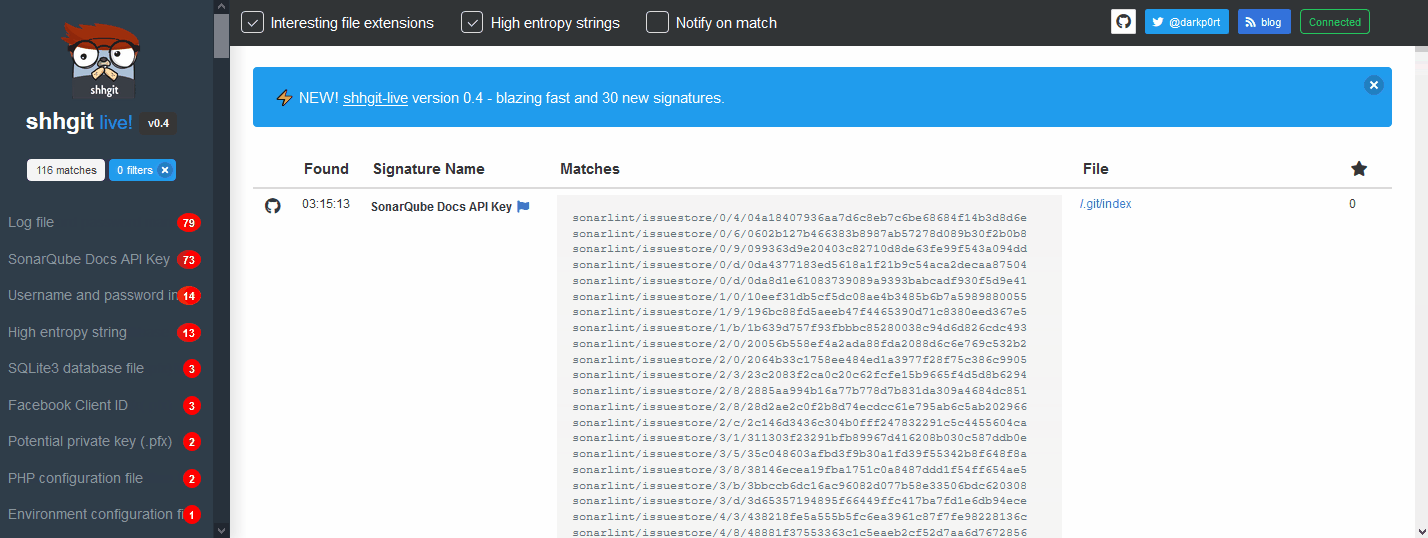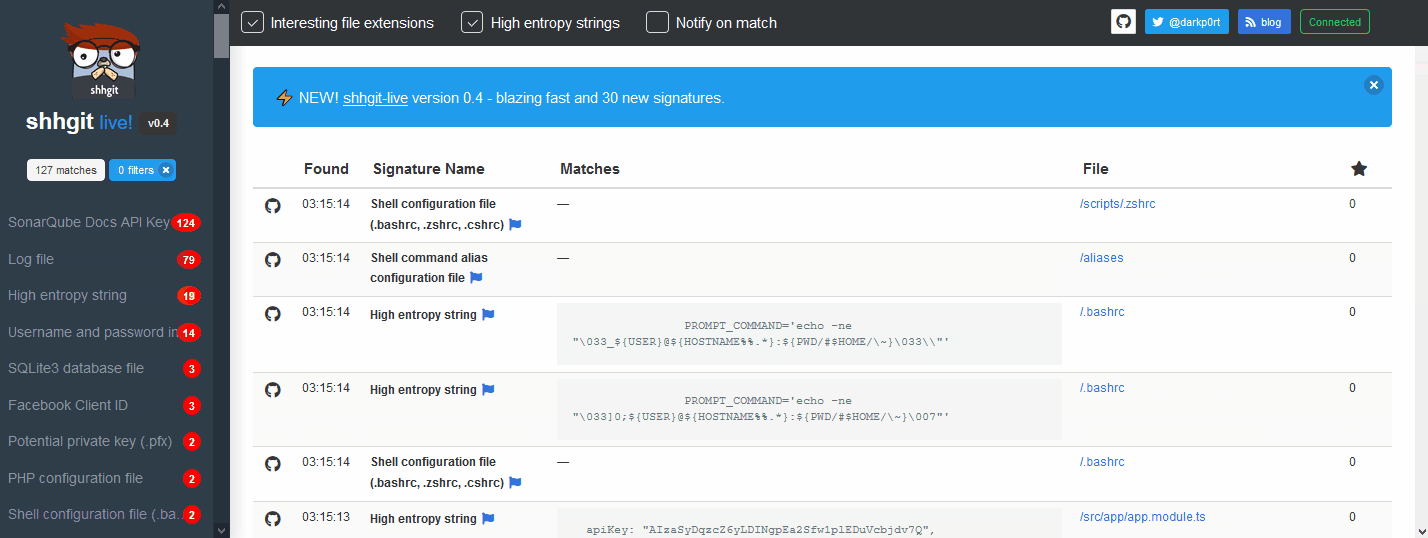 eth0izzle/shhgit
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.
 safedep/vet
Protect against malicious open source packages 🤖
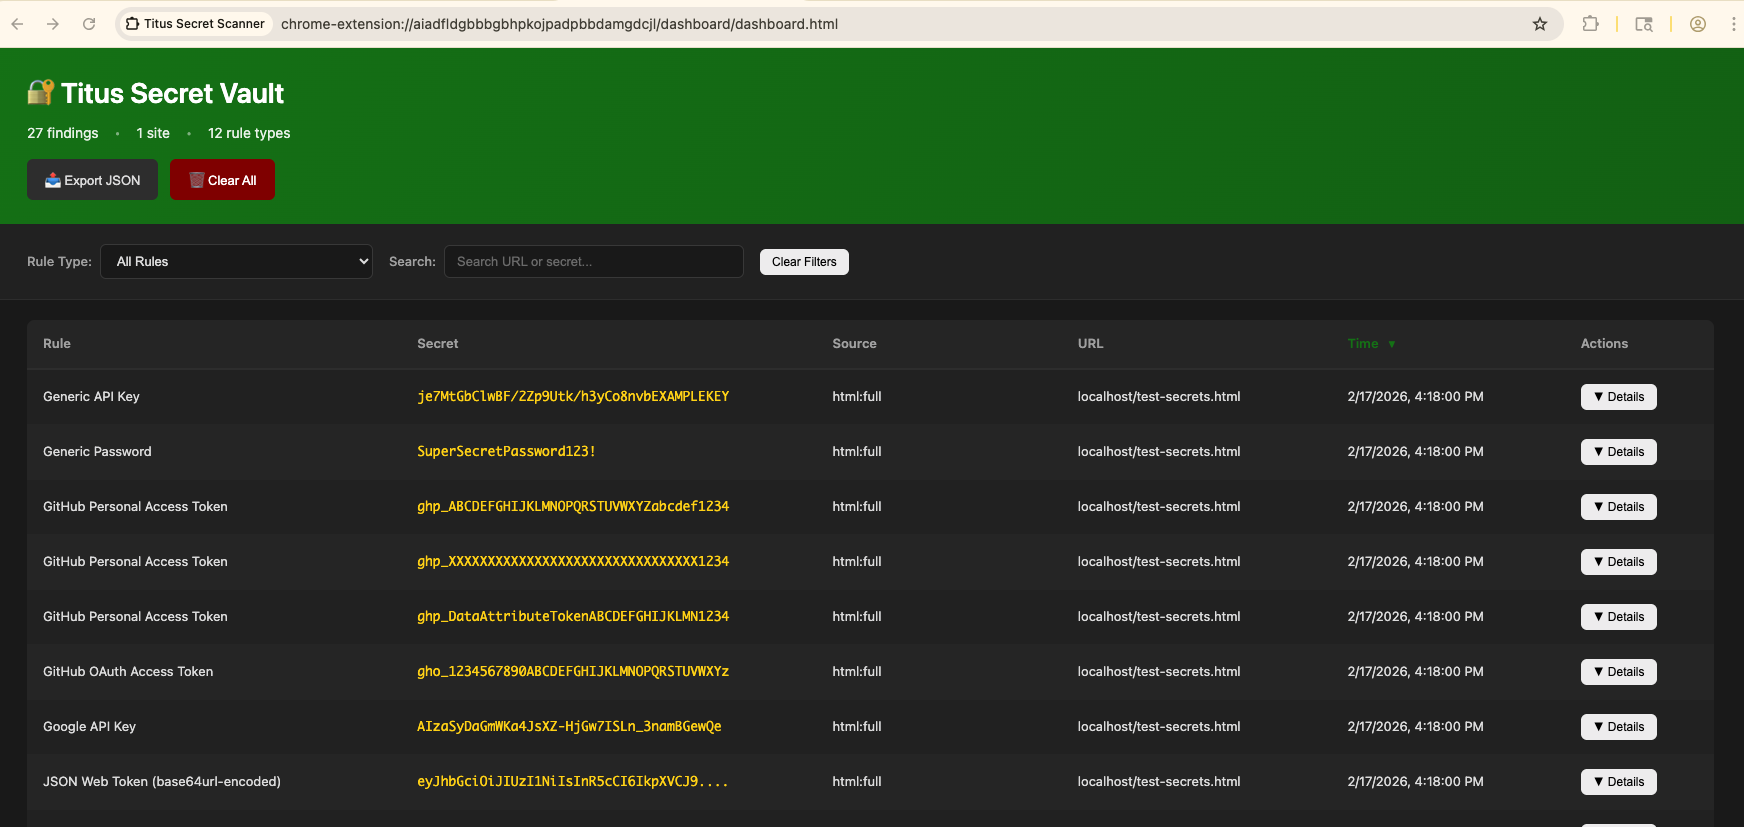 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…