

horusec
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
cloud-securitycode-analysiscontainer-security+5
1.3k3 years ago
zupit/horusecHorusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 oscerd/cve-2026-55994
PoC reproducer for CVE-2026-55994 (Apache Camel camel-iggy): the consumer copies an Iggy message's user-headers onto the Exchange unfiltered, so an…
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
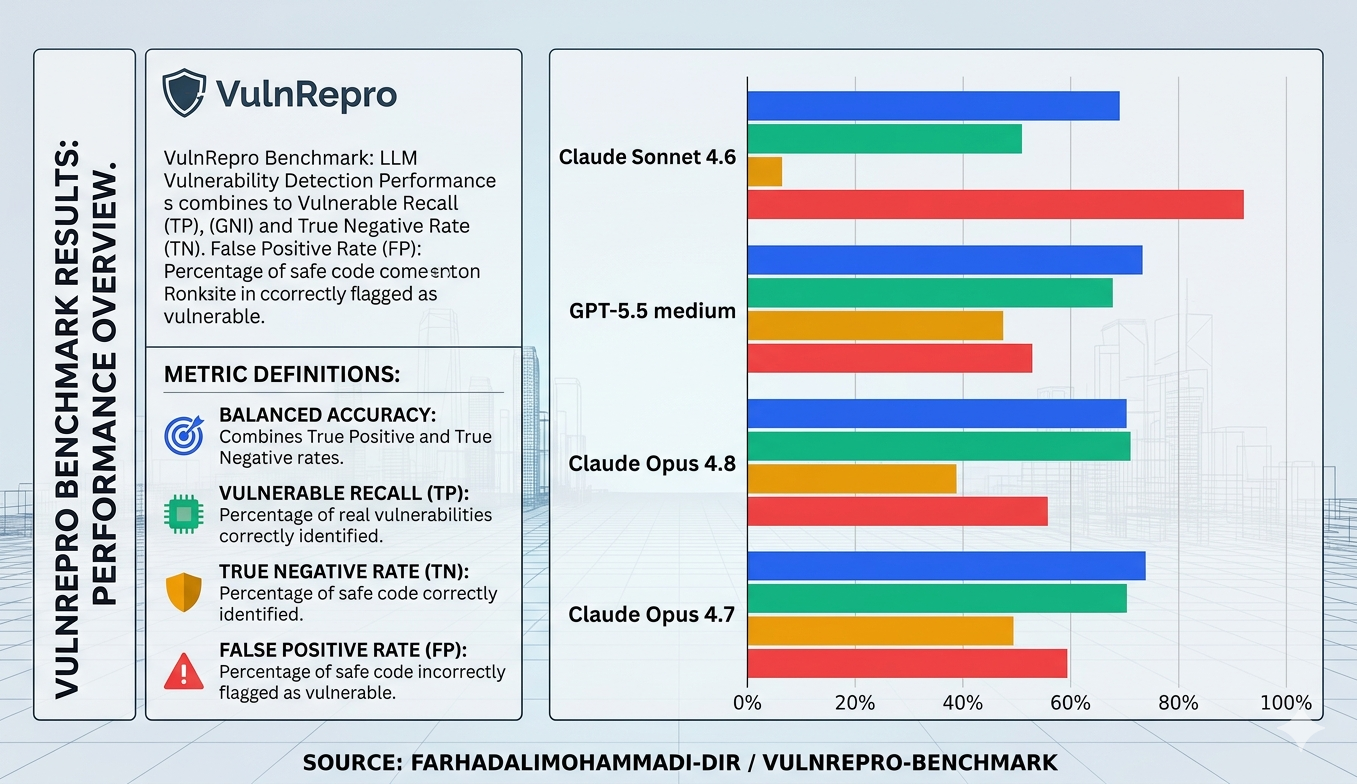 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 w2xim3/cve-2023-6933
Introduction to CVE-2023-6933 Vulnerability
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 pabloopez/cve-2024-21534
Proof-of-concept (PoC) exploit for JSONPath-plus vulnerability
 evillm/cve-2023-4634-poc
Proof-of-concept exploit for CVE-2023-4634, a remote code execution vulnerability in the WordPress Media Library Assistant plugin. Includes a…
 praetorian-inc/gokart
A static analysis tool for securing Go code
 vert16x/cve-2023-32571-poc
Proof-of-concept exploit for CVE-2023-32571 demonstrating Dynamic Linq injection to achieve remote code execution, with a Docker-based lab…
 4rtamis/cve-2022-23614
Proof of concept for CVE-2022-23614 (command injection in Twig)
 minsmiths/cve-2023-34446
Proof-of-concept exploit for CVE-2023-36664, a Ghostscript command injection vulnerability. Includes Docker lab environment, detailed analysis of…
 ksaweryr/cve-2023-45612-poc
Proof of concept for XXE in Ktor (CVE-2023-45612)
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 a0xnirudh/kurukshetra
Kurukshetra - A framework for teaching secure coding by means of interactive problem solving.