TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Fix-Like Artifacts With Embedded Defects

Project Aura: Security auditing and code introspection

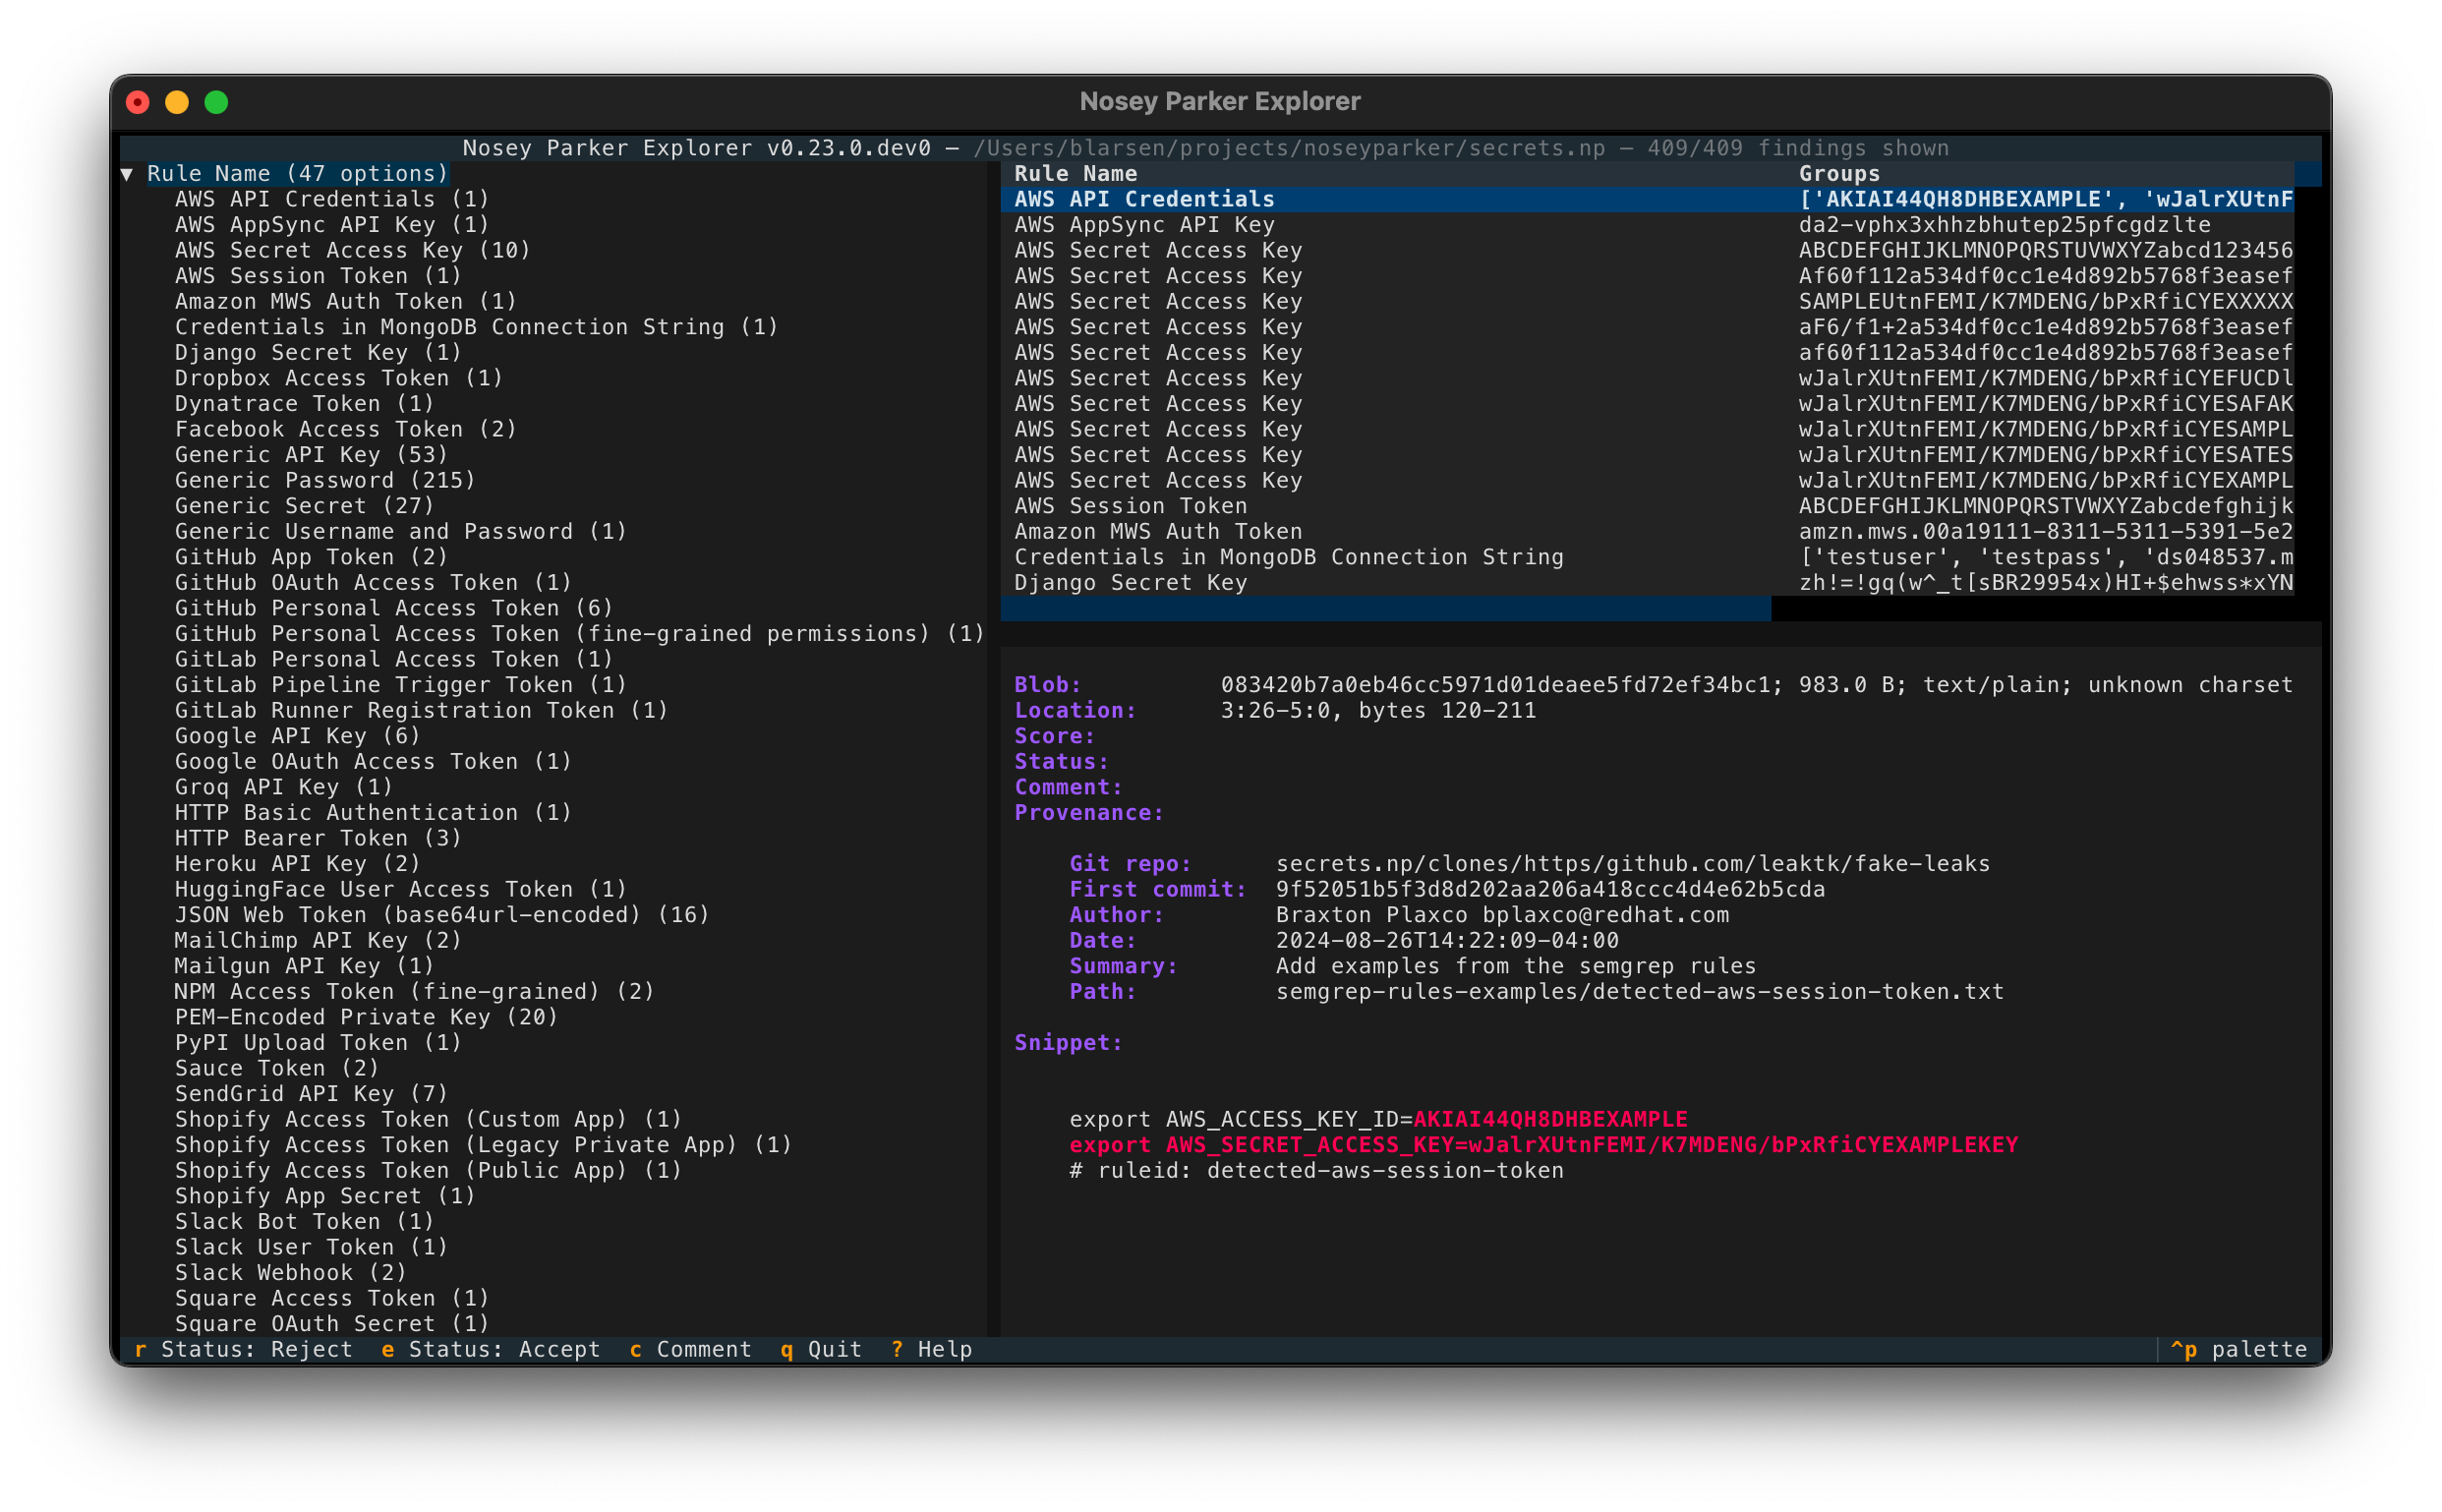
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.

A project security/vulnerability/risk scanning tool

kadimus is a tool to check and exploit lfi vulnerability.

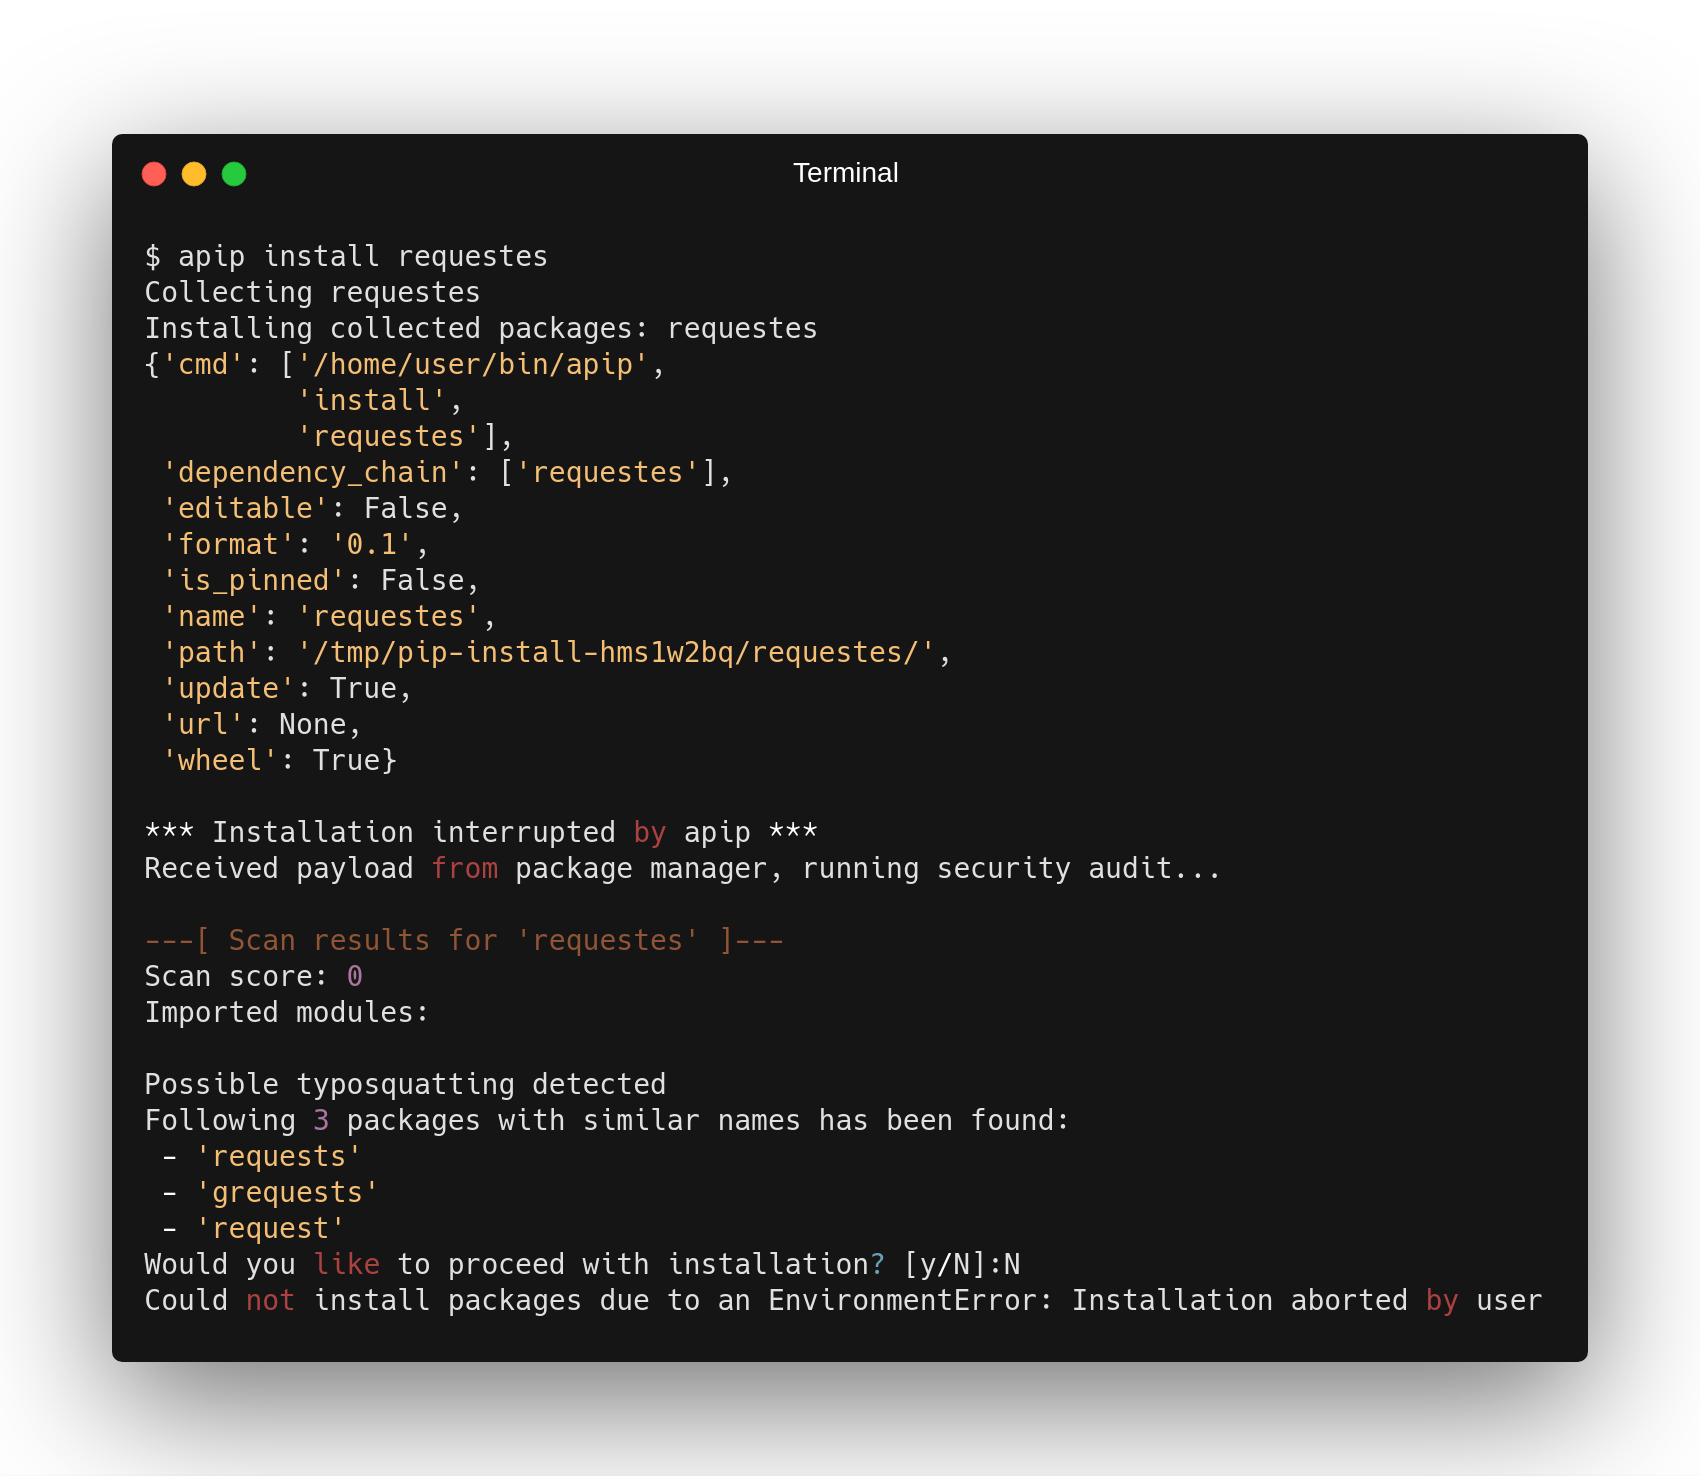
Identify hardcoded secrets in static structured text

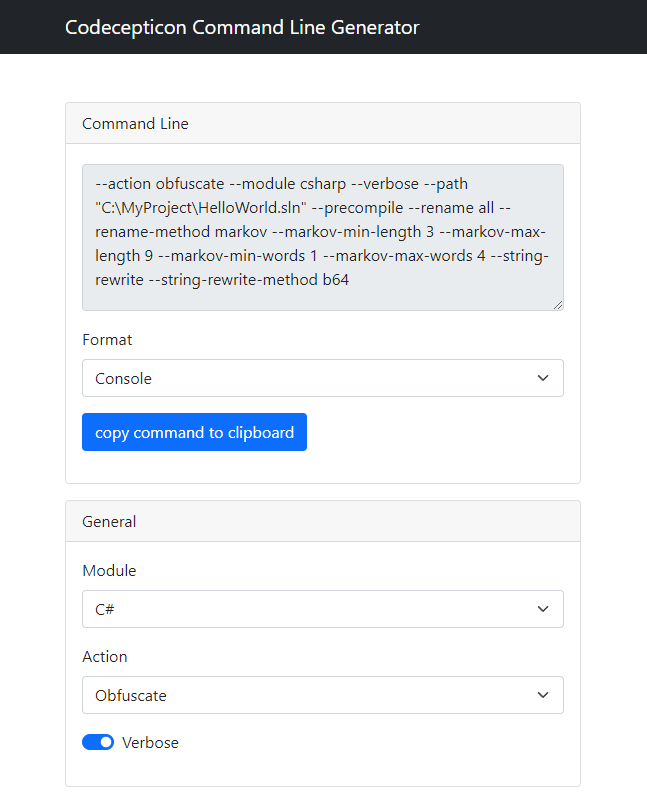
.NET/PowerShell/VBA Offensive Security Obfuscator

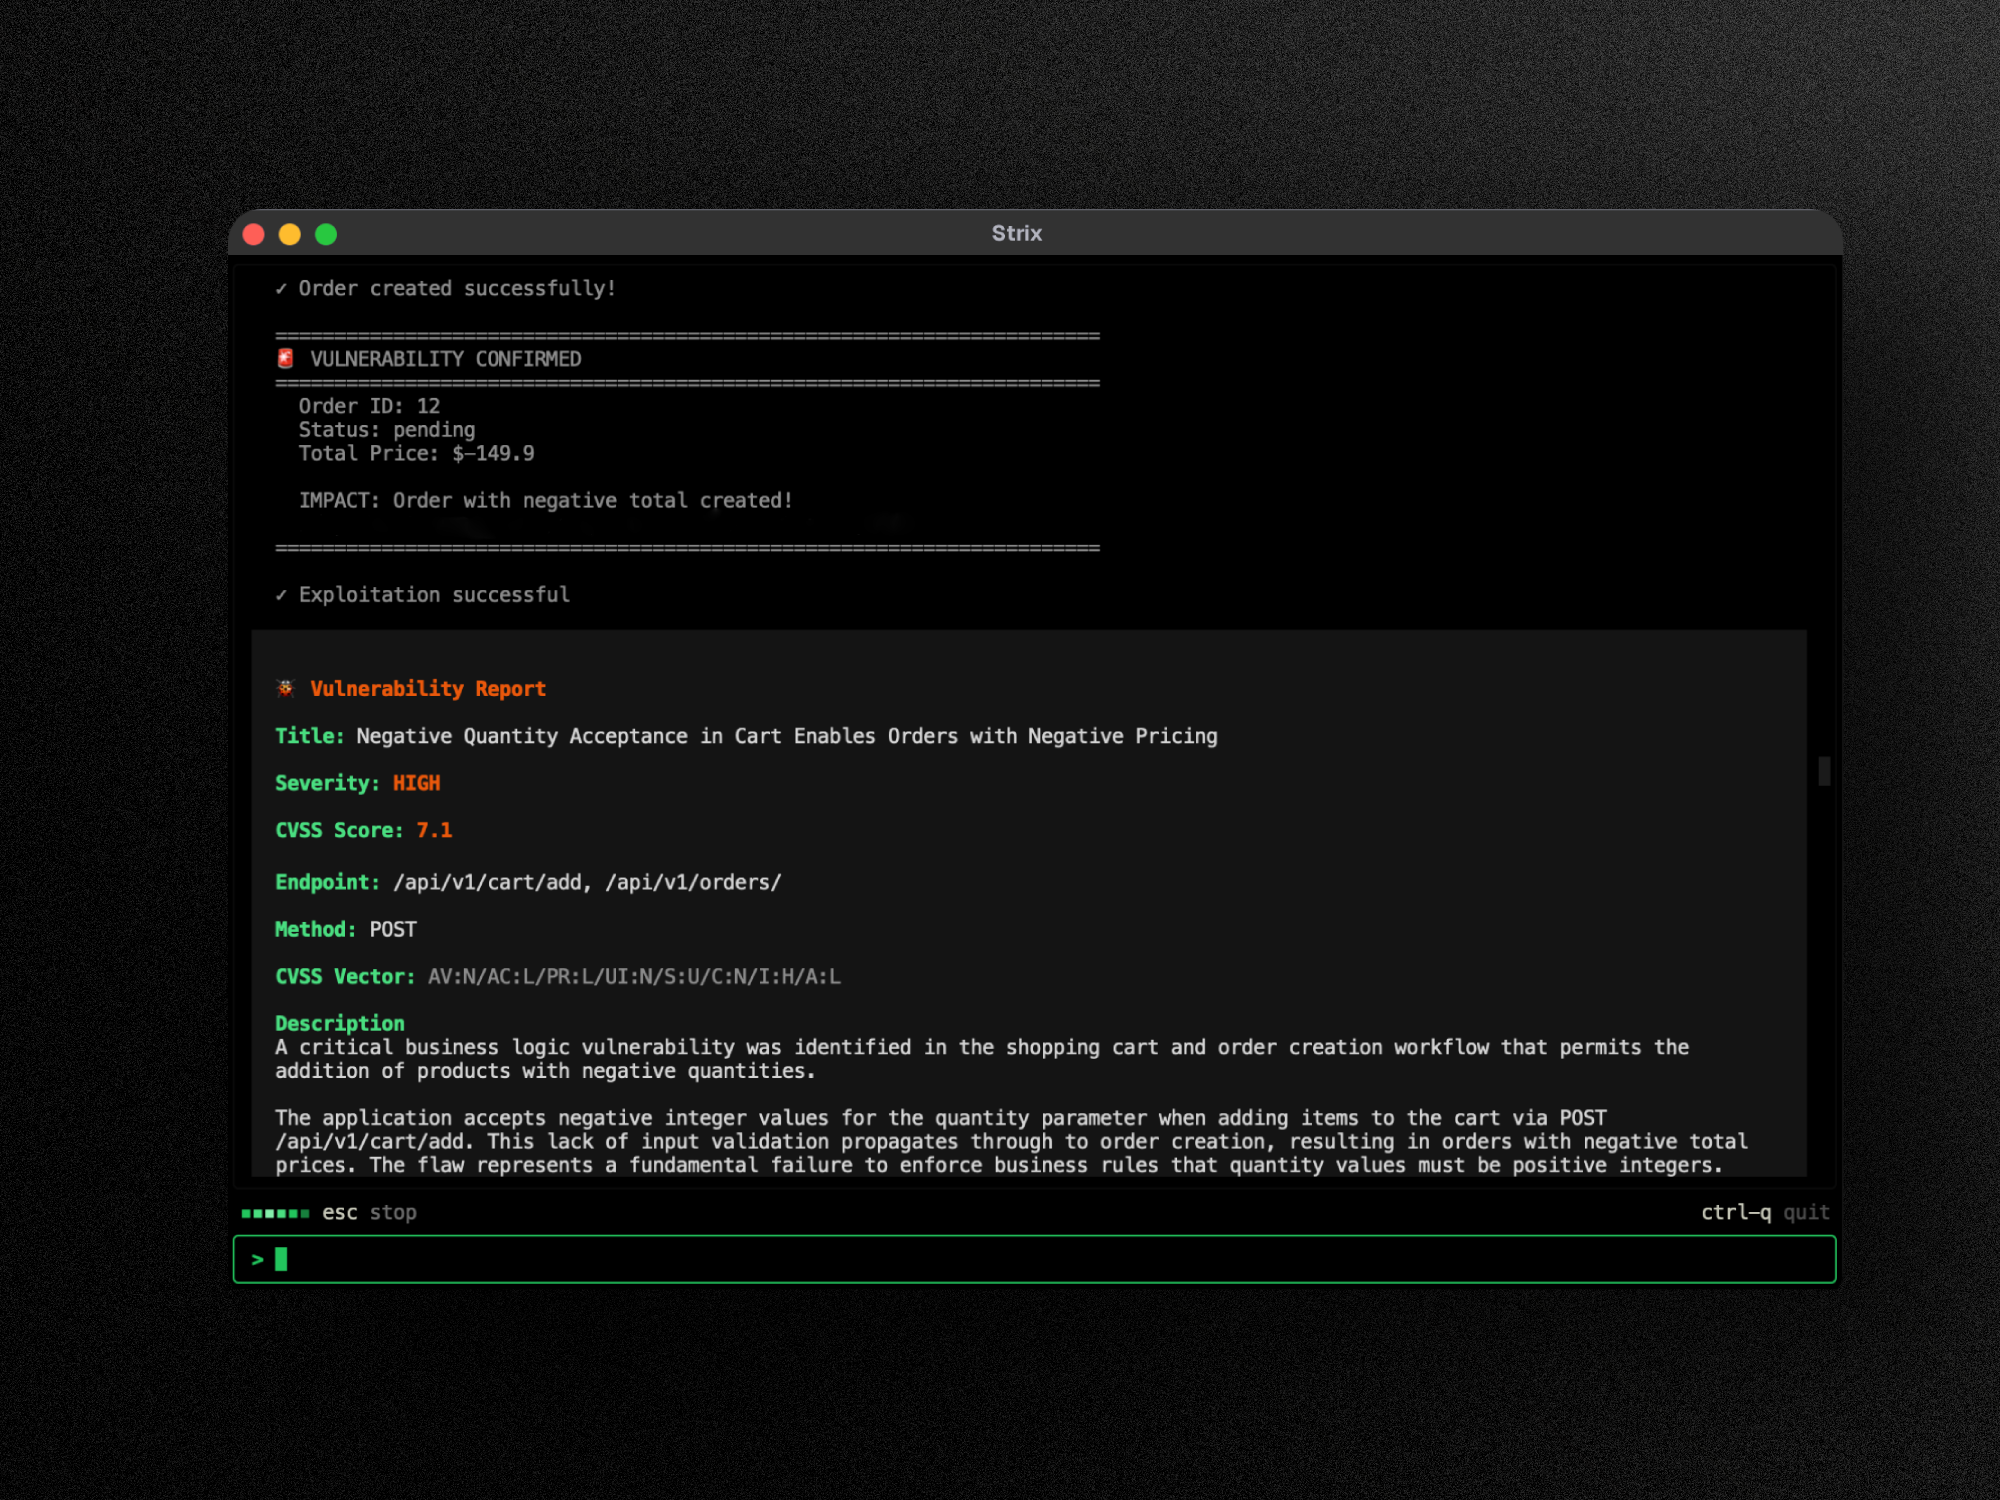
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security

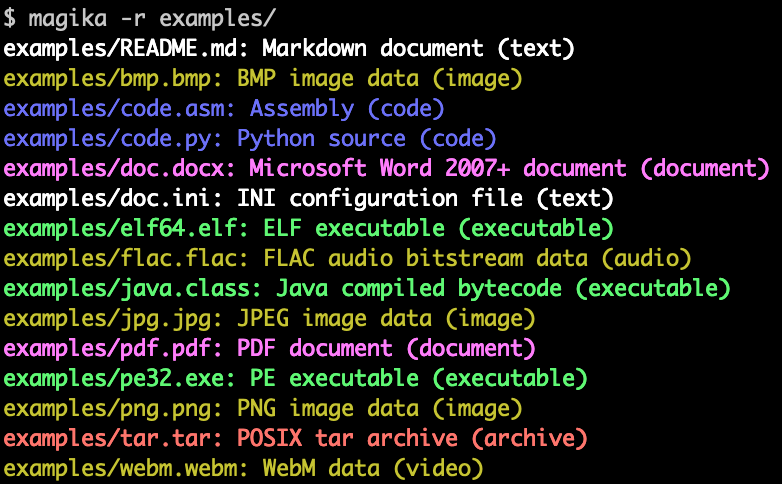
Fast and accurate AI powered file content types detection

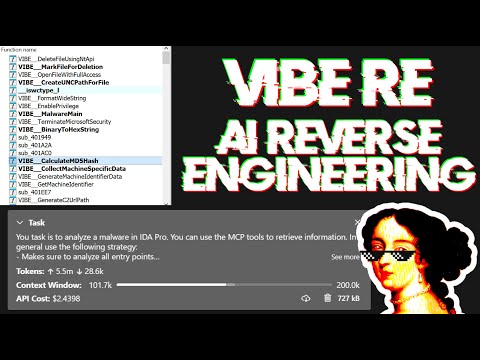
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.

Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…

Bandit is a tool designed to find common security issues in Python code.


An extensible multilanguage static code analyzer.

Prevents you from committing secrets and credentials into git repositories

Server-Side Template Injection and Code Injection Detection and Exploitation Tool