

chainoffools
 kudelskisecurity/chainoffools
Proof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
code-analysiscryptographyexploitation+2
335
kudelskisecurity/chainoffoolsProof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
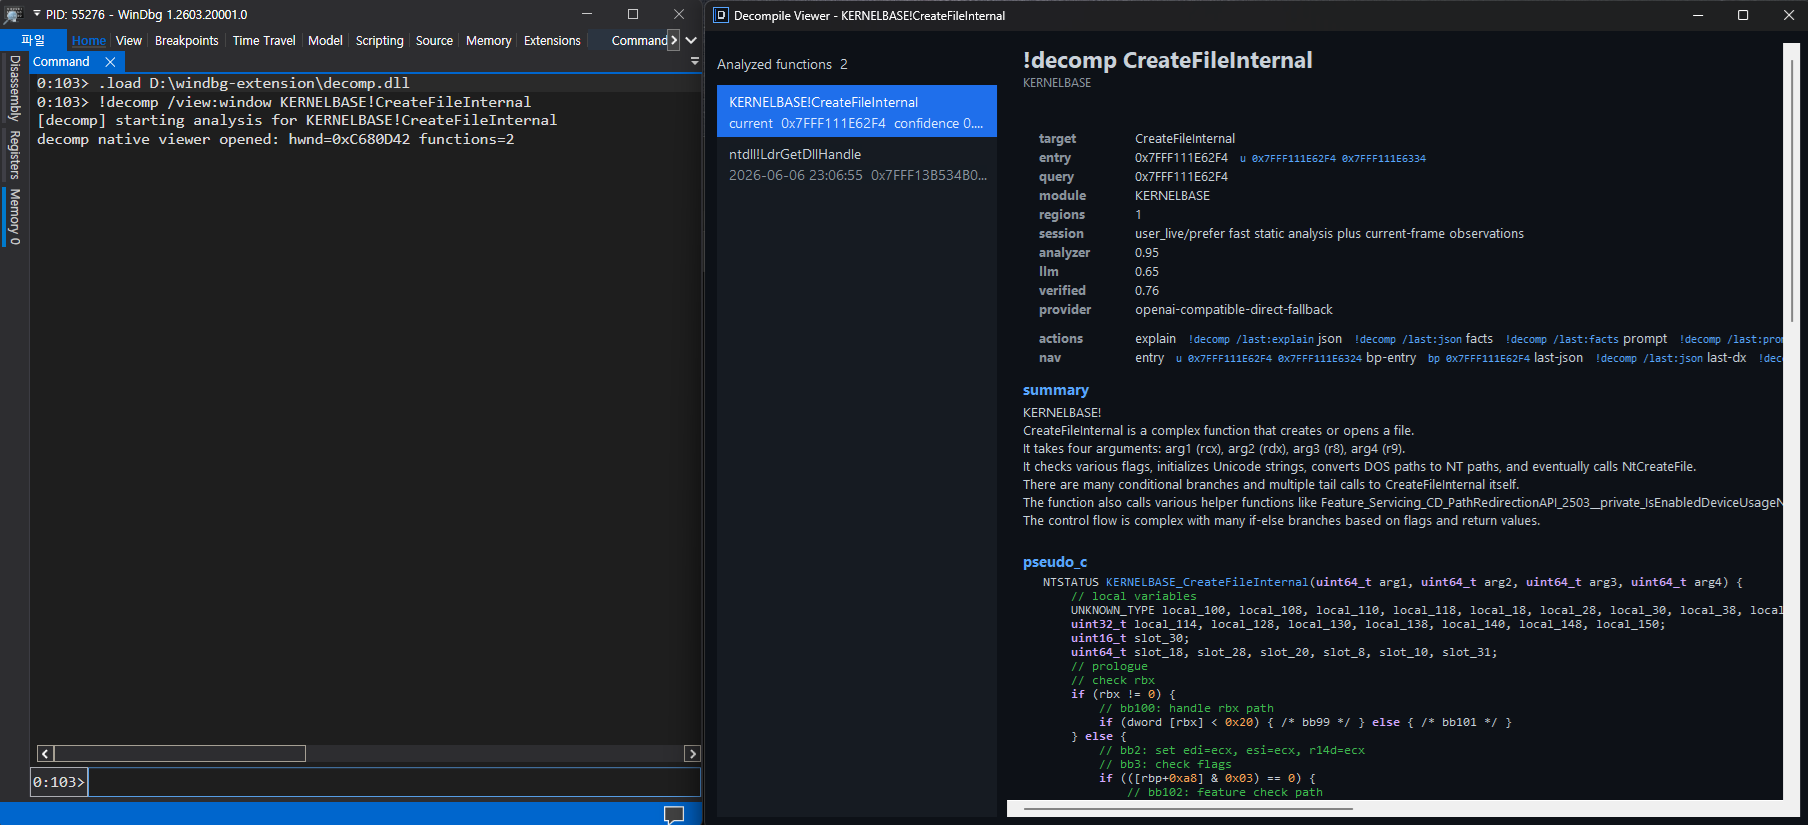 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 hackinglz/cve-2025-27237
CVE 2025 27237 Zabbix LPE proof of concept.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 fr4nkxixi/cve-2021-26871_poc
Proof-of-concept exploit for CVE-2021-26871, a type confusion vulnerability in Windows WalletService's PROPVARIANT handling, enabling local privilege…
 kai6u/tribell_edge_sandbox_escape
Tribell Edge Sandbox Escape - PoCs of Edge's legacy vulnerabilities BadgeUpdateManager / TileFlyoutUpdateManager / ToastNotificationManager to…
 iiictech/-cve-2020-0601-ecc---exploit
CurveBall (CVE-2020-0601) - PoC CVE-2020-0601, or commonly referred to as CurveBall, is a vulnerability in which the signature of certificates using…
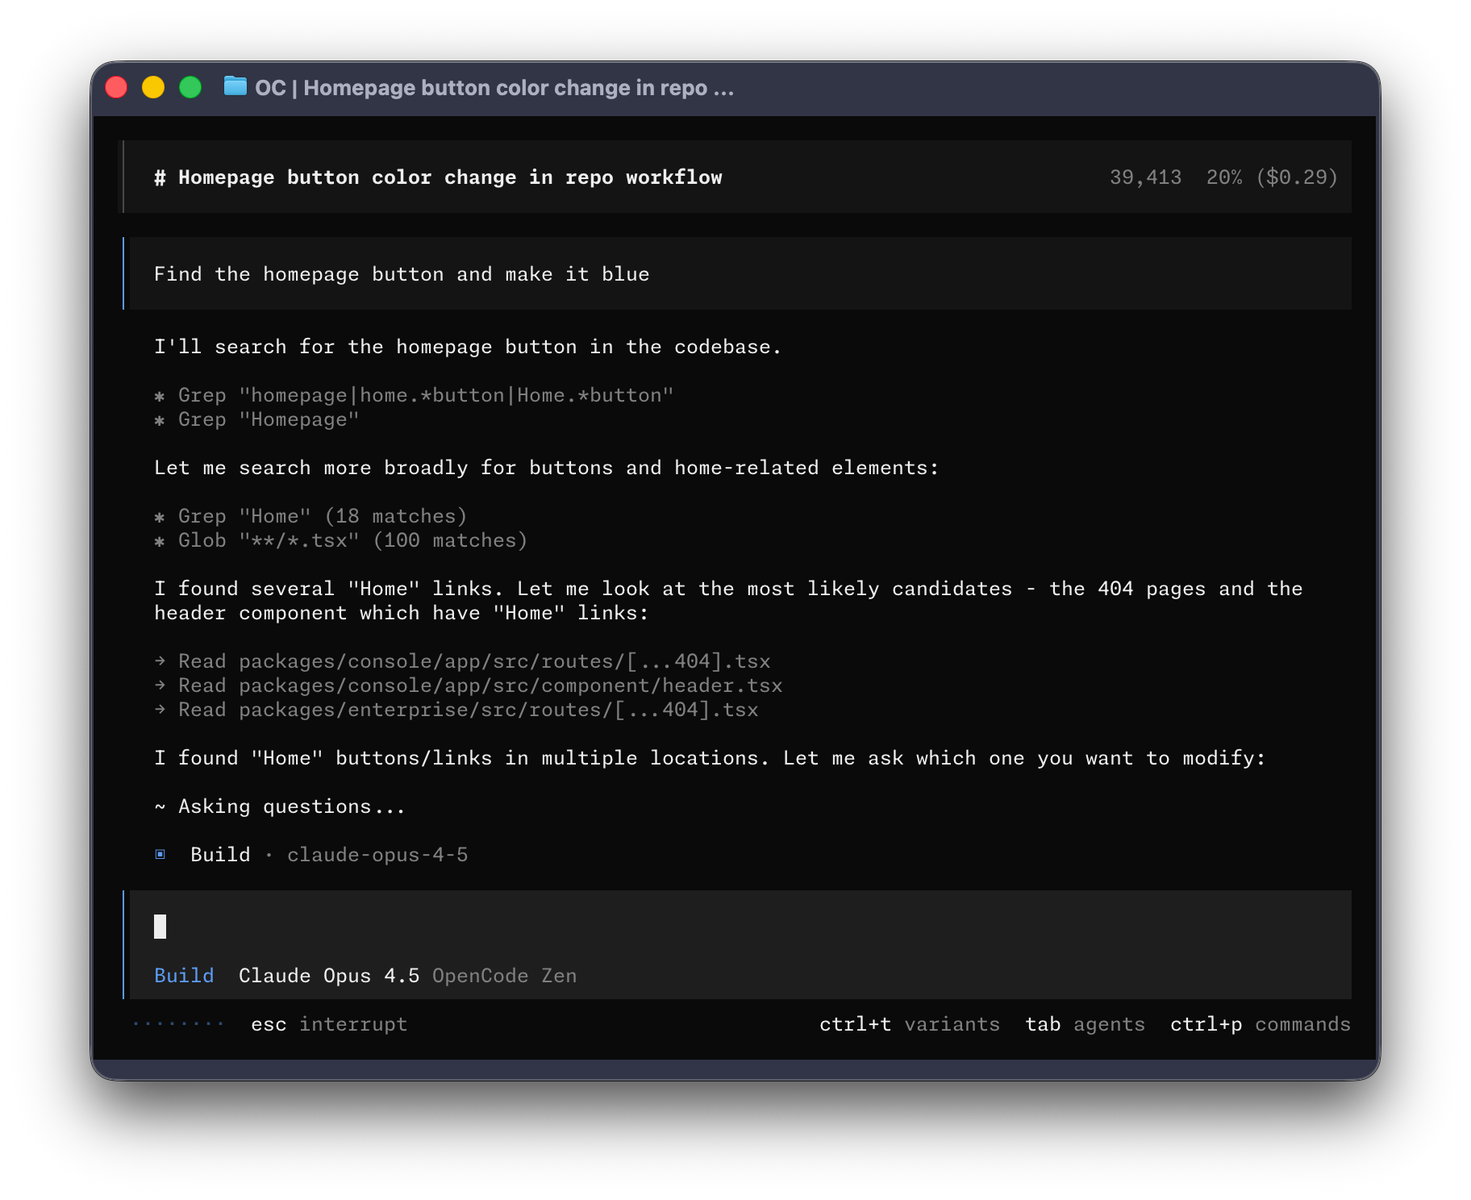 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 webr0ck/poc-cve-2018-1273
Proof-of-concept exploit for CVE-2018-1273, a Spring Data Commons property binder vulnerability leading to remote code execution via crafted HTTP…
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 geraldoalcantara/cve-2023-50071
Multiple SQL injection vulnerabilities in /customer_support/ajax.php?action=save_department in Customer Support System 1.0 allow authenticated…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 0xmrma/cve-2026-14361
Consul Template's writeToFile helper opened an operator-supplied destination directly and followed linked path components, allowing rendered output…
 x-defender/cve-2023-29007_win-version
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation on Windows systems for…
 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall