
gmh5225
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
ai-assisted-reversingbinary-analysisbinary-exploitation+4
gmh5225/gmh5225LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
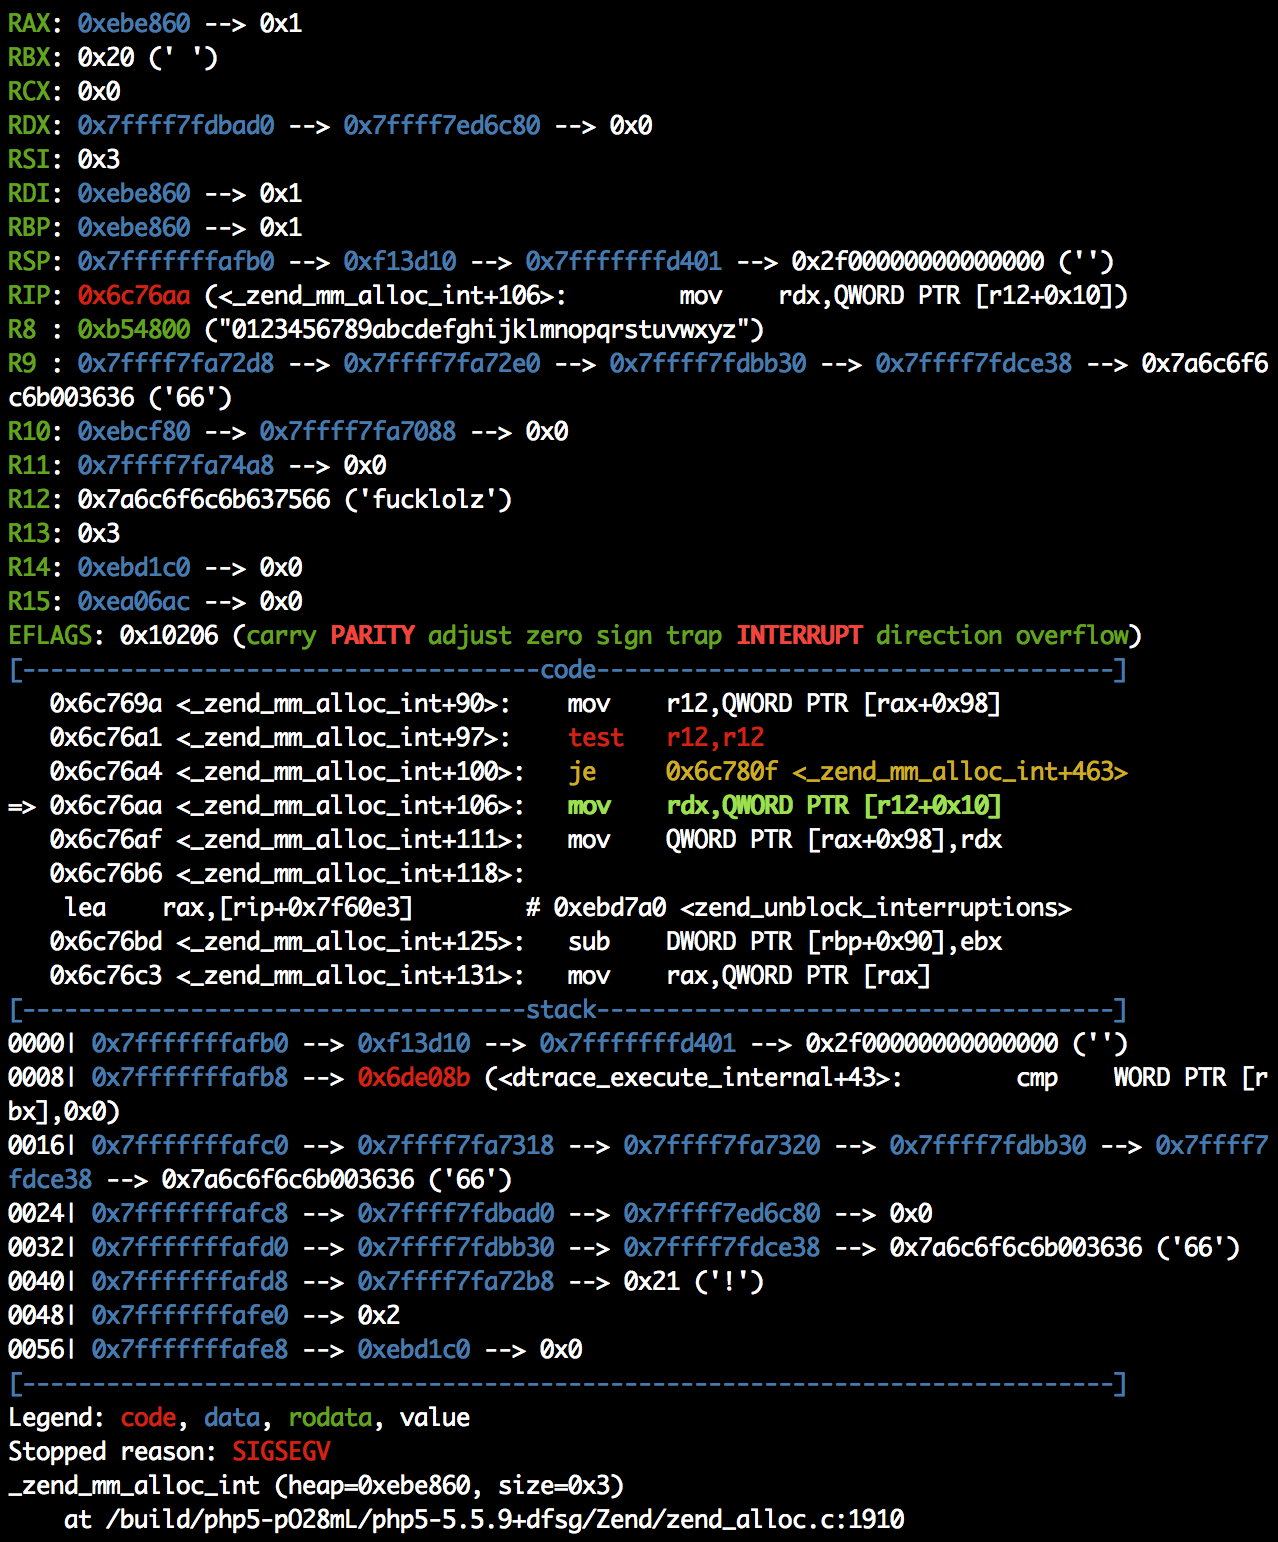
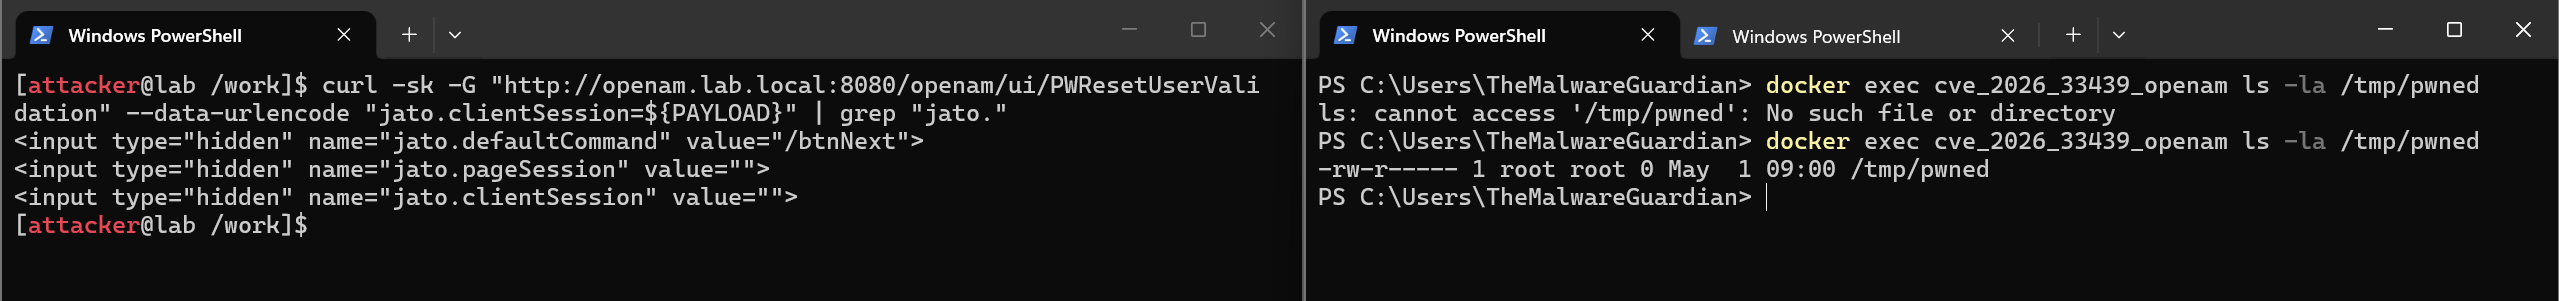 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
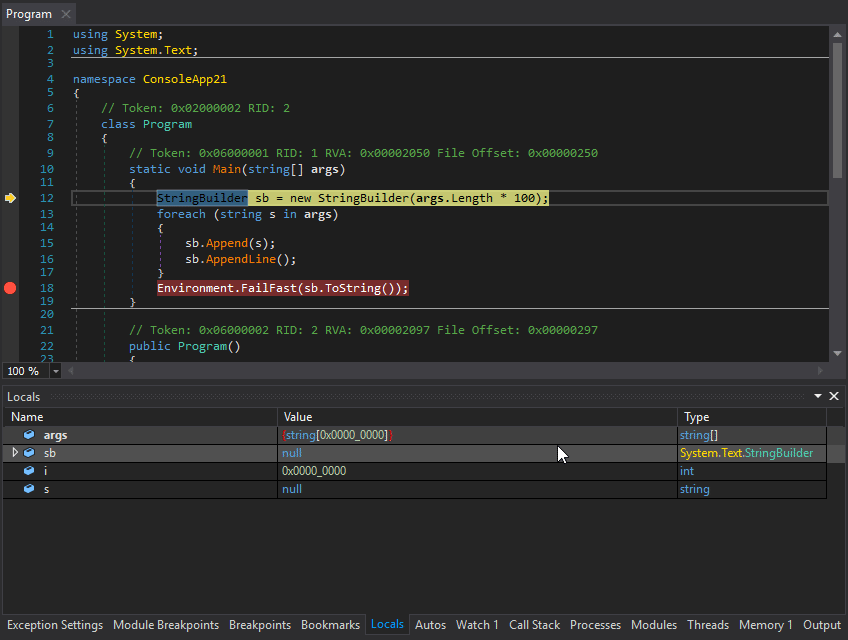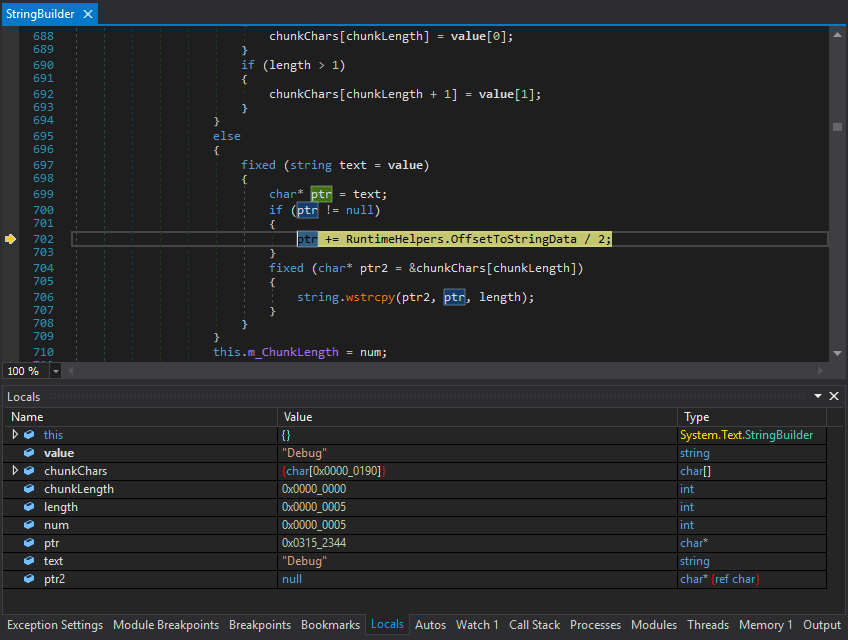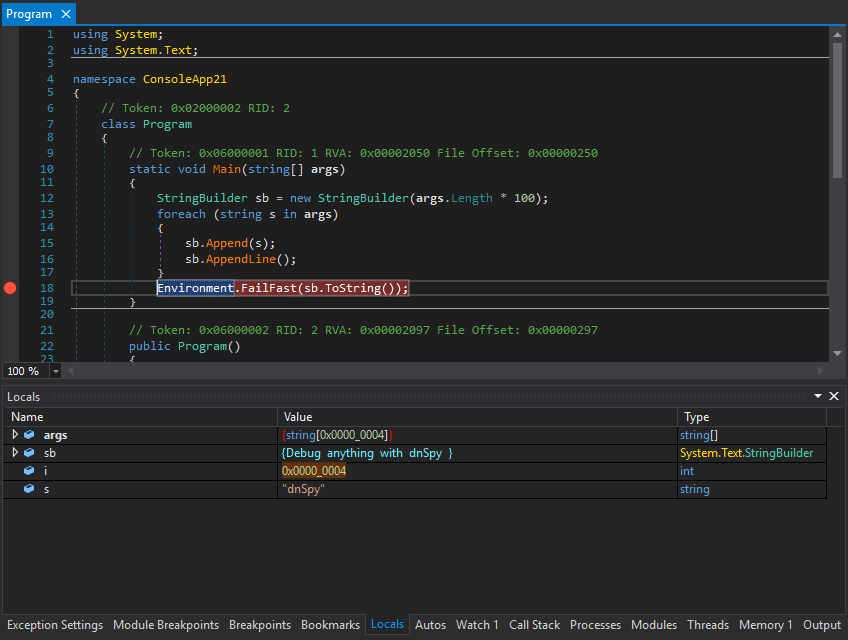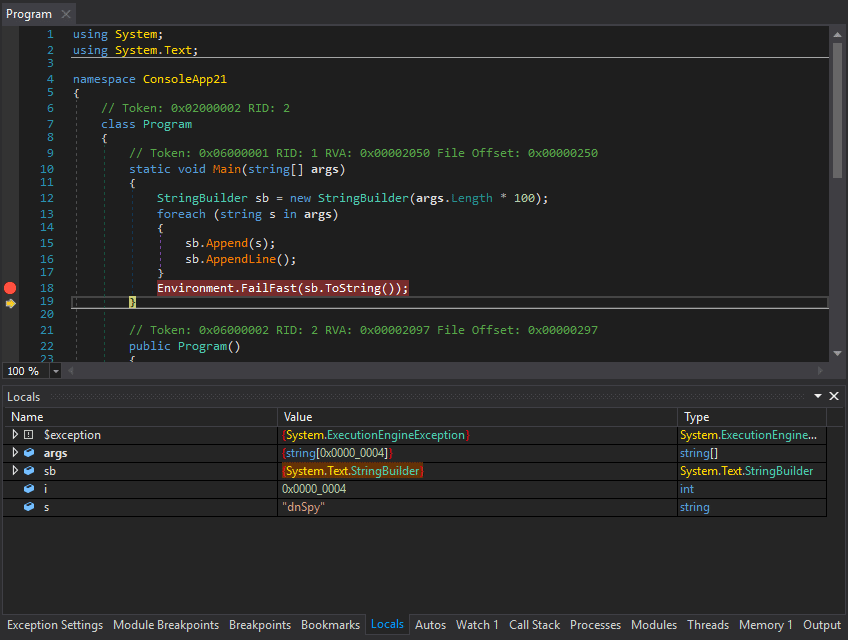 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 snowsnowsnows/eaglevm
Native code virtualizer for x64 binaries
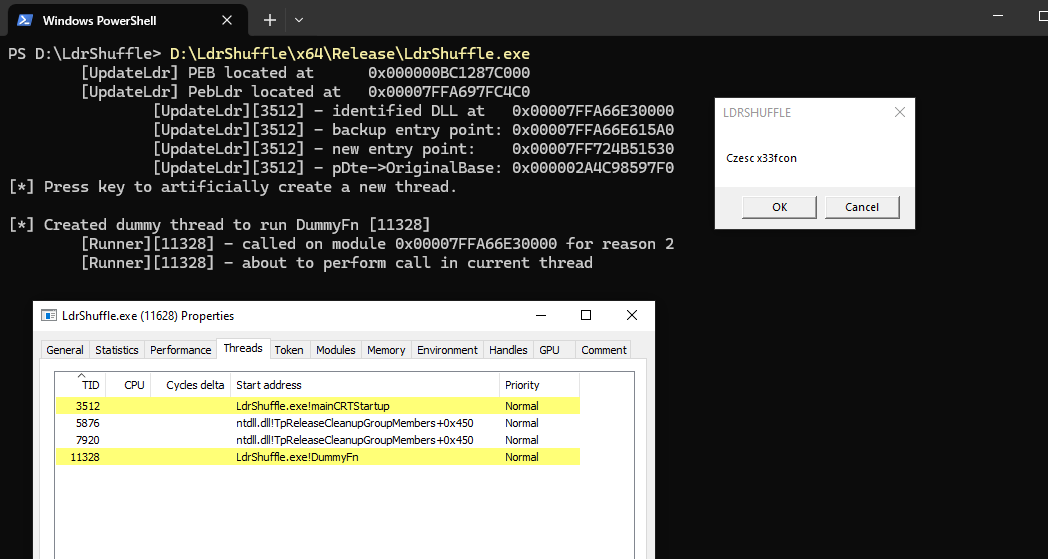 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 codewhitesec/unmarshalpwn
POC for CVE-2018-0824
 gamesarchive/cve-2025-48543
Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…
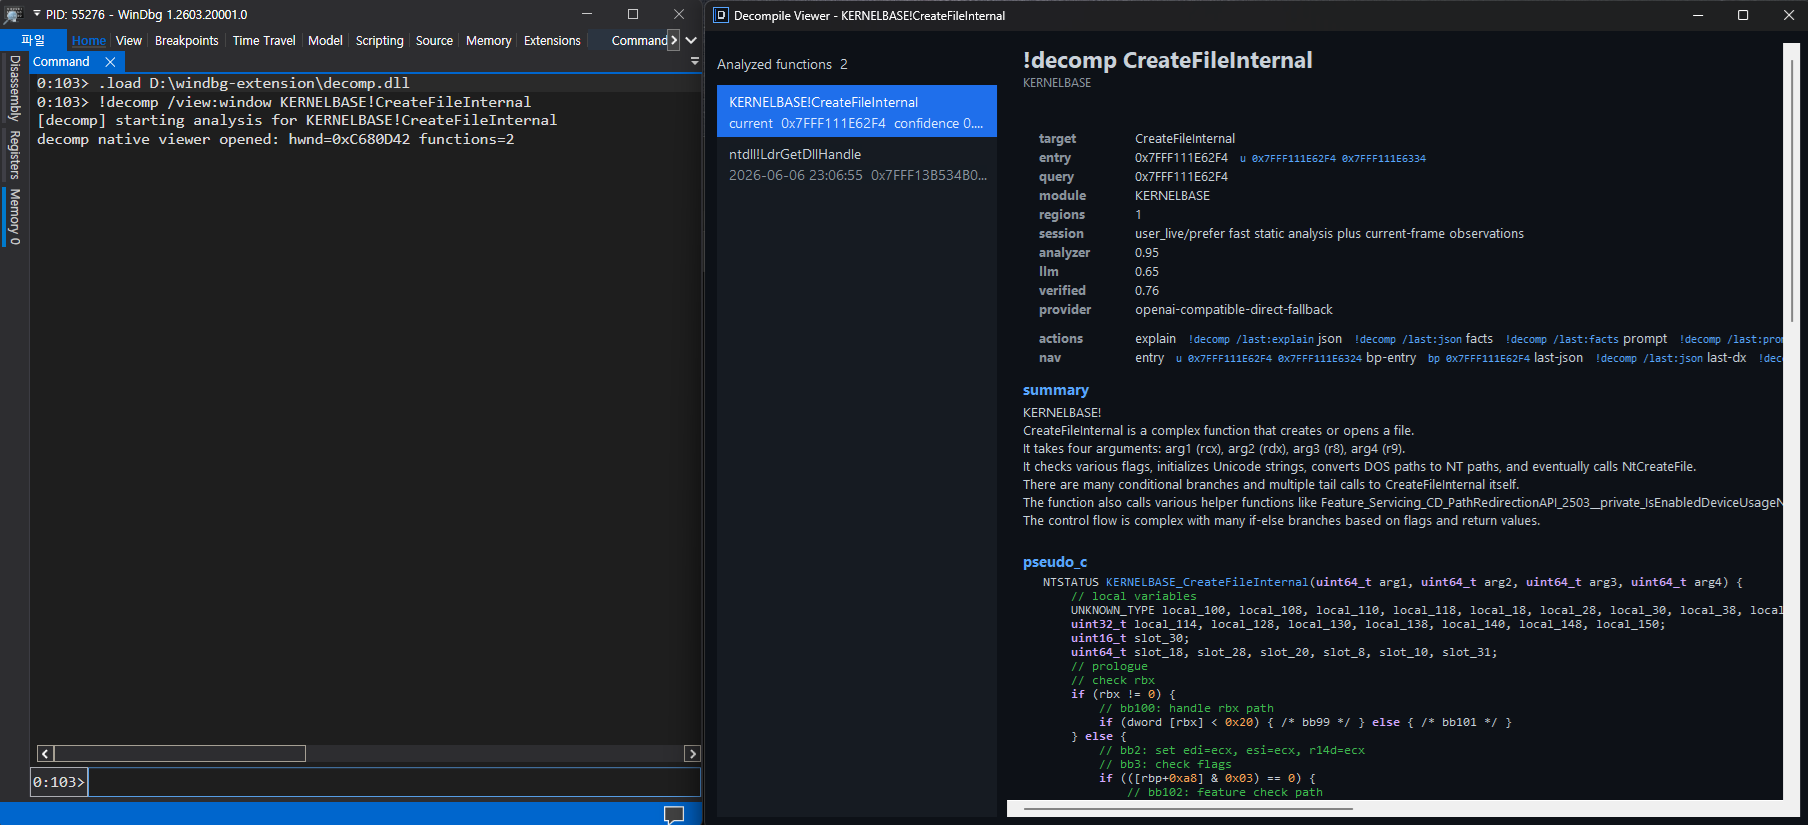 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 bi-zone/cve-2024-7965
This repository contains PoC for CVE-2024-7965. This is the vulnerability in the V8 that occurs only within ARM64.
 zhuowei/coretrustdemo
Proof-of-concept for CVE-2022-26766 on macOS 12.3.1
 rvzsec/cve-2023-30547
PoC Exploit for VM2 Sandbox Escape Vulnerability
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 haile01/perl_spreadsheet_excel_rce_poc
POC for RCE vulnerability in ParseExcel library, and ParseXLSX too, as a depending library
 ioncodes/curveball
PoC for CVE-2020-0601 - CryptoAPI exploit