

infer
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
code-analysisdevsecopsstatic-analysis+1
facebook/inferA static analyzer for Java, C, C++, and Objective-C
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
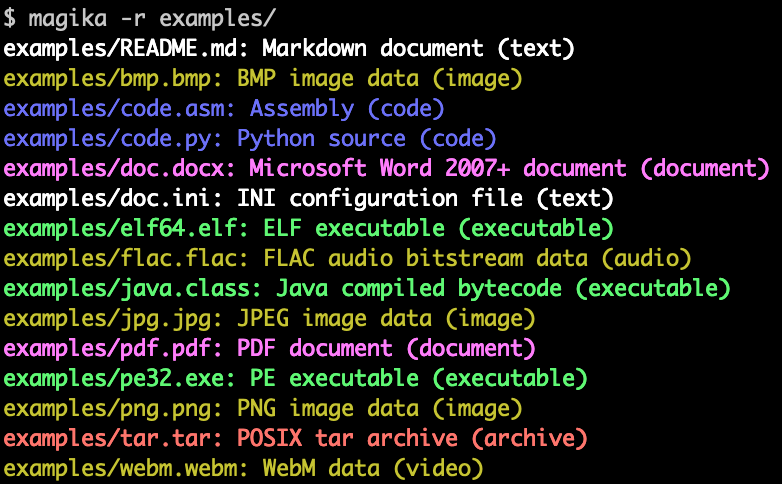 google/magika
Fast and accurate AI powered file content types detection
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 pyca/cryptography
cryptography is a package designed to expose cryptographic primitives and recipes to Python developers.
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 crytic/slither
Static Analyzer for Solidity and Vyper
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
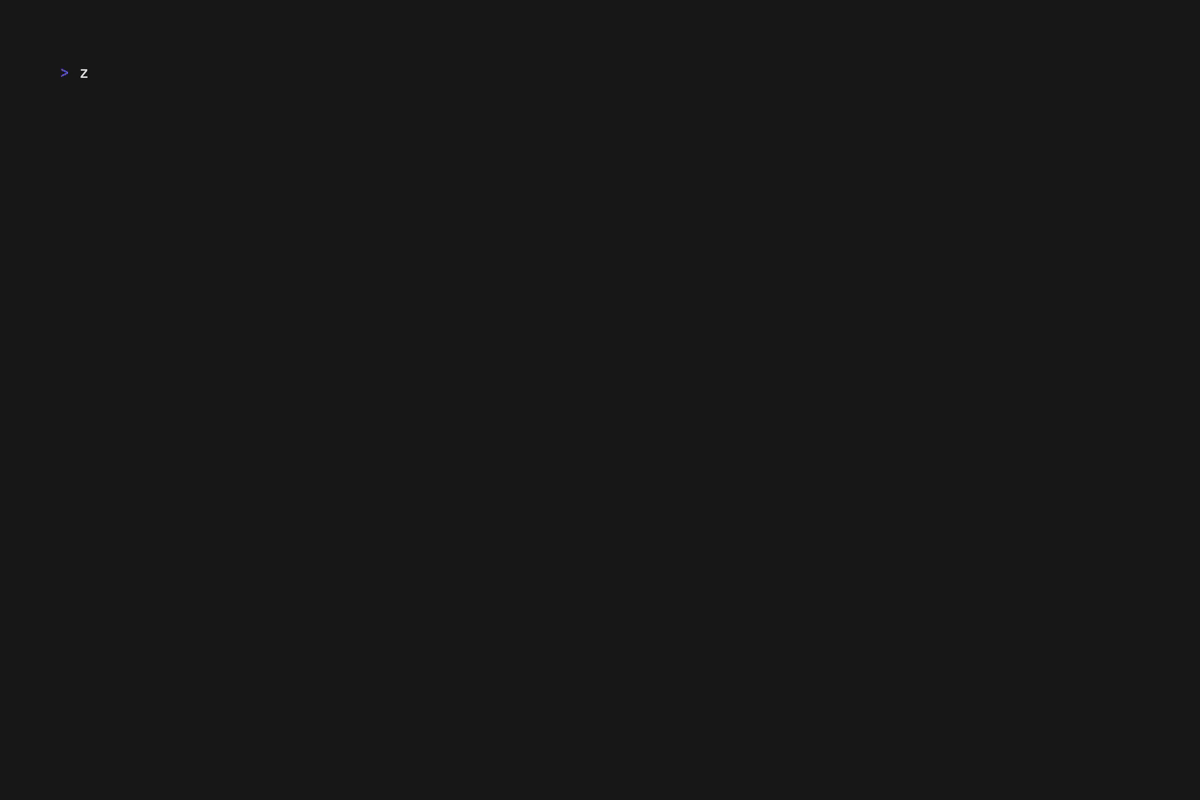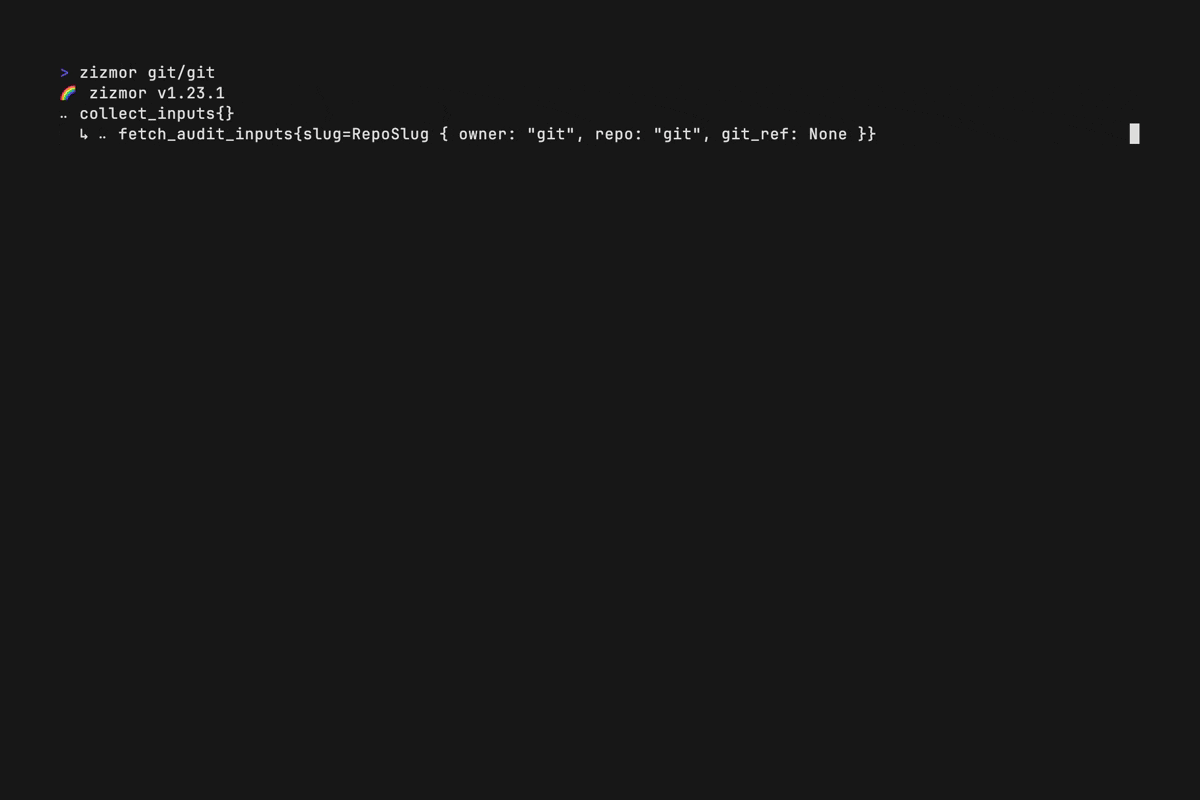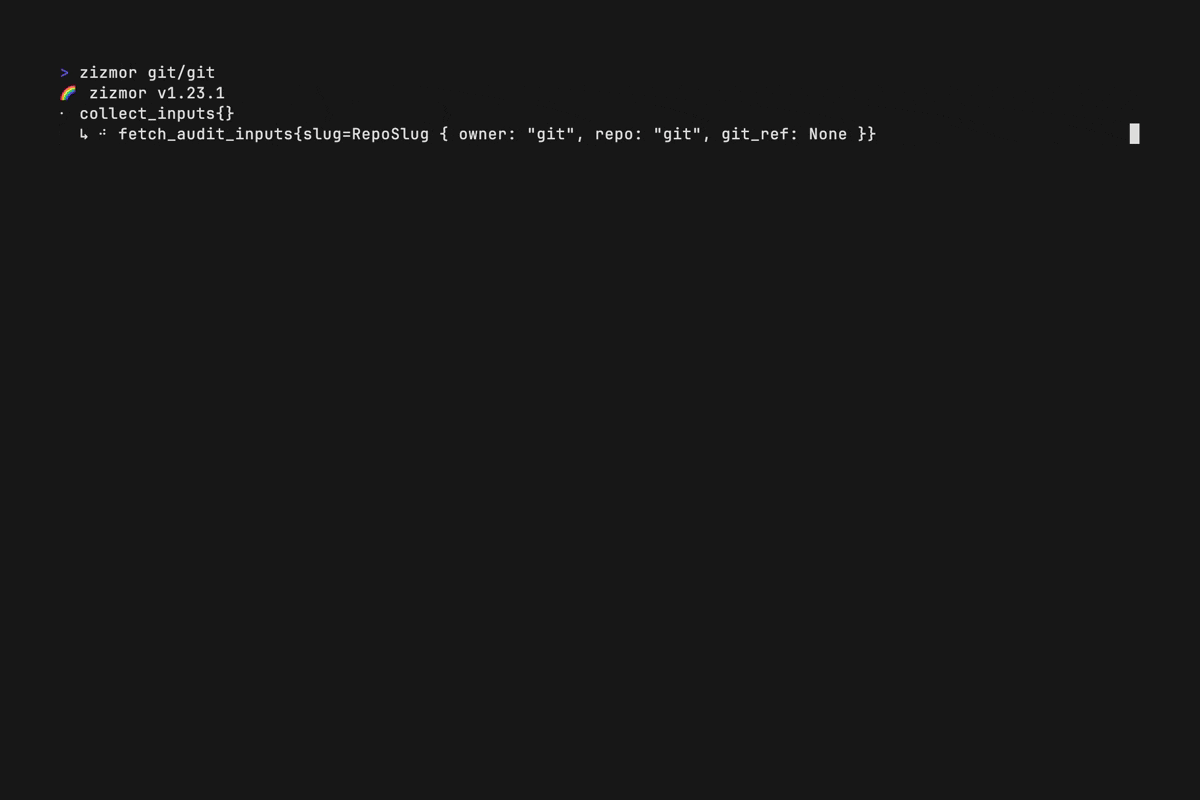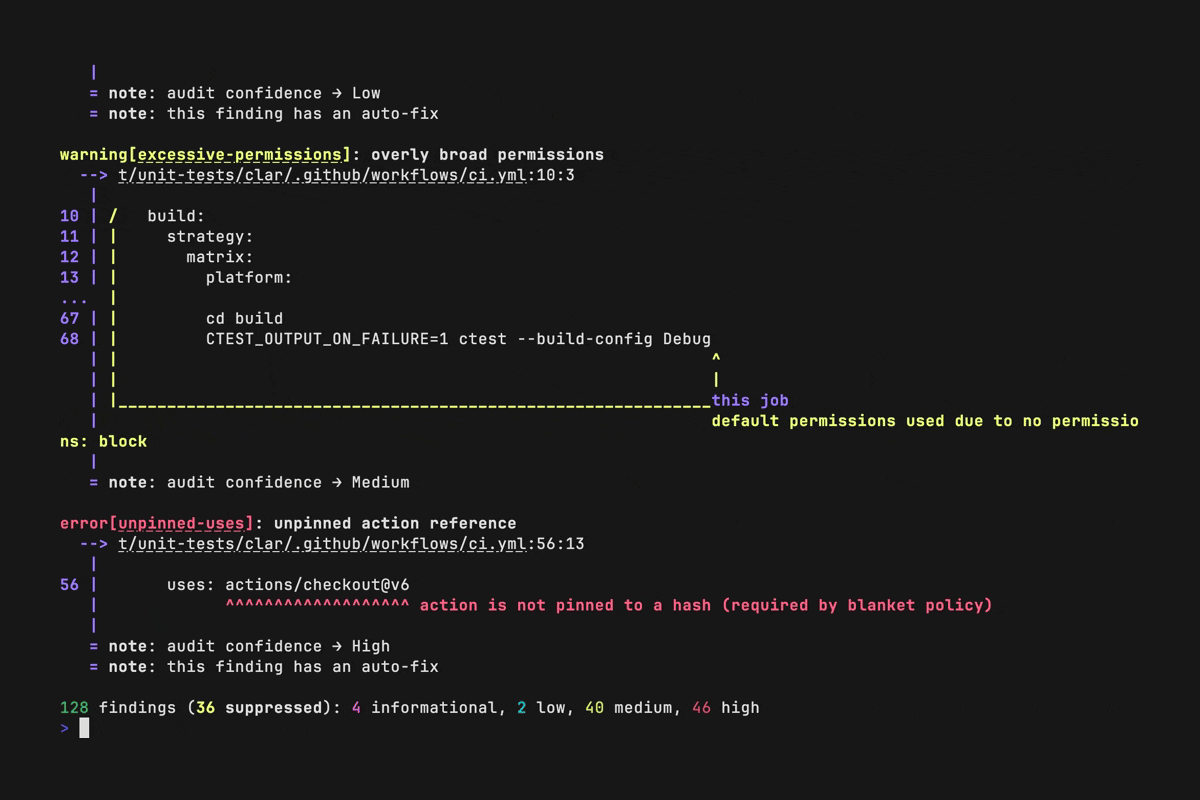 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…