

GitLeaks
 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
code-analysiscontainer-securitydevsecops+1
niclas-zone/ctr/gitleaksContainerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
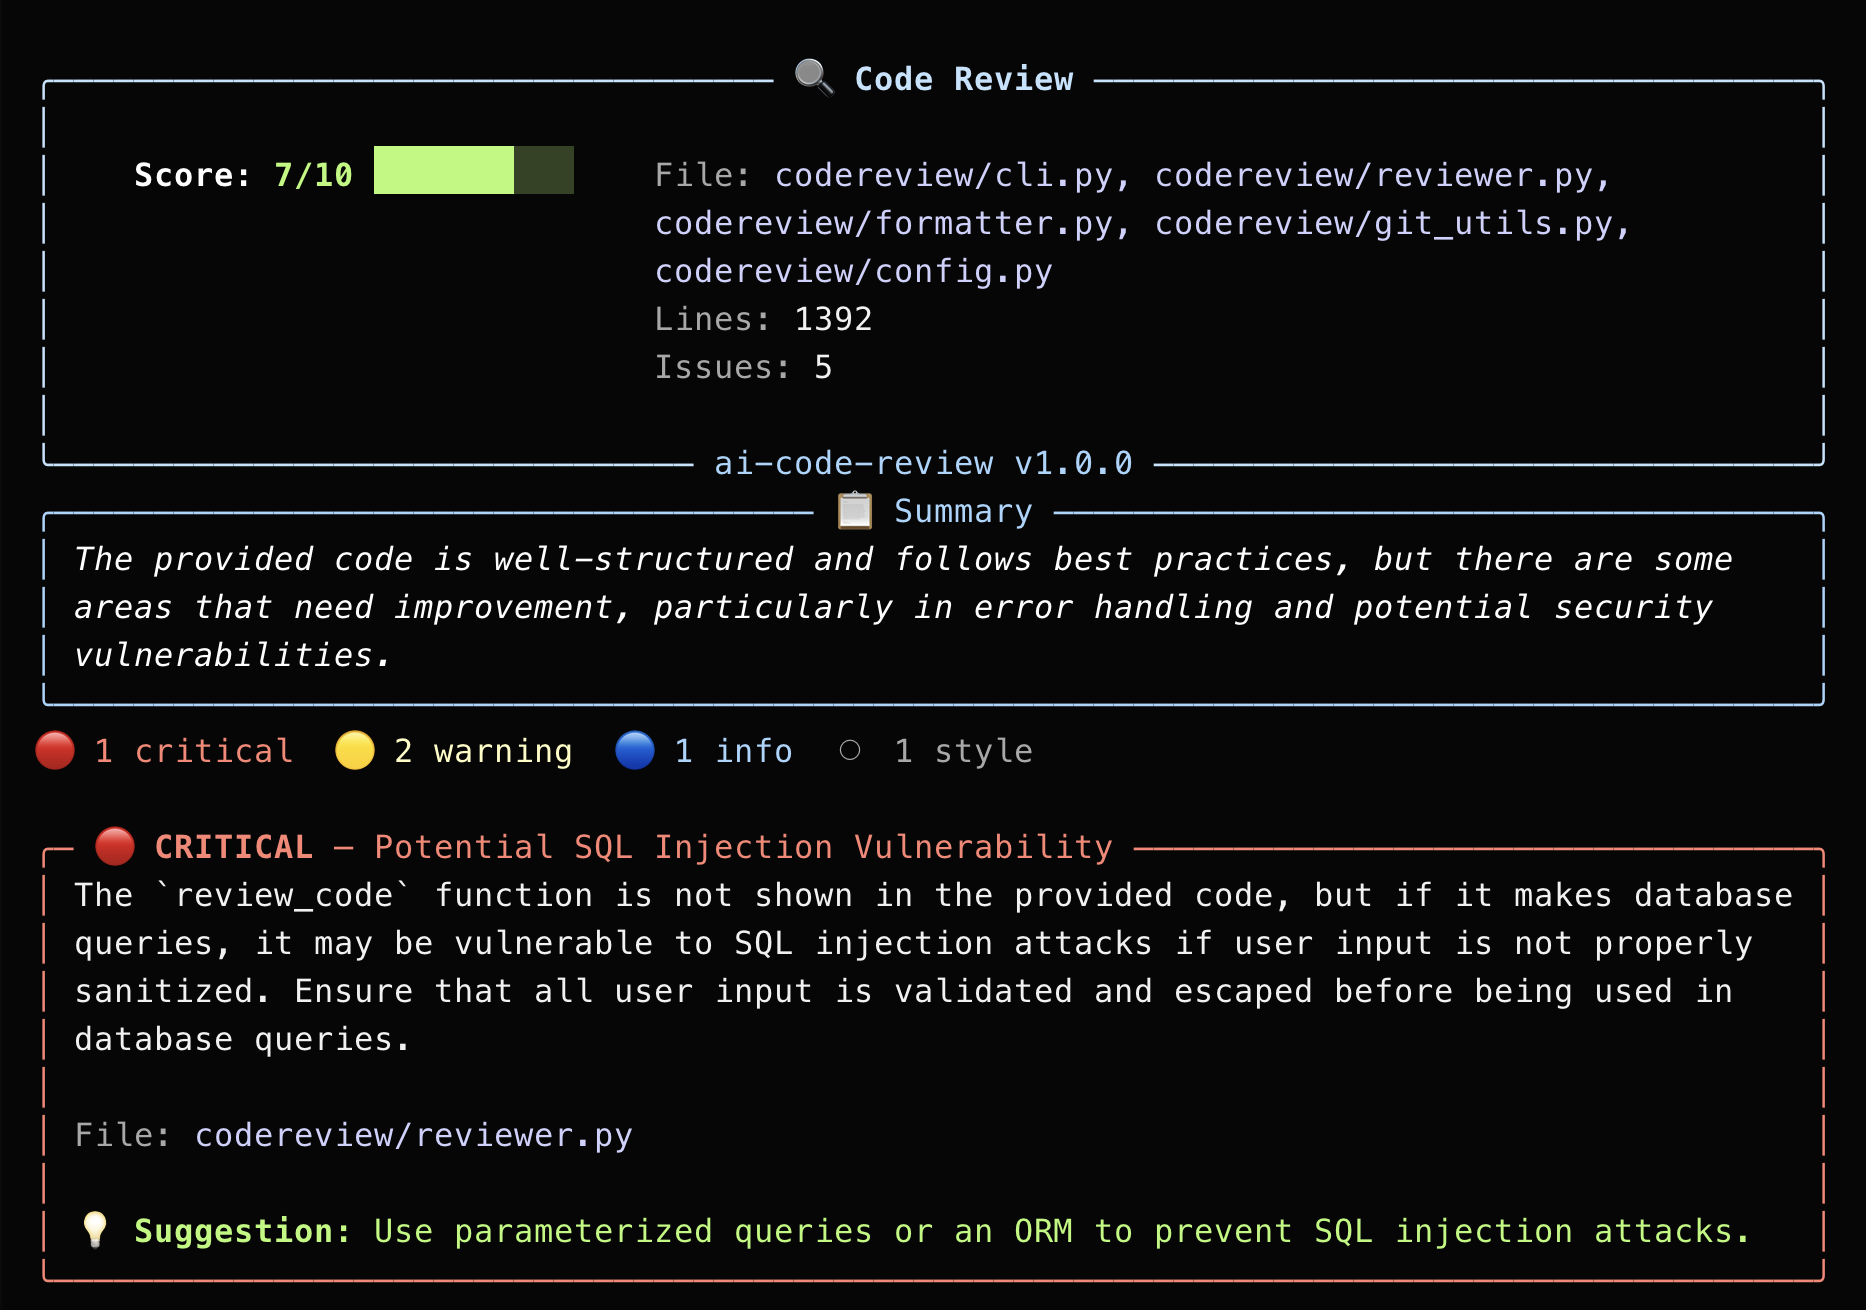
 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 niclas-zone/ci/gitleaks
CI component for Gitleaks SAST tool that scans git repositories for hardcoded secrets, API keys, and tokens with custom and remote configuration…
 mayank729/cve-2025-55182-scanner
🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
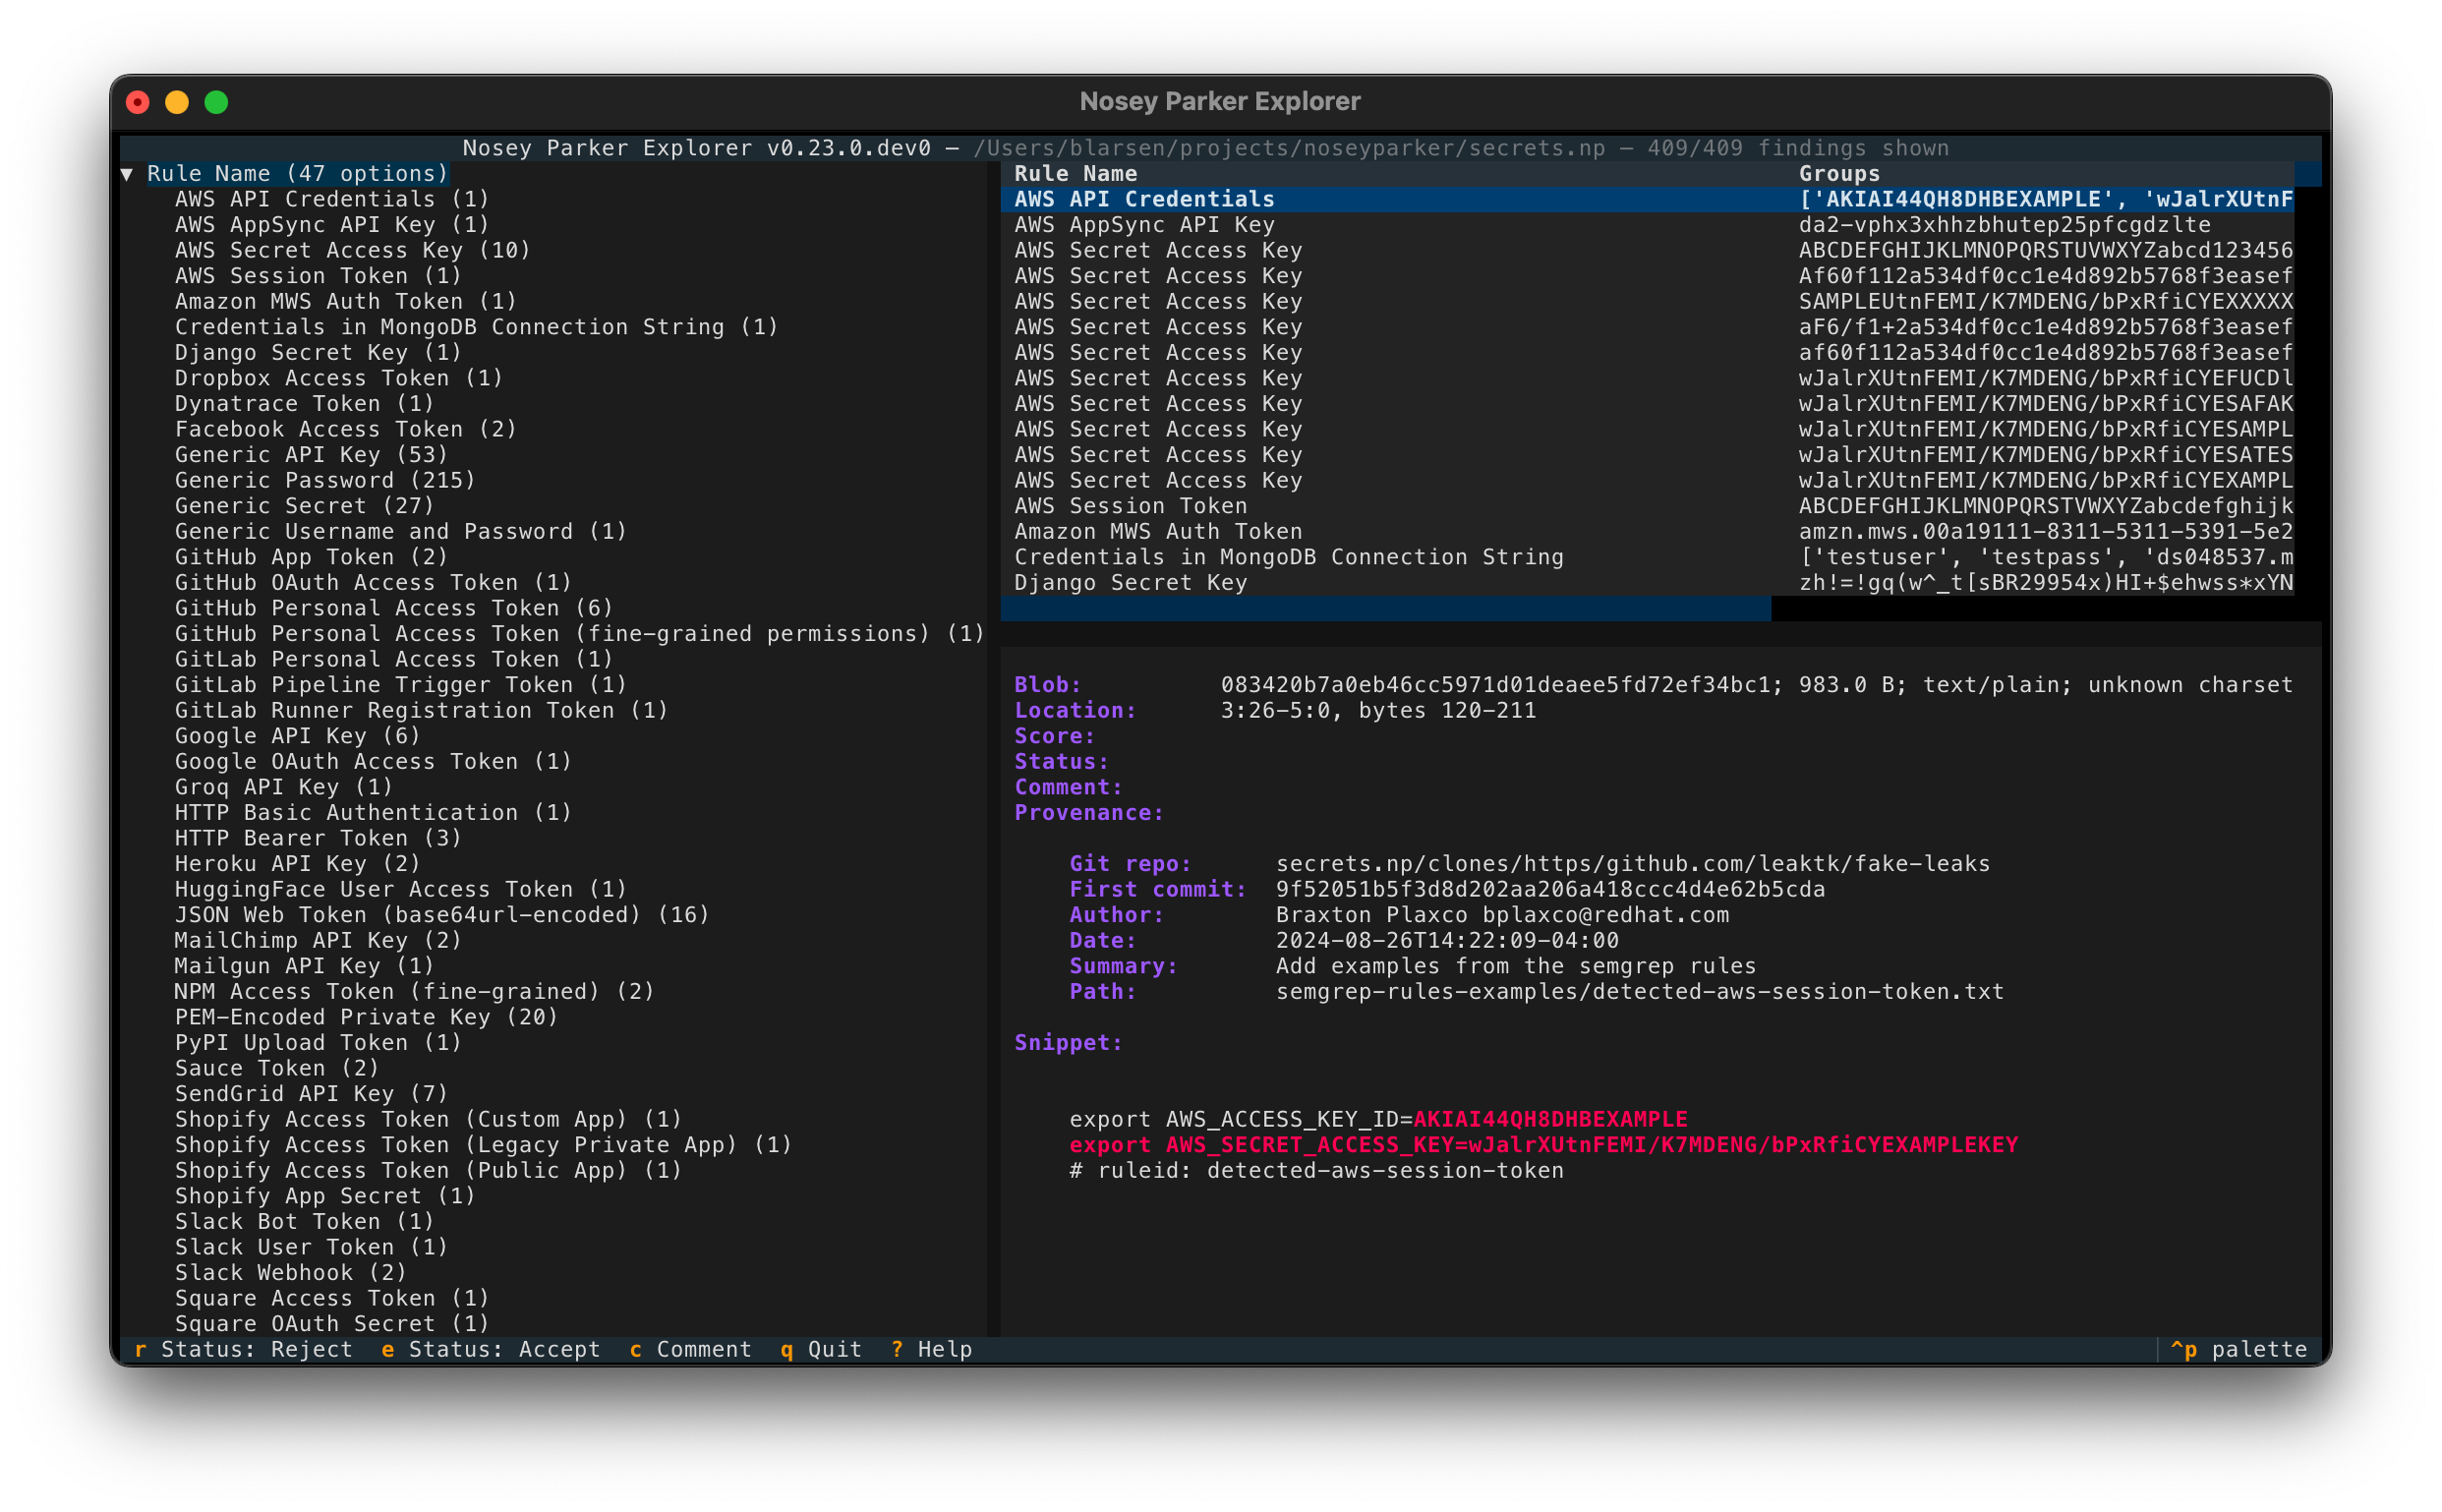 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
 soxoj/gitcolombo
🧬 Extract and analyze contributors info from git repos
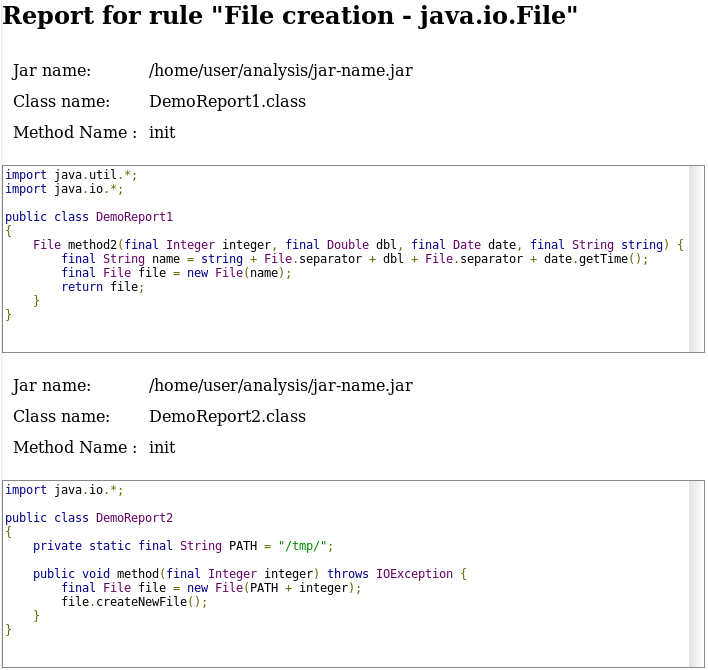 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances