

static-analysis
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
code-analysiscurated-resourcesdevsecops+5
14.8k
analysis-tools-dev/static-analysisCurated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 snyk/agent-scan
Security scanner for AI agents, MCP servers and agent skills.
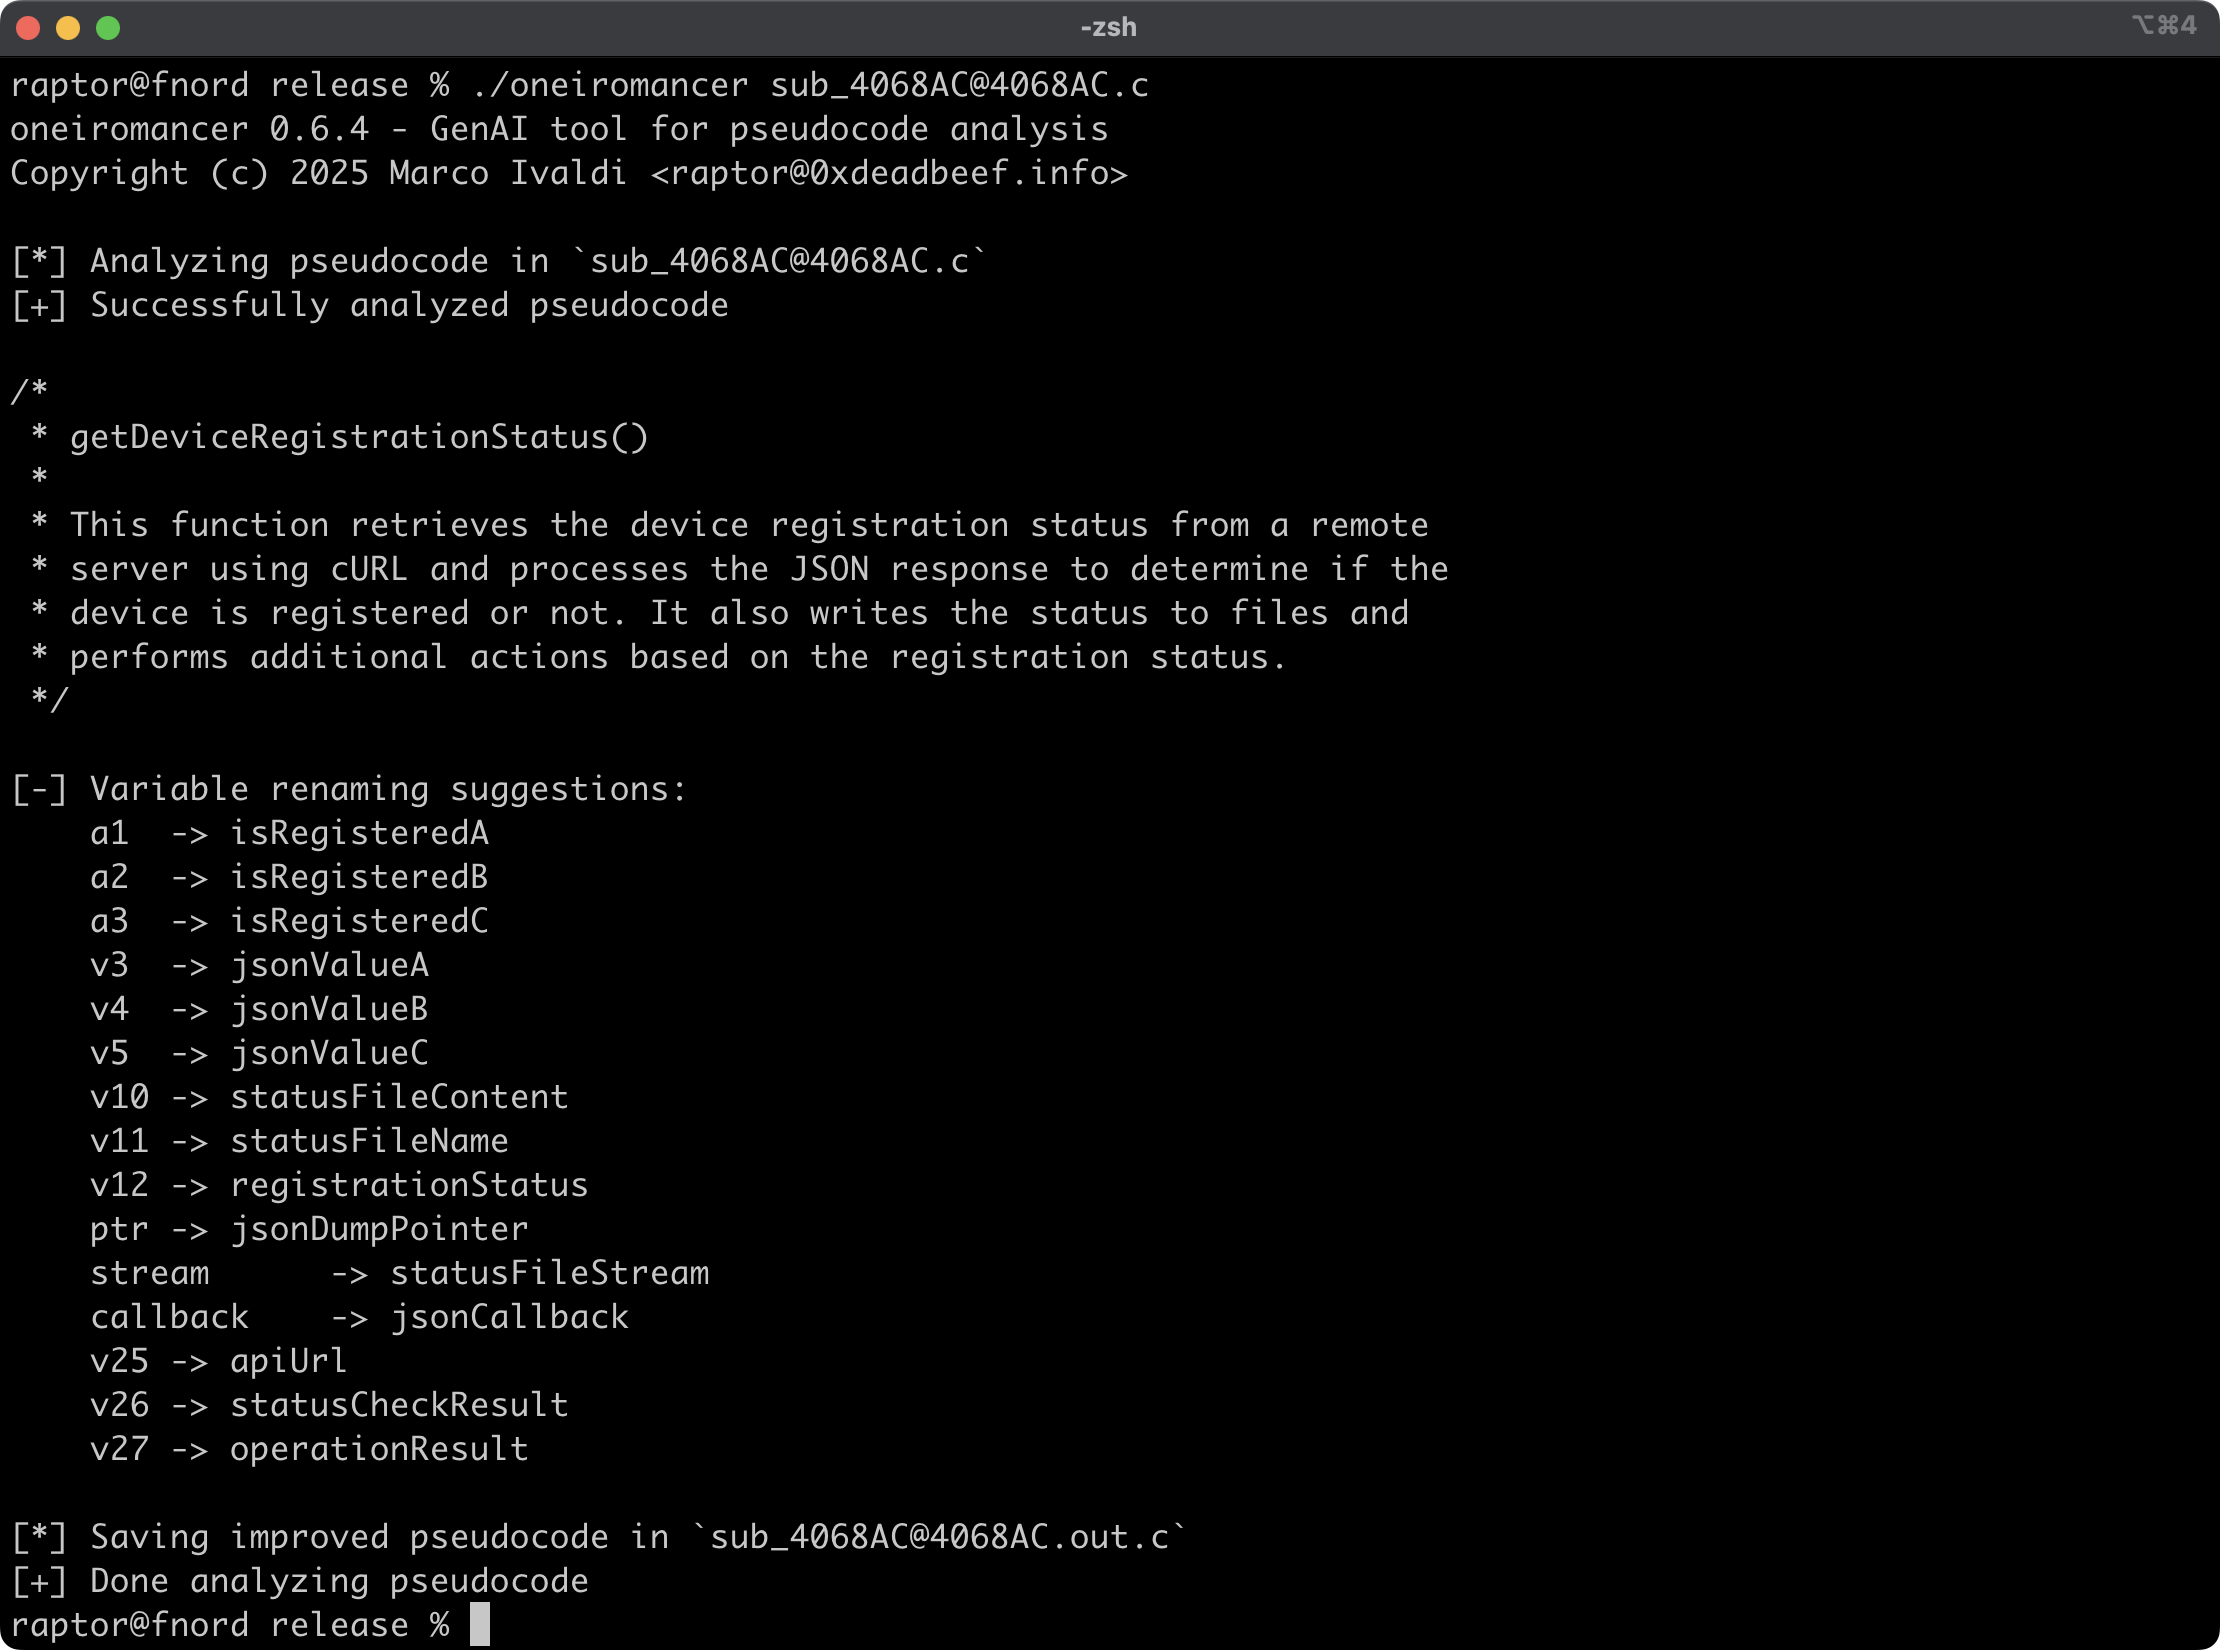 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 zydak/leetobfuscator
Obfuscates C/C++ through LLVM passes: string encryption, control-flow flattening, MBA rewriting, and anti-analysis to defeat reverse engineering.
 antonin-deniau/cave_miner
Search for code cave in all binaries
 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 theopaid/cve-2026-66730-infinite-loop-dos-in-facil.io-mime-parser
Security Advisory: Infinite Loop DoS in facil.io MIME Parser (Partial Boundary)
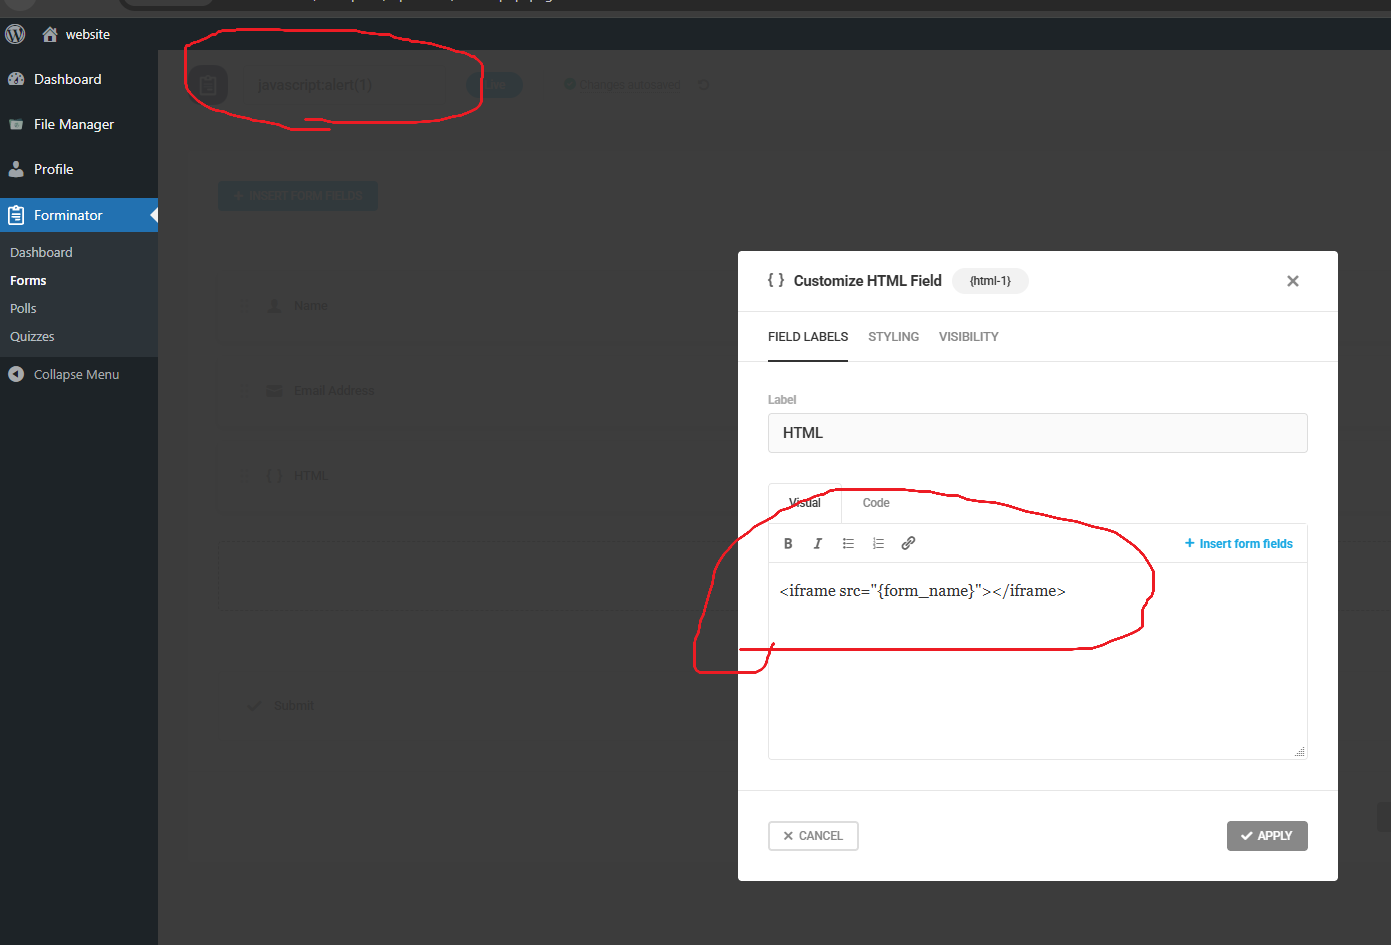 typedefabcd1234ntd/cve-2026-2002-poc
CVE-2026-2002 writeup and Proof-of-concept
 biitts/cve-2026-44789-n8n-prototypepollution-rce
CVE-2026-44789 — n8n <1.123.43 HTTP Request pagination prototype pollution to RCE (NODE_OPTIONS runner-spawn gadget). Lab + automated PoC, verified…
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 nova-hunting/nova-tracer
NOVA - Claude Code Protection System against prompt injection attacks