
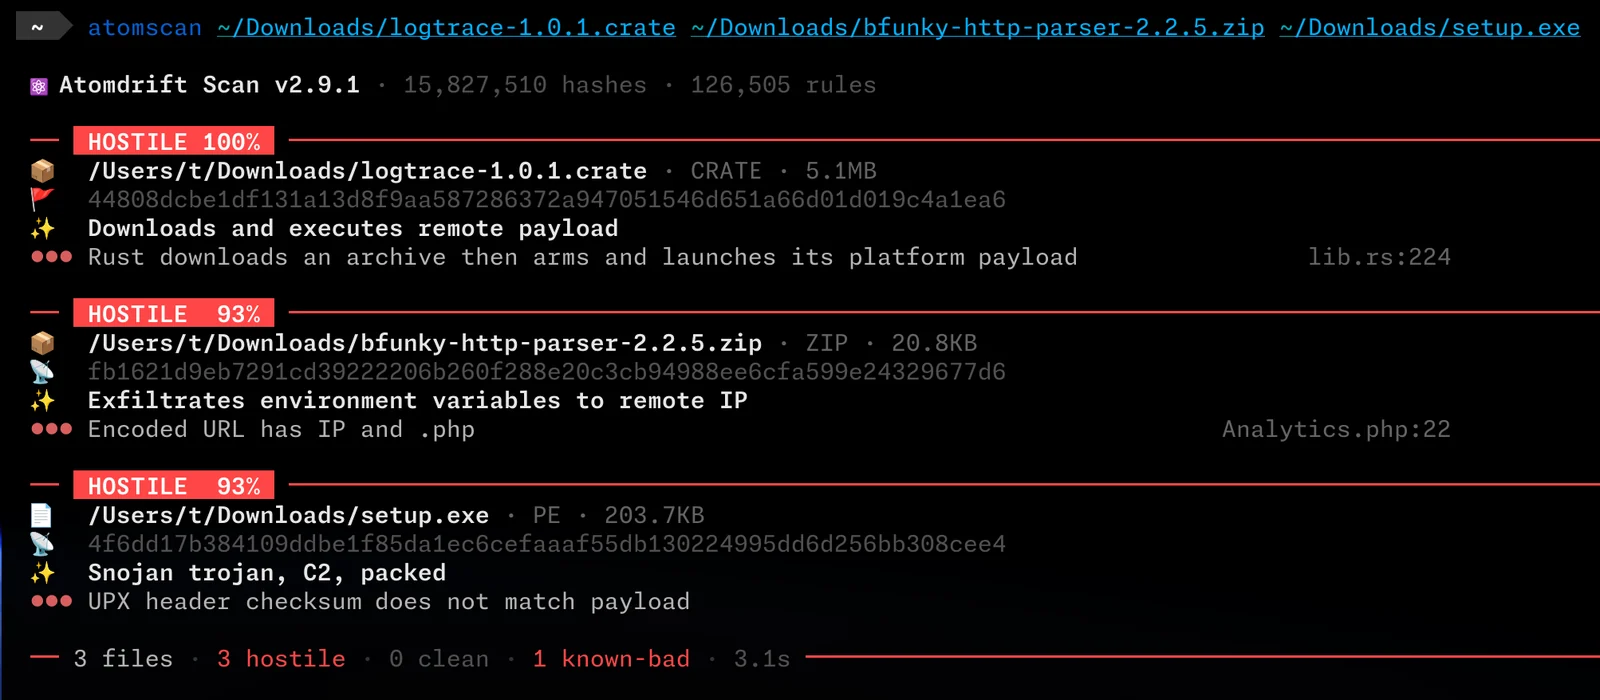
scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
512 days ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
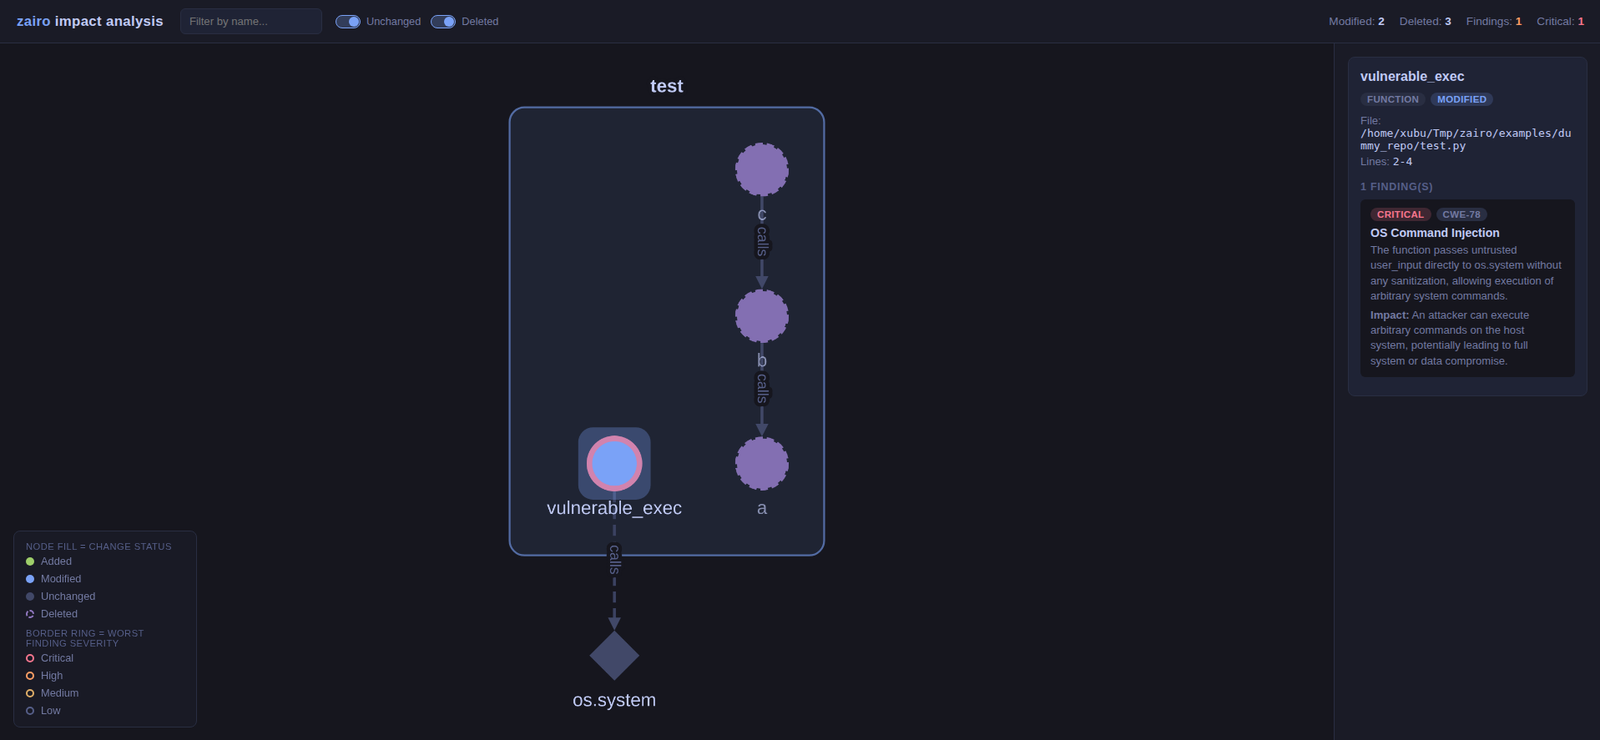 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 3ele-projects/cve-2026-39440-funnelforms-fix
Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
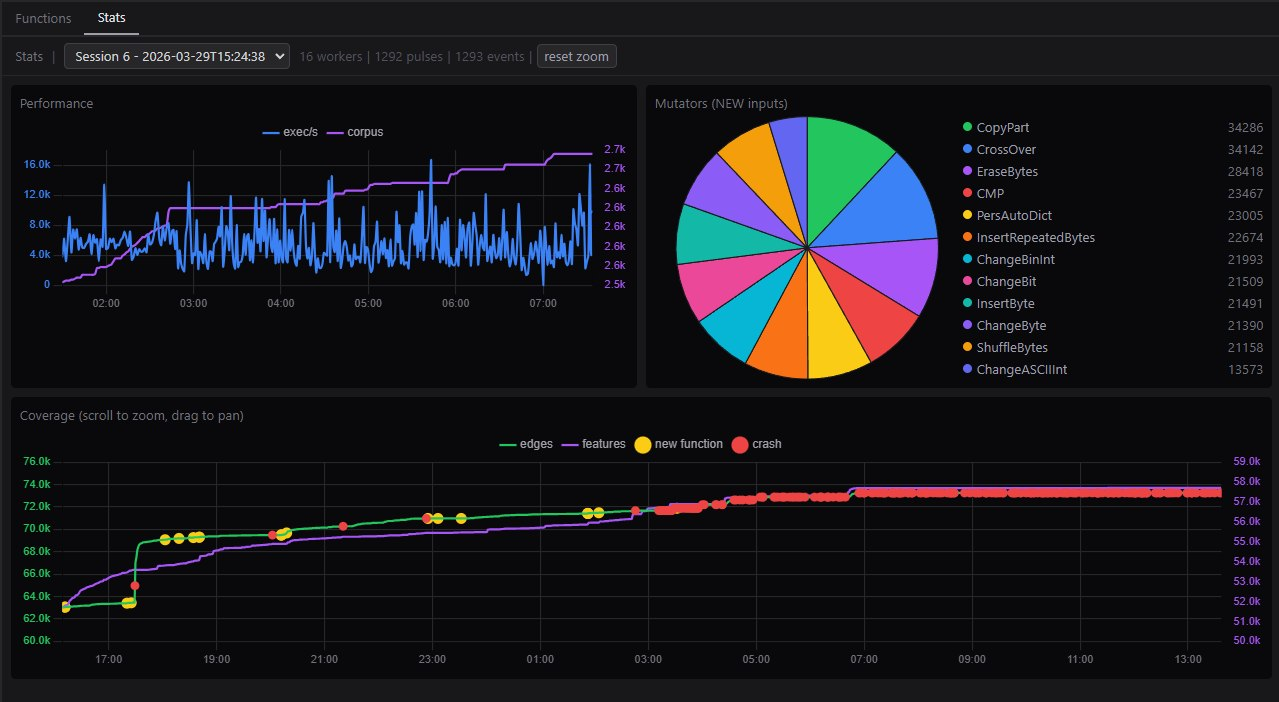 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 califio/ngxray
ngxray — nginx config security scanner
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
