

scan4secrets
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
code-analysisconfiguration-auditingcrawler+9
123
m14r41/scan4secretsFind credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 zoly-zoly/cve-2025-3248
Educational analysis and proof-of-concept exploit for CVE-2025-3248, a critical unauthenticated code injection vulnerability in Langflow, including…
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
 trachinus/cve-2026-4813
Proof-of-concept exploit for authenticated remote code execution via XSLT injection in Lutece Core, demonstrating command execution through crafted…
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 hideki233/cve-2025-3248-langflow-rce
Proof-of-concept exploit for CVE-2025-3248, an unauthenticated remote code execution vulnerability in Langflow, demonstrating code injection via the…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
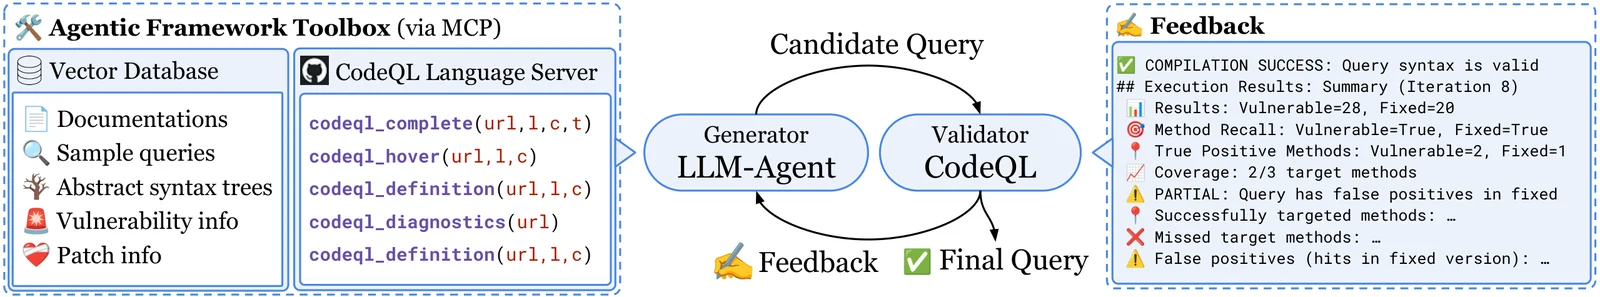 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…