
IAT-Hook
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
binary-exploitationcode-analysismalware-analysis+4
gmh5225/iat-hookC++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 anna-kravets/codeql-buffer-overflow-variant
Synthetic CWE-120 stack buffer overflow variant of CVE-2020-8597 (pppd EAP) as a CodeQL static-analysis target
 quarkslab/quokka
Quokka: A Fast and Accurate Binary Exporter
 mudongliang/source-packages
This repo stores source code of the vulnerable program.
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
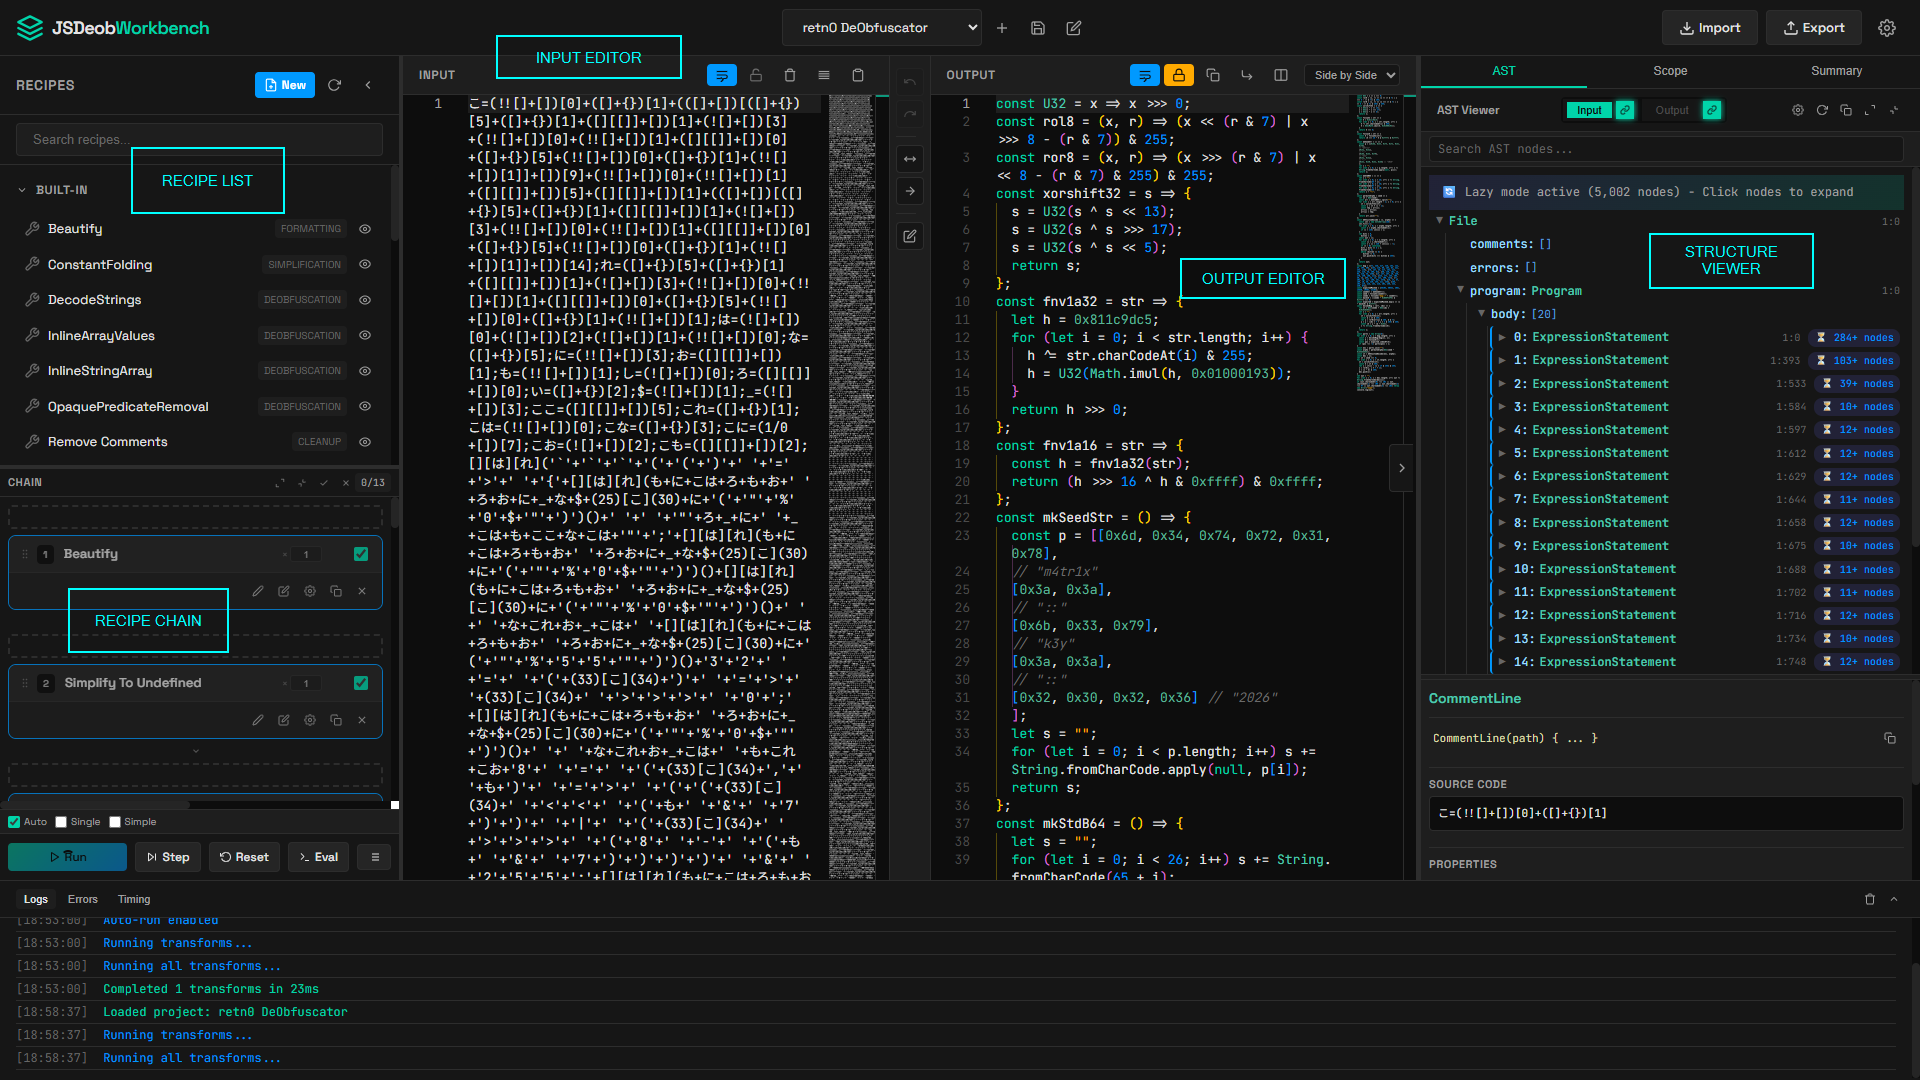 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 brinmon/cve-2024-44337
CVE-2024-44337 POC The package `github.com/gomarkdown/markdown` is a Go library for parsing Markdown text and rendering as HTML. which allowed a…
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 galoisinc/mate
Interactive program analysis suite using Code Property Graphs to hunt for bugs in C and C++ code, unifying application-specific and low-level…