

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 frida/frida
Main repo for hosting release binaries
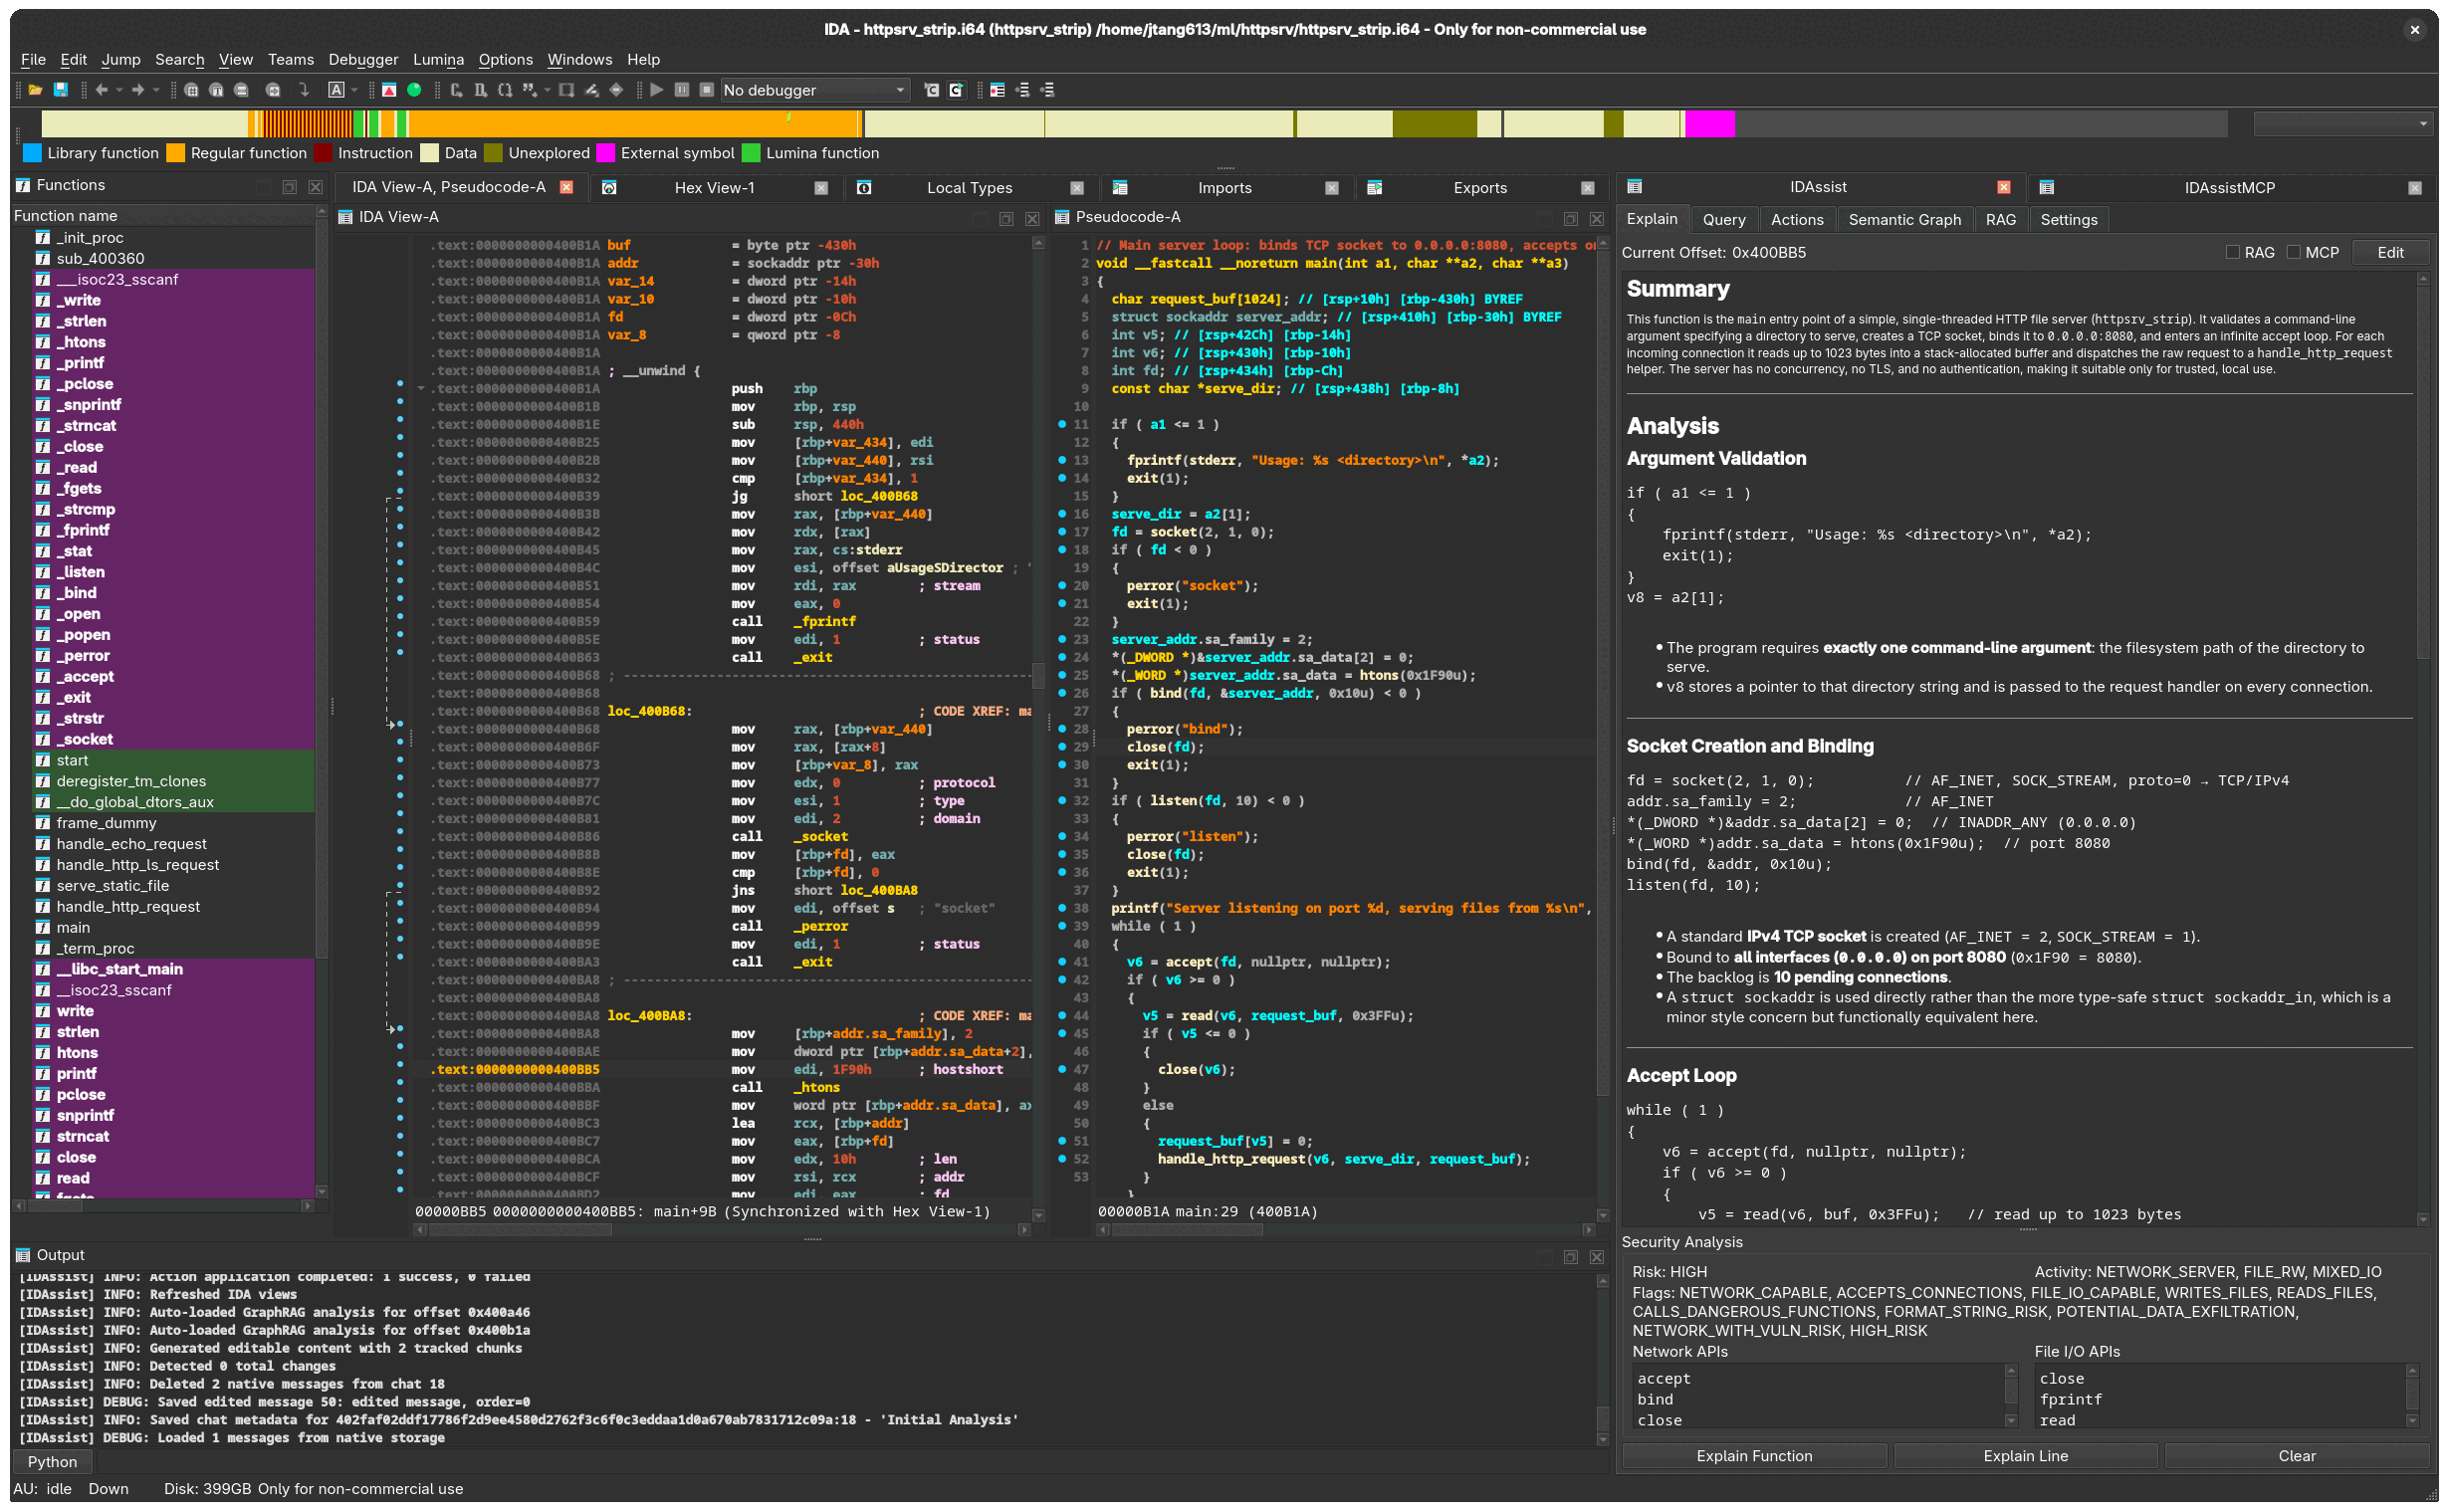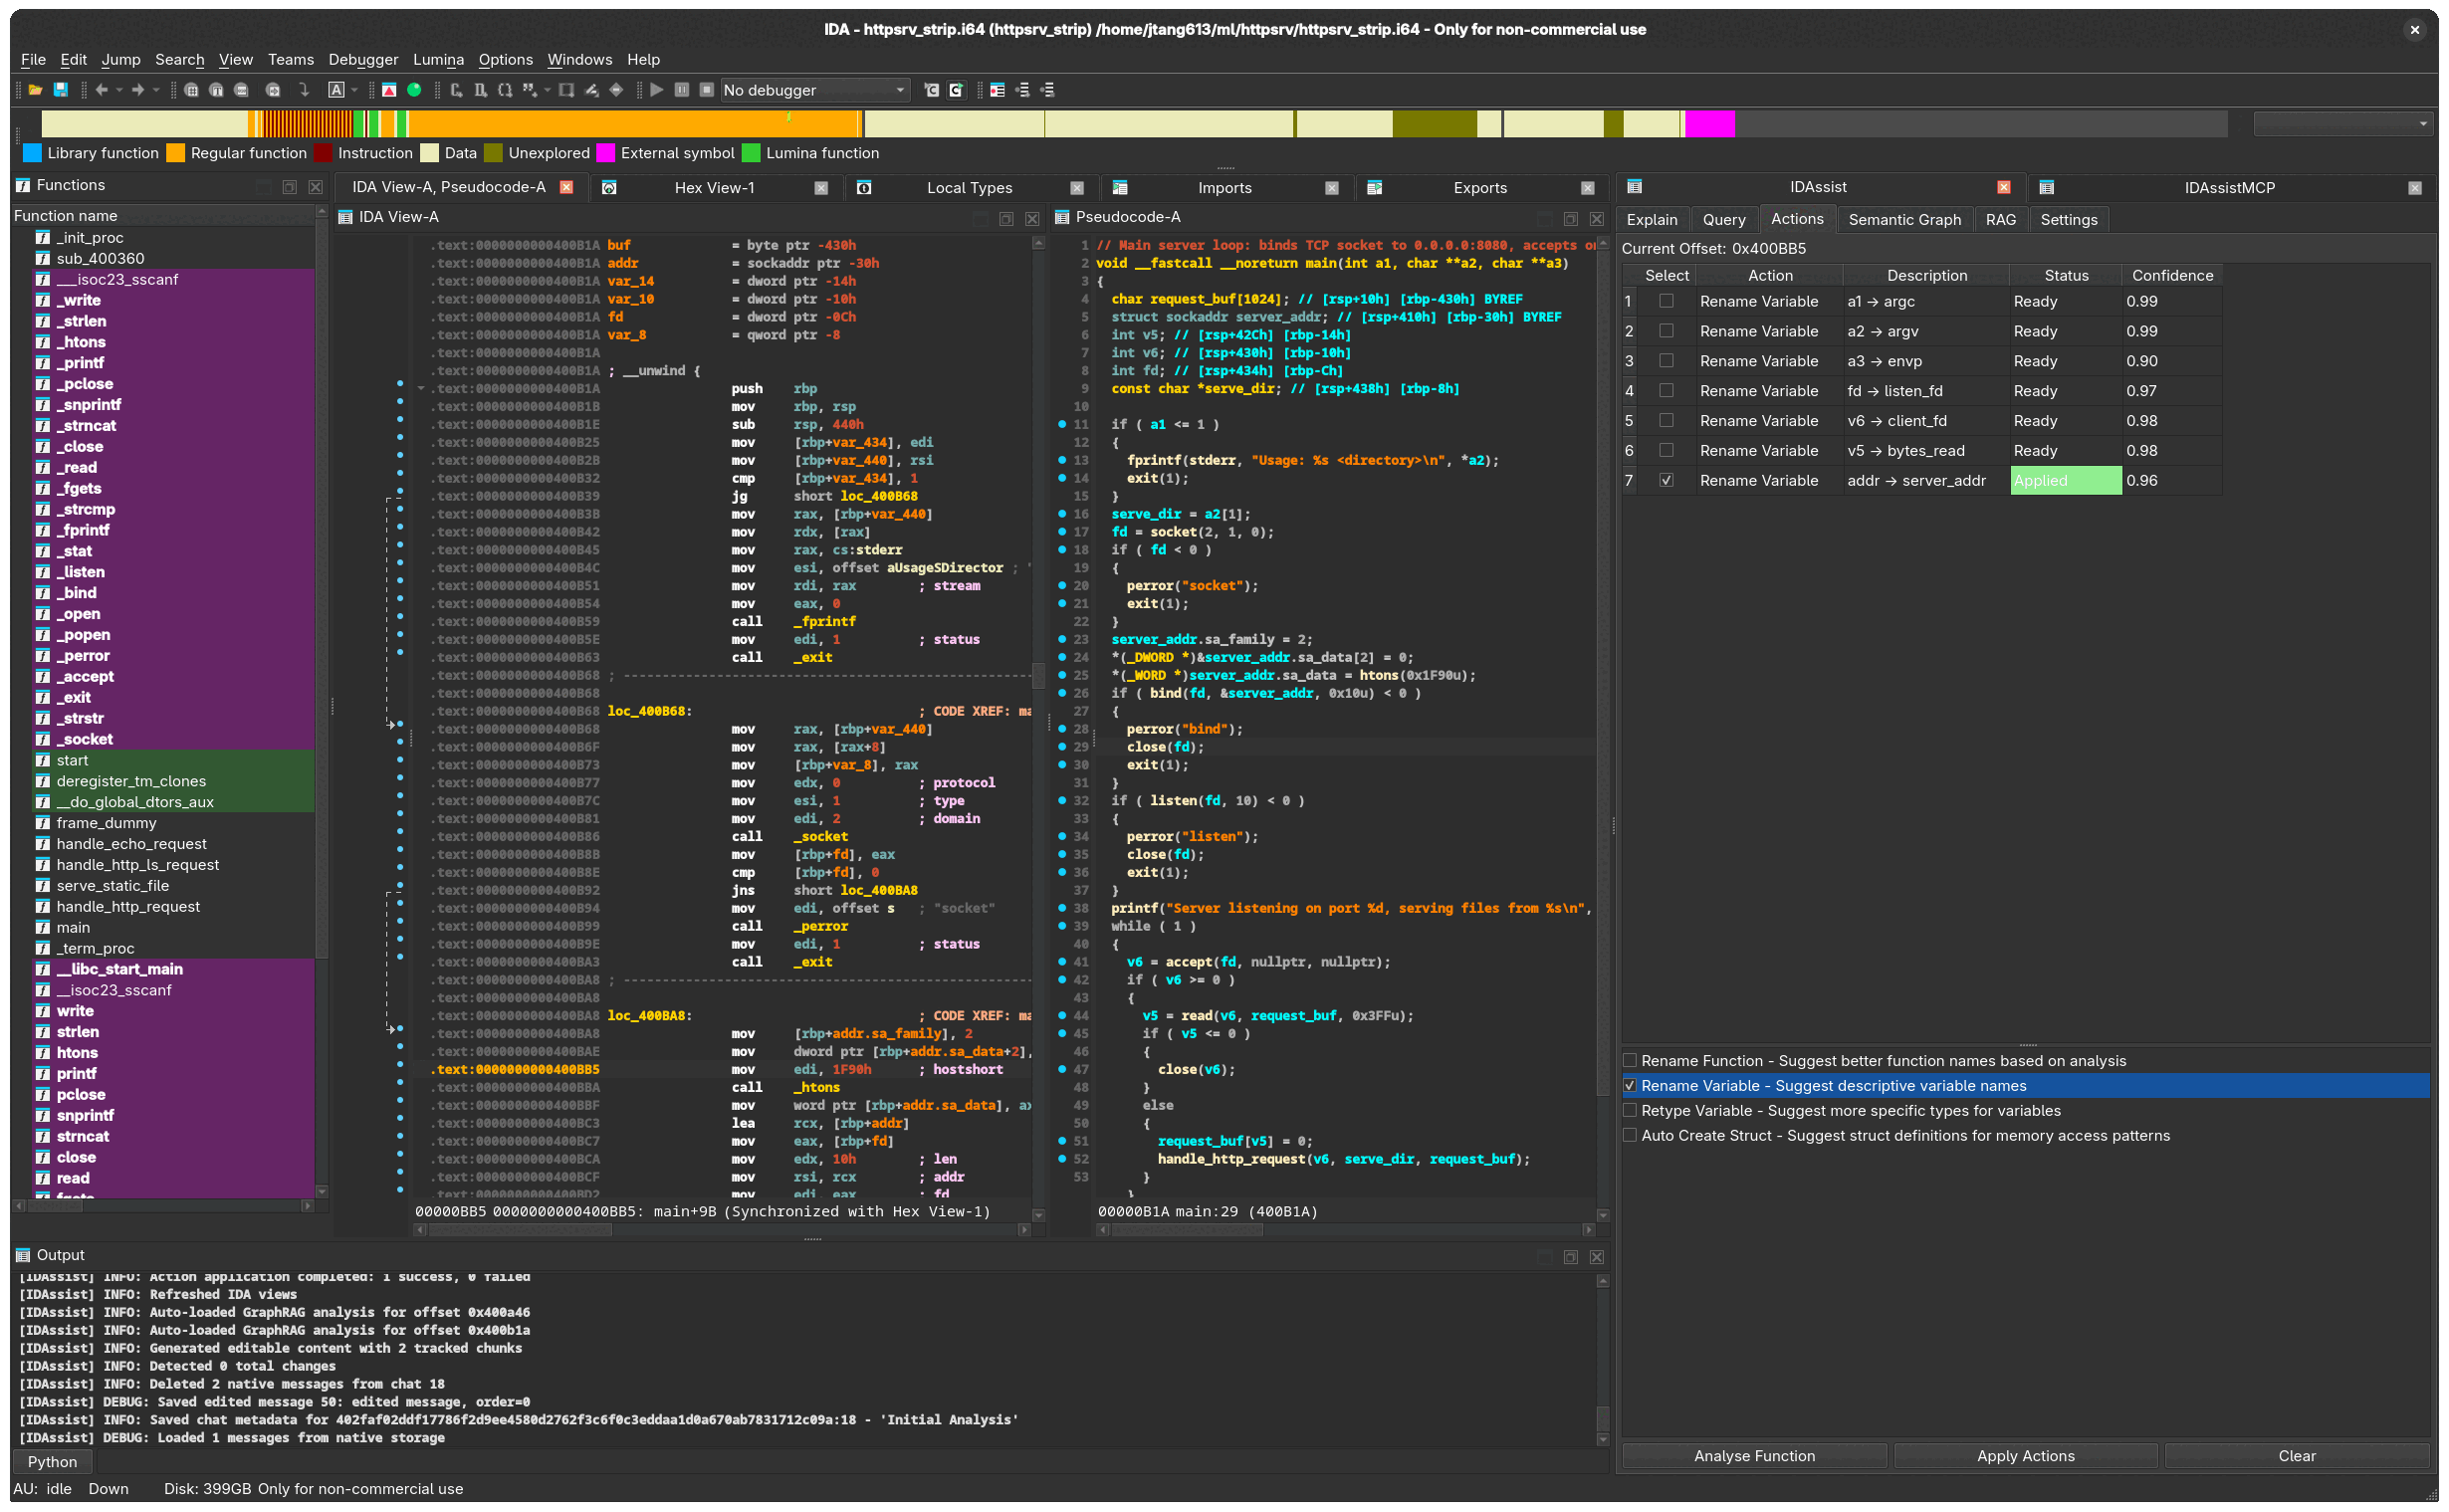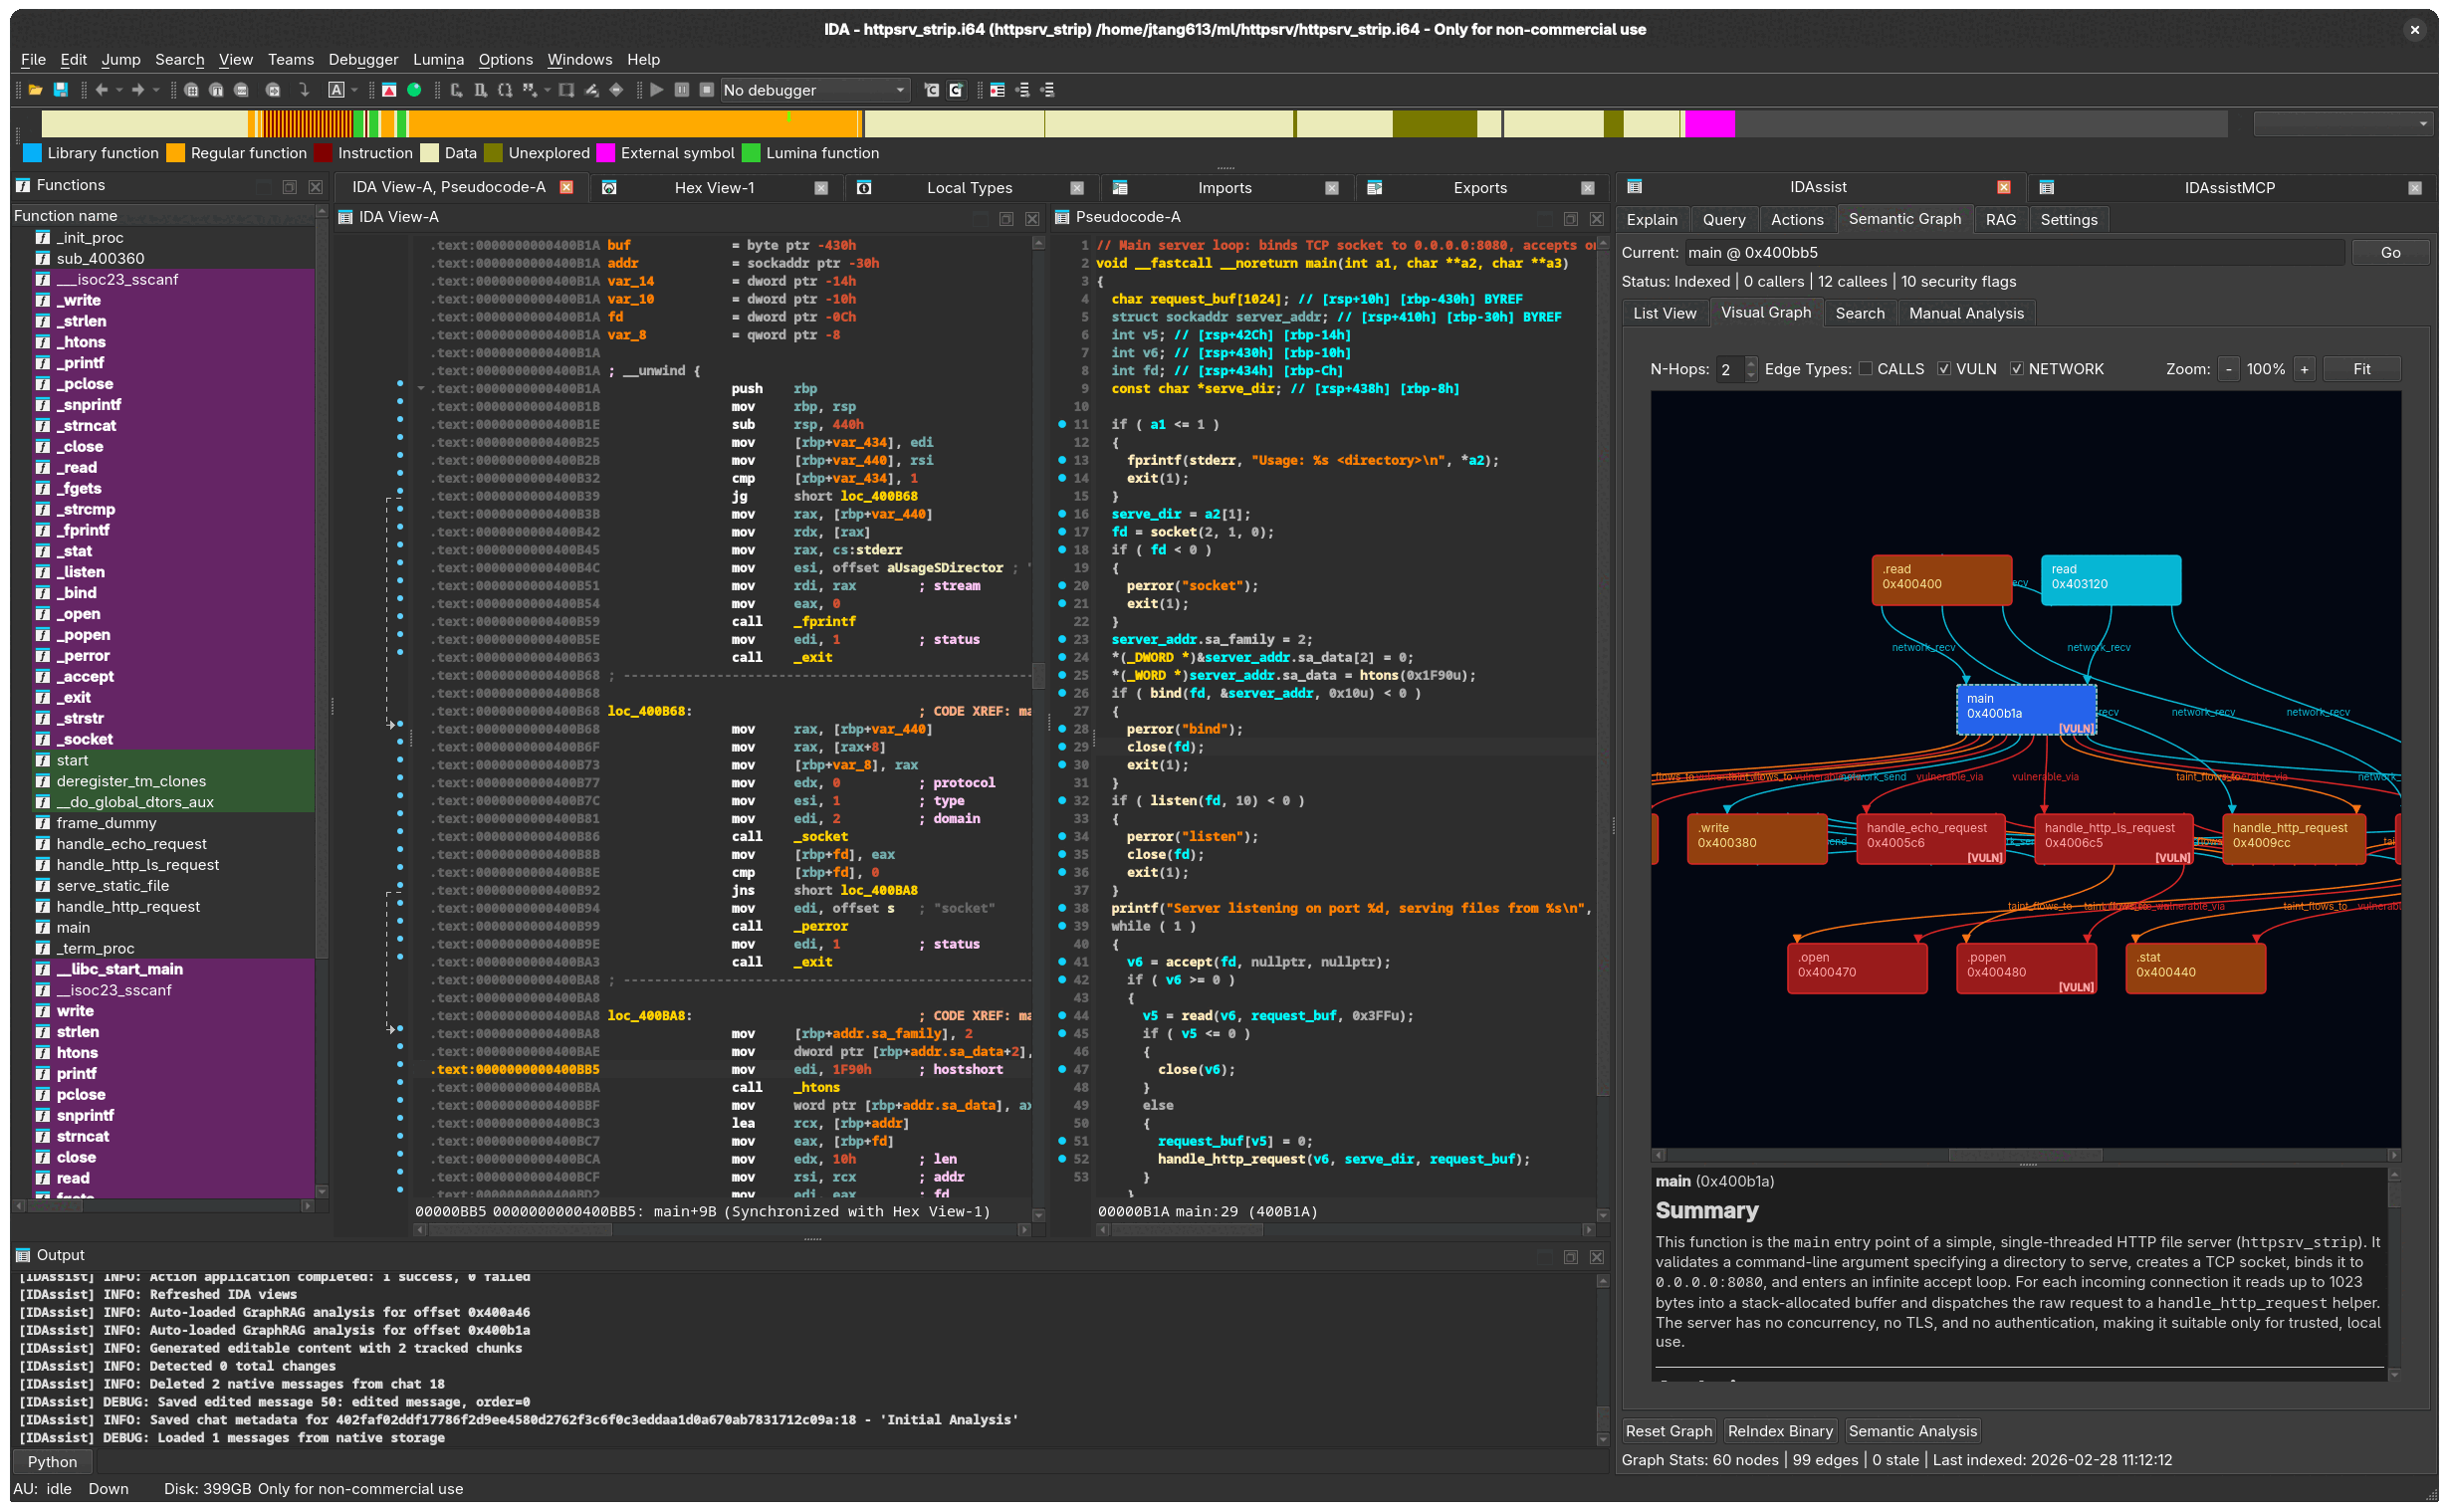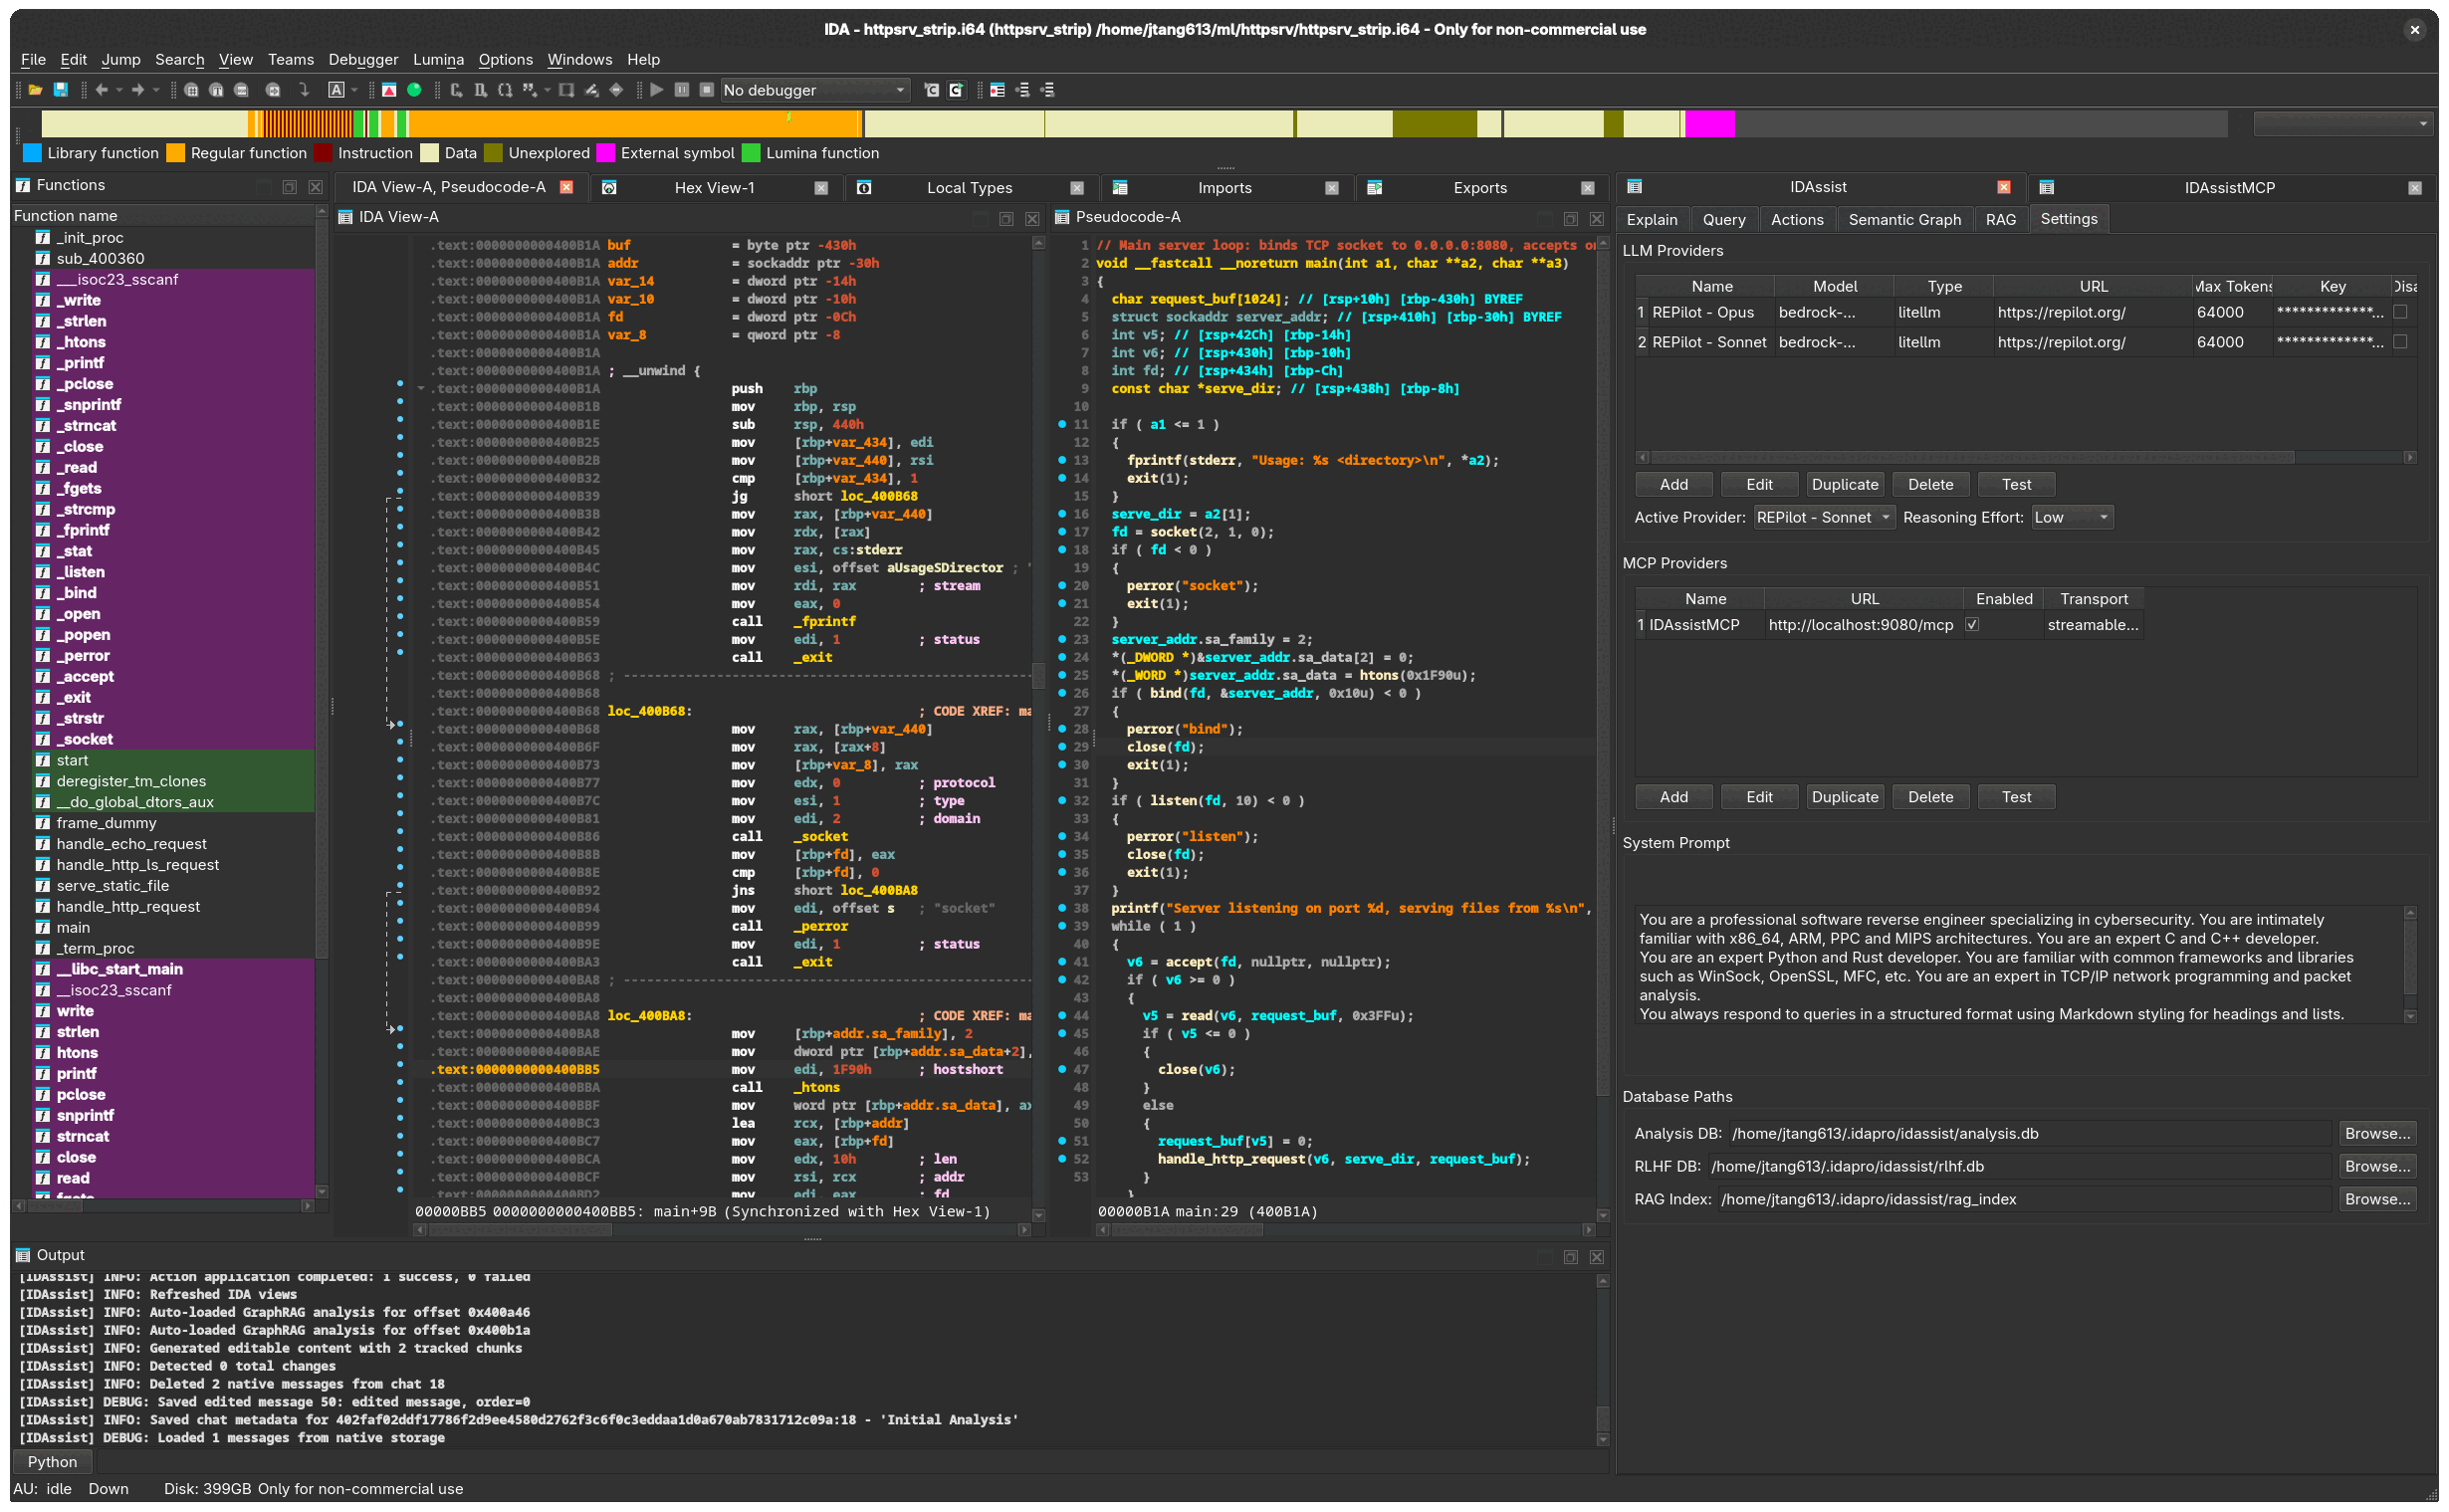 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 dionach/reposcanner
Python script to scan Git repos for interesting strings
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
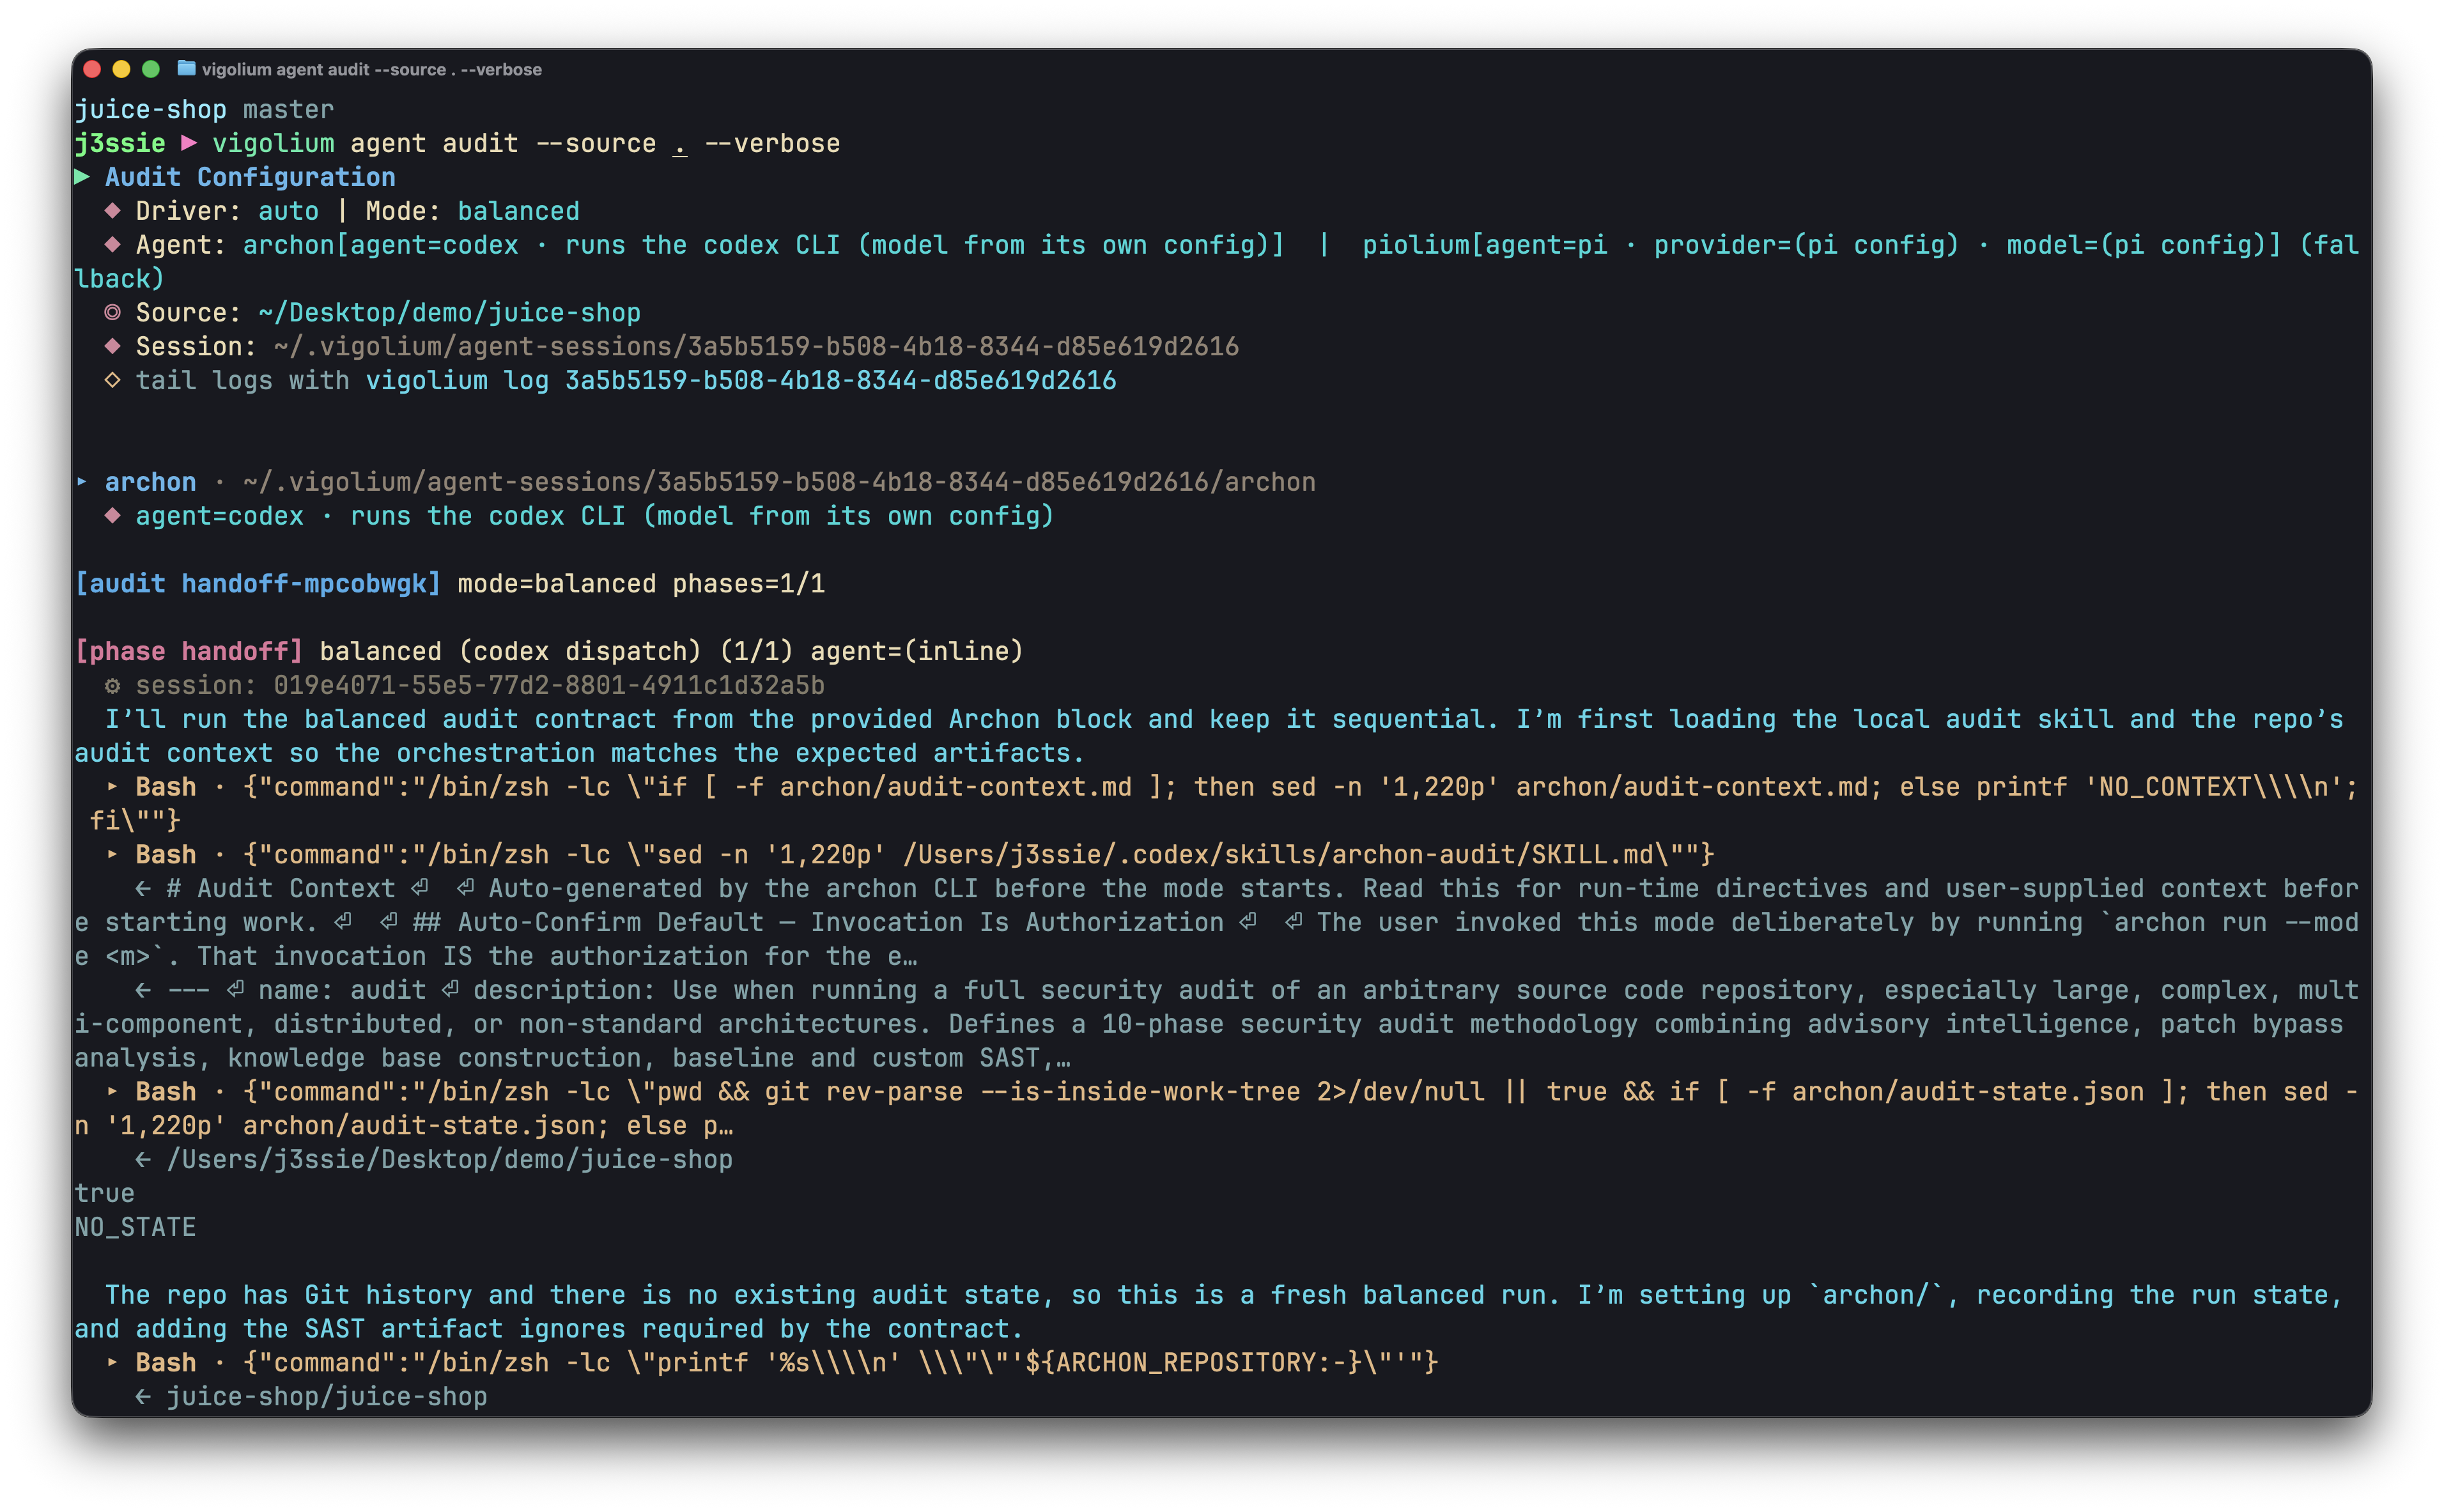 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
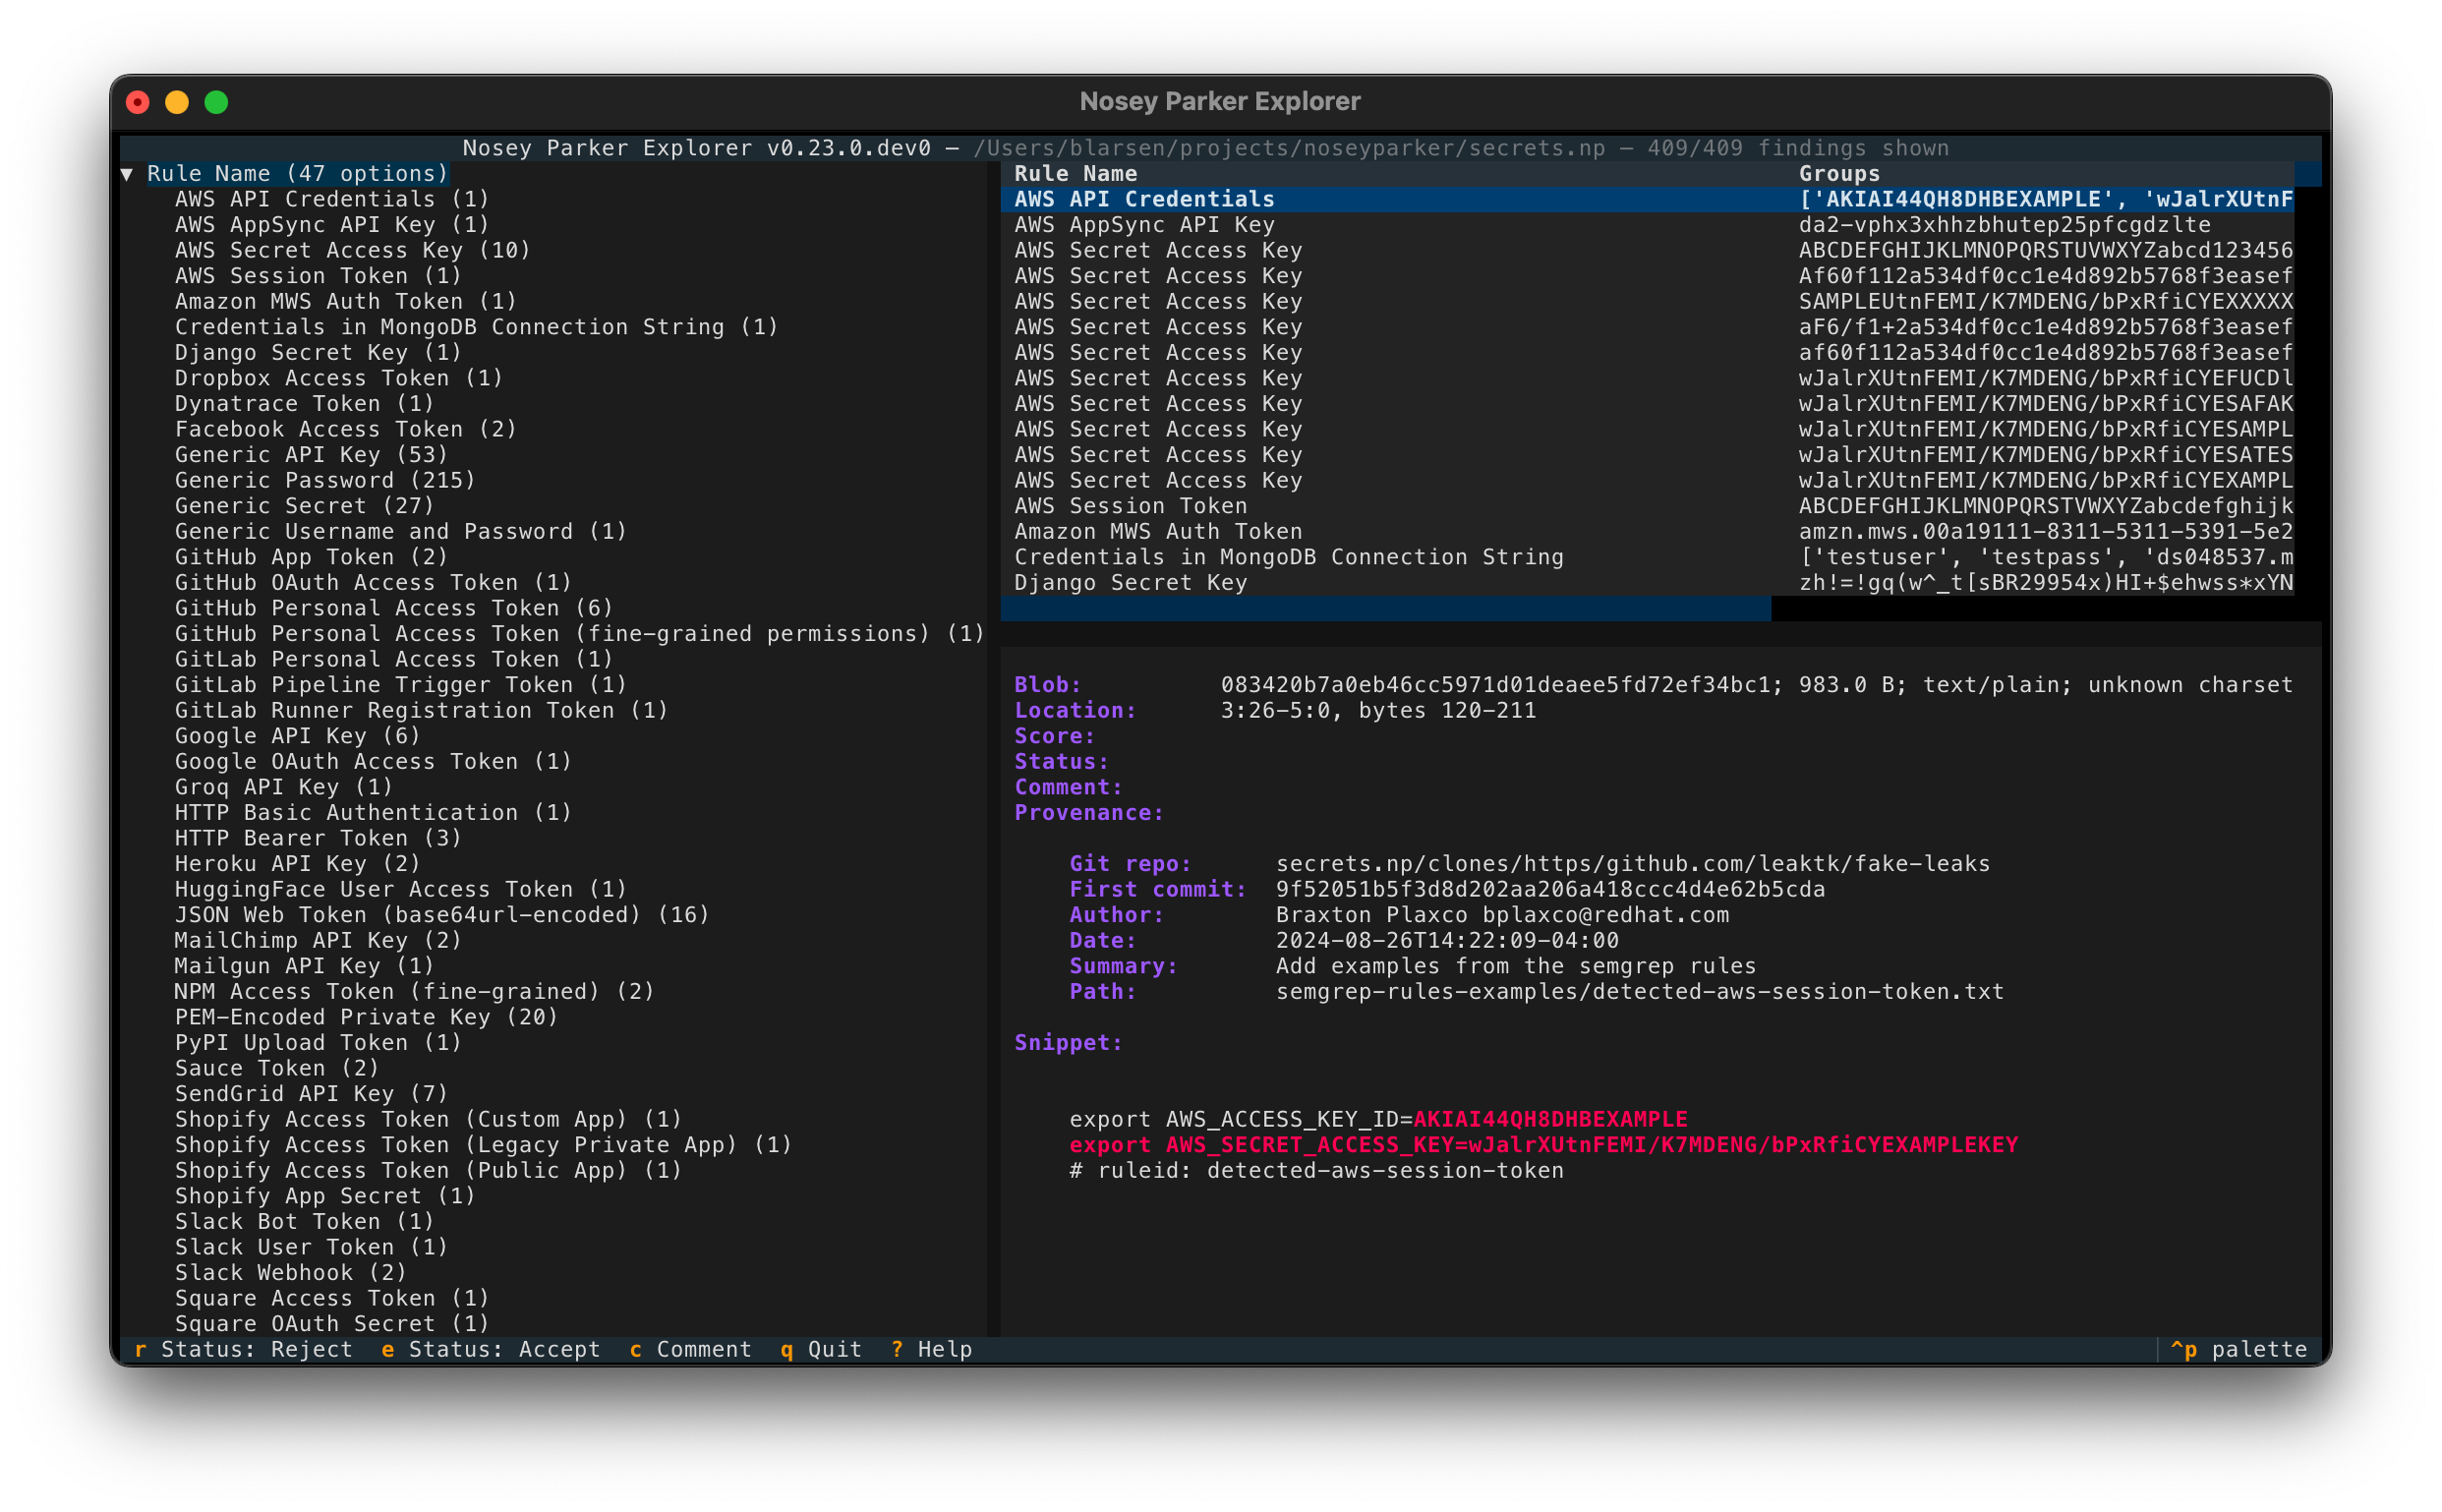 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 nightwatchcybersecurity/gitbleed_tools
Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.