shannon
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
ai-securityapi-security-testingcode-analysis+5
46.6k
keygraphhq/shannonShannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 danoszz/penthera
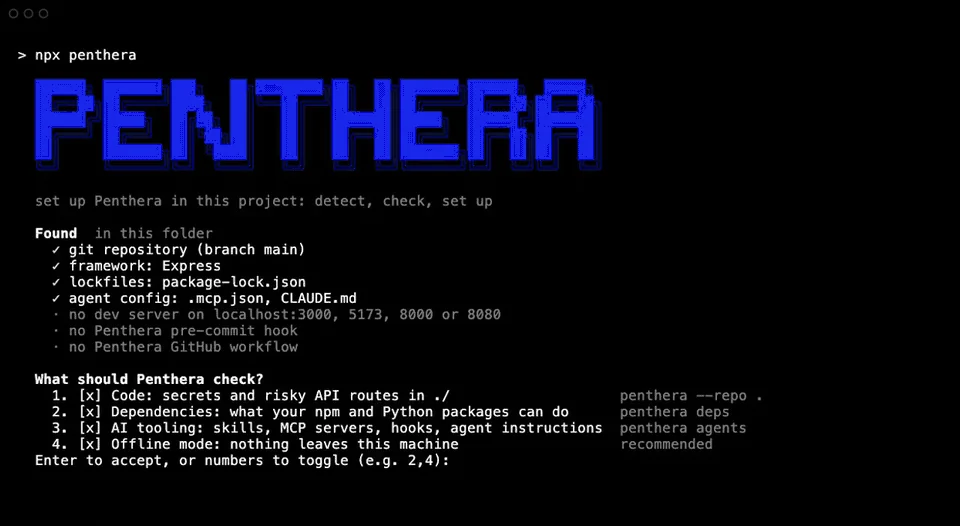
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
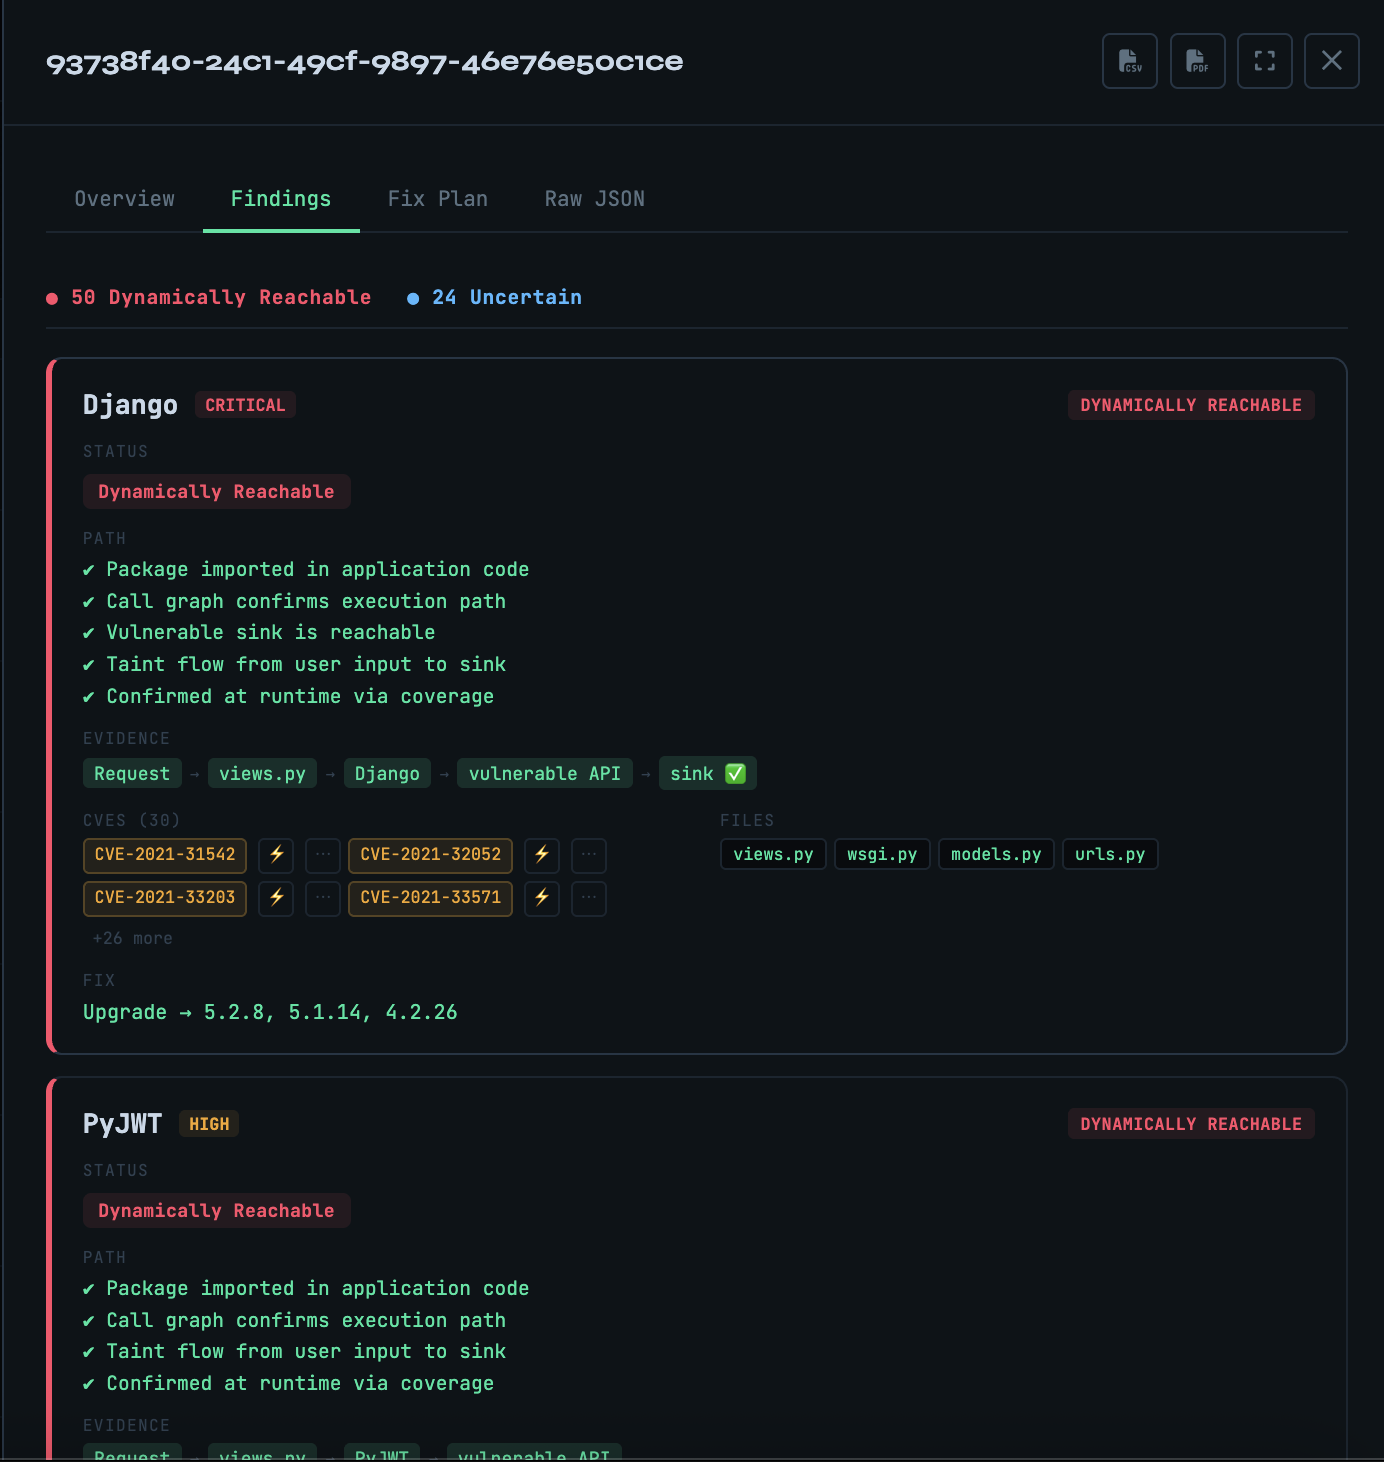 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 owasp/asvs
Application Security Verification Standard
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
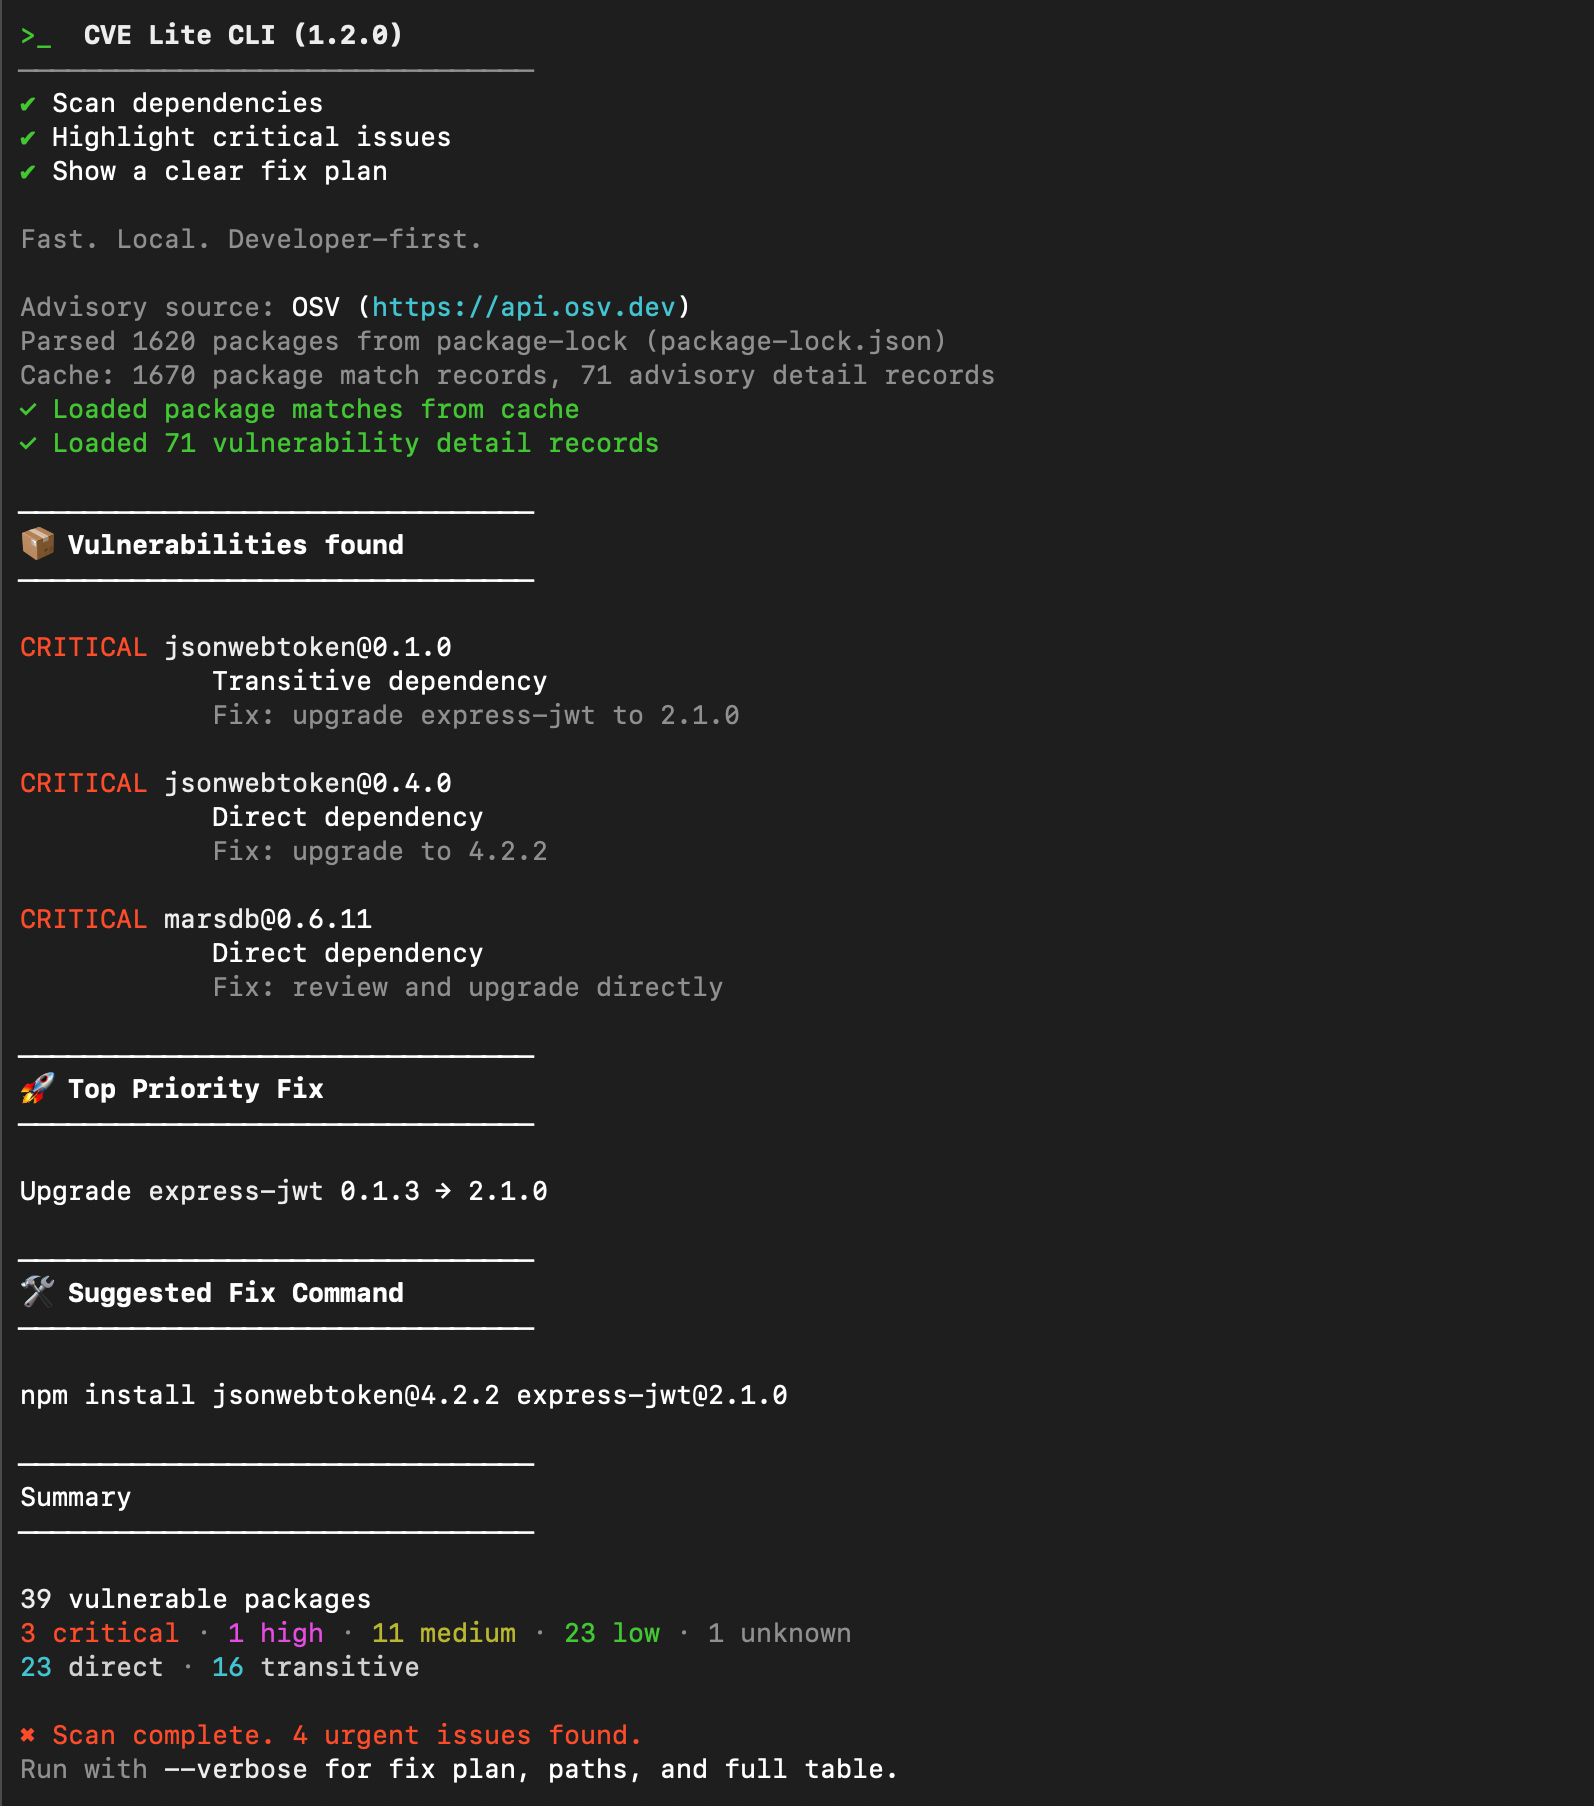 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
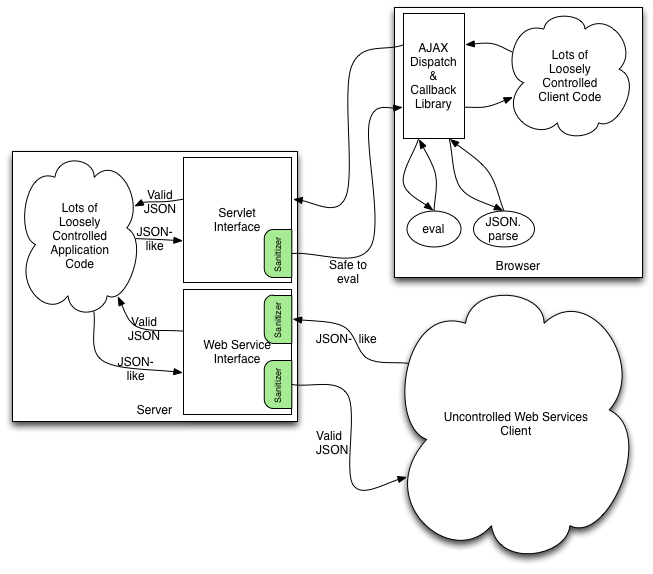 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.