
jailer
 gen0sec/jailer
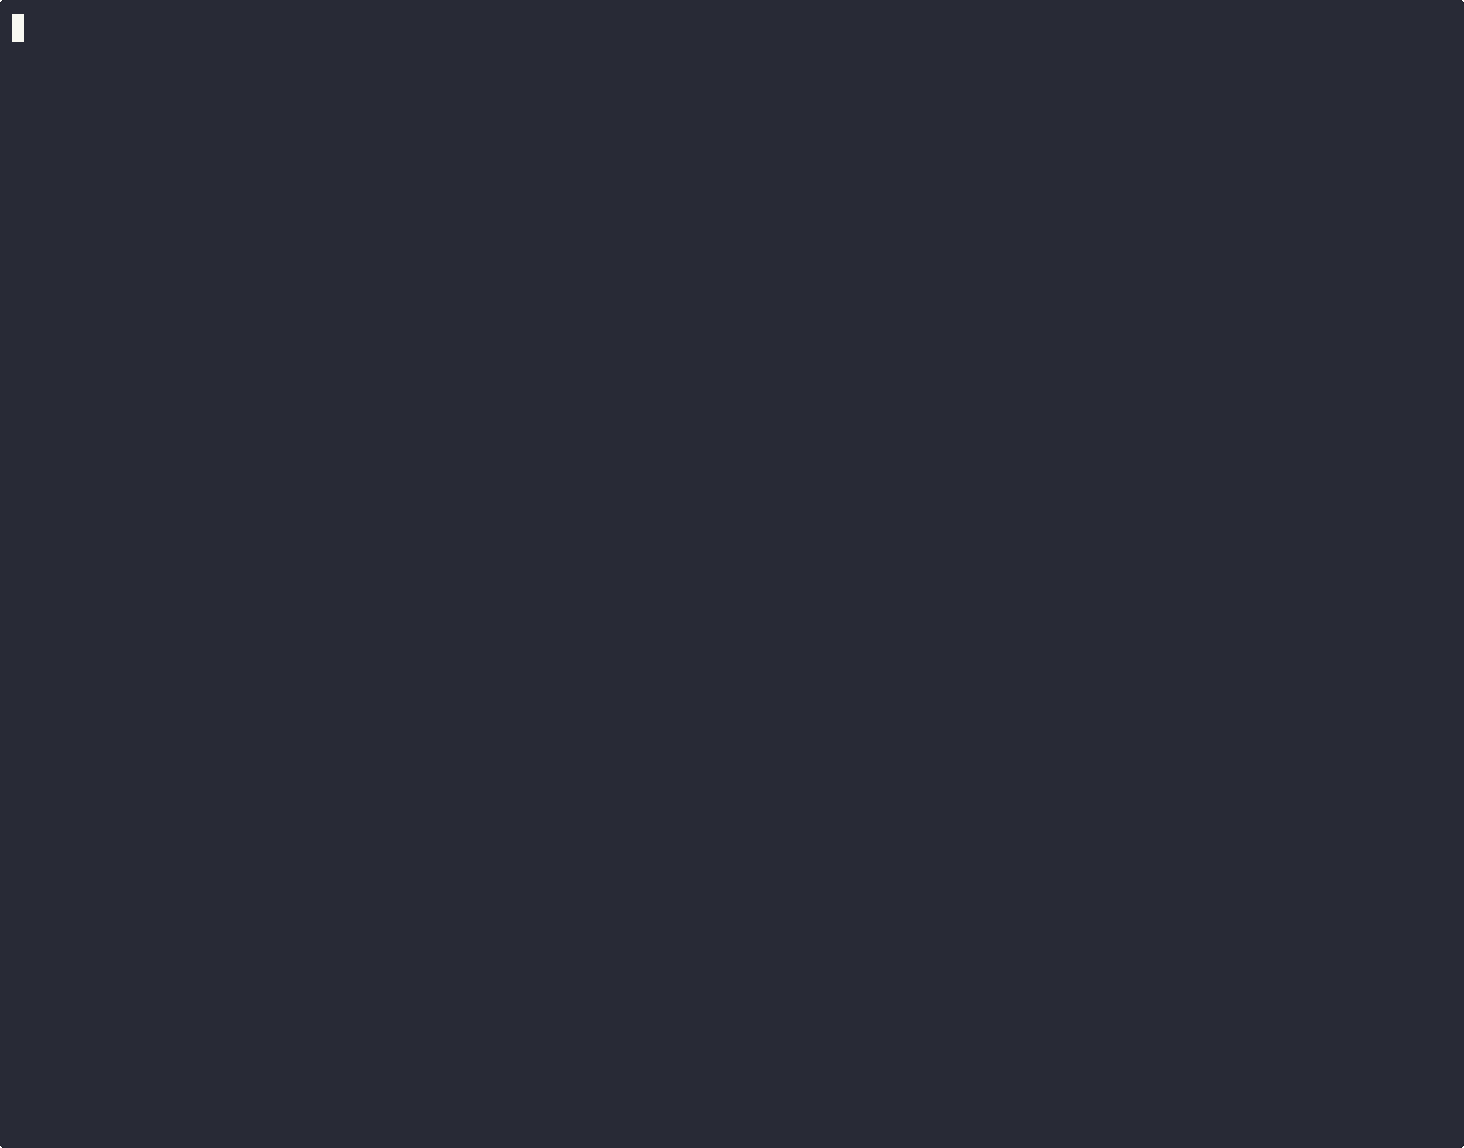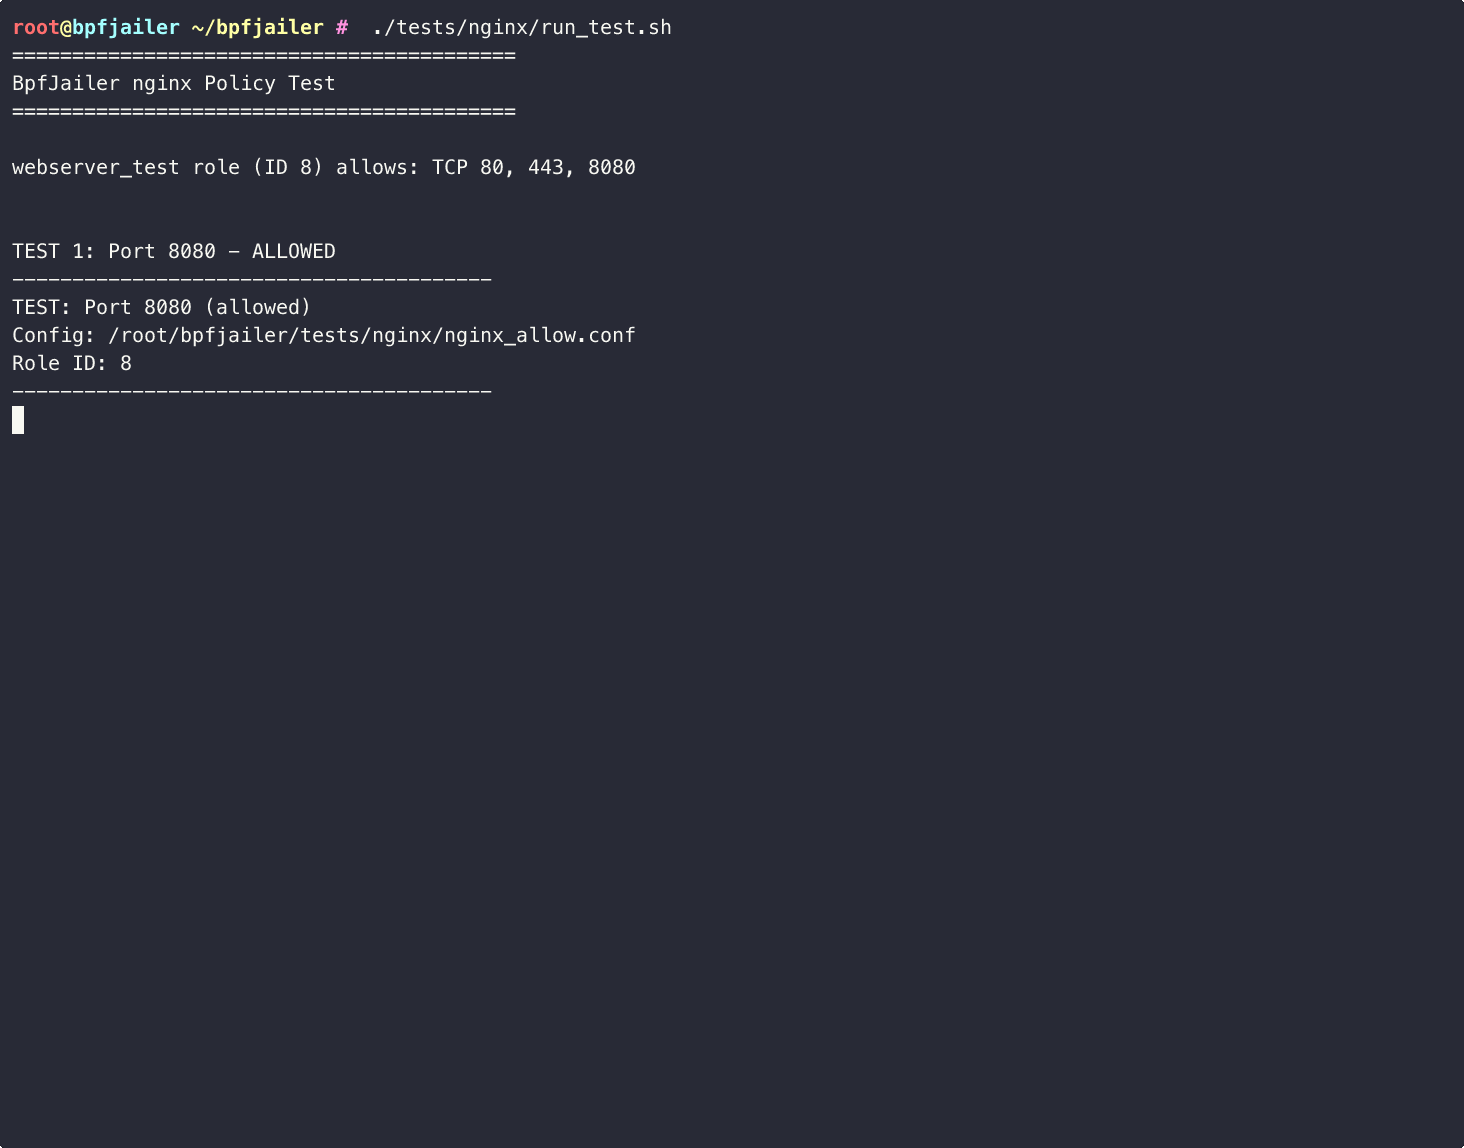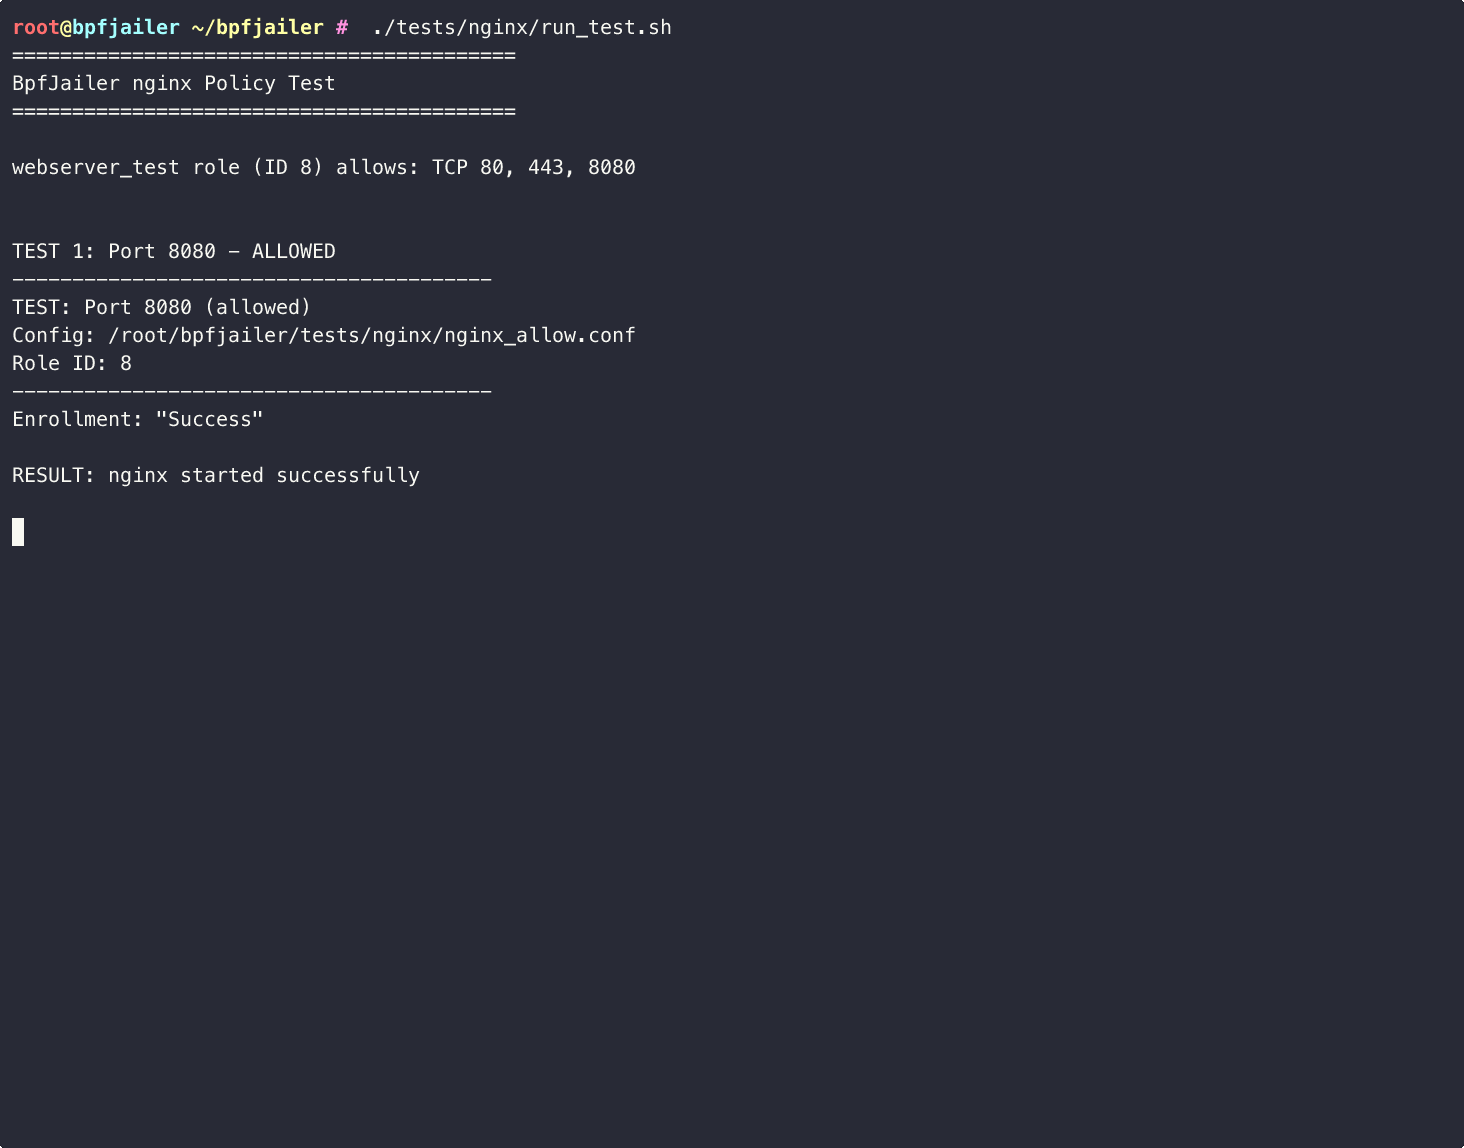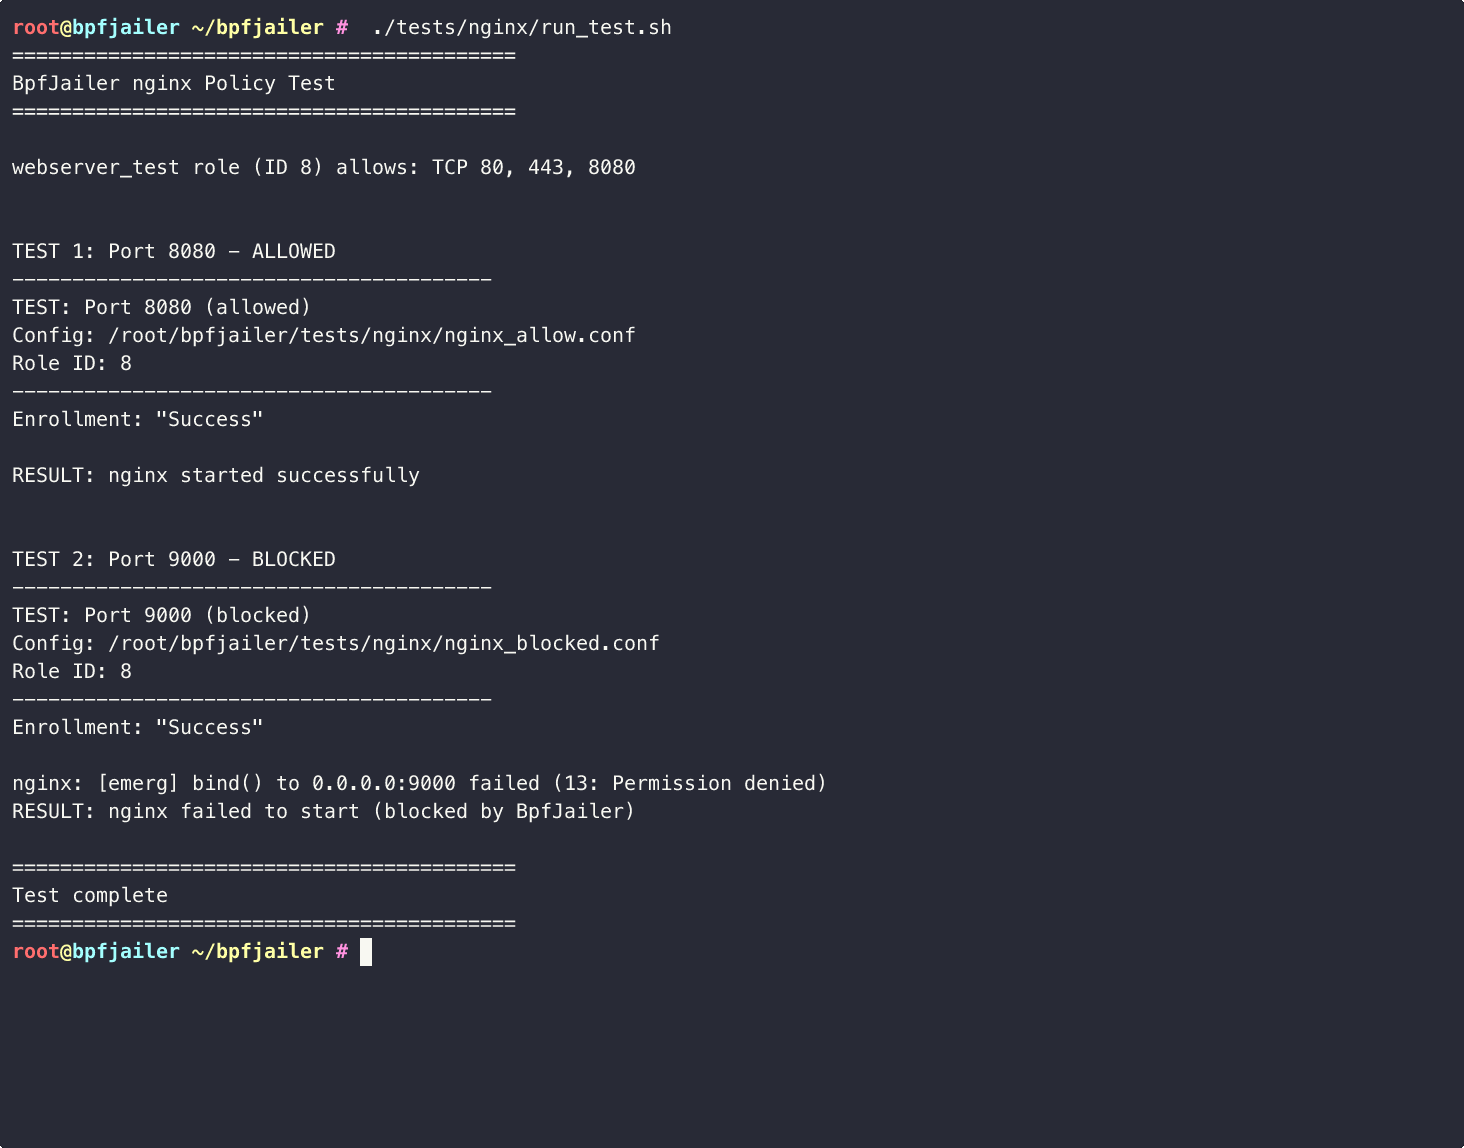
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
cloud-securitycontainer-securitydefensive-tools+1
gen0sec/jailerJailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
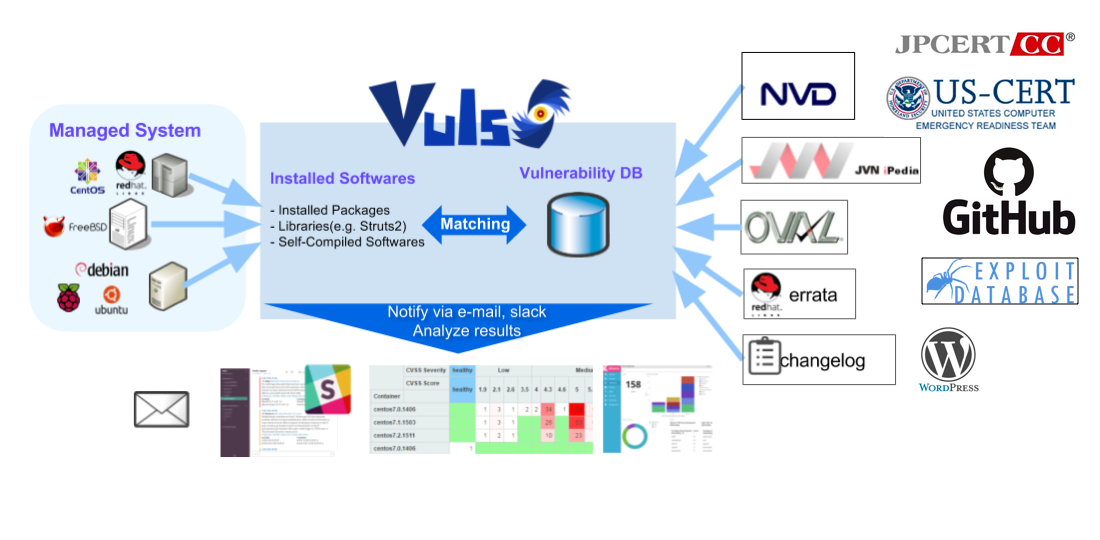 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 cloud-gouv/securix
SécurixOS is a NixOS-based secure operating system tailored for small to medium-sized teams. It provides a minimal, hardened environment with strong…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
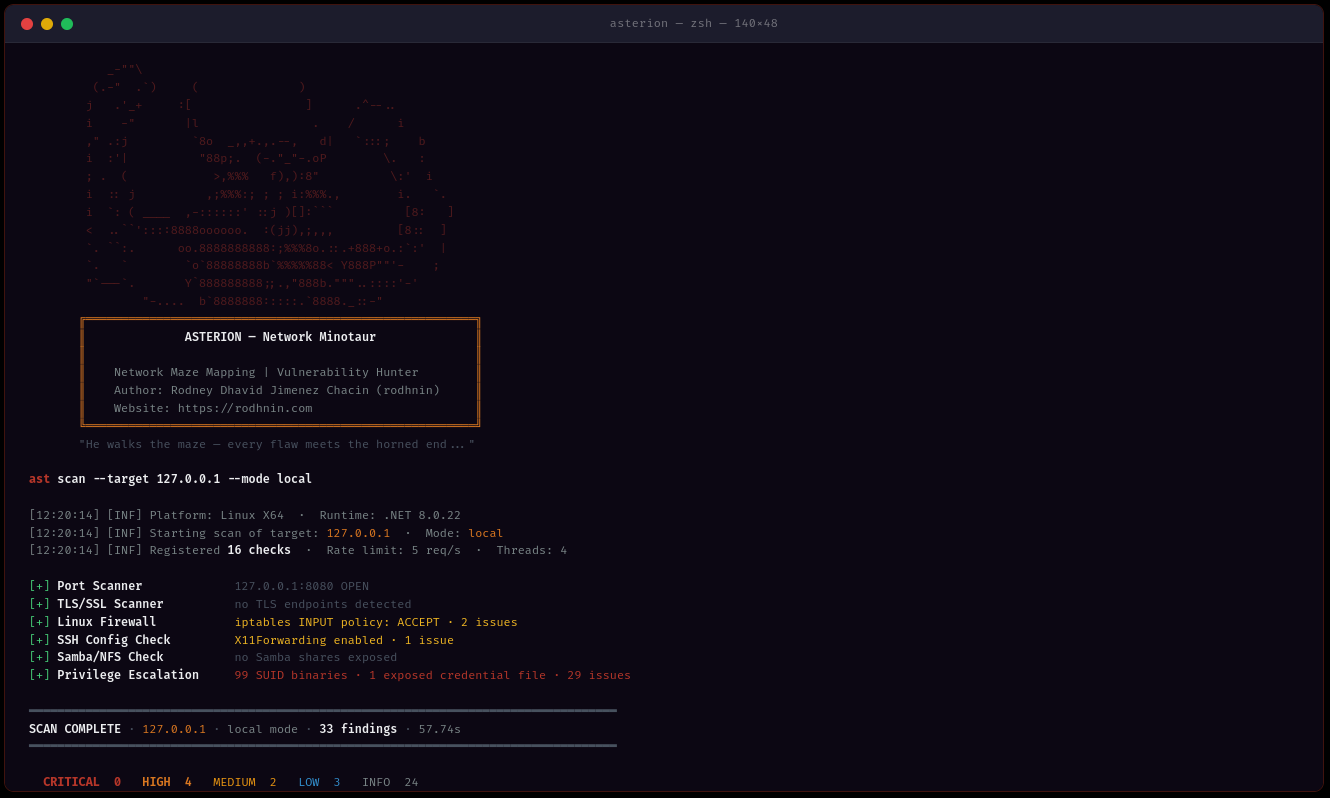 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 cain66666/openclaw-hardening-check
Offline, read-only hardening check for a self-hosted OpenClaw install — gateway exposure, auth, CVE-2026-25253. Never prints secrets, makes no…
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 dgourillon/mitigate-cve-2024-6387
Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
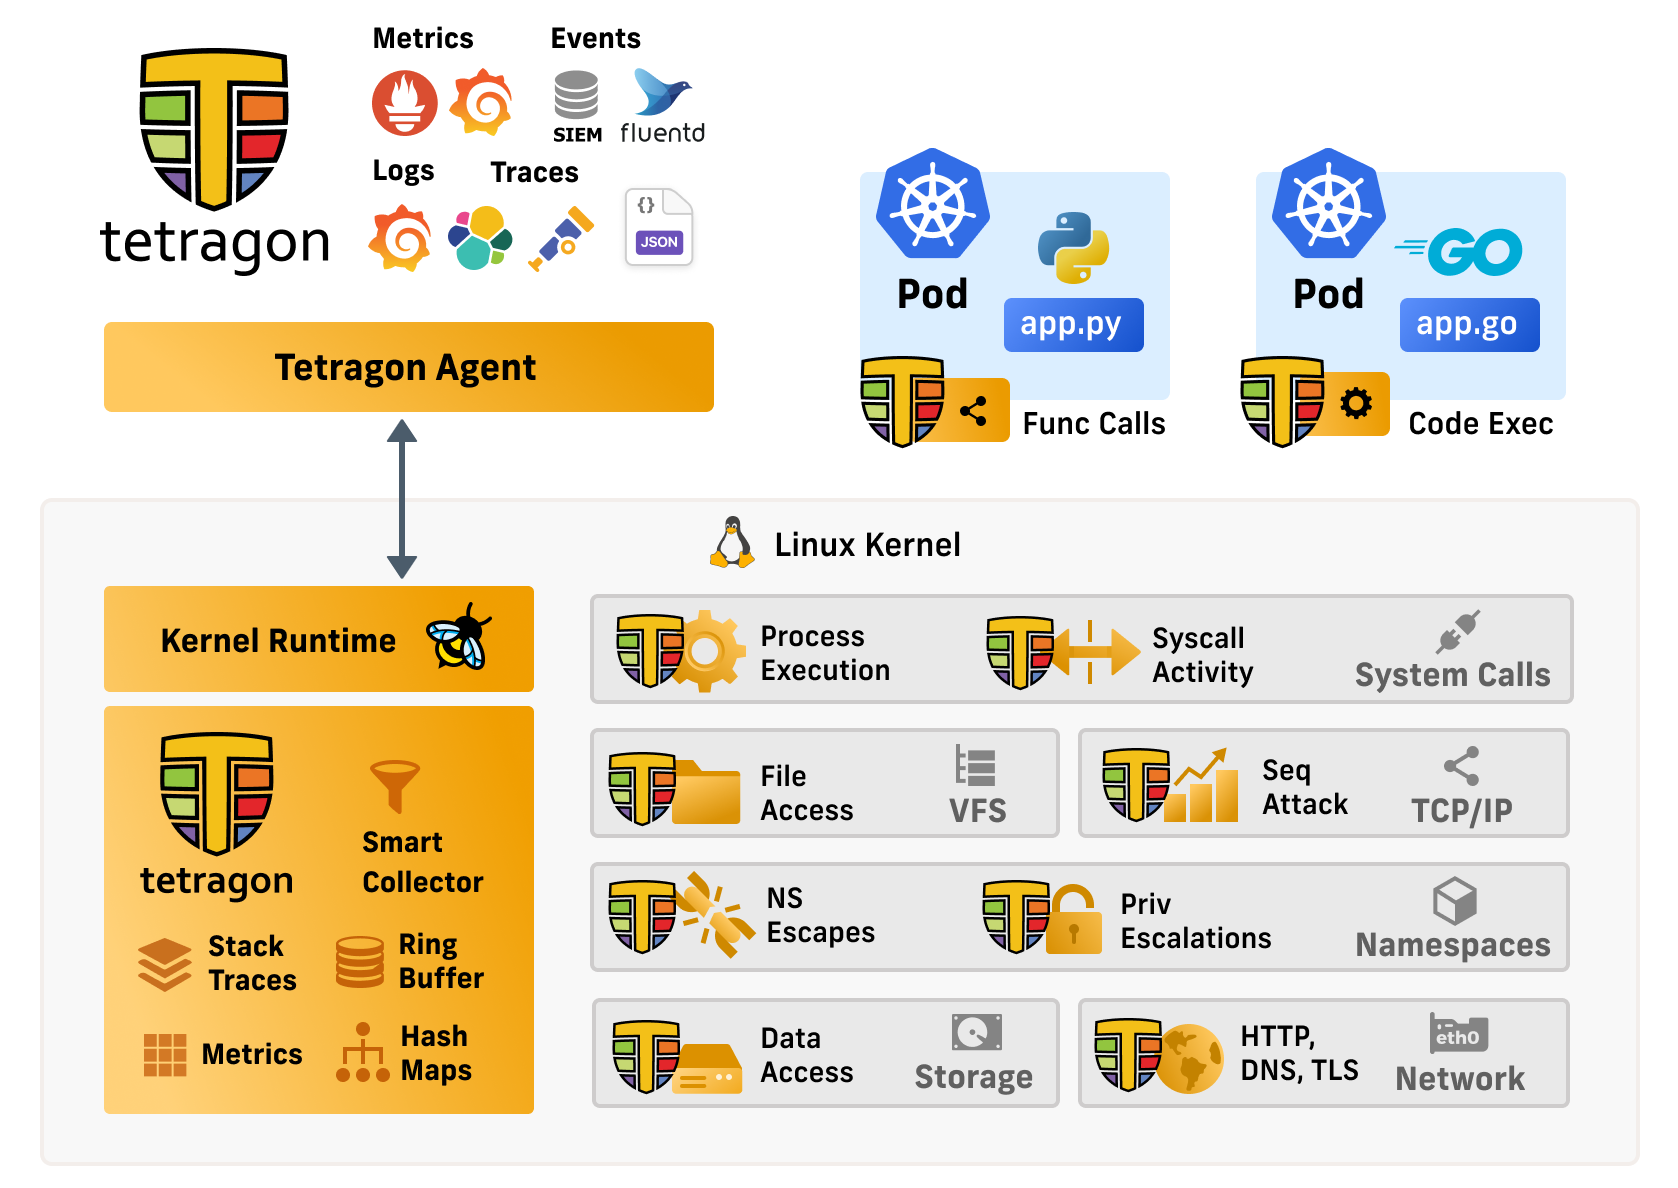 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandbox
 denuitt1/mhr-cfw
A Domain-Fronting Relay that routes traffic though GAS (Google Apps Script) and forwards it to Cloudflare Workers. Designed to bypass DPI.