
CVE-2025-1974
 0xbingo/cve-2025-1974
A minimal test tool to help detect annotation injection vulnerabilities in Kubernetes NGINX Ingress controllers. This script sends a crafted…
cloud-securitycontainer-securityeducation+4
0xbingo/cve-2025-1974A minimal test tool to help detect annotation injection vulnerabilities in Kubernetes NGINX Ingress controllers. This script sends a crafted…
 jinlei-chen-uwo/cve-2024-34351-demo
Minimal Next.js 14.0.0 demo app for CVE-2024-34351 SSRF vulnerability. Includes exploit setup, interactsh confirmation, Burp interception, and AWS…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
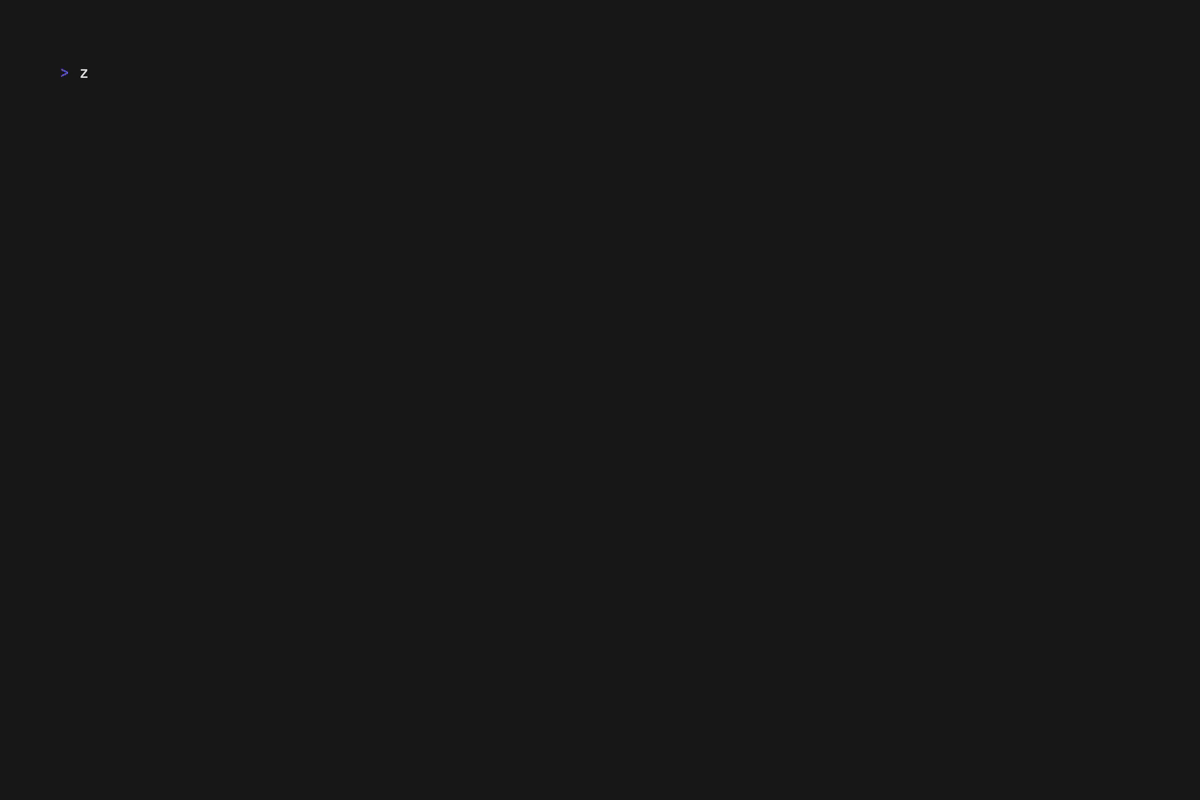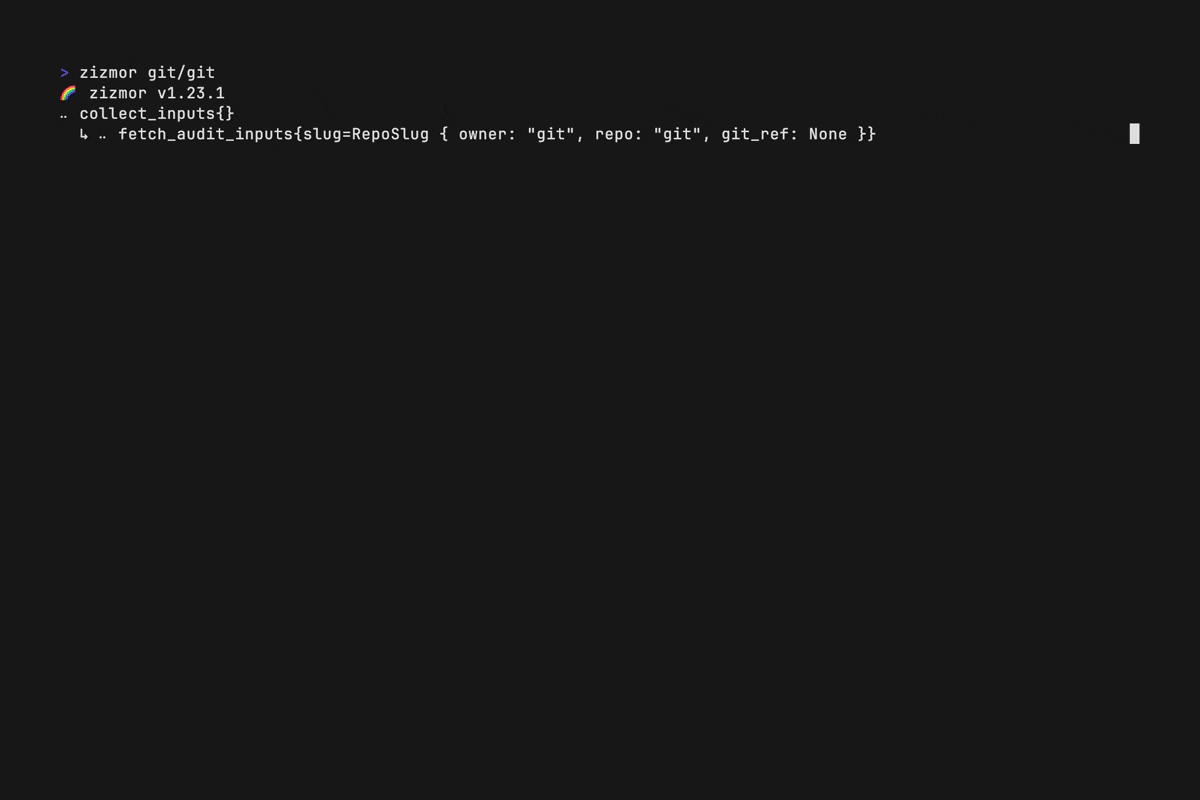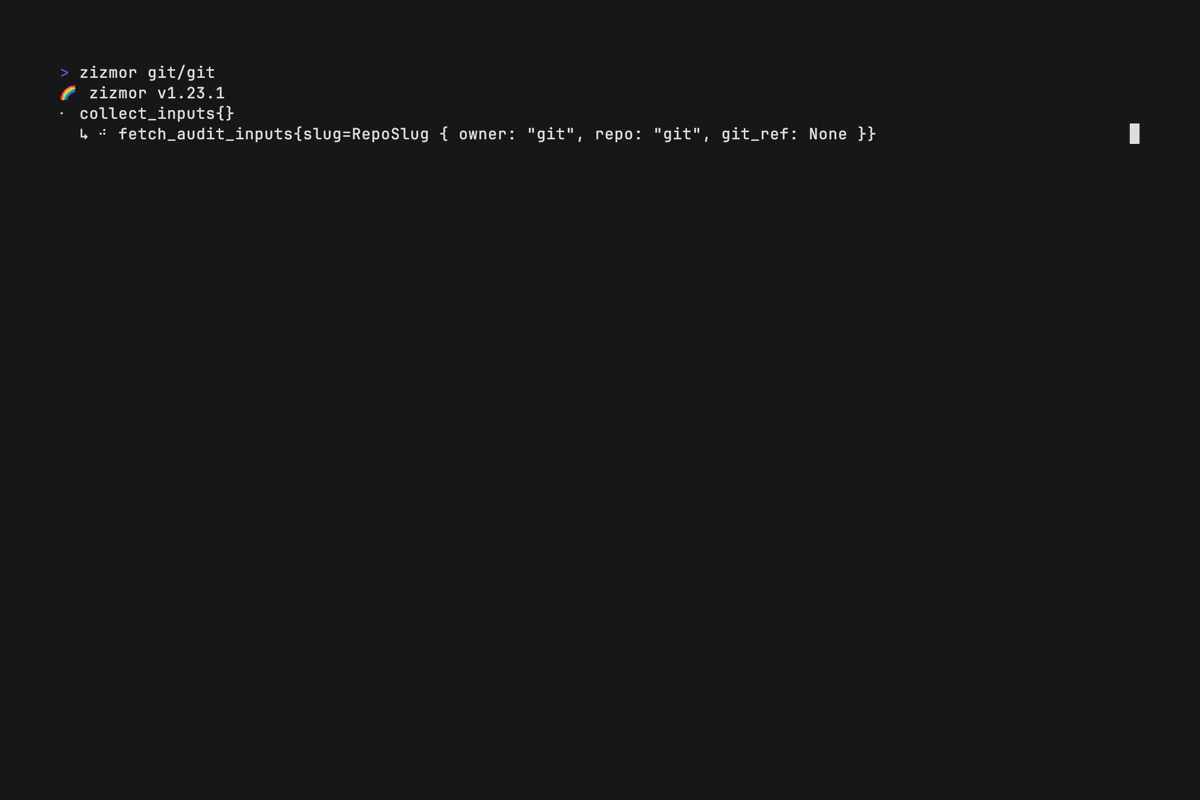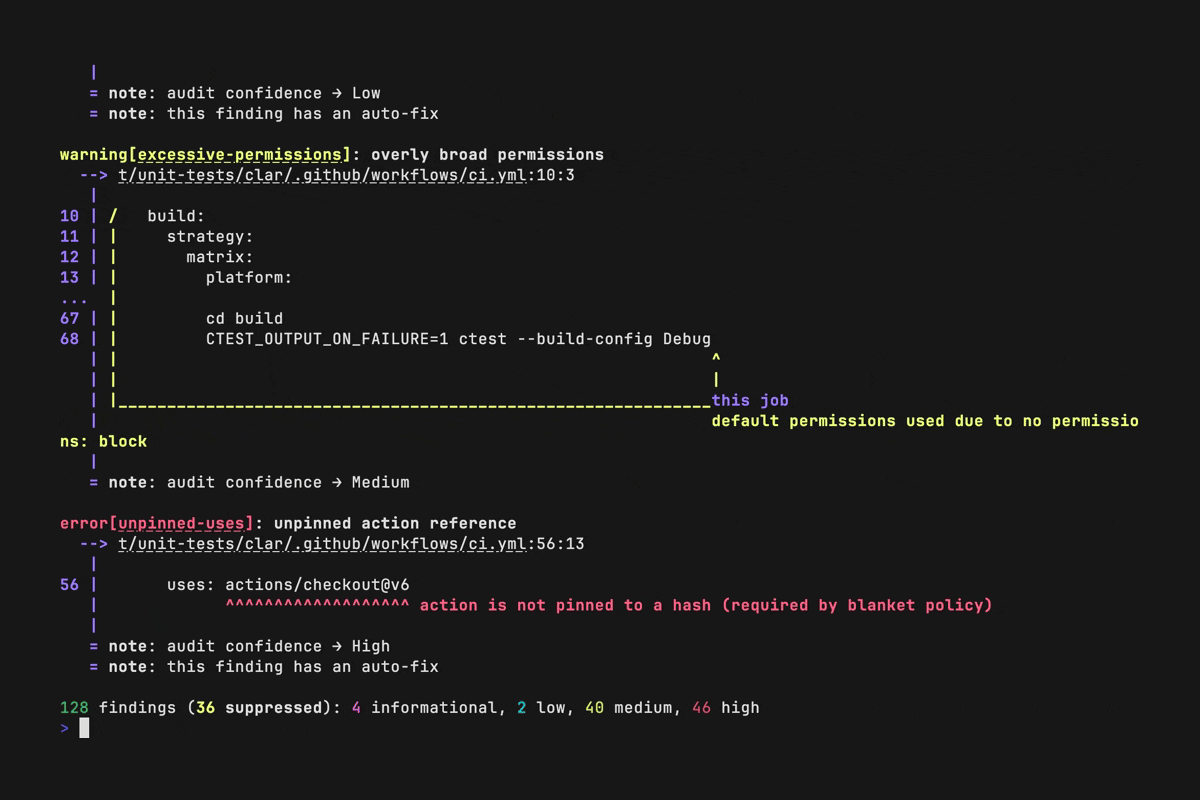 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
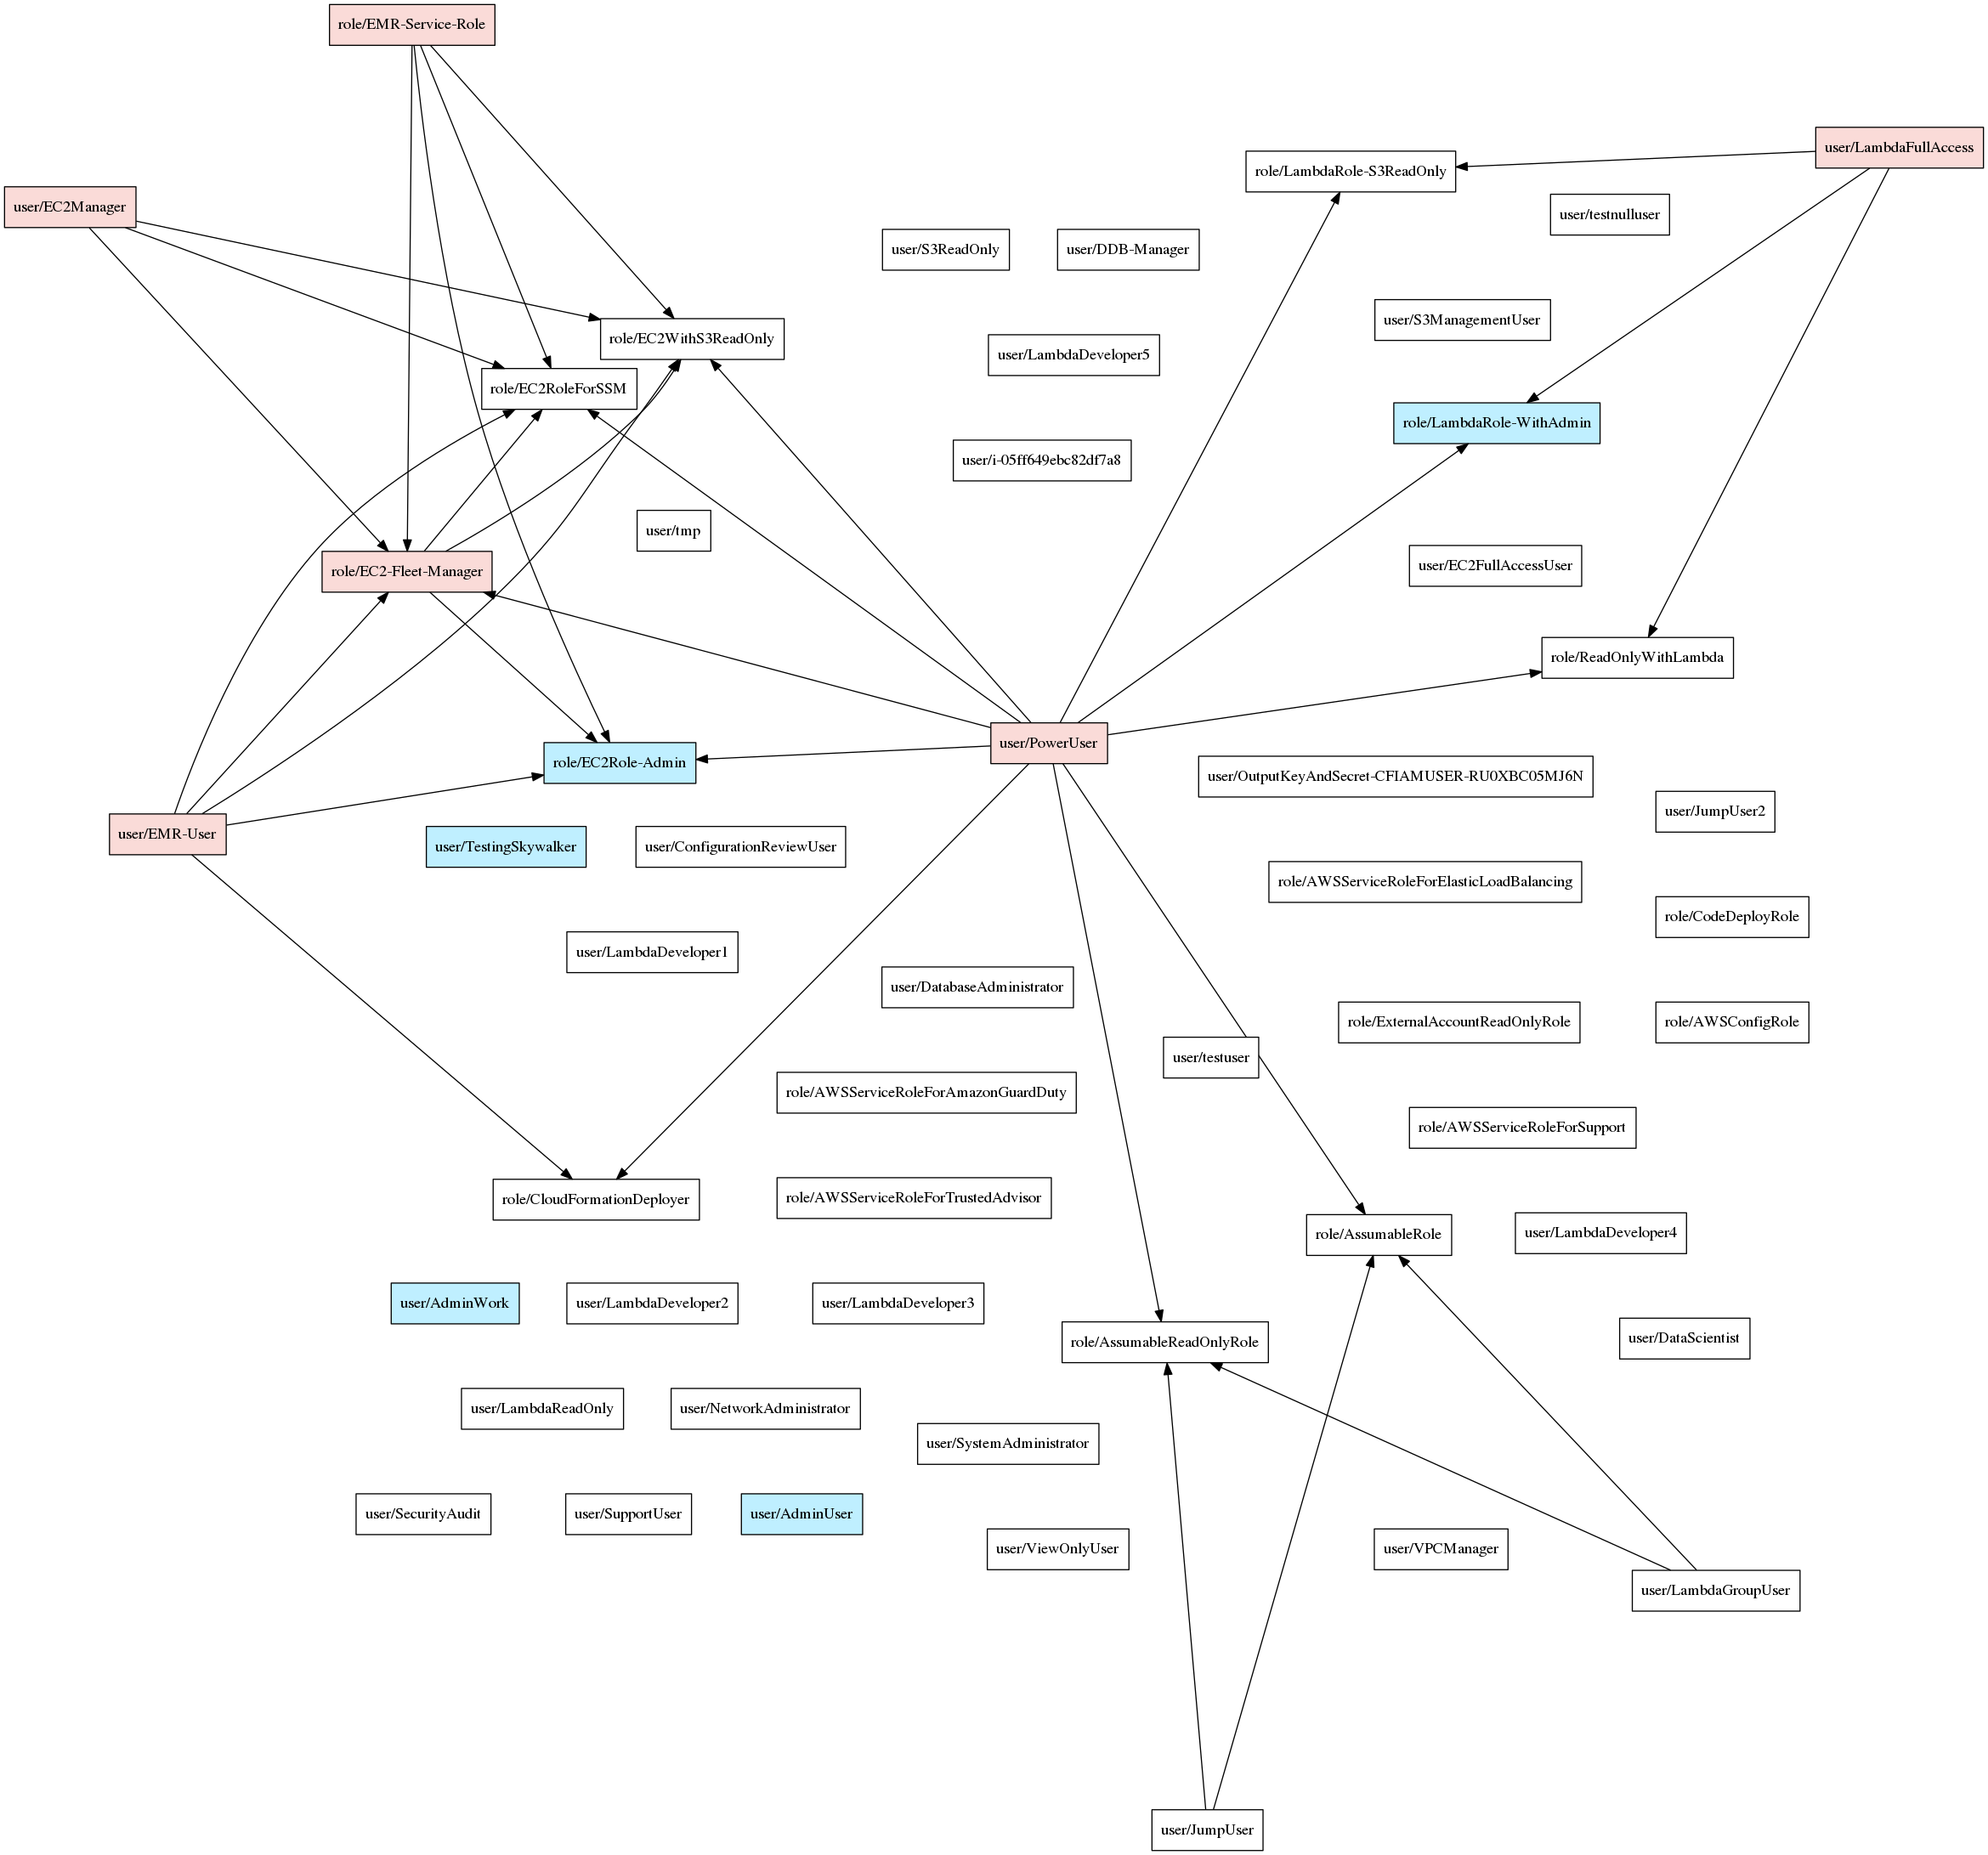 nccgroup/pmapper
A tool for quickly evaluating IAM permissions in AWS.
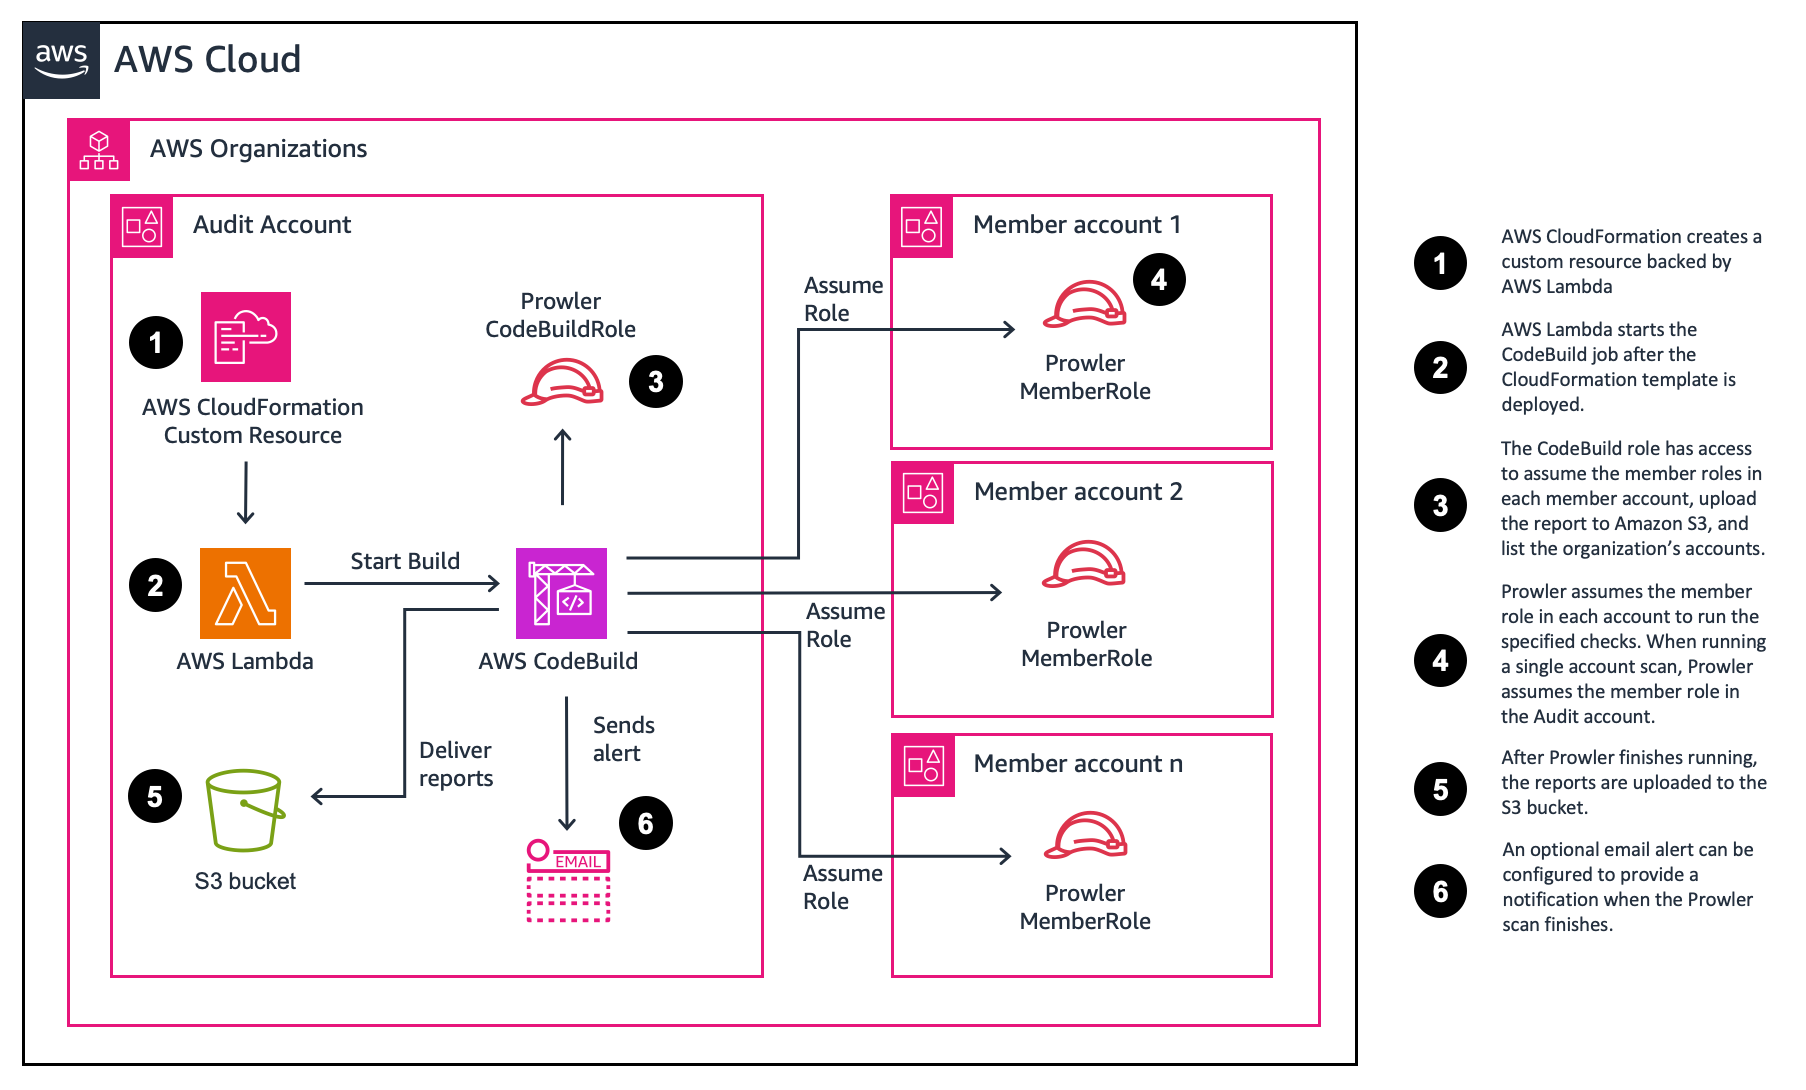 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
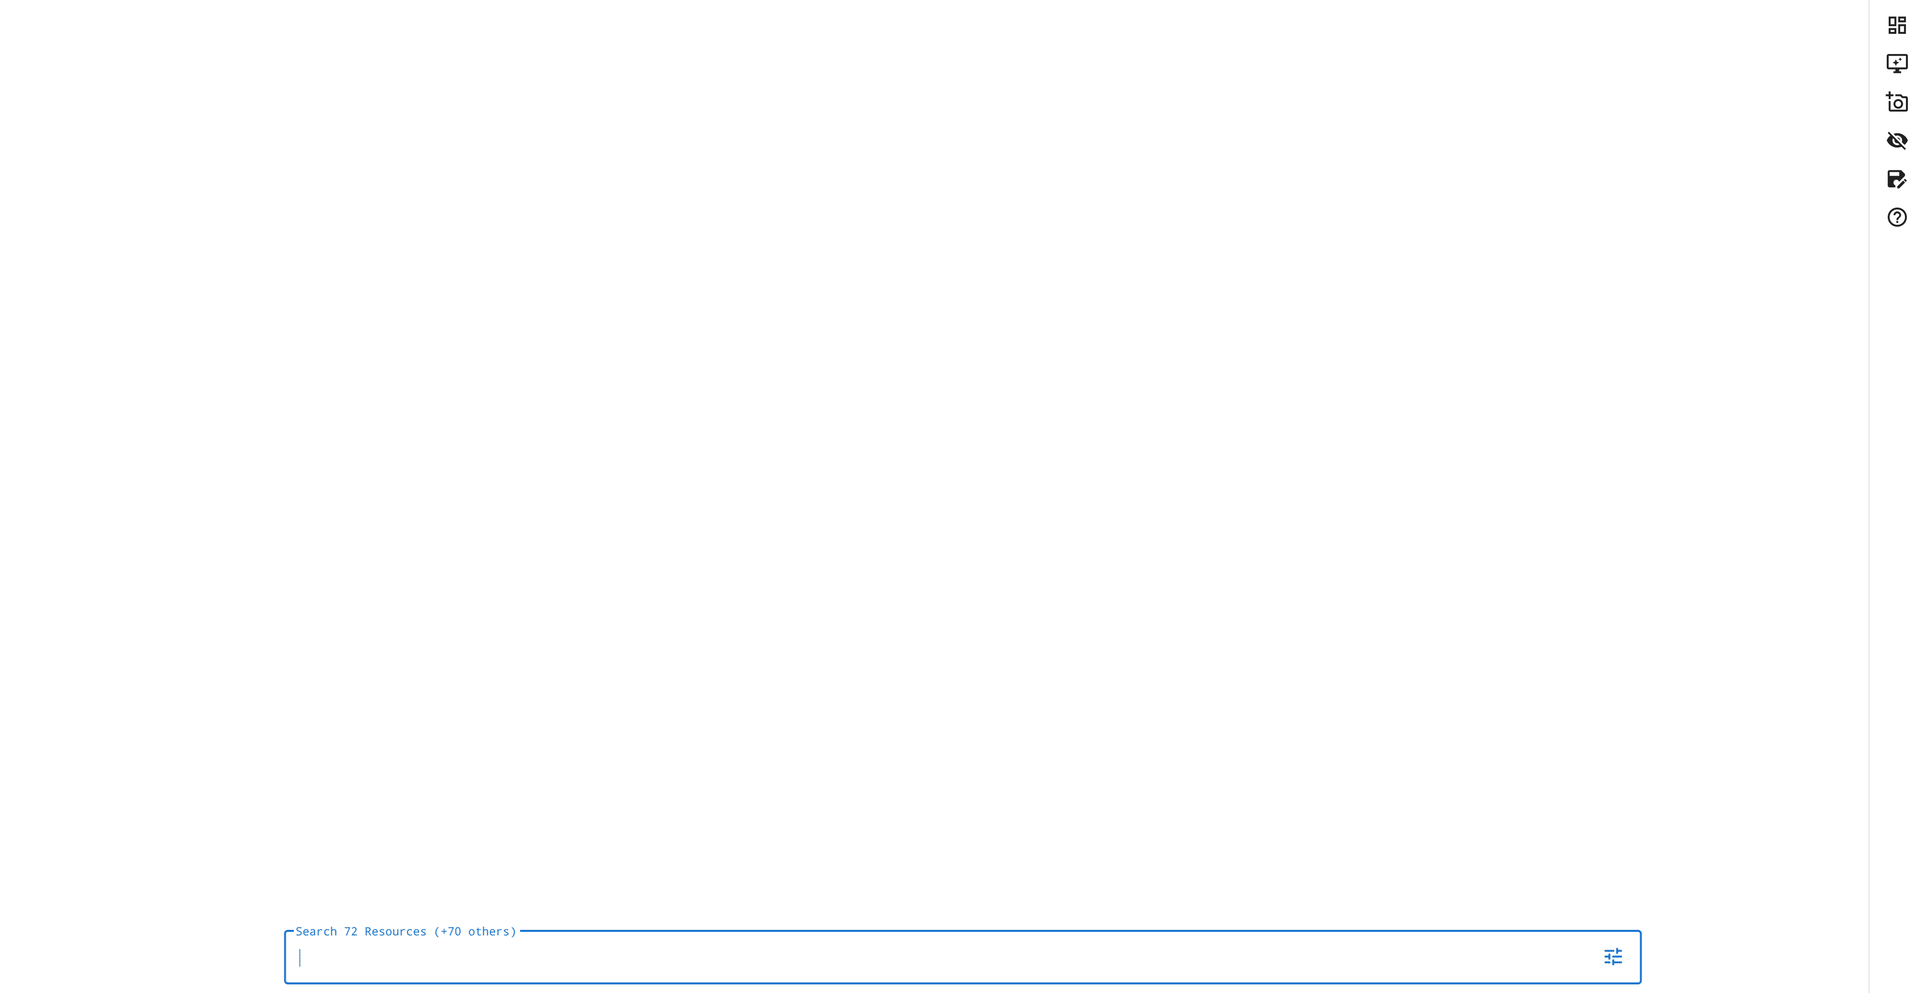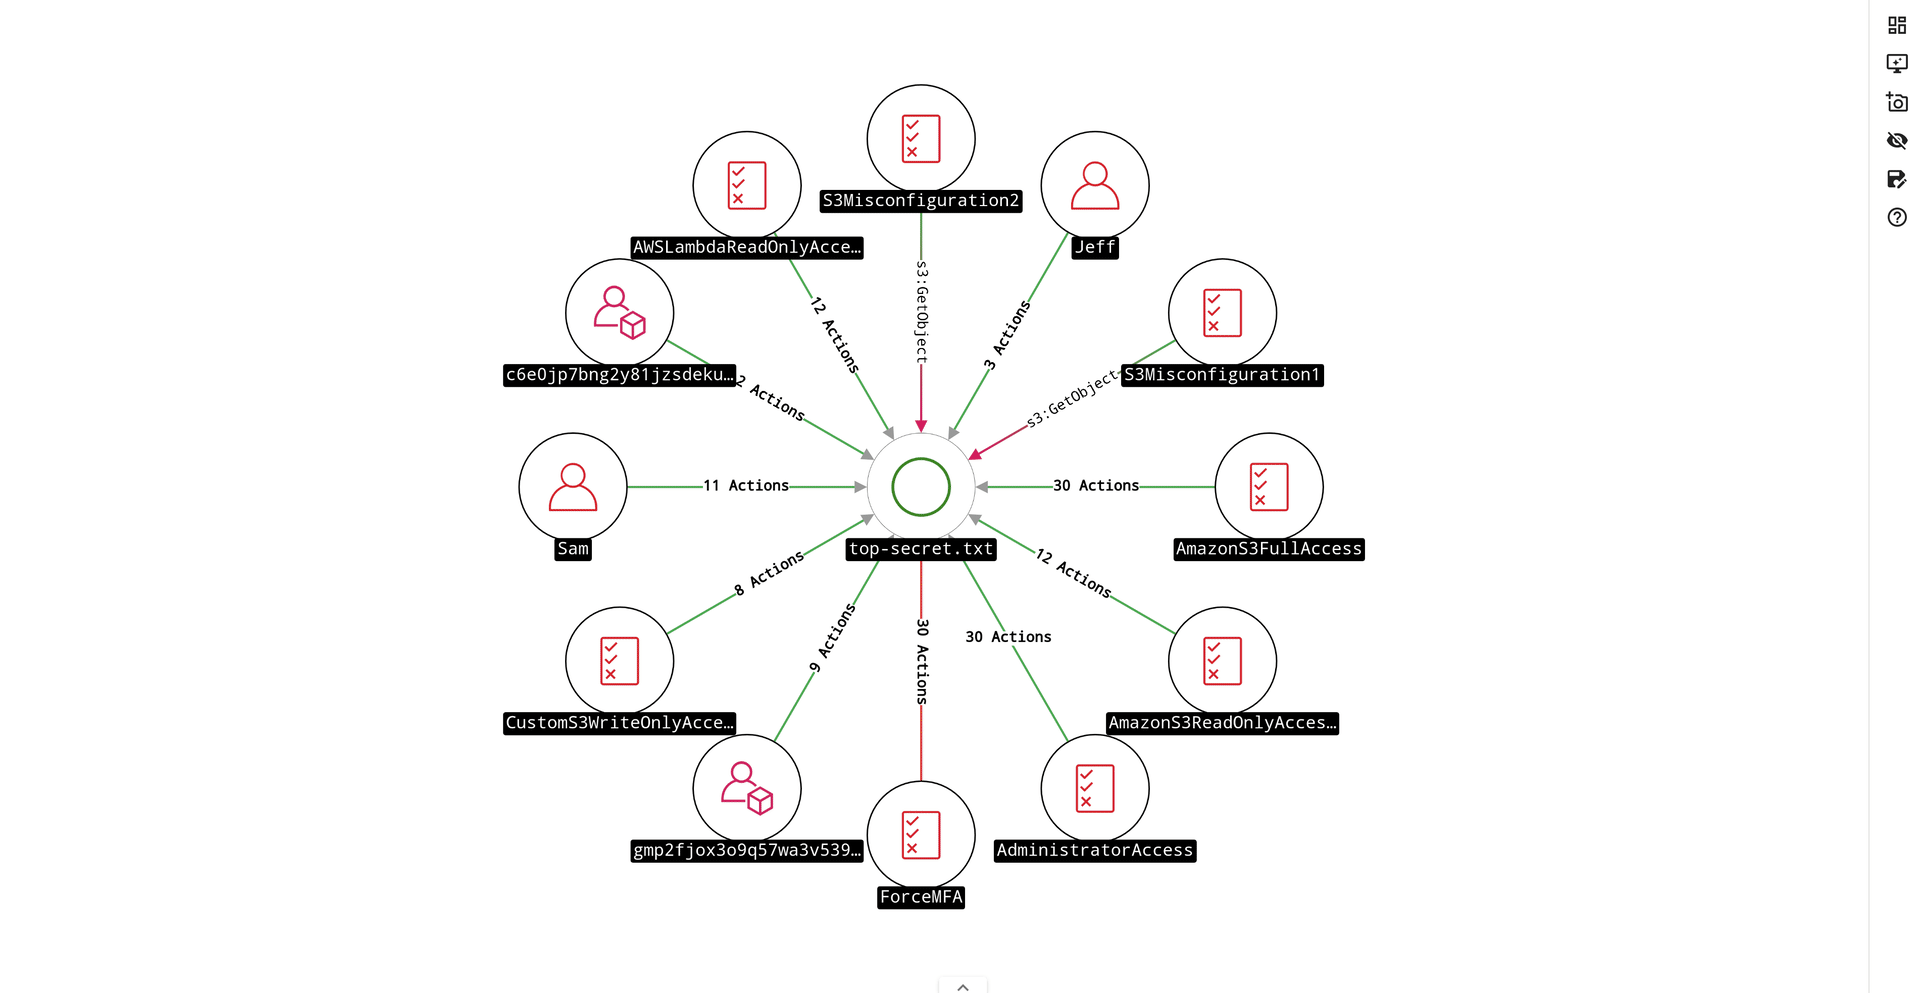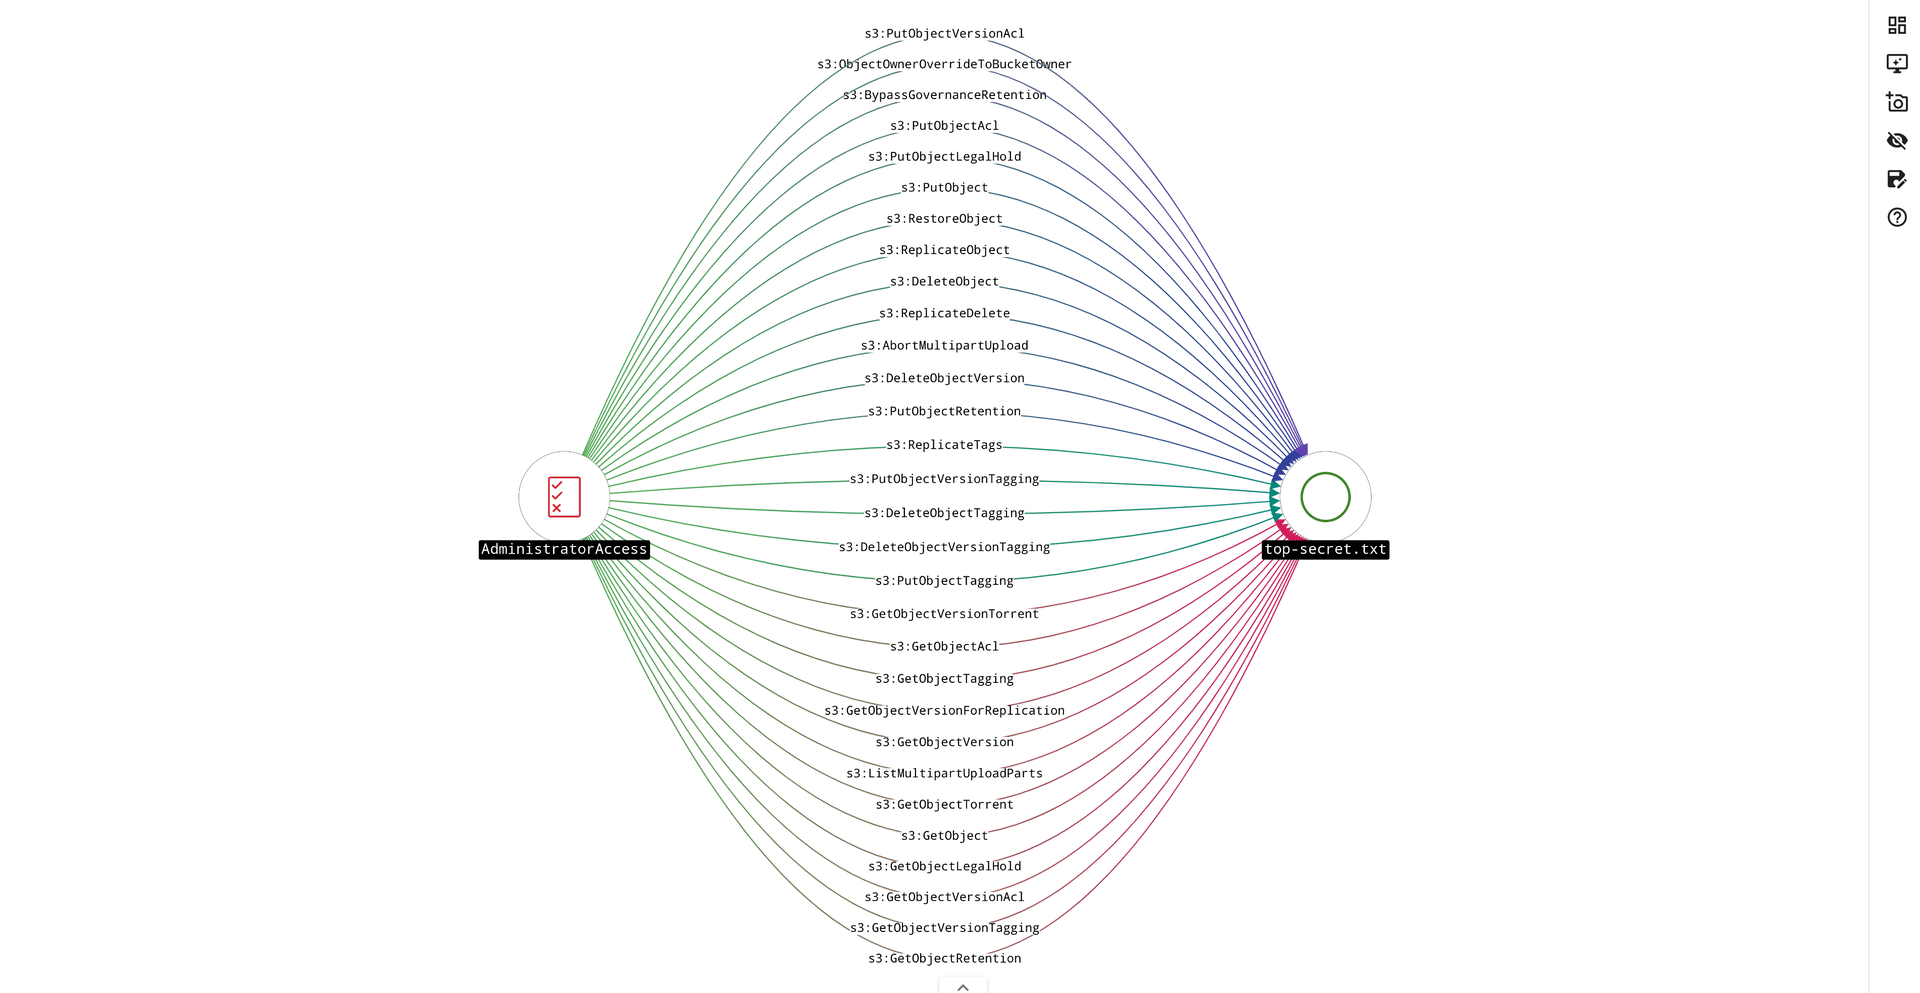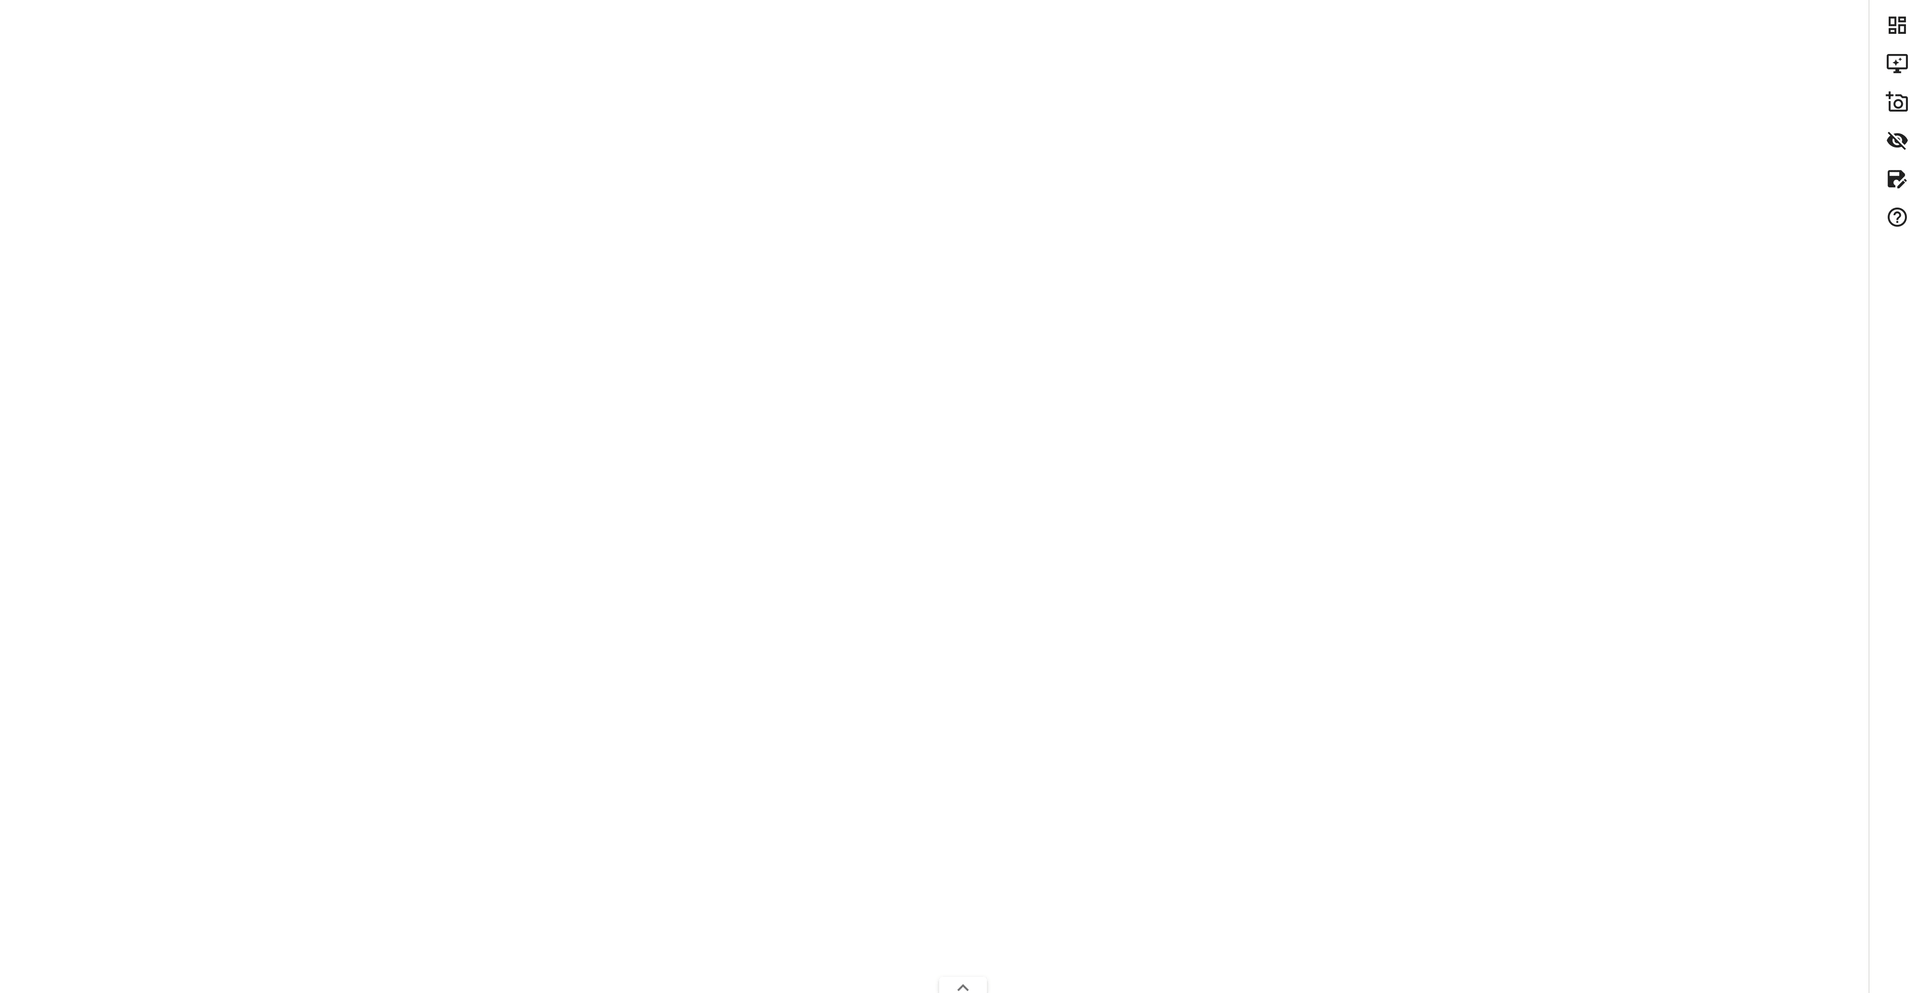 reverseclabs/awspx
A graph-based tool for visualizing effective access and resource relationships in AWS environments.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 nccgroup/aws-inventory
Discover resources created in an AWS account.
 cyberark/blobhunter
Find exposed data in Azure with this public blob scanner
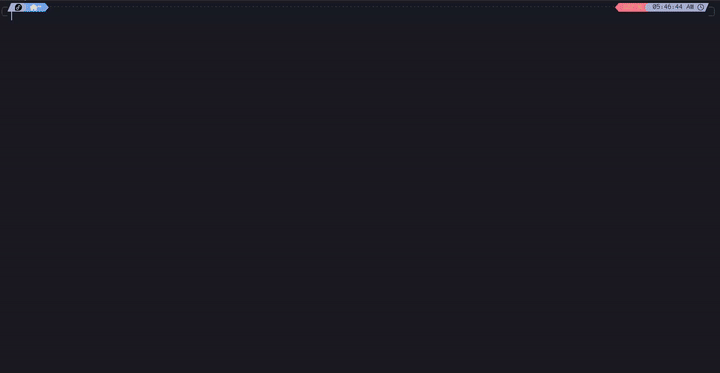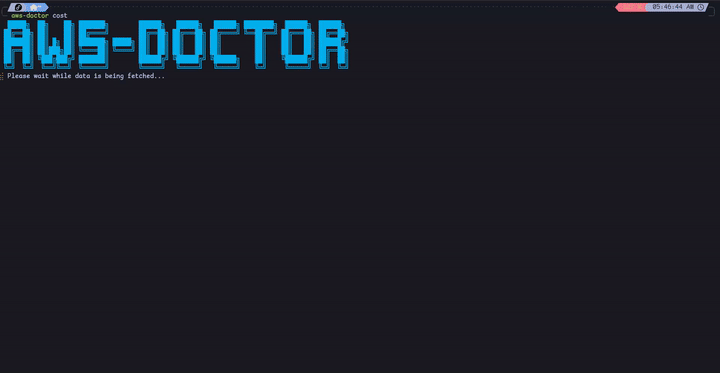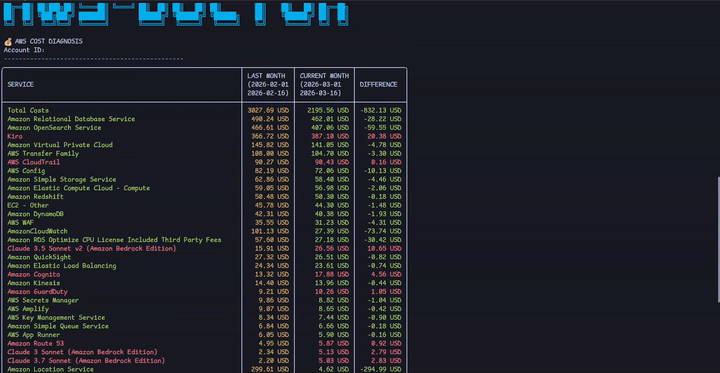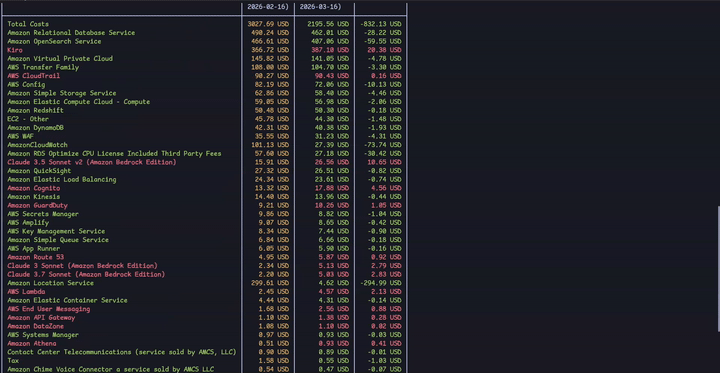 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️