

AWS-Threat-Simulation-and-Detection
 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic
adversarial-attackcloud-securityeducation+2
sbasu7241/aws-threat-simulation-and-detectionPlaying around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic
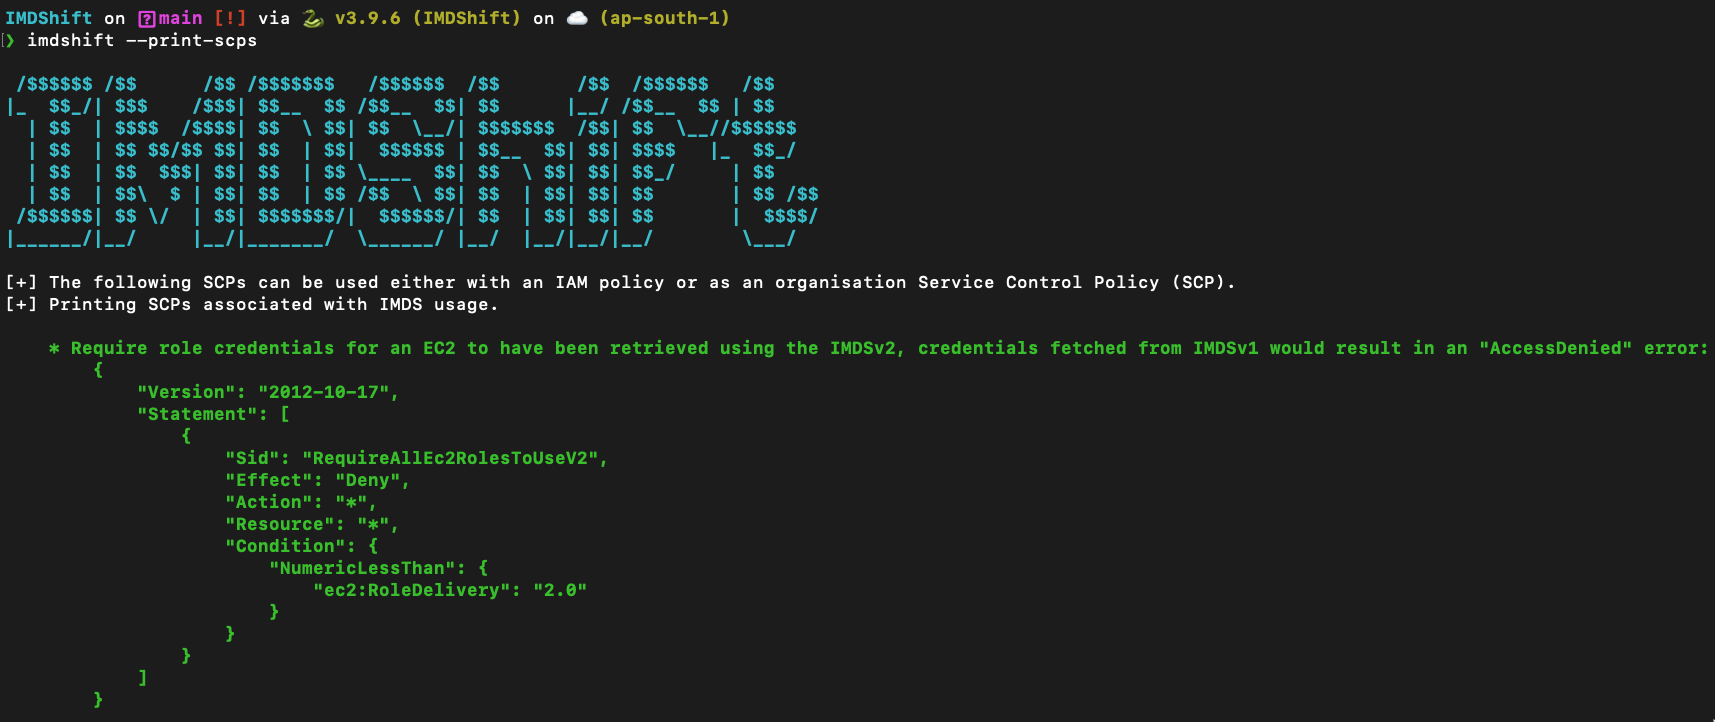 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
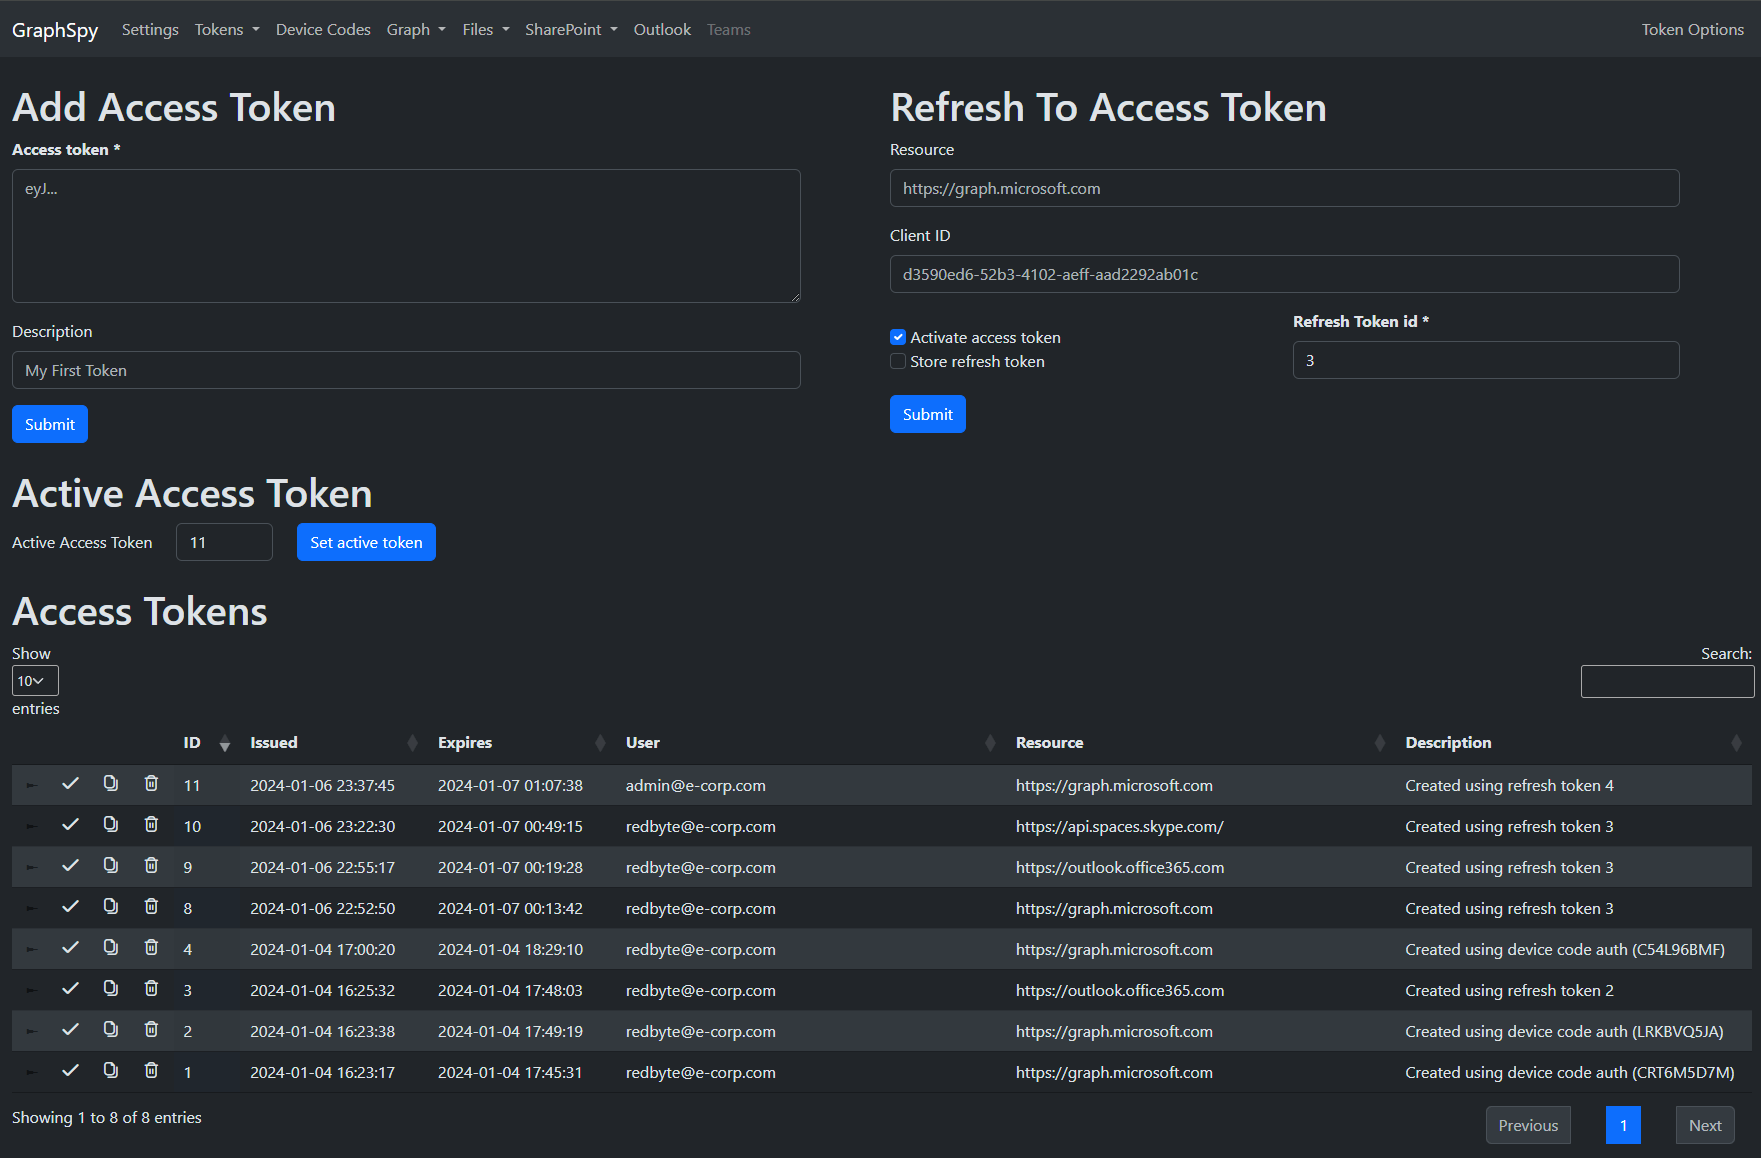 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.
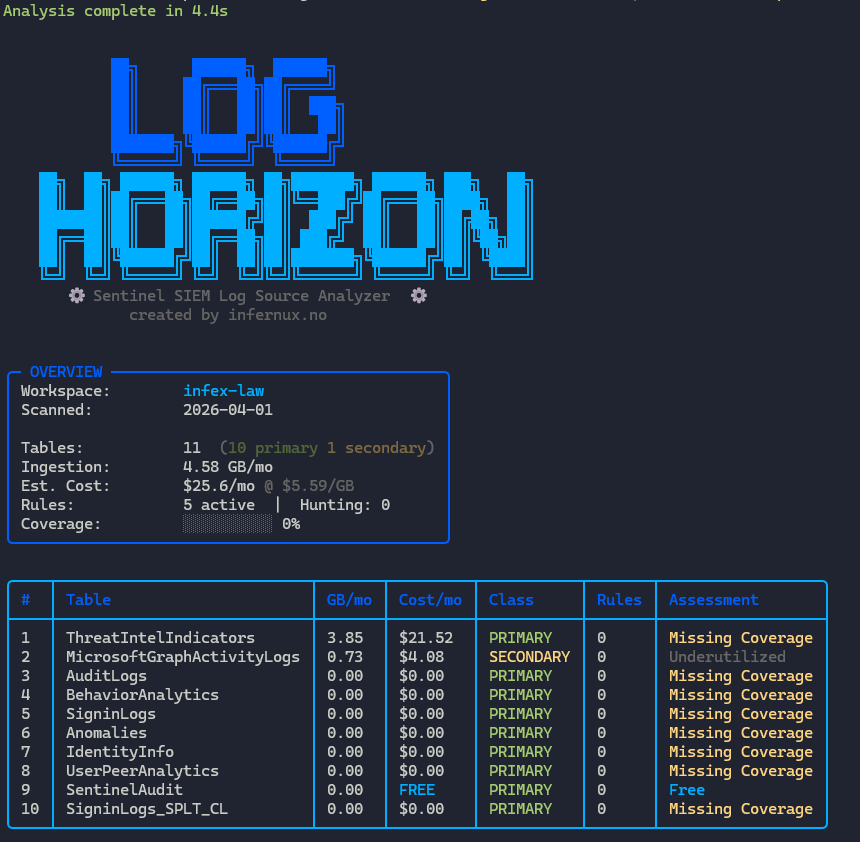 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 trickyearlobe/inspec-log4j
An Inspec profile to check for Log4j CVE-2021-44228 and CVE-2021-45046
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 bgeesaman/subpath-exploit
Writeup of CVE-2017-1002101 with sample "exploit"/escape
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 ololadeabiola03/aisecplus-week01-servicenow-ai-security-incident
Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 treebuilder/aad-sso-enum-brute-spray
POC of SecureWorks' recent Azure Active Directory password brute-forcing vuln
 bishopfox/dufflebag
Search exposed EBS volumes for secrets
 shabarkin/aws-enumerator
Read-only AWS service enumerator with 600+ API calls for cloud reconnaissance, info dumping, and result analysis during penetration testing.
 securisec/cliam
Cloud agnostic IAM permissions enumerator