
AWS-Key-Hunter
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
cloud-securitycode-analysisinformation-gathering+2
39
iamlucif3r/aws-key-hunter[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 mr-xn/cve-2023-28432
CVE-2023-28434 nuclei templates
 whiteoaksecurity/goawsconsolespray
Tool to spray AWS Console IAM Logins
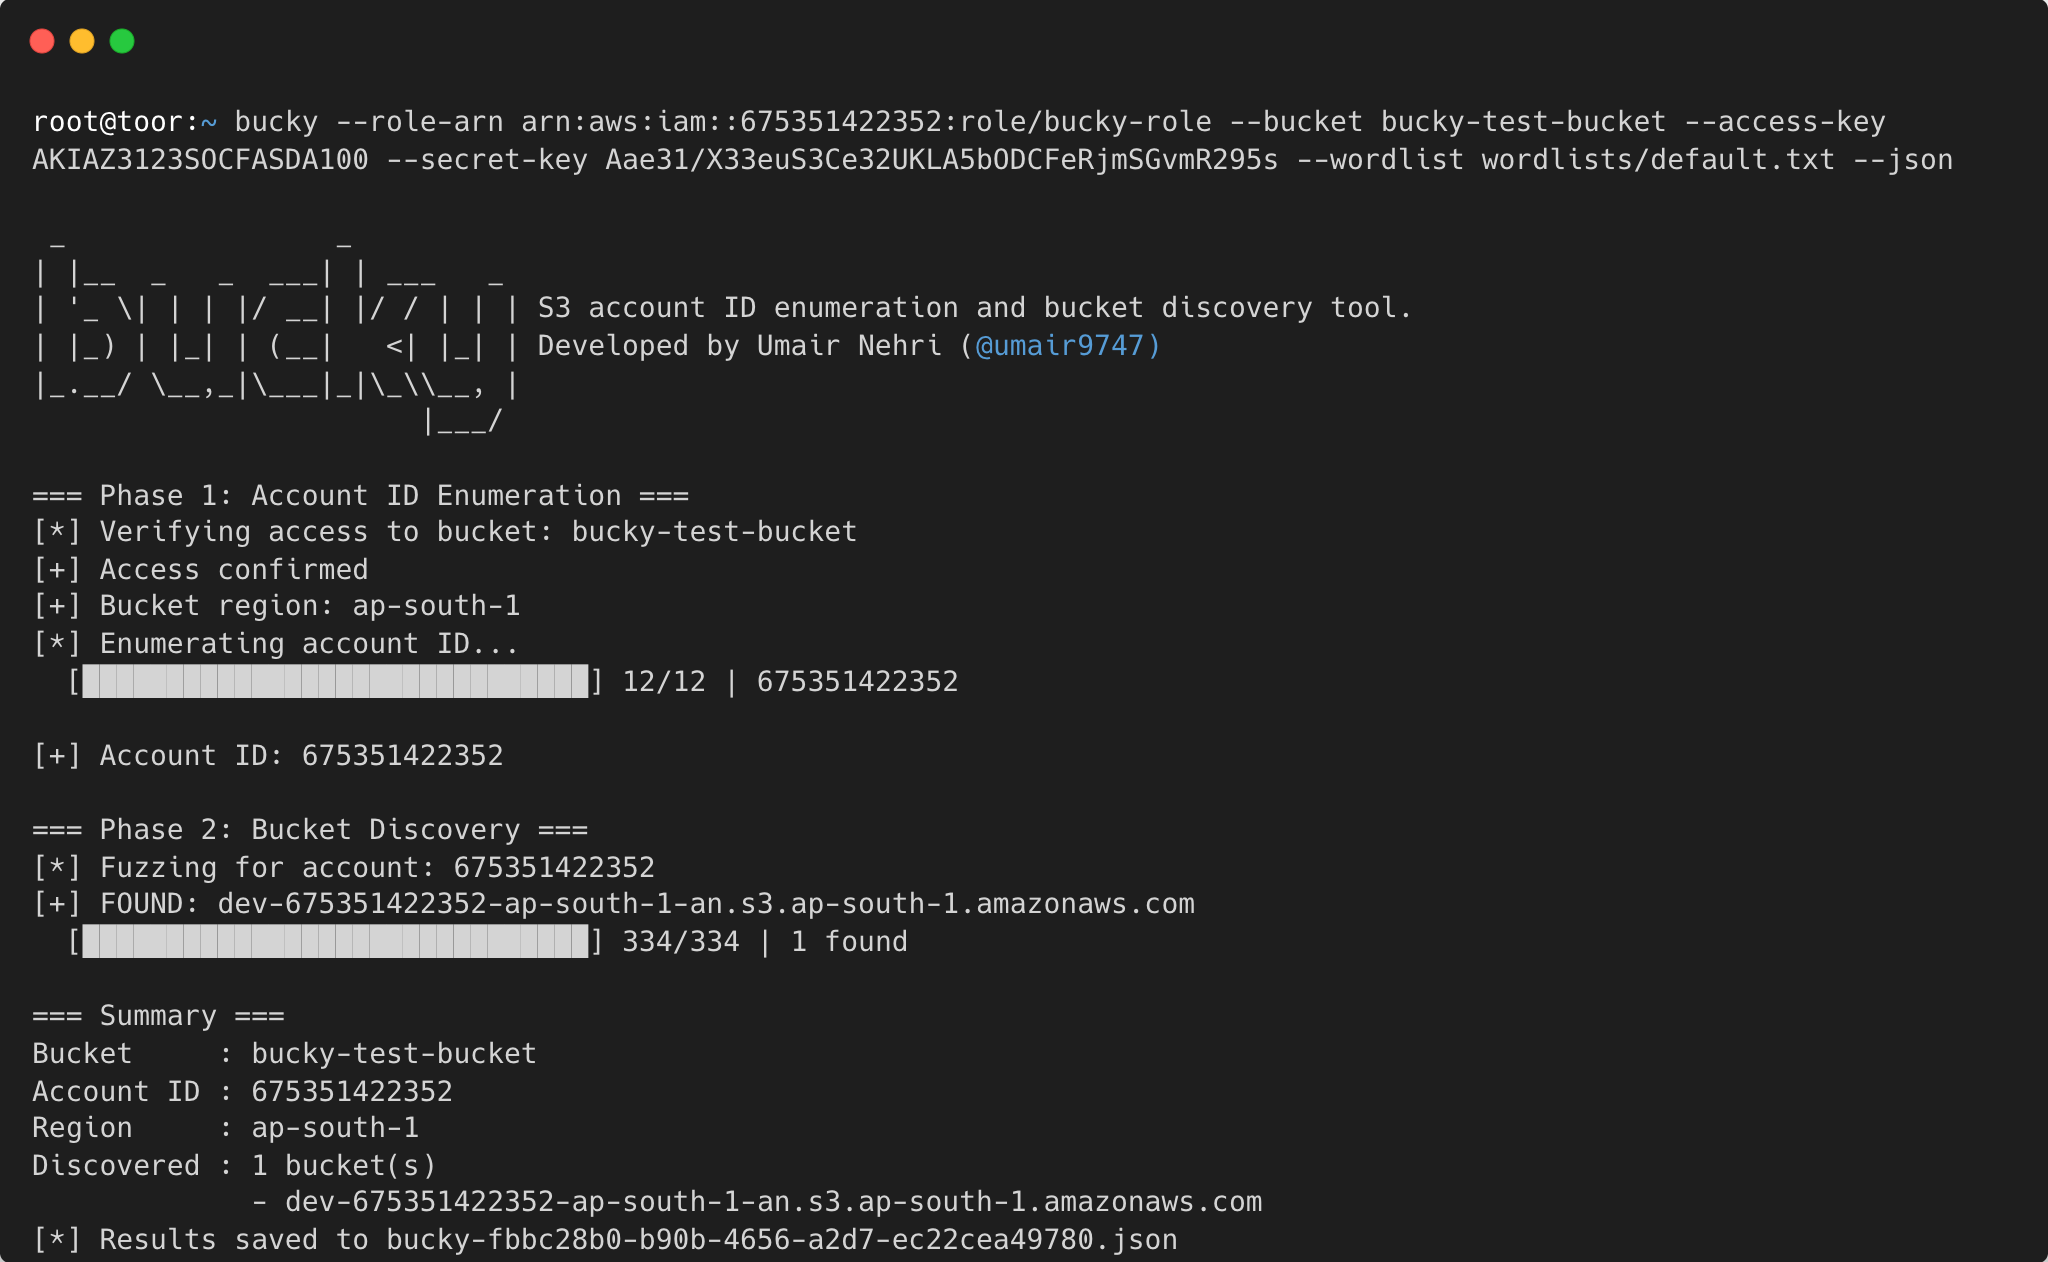 umair9747/bucky
An S3 account ID enumeration and bucket discovery tool
 marcosimioni/omigood
OMIGOD! OM I GOOD? A free scanner to detect VMs vulnerable to one of the "OMIGOD" vulnerabilities discovered by Wiz's threat research team,…
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 acheiii/cve-2023-28432
CVE-2023-28432 POC
 gobysec/cve-2023-28432
Exploit for CVE-2023-28432, a sensitive information disclosure vulnerability in MinIO's verify interface, allowing attackers to read system…
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 murataydemir/cve-2021-21975
[CVE-2021-21975] VMware vRealize Operations Manager API Server Side Request Forgery (SSRF)
 isee857/cve-2025-27817
Apache Kafka客户端未对用户输入进行严格验证和限制,未经身份验证的攻击者可通过构造恶意配置读取环境变量或磁盘任意内容,或向非预期位置发送请求,提升REST API的文件系统/环境/URL访问权限。
 stolichnayer/cve-2025-22828
Apache CloudStack vulnerability allows unauthorized access to annotations on certain resources.
 epsylon/prommetrix
Prommetrix can obtain relevant information from the instances of 'Node Exporter' executed by 'Prometheus'.
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 abdugafforov-bobur/cve-2026-67620-poc
CVE-2026-67620 - Flowise SSRF via incomplete cloud-metadata deny-list (Oracle OCI 192.0.0.192 + Alibaba 100.100.100.200 bypass the DEFAULT_DENY_LIST)