AWSTESTEXPLOIT
 catnip-express-maxim/awstestexploit
Testing if AWS exploit CVE-2025-2598 still works
cloud-securityexploitationpenetration-testing+2
catnip-express-maxim/awstestexploitTesting if AWS exploit CVE-2025-2598 still works
 skasanagottu57gmailv/gerhart01
CVE-2020-0890 | Windows Hyper-V Denial of Service Vulnerability proof-of-concept code
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 mondoohq/installer
Linux, macOS and Windows Install scripts for cnquery & cnspec
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 williavs/nextjs-security-update
Batch upgrade all your Next.js apps to patched versions - fight back against CVE-2025-55183/55184/67779
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
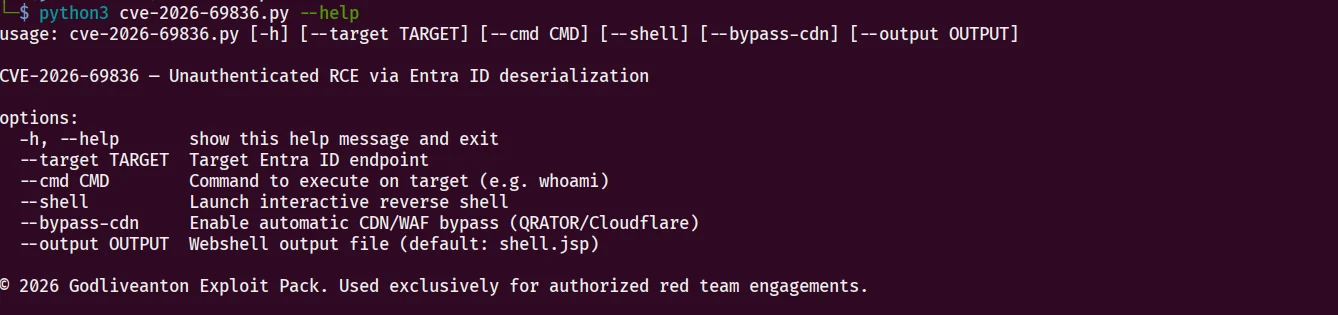 sentinel-aidefense/cve-2026-69836-exp
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization
 pavilionq/cve-2023-33246-mitigation
Maven-based demonstration of CVE-2023-33246 mitigation for Apache RocketMQ, featuring attack testing and enhanced parameter validation to prevent…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
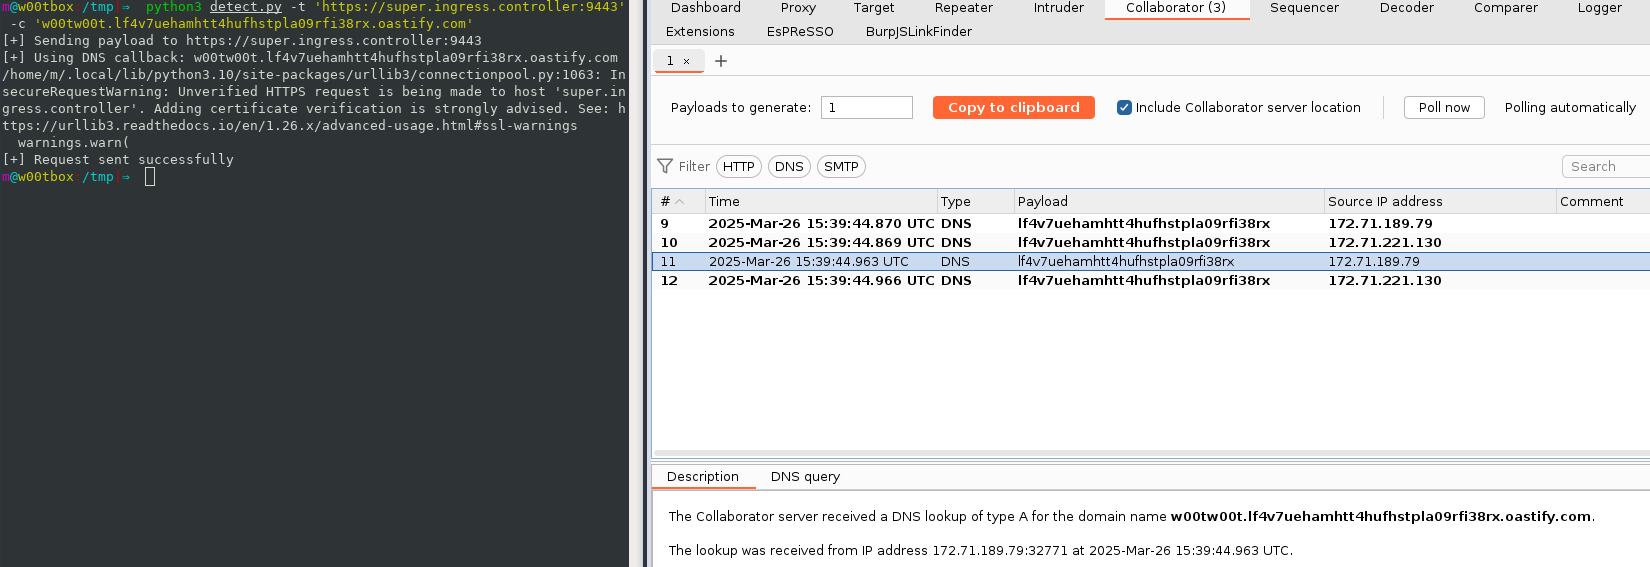 m-q-t/ingressnightmare-detection-poc
Proof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
 devsecopsdocs/nuclearpond
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 gdatasoftwareag/vaas
Verdict-as-a-Service SDKs: Analyze files for malicious content
 smaranchand/bucky
Bucky (An automatic S3 bucket discovery tool)
 oligocybersecurity/shelltorchchecker
A tool that checks if a TorchServe instance is vulnerable to CVE-2023-43654
 kingofbugbounty/nuclearpond-ofjaaah
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.