
PentestingEverything
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
api-securitycloud-securityctf+9
2.1k
m14r41/pentestingeverythingComplete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 bridgecrewio/terragoat
Intentionally vulnerable Terraform infrastructure for learning cloud misconfiguration detection and DevSecOps practices across AWS, Azure, and GCP.
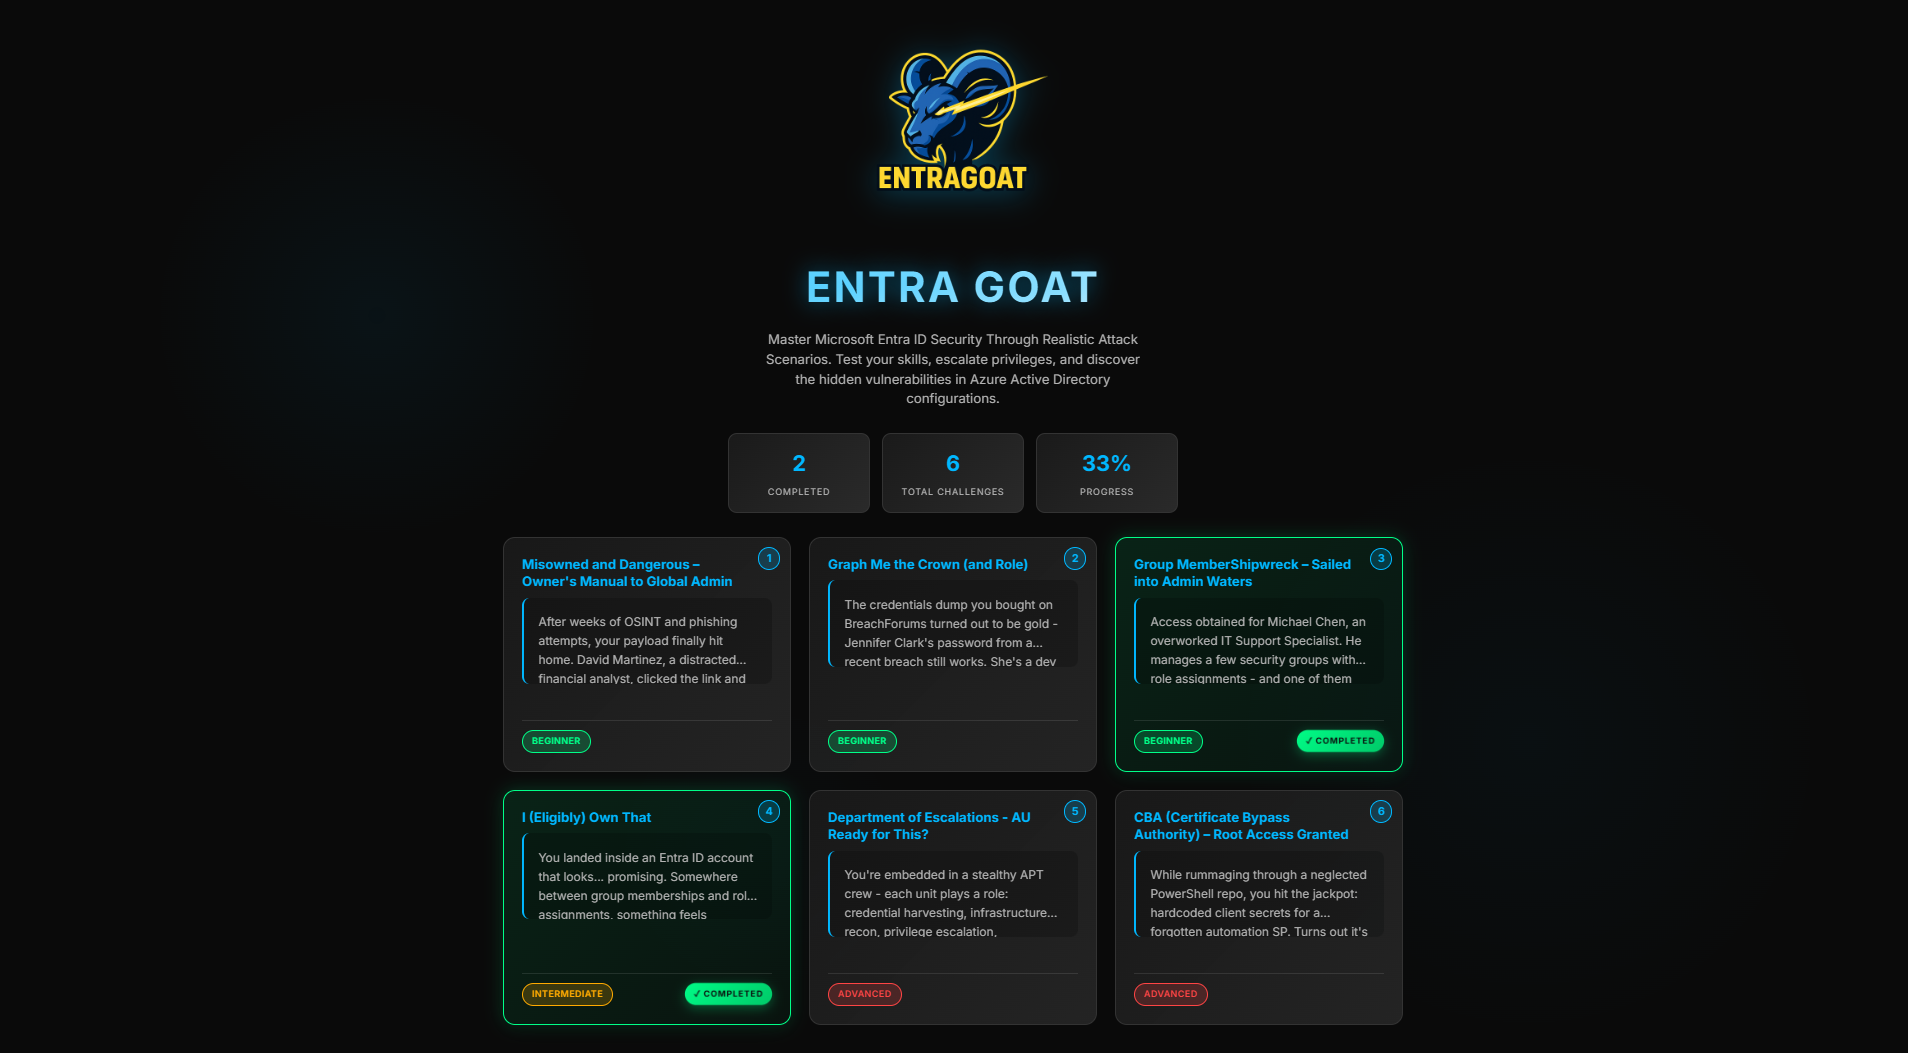 semperis/entragoat
A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges.
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
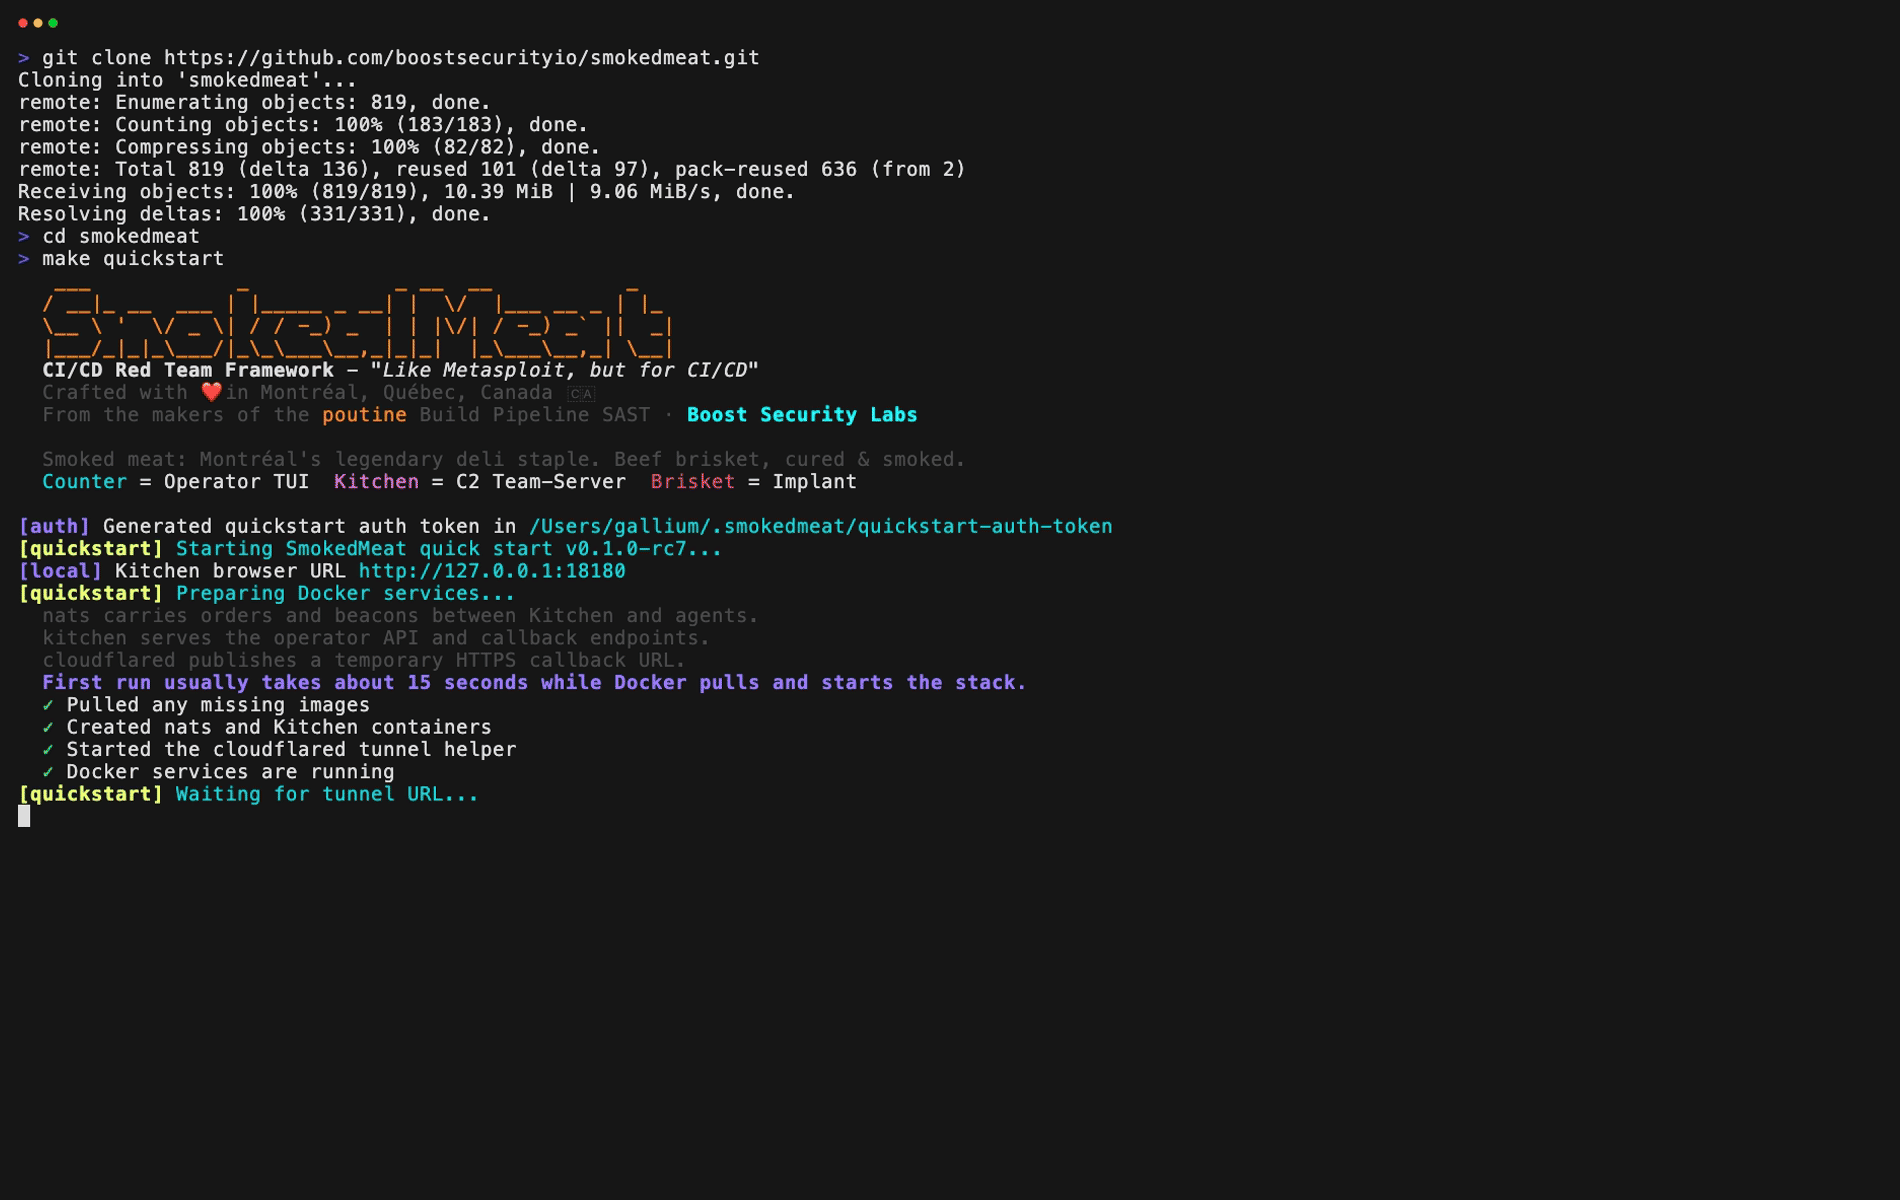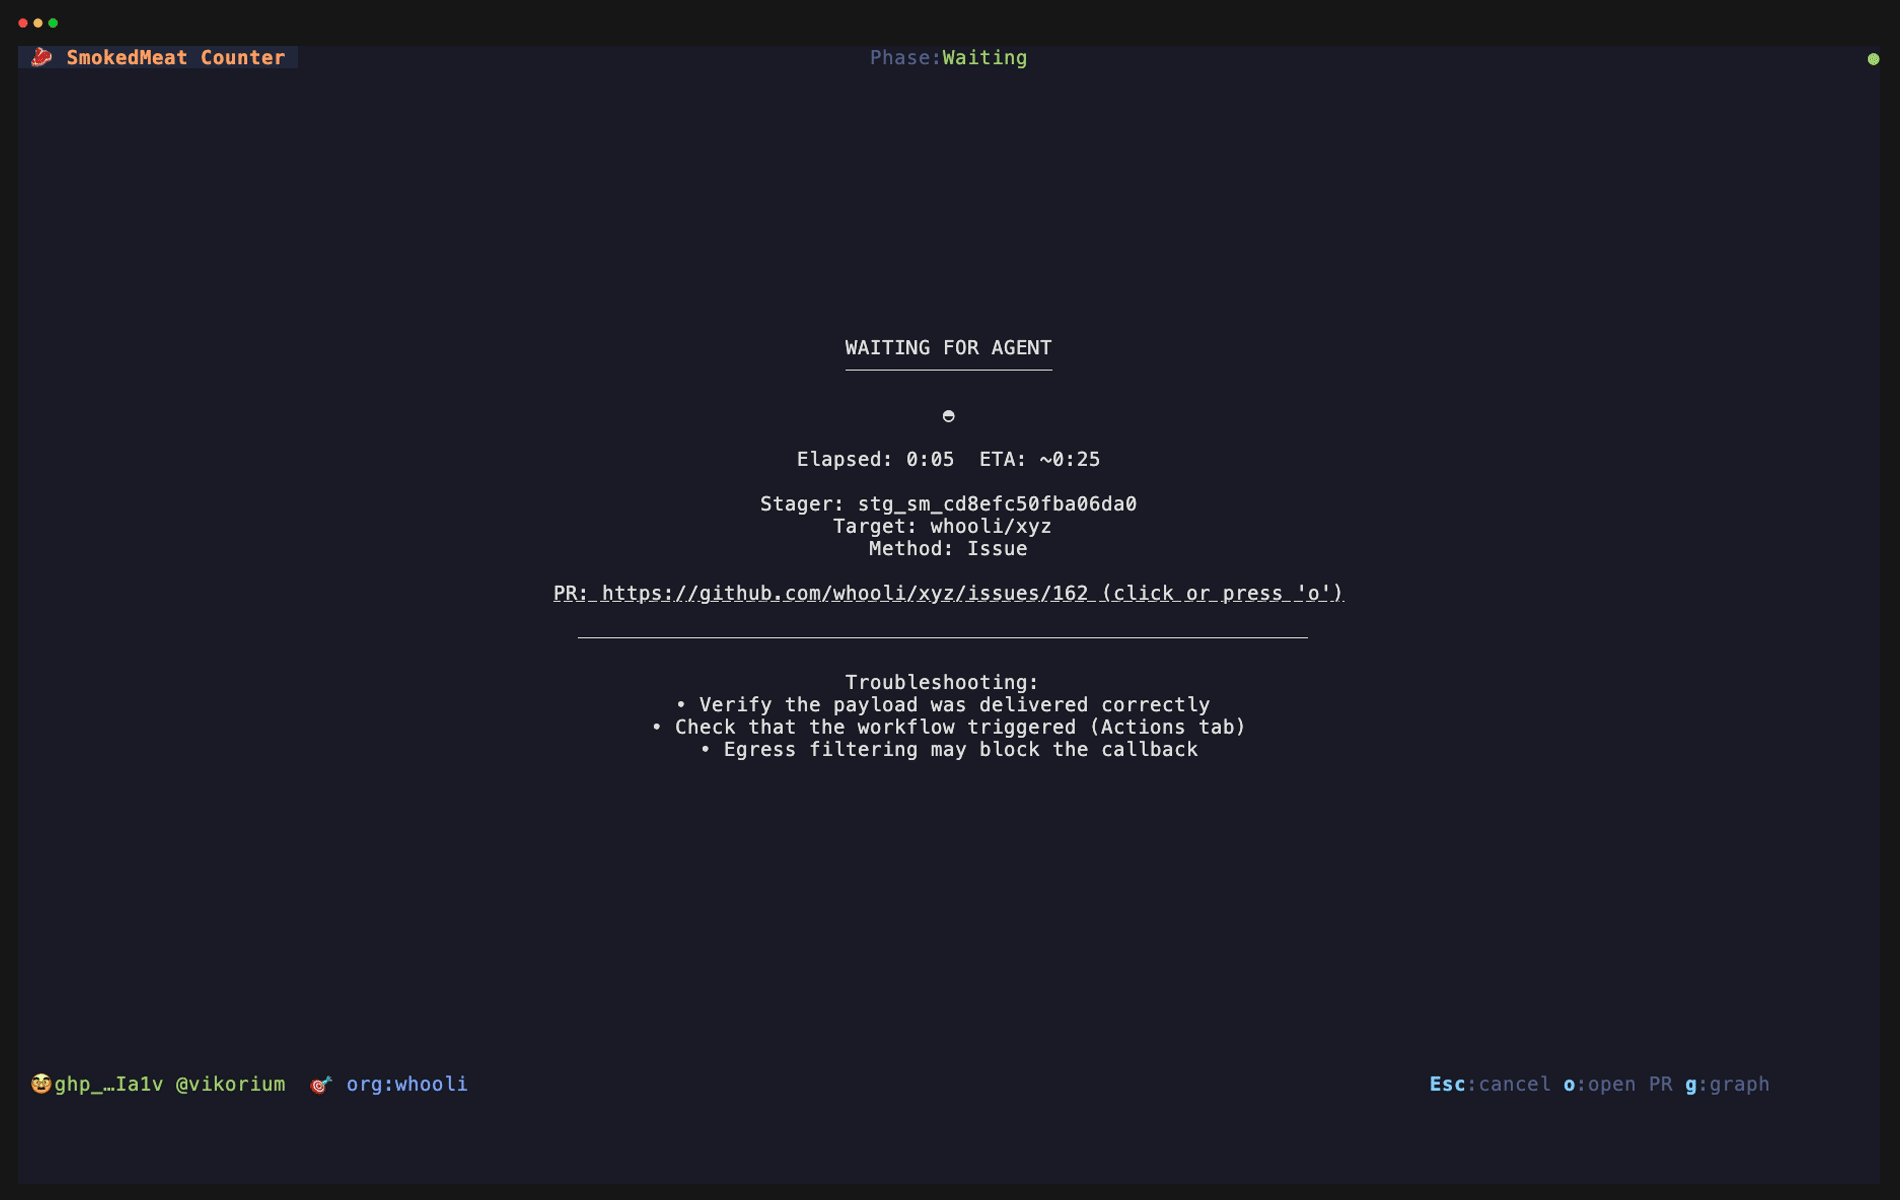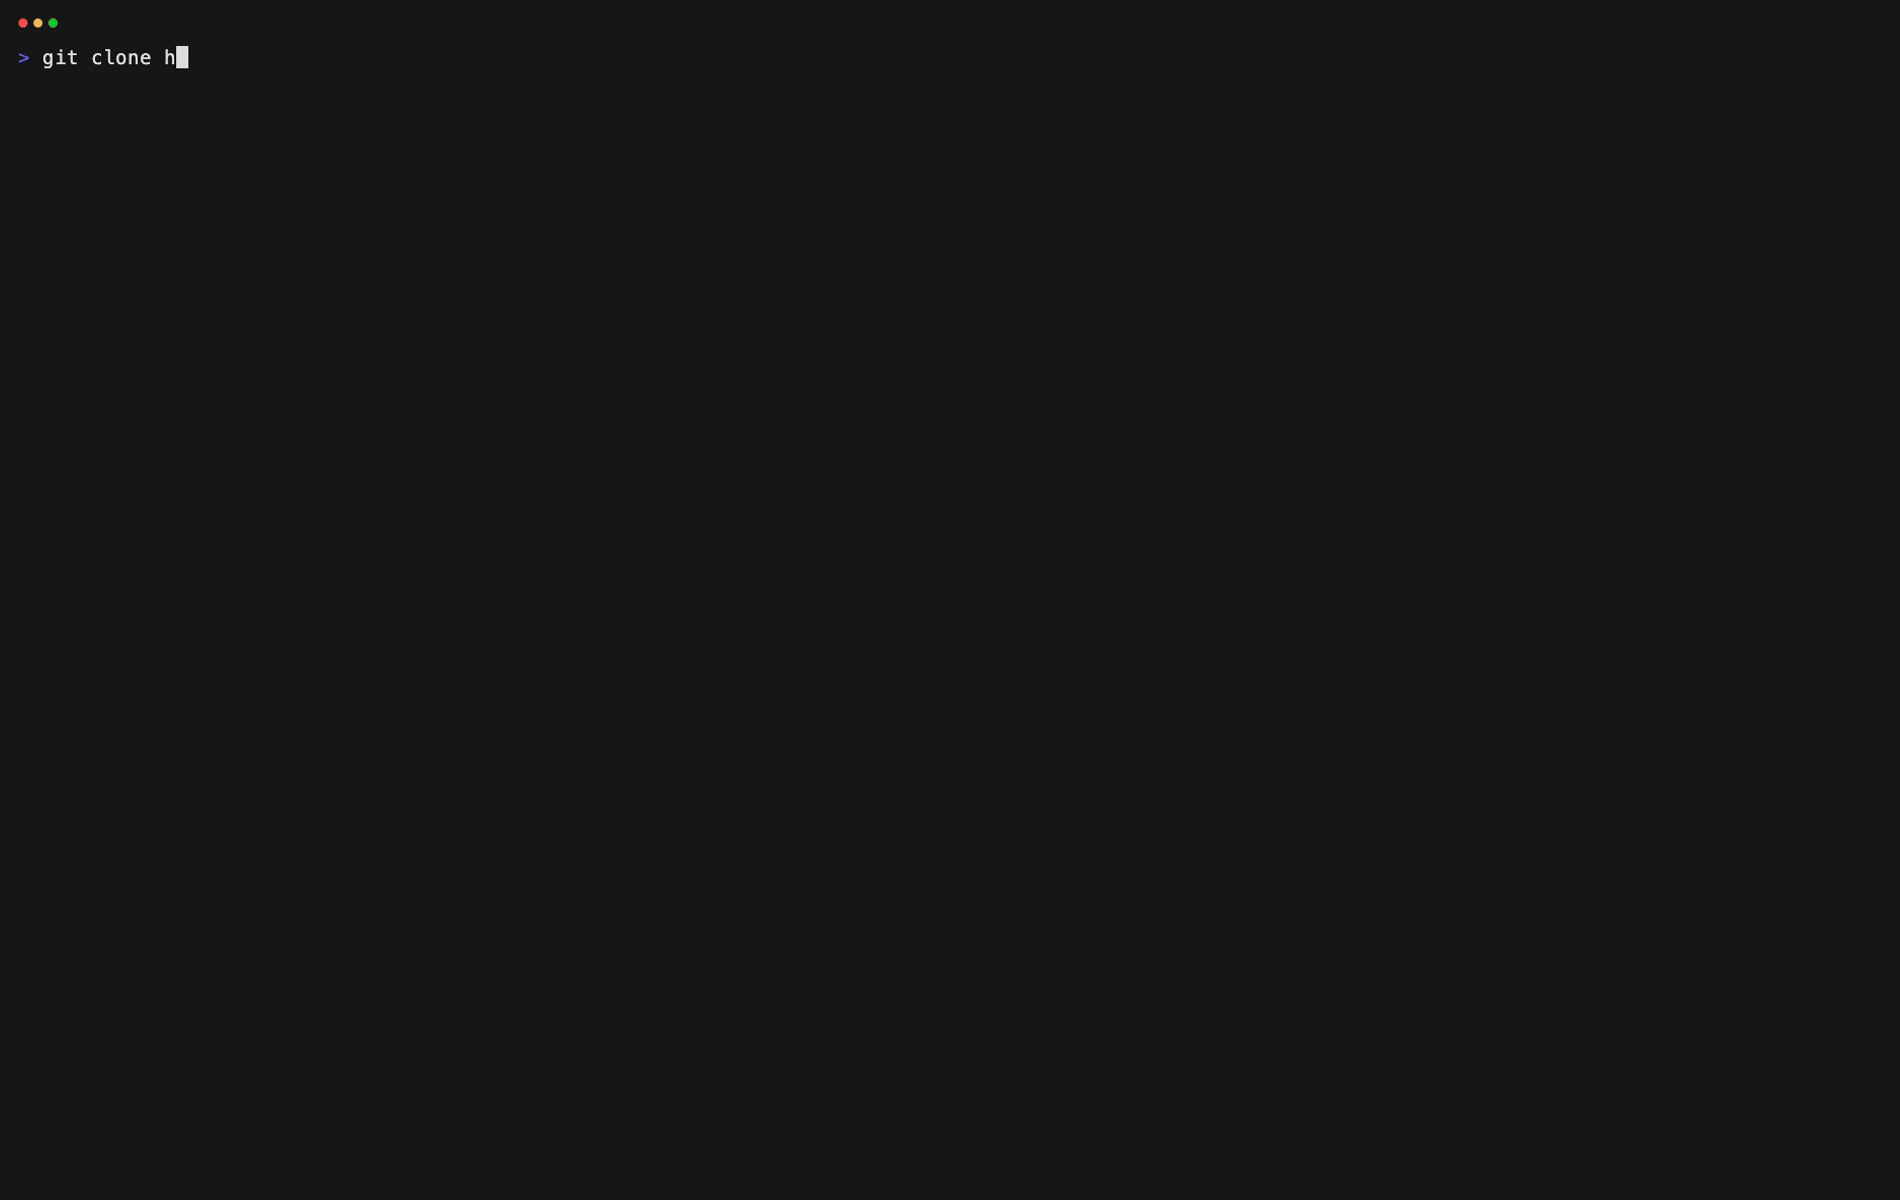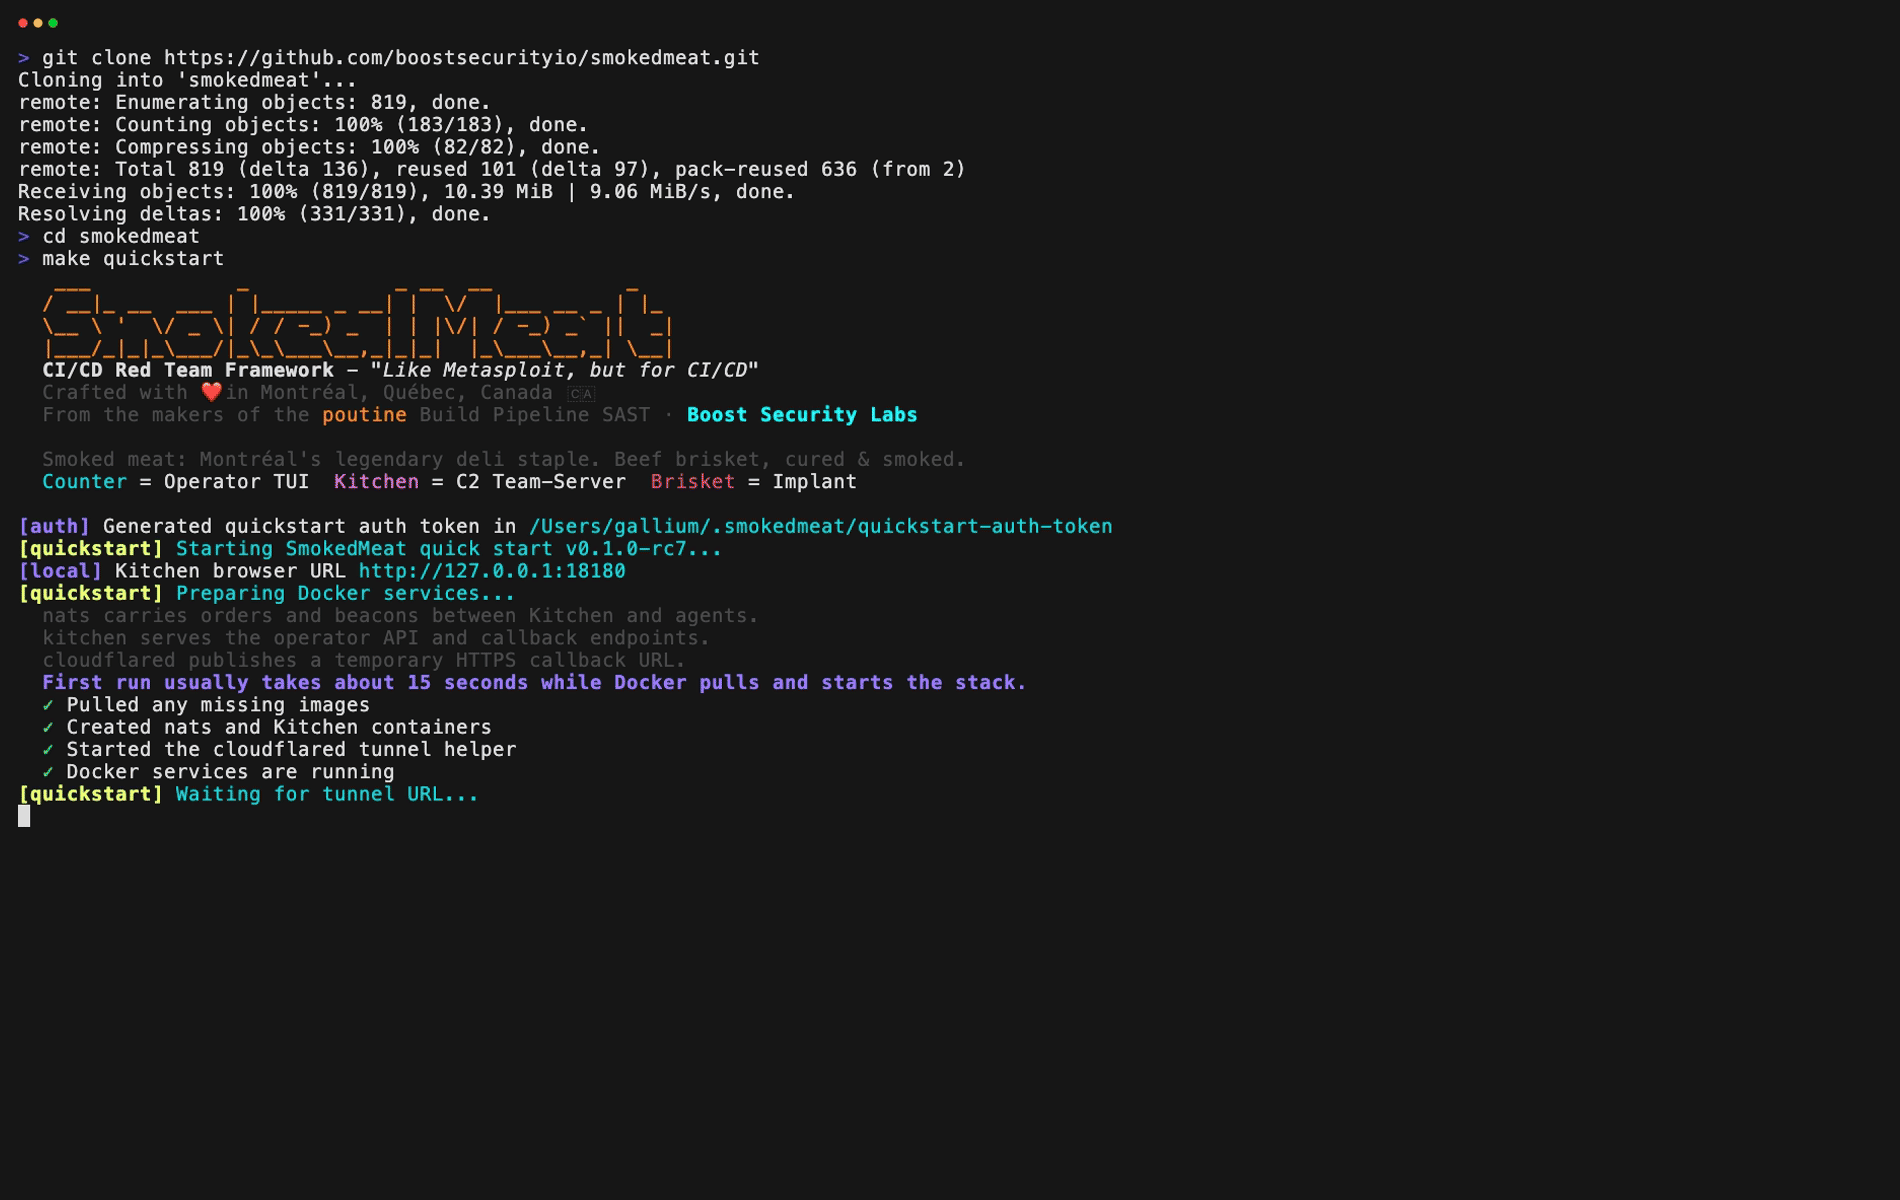 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
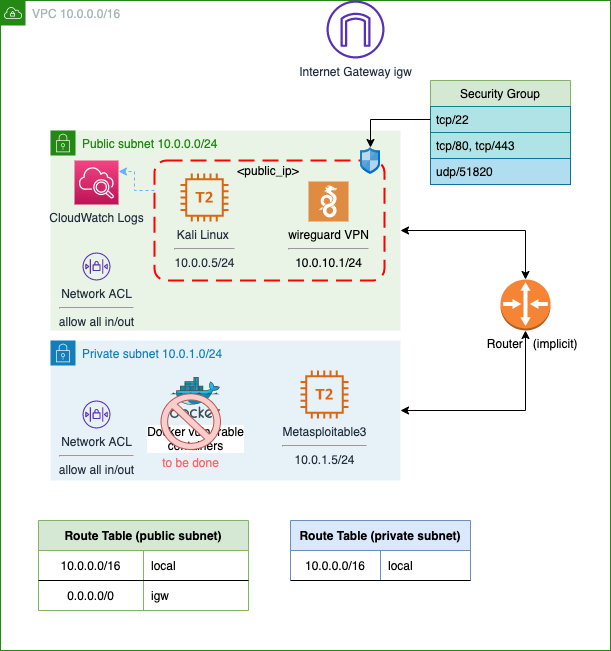 juanjosanz/aws-pentesting-lab
Pentesting lab with a Kali Linux instance accessible via ssh & wireguard VPN and with vulnerable instances in a private subnet
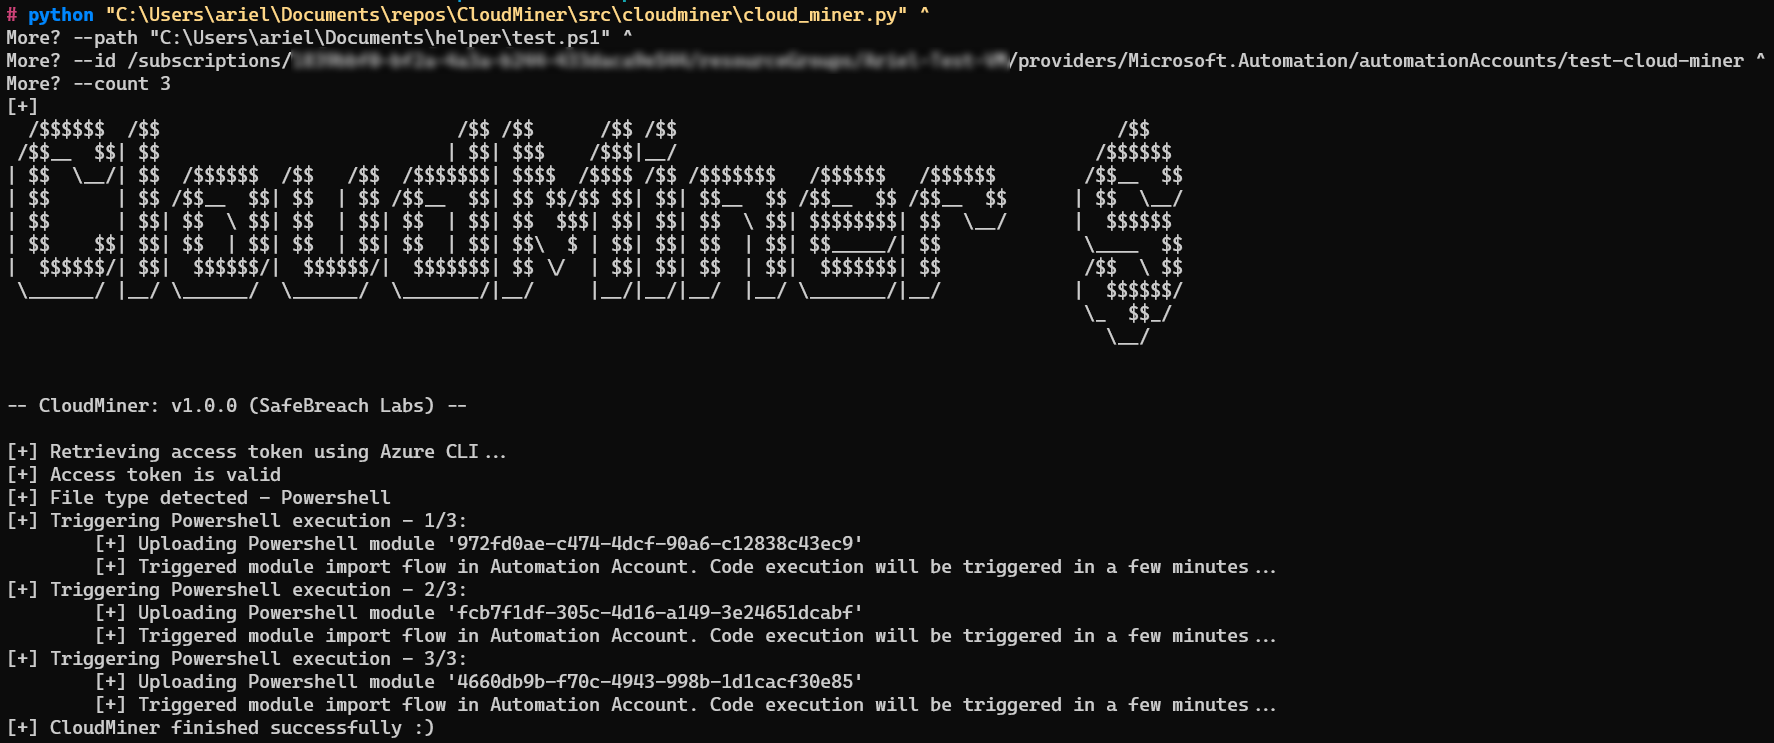 safebreach-labs/cloudminer
Execute code using Azure Automation service without getting charged
 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
 dinosn/cve-2026-44578
CVE-2026-44578: Next.js WebSocket Upgrade SSRF — pre-auth credential theft via localhost:80. Lab + exploit + audit.
 gteissier/cve-2017-10617
Proof-of-concept exploit for Juniper Contrail XXE vulnerability (CVE-2017-10617) with Docker-based lab environment demonstrating local file…
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 george0papasotiriou/cve-2026-23007-serverless-cold-start-memory-remanence-data-leakage-
Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…
 regaan/cve-2026-33340
CVE-2026-33340: Critical SSRF in lollms-webui /api/proxy - Unauthenticated arbitrary request forgery (CVSS 9.1)
 jinlei-chen-uwo/cve-2024-34351-demo
Minimal Next.js 14.0.0 demo app for CVE-2024-34351 SSRF vulnerability. Includes exploit setup, interactsh confirmation, Burp interception, and AWS…
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 fevar54/cve-2026-54420-litespeed-symlink-exploit
PoC de CVE-2026-54420: explotacion via symlink en el plugin LiteSpeed de cPanel/WHM.