

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 logisek/huntcyberark
CyberArk Security Audit
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 corgizz/springcloud
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
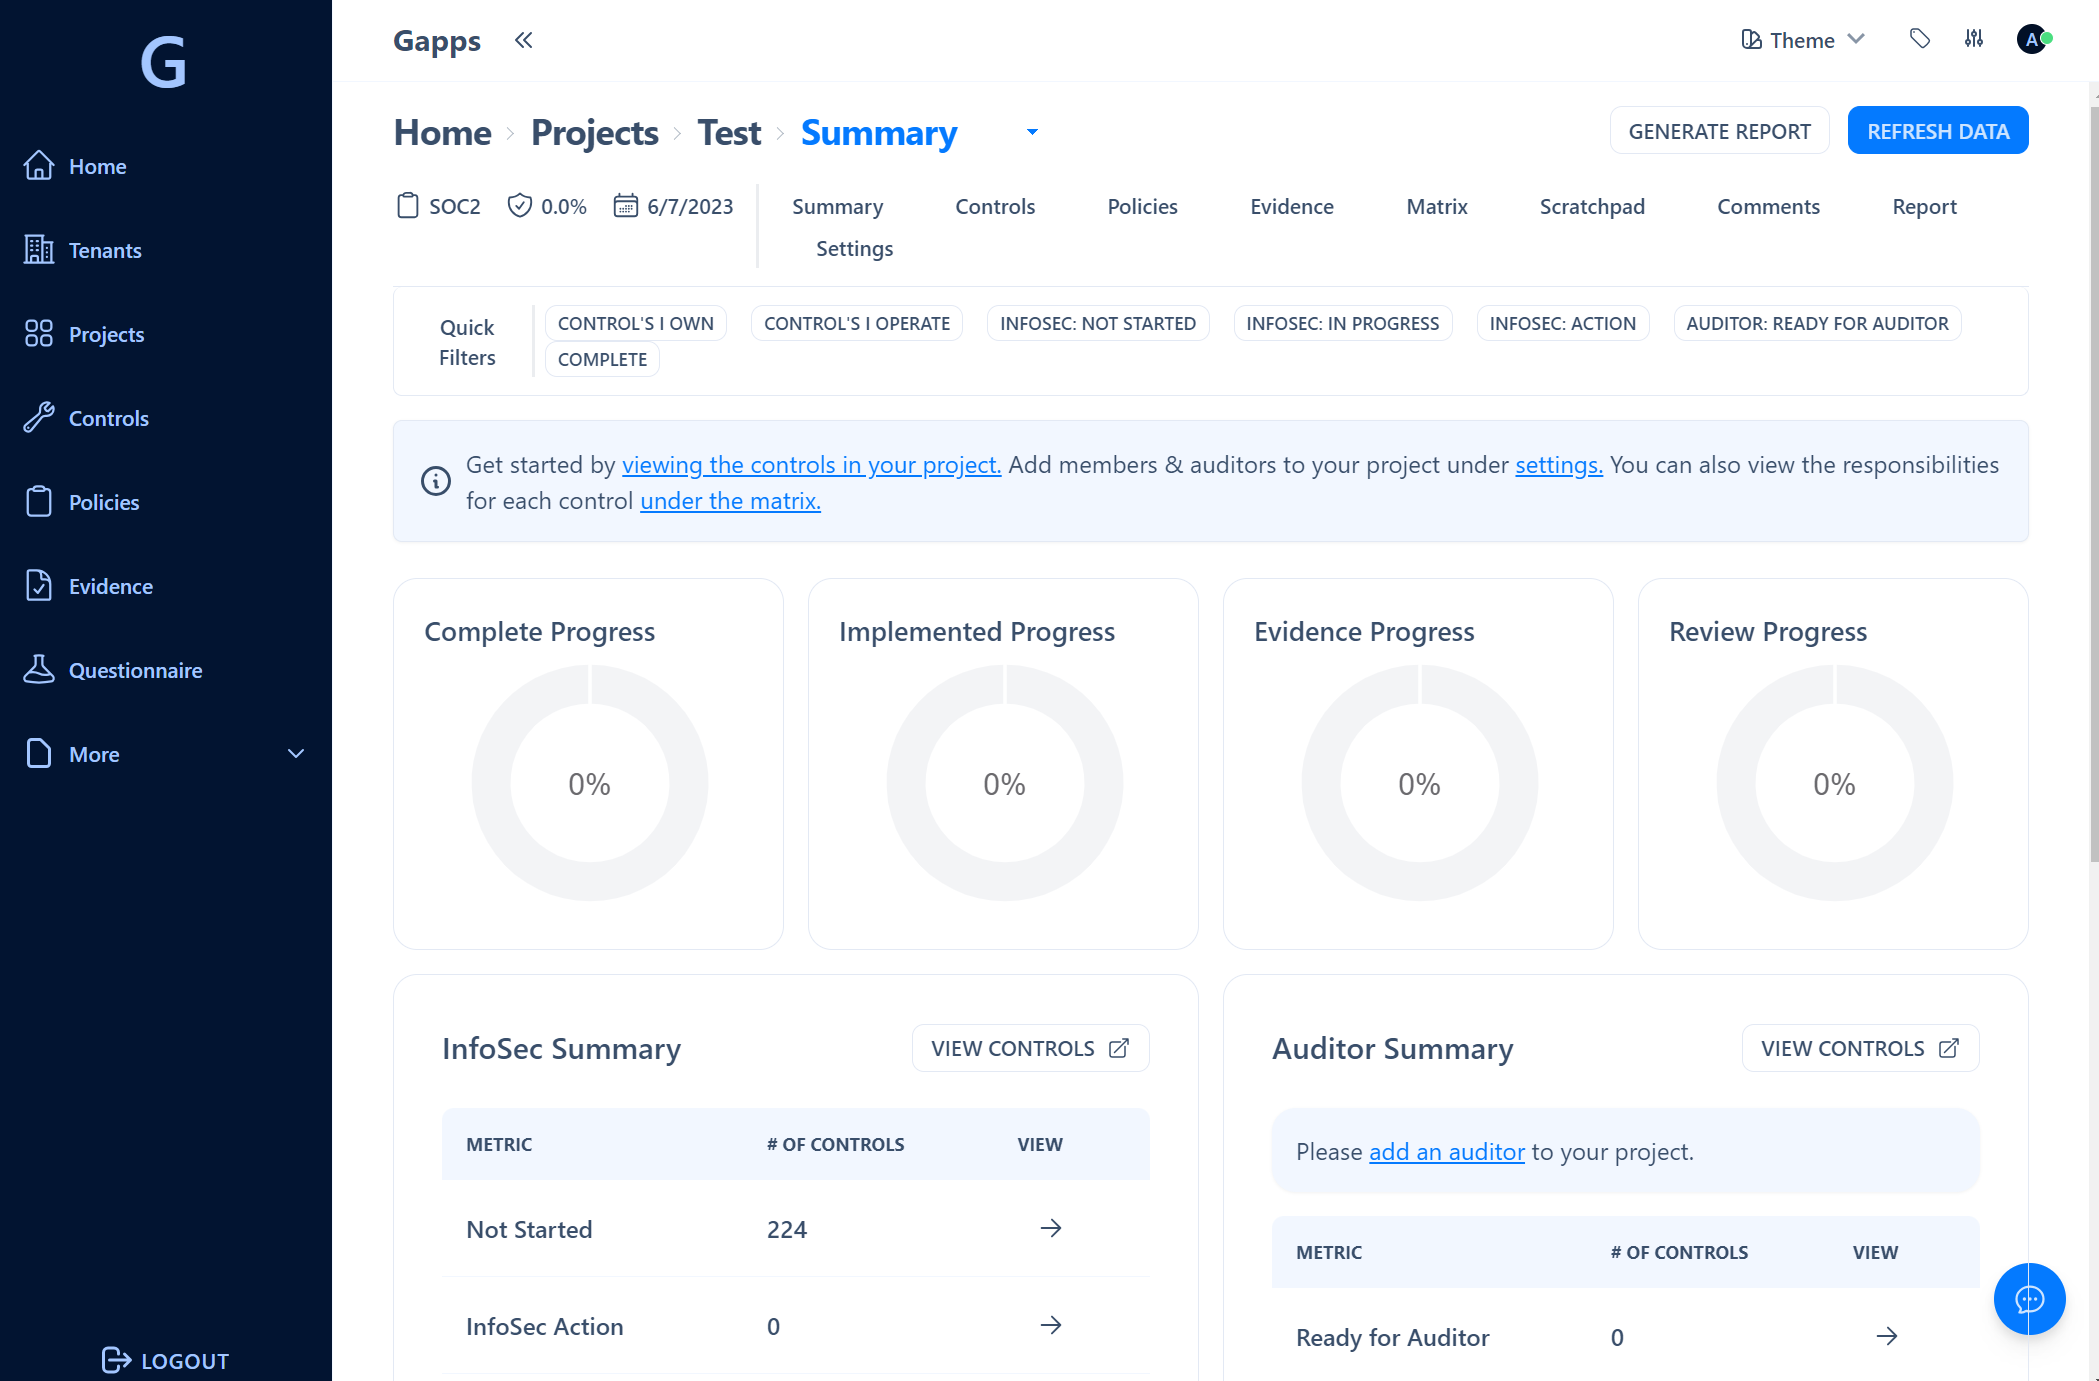 bmarsh9/gapps
Security compliance platform - SOC2, CMMC, ASVS, ISO27001, HIPAA, NIST CSF, NIST 800-53, CSC CIS 18, PCI DSS, SSF tracking
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…