
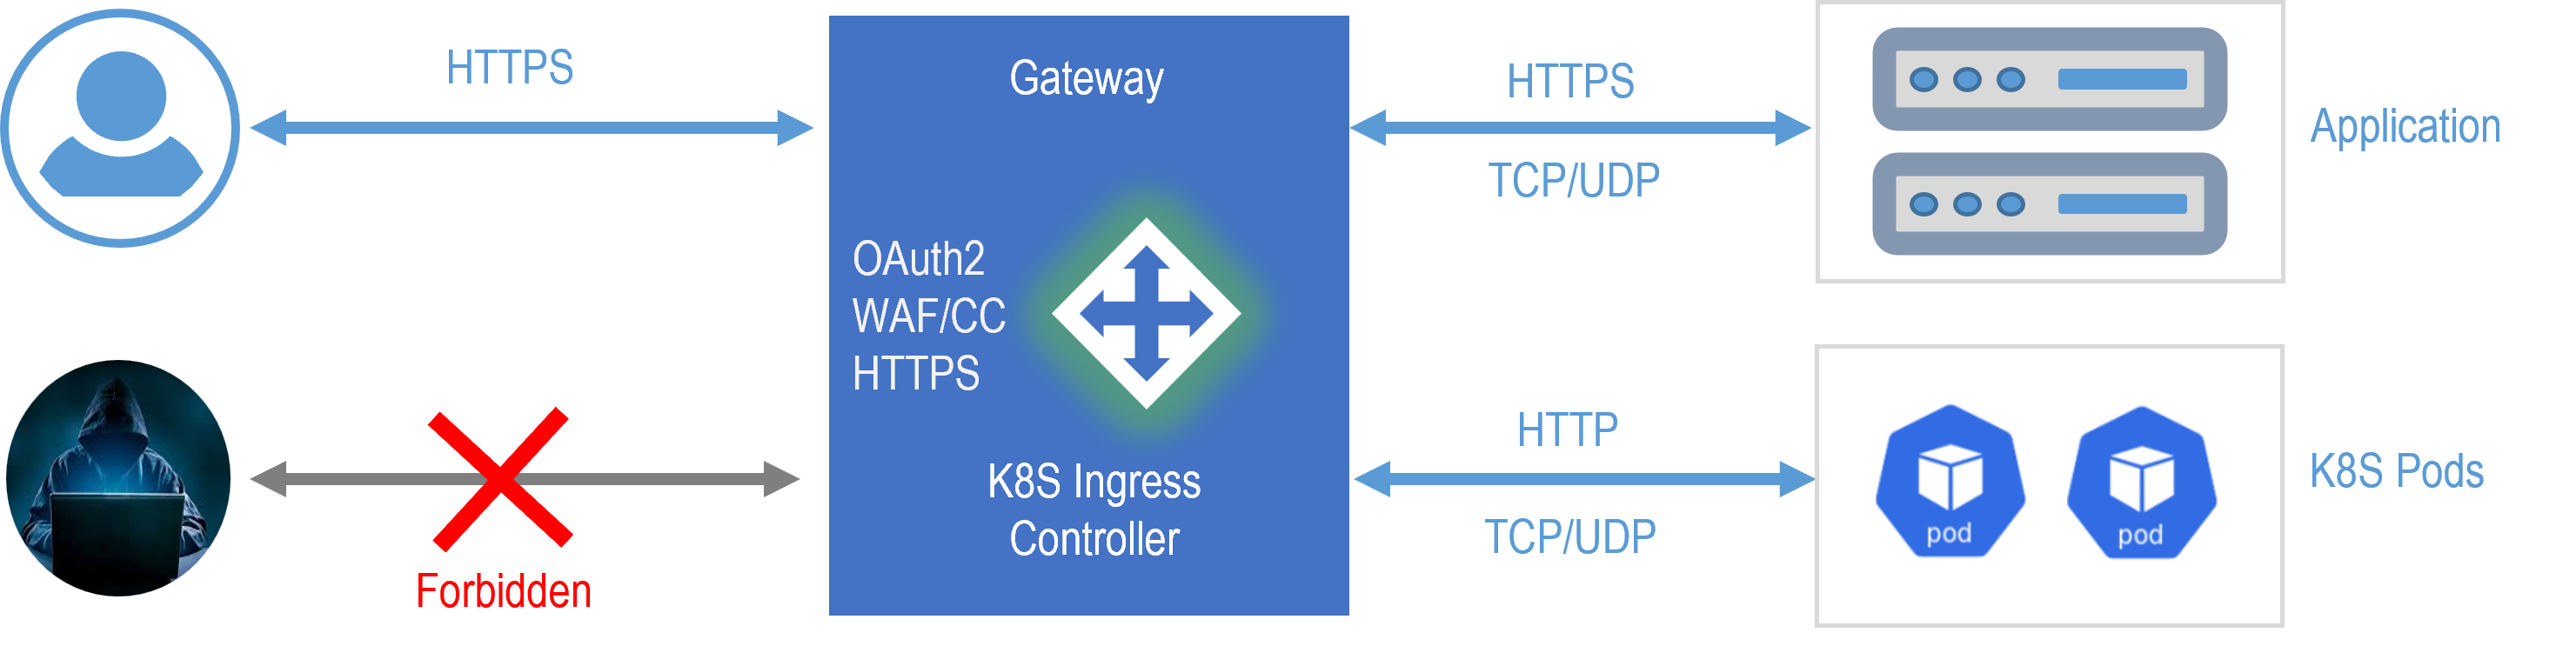
janusec
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
api-securityauthenticationcloud-security+8
1.2k
janusec/janusecUnified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 appliscale/cloud-security-audit
A command line security audit tool for Amazon Web Services
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 tenable/kaimonkey
Deliberately vulnerable Terraform infrastructure for learning cloud security misconfigurations and validating IaC scanner detection across AWS and…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 justinsteven/advisories
Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 c6fc/warcannon
High speed/Low cost CommonCrawl RegExp in Node.js
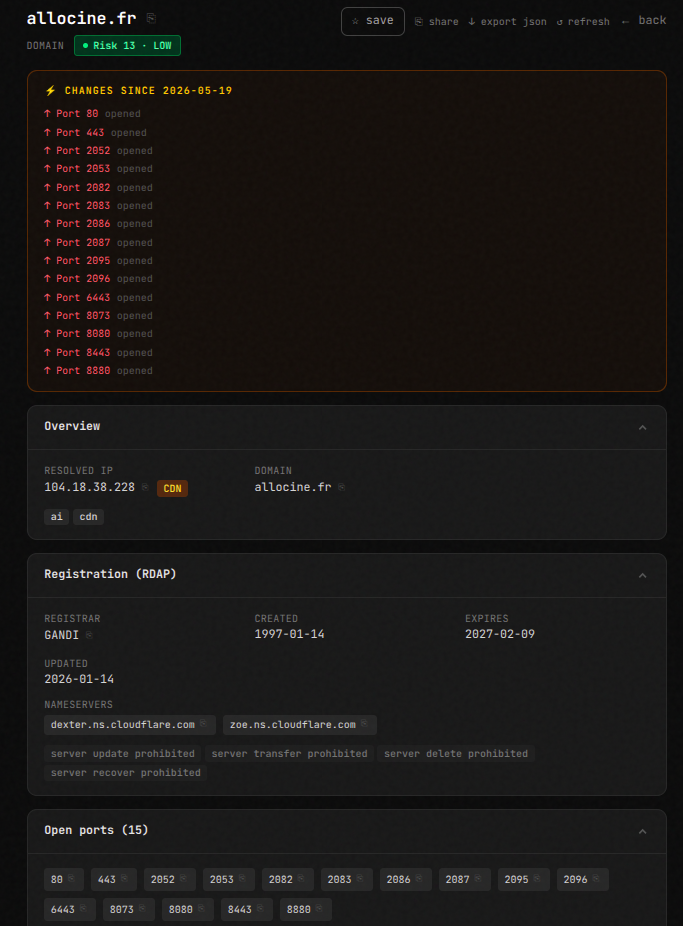 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 wadesweaponshed/check-point-trusted-access-review
Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 kimjuhyeong95/cve-2025-24514
Remote vulnerability scanner for CVE-2025-24514, an ingress-nginx auth-url injection leading to NGINX config manipulation and potential RCE.…