

enject
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
authenticationcloud-securitydevsecops+3
500
greatscott/enjectenject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 redsiege/autofunkt
Python script for automating the creation of serverless cloud redirectors from Cobalt Strike malleable C2 profiles
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
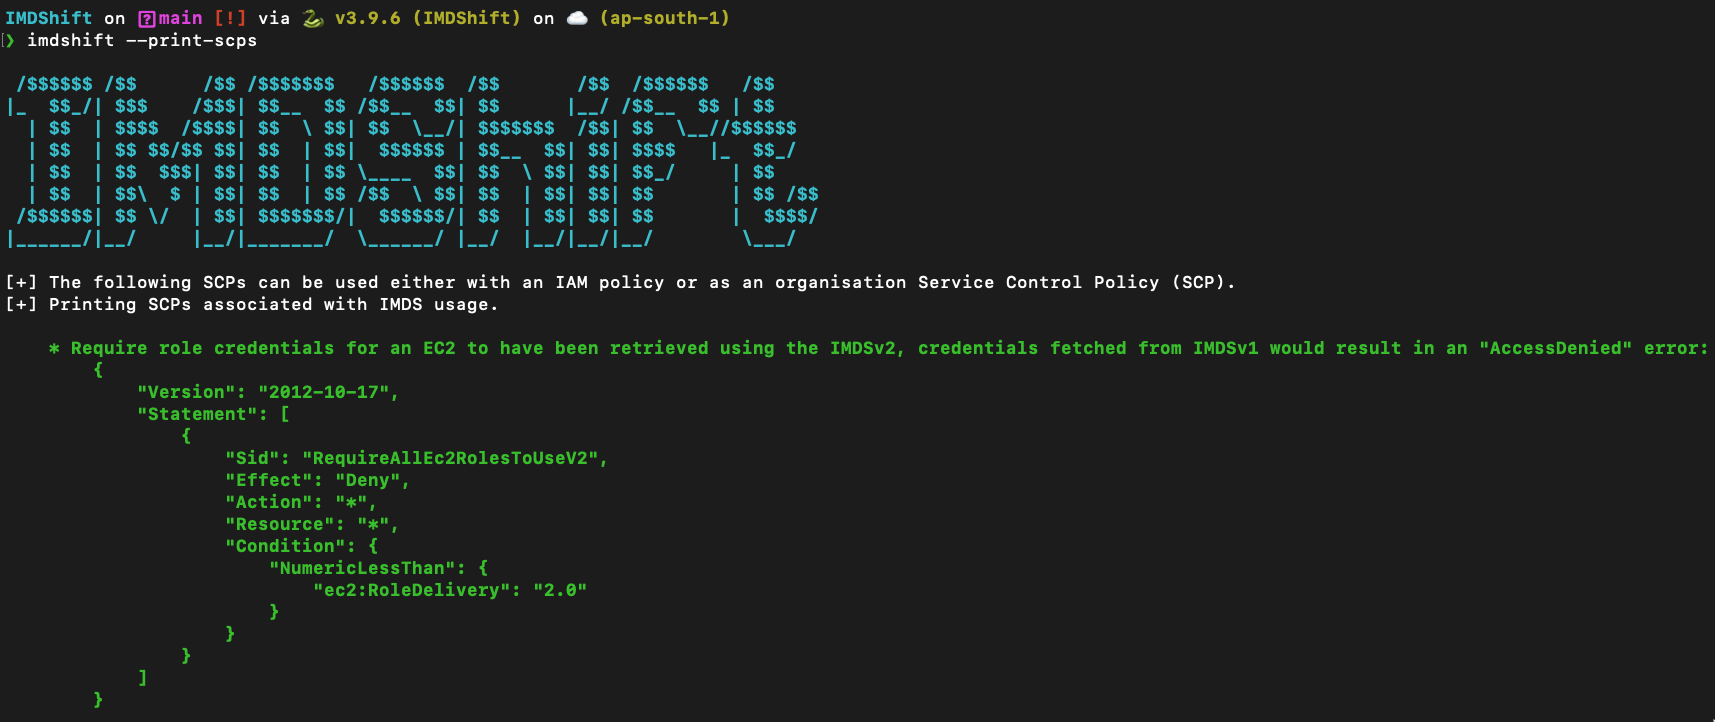 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
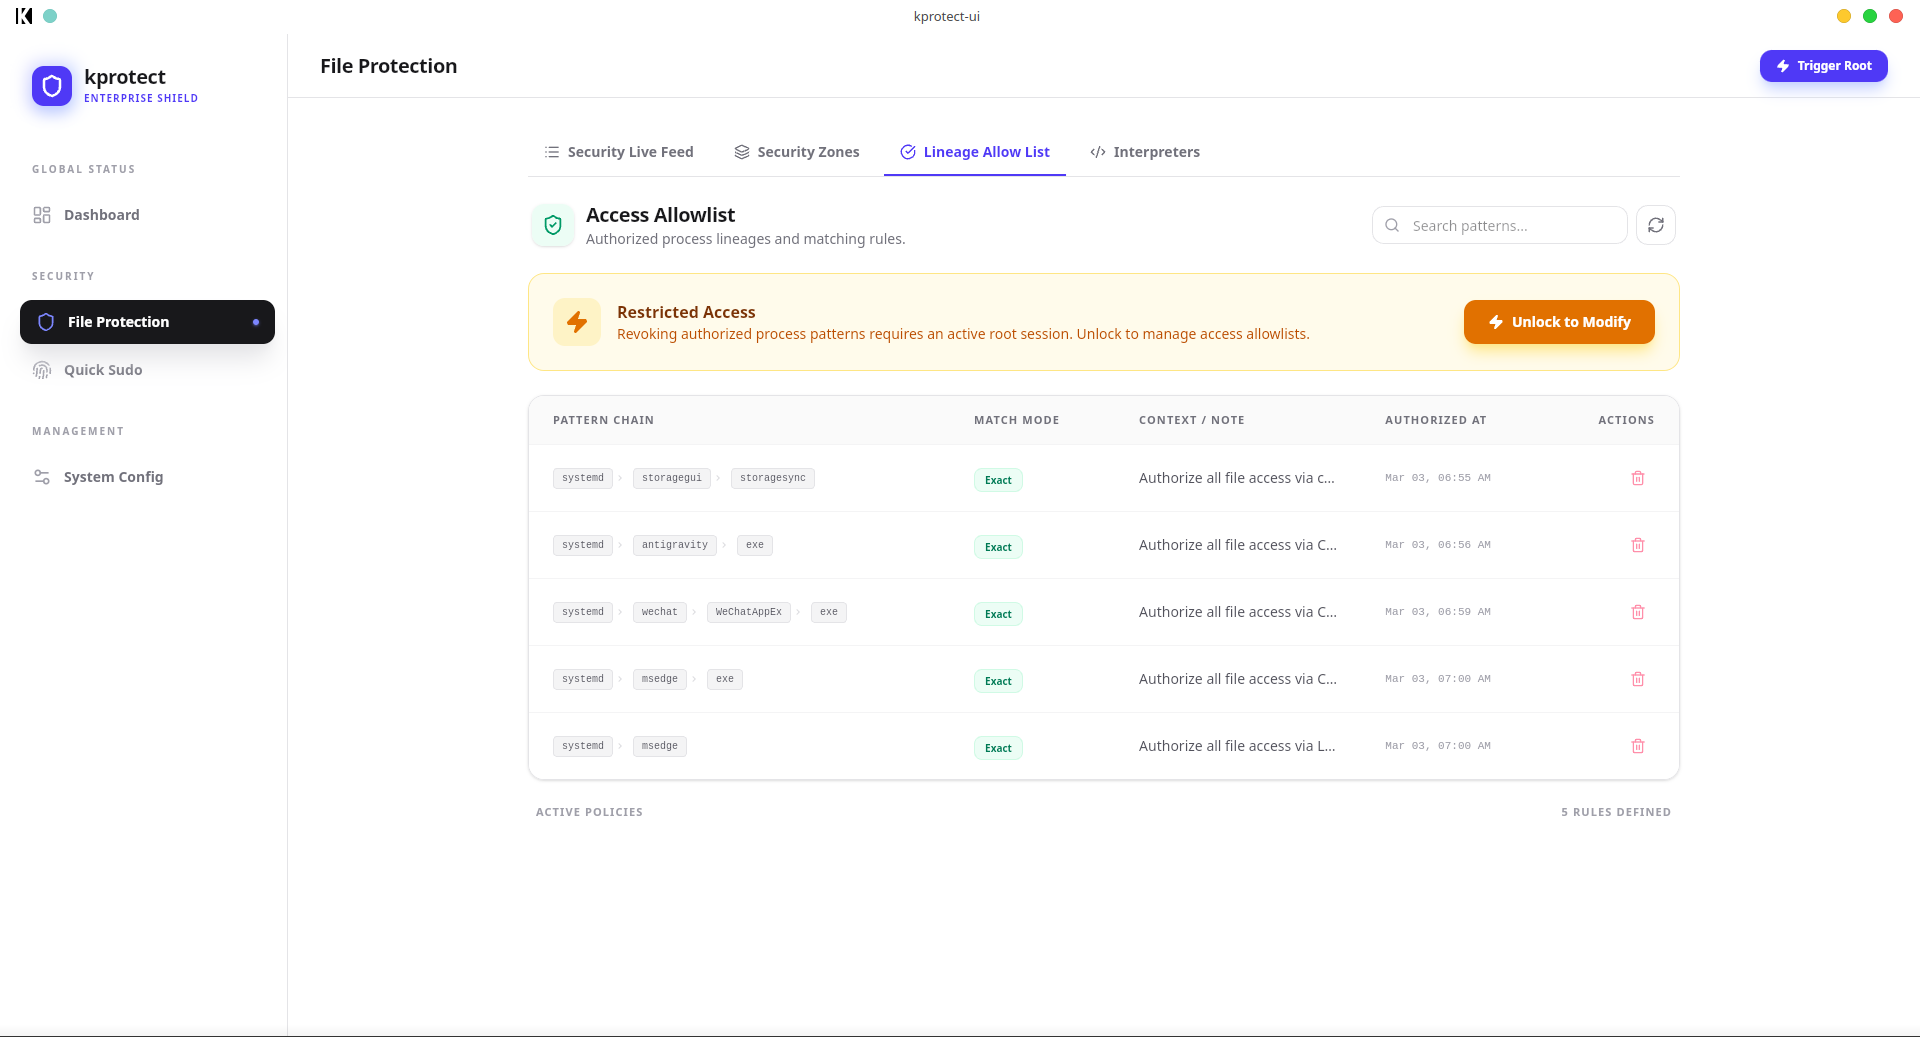 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
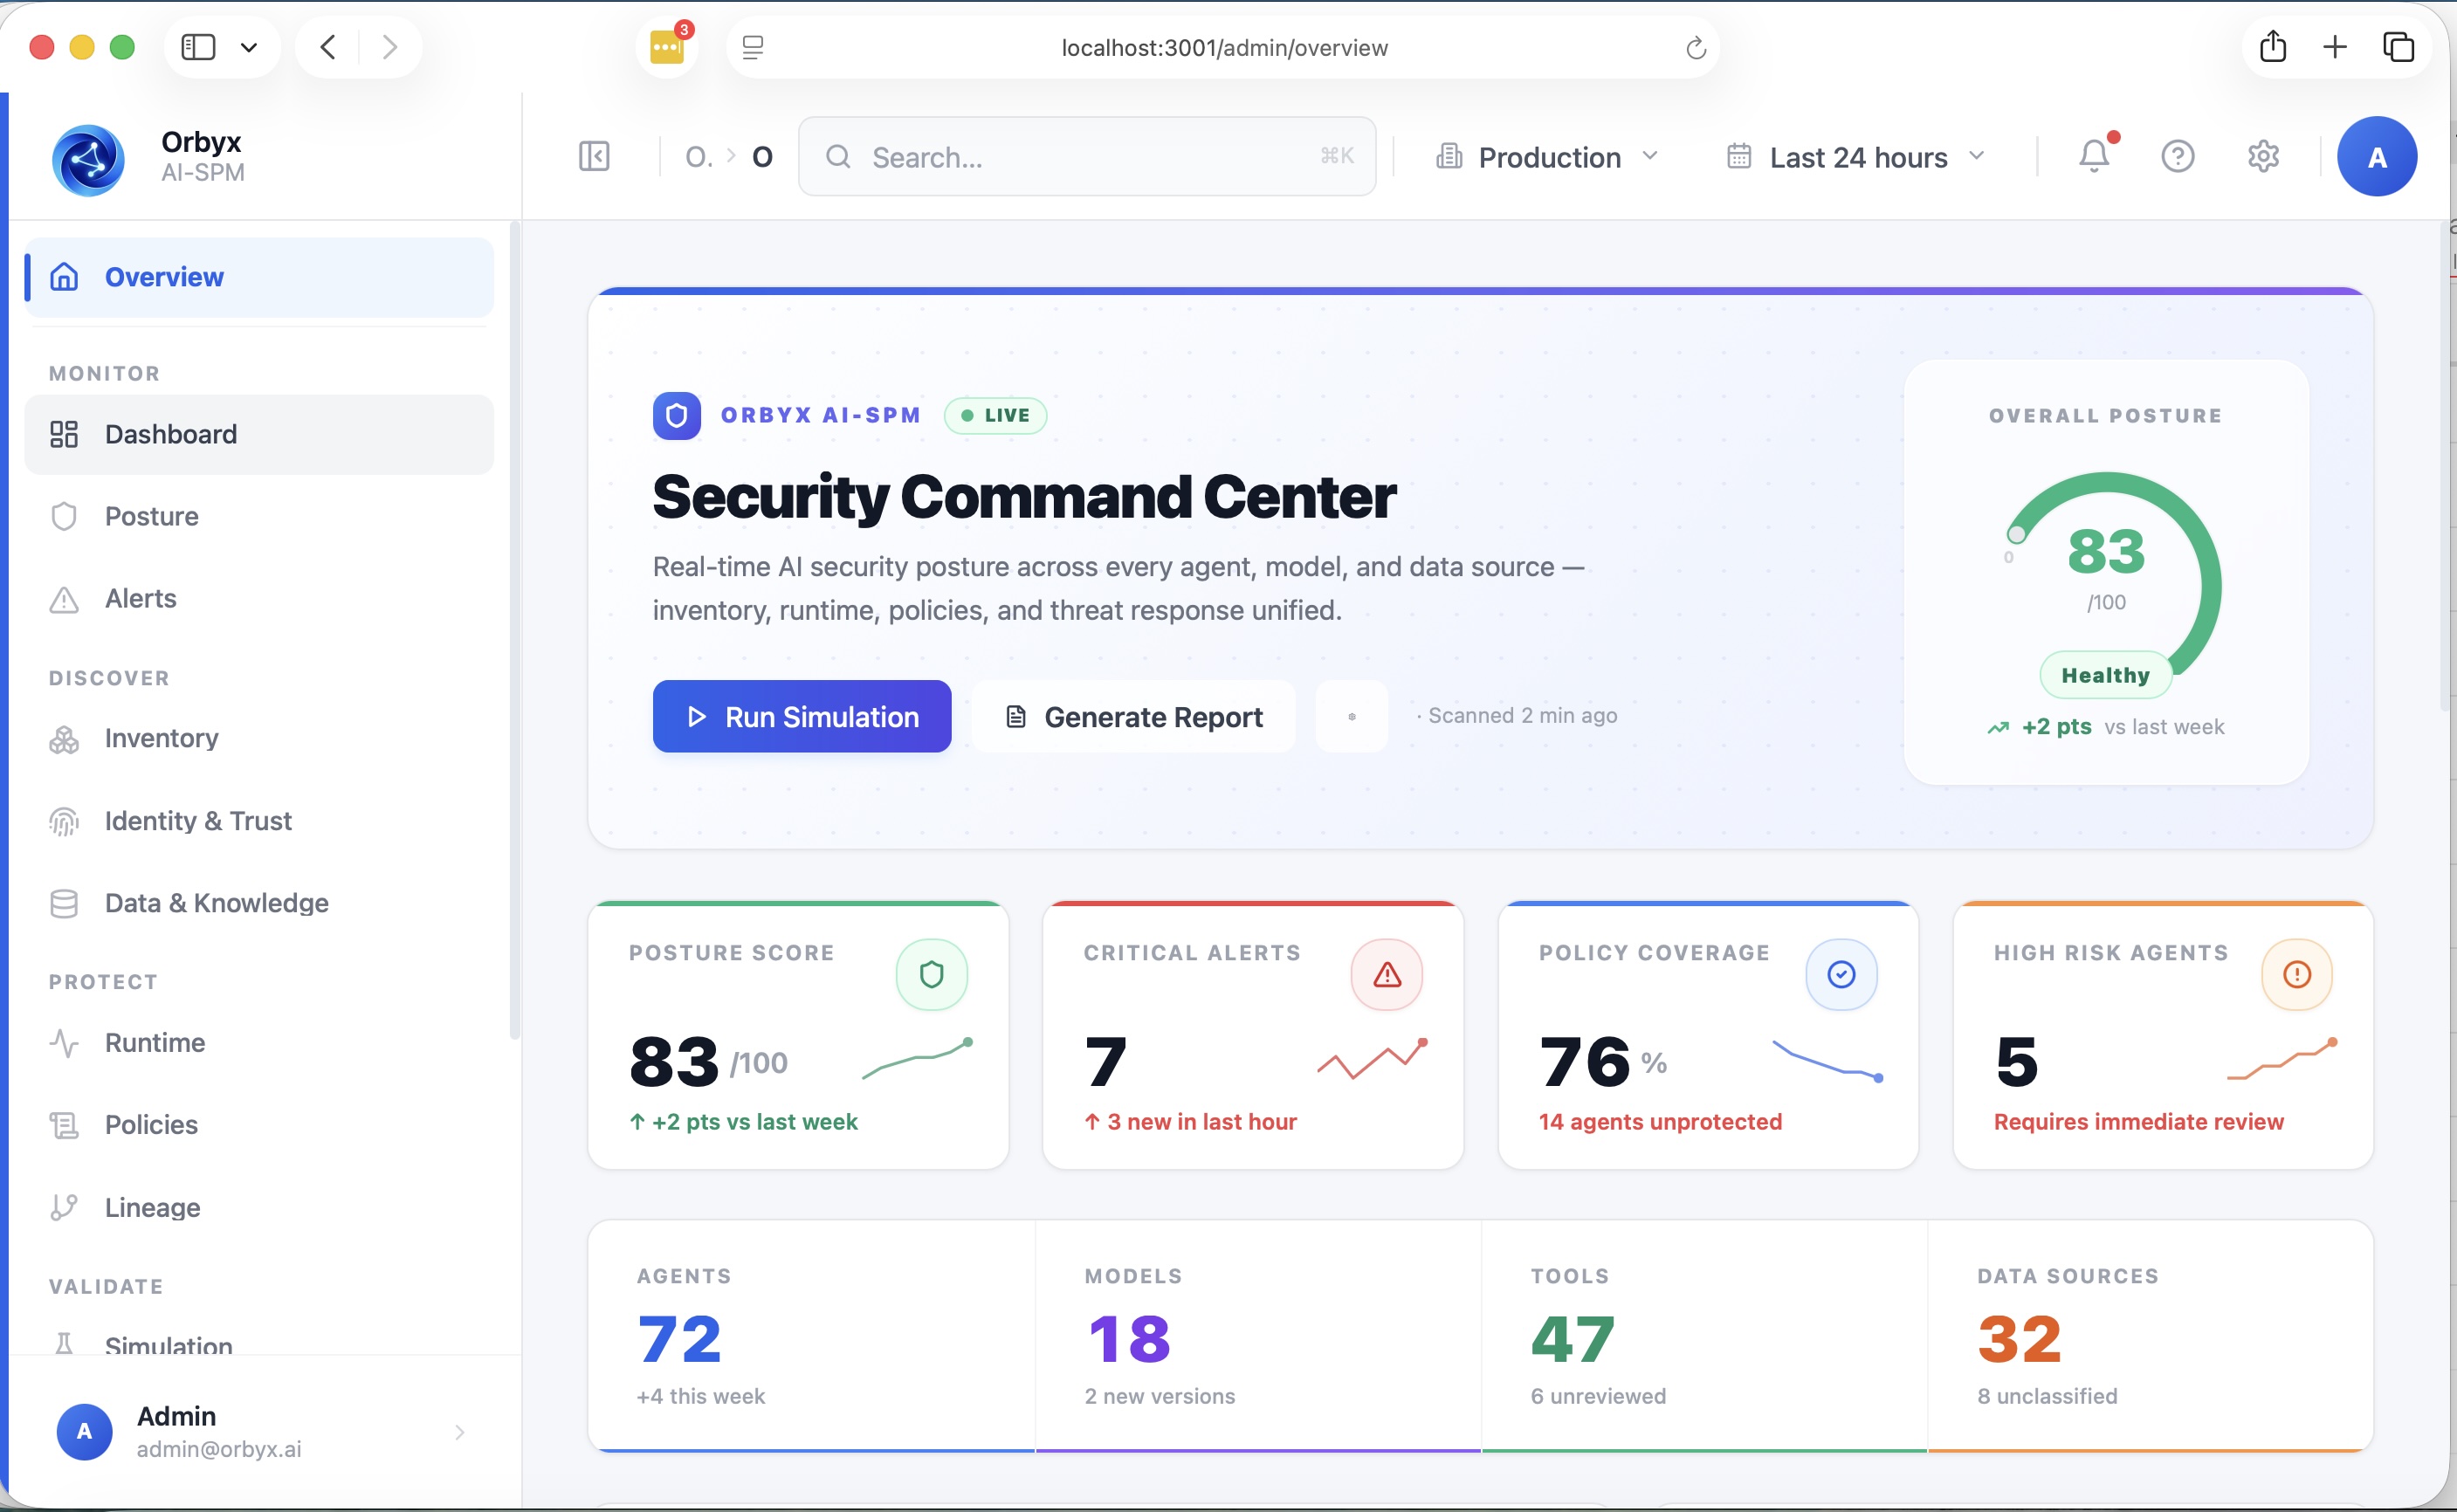 dshapi/ai-spm
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
 unicornunicode/fact
Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 hi-unc1e/cve-2025-1974-poc
PoC of CVE-2025-1974, modified from the world-first PoC~
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…