

HybridTestFramework
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
api-security-testingcloud-securitycontainer-security+3
153
dipjyotimetia/hybridtestframeworkEnd to End testing of Web, API, Cloud, Events and Security

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
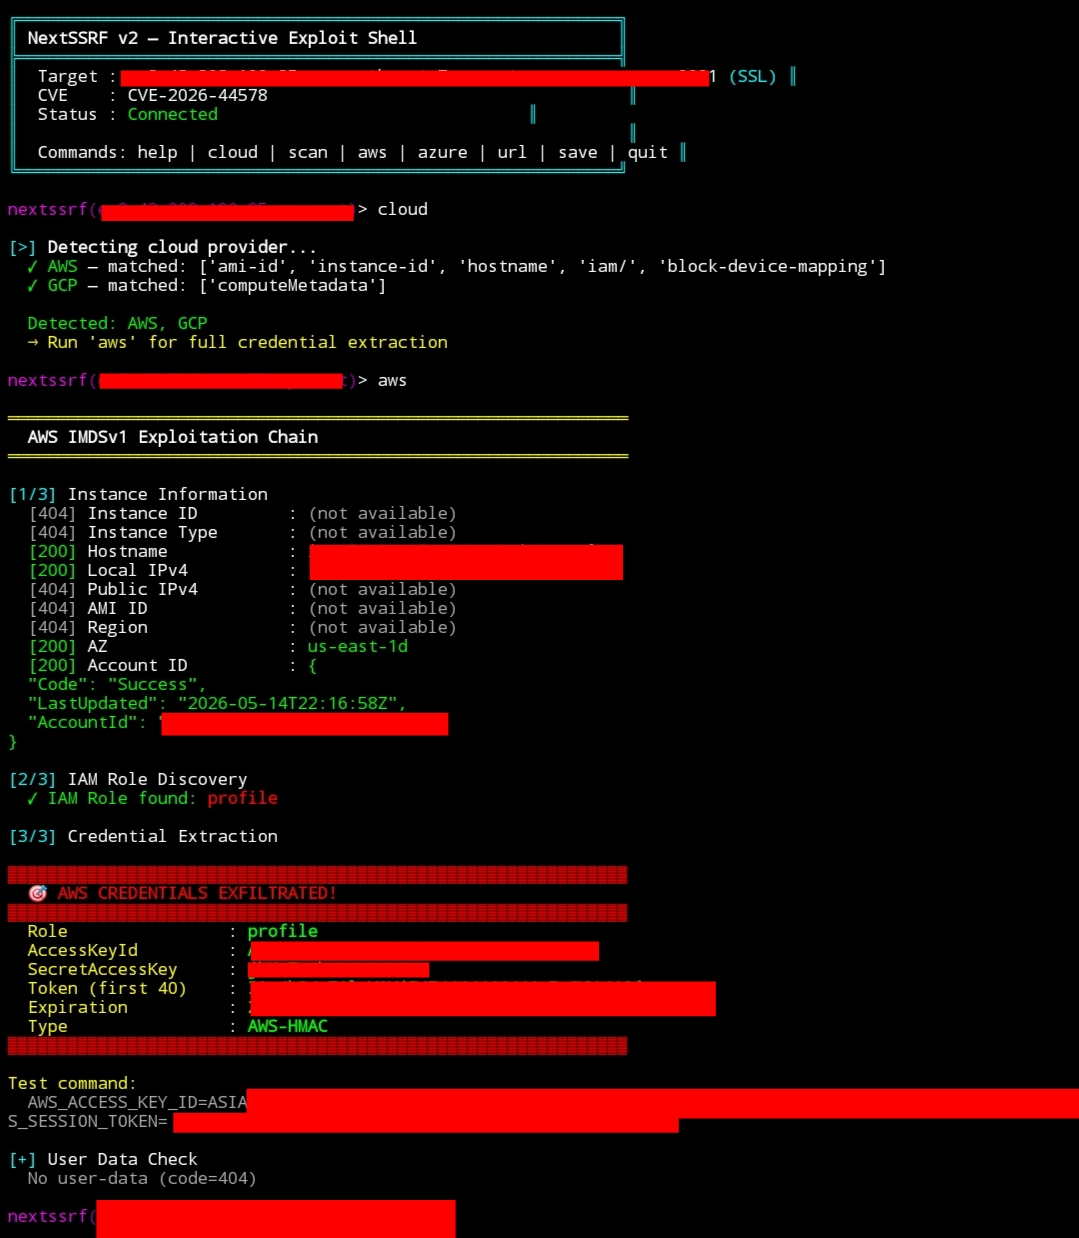 ynsmroztas/nextssrf
CVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
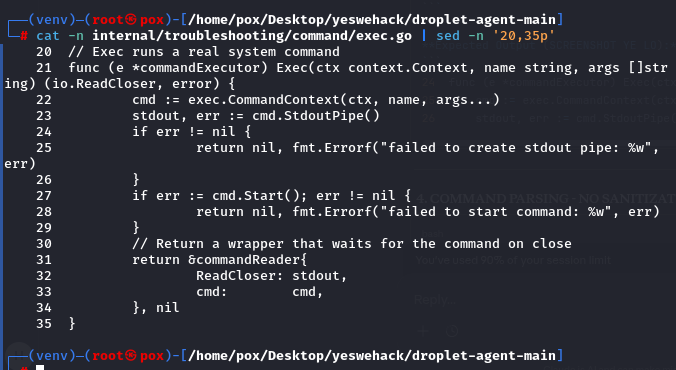 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
 grtmaldet/big-ip-next-cve-2024-26026
Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…
 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.
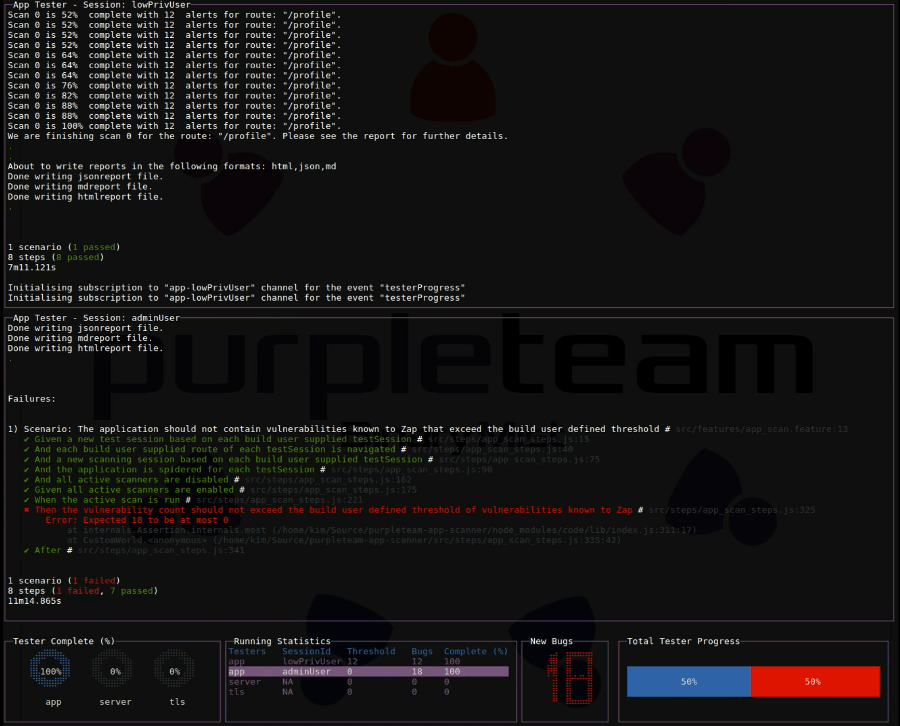 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 owasp/dvsa
a Damn Vulnerable Serverless Application
 logisek/huntcyberark
CyberArk Security Audit