
Azur3Alph4
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
cloud-securityinformation-gatheringpenetration-testing+3
63
hyd3sec/azur3alph4PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 sebastian-mora/aws-loot
Enumerates AWS environments for secrets by scanning EC2 userdata, Lambda environment variables and source code, and CodeBuild instances for…
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 nccgroup/s3_objects_check
Whitebox evaluation of effective S3 object permissions, to identify publicly accessible files.
 cnotin/m365_groups_enum
Enumerate Microsoft 365 Groups in a tenant with their metadata
 securisec/cliam
Cloud agnostic IAM permissions enumerator
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 bishopfox/cirro
Creating attacks paths across management and data planes
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 in3tinct/taken
Takeover subdomains using AWS dangling elastic ips and have a working POC for Subdomain Takeover.
 hahwul/s3reverse
The format of various s3 buckets is convert in one format. for bugbounty and security testing.
 yuyudhn/azsubenum
DNS-based subdomain enumeration tool for Azure services, probing App Services, Storage Accounts, Databases, Key Vaults, and CDN endpoints via…
 daddycocoaman/azbelt
AAD related enumeration in Nim
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 joelgmsec/azuregraph
PowerShell tool for enumerating Azure AD users, devices, applications, and domains via Microsoft Graph API, with offline data export capability.
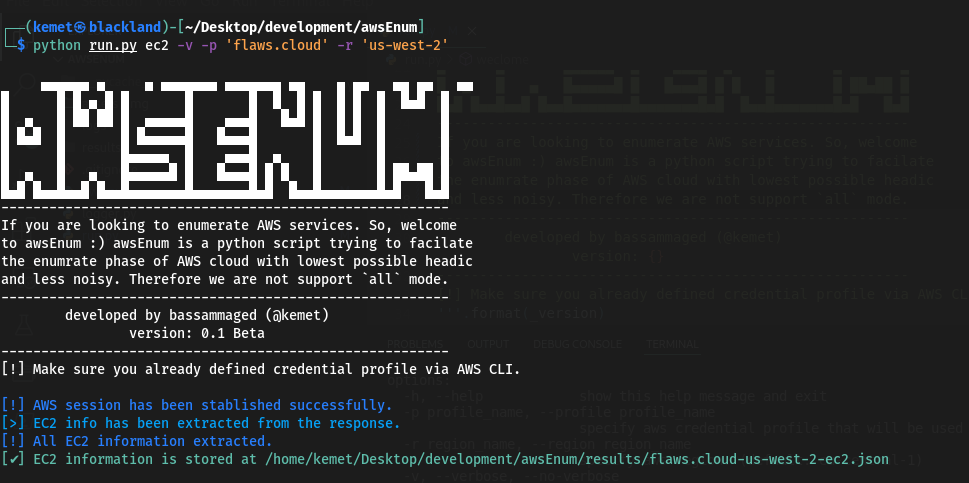 bassammaged/awsenum
Enumerate AWS cloud resources based on provided credential
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.