
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
awsEnum — Enumerate AWS cloud resources based on provided credential | Kitploit

Tools/GitHubGitHub/bassammaged/awsenum
Vulnerability AnalysisInformation GatheringPenetration TestingCloud Security
GitHubbassammaged/awsenum

awsEnum

Enumerate AWS cloud resources based on provided credential

View Repository
527374 years agoReviewed by Kitploit
Share

awsEnum

Enumrate AWS services! with no nosies

awsEnum is a python script enumrate AWS services through the provided credential.
:book: Table of Contents

Table of Contents
  1. Screenshot
  2. Disclaimer
  3. Features
  4. Prerequisites
  5. How to Install
  6. Results and FQAs
  7. To-Do

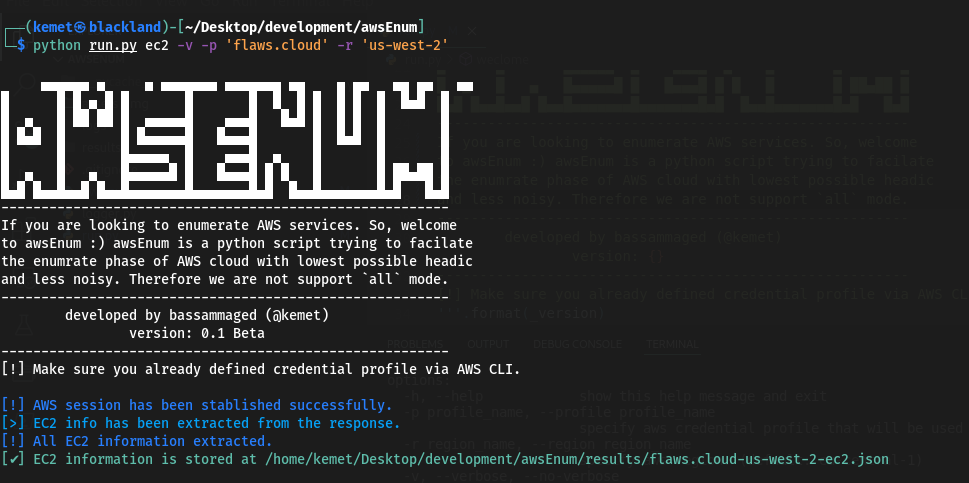
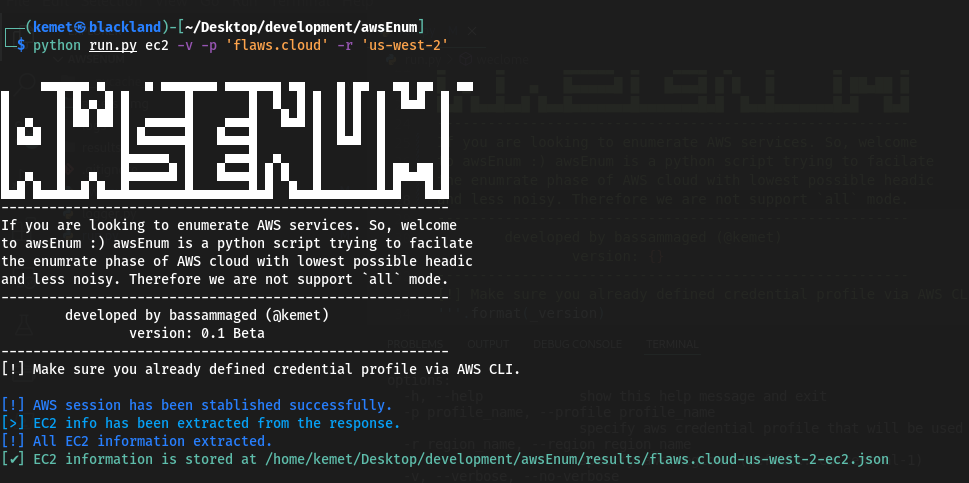
:clapper: Screenshot

     ▄▄▄▄▄▄ ▄     ▄ ▄▄▄▄▄▄▄ ▄▄▄▄▄▄▄ ▄▄    ▄ ▄▄   ▄▄ ▄▄   ▄▄ 
█      █ █ ▄ █ █       █       █  █  █ █  █ █  █  █▄█  █
█  ▄   █ ██ ██ █  ▄▄▄▄▄█    ▄▄▄█   █▄█ █  █ █  █       █
█ █▄█  █       █ █▄▄▄▄▄█   █▄▄▄█       █  █▄█  █       █
█      █       █▄▄▄▄▄  █    ▄▄▄█  ▄    █       █       █
█  ▄   █   ▄   █▄▄▄▄▄█ █   █▄▄▄█ █ █   █       █ ██▄██ █
█▄█ █▄▄█▄▄█ █▄▄█▄▄▄▄▄▄▄█▄▄▄▄▄▄▄█▄█  █▄▄█▄▄▄▄▄▄▄█▄█   █▄█
--------------------------------------------------------
If you are looking to enumerate AWS services. So, welcome
to awsEnum, awsEnum is a python script trying to facilitate 
the enumerate phase of AWS cloud with the lowest possible
headache and less noise. Therefore we are not supporting 
the `all` mode. ----------------------------------------
--------------------------------------------------------
        developed by bassammaged (@kemet)
                version: 0.1 Beta
--------------------------------------------------------
[!] Make sure you already defined credential profile via AWS CLI.

usage: run.py [-h] [-p profile_name] [-r region_name] [-v | --verbose | --no-verbose] [-t TRIES] aws_service_name

positional arguments:
  aws_service_name      Specify the aws service for enumration. Supported services are: ['ec2', 'iam', 's3'] (default: all)

options:
  -h, --help            show this help message and exit
  -p profile_name, --profile profile_name
                        specify aws credential profile that will be used through the enumeration. (default: default)
  -r region_name, --region region_name
                        specify aws region. (default: eu-central-1)
  -v, --verbose, --no-verbose
                        Allows the script to print out the message level start with debug. (default: False)
  -t TRIES, --tries TRIES
                        set maximum tries. (default: 1000)

:pencil: Disclaimer

awsEnum is in beta version and is supposed to be free of issues but if any issues encountered, please submit the ticket,awsEnum is coded and published to be used in partical circumstances:

  1. Engaging in penetration testing activity.
  2. Carry on Bug hunting activity.
  3. AWS cloud security Audit.
  4. Any other legal activity that already approved by the owner of the asset.

awsEnum is craeted to work under hoodie, which means there's no intention to support all mode.

:fuelpump: Features

  • Connect to aws service through boto3, on other word! signing request.
  • awsEnum allows user to set the number of requests [By default: 1000].
  • awsEnum store result into json file.
  • Keep AWS credential within awscli confugration and just pass profile_name to awsEnum.
  • Supported service: ec2, iam, s3.

:cd: Prerequisites

  1. Python3
  2. pip package manager
  3. python3 -m pip install requirements.txt
  4. Feel Free to use awsEnum via run.py script

:paperclip: Results and FQAs

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →






