
iam-vulnerable
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
cloud-securityeducationidentity-access-management+4
591
bishopfox/iam-vulnerableUse Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
 voulnet/barq
barq: The AWS Cloud Post Exploitation framework!
 yelp/amira
AMIRA: Automated Malware Incident Response & Analysis
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
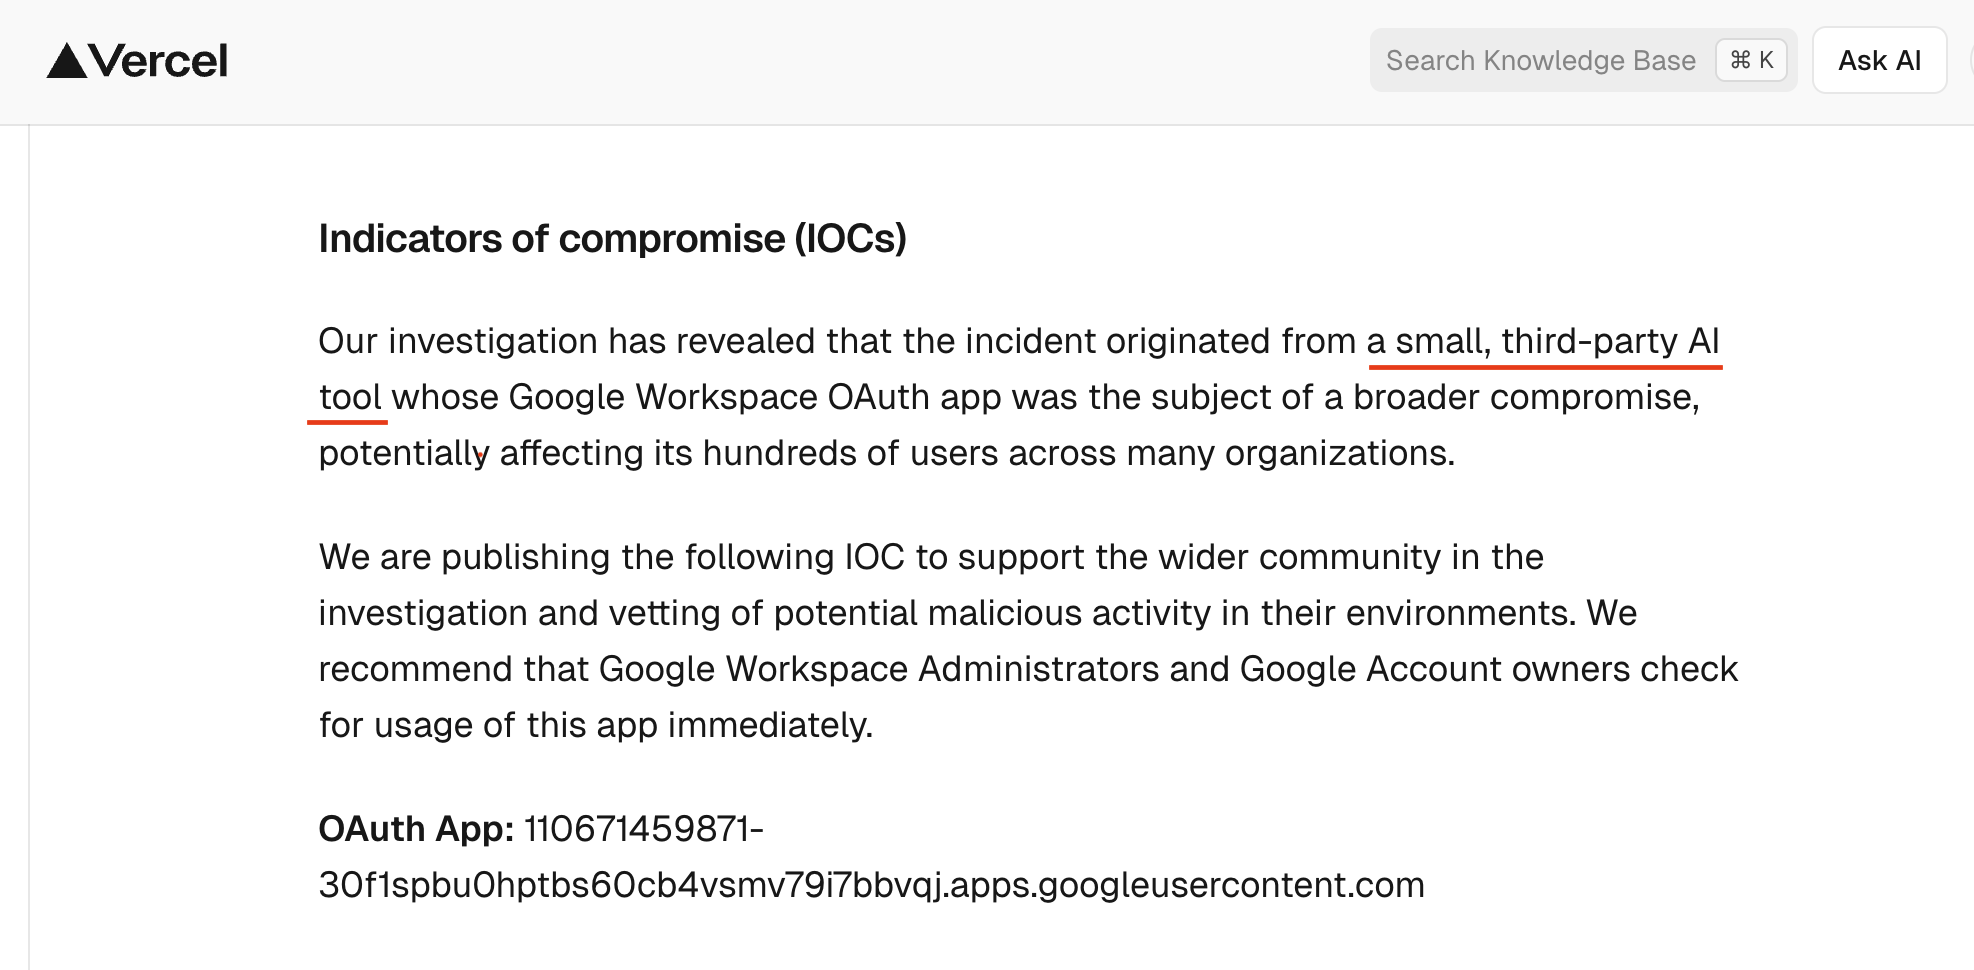 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 killswitch-gui/flask_heroku_redirector
flask heroku C2 redirector template
 killswitch-gui/flask_appengine_redirector
Google App Engine Flask C2 redirector
 irsl/google-osconfig-privesc
Proof of concept about the privilege escalation flaw identified in Google's Osconfig
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 blackm4c/cve-2021-41805
HashiCorp Consul exploit with python. (CVE-2021-41805)
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 mochizuki875/cve-2024-10220-githooks
CVE-2024-10220 Test repo
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636
 markuman/aws-log4j-mitigations
CVE-2021-44228 log4j mitigation using aws wafv2 with ansible
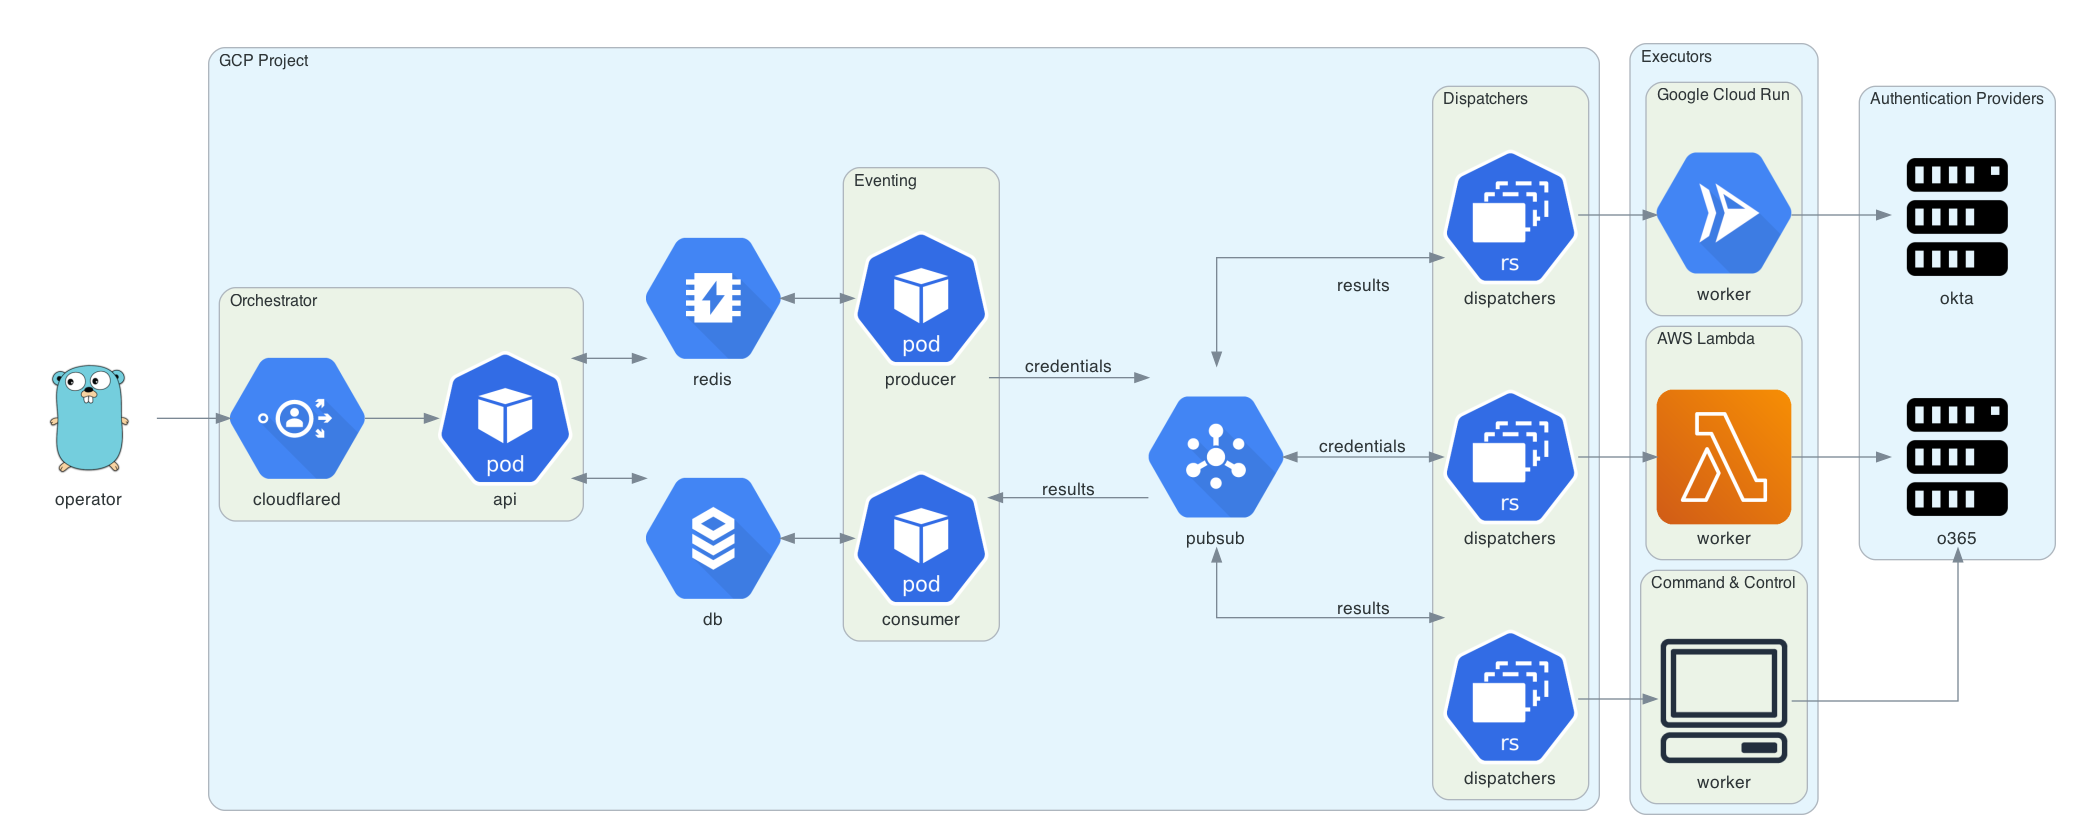 praetorian-inc/trident
automated password spraying tool
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 pgporada/ansible-role-cve
Mitigates CVE-2016-5195 aka DirtyCOW