

kube-reaper
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
cloud-securityconfiguration-auditingcontainer-security+9
3
stillbigjosh/kube-reaperScans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).
 gduma-phdata/patch-cve-2026-07219
Deploys a critical patch for F5 BIG-IP iControl REST vulnerability CVE-2026-07219, with validation and deployment tracking for production…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
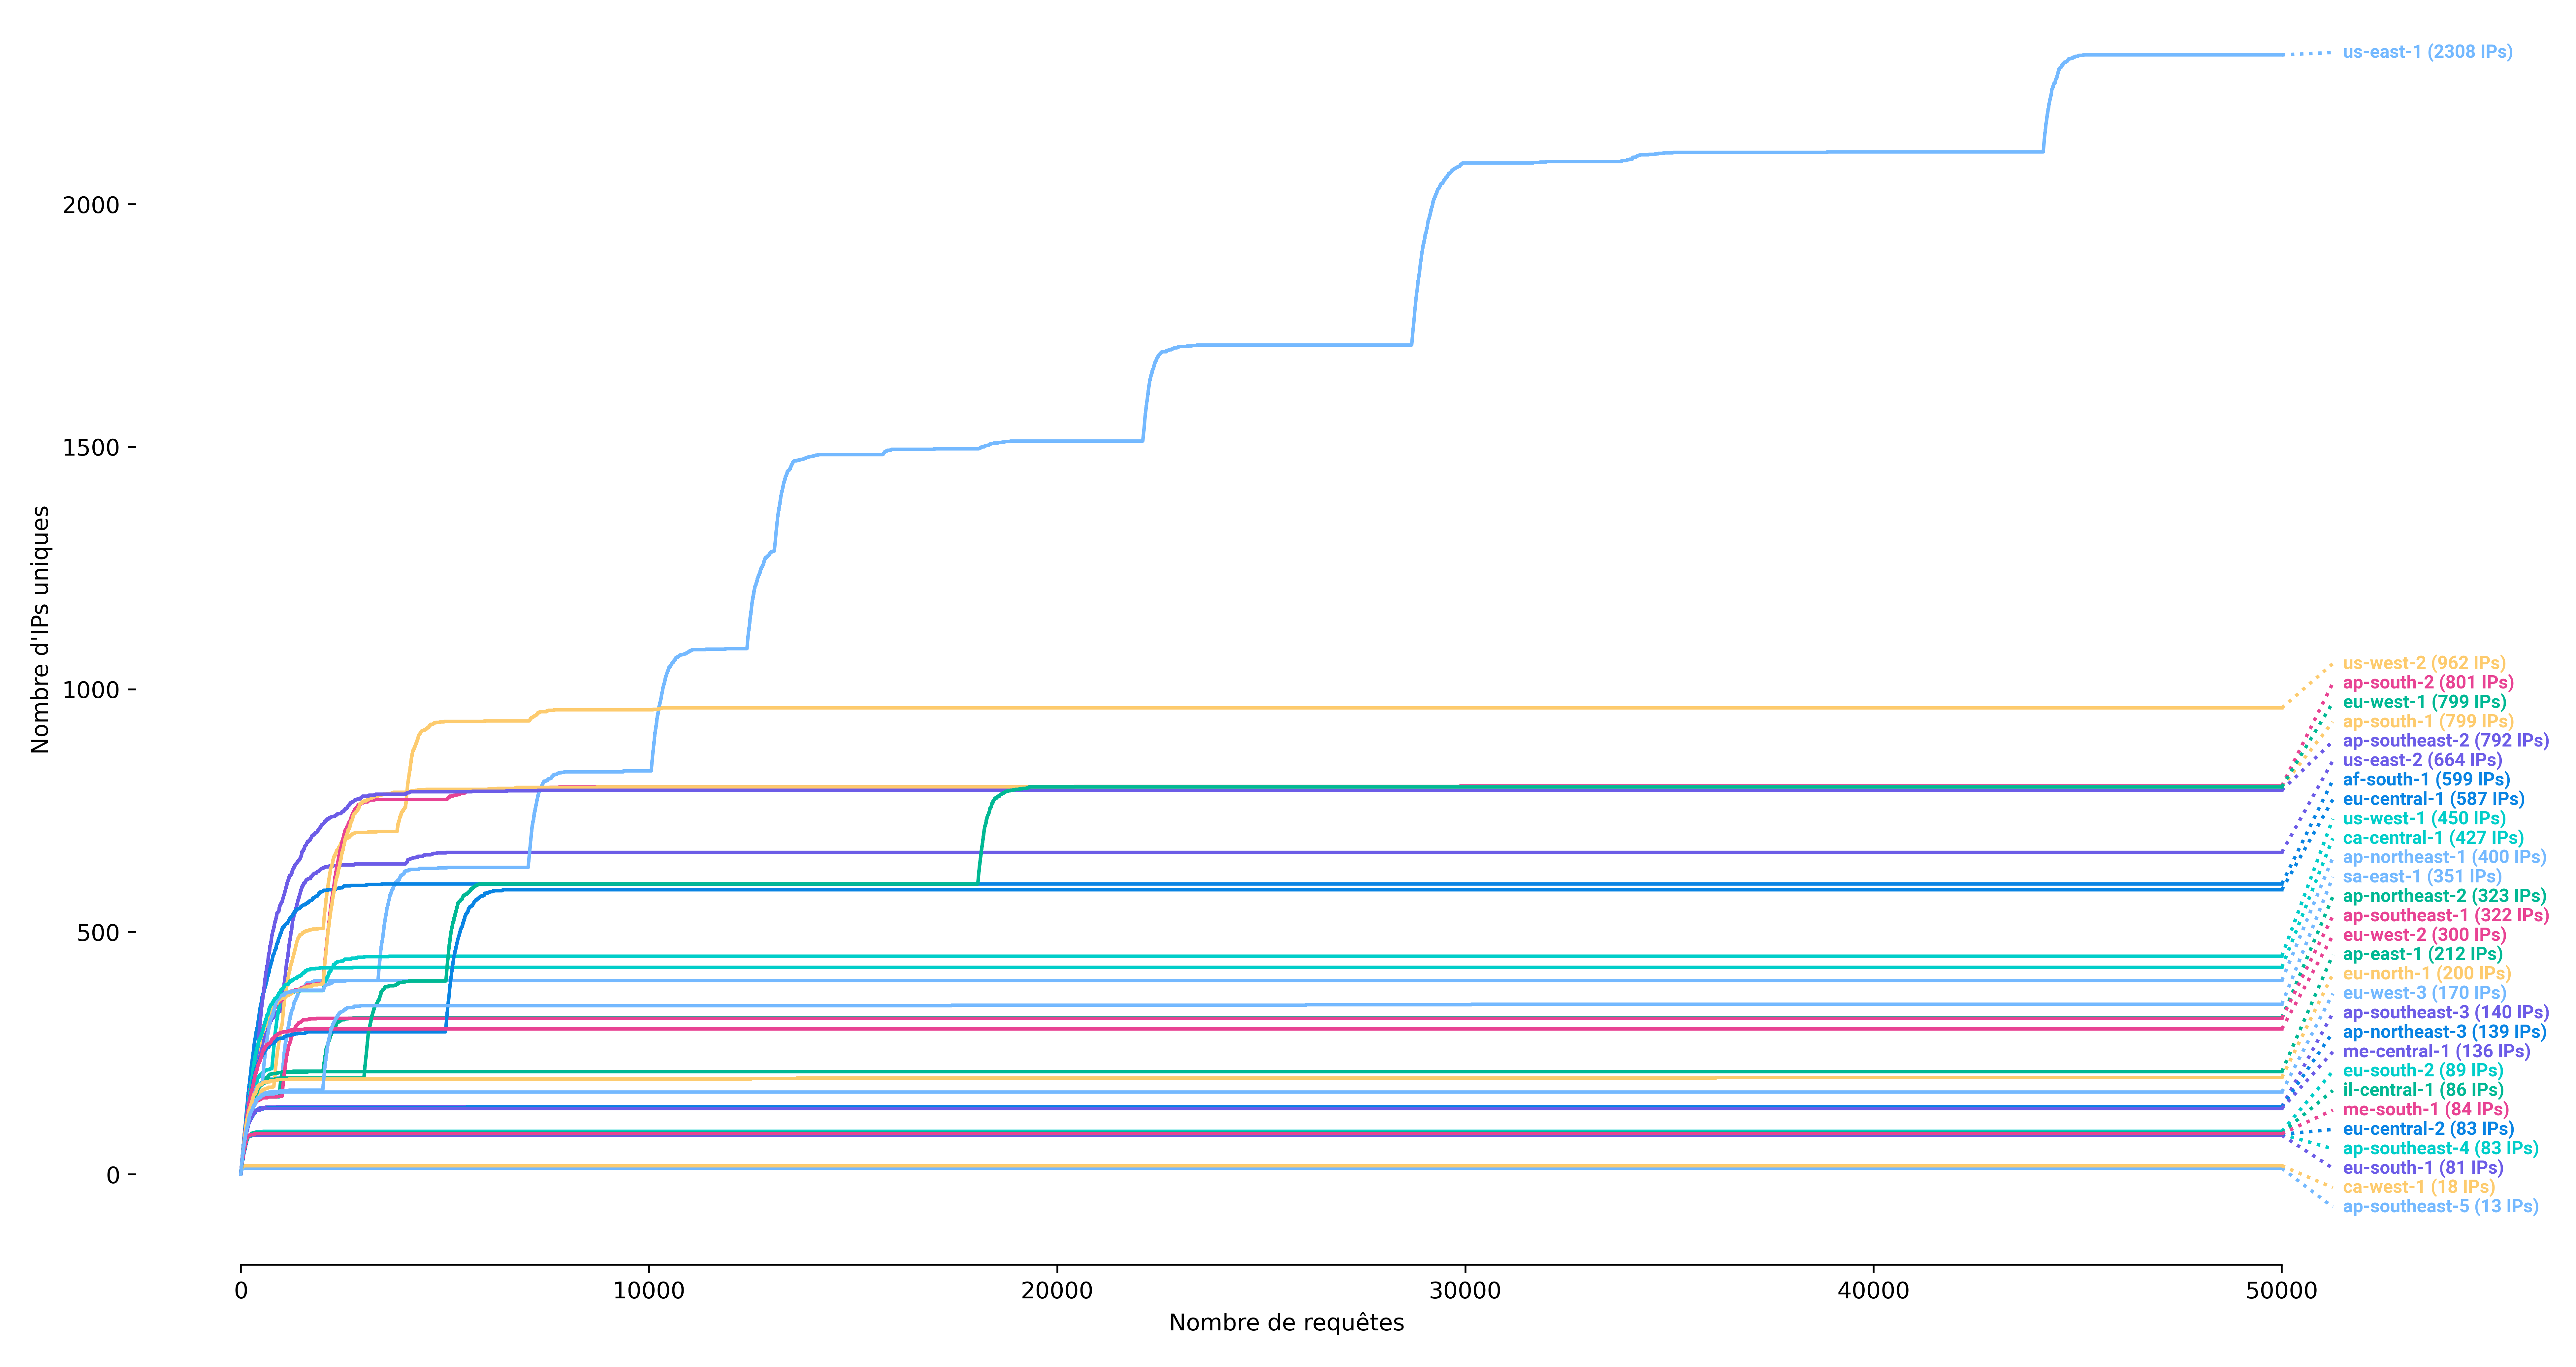 synacktiv/ipspinner
IPSpinner works as a local proxy that redirects requests through external services.
 jenderal92/s3-bucket-take-0v3r
AWS AMAZON S3 Bucket Takeover Scanner & Claim Tool
 traccar/traccar
Traccar GPS Tracking System
 mgiay/cve-2026-8053-mongodb
Desc "CVE-2026-8053 CHECKER"-20260518-16h30-GMT+7
 wadesweaponshed/check-point-trusted-access-review
Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…