

area51
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
api-security-testingcloud-securityemail-security+4
7
thoropass-public/area51The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
 grabesec/xcp_ng_cve-2026-31431_tester
Non-destructive detector for CVE-2026-31431 (Copy Fail) local privilege escalation in XCP-ng 8.3 Dom0, validating kernel vulnerability via page-cache…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
 zeropathai/spinnaker-poc
POCs for CVE-2026-32604 and CVE-2026-32613 which allow post-auth RCE and credential theft in Spinnaker
 exploreunknowed/cve-2026-24306
Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…
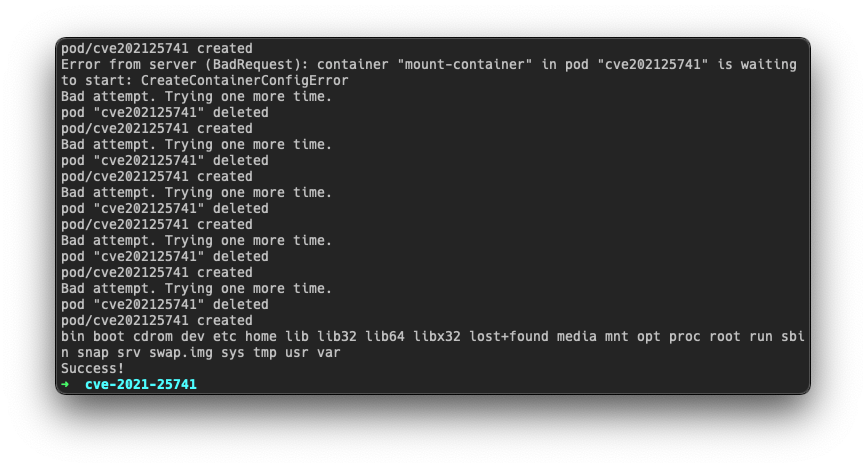 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 0rx1/cve-2021-43858
Exploit for MinIO privilege escalation vulnerability CVE-2021-43858, allowing unauthorized access to cloud storage. Written in Go, run with 'go run…
 yoshino-s/cve-2025-62506
Verification script for CVE-2025-62506, a privilege escalation vulnerability in MinIO service accounts, testing if restricted accounts can bypass…
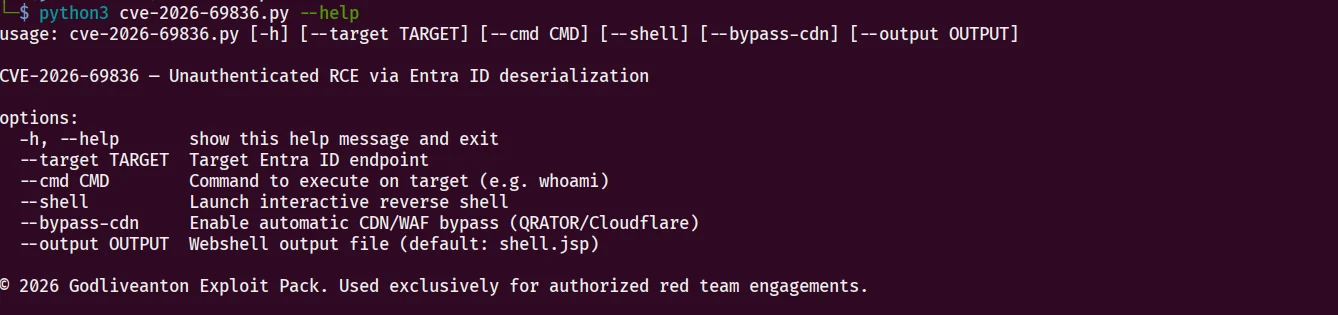 sentinel-aidefense/cve-2026-69836-exp
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 rockmelodies/bentoml_cve-2025-54381
Ai相关
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 biutrap/cve-2026-64849
Proof-of-concept exploit for CVE-2026-64849: triggers SSRF in MLflow webhook API via crafted POST, fetching cloud instance metadata from…
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…