azure-pentesting-suite

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…

Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…

Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…

Python3 rewrite of AsOutsider features of AADInternals

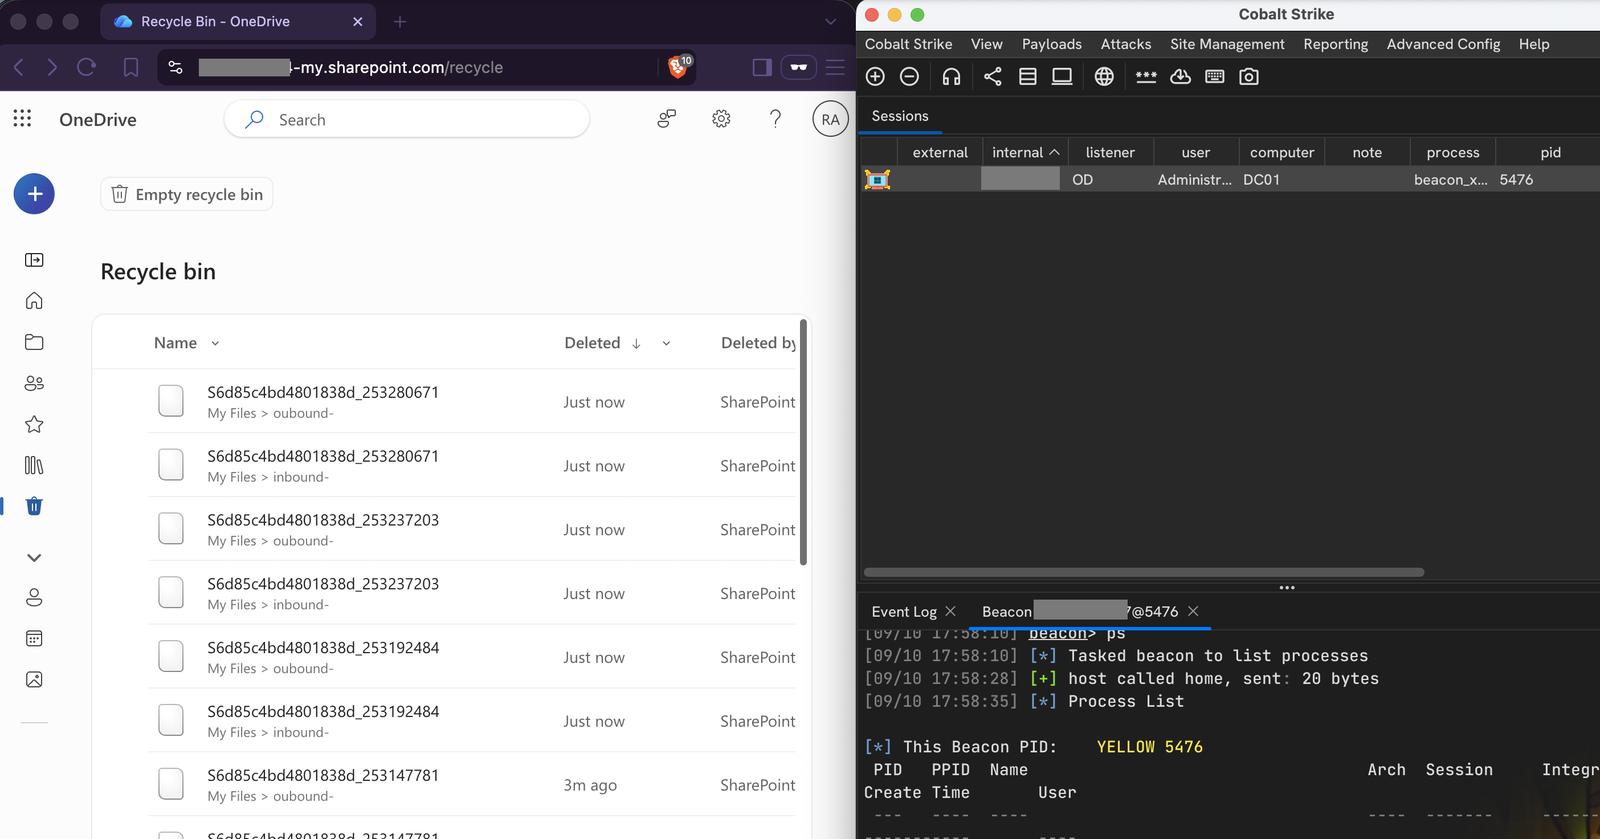
OneDrive as a covert C2 transport for Cobalt Strike

Proof-of-concept exploit for CVE-2026-32604, a command injection RCE in Spinnaker's GitRepo artifact handling via the version field.

Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)

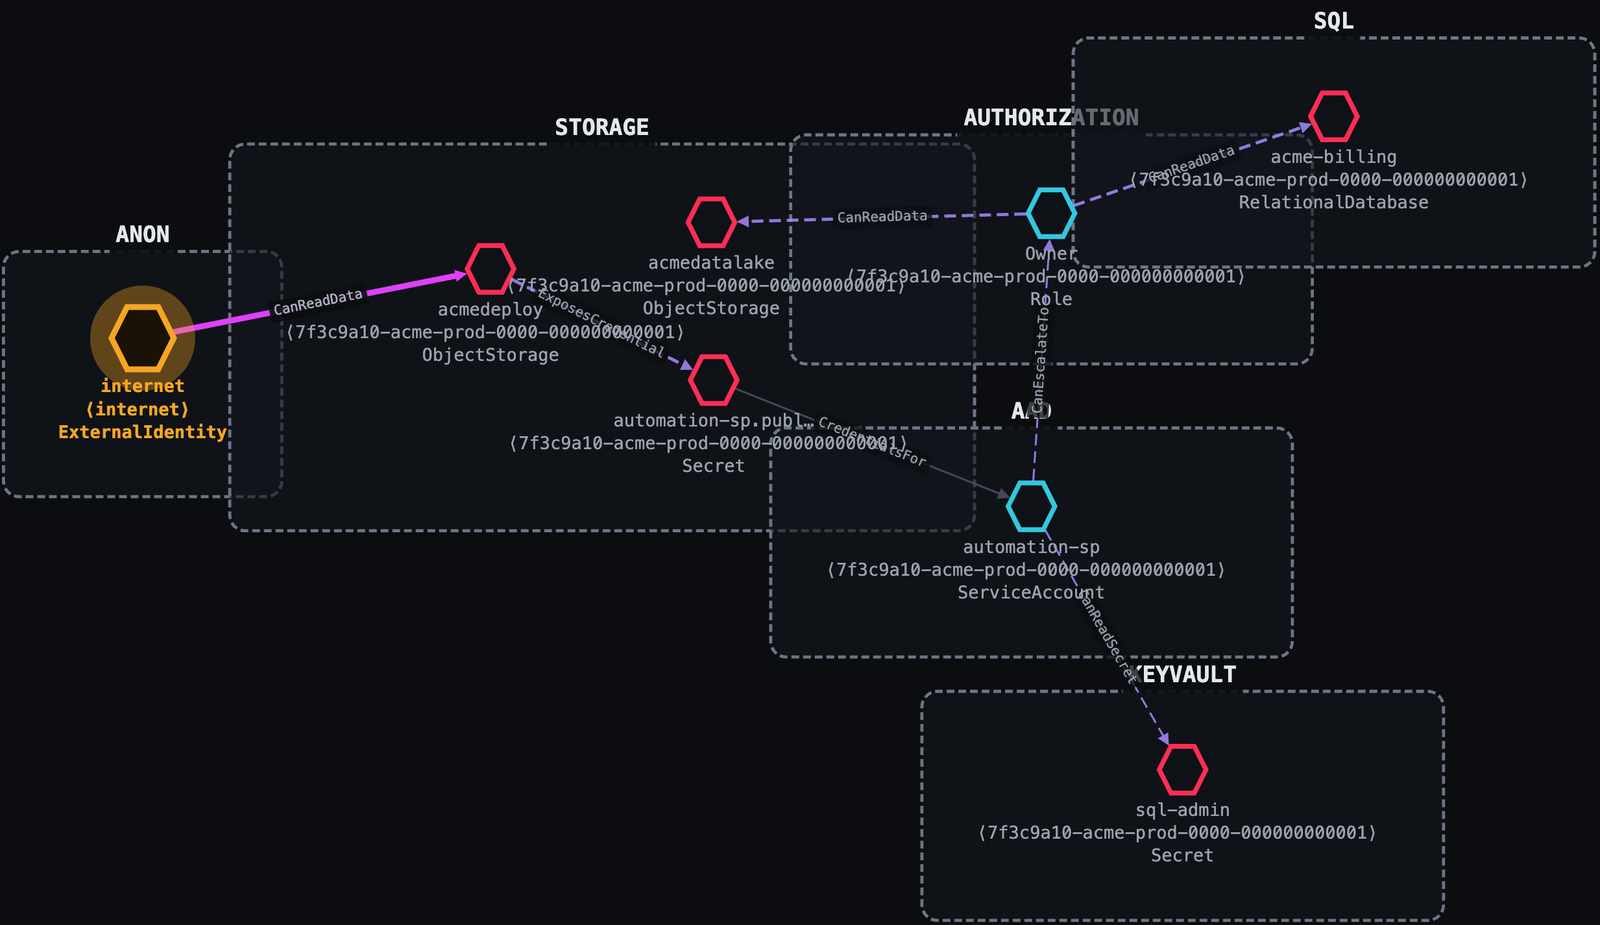
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…

A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…

Governed execution cells for AI agents.

Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

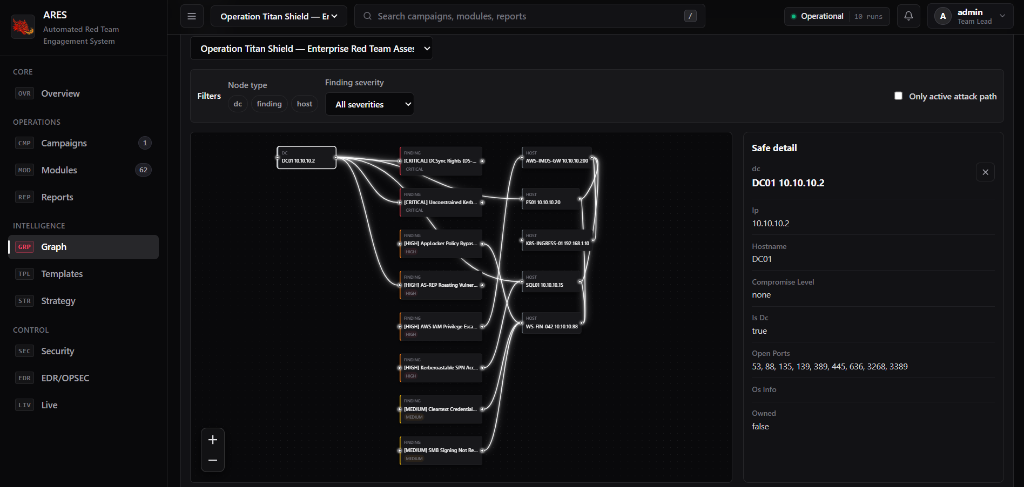
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…