

kube-reaper
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
cloud-securityconfiguration-auditingcontainer-security+9
3
stillbigjosh/kube-reaperScans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 tcollins-hashicorp/vault-cve-2026-5006-audit
Audit and educational toolkit for CVE-2026-5006, a Vault templated-policy slash-injection vulnerability. Includes a read-only audit script generating…
 xf-secops/cve-2026-32662
Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 yandex-cloud-examples/yc-mk8s-copy-fail-mitigation
DaemonSet для митигации уязвимости CVE-2026-31431 (Copy Fail)
 gduma-phdata/patch-cve-2026-07219
Deploys a critical patch for F5 BIG-IP iControl REST vulnerability CVE-2026-07219, with validation and deployment tracking for production…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
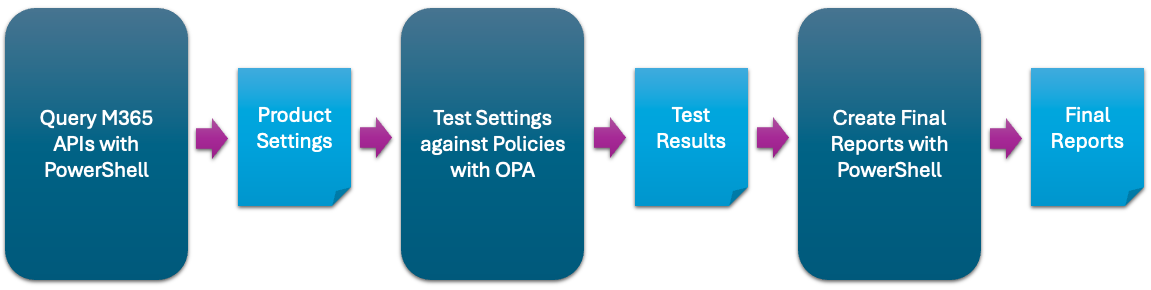 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…