

waf-fu
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
cloud-securitydefensive-toolsincident-response+6
2
confused-binary/waf-fuTerminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 eshlomo1/microsoft-sentinel-secops
SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
 unfold-security/cve-2026-41940-detection
Detection signatures for CVE-2026-41940 and shemas for cPanel logs
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
 darwinsec/defcon-kql-kung-fu-22
DEF CON Cloud Village workshop slides teaching KQL for cloud security log analysis, with practical exercises in a shared Azure Log Analytics…
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
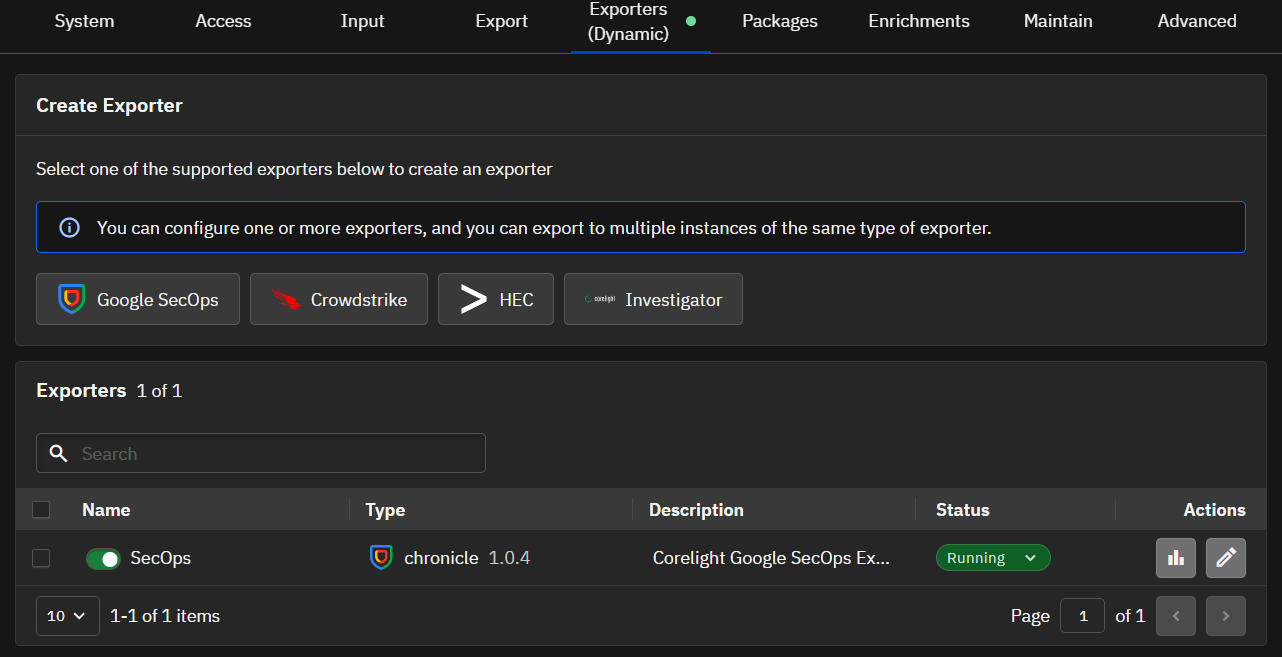 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 githubfoam/nxlog-ubuntu-githubactions
CI pipeline for building nxlog-ce on Ubuntu with CVE-2020-35488 vulnerability detection, enabling automated log collection and security auditing in…
 aleongx/kql_sentinel_cve-2025-21333
KQL para deteccion de CVE-2025-21333 en Sentinel
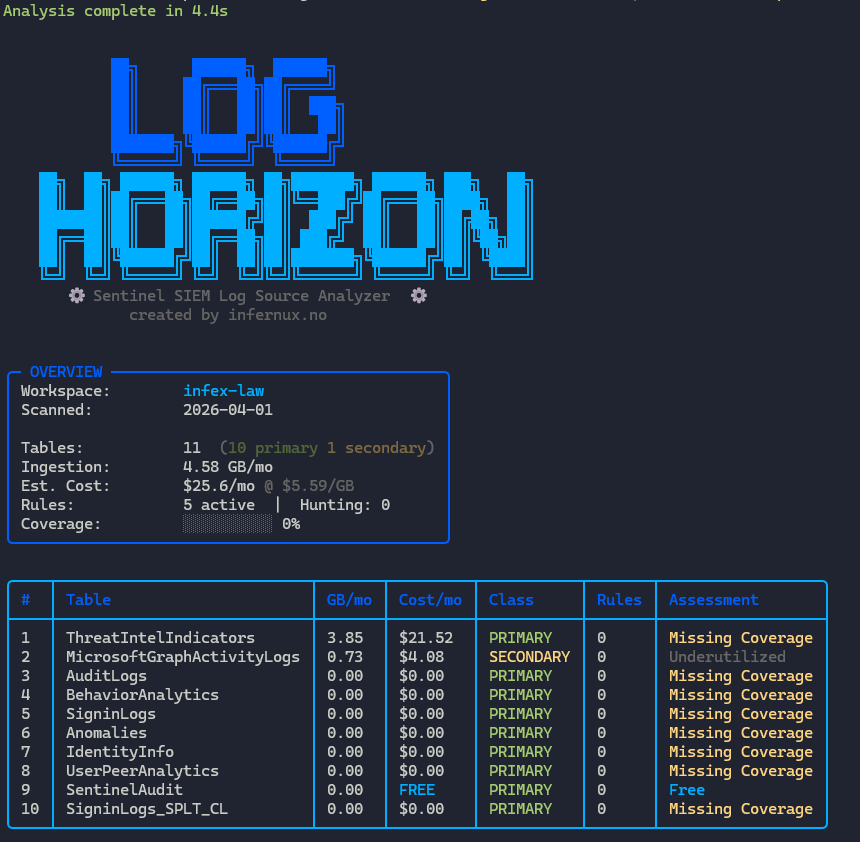 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 hybridbrothers/hunting-queries-detection-rules
The purpose of this repository is to share KQL queries to help identify security misconfigurations, hunt for specific patterns, or detect malicious…
 alteredsecurity/cve-2021-38647
CVE-2021-38647 - POC to exploit unauthenticated RCE #OMIGOD
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
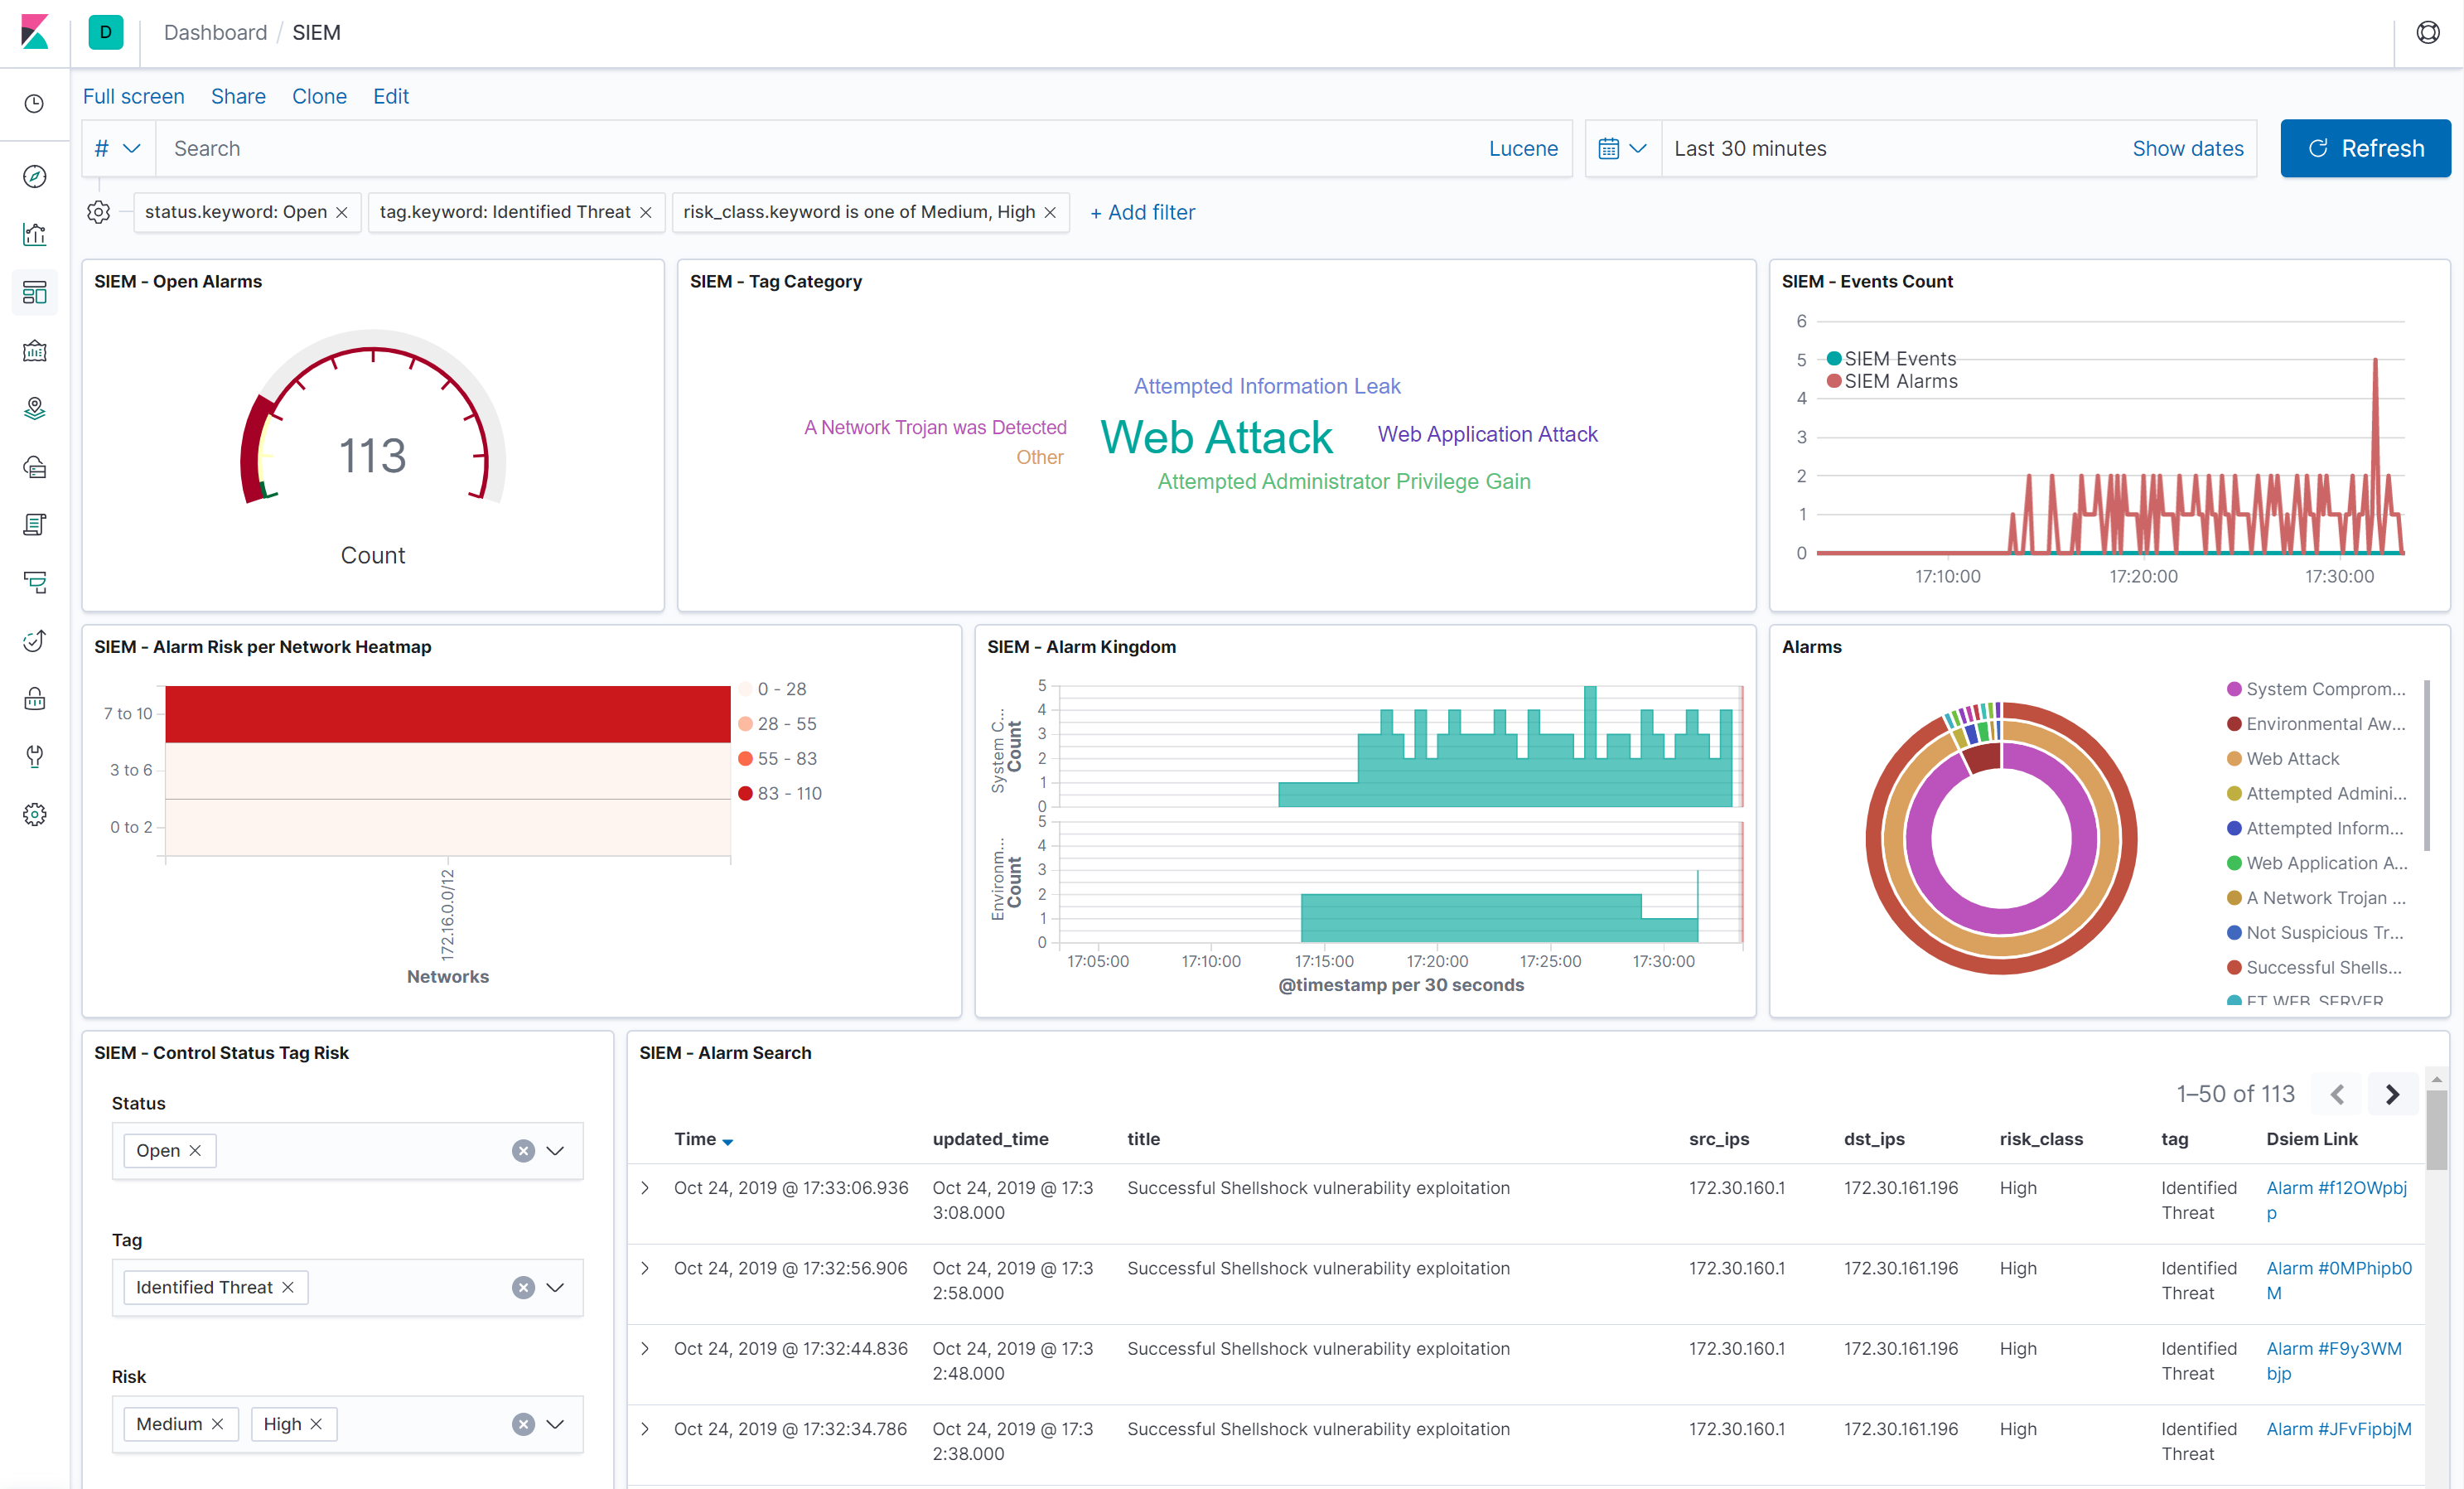 defenxor/dsiem
Security event correlation engine for ELK stack
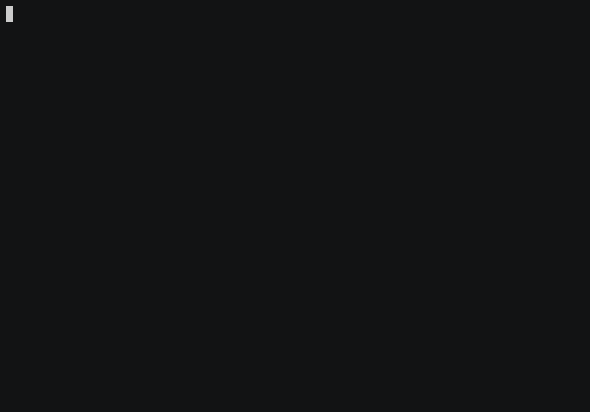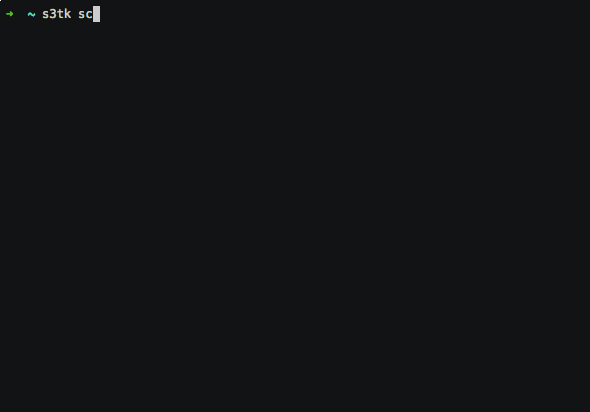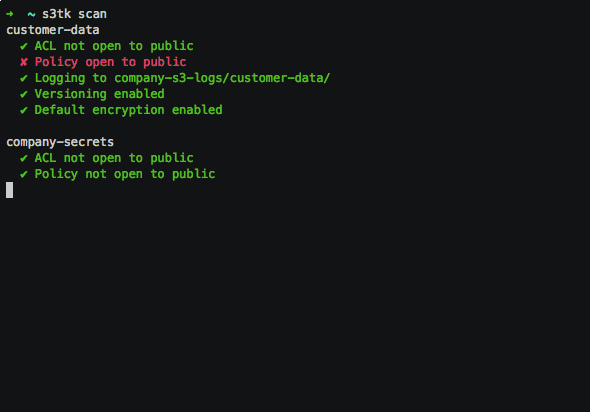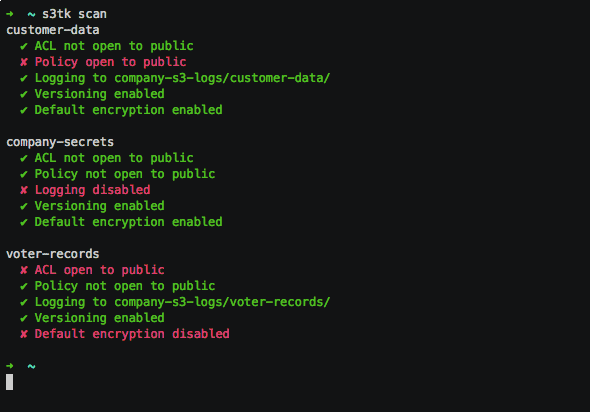 ankane/s3tk
A security toolkit for Amazon S3
 matanolabs/matano
Open source security data lake for threat hunting, detection & response, and cybersecurity analytics at petabyte scale on AWS