

Vader-Pro-VDR
 tridents10/vader-pro-vdr
AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
ai-securitycloud-securityconfiguration-auditing+5
1
tridents10/vader-pro-vdrAI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
 oscerd/cve-2026-79986
Reproducer and analysis for CVE-2026-79986, a path traversal in Apache Camel camel-azure-files where share listing names escape the polled directory.
 diedromeo/cve-2026-62201-openclaw-ssrf
Deep-dive analysis of CVE-2026-62201: OpenClaw sandbox exec-server network policy bypass (SSRF). Root cause, vulnerable vs patched code,…
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 grabesec/xcp_ng_cve-2026-31431_tester
Non-destructive detector for CVE-2026-31431 (Copy Fail) local privilege escalation in XCP-ng 8.3 Dom0, validating kernel vulnerability via page-cache…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 mbanyamer/cve-2026-24514-kubernetes-dos
Proof-of-concept exploit for CVE-2026-24514, a memory exhaustion denial-of-service in ingress-nginx validating admission webhook, allowing…
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
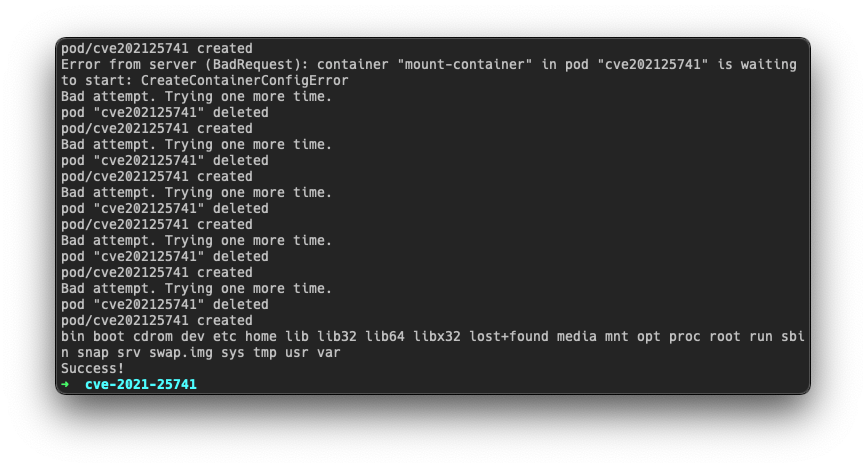 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 0rx1/cve-2021-43858
Exploit for MinIO privilege escalation vulnerability CVE-2021-43858, allowing unauthorized access to cloud storage. Written in Go, run with 'go run…
 yoshino-s/cve-2025-62506
Verification script for CVE-2025-62506, a privilege escalation vulnerability in MinIO service accounts, testing if restricted accounts can bypass…
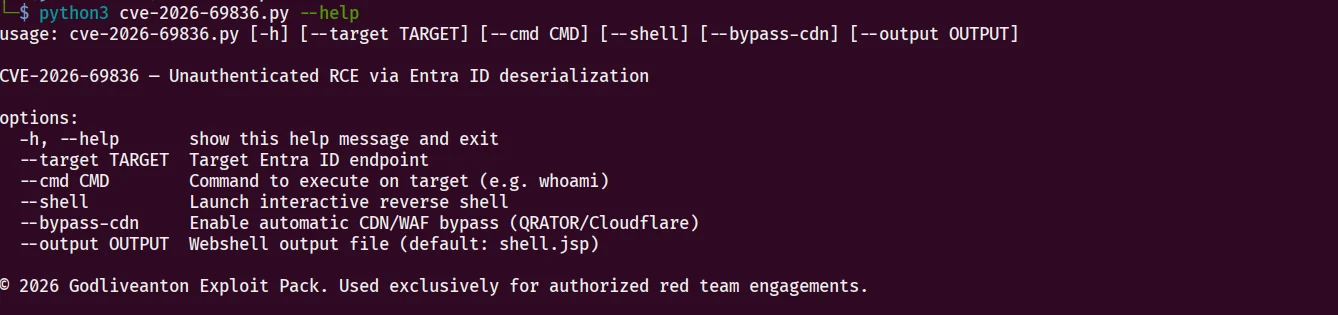 sentinel-aidefense/cve-2026-69836-exp
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization