
RAGE
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
cloud-securityconfiguration-auditingdefensive-tools+7
6
trustedsec/rageVendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 ustayready/thunderstorm
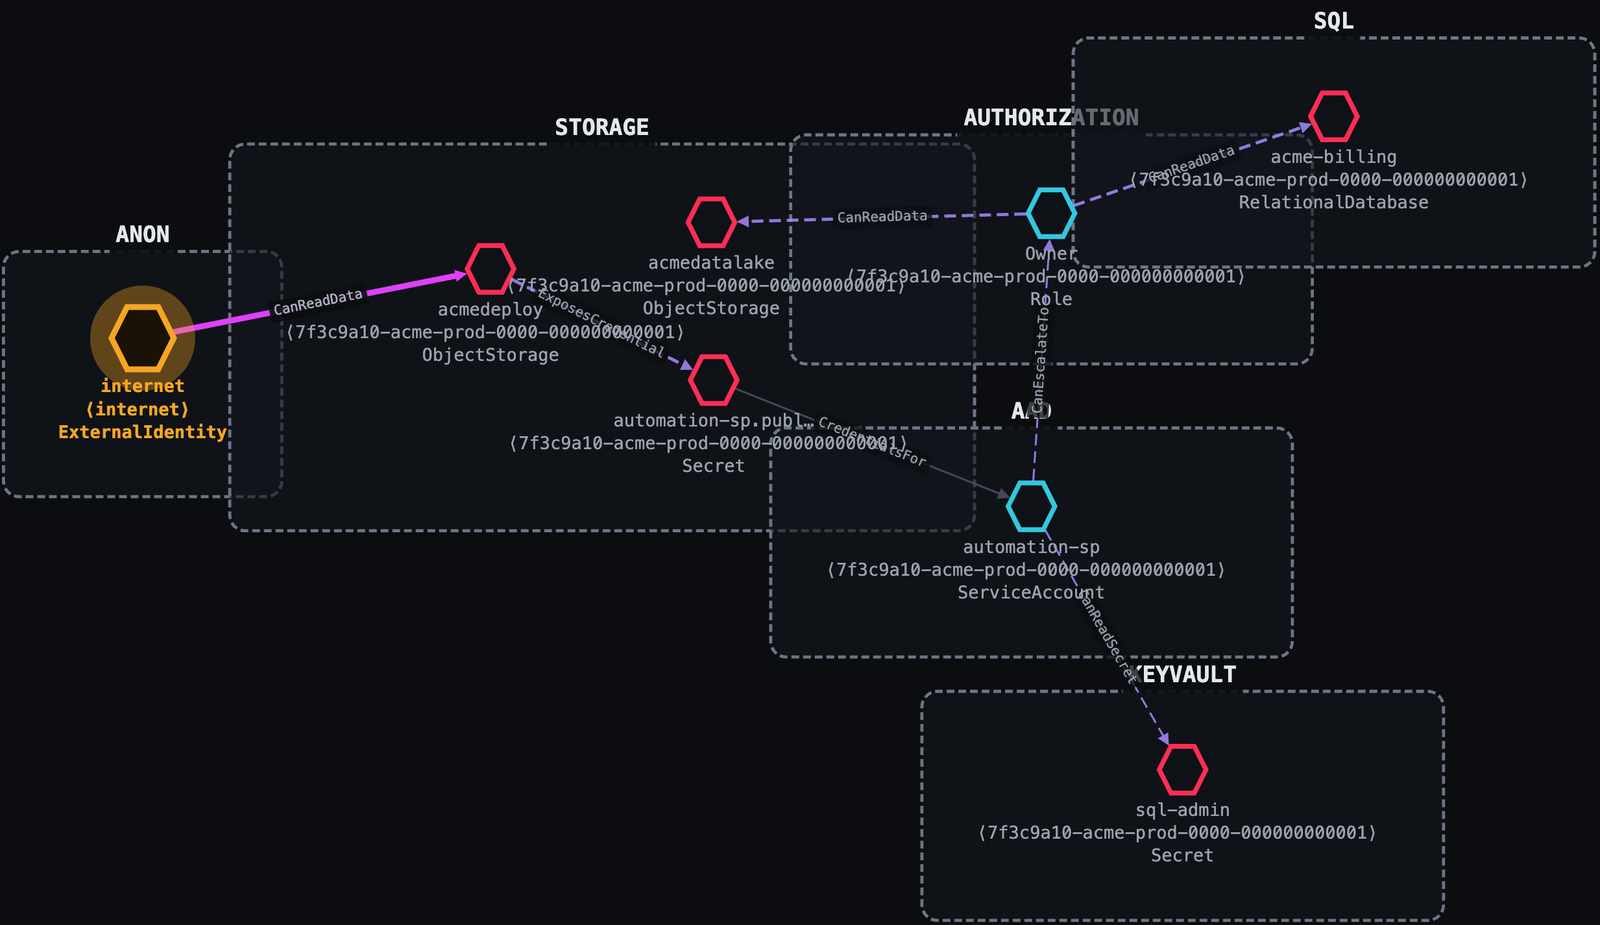
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 runewardd/runeward
Governed execution cells for AI agents.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
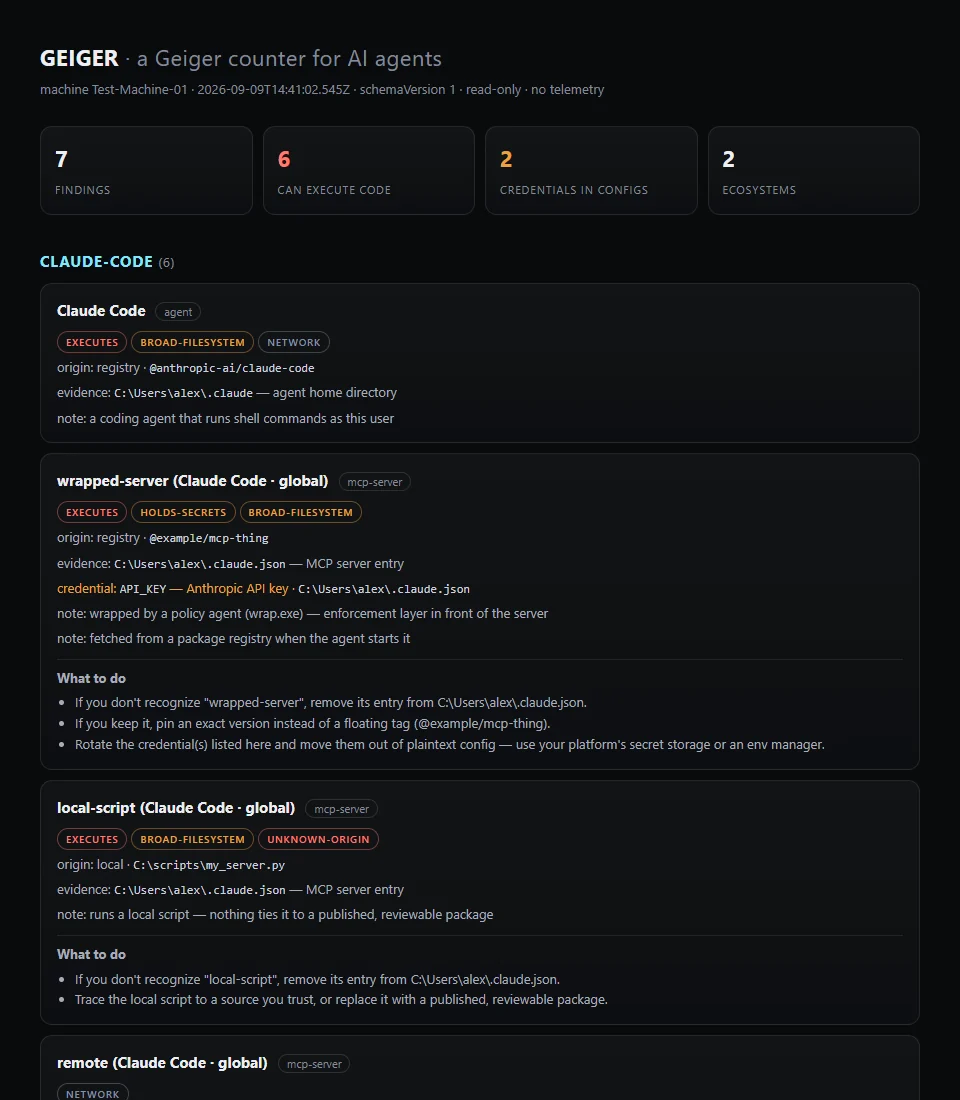 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 pvharmo2/gha-lab-8aba6b05dc
Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 pvharmo2/gha-lab-3f1ff30e9c
Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…