
osmedeus
 j3ssie/osmedeus
A Modern Orchestration Engine for Security
cloud-securitydevsecopsinformation-gathering+5
j3ssie/osmedeusA Modern Orchestration Engine for Security
 apache/brpc
Industrial-grade C++ RPC framework for building high-performance distributed systems, supporting multiple protocols (HTTP, gRPC, Redis, Thrift) with…
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
 koenrh/s3enum
Fast and stealthy Amazon S3 bucket enumeration tool for pentesters.
 cnotin/m365_groups_enum
Enumerate Microsoft 365 Groups in a tenant with their metadata
 chrismaddalena/odin
Automated network asset, email, and social media profile discovery and cataloguing.
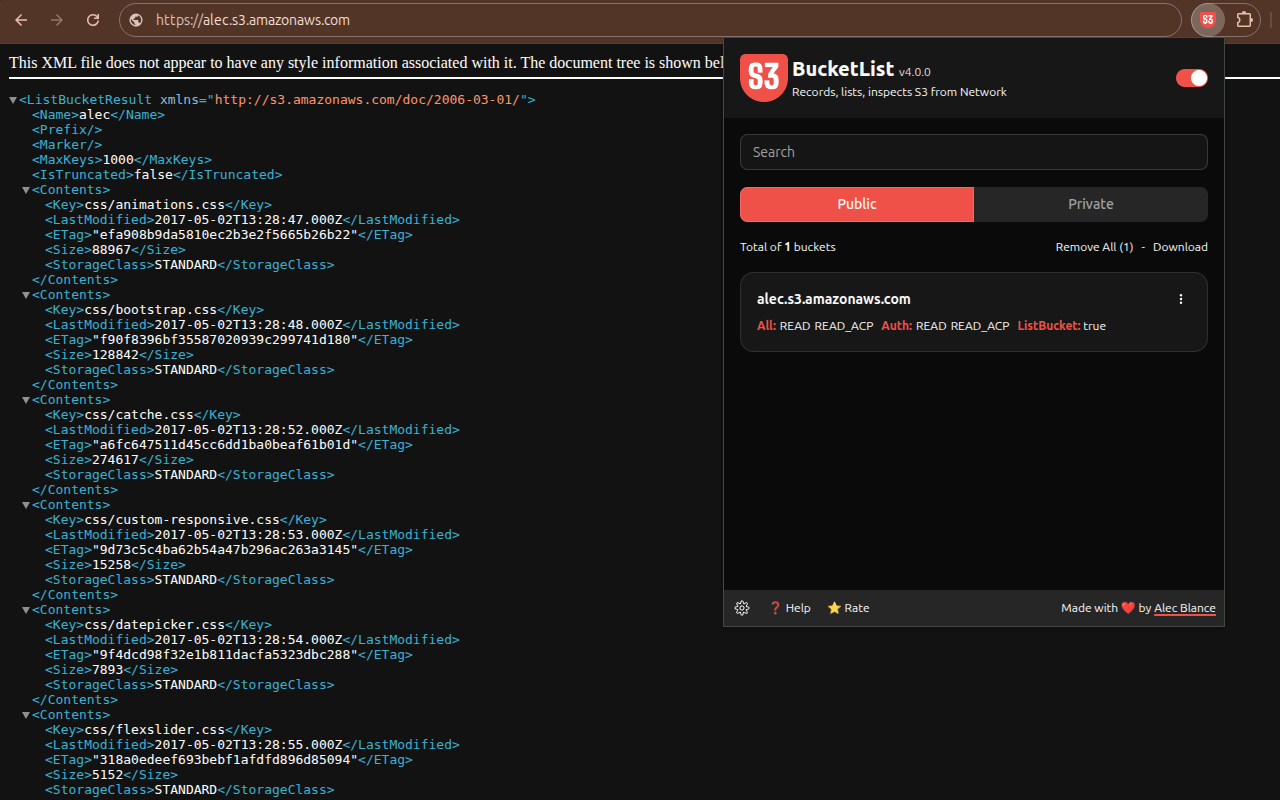 alecblance/s3bucketlist
Chrome and Firefox extension that lists Amazon S3 Buckets while browsing
 sebastian-mora/aws-loot
Enumerates AWS environments for secrets by scanning EC2 userdata, Lambda environment variables and source code, and CodeBuild instances for…
 hahwul/s3reverse
The format of various s3 buckets is convert in one format. for bugbounty and security testing.
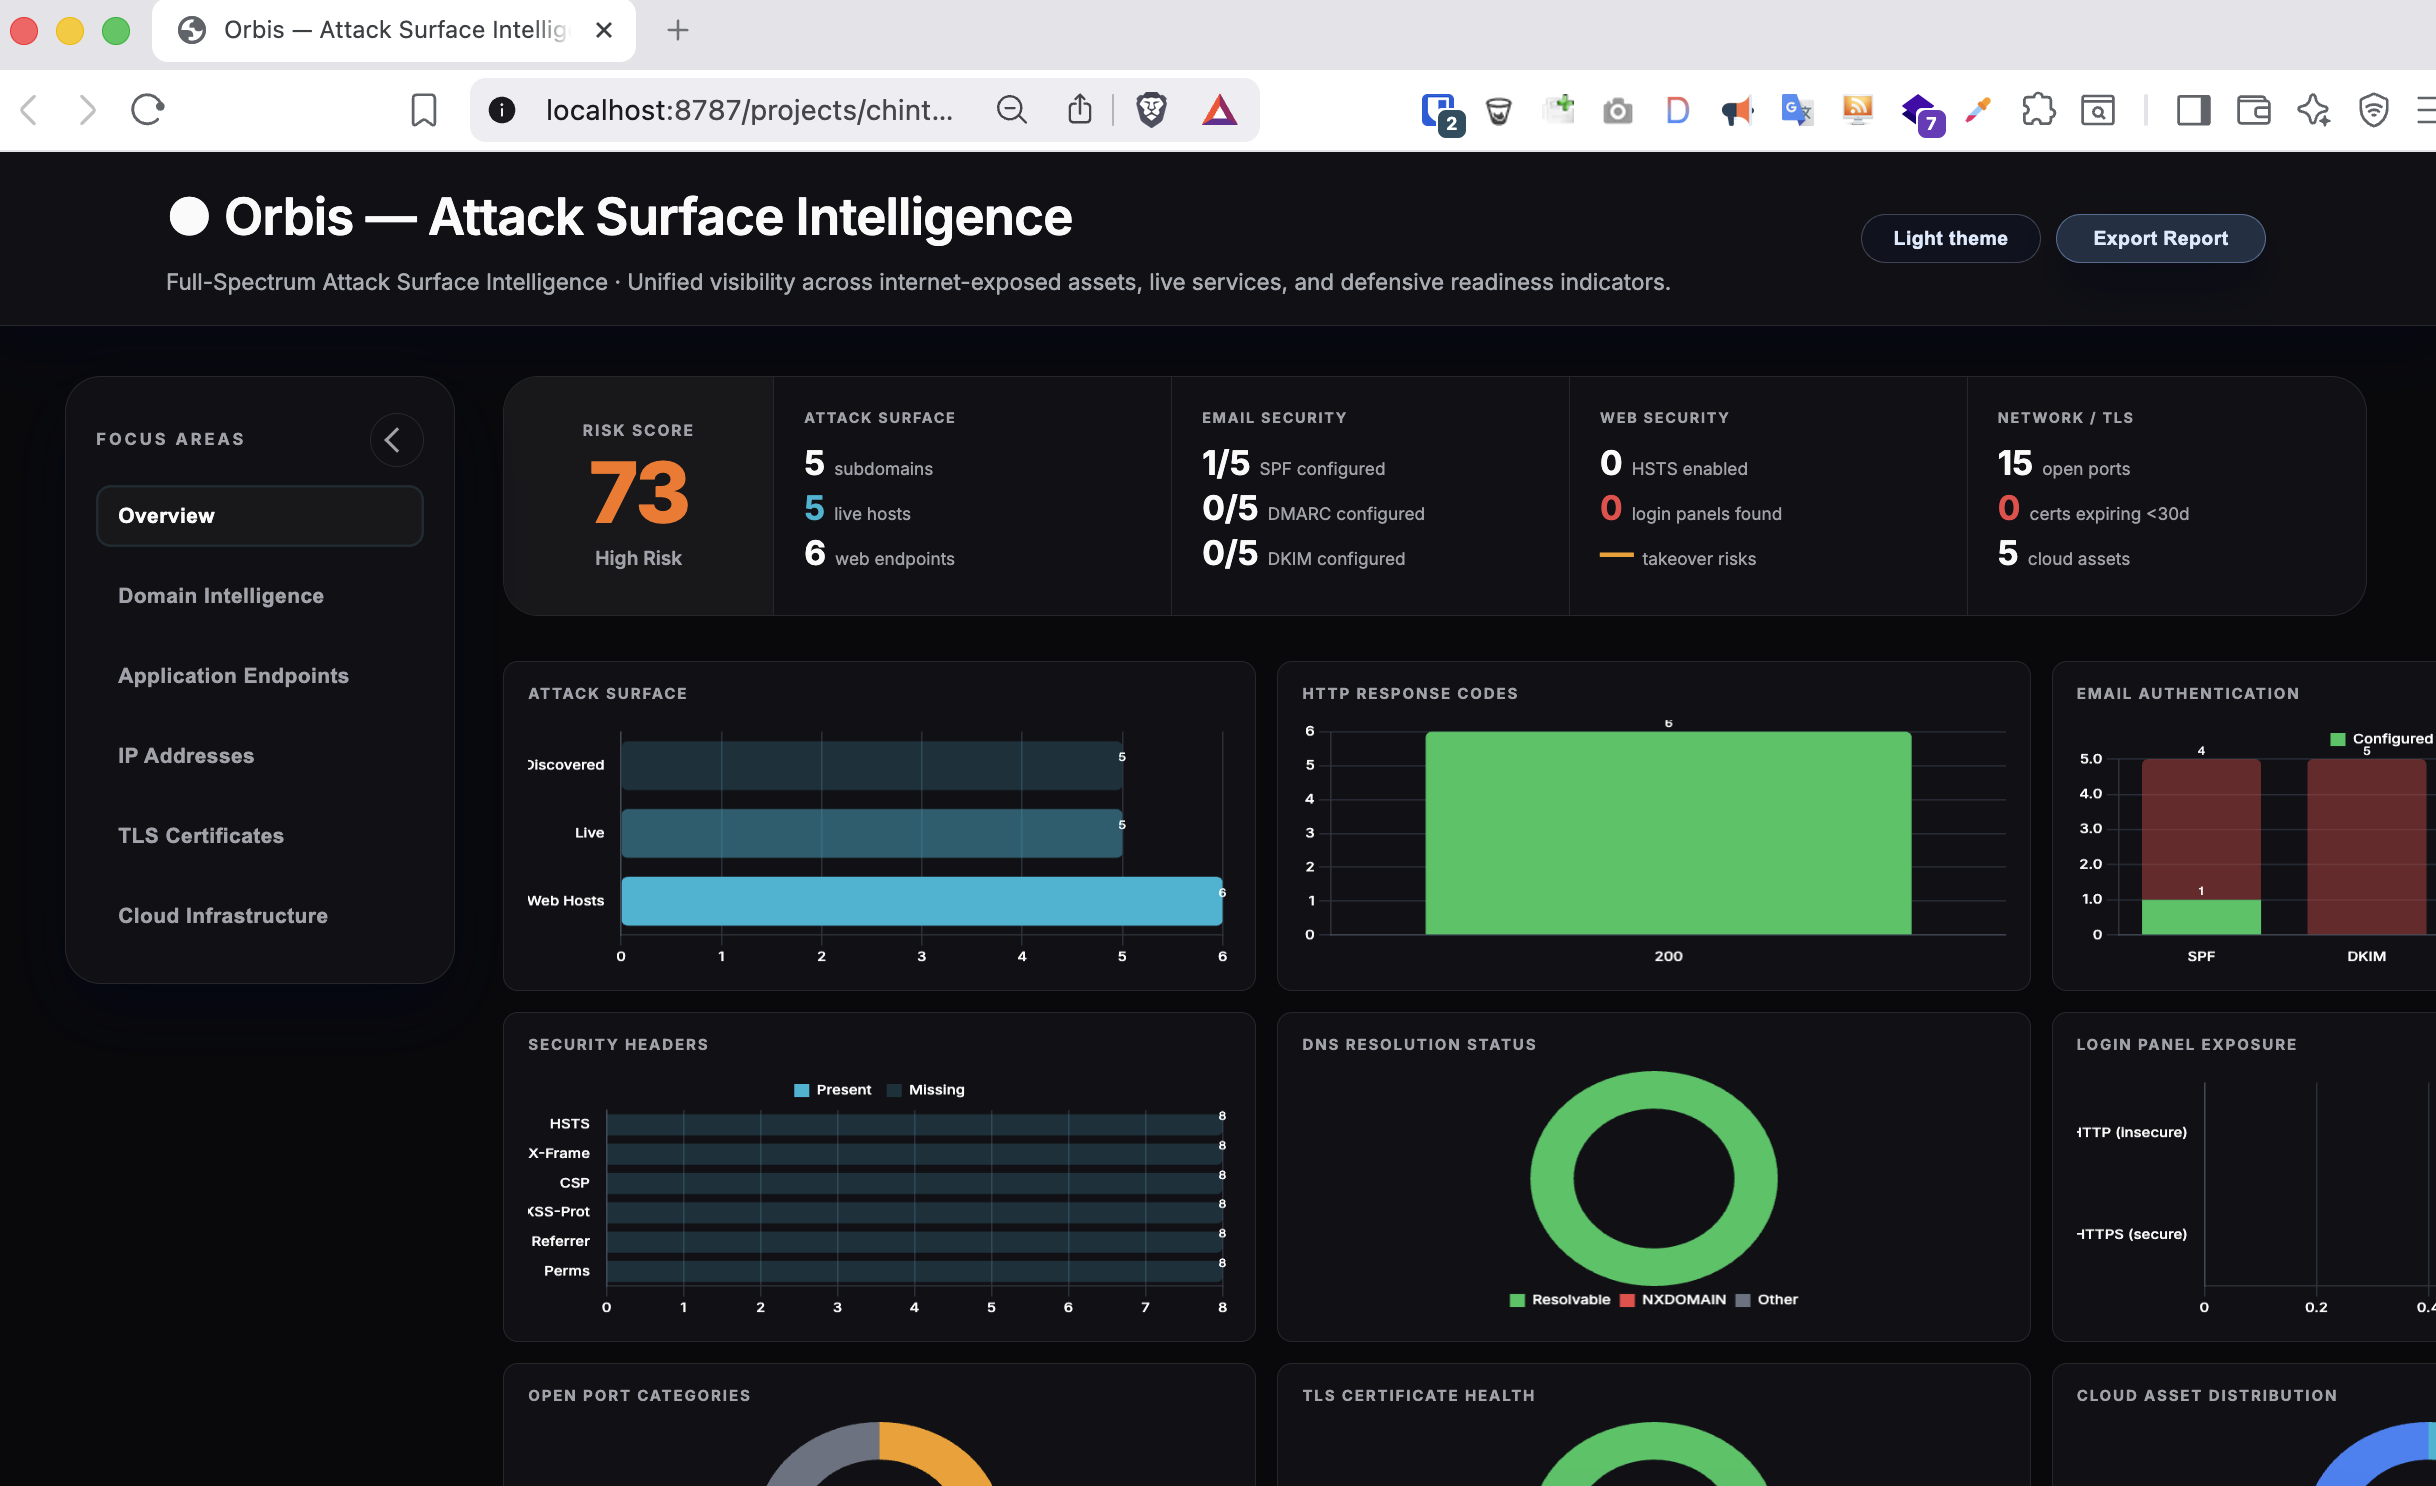 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 specterops/azurehound
Collects Azure tenant data (users, groups, roles, resources) and exports it for BloodHound attack path analysis in cloud penetration testing and red…
 securisec/cliam
Cloud agnostic IAM permissions enumerator
 ph33rr/cirrusgo
A fast tool to scan SAAS,PAAS App written in Go
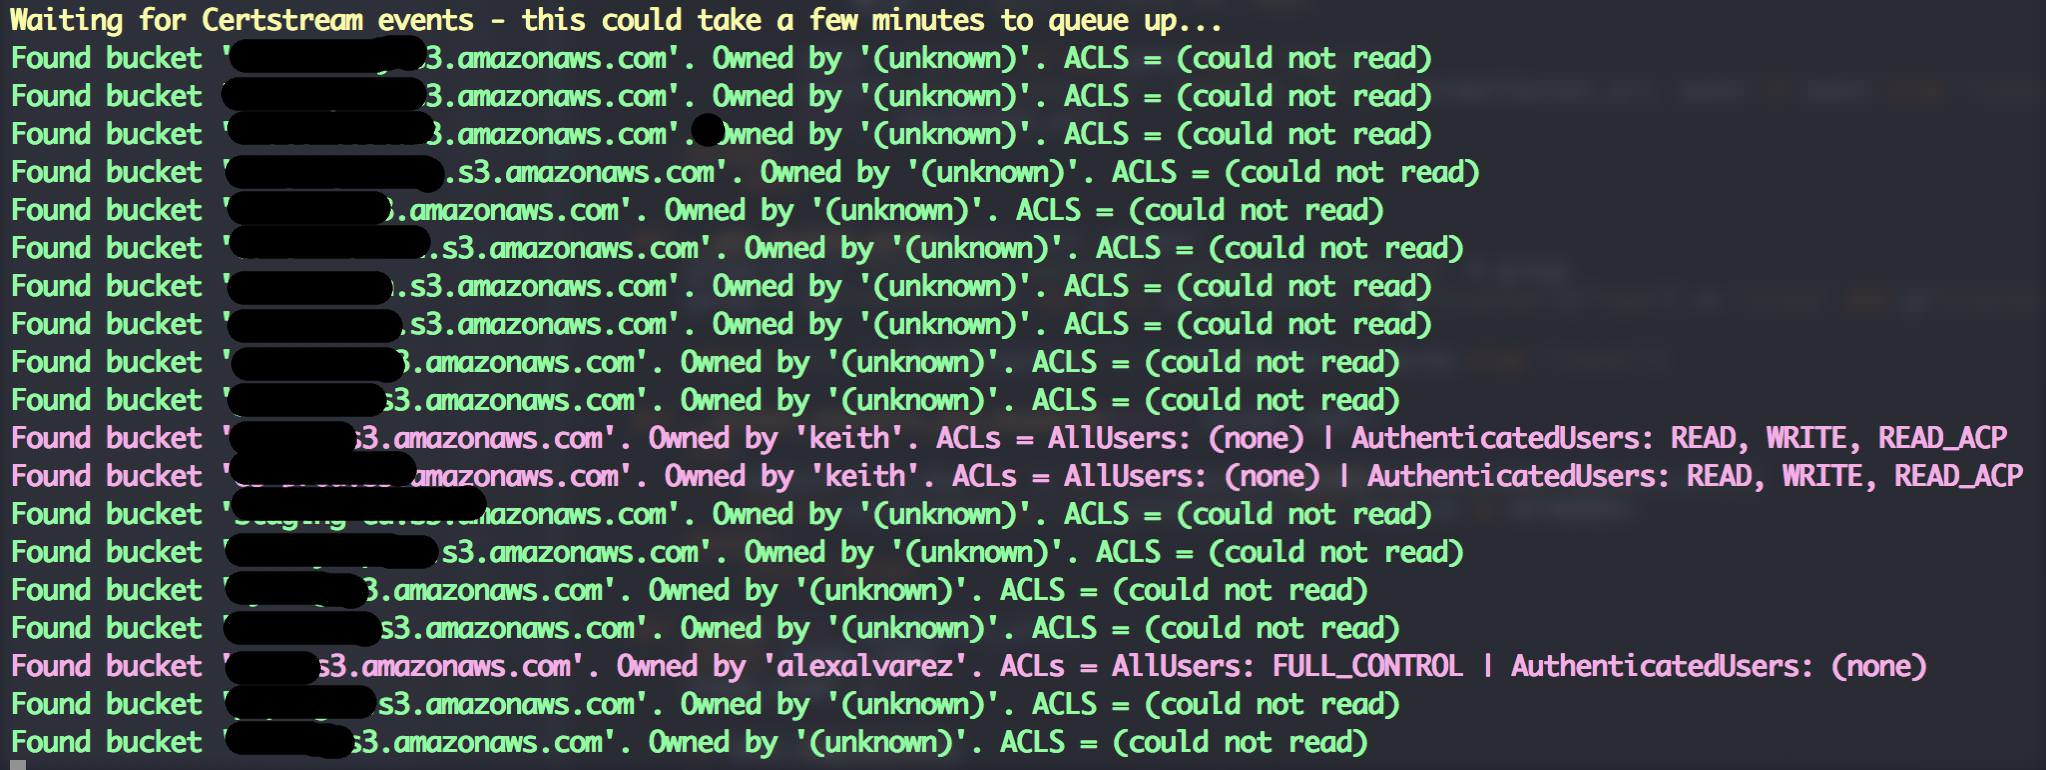 eth0izzle/bucket-stream
Find interesting Amazon S3 Buckets by watching certificate transparency logs.
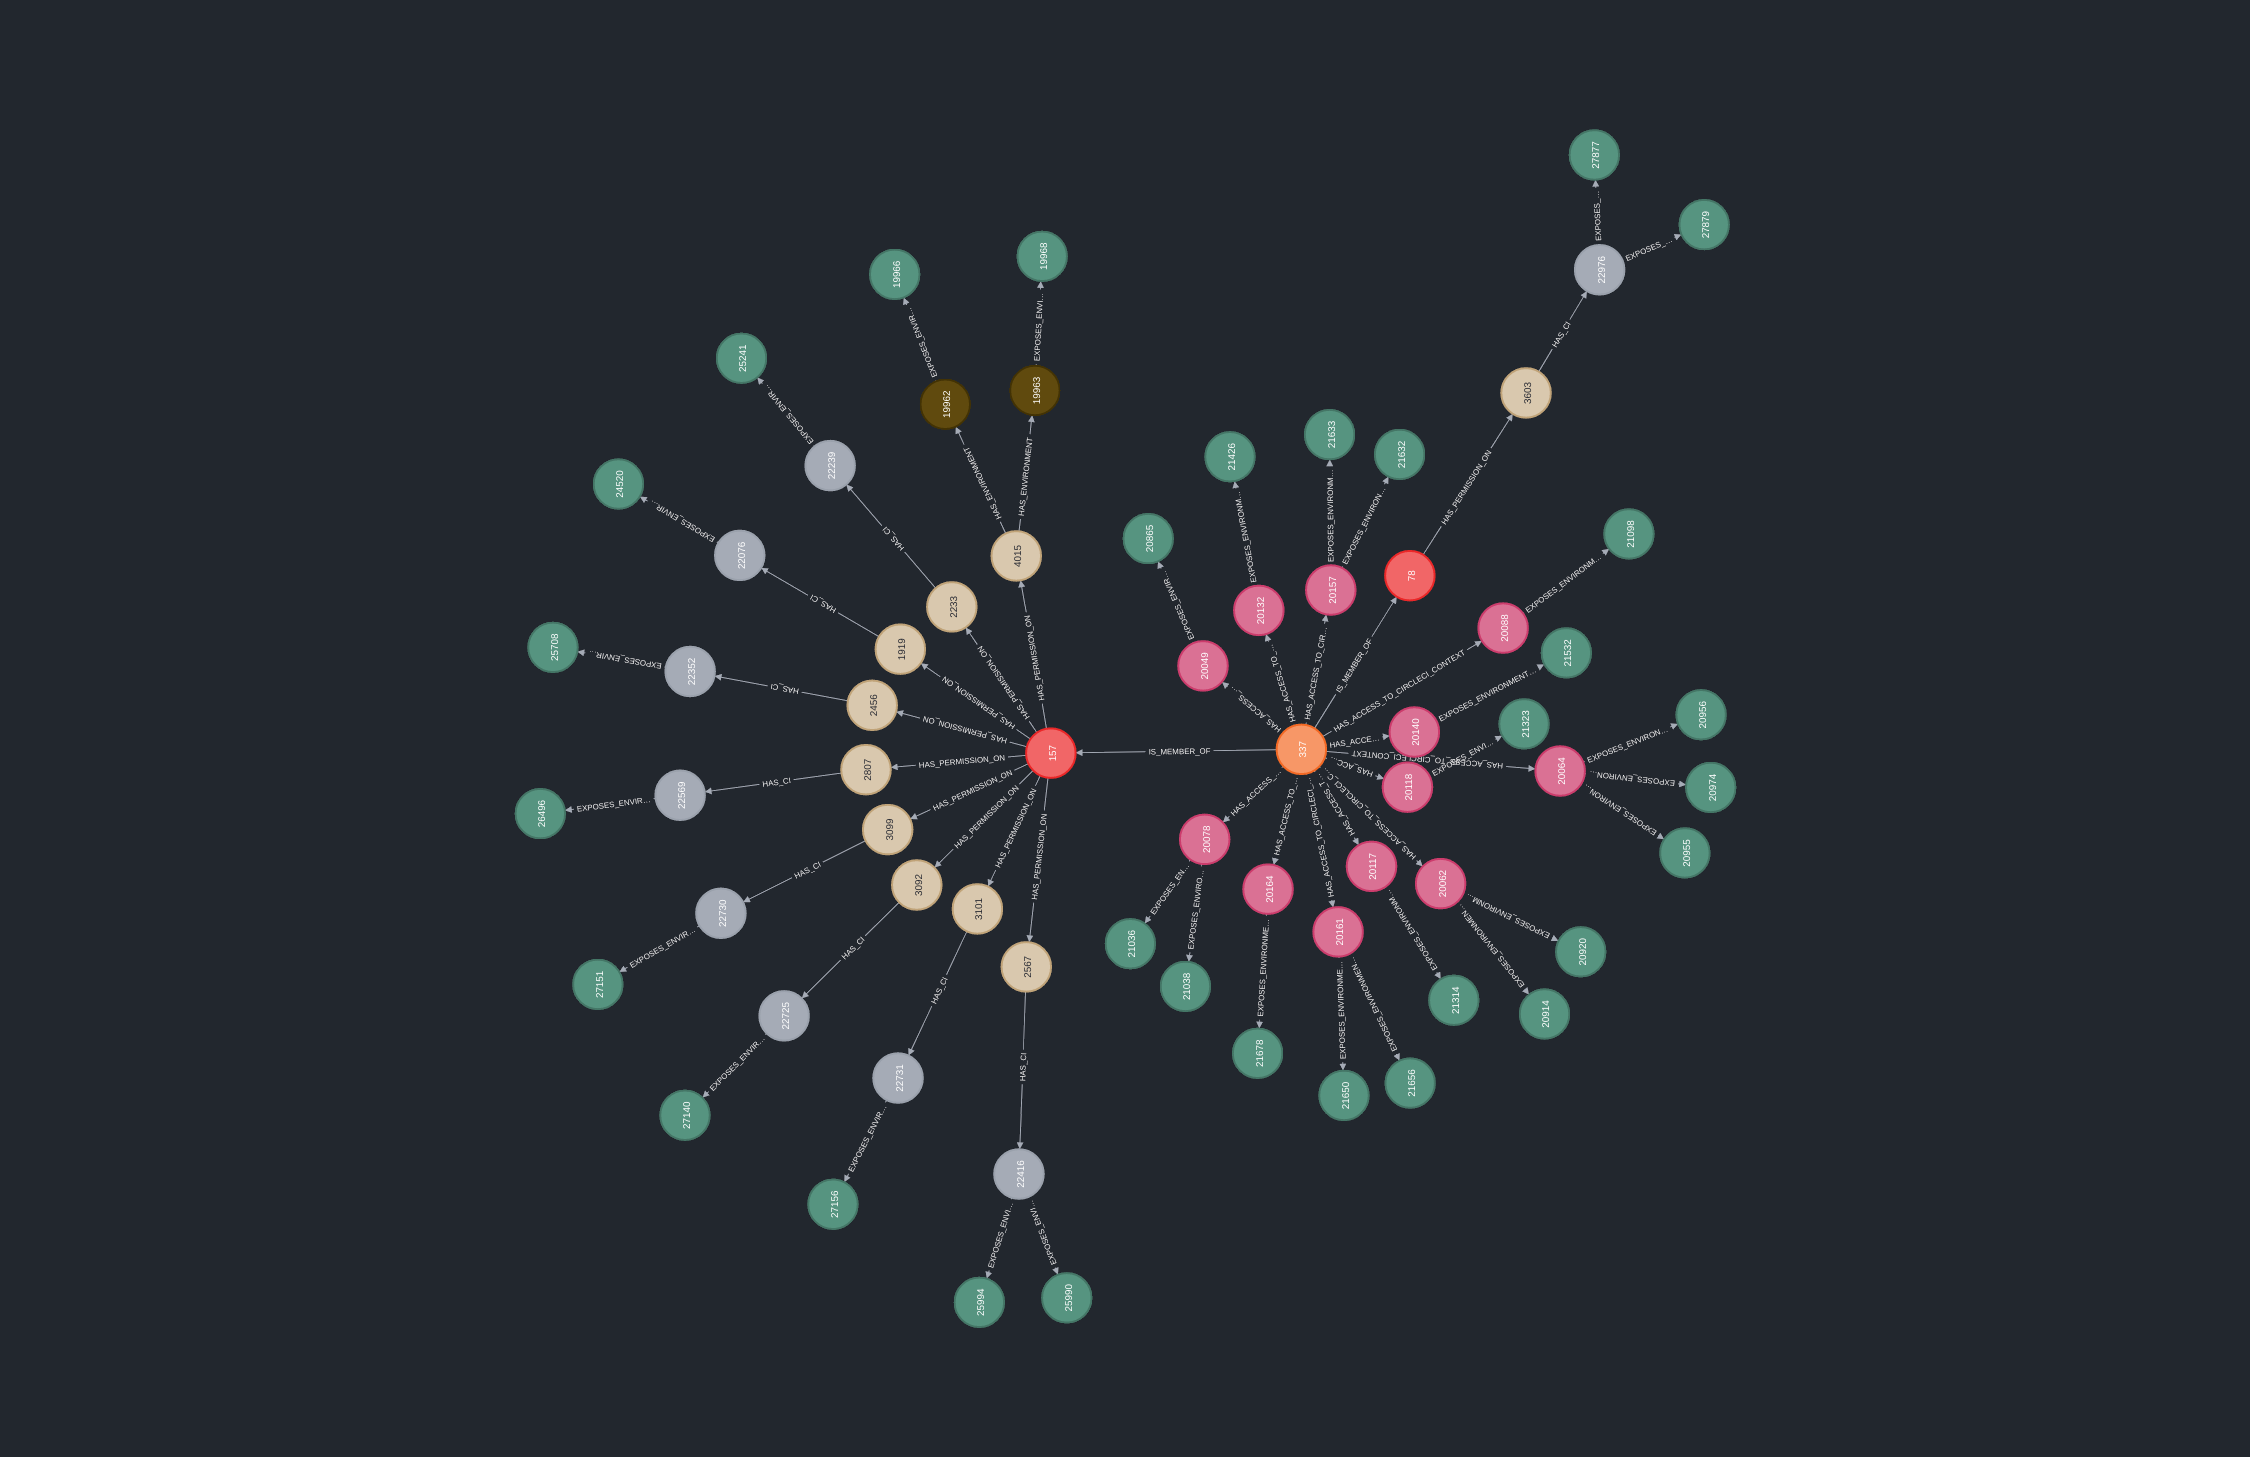
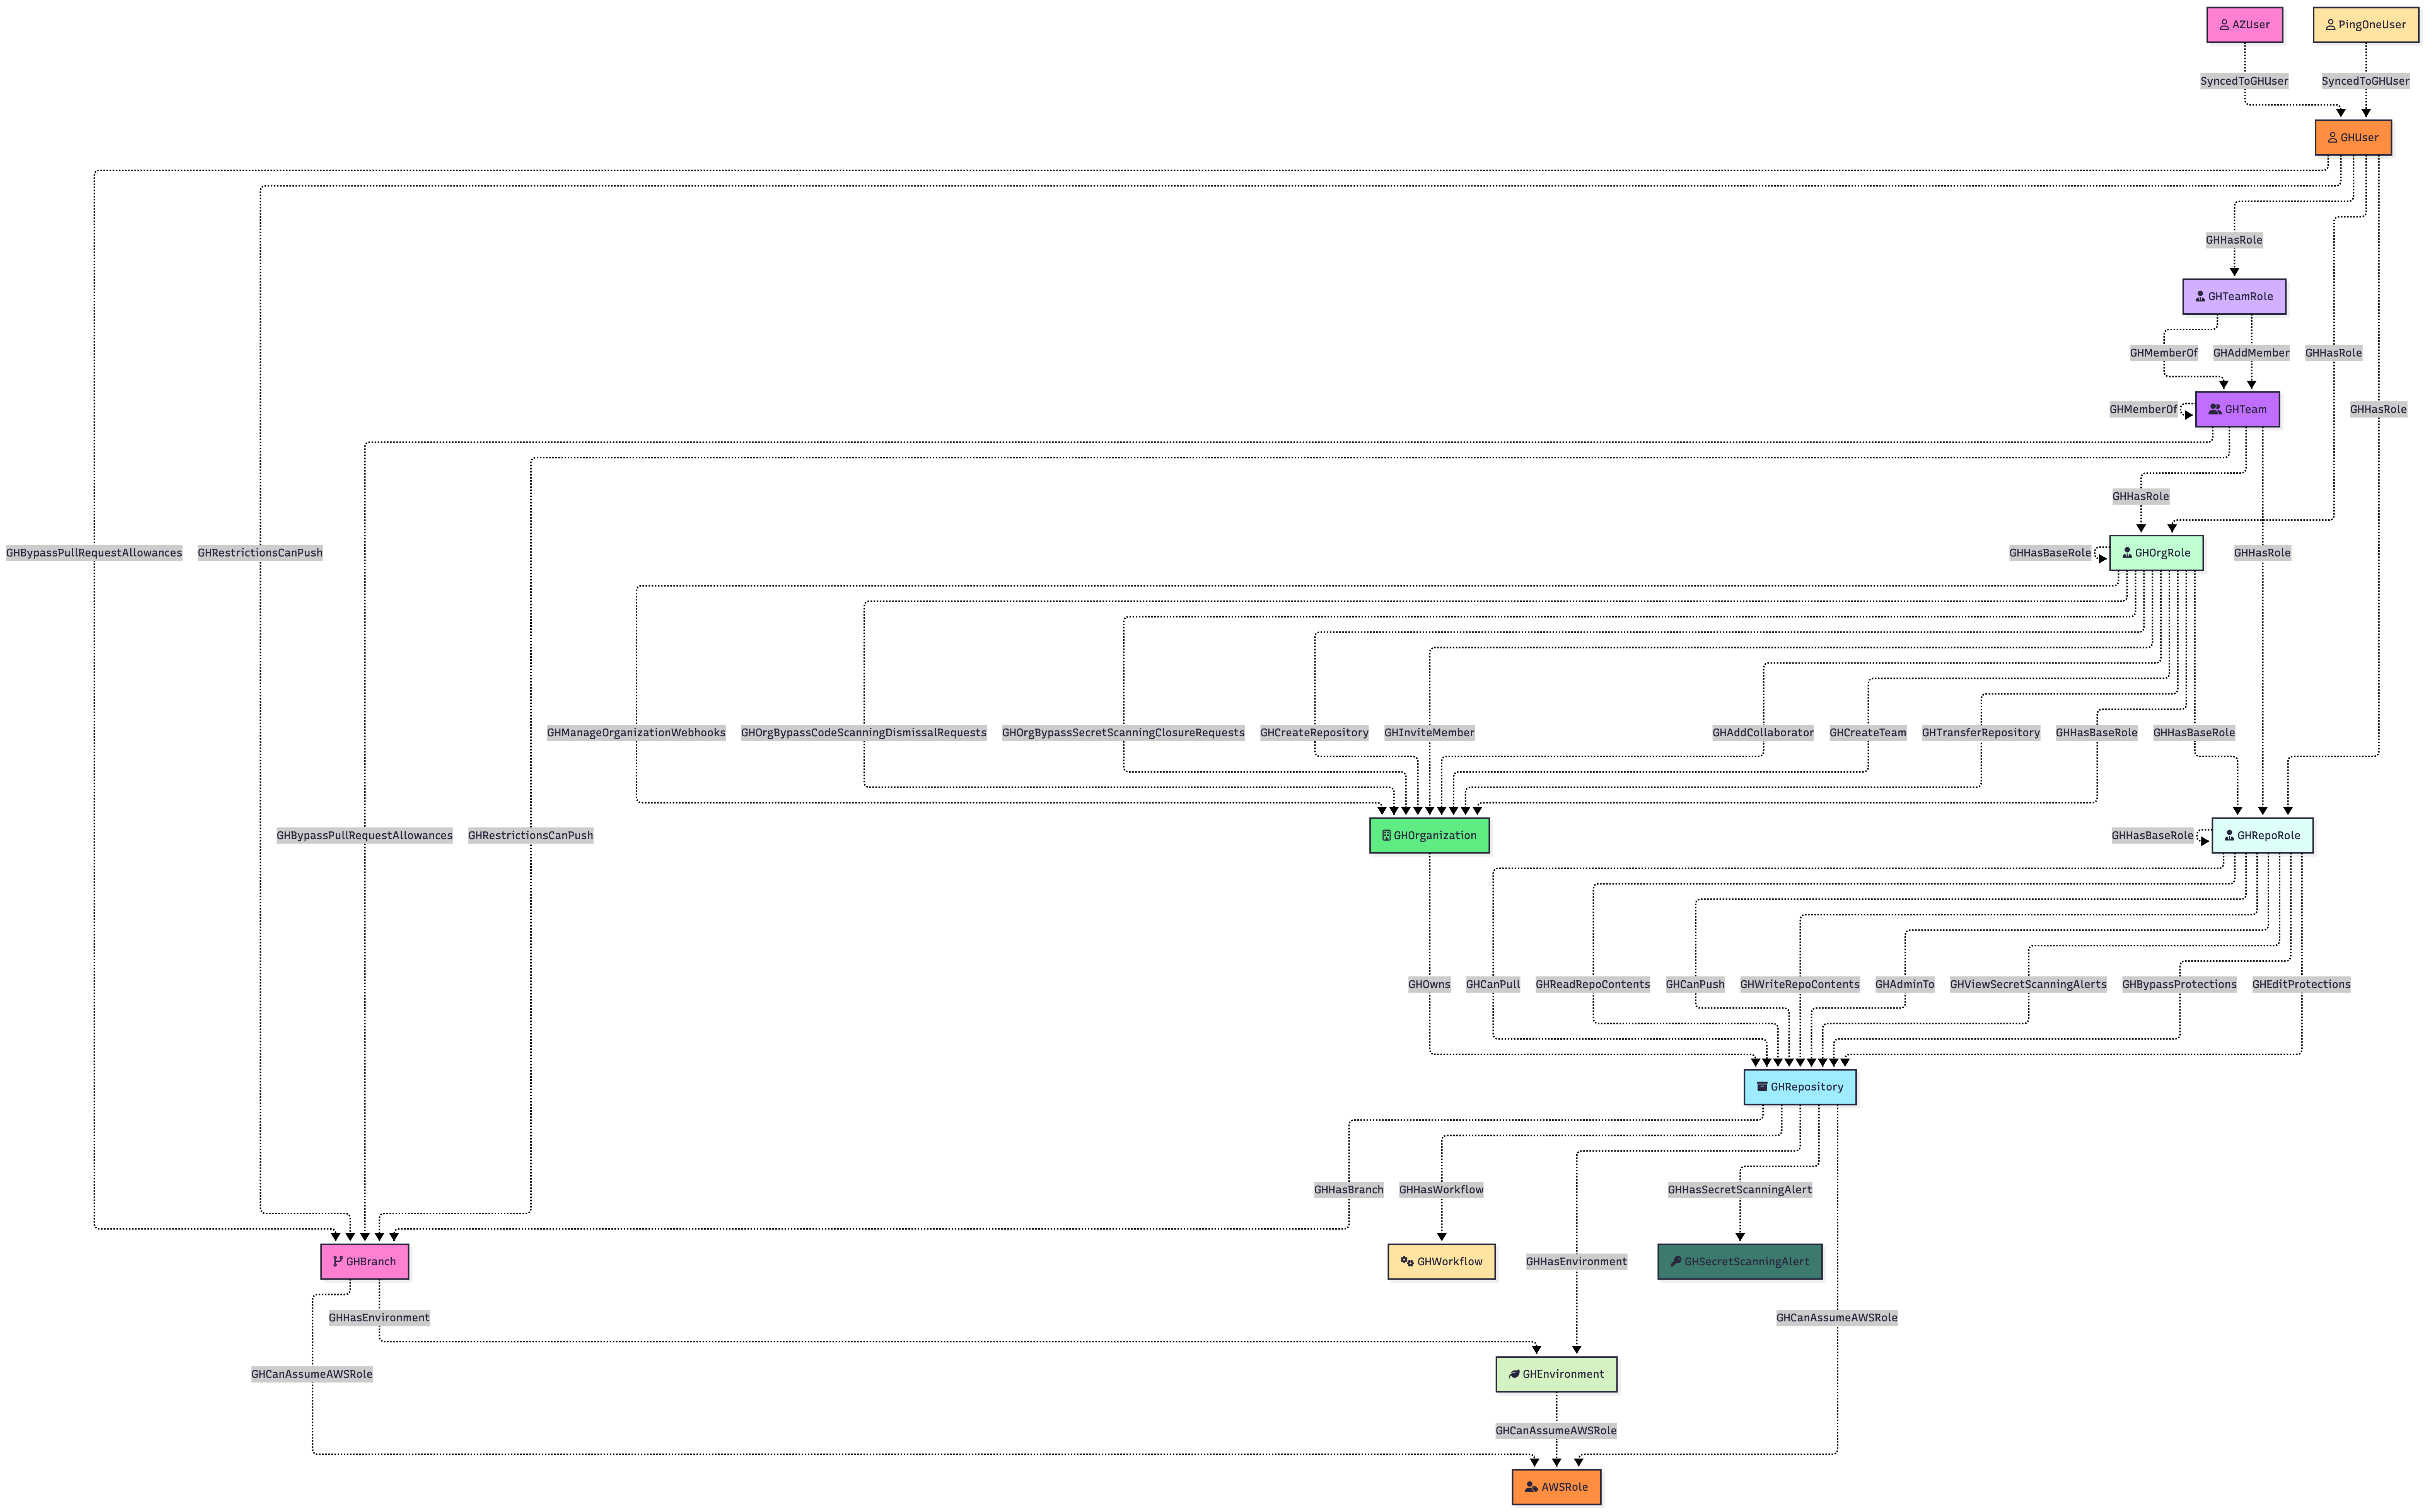 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 jordanpotti/awsbucketdump
Security Tool to Look For Interesting Files in S3 Buckets
 netspi/ateam
Python reconnaissance tool for discovering Azure services and attributing tenant ownership via DNS validation, multi-service probing, and response…