
ayaFlow
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
cloud-securitydns-analysisnetwork-mapping+2
davidhavoc/ayaflowA high-performance, eBPF-based network traffic analyzer written in Rust.
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 chrismaddalena/odin
Automated network asset, email, and social media profile discovery and cataloguing.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 secdev02/easytokens
Kali365 - EvilTokens Replica
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
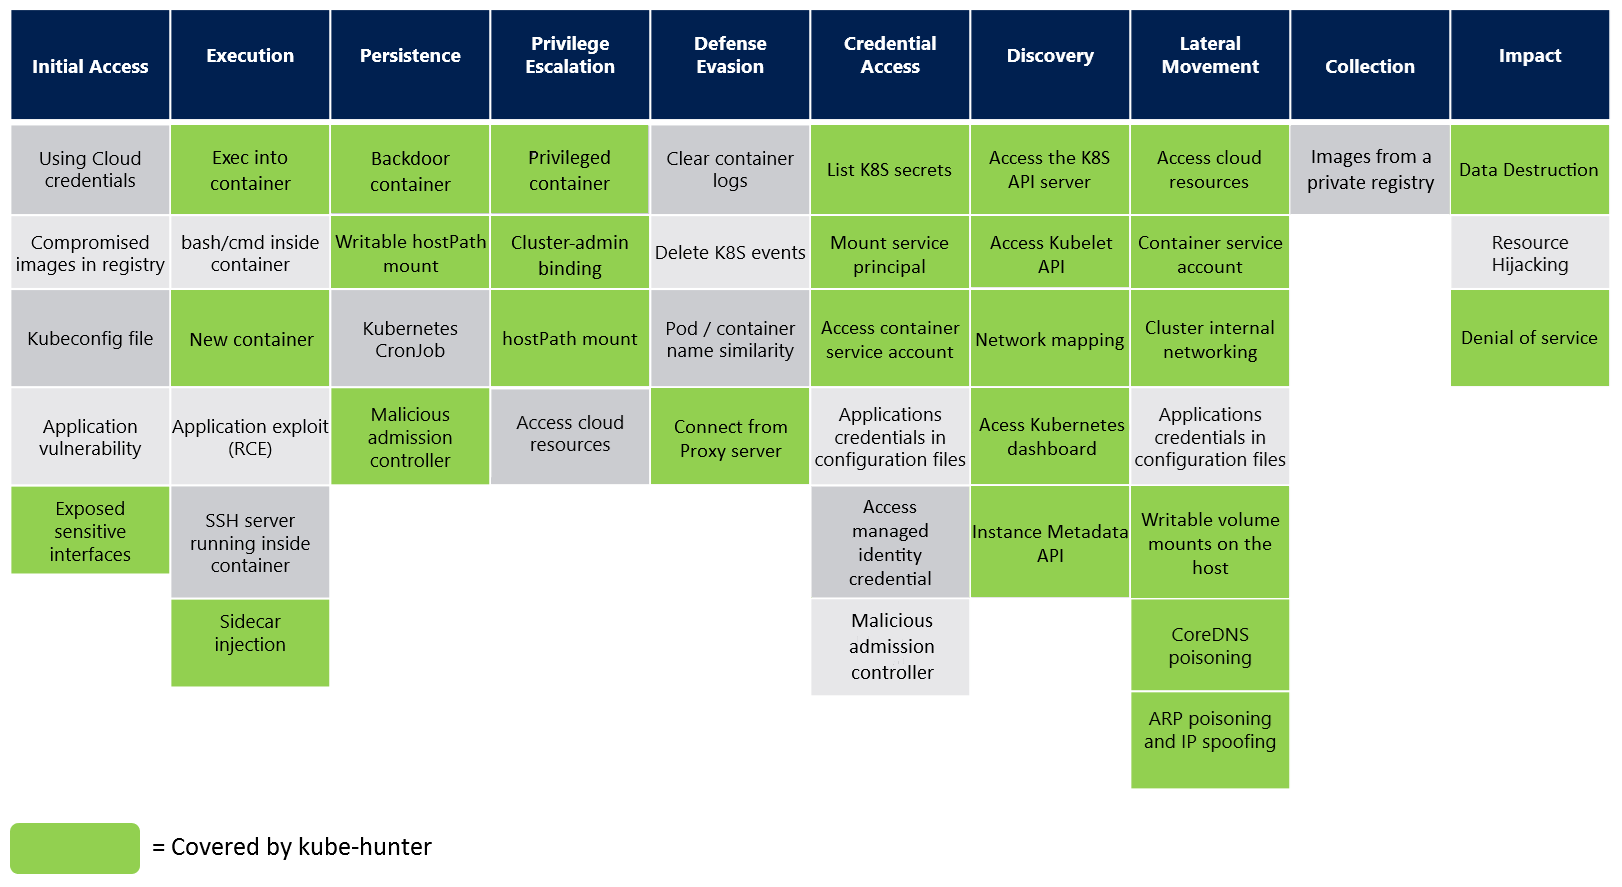 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 denuitt1/mhr-cfw
A Domain-Fronting Relay that routes traffic though GAS (Google Apps Script) and forwards it to Cloudflare Workers. Designed to bypass DPI.
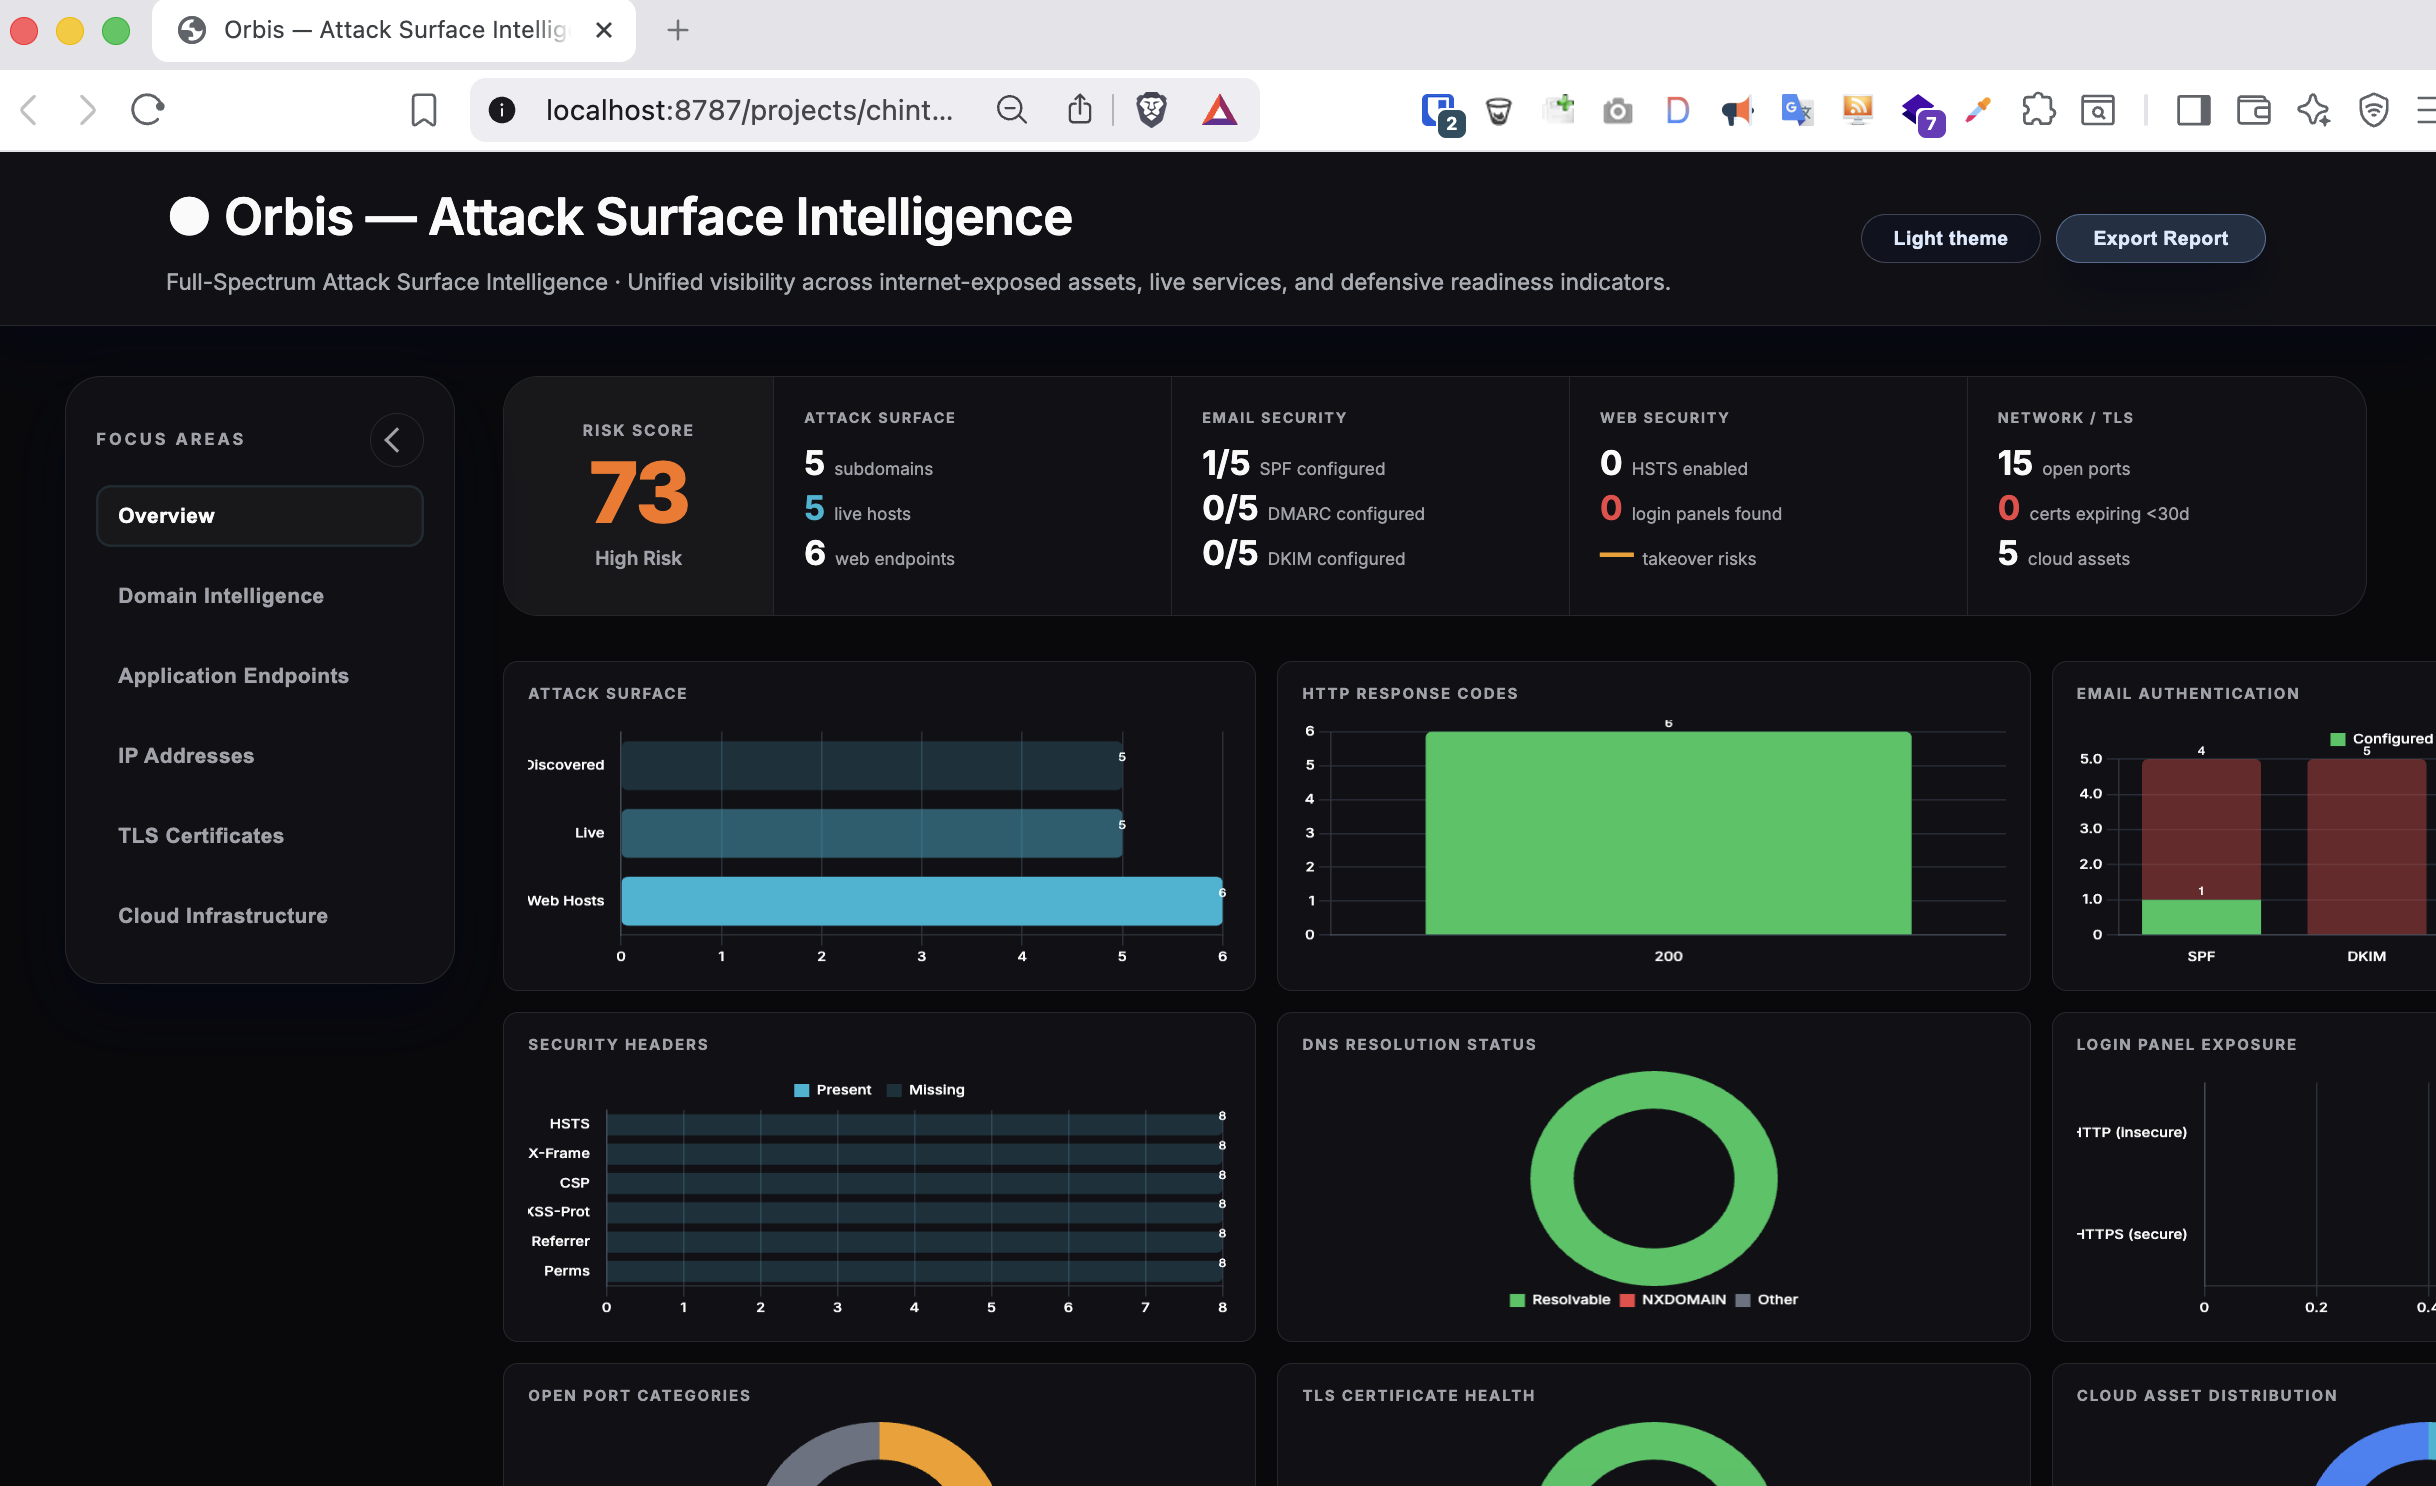 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
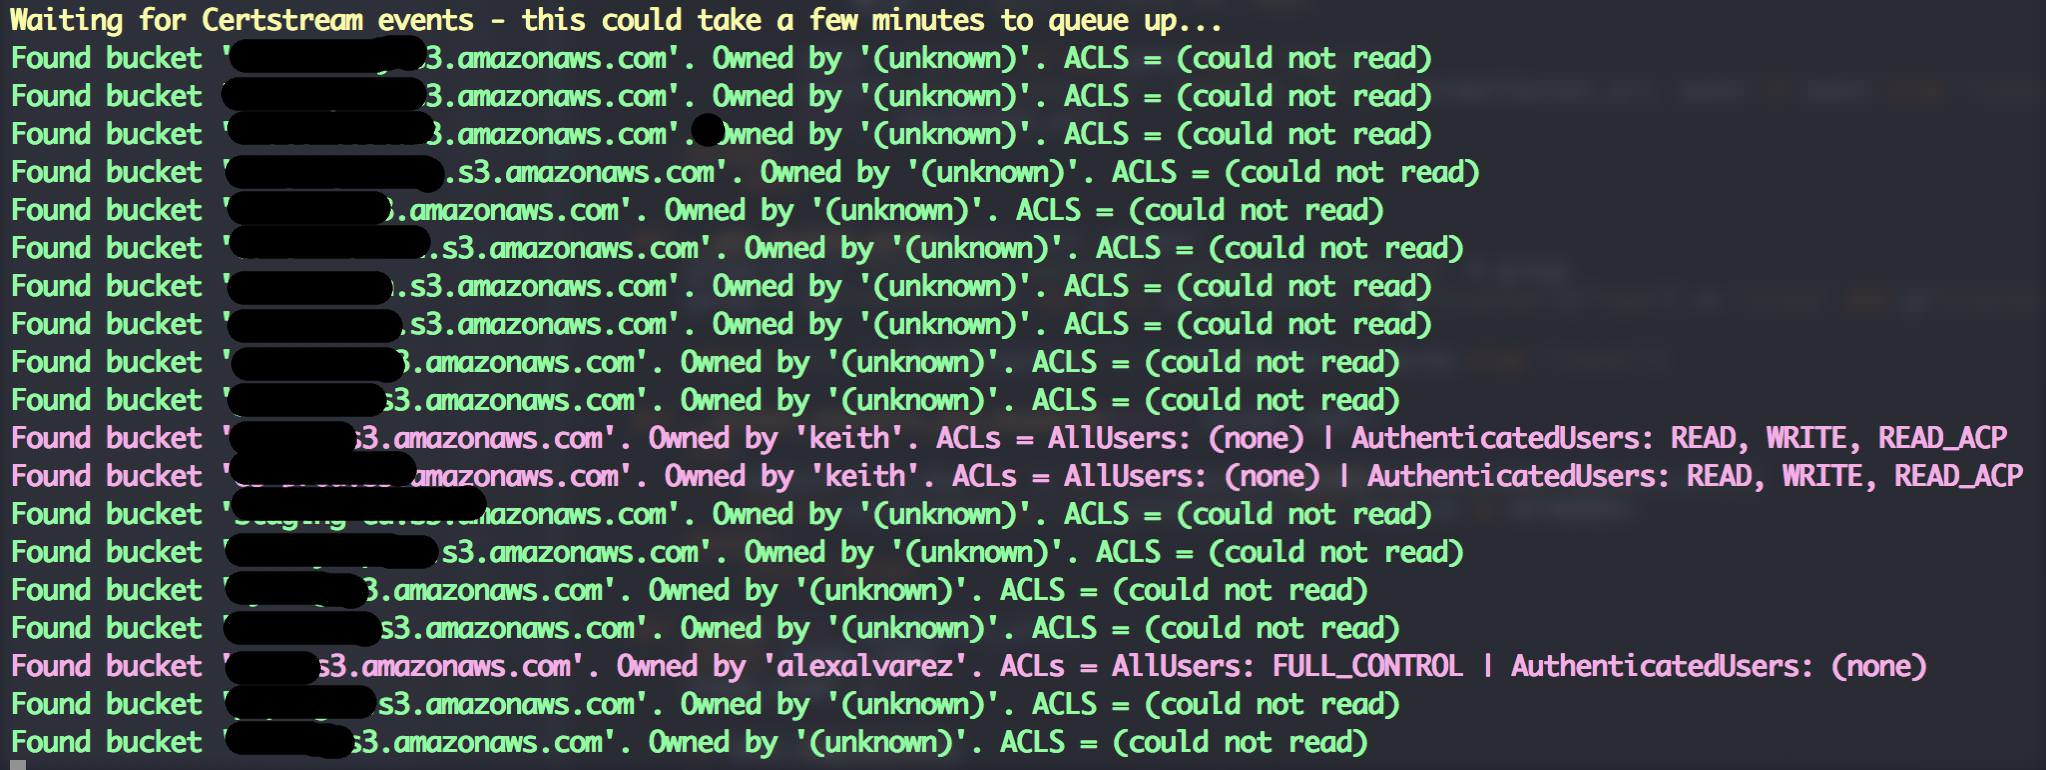 eth0izzle/bucket-stream
Find interesting Amazon S3 Buckets by watching certificate transparency logs.
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
 jordanpotti/awsbucketdump
Security Tool to Look For Interesting Files in S3 Buckets
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 yehgdotnet/s3scanner
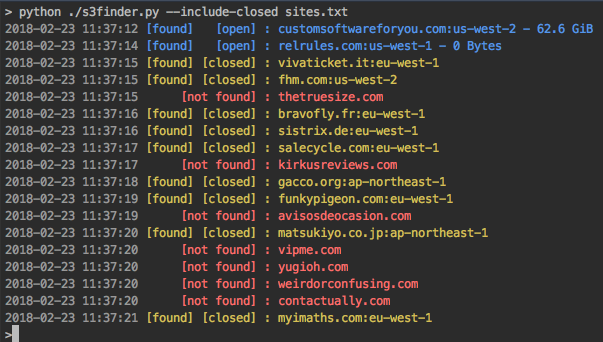
Scan for open S3 buckets and dump