

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.2k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
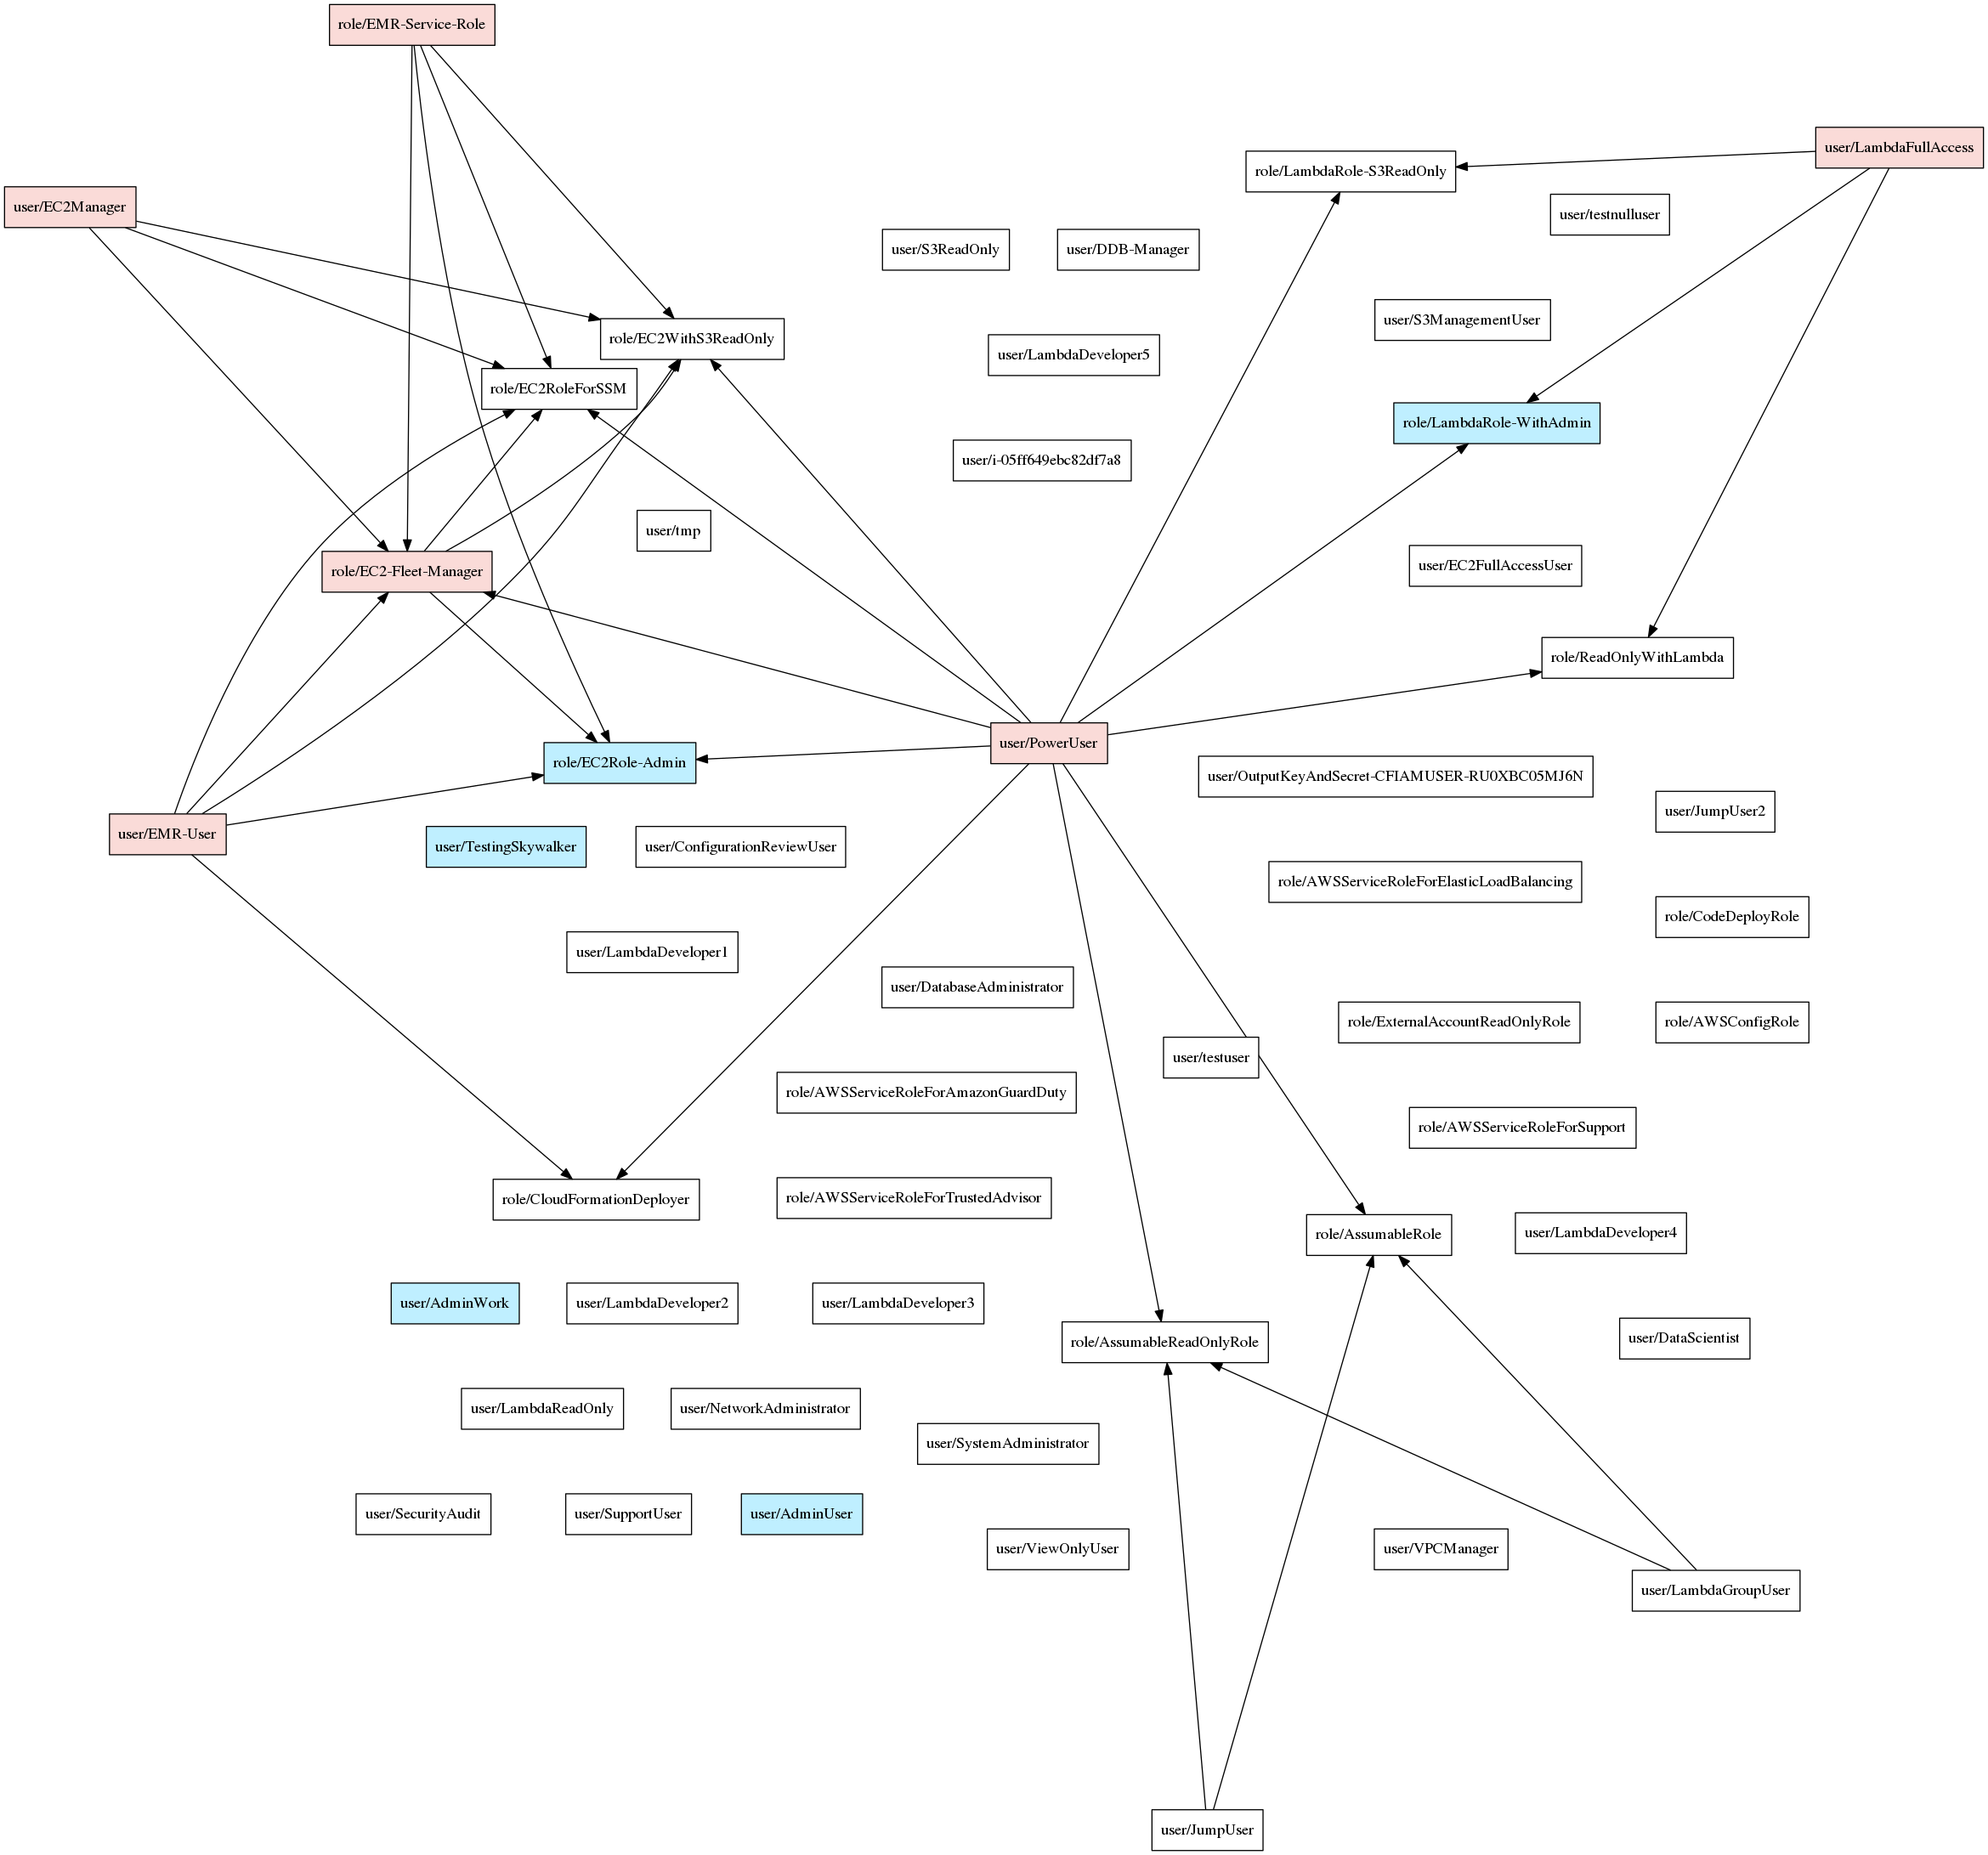 nccgroup/pmapper
A tool for quickly evaluating IAM permissions in AWS.
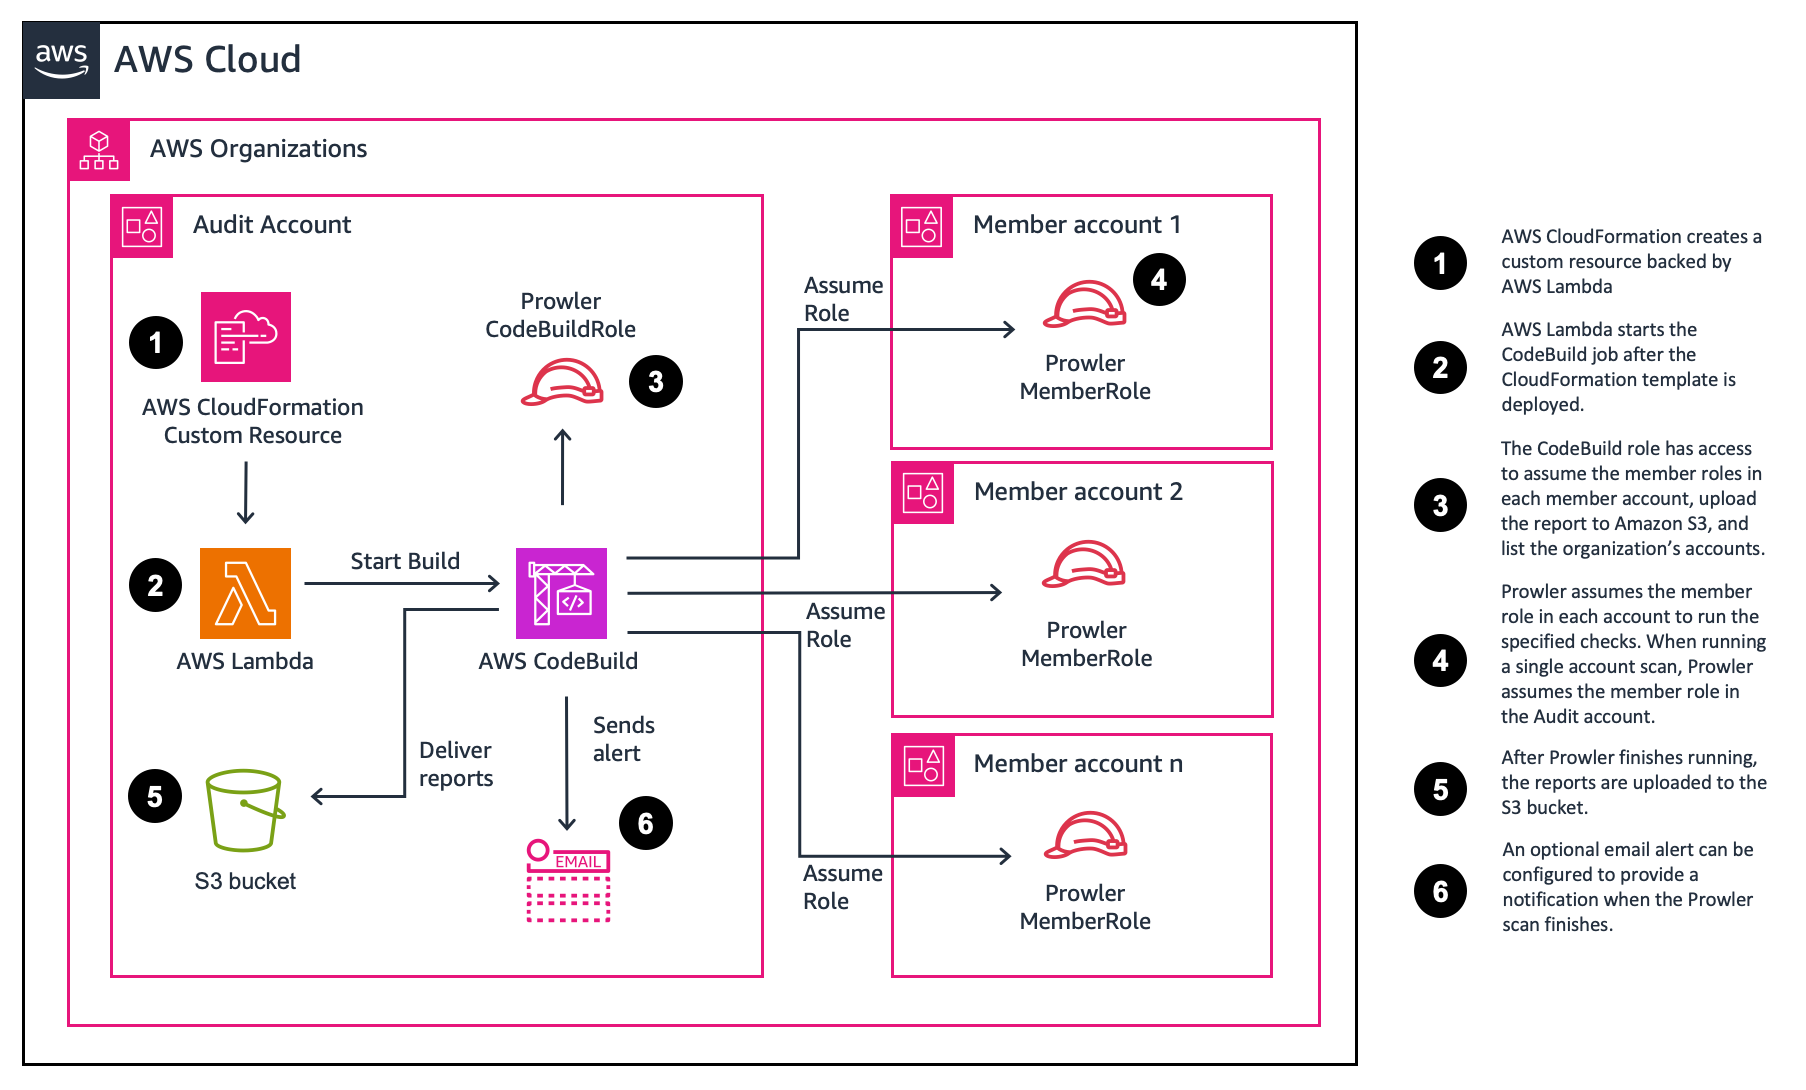 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
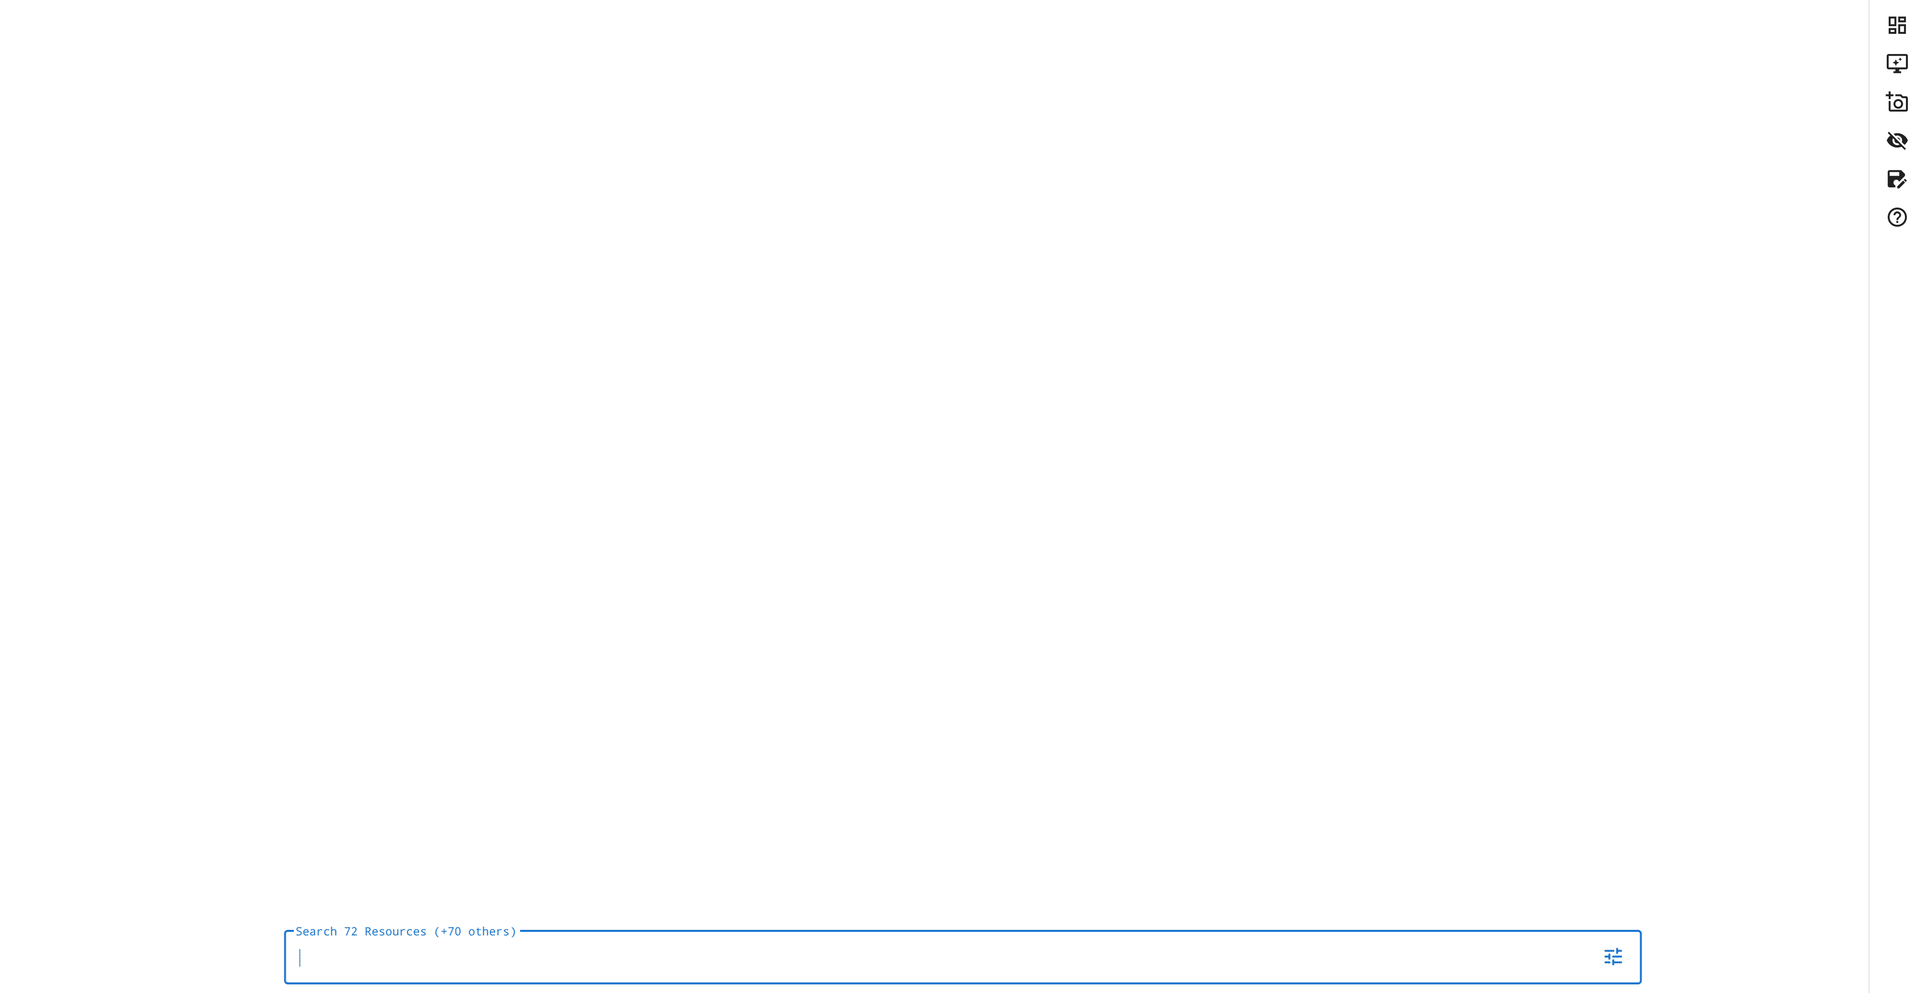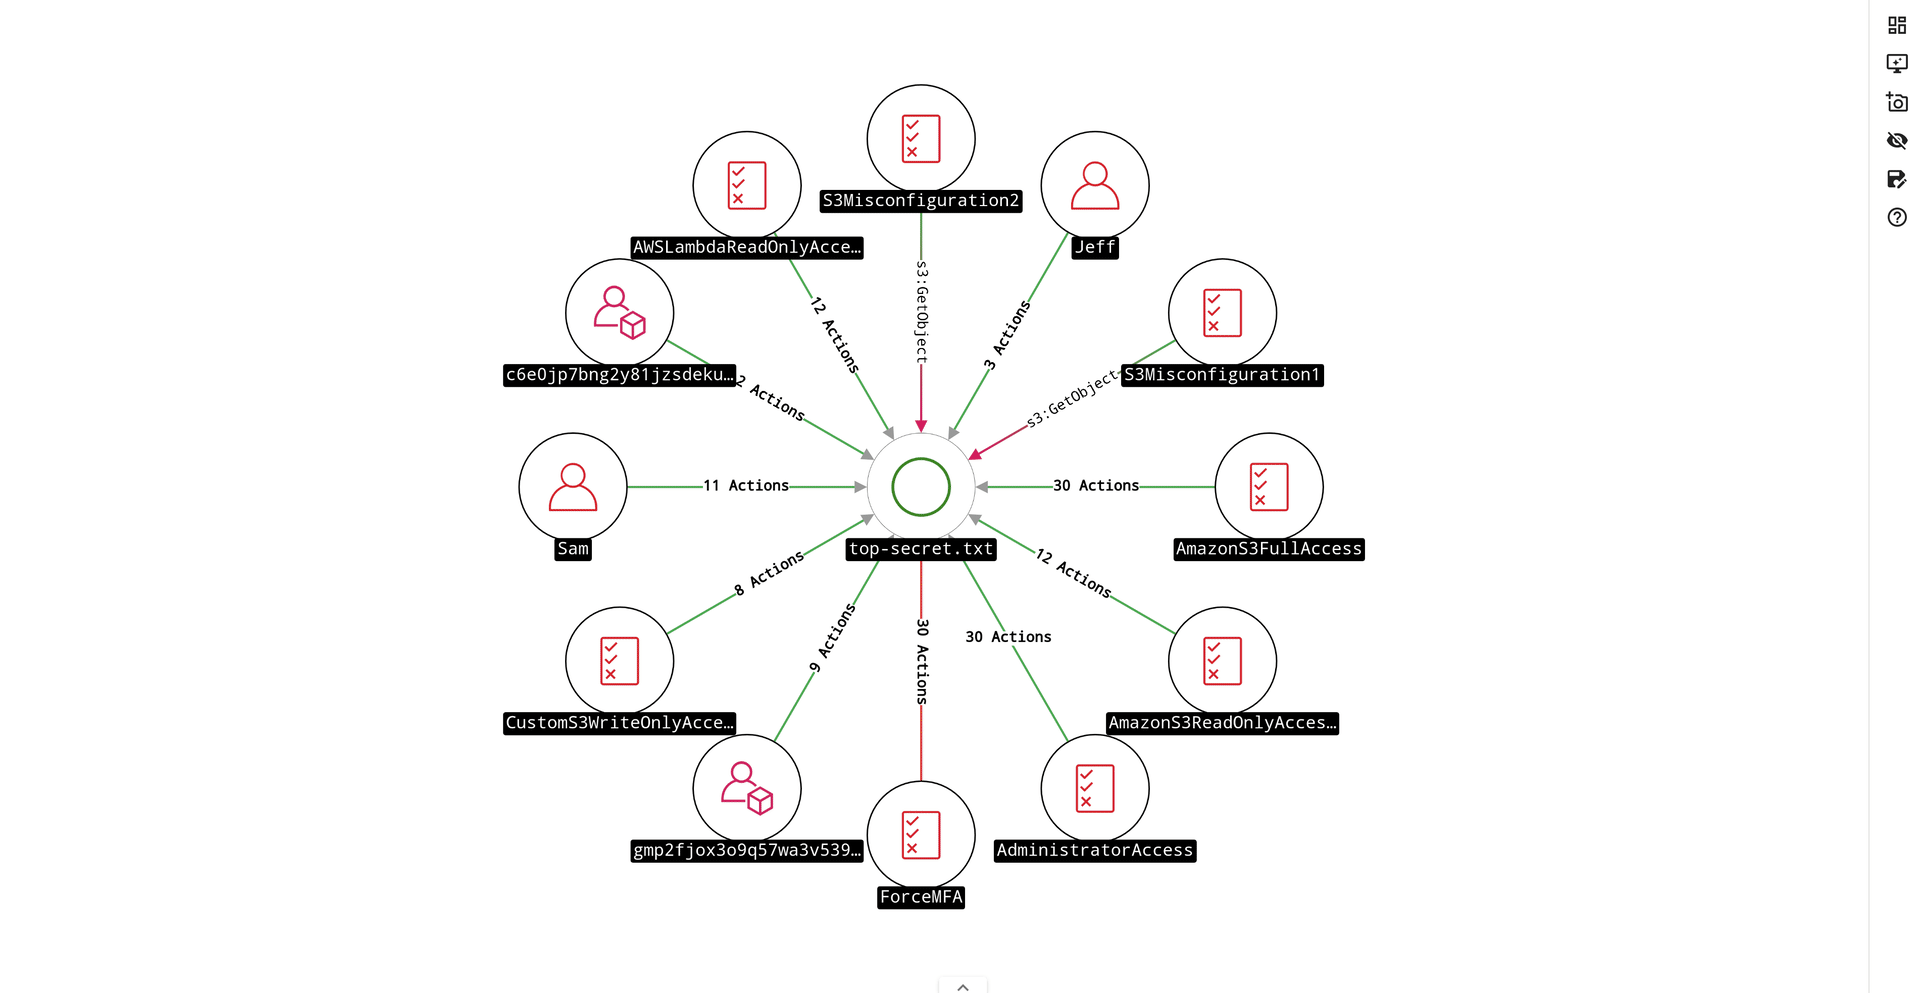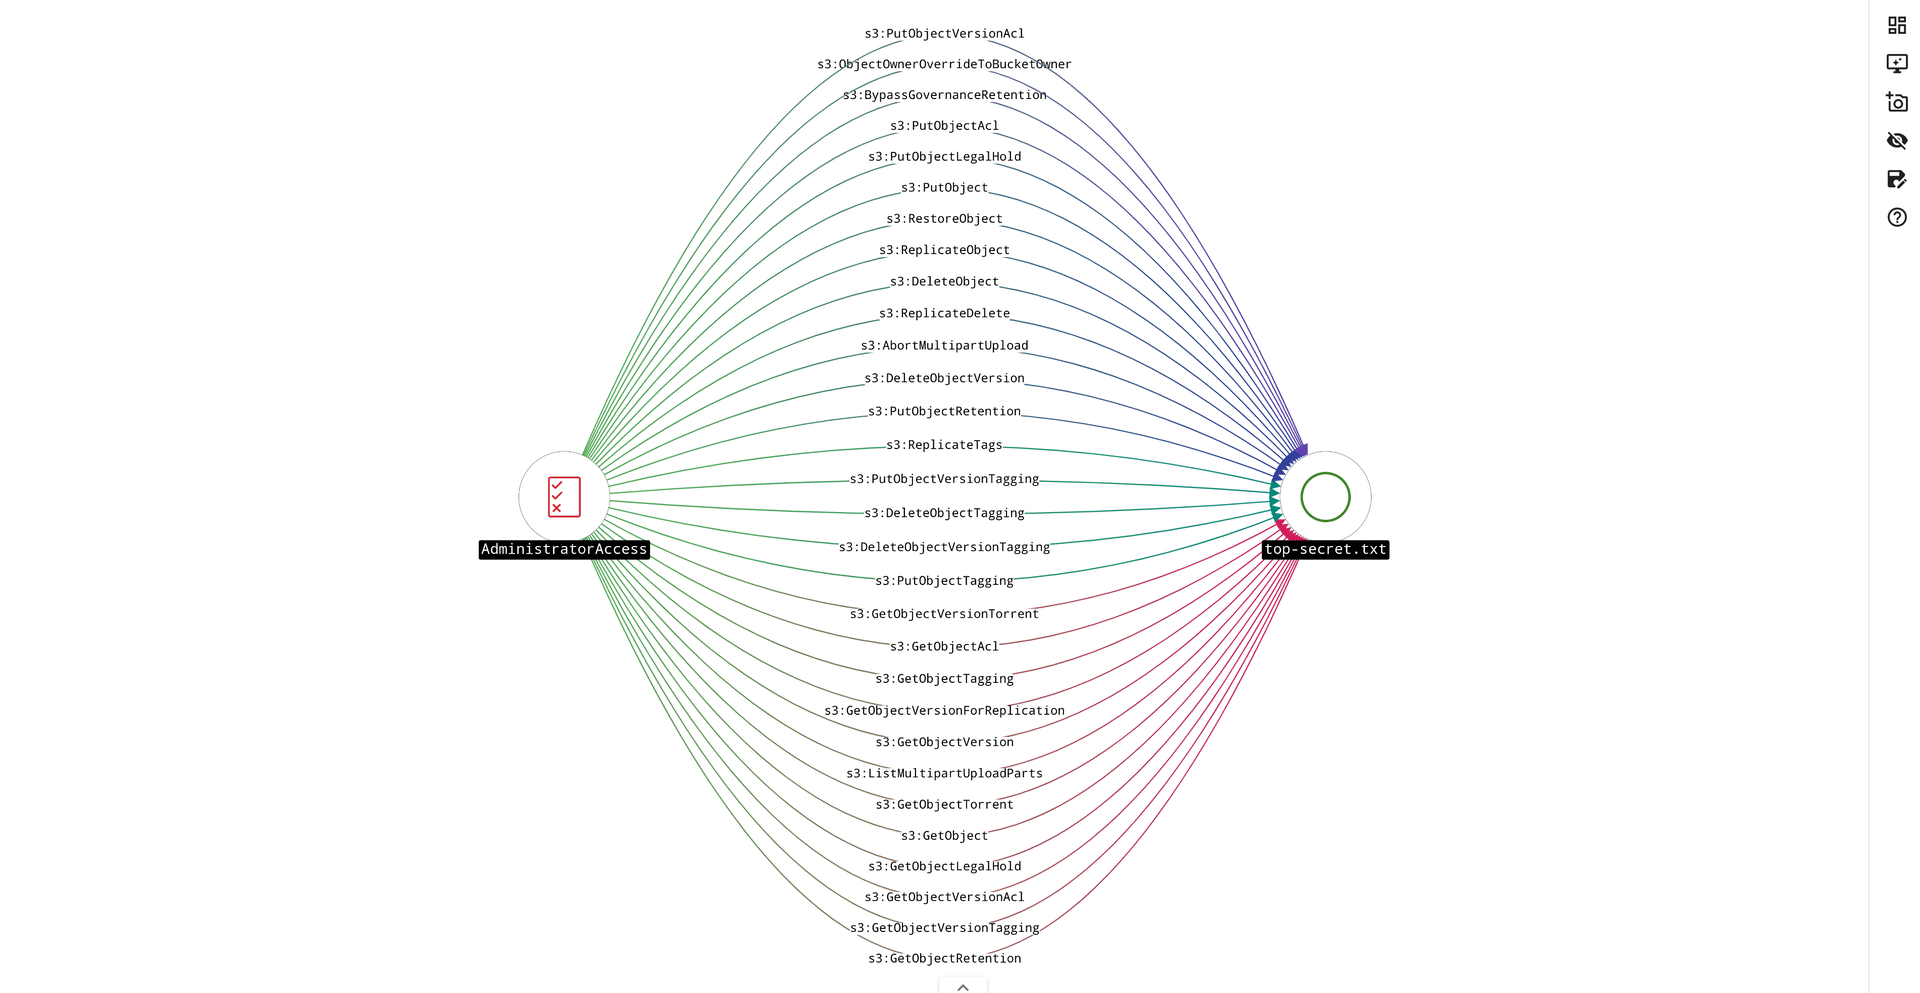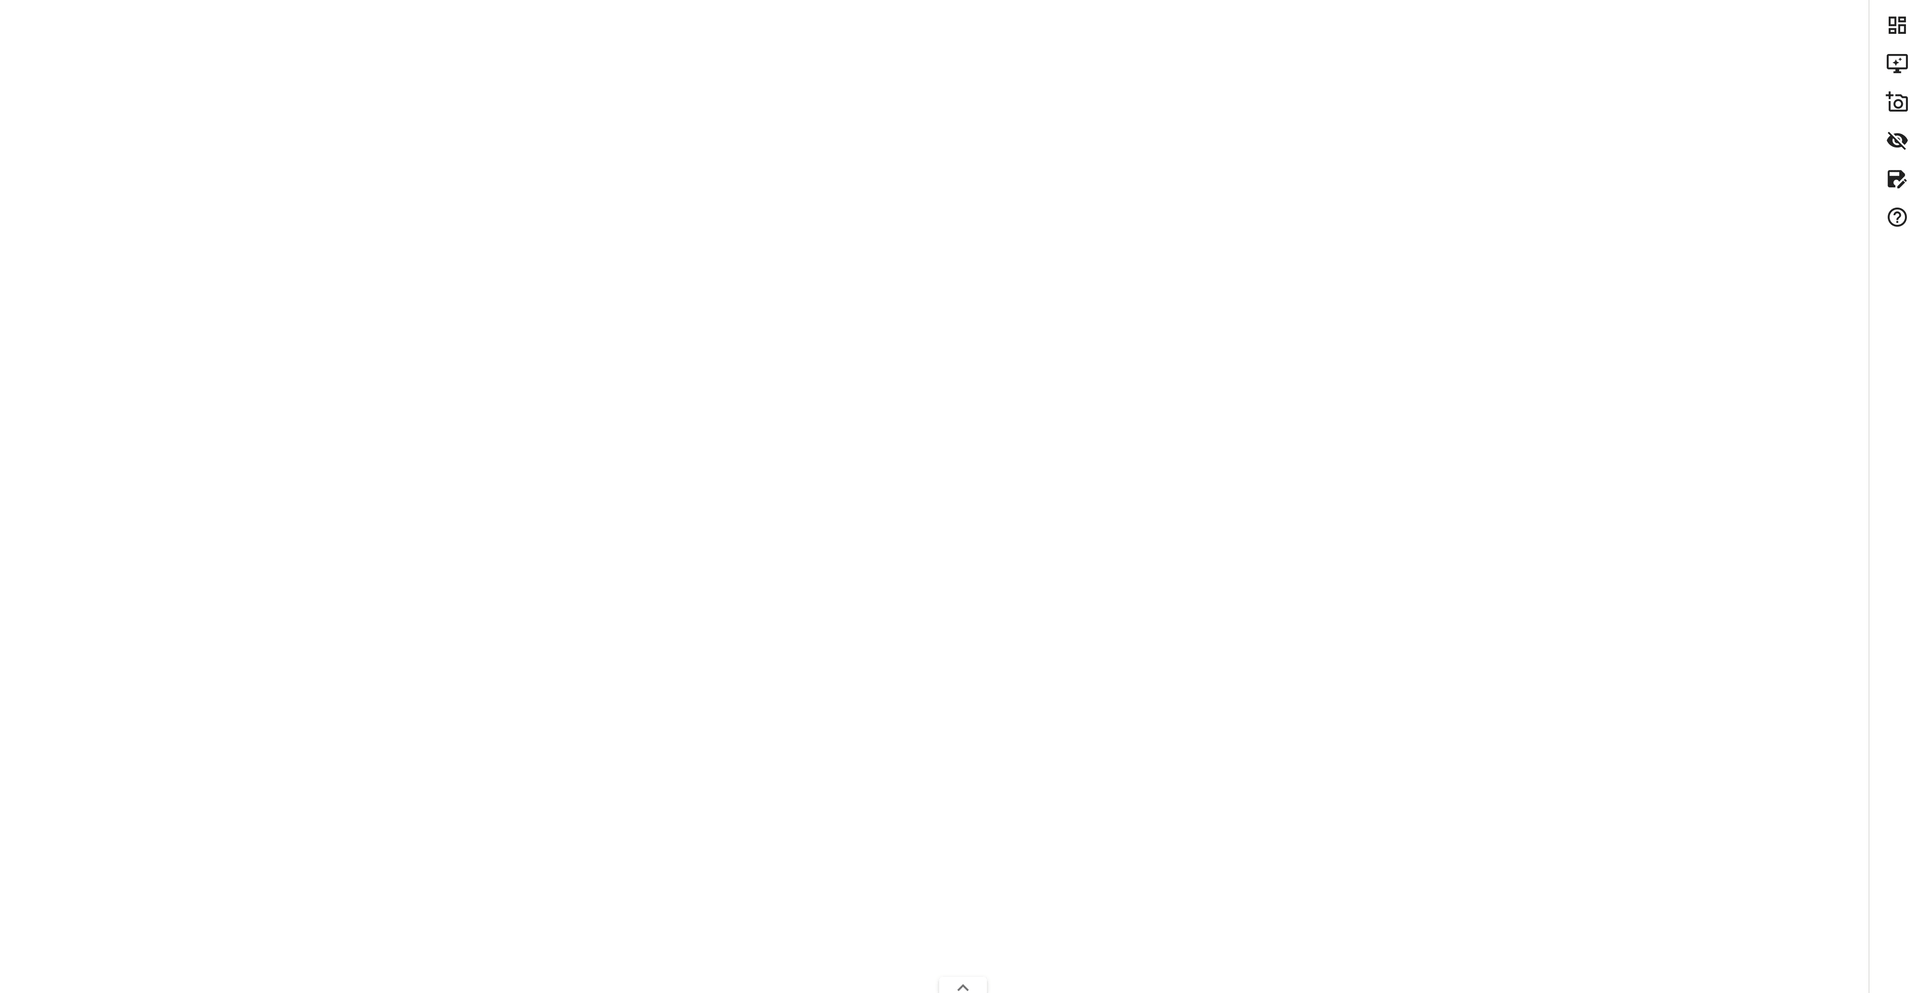 reverseclabs/awspx
A graph-based tool for visualizing effective access and resource relationships in AWS environments.
 nccgroup/aws-inventory
Discover resources created in an AWS account.
 cyberark/blobhunter
Find exposed data in Azure with this public blob scanner
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
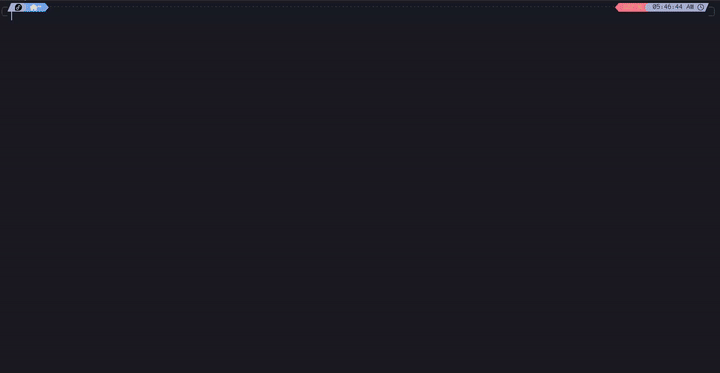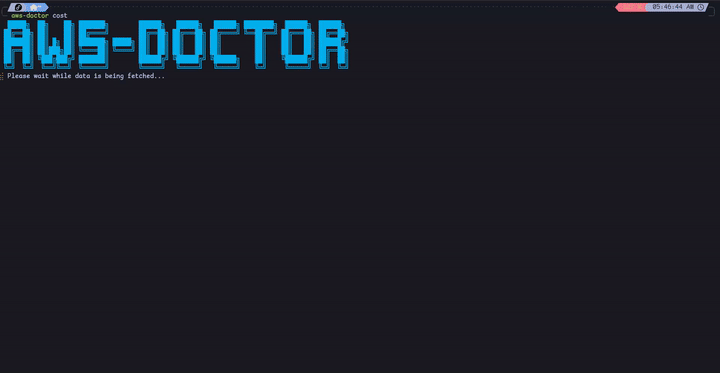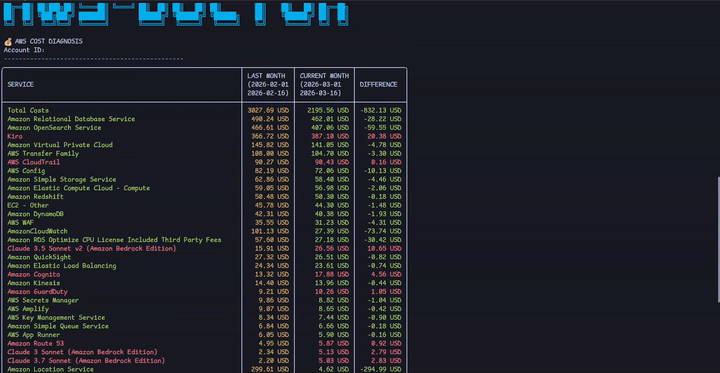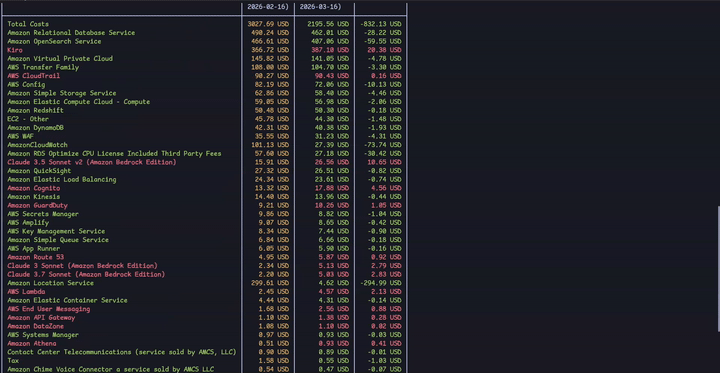 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 tenable/cnappgoat
CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS
 cred-club/dial
Event-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…
 tenable/escalategpt
An AI-powered tool for discovering privilege escalation opportunities in AWS IAM configurations.