
cs-suite
 securityftw/cs-suite
Cloud Security Suite - One stop tool for auditing the security posture of AWS/GCP/Azure infrastructure.
cloud-infrastructure-securitycloud-securityconfiguration-auditing+2
1.2k
securityftw/cs-suiteCloud Security Suite - One stop tool for auditing the security posture of AWS/GCP/Azure infrastructure.
 george0papasotiriou/cve-2026-21008-kubernetes-service-account-token-mounted-in-hostpath
Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS
 armourbird/csf
ArmourBird CSF - Container Security Framework
 kalilinux/build-scripts/kali-cloud
Scripts to build Kali cloud images (fork of https://salsa.debian.org/cloud-team/debian-cloud-images)
 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
 maniak-academy/mitigate-cve-2023-46747
Ansible playbook to automate mitigation of CVE-2023-46747 (BIG-IP unauthenticated RCE) by applying F5's official script across multiple devices.
 nserser/lr-webpki
Reference implementation of LR+ post-quantum authentication over WebPKI CA context, with corpus pipeline, reconstruction, evaluation, and provenance…
 gdraperi/remote-bitlocker-encryption-report
PowerShell script to mitigate CVE-2018-12038. The script takes a list of PC as input, gets their BitLocker encryption type remotely, and outputs a…
 jdmulloy/meltdown-aws-scanner
Naive shell script to verify Meltdown (CVE-2017-5754) patch status of EC2 instances
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 netflix/security_monkey
Security Monkey monitors AWS, GCP, OpenStack, and GitHub orgs for assets and their changes over time.
 netflix/repokid
AWS Least Privilege for Distributed, High-Velocity Deployment
 owasp/dvsa
a Damn Vulnerable Serverless Application
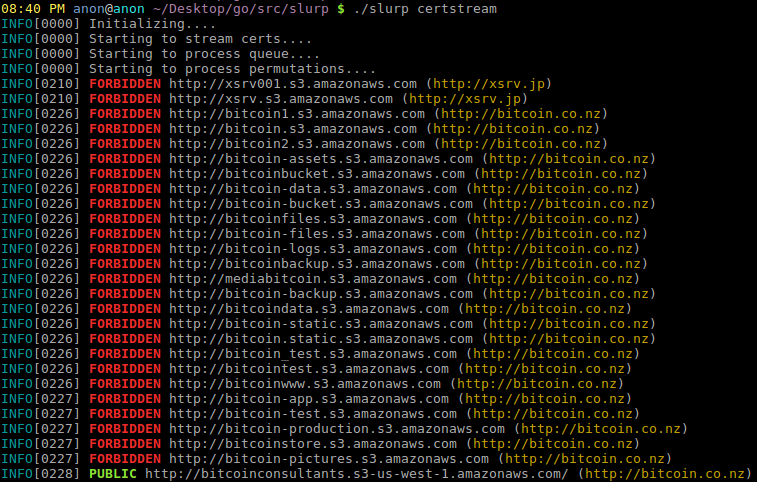 0xbharath/slurp-old
A tool to enumerate S3 buckets manually or via certstream