
holos
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
cloud-infrastructure-securitydevsecopsgeneral-purpose-utilities+3
144
zeroecco/holosDeclarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 guilherme-grimm/graph-go
simply nodes and graphs
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 denizparlak/hayat
Hayat is a script for report and analyze Google Cloud Platform resources.
 inceptionstack/lowkey
Deploy self-hosted AI coding agents (OpenClaw, Claude Code, Codex) into your AWS account with CloudFormation, IAM profiles, and sandbox isolation for…
 owasp/kubelight
OWASP Kubernetes security and compliance tool [WIP]
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 dev-sec/puppet-ssh-hardening
This puppet module provides secure ssh-client and ssh-server configurations.
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
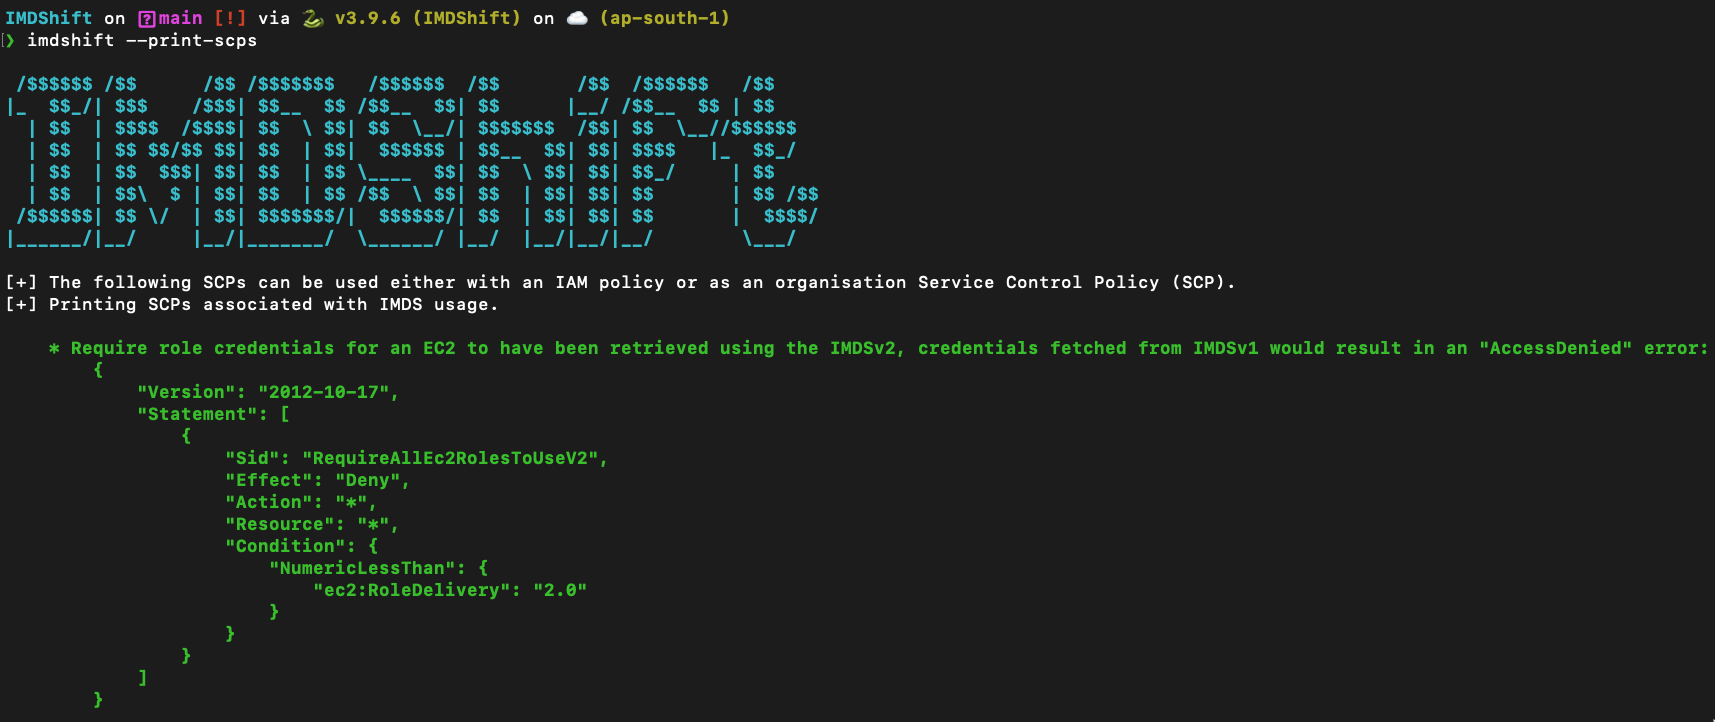 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
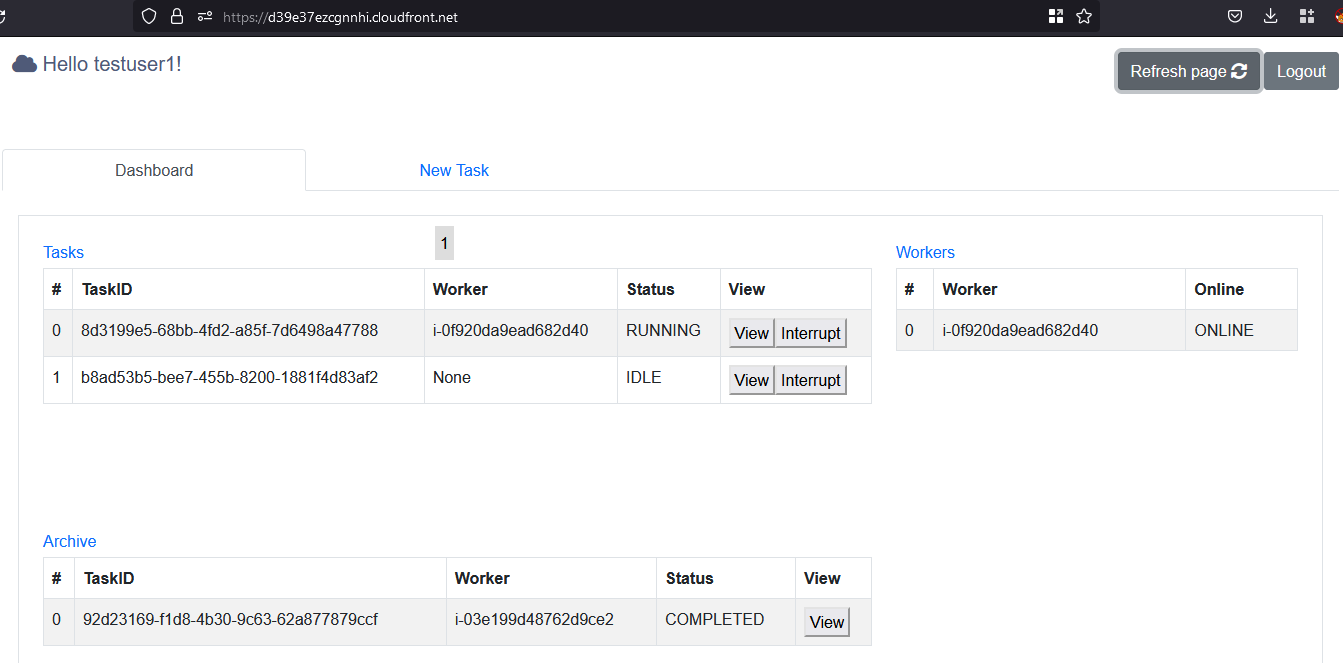 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 aquasecurity/trivy-plugin-aqua
Plugin for integrating Trivy with Aqua Security platform to scan IaC, pipelines, and dependencies for vulnerabilities and misconfigurations.
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 ustayready/outpost
AWS Testing and Reporting Management Tool
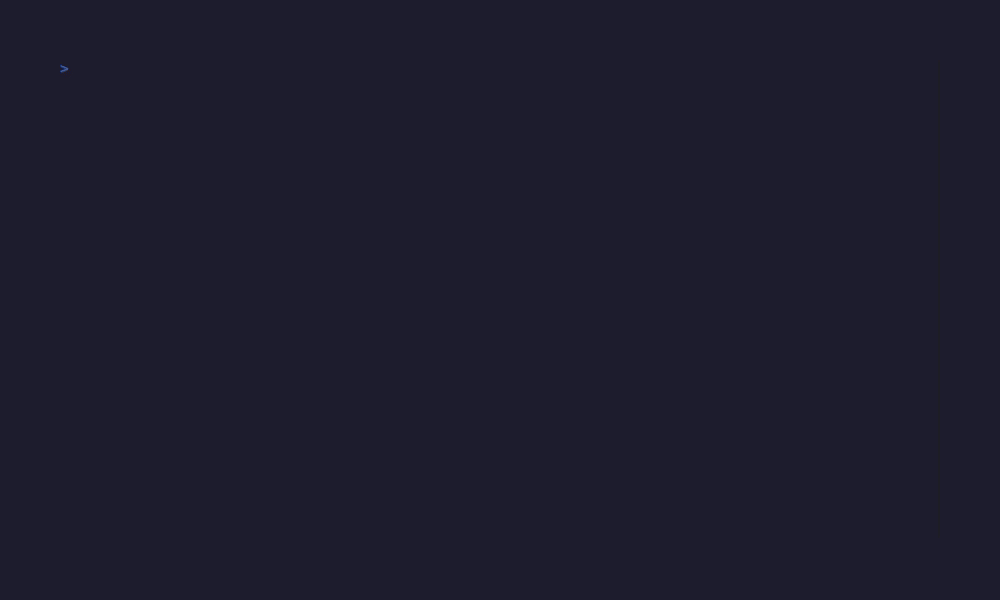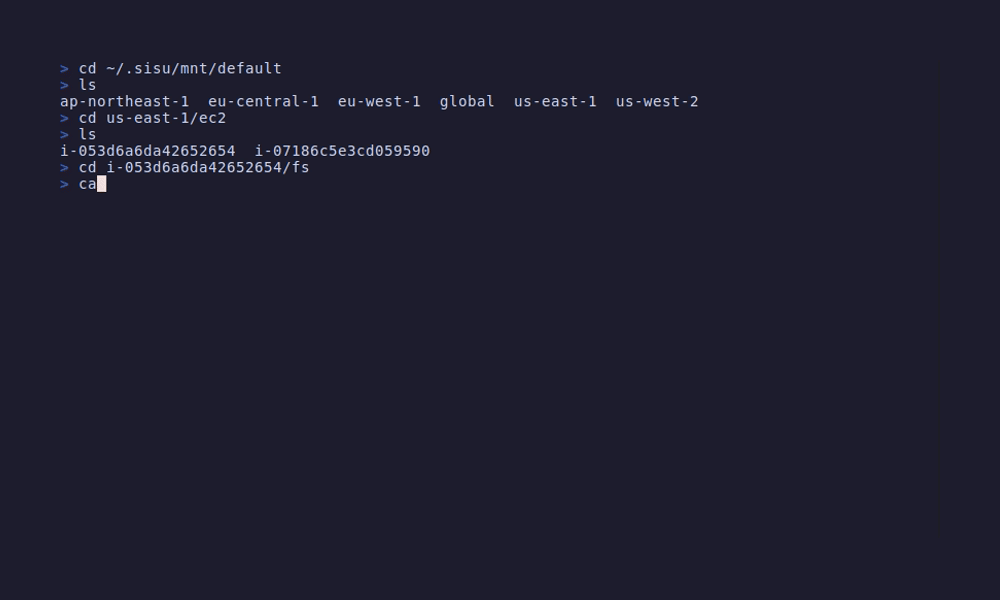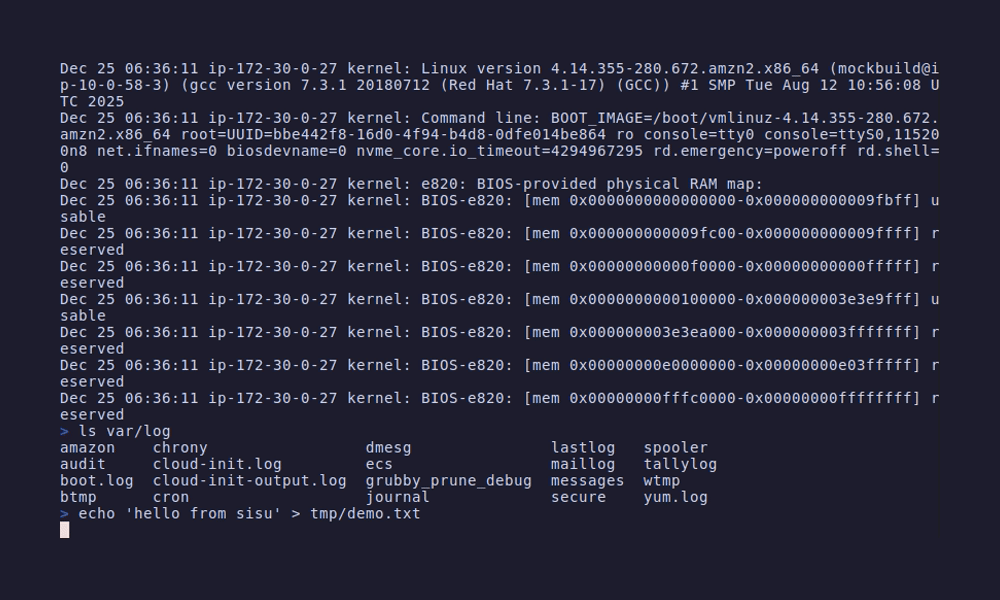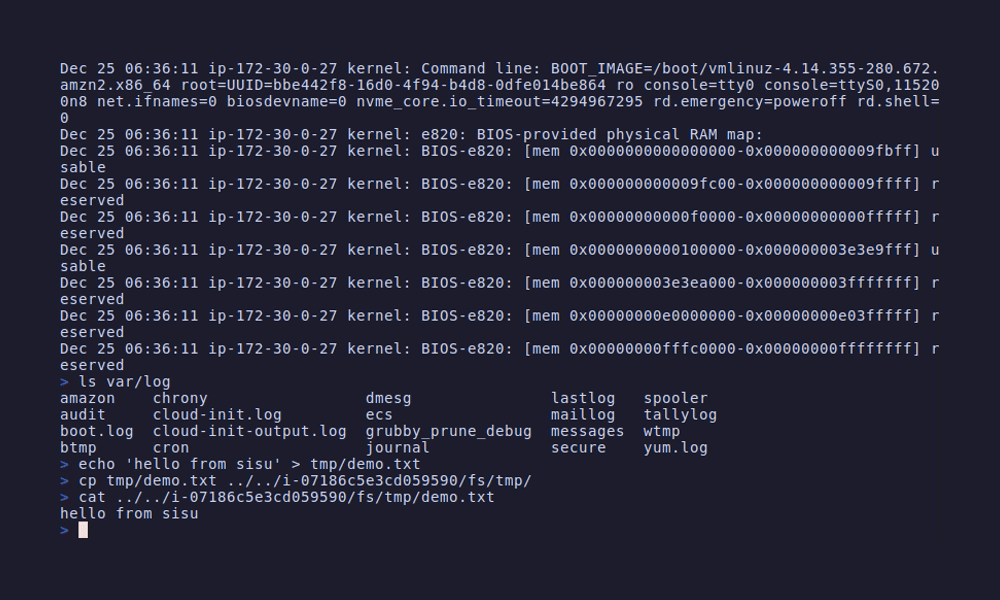 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…