
CureIAM
 gojek/cureiam
Clean accounts over permissions in GCP infra at scale
cloud-infrastructure-securitycloud-securityconfiguration-auditing+2
gojek/cureiamClean accounts over permissions in GCP infra at scale
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 hodgeluke/ai-agent-security-research
Open security research on AI coding agent infrastructure. Agent-executable remediation manifests for CVE-2026-22812 and CVE-2026-22813.
 chaosblade-io/chaosblade
An easy to use and powerful chaos engineering experiment toolkit.(阿里巴巴开源的一款简单易用、功能强大的混沌实验注入工具)
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 crowdstrike/crt
Audits Azure AD and Exchange Online configurations for hard-to-find permissions, federation trusts, mail forwarding rules, and delegated access to…
 aaaguirrep/offensive-docker-vps
Create a VPS on Google Cloud Platform or Digital Ocean easily with Offensive Docker included to launch assessment to the targets.
 salesforce/metabadger
Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).
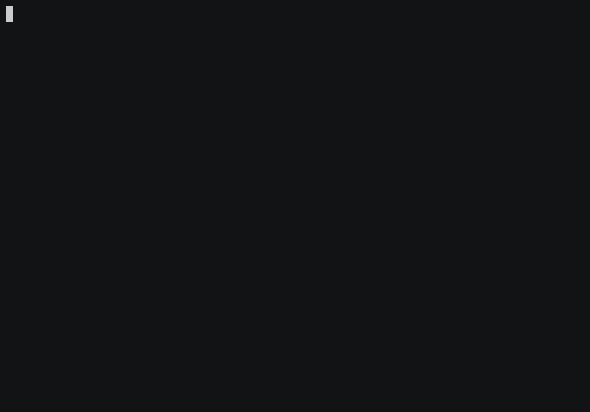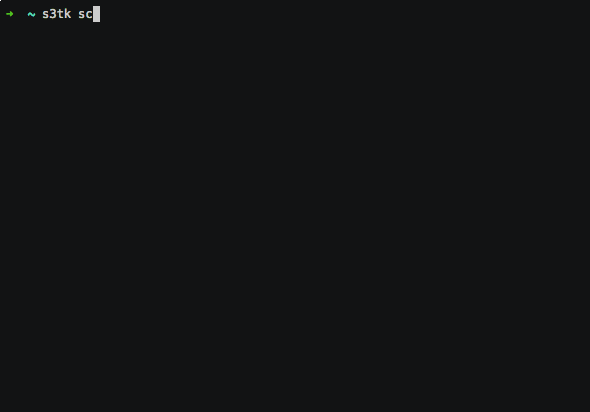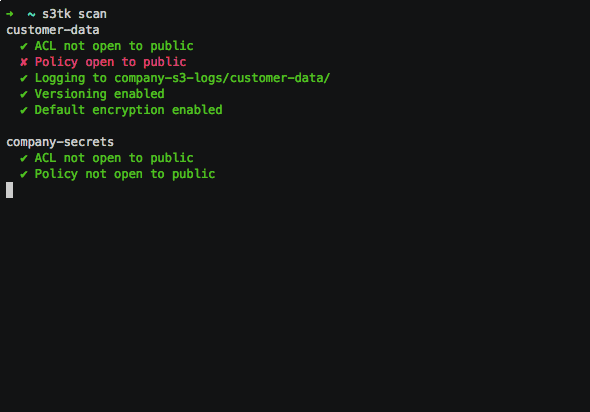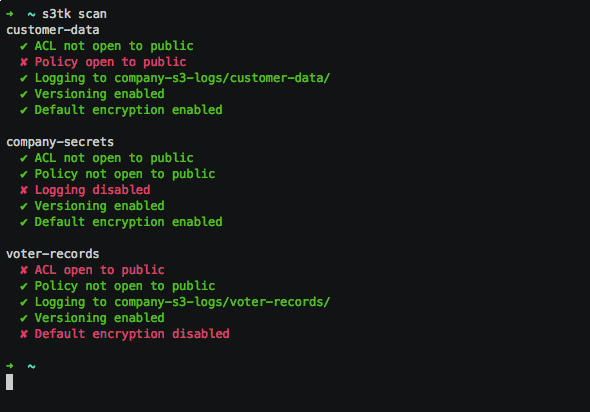 ankane/s3tk
A security toolkit for Amazon S3
 owasp/docker-security
Getting a handle on container security
 9rnt/poro
Scan publicly accessible assets on your AWS cloud environment
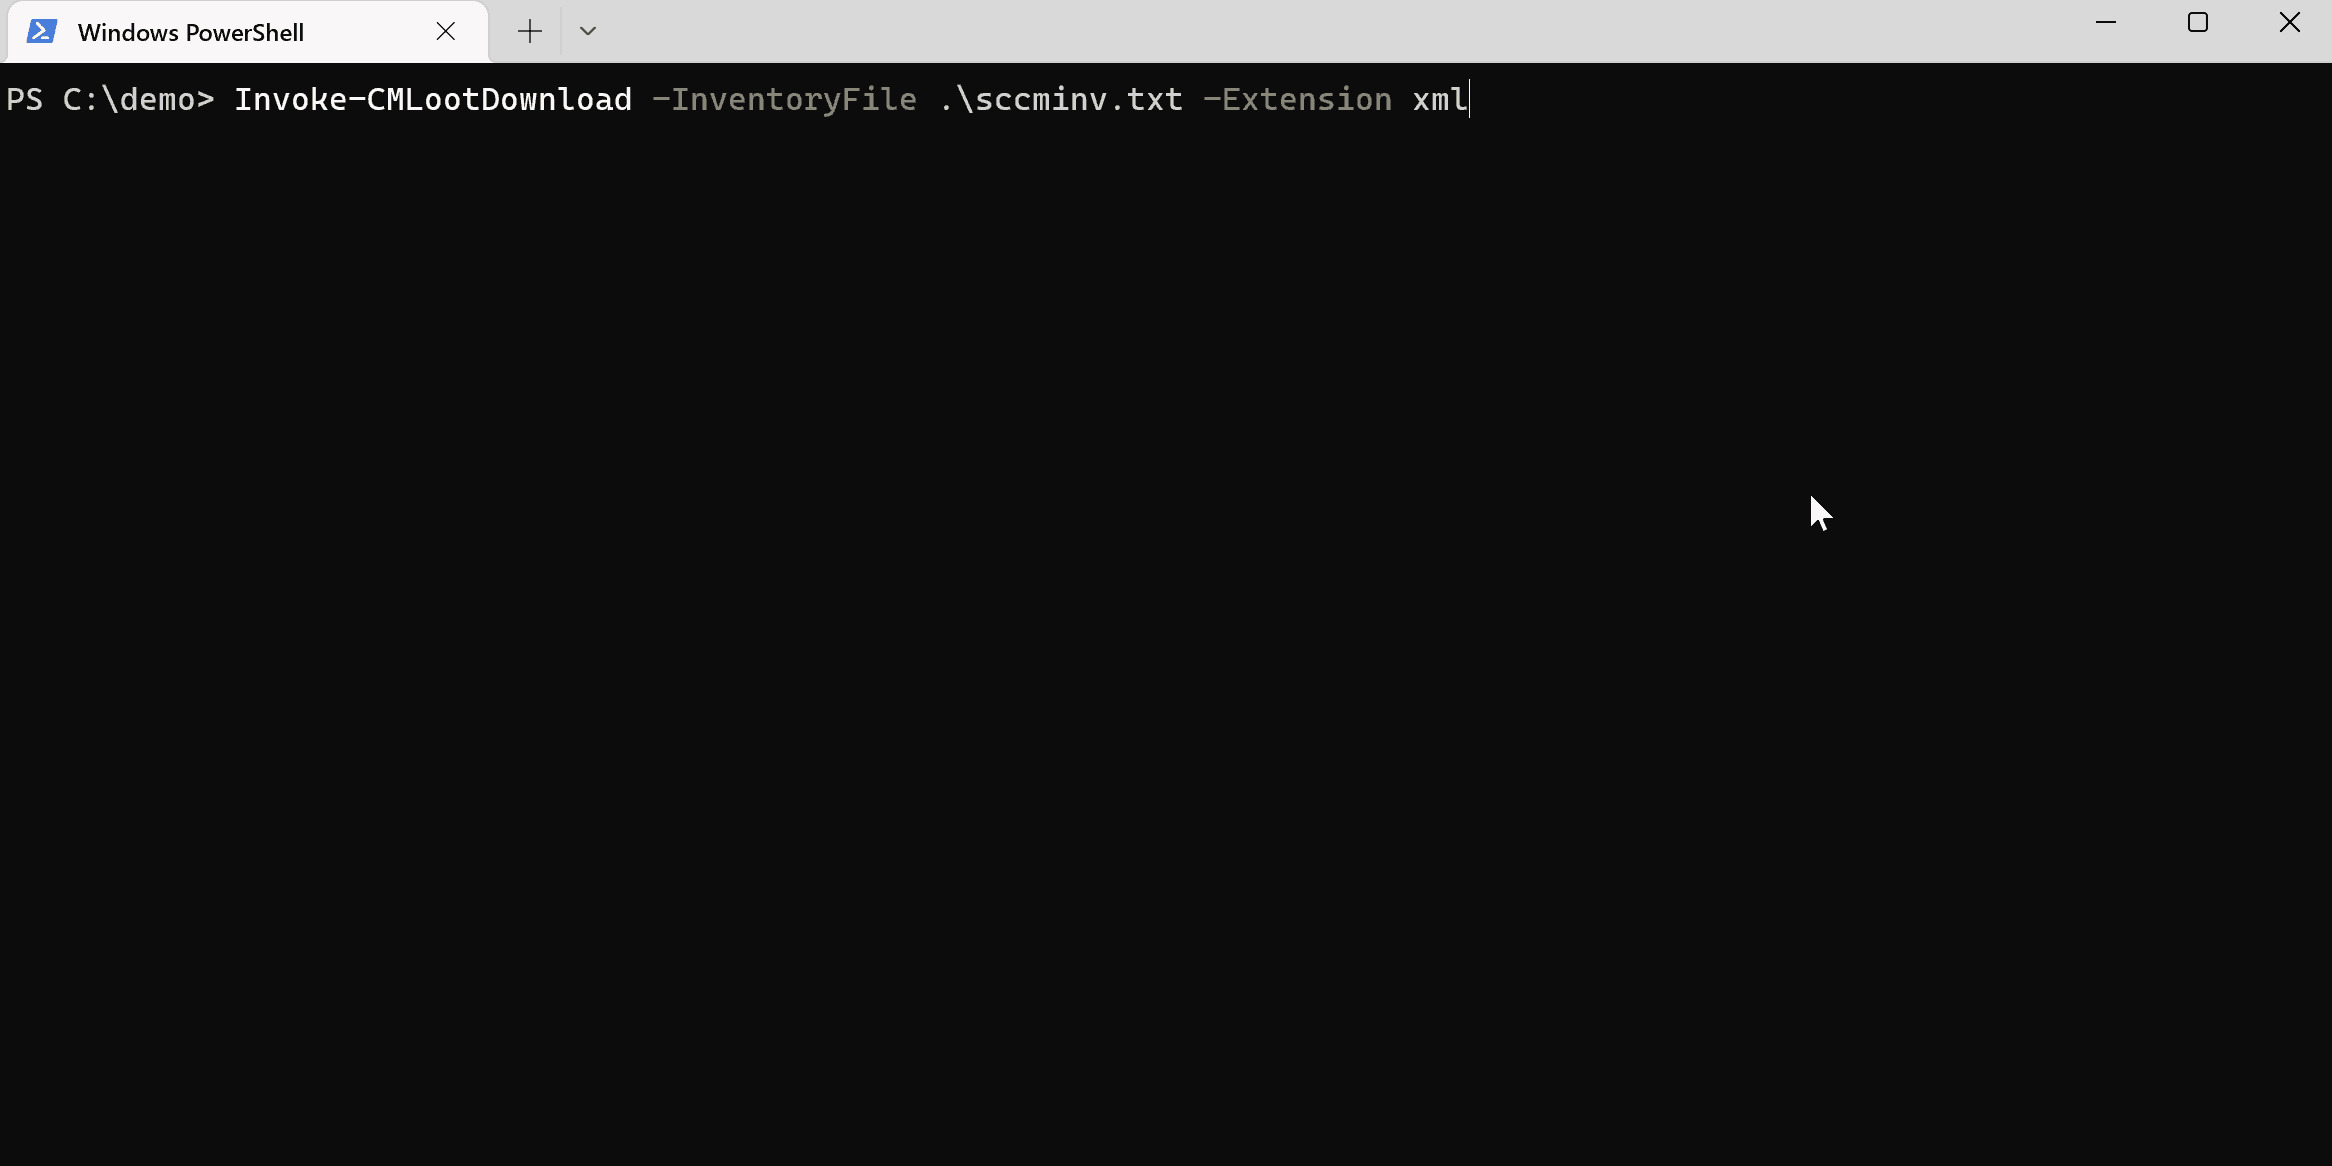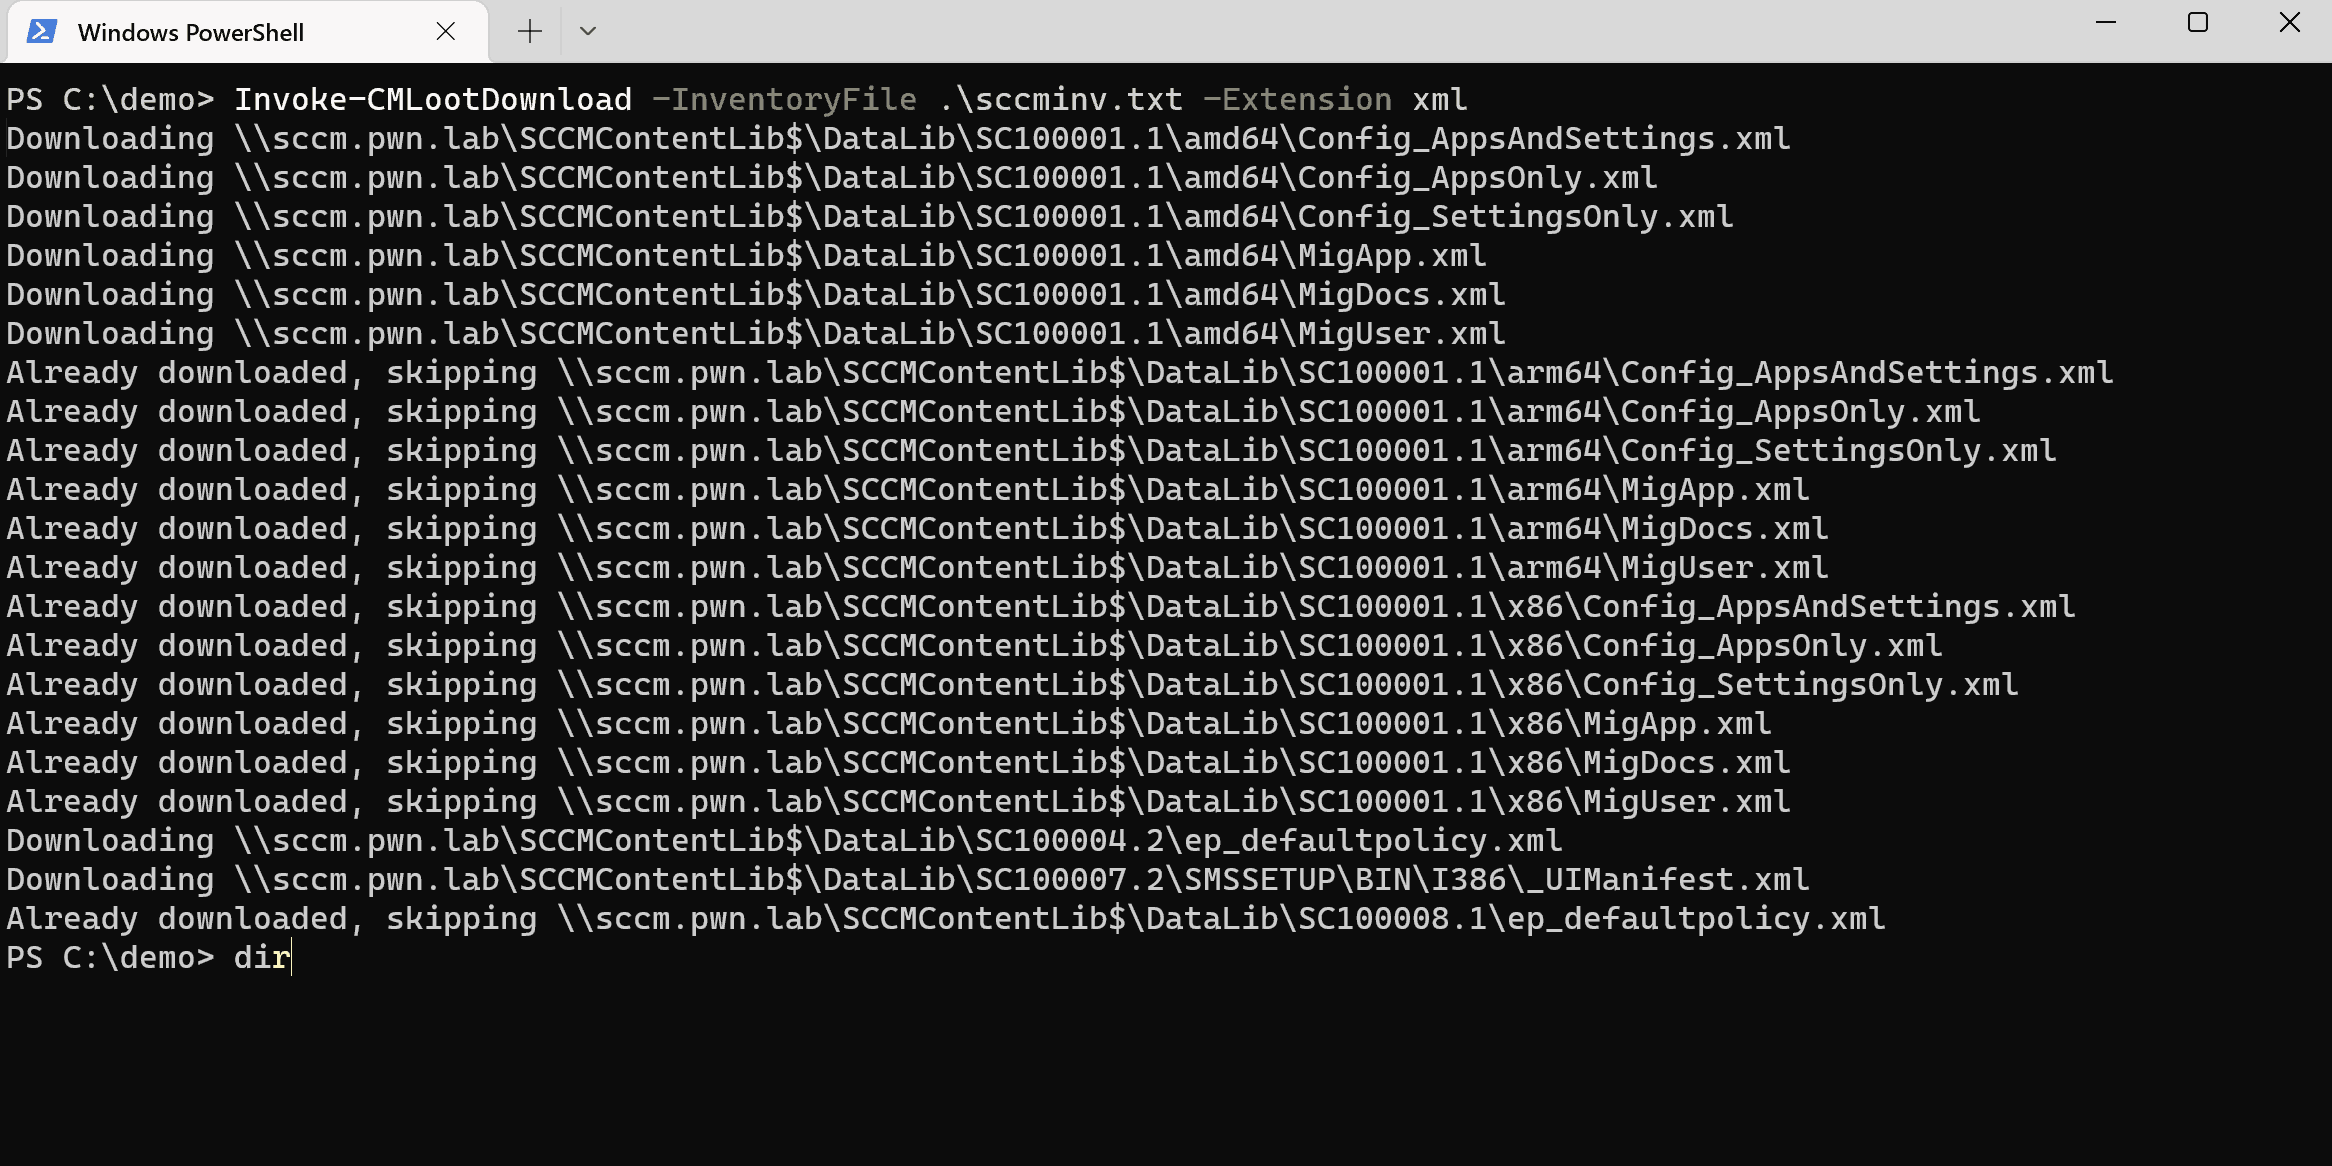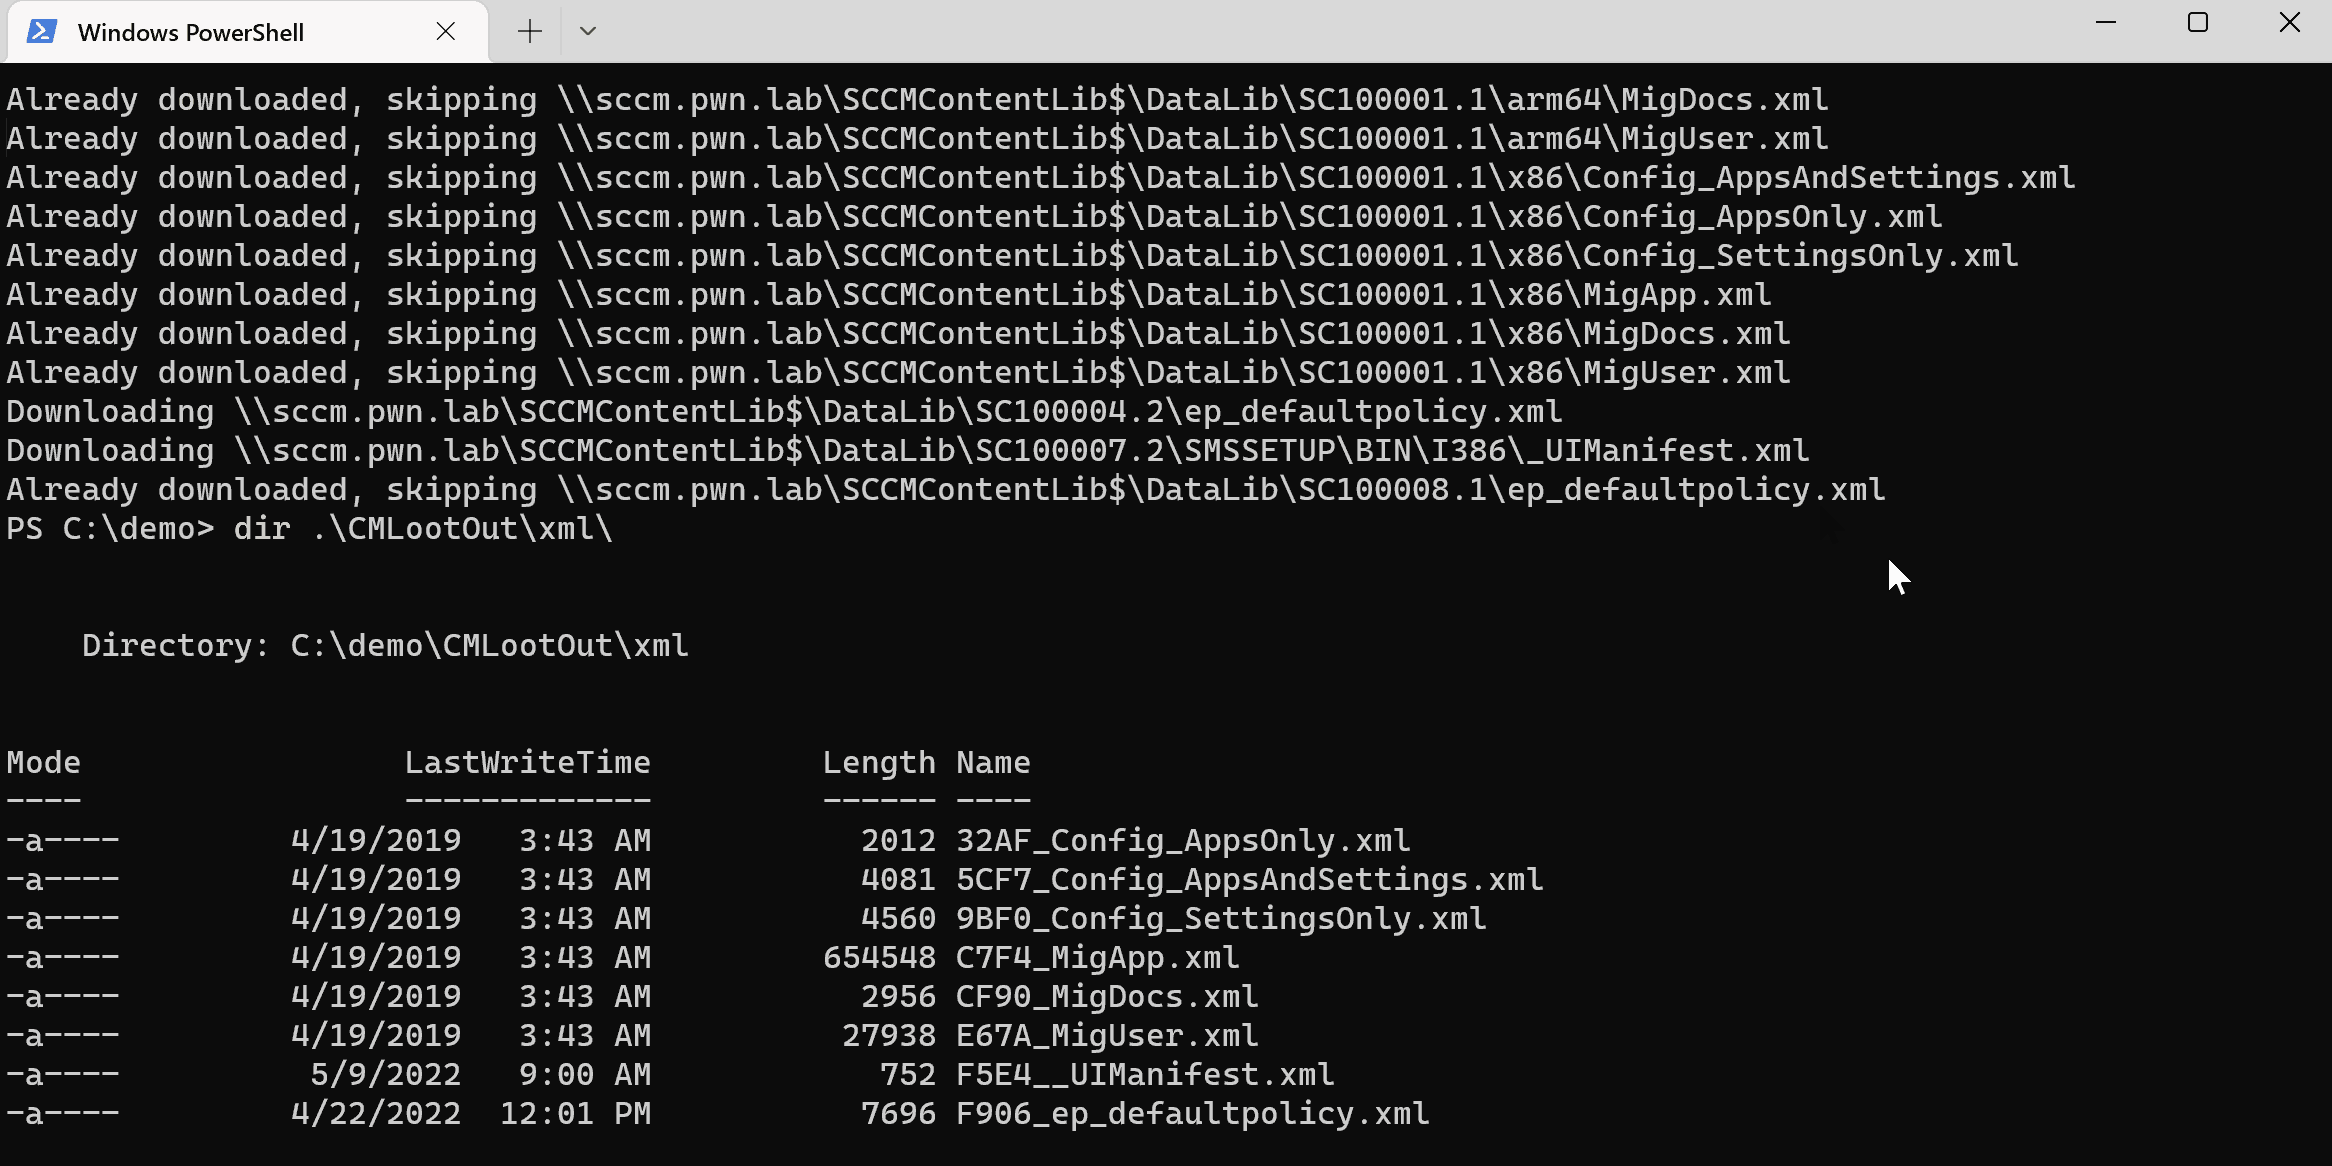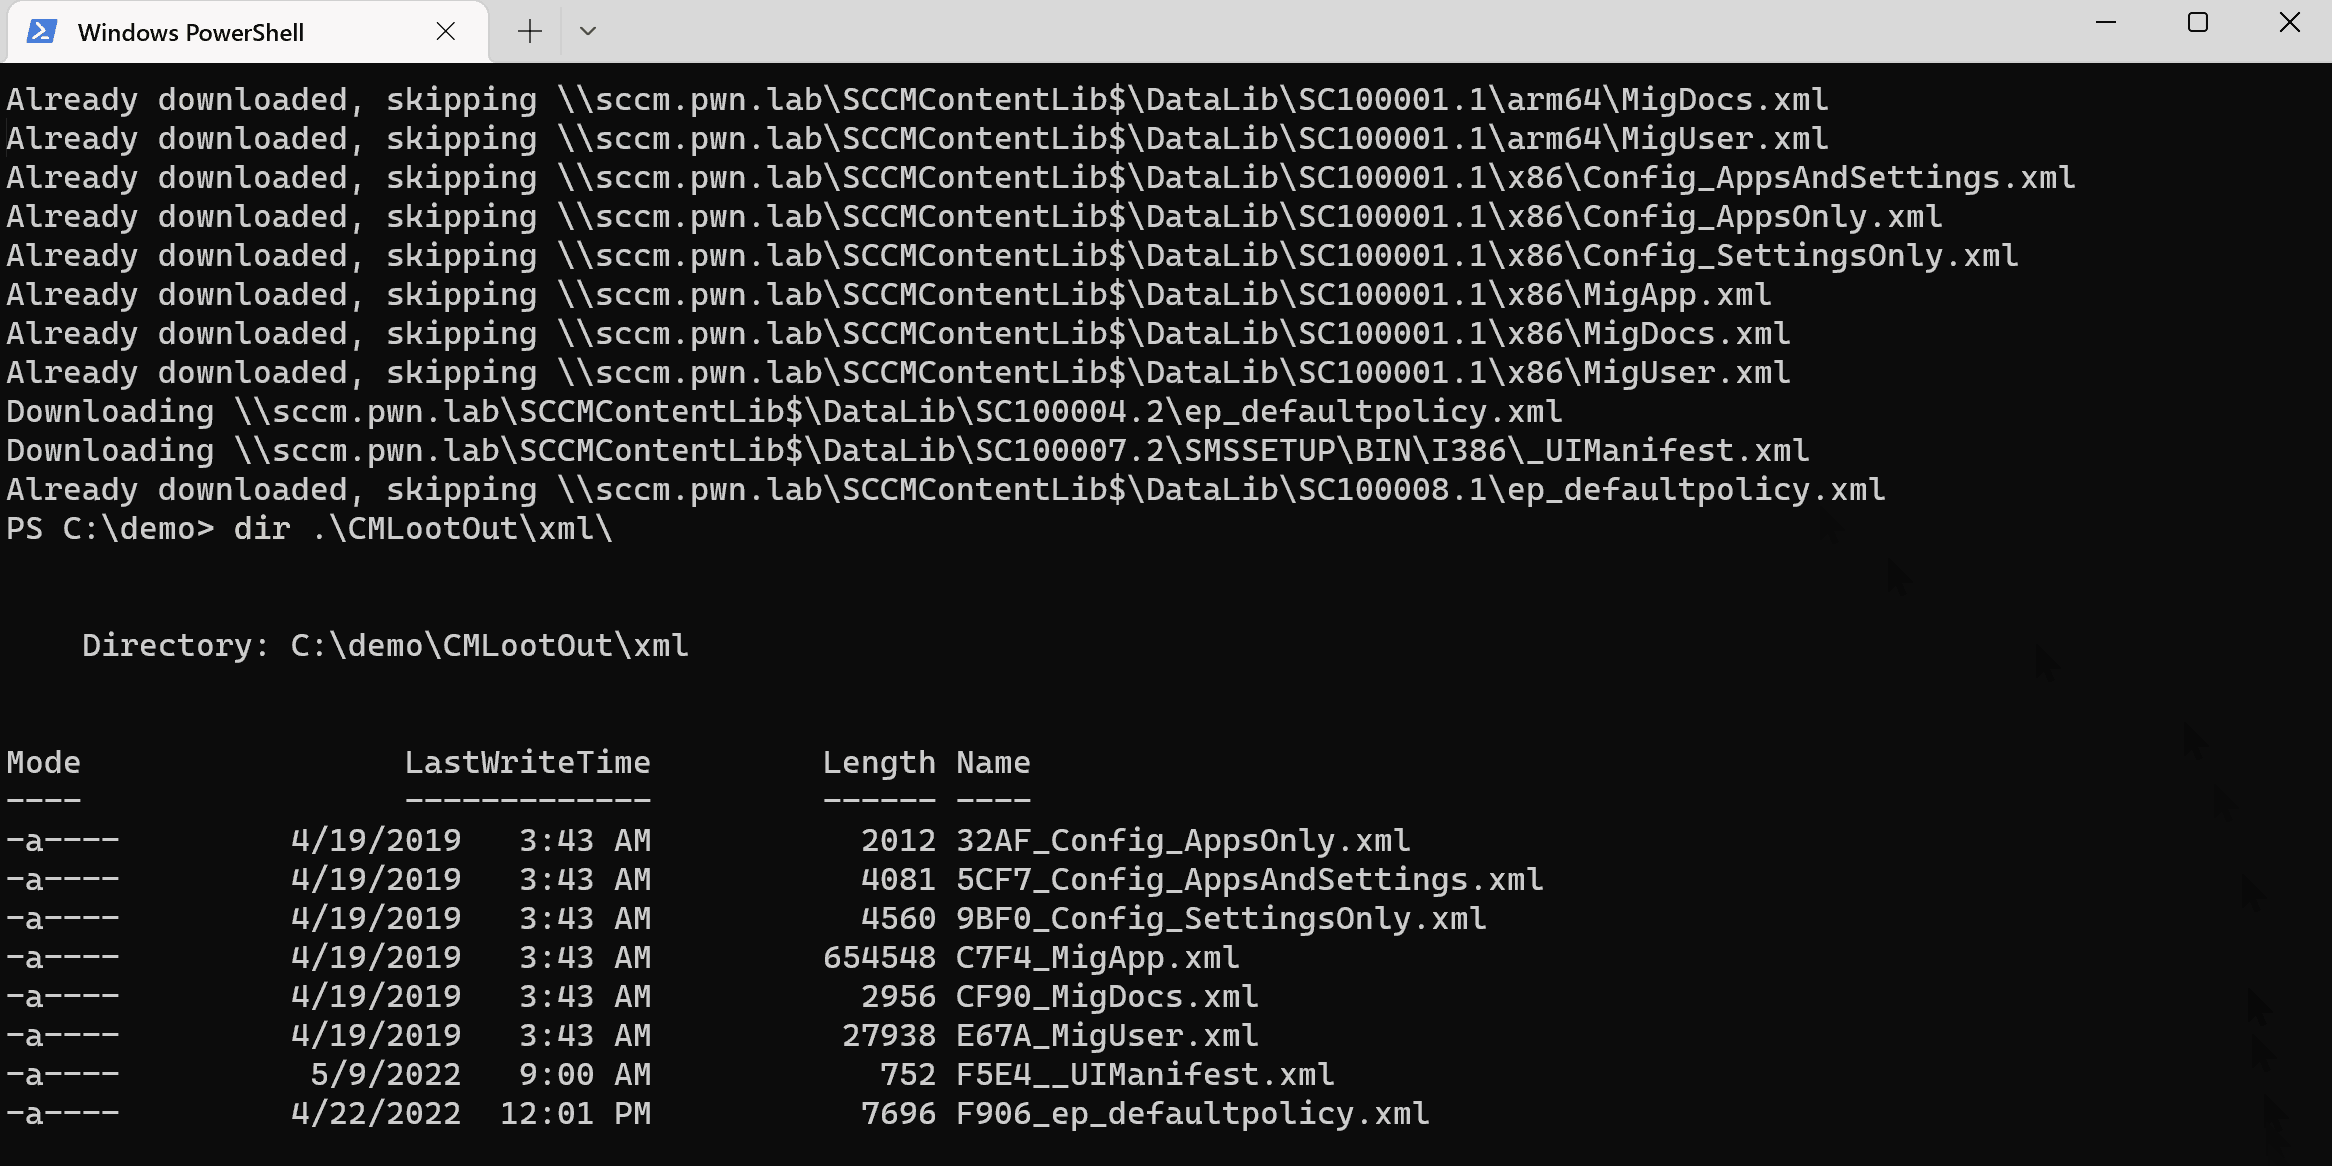 1njected/cmloot
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) SMB shares
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
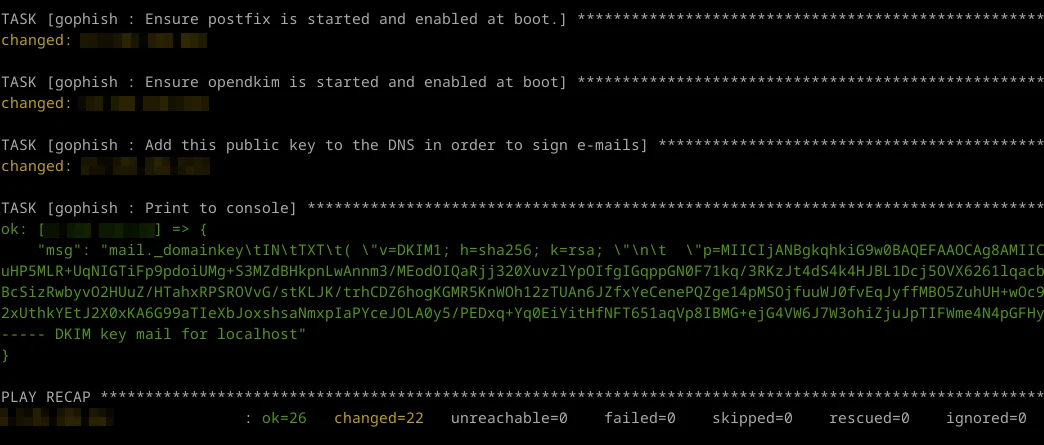 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 dviejopomata/cve-2020-8554
Proof-of-concept exploit for CVE-2020-8554, demonstrating Kubernetes service externalIP manipulation to achieve man-in-the-middle attacks on cluster…
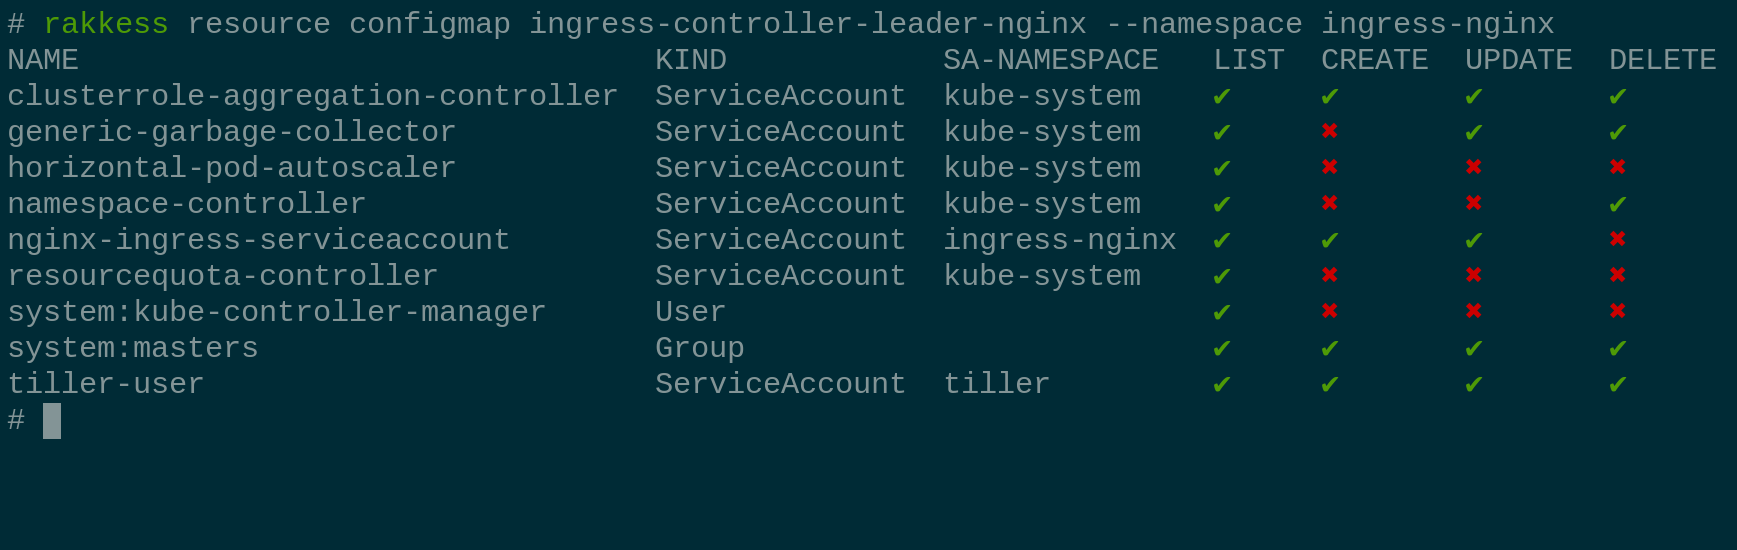 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources
 qarait/ephemera
Zero-Trust SSH CA