

SCOPE
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
ai-securitycloud-infrastructure-securitycloud-security+8
54
tayontech/scopeAI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 armourbird/csf
ArmourBird CSF - Container Security Framework
 derekpreston81/cve_adc_ioc_2026
Citrix NetScaler CVE Preconditions Checker as per CTX696604 | Supported CVE : CVE-2026-8451, CVE-2026-8452, CVE-2026-8655, CVE-2026-10816,…

 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.
 tuladhar/ingress-nightmare
IngressNightmare (CVE-2025-1974)
 netflix/security_monkey
Security Monkey monitors AWS, GCP, OpenStack, and GitHub orgs for assets and their changes over time.
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
 aws/serverless-application-model
Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 netflix/repokid
AWS Least Privilege for Distributed, High-Velocity Deployment
 owasp/dvsa
a Damn Vulnerable Serverless Application
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 cyberark/blobhunter
Find exposed data in Azure with this public blob scanner
 devzero-security/redstackpro
Compose red team infrastructure and Active Directory ranges on a canvas, then compile to a complete Terraform and Ansible working directory you run…
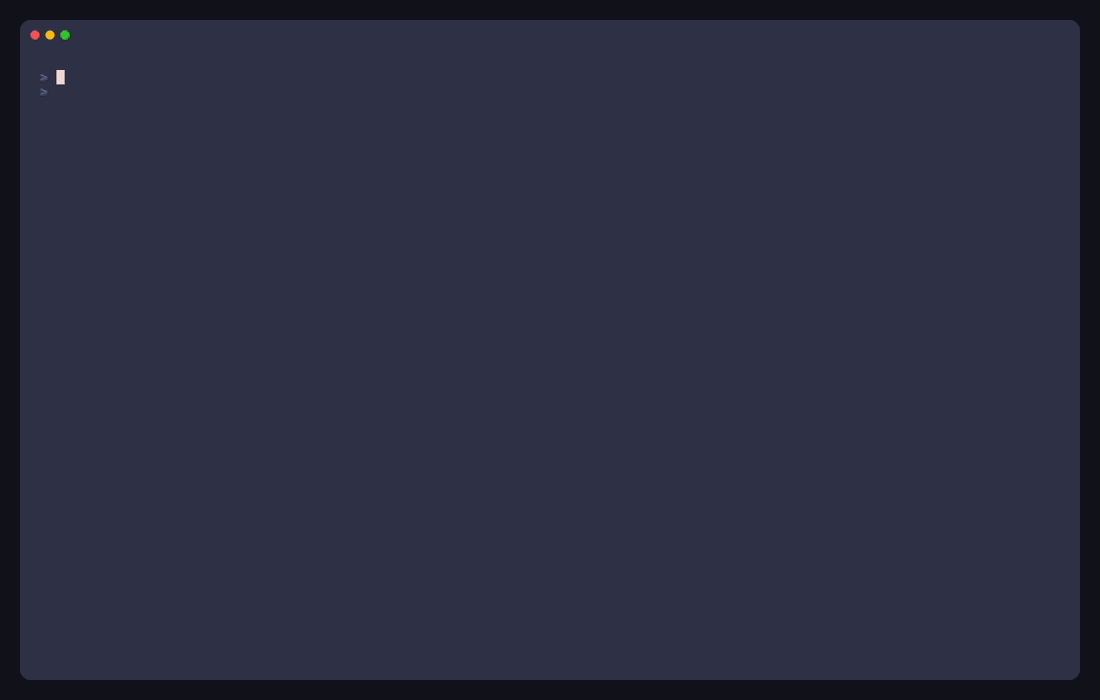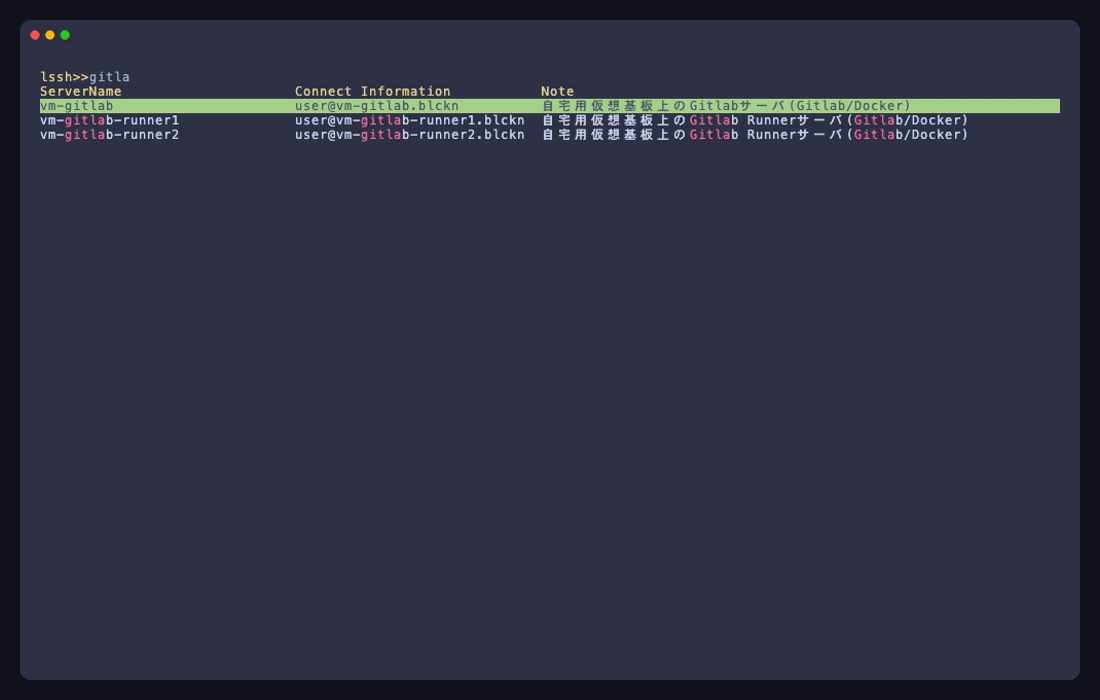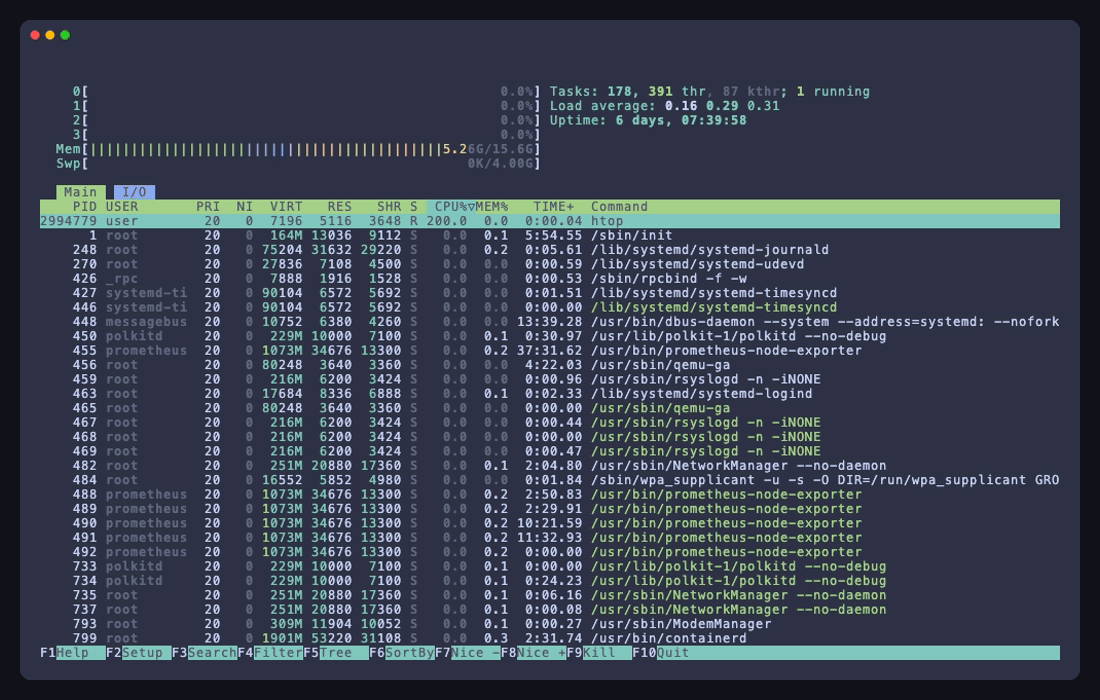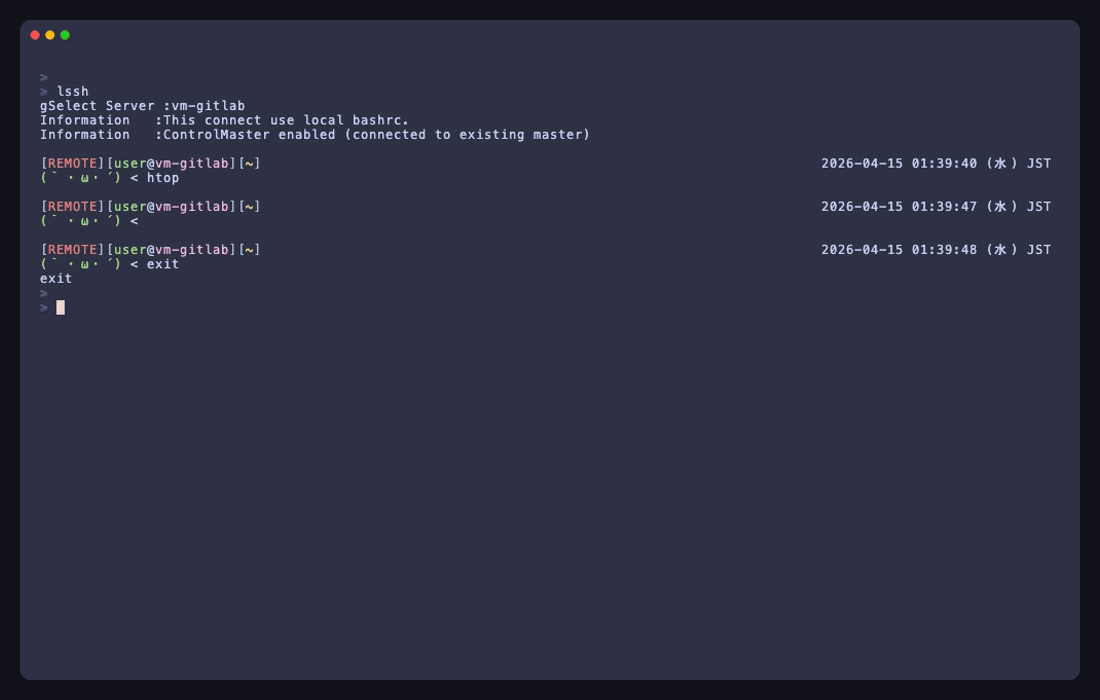 blacknon/lssh
A terminal-native remote access suite for SSH, cloud inventories, provider-backed connectors, parallel commands, mux workspaces, file transfer, and…
 9rnt/poro
Scan publicly accessible assets on your AWS cloud environment
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS