
Thunderstorm
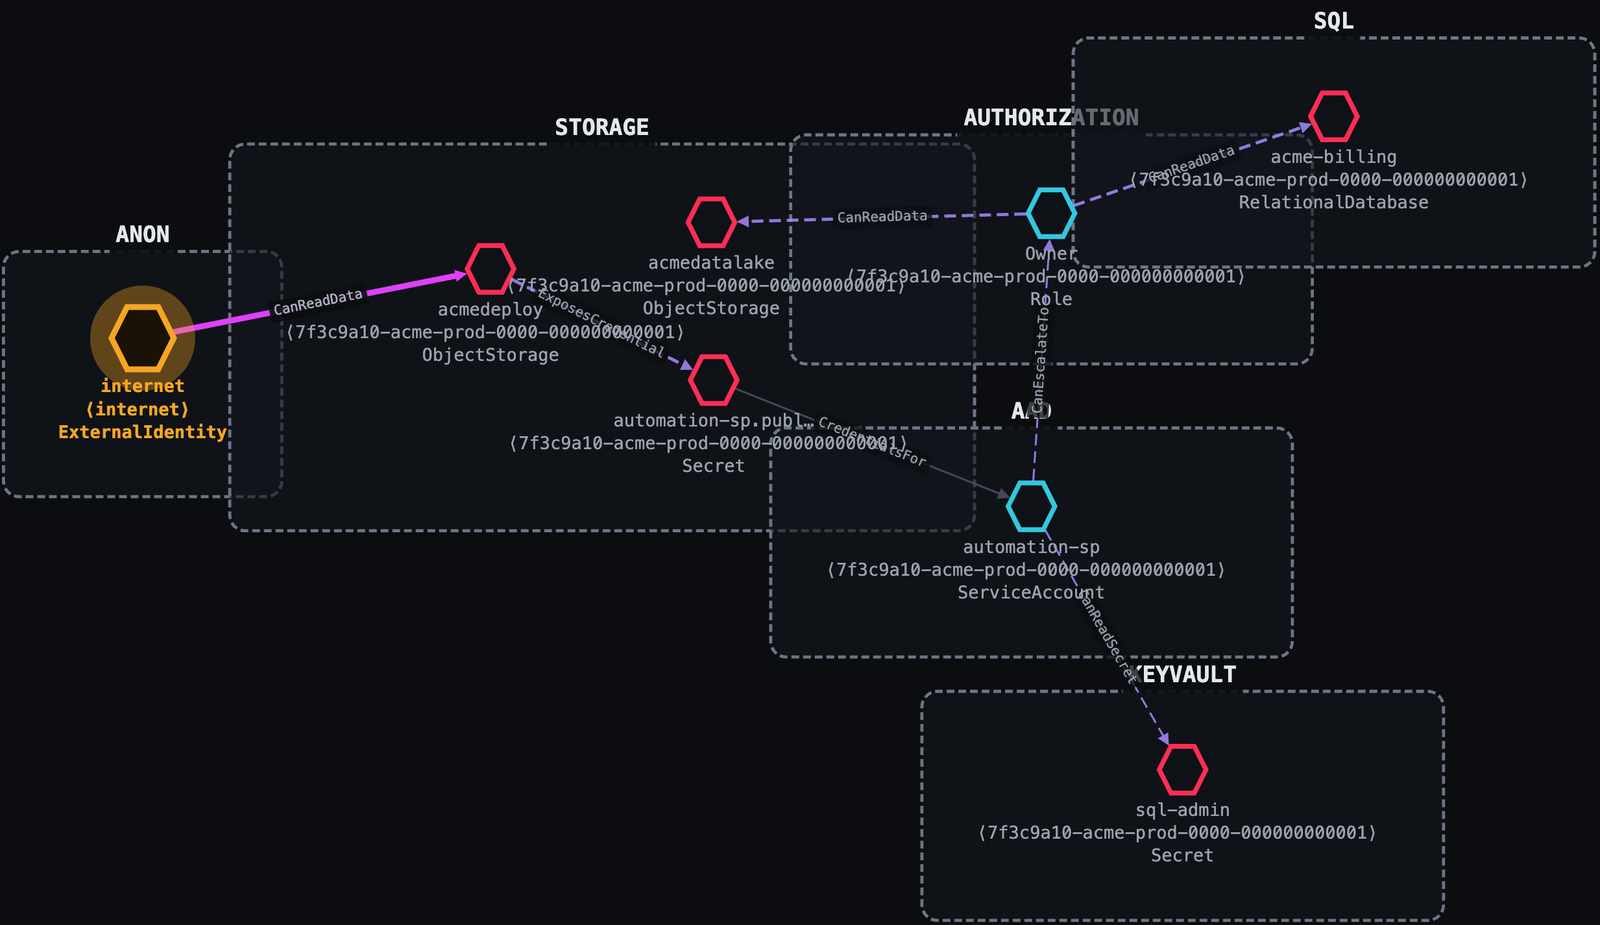
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

kubeaudit helps you audit your Kubernetes clusters against common security controls

Extensible Azure Security Tool - Documentation

Open Cloud Security Posture Management Engine

Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.

A software supply chain framework powered by Nix.

Open-source IoT Platform - Device management, data collection, processing and visualization.

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Dockerized mail server suite with Postfix, Dovecot, Rspamd, and ClamAV. Provides secure email hosting with integrated spam filtering, antivirus, and…

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark

Branchable computing by using a portable, lightweight, self-contained virtual machine

Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.

CloudMapper helps you analyze your Amazon Web Services (AWS) environments.

Write tests against structured configuration data using the Open Policy Agent Rego query language