
ROADtools
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
authenticationcloud-infrastructure-securitycloud-security+5
2.7k
dirkjanm/roadtoolsA collection of Azure AD/Entra tools for offensive and defensive security purposes
 crowdstrike/crt
Audits Azure AD and Exchange Online configurations for hard-to-find permissions, federation trusts, mail forwarding rules, and delegated access to…
 tmobile/pacbot
PacBot (Policy as Code Bot)
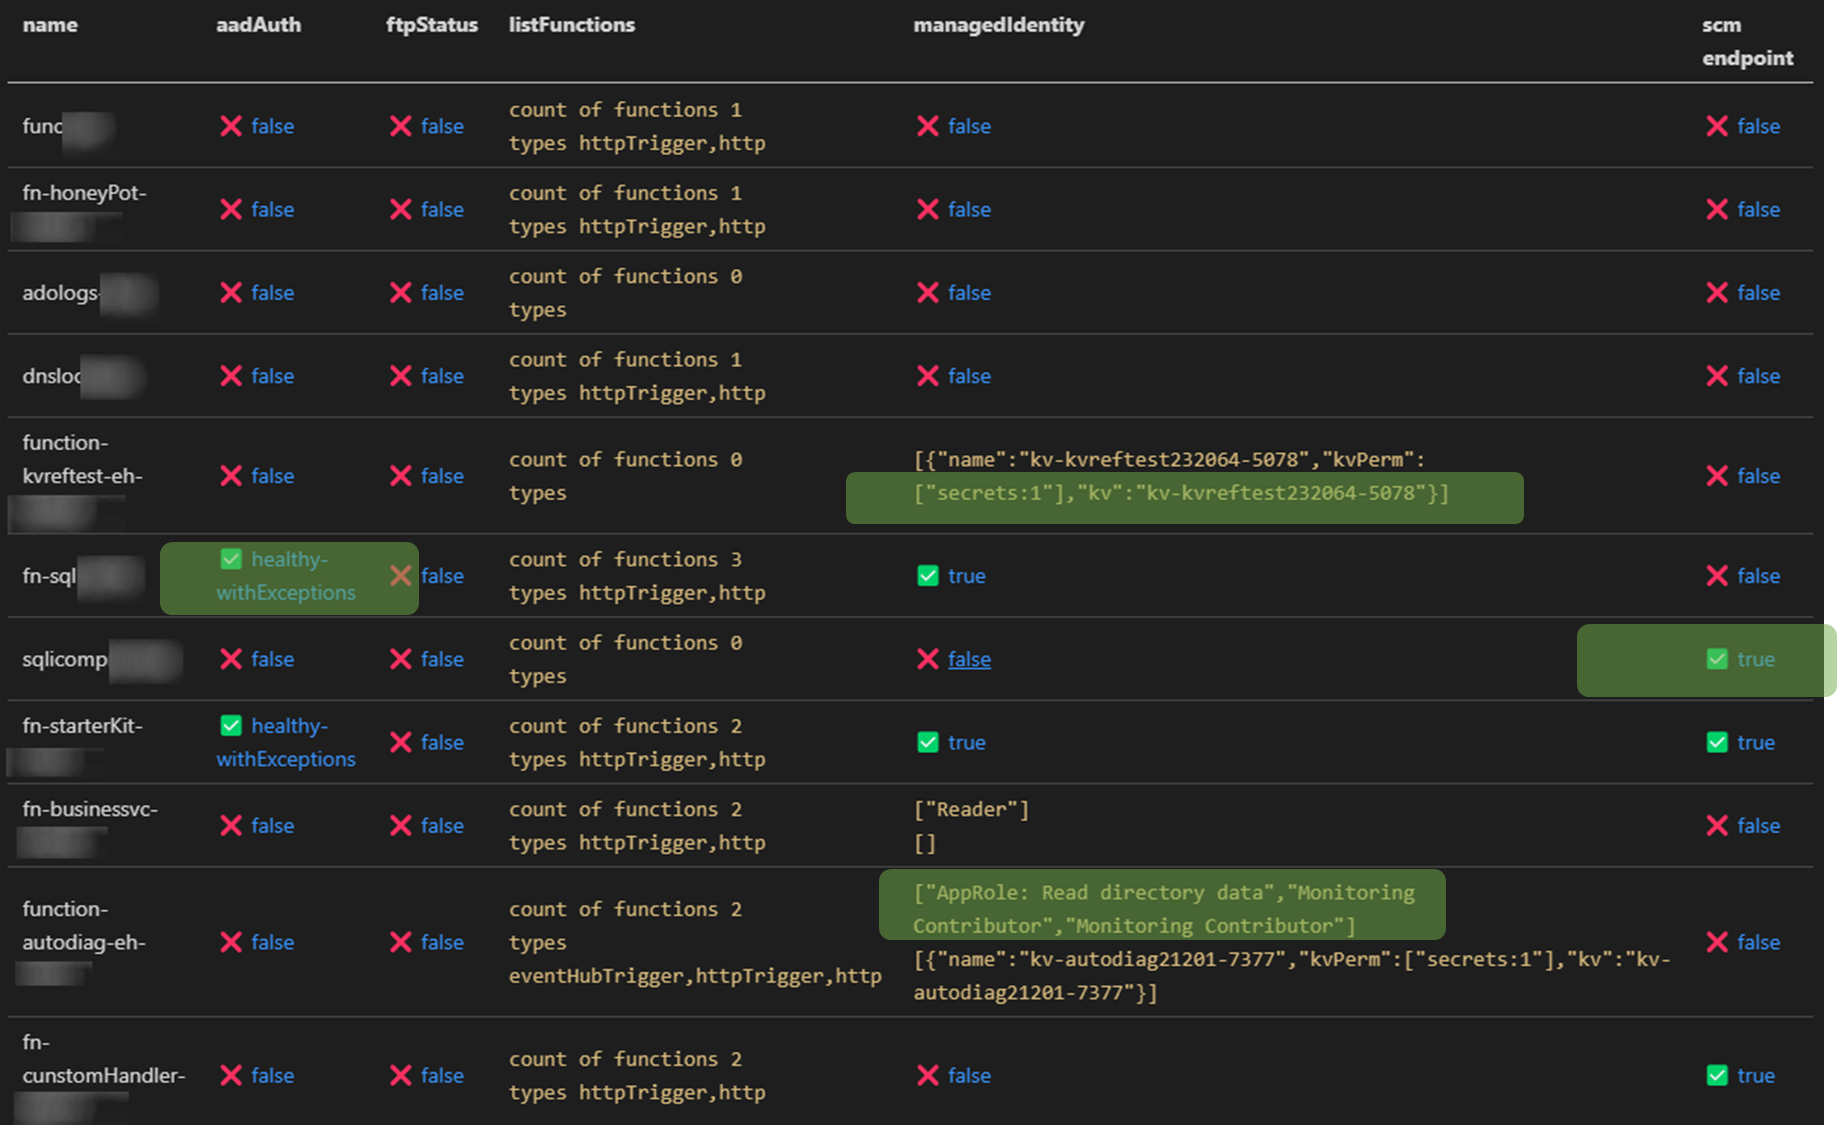 jsa2/east
Extensible Azure Security Tool - Documentation
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
 radzarr/wsusresponder
Module PowerShell de réponse à l'incident CVE-2025-59287 — WSUS Remote Code Execution (RCE)
 iknowjason/purplecloud
A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…
 mandiant/azure_workshop
Terraform-deployable vulnerable-by-design Azure lab with realistic attack paths and common misconfigurations for practicing red teaming and security…
 azuread/azure-ad-incident-response-powershell-module
The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…
 0xballpoint/load
Lord Of Active Directory - automatic vulnerable active directory on AWS
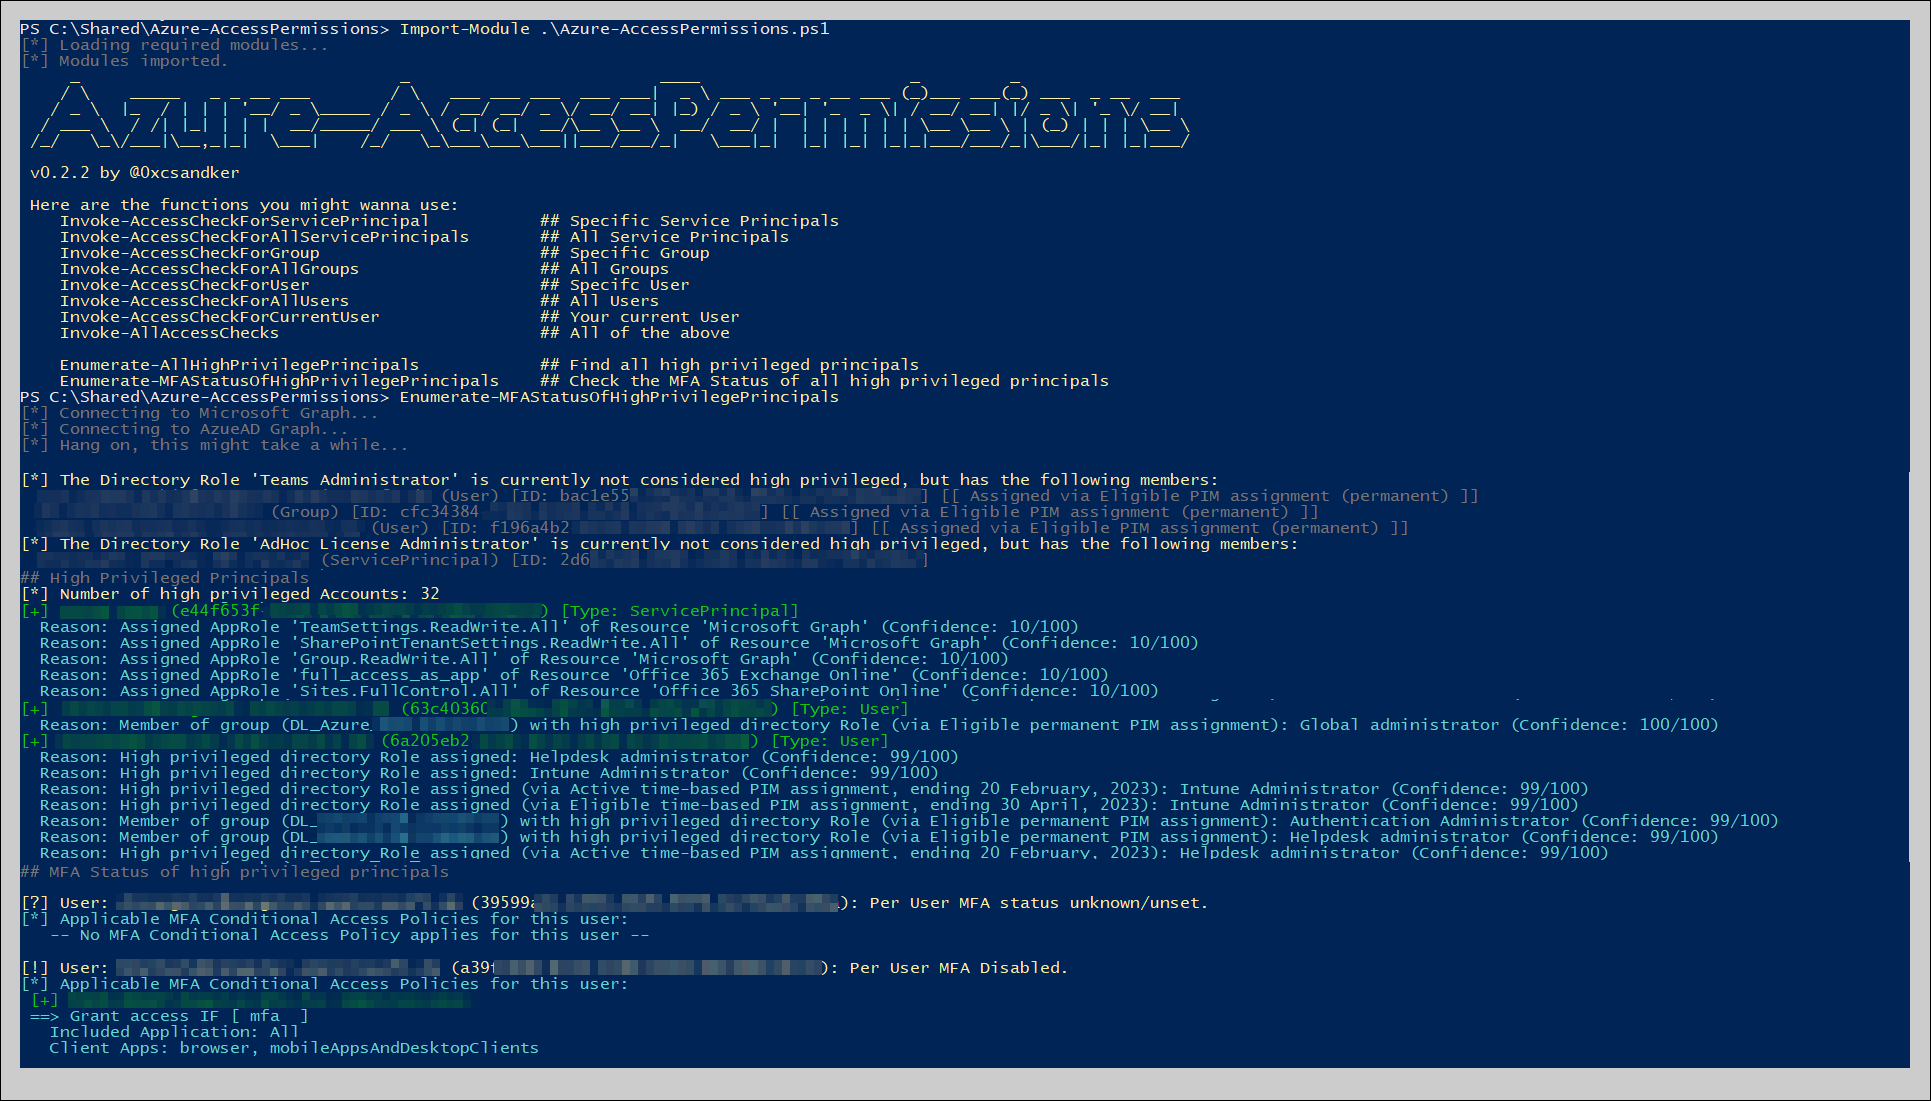 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
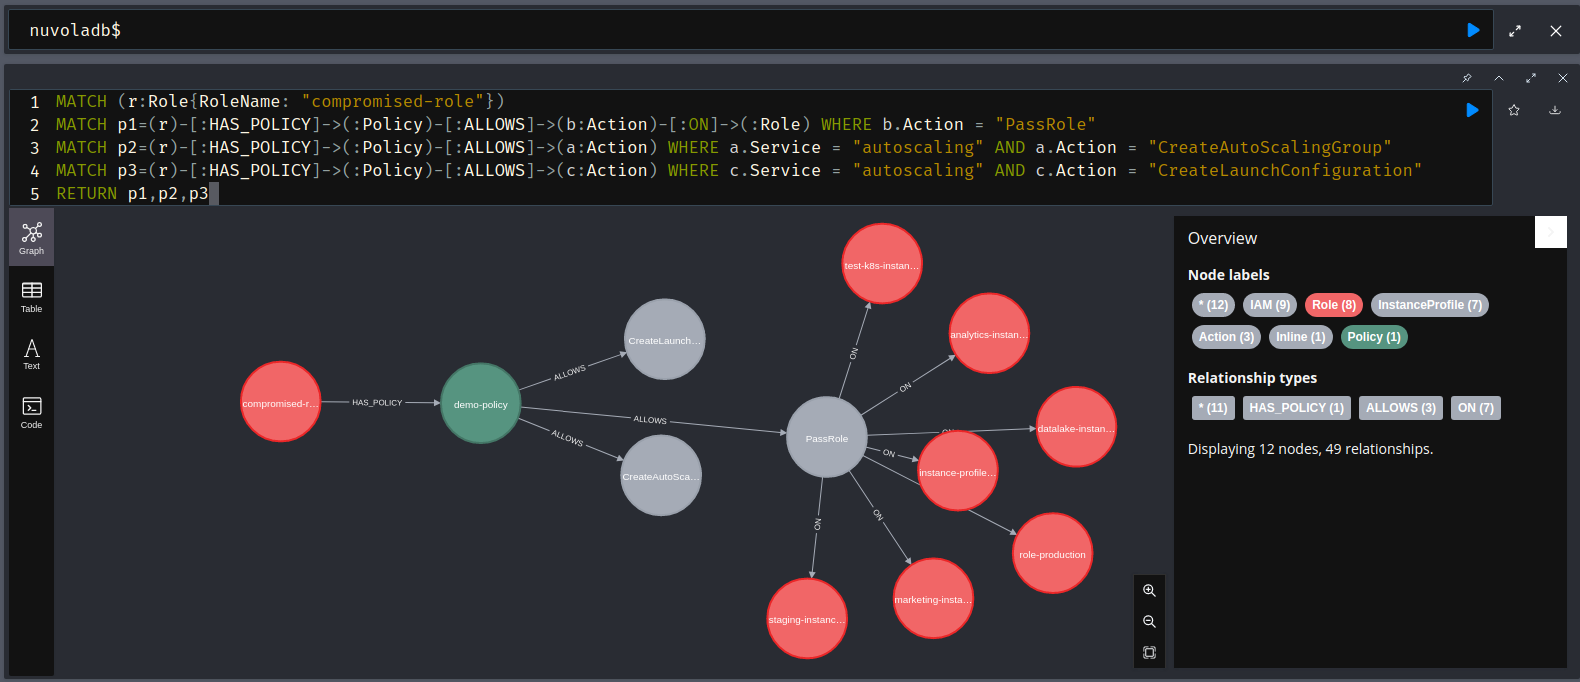 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 automatedlab/automatedlab
PowerShell-based provisioning framework for deploying complex lab environments on Hyper-V and Azure. Supports Windows, Linux, and products like AD,…
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.